metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

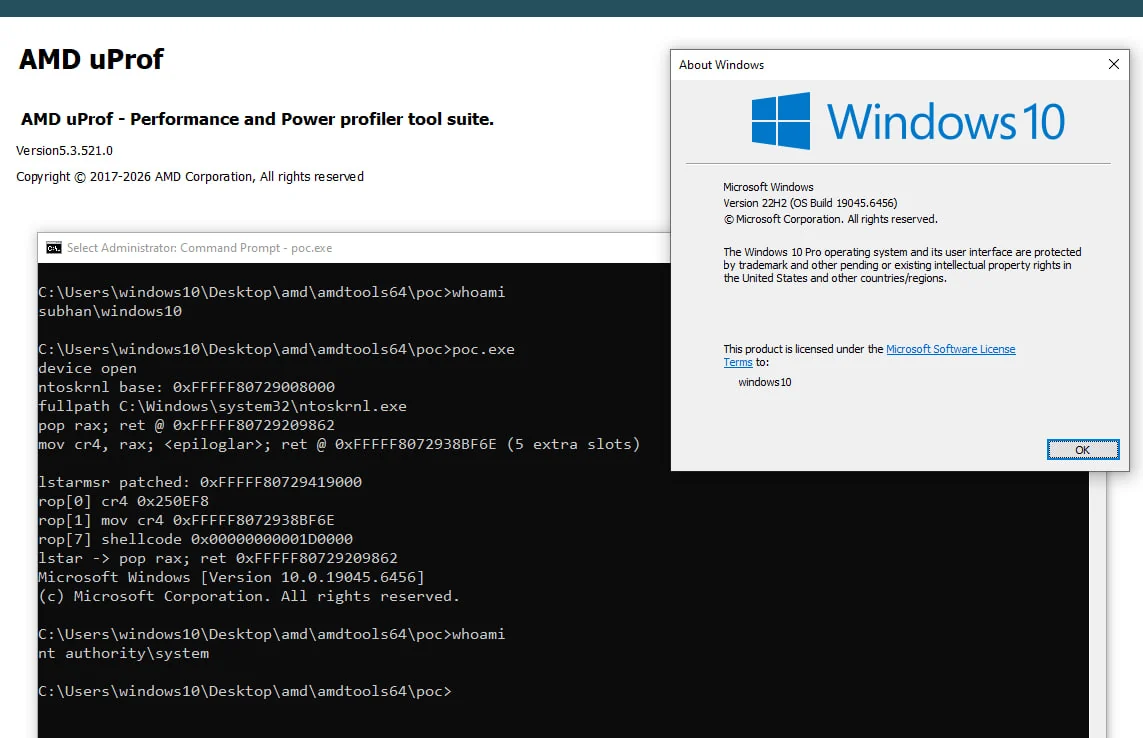
Proof-of-concept exploiting AMD AmdTools64.sys MSR read/write IOCTLs to overwrite IA32_LSTAR, bypass SMEP and escalate from administrator to SYSTEM…

ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.

Adversary Emulation Framework

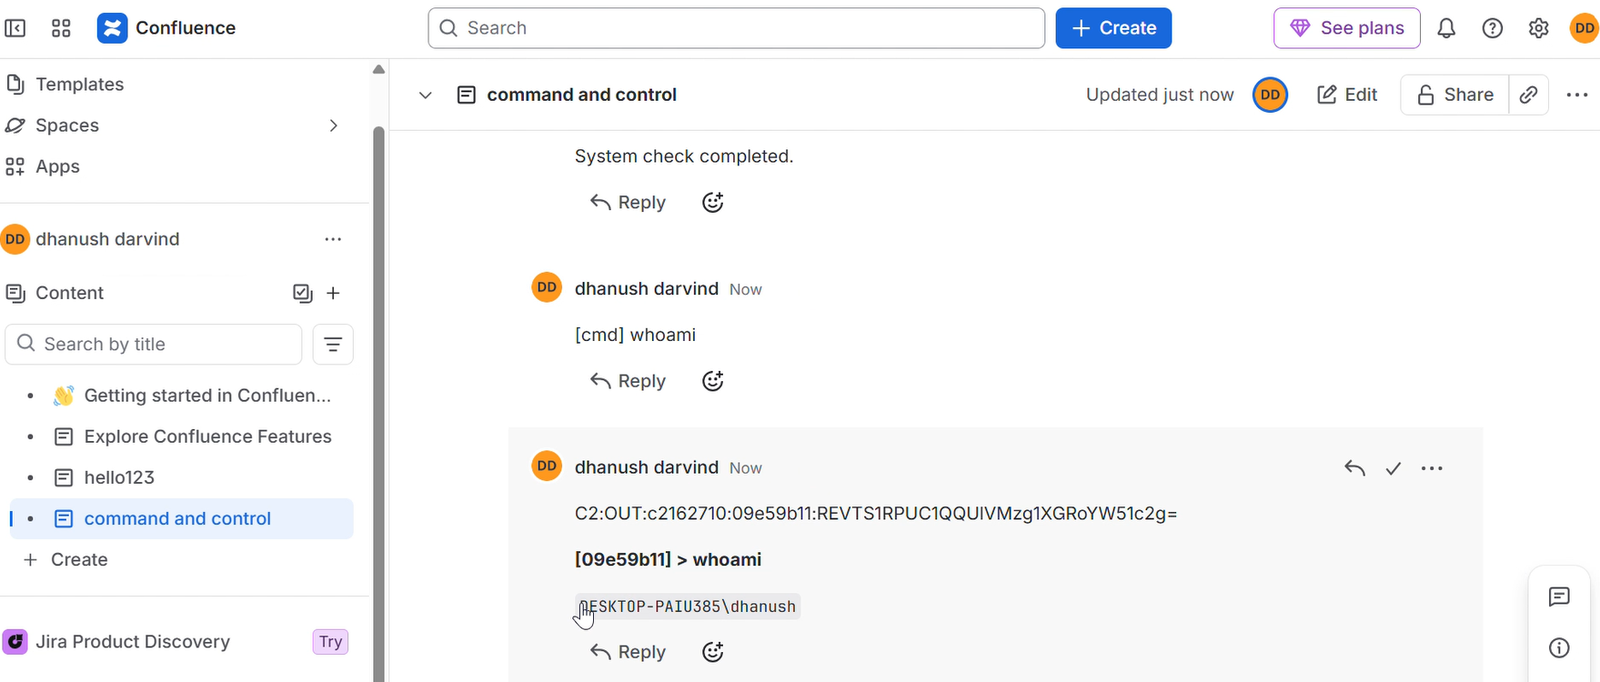
This is a project aimed to make every other Saas product a C2, confluence is just the beginning.

Minimal Windows x64 reflective PE mapper that loads DLLs from memory without LoadLibrary, resolves exports, and dispatches calls through a…

Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.

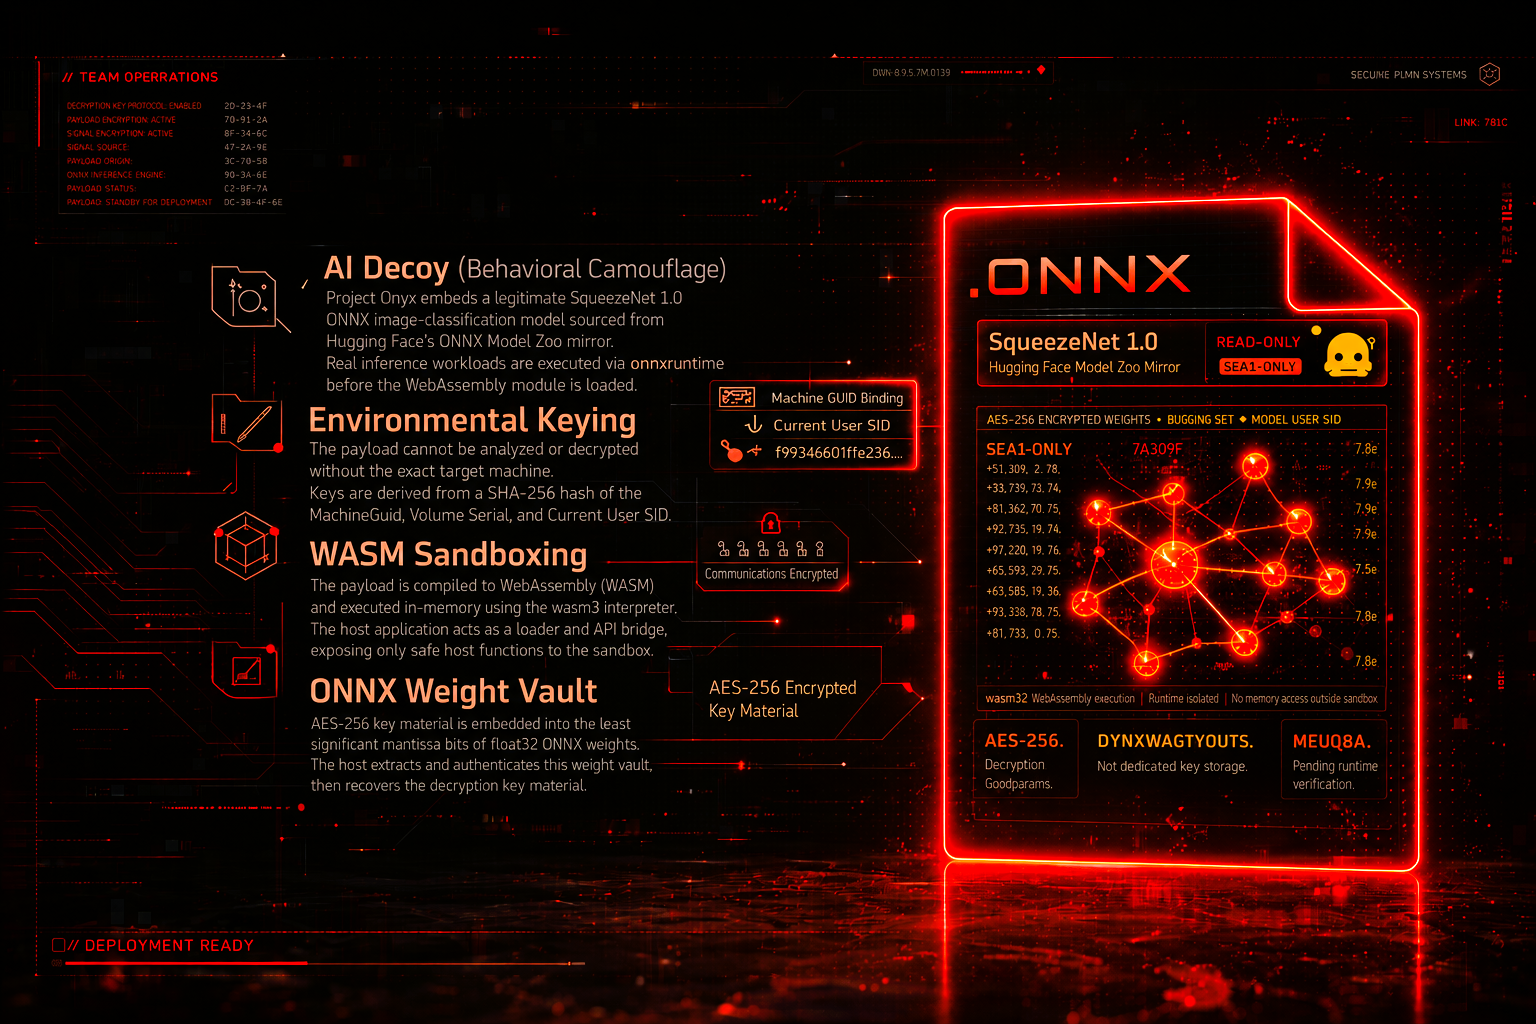
Advanced EDR Evasion via AI Telemetry Spoofing & WASM Sandboxing. Project Onyx is a PoC Red Team pipeline designed to demonstrate advanced evasion…

Chrome 152 V8 exploit chaining CVE-2026-85046 and CVE-2026-87491 to corrupt the heap, forge Wasm metadata, and execute native code from the renderer.

Statically extracts and decrypts AES-CBC/XOR-obfuscated shellcode from laZzzy-wrapped PE binaries via signature matching and RIP-relative address…

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.

Generate polymorphic, position-independent virtual machines (PIVMs) from arbitrary x86/x64 shellcode.

Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.

The FreeBSD ICMP buffer overflow, freebsd buffer overflow poc

Google Chrome CVE-2026-6307 PoC

Adversary emulation and C2 framework for security research

Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)