

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
42 results
Neo preview

Neo

GitHubstillbigjosh/neo

The NeoC2 Framework

command-and-controlexploit-frameworksids-ips-evasion+8
371 day ago
sliver preview

sliver

GitHubbishopfox/sliver

Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
11.9k3 days ago
Project-Onyx preview

Project-Onyx

GitHubx-3306/project-onyx

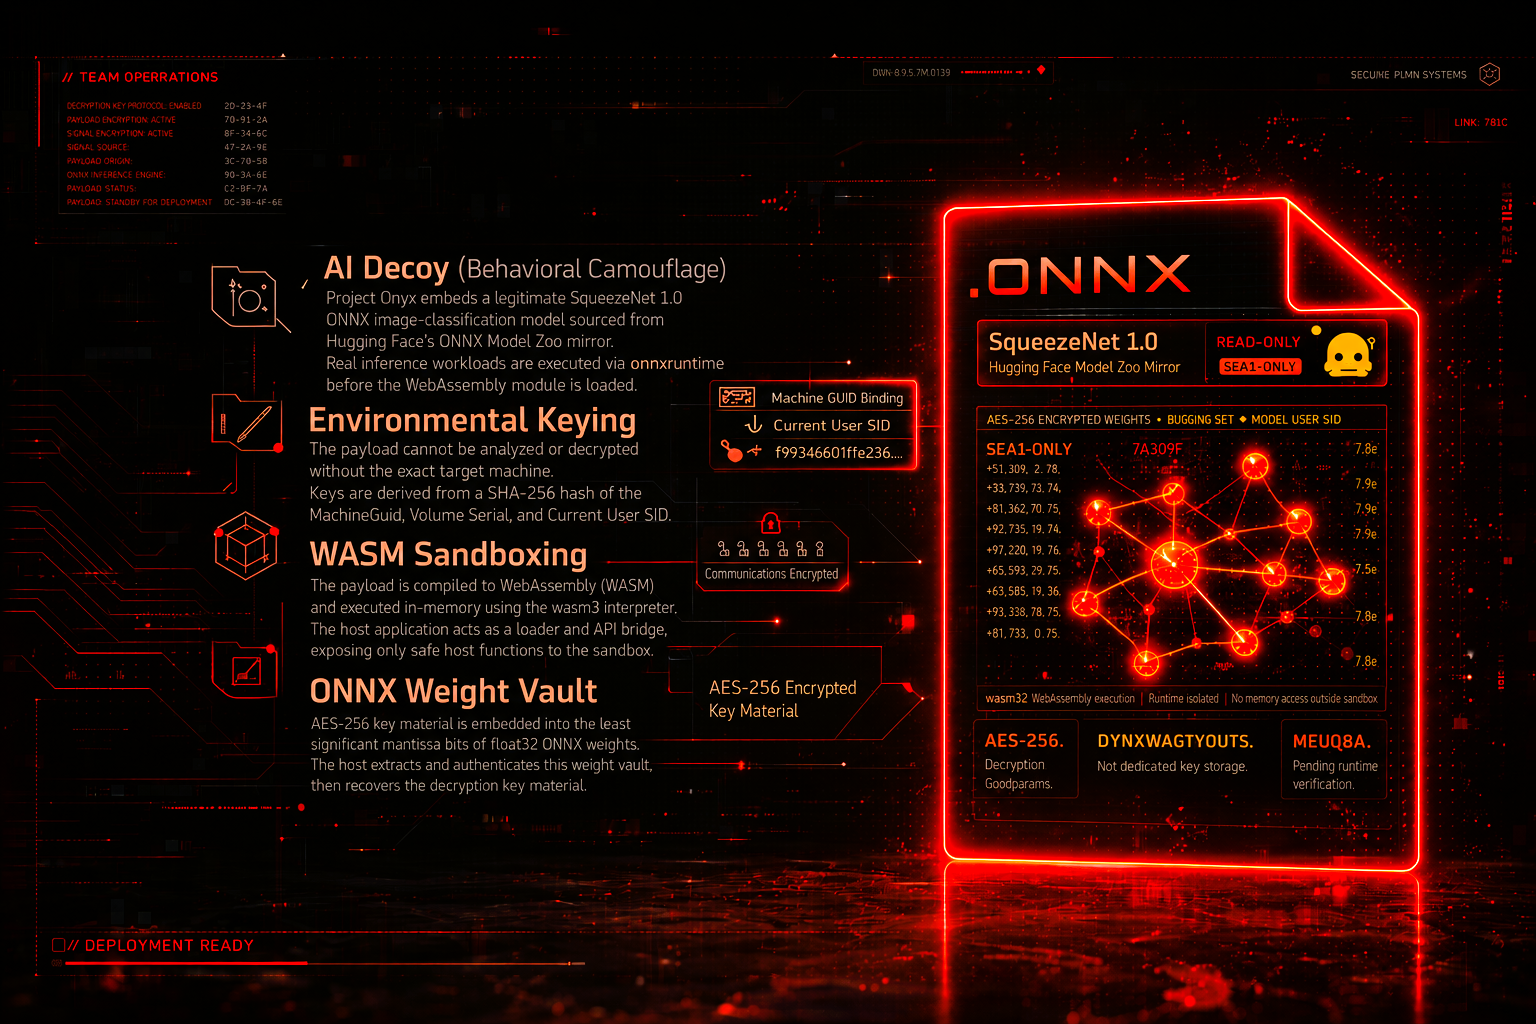
Advanced EDR Evasion via AI Telemetry Spoofing & WASM Sandboxing. Project Onyx is a PoC Red Team pipeline designed to demonstrate advanced evasion…
ai-securitycommand-and-controlcryptography+6
1177 days ago
mkPIVM preview

mkPIVM

GitHubd7ead/mkpivm

Generate polymorphic, position-independent virtual machines (PIVMs) from arbitrary x86/x64 shellcode.
exploitationmalware-analysispayload-generation+3
3861 month ago
Supernova preview

Supernova

GitHubnickvourd/supernova

Multi-cipher shellcode encryptor and obfuscator with automatic output conversion to C, C#, Rust, Nim, Python, and more. Supports ROT, XOR, RC4, AES,…
encryption-decryption-toolsexploit-frameworksmalware-analysis+3
1.0k2 months ago
Lucky-Spark preview

Lucky-Spark

GitHubschich/lucky-spark

A stealthy stager designed for shellcode payloads staged with http/https like Sliver, or on github raw.

binary-analysiscommand-and-controlexploitation+6
632 months ago
Maverick preview

Maverick

GitHubblacksnufkin/maverick

Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
binary-analysiscommand-and-controlencryption-decryption-tools+5
1173 months ago
rwsploit preview

rwsploit

GitHubabq0/rwsploit

Automated exploitation scanner for Oracle Reports Server (rwservlet) — CVE-2012-3152 / CVE-2012-3153. Detects, fingerprints, reads files via LFI,…

exploitationinformation-gatheringpayload-generation+6
64 months ago
ByteCaster preview

ByteCaster

GitHubprint3m/bytecaster

Swiss Army Knife for payload encryption, obfuscation, and conversion to byte arrays – all in a single command (14 output formats supported)! ☢️
encryption-decryption-toolspayload-developmentred-teaming+1
2316 months ago
byvalver preview

byvalver

GitHubumpolungfish/byvalver

takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities

binary-analysisexploitationmachine-learning+6
626 months ago
TangledWinExec preview

TangledWinExec

GitHubdaem0nc0re/tangledwinexec

PoCs and tools for investigation of Windows process execution techniques
adversarial-attackdebuggersids-ips-evasion+6
9597 months ago
venom preview

venom

GitHubboku7/venom

Venom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence
command-and-controlencryption-decryption-toolslateral-movement+6
43910 months ago
redpill preview

redpill

GitHubr00t-3xp10it/redpill

Assist reverse tcp shells in post-exploration tasks
defensive-toolsinformation-gatheringlateral-movement+6
21811 months ago
PichichiH0ll0wer preview

PichichiH0ll0wer

GitHubitaymigdal/pichichih0ll0wer

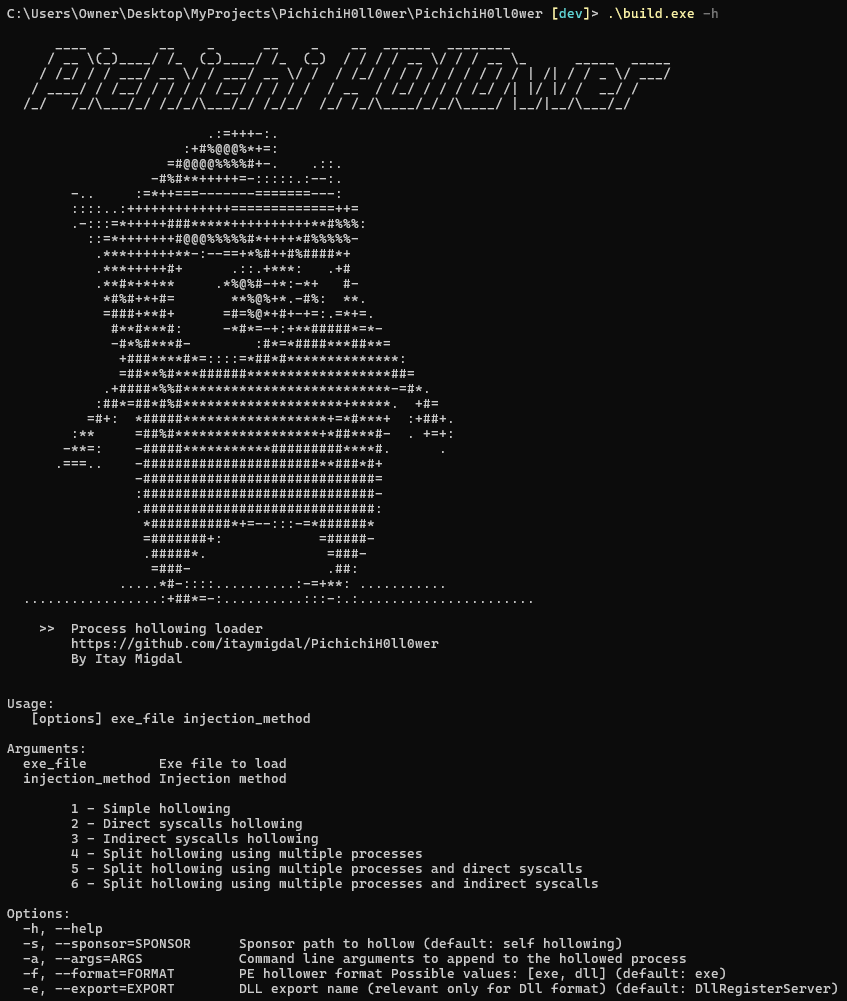
Nim-based process hollowing loader for PE executables with configurable injection methods, direct/indirect syscalls, anti-debug, payload encryption,…

binary-exploitationexploitationpayload-generation+3
641 year ago
Villain preview

Villain

GitHubt3l3machus/villain

Villain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with…

command-and-controlexploit-frameworkspayload-generation+4
4.5k1 year ago
CVE-2024-48990_needrestart preview

CVE-2024-48990_needrestart

GitHubczeti/cve-2024-48990_needrestart

Exploit for CVE-2024-48990 - Privilege Escalation in Needrestart 3.7-3. For eductional purposes only
binary-exploitationeducationexploitation+5
51 year ago
NyxInvoke preview

NyxInvoke

GitHubblacksnufkin/nyxinvoke

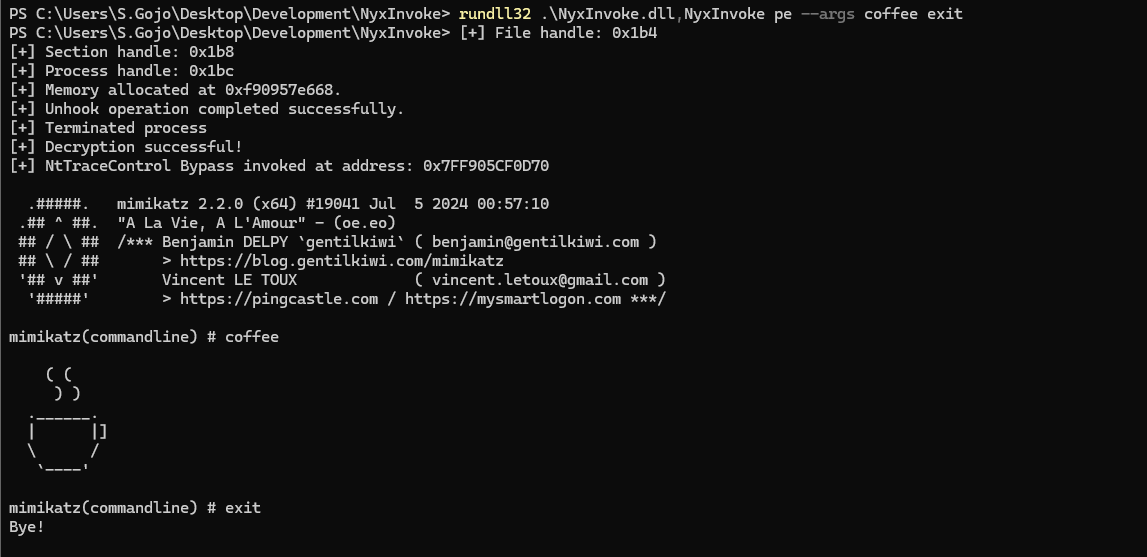
NyxInvoke is a Rust CLI tool for running .NET assemblies, PowerShell, and BOFs with Patchless AMSI and ETW bypass features. with Dual-build support

command-and-controlexploitationids-ips-evasion+6
2411 year ago
baron-samedit preview

baron-samedit

GitHubczeti/baron-samedit

This repository contains a Proof-of-Concept (PoC) exploit for the Baron Samedit vulnerability (CVE-2021-3156). The exploit demonstrates privilege…

binary-exploitationexploitationpayload-development+4
1 year ago
Previous123Next