Simple-Polymorphic-Engine-SPE32

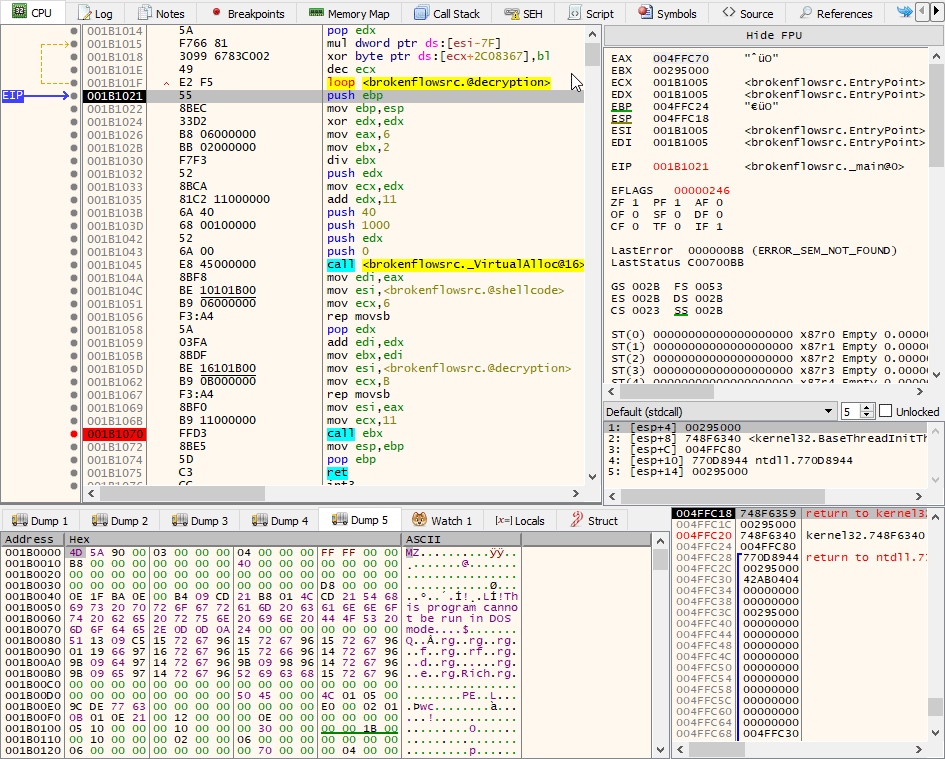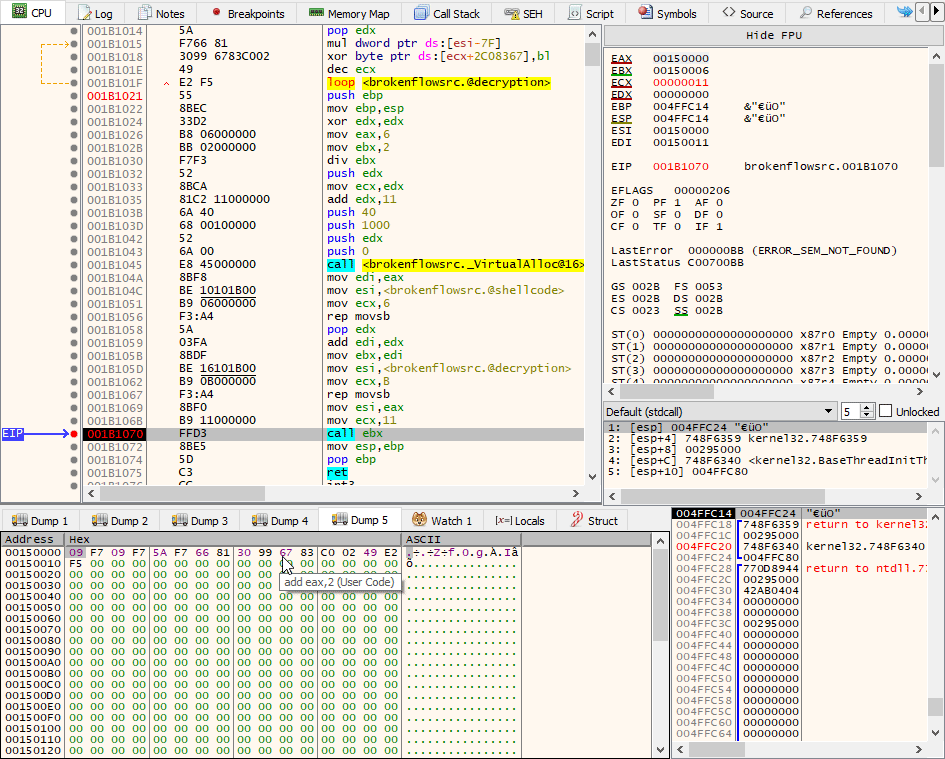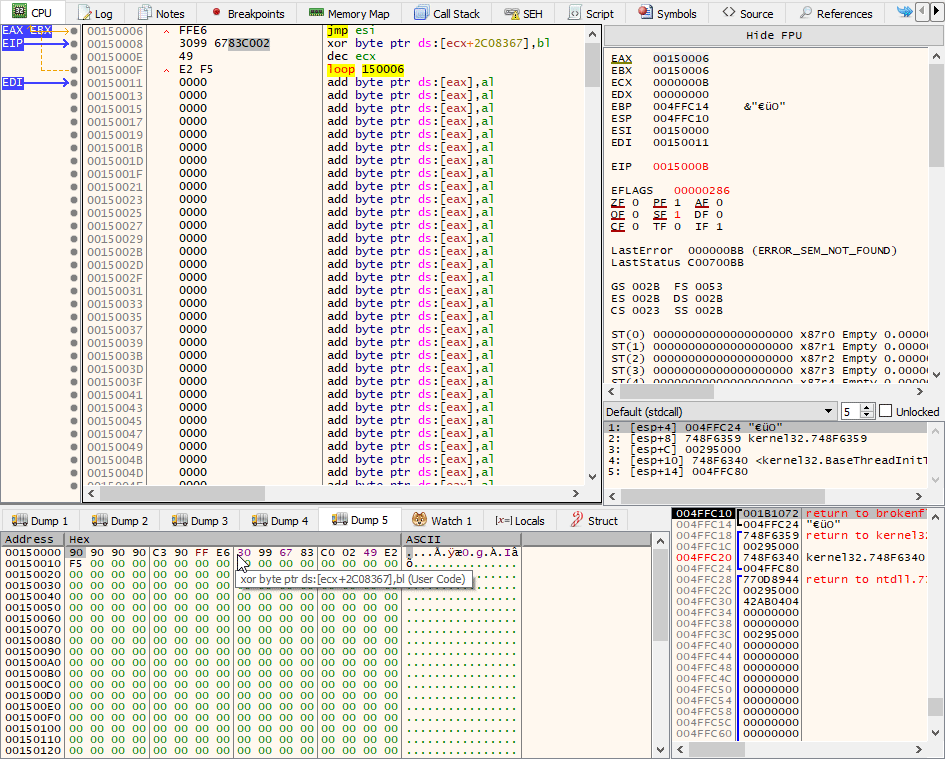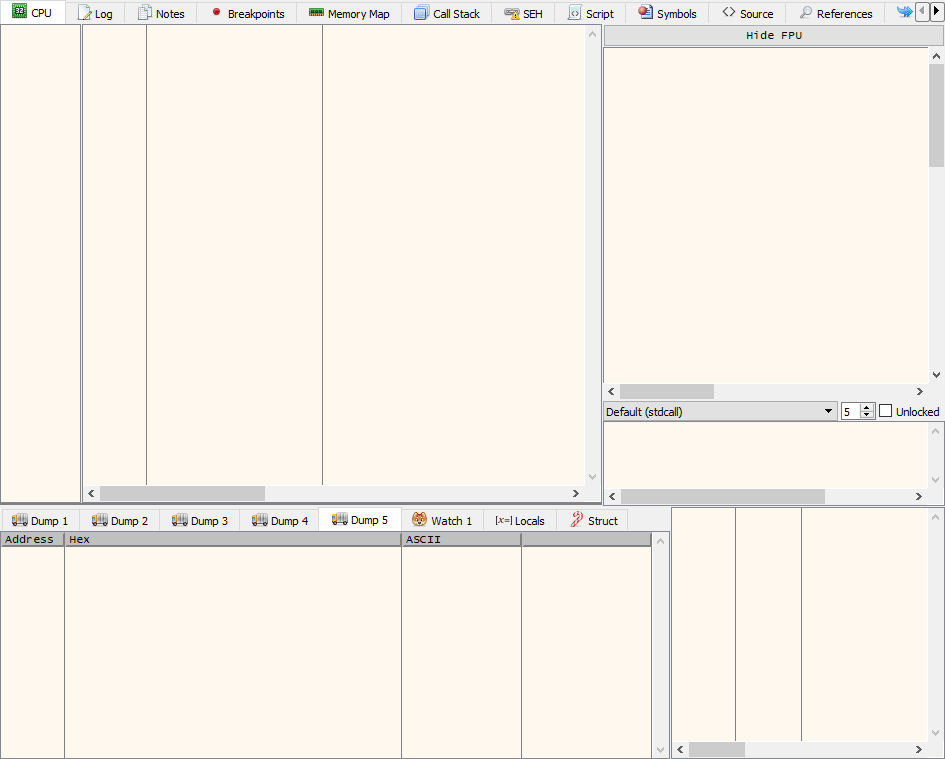
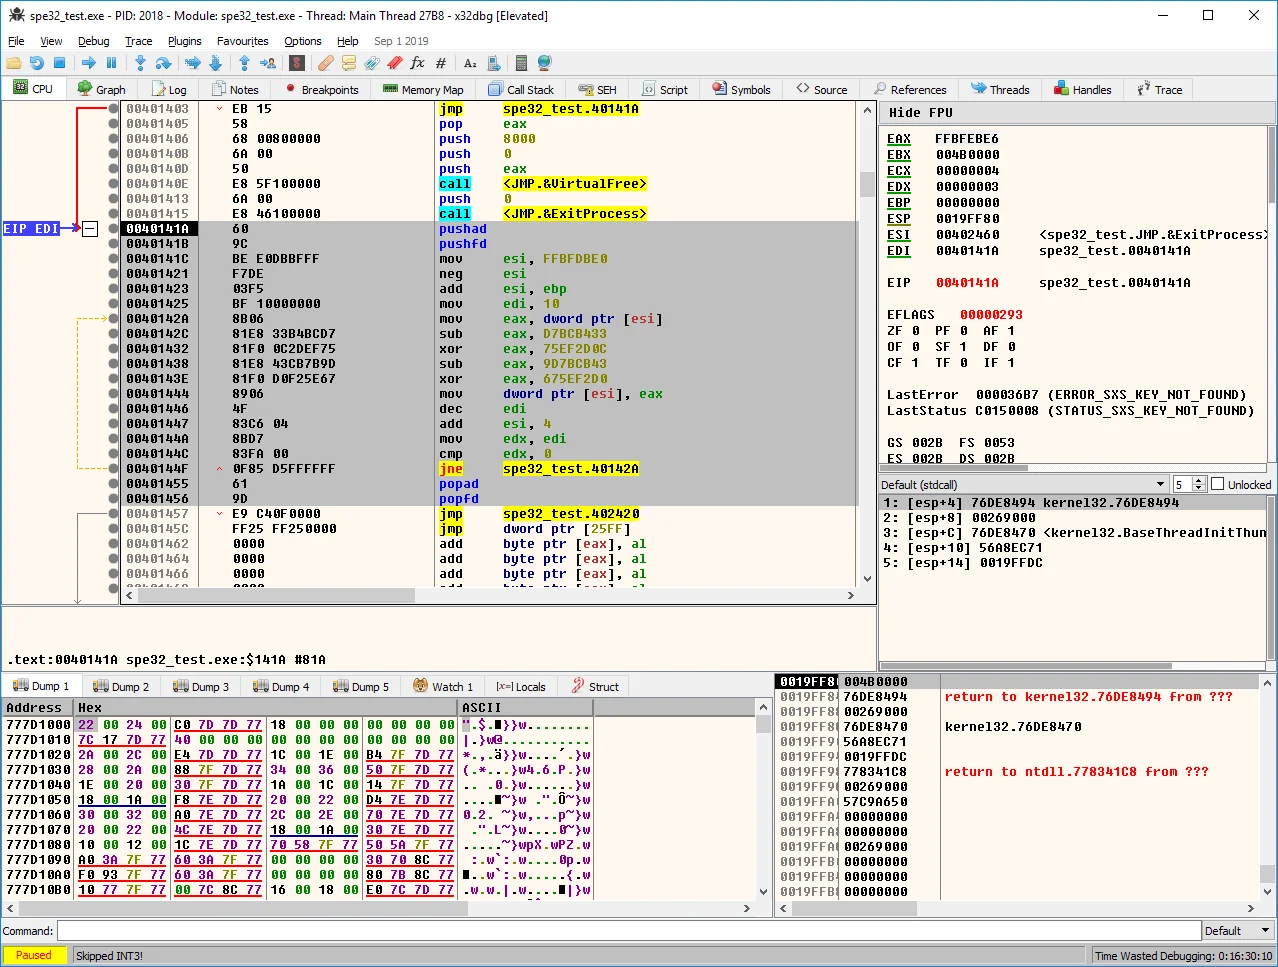
Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written…

Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written…

Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…

A simple shell code encryptor/decryptor/executor to bypass anti virus.

Simple executable generator with encrypted shellcode.

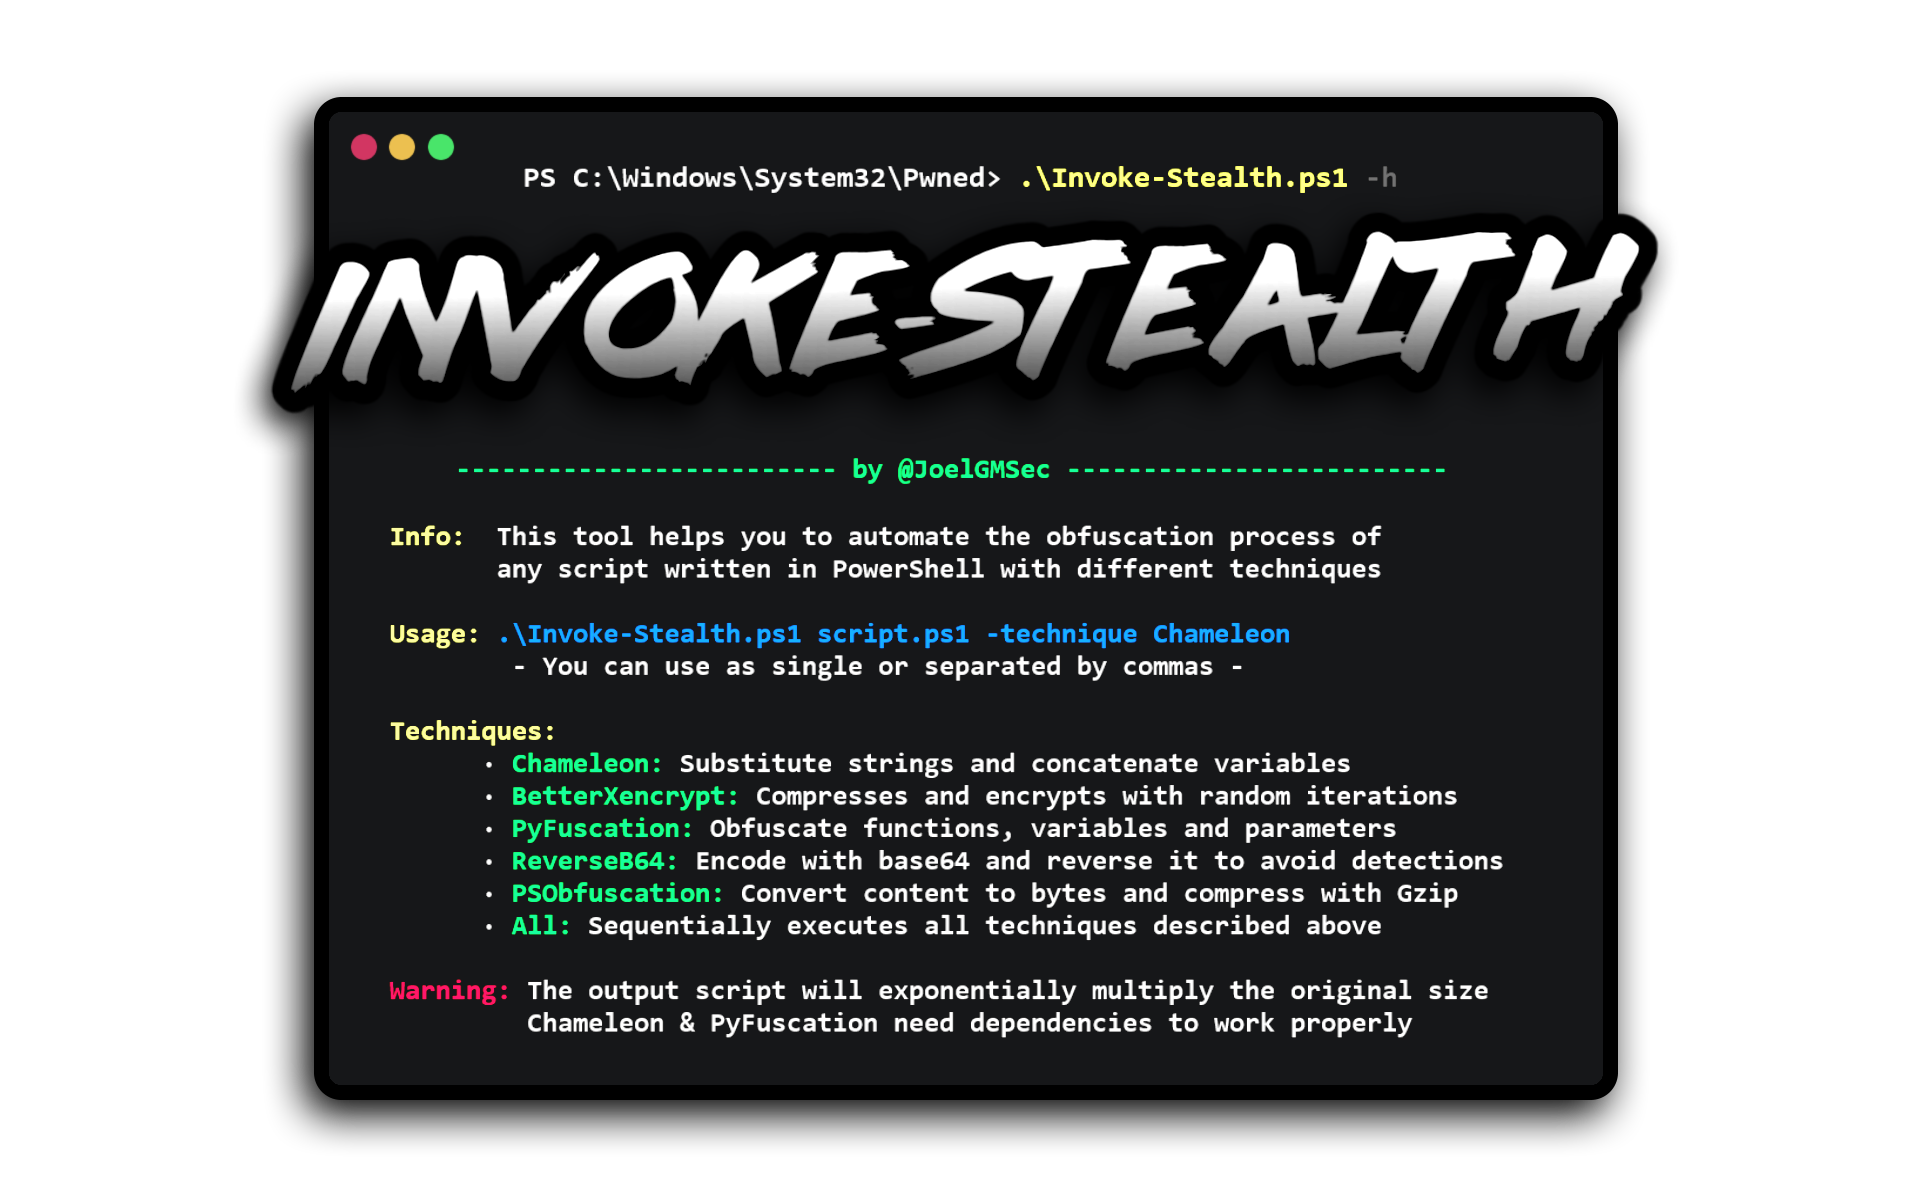
Simple & Powerful PowerShell Script Obfuscator

Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar

Armor is a simple Bash script designed to create encrypted macOS payloads capable of evading antivirus scanners.

Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…

Killer is a super simple tool designed to bypass AV/EDR security tools using various evasive techniques and used by Patchwork group.

Hershell is a simple TCP reverse shell written in Go.

Yet another shellcode runner consists of different techniques for evaluating detection capabilities of endpoint security solutions

Binary String Toolkit (BST). Quickly and easily convert binary strings for all your exploit development needs. 😎

Authenticated remote code execution exploit for PlaySMS 1.4 via CSV phonebook upload. Provides single-command and interactive shell modes for…

This repo contains : simple shellcode Loader , Encoders (base64 - custom - UUID - IPv4 - MAC), Encryptors (AES), Fileless Loader (Winhttp, socket)

template for developing custom C2 channels for Cobalt Strike using IAT hooks applied by a reflective loader.

Simple dotnet Native AOT app that uses LibObjectFile to convert shellcode to ELF

Simple dotnet Native AOT app that uses AsmResolver to convert shellcode to PE

A simple PoC to invoke an encrypted shellcode by using an hidden call