
dropengine
 s0lst1c3/dropengine
DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…
defensive-toolsexploit-frameworkspayload-development+5
214
s0lst1c3/dropengineDropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
 zcutlip/bowcaster
Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…
 cerberusmrxi/cerberus-react2shell-scanner-exploit
Elite exploitation toolkit for CVE-2025-55182 (React Server Components RCE). Async polymorphic payloads, advanced WAF/CDN bypass, proxy rotation,…
 secforce/cve-2018-8941
D-Link DSL-3782 Code Execution (Proof of Concept)
 arthastang/router-exploit-shovel
Automated Application Generation for Stack Overflow Types on Wireless Routers
 daniel224455/katana
Let's hijack our bootchain - CVE-2021-30327
 cryptogenic/ps4-5.05-kernel-exploit
A fully implemented kernel exploit for the PS4 on 5.05FW
 synacktiv/canon-mf644
Exploit and firmware analysis toolkit for Canon MF644 printer vulnerabilities, including Python exploits, ARM shellcode, and IDA Pro loader scripts…
 yanoshercohen/react2shell_cve-2025-55182
React2Shell (CVE-2025-55182) Exploit
 flopz-project/flopz
Pure Python assembler toolkit for creating shellcode, dynamically patching binaries, and instrumenting firmware images for debugging and fuzzing on…
 gelukcrab/react-server-components-rce
React Server Components 远程代码执行漏洞(CVE-2025-55182)
 otsmane-ahmed/cve-2025-2620-poc
Proof-of-concept exploit for CVE-2025-2620, a critical stack-based buffer overflow in D-Link DAP-1620 routers enabling unauthenticated remote code…
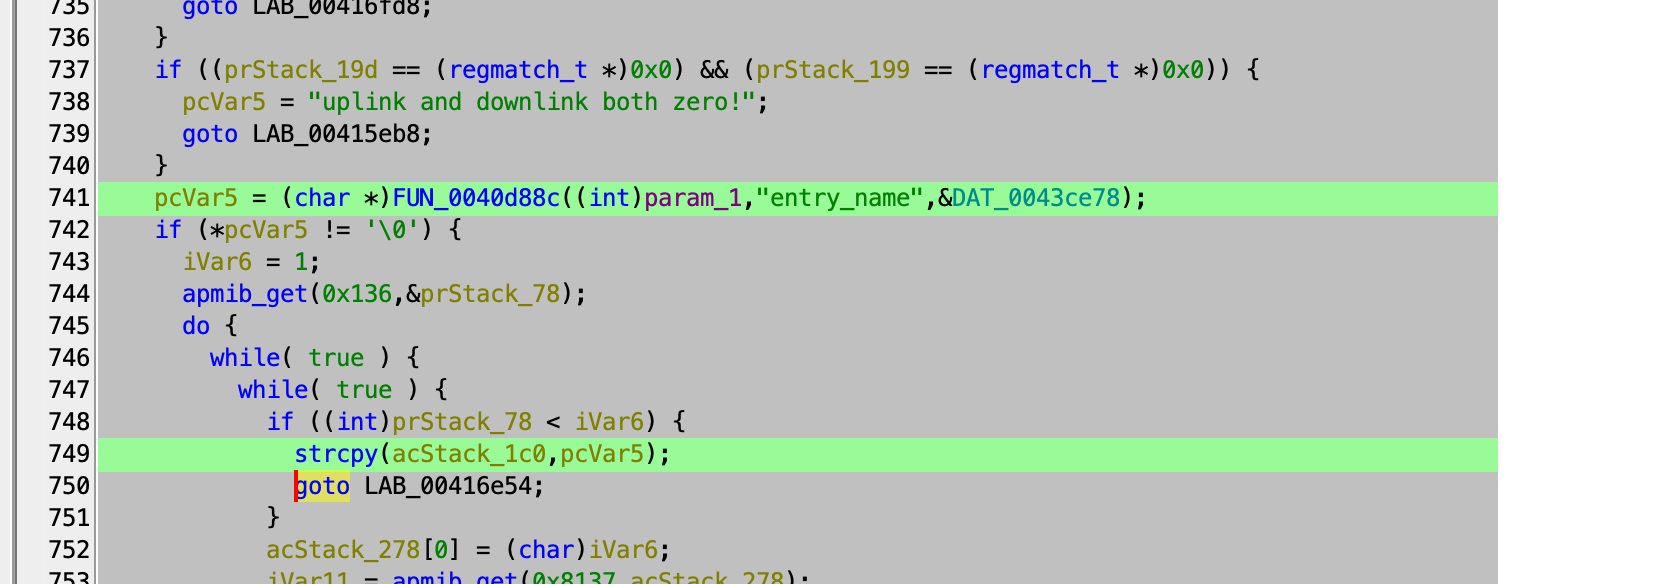 laskdjlaskdj12/cve-2024-35106-poc
Proof-of-concept exploit for CVE-2024-35106, a stack buffer overflow in NEXTU FLETA AX1500 Wi-Fi 6 router. Demonstrates denial-of-service and…
 gh0x0st/invoke-psobfuscation
An in-depth approach to obfuscating the individual components of a PowerShell payload whether you're on Windows or Kali Linux.
 laskdjlaskdj12/cve-2024-29671-poc
This is POC of CVE-2024-29671
 hujiaozhuzhu/cve-2025-55182_liyon
Python-based exploit for CVE-2025-55182 (React Server Components RCE) with interactive shell, reverse shell, batch scanning, and Docker-based…
 davidbuchanan314/wampage
WAMpage - A WebOS root LPE exploit chain (CVE-2022-23731)