

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/davidbuchanan314/wampage
Embedded Systems SecurityPrivilege EscalationVulnerability AnalysisExploitationShellcodeHardware SecurityPayload DevelopmentBinary Exploitation
GitHubdavidbuchanan314/wampage

WAMpage

WAMpage - A WebOS root LPE exploit chain (CVE-2022-23731)

View Repository
497294 years agoReviewed by Kitploit
Share
Website

WAMpage

WAMpage - A WebOS root LPE exploit chain (CVE-2022-23731)

This exploit is mainly of interest to other researchers - if you just want to root your TV, you probably want RootMyTV, which offers a reliable 1-click persistent root.

Currently only supports WebOS 4.x on 32-bit SoCs. This software is provided AS IS, use at your own risk, etc. etc.

Writeup: https://www.da.vidbuchanan.co.uk/blog/webos-wampage.html
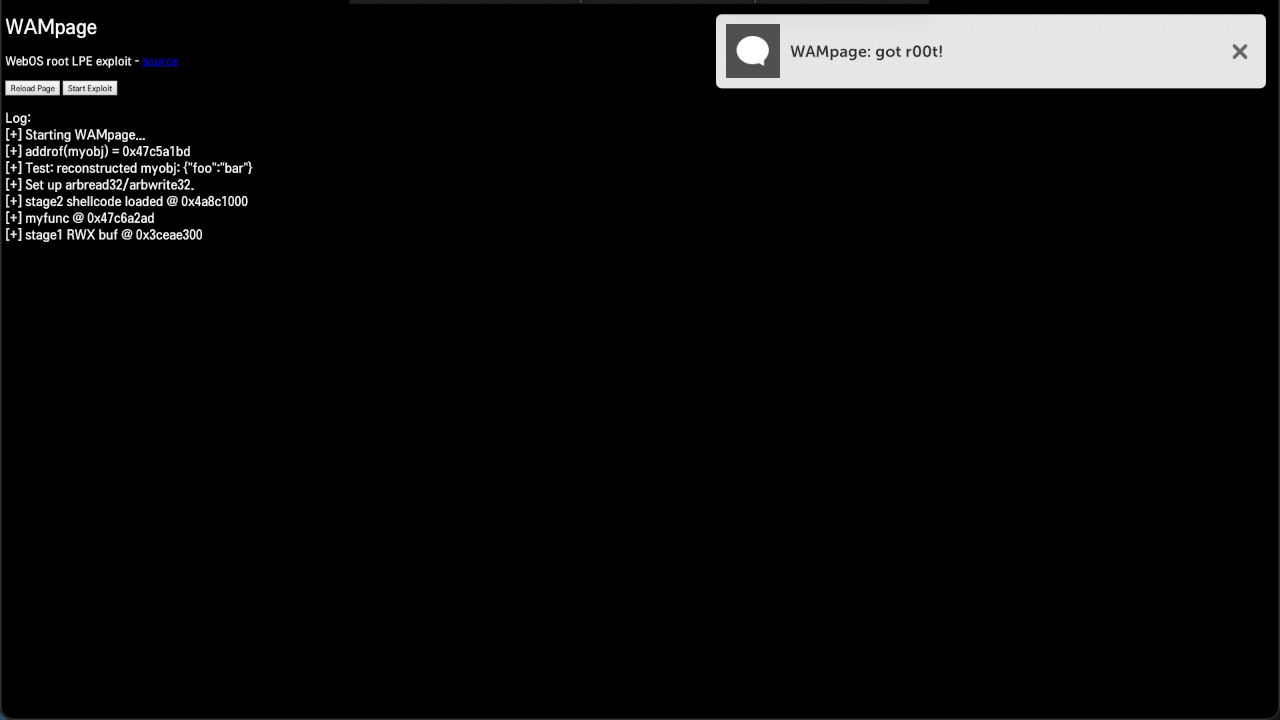
image

Building

Prerequesites:

apt install qemu-user
npm install -g @webosose/ares-cli

Compiling:

make

Testing Locally

make test will build and run the exploit in d8, running in qemu-arm. (A pre-compiled version of d8 and its dependencies are included in the bin/ directory). If the exploit works succesfully, you'll probably get something like this:

[+] Starting WAMpage...
[+] addrof(myobj) = 0x5a68f5d1
[+] Test: reconstructed myobj: {"foo":"bar"}
[+] Set up arbread32/arbwrite32.
[+] stage2 shellcode loaded @ 0xff458000
[+] myfunc @ 0x5a693369
[+] stage1 RWX buf @ 0x5bb8f280
[+] Copied stage1 shellcode. Calling...
Traceback (most recent call last):
  File "<stdin>", line 25, in <module>
IOError: [Errno 13] Permission denied: '/dev/mem'

The permission error is expected, assuming your machine isn't totally misconfigured.

You can test the devmemes.py exploit by running it directly on a TV, but you'll either need root to begin with, or some other kind of unsandboxed/unjailed shell.

Installation on TV

You can use ares-install, or manually copy over the IPK and run this from the devmode shell:

luna-send-pub -i 'luna://com.webos.appInstallService/dev/install' '{"id":"tv.rootmy.wampage","ipkUrl":"/path/to/wampage.ipk","subscribe":true}'

Running on TV

Launch the app and press the "Start Exploit" button. If all goes well, a telnet server should open up on port 31337.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    732
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    405
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    342
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    261
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259

Explore all tools

Browse our collection of tools

View all tools →




