
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
296 results
pythem preview

pythem

GitHubm4n3dw0lf/pythem

pentest framework

exploitationfuzzingnetwork-mapping+5
1.2k7 years ago
sploit preview

sploit

GitHubzznop/sploit

Go package that aids in binary analysis and exploitation

binary-analysisbinary-exploitationctf+6
1815 years ago
Relapse-Exploit preview
Archived

Relapse-Exploit

GitHubntfargo/relapse-exploit

PS5 exploit chain for firmware 7.00-13.60 combining a WebKit JSC info leak and typedarray corruption with an aio_multi_wait UAF race for kernel…
binary-exploitationeducationexploitation+5
1.8k6 days ago
RawrXDA preview

RawrXDA

GitHubitsmehrawrxd/rawrxda

RawrXDA

binary-analysisbinary-exploitationcode-analysis+7
82 months ago
Graffiti preview

Graffiti

GitHubekultek/graffiti

A tool to generate obfuscated one liners to aid in penetration testing

payload-developmentpayload-generationpenetration-testing+1
1807 years ago
EternalBlueC preview

EternalBlueC

GitHubbhassani/eternalbluec

EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…

binary-exploitationeducationexploitation+7
61827 days ago
MSRKit preview

MSRKit

GitHubrurixis/msrkit

A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
binary-exploitationexploitationpayload-development+5
6515 days ago
nasm_linux_x86_64_pure_sharedlib preview

nasm_linux_x86_64_pure_sharedlib

GitHubtherealdreg/nasm_linux_x86_64_pure_sharedlib

NASM Linux x86_64 pure (no deps) shared library (.so), POC for Reflective ELF SO injection
exploitationpayload-developmentpost-exploitation+2
313 years ago
Simple-Polymorphic-Engine-SPE32 preview

Simple-Polymorphic-Engine-SPE32

GitHubpelock/simple-polymorphic-engine-spe32

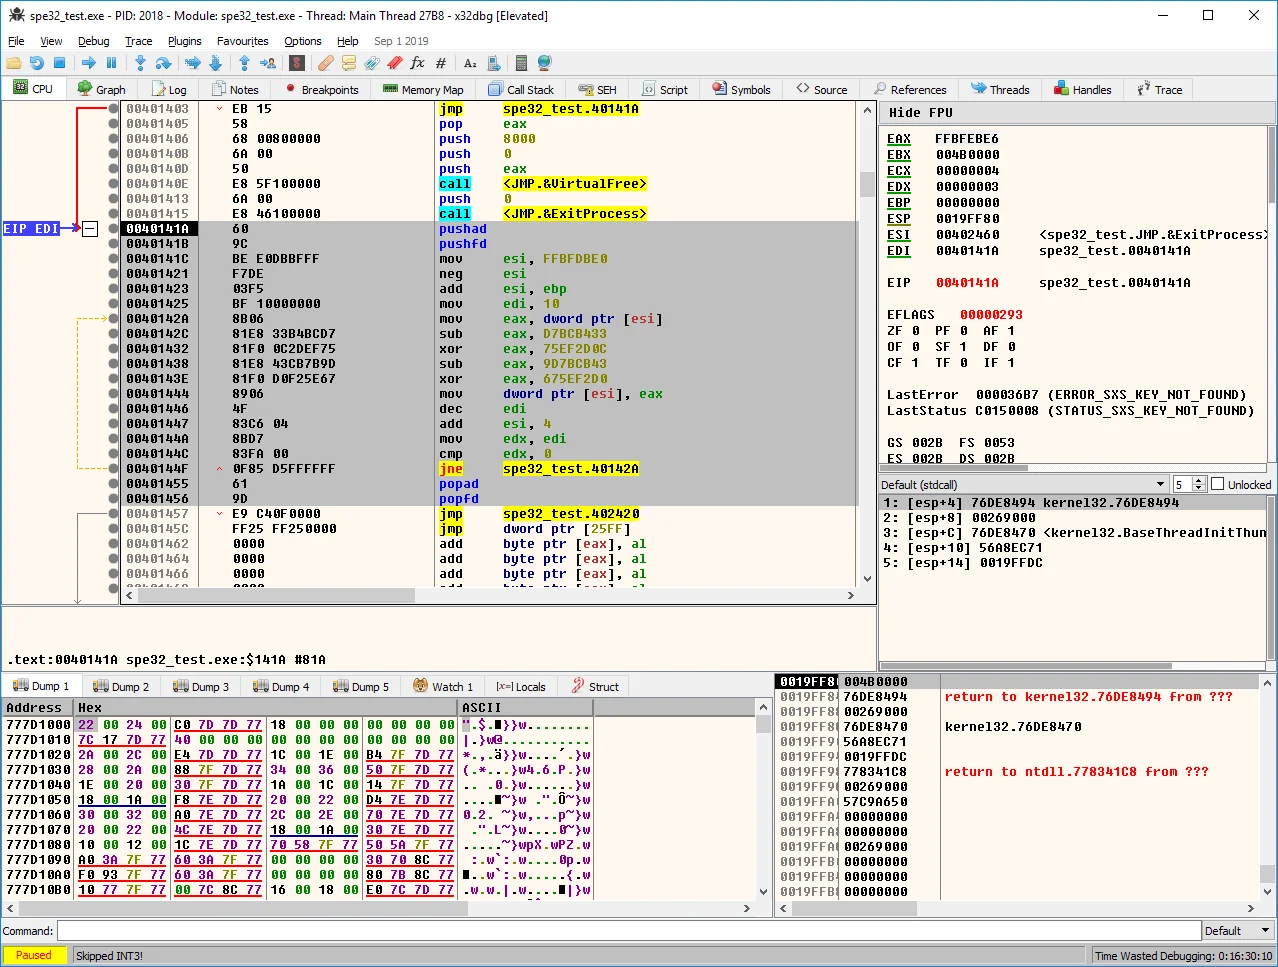
Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written…

encryption-decryption-toolsmalware-analysisreverse-engineering+1
1583 years ago
CVE-2024-50986 preview

CVE-2024-50986

GitHubriftsandroses/cve-2024-50986

An issue in Clementine v.1.3.1 allows a local attacker to execute arbitrary code via a crafted DLL file (DLL Hijacking)

binary-exploitationexploitationpayload-generation+4
1 year ago
NovaLdr preview

NovaLdr

GitHubblacksnufkin/novaldr

Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
code-analysiseducationexploitation+7
2642 years ago
ShellCodeEmulator preview

ShellCodeEmulator

GitHubohjeongwook/shellcodeemulator

Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
binary-analysisdynamic-analysis-sandboxingmalware-analysis+3
1276 years ago
XenoboxX preview

XenoboxX

GitHubcecio/xenoboxx

Hardware Sandbox Toolkit

dynamic-analysis-sandboxingforensicshardware-security+4
62 years ago
SleepyCrypt preview

SleepyCrypt

GitHubsolomonsklash/sleepycrypt

A shellcode function to encrypt a running process image when sleeping.

ids-ips-evasionpayload-developmentred-teaming+1
3375 years ago
meterssh preview

meterssh

GitHubtrustedsec/meterssh

MeterSSH is a way to take shellcode, inject it into memory then tunnel whatever port you want to over SSH to mask any type of communications as a…

command-and-controlexploitationpayload-development+4
5309 years ago
TeamsImplant preview

TeamsImplant

GitHuballevon412/teamsimplant

Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…
command-and-controlexploit-frameworkspayload-development+5
2074 years ago
SdoKeyCrypt-sys-local-privilege-elevation preview

SdoKeyCrypt-sys-local-privilege-elevation

GitHubhypersine/sdokeycrypt-sys-local-privilege-elevation

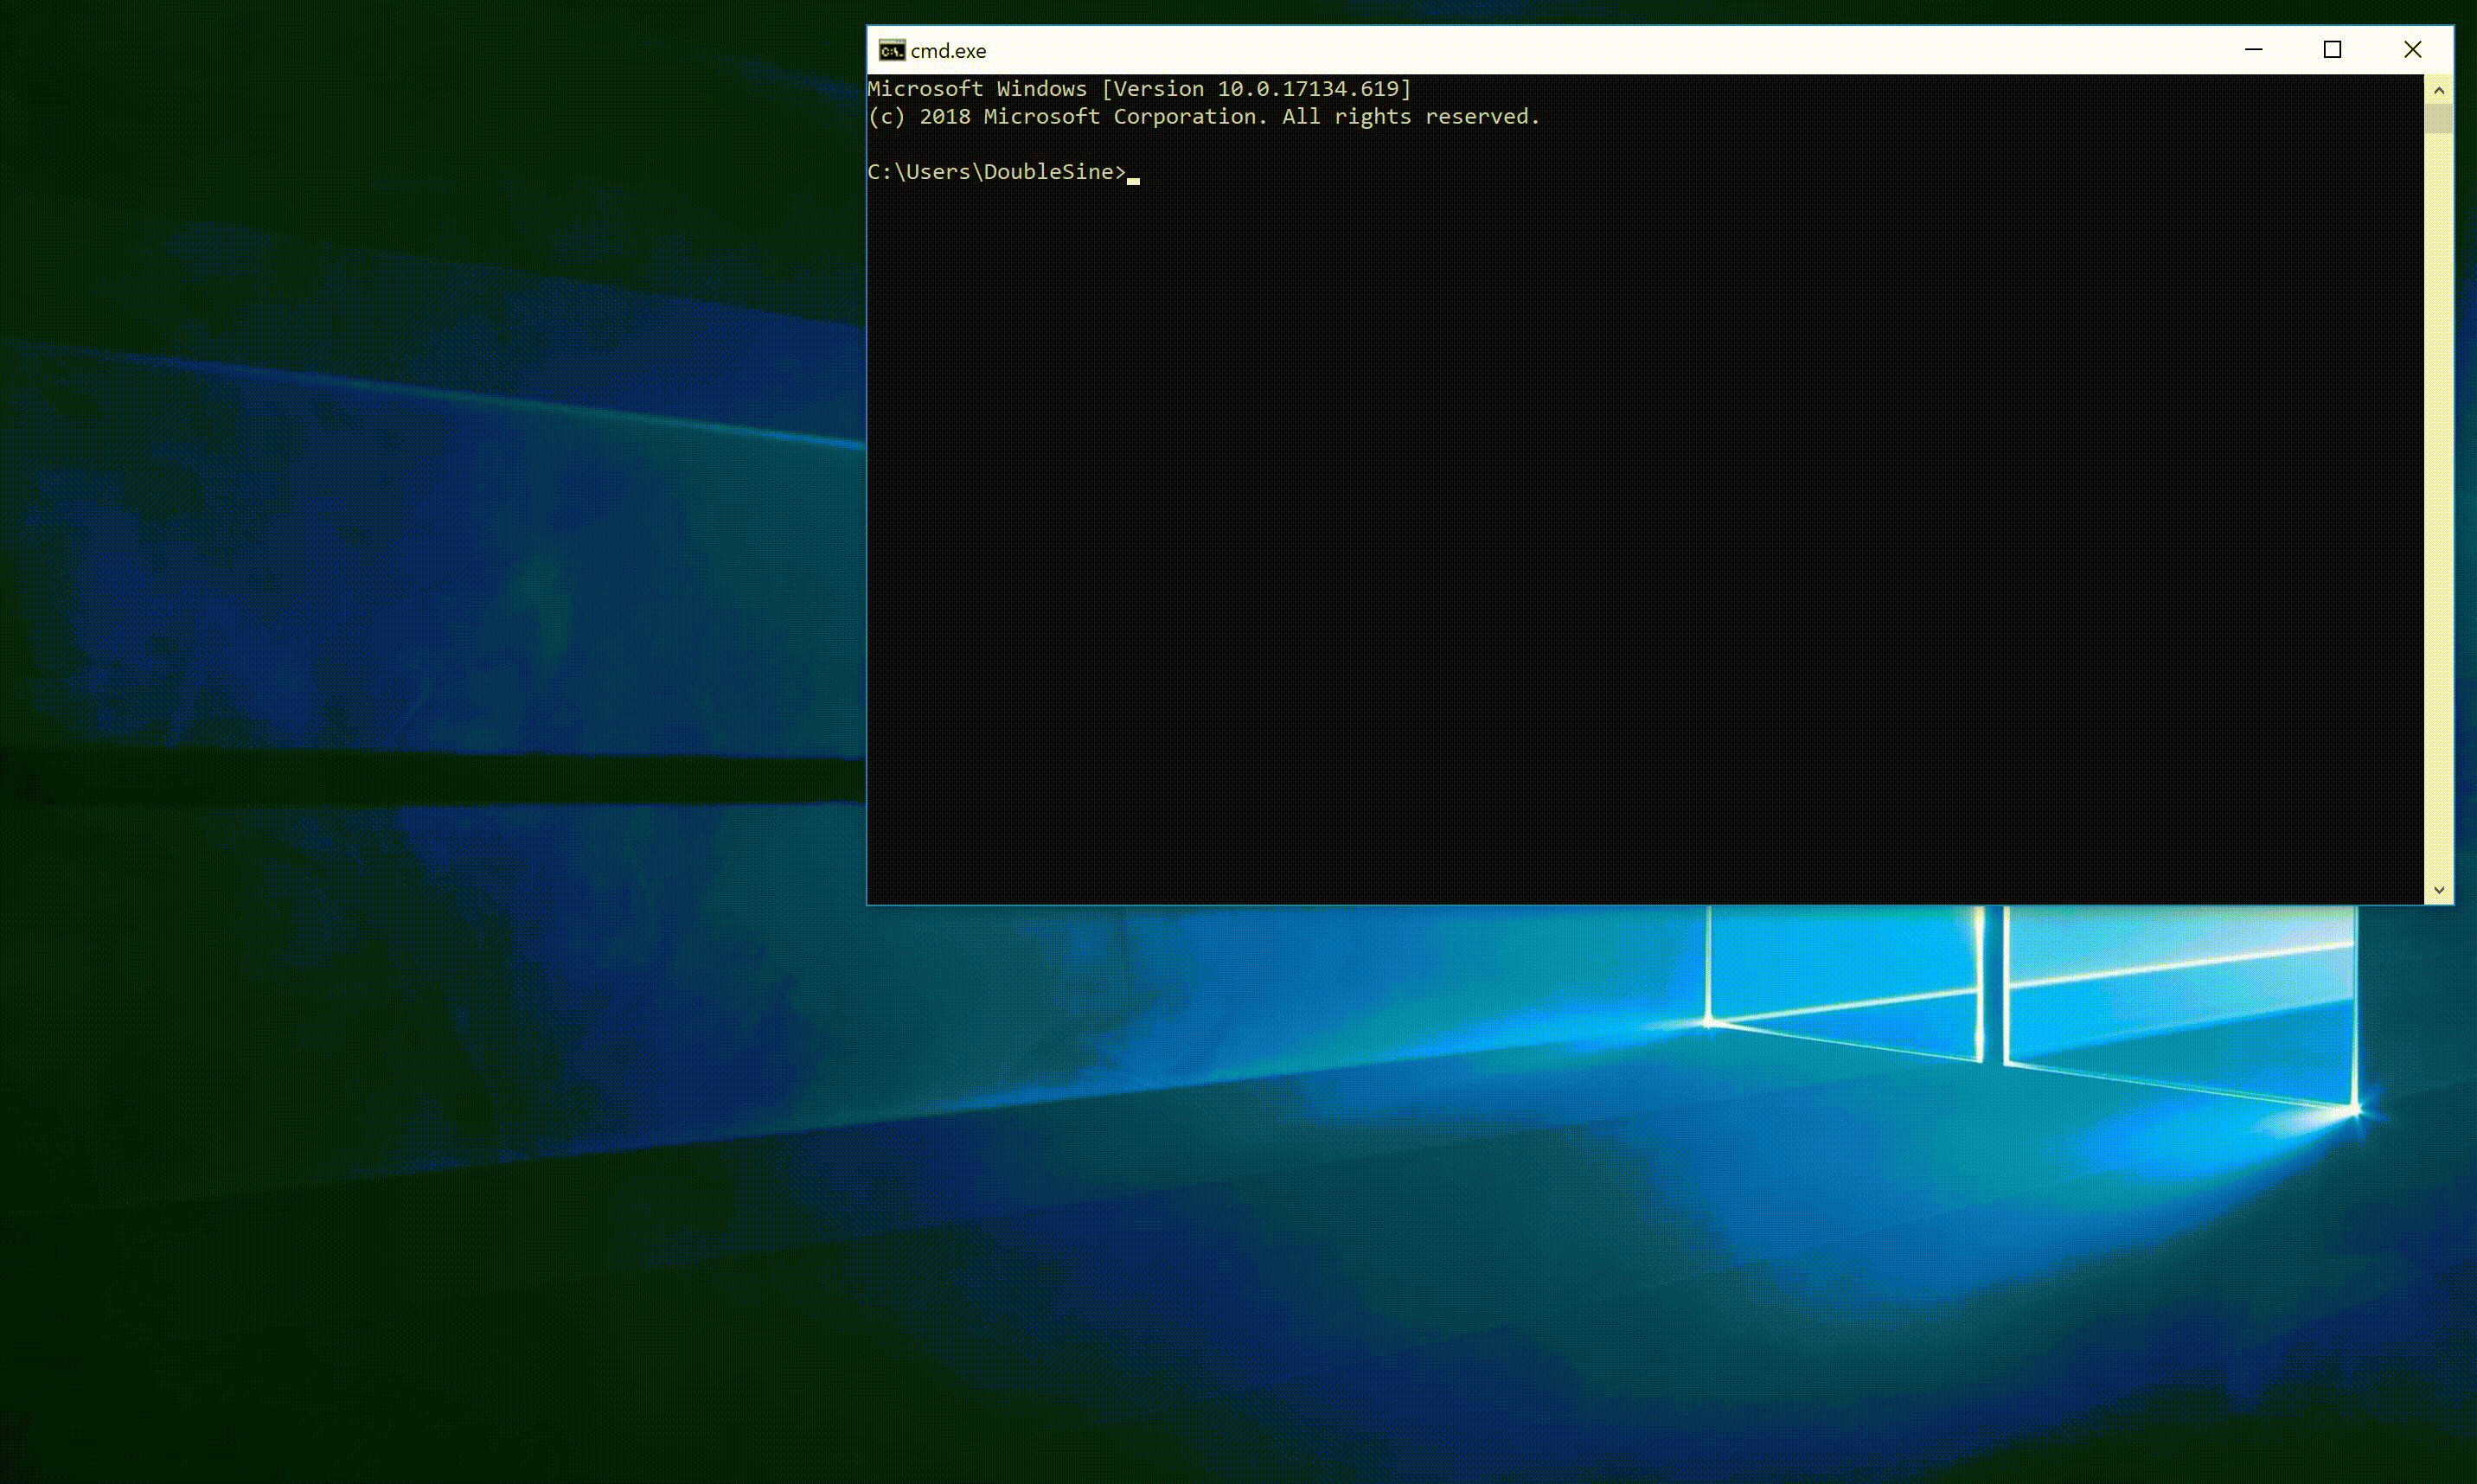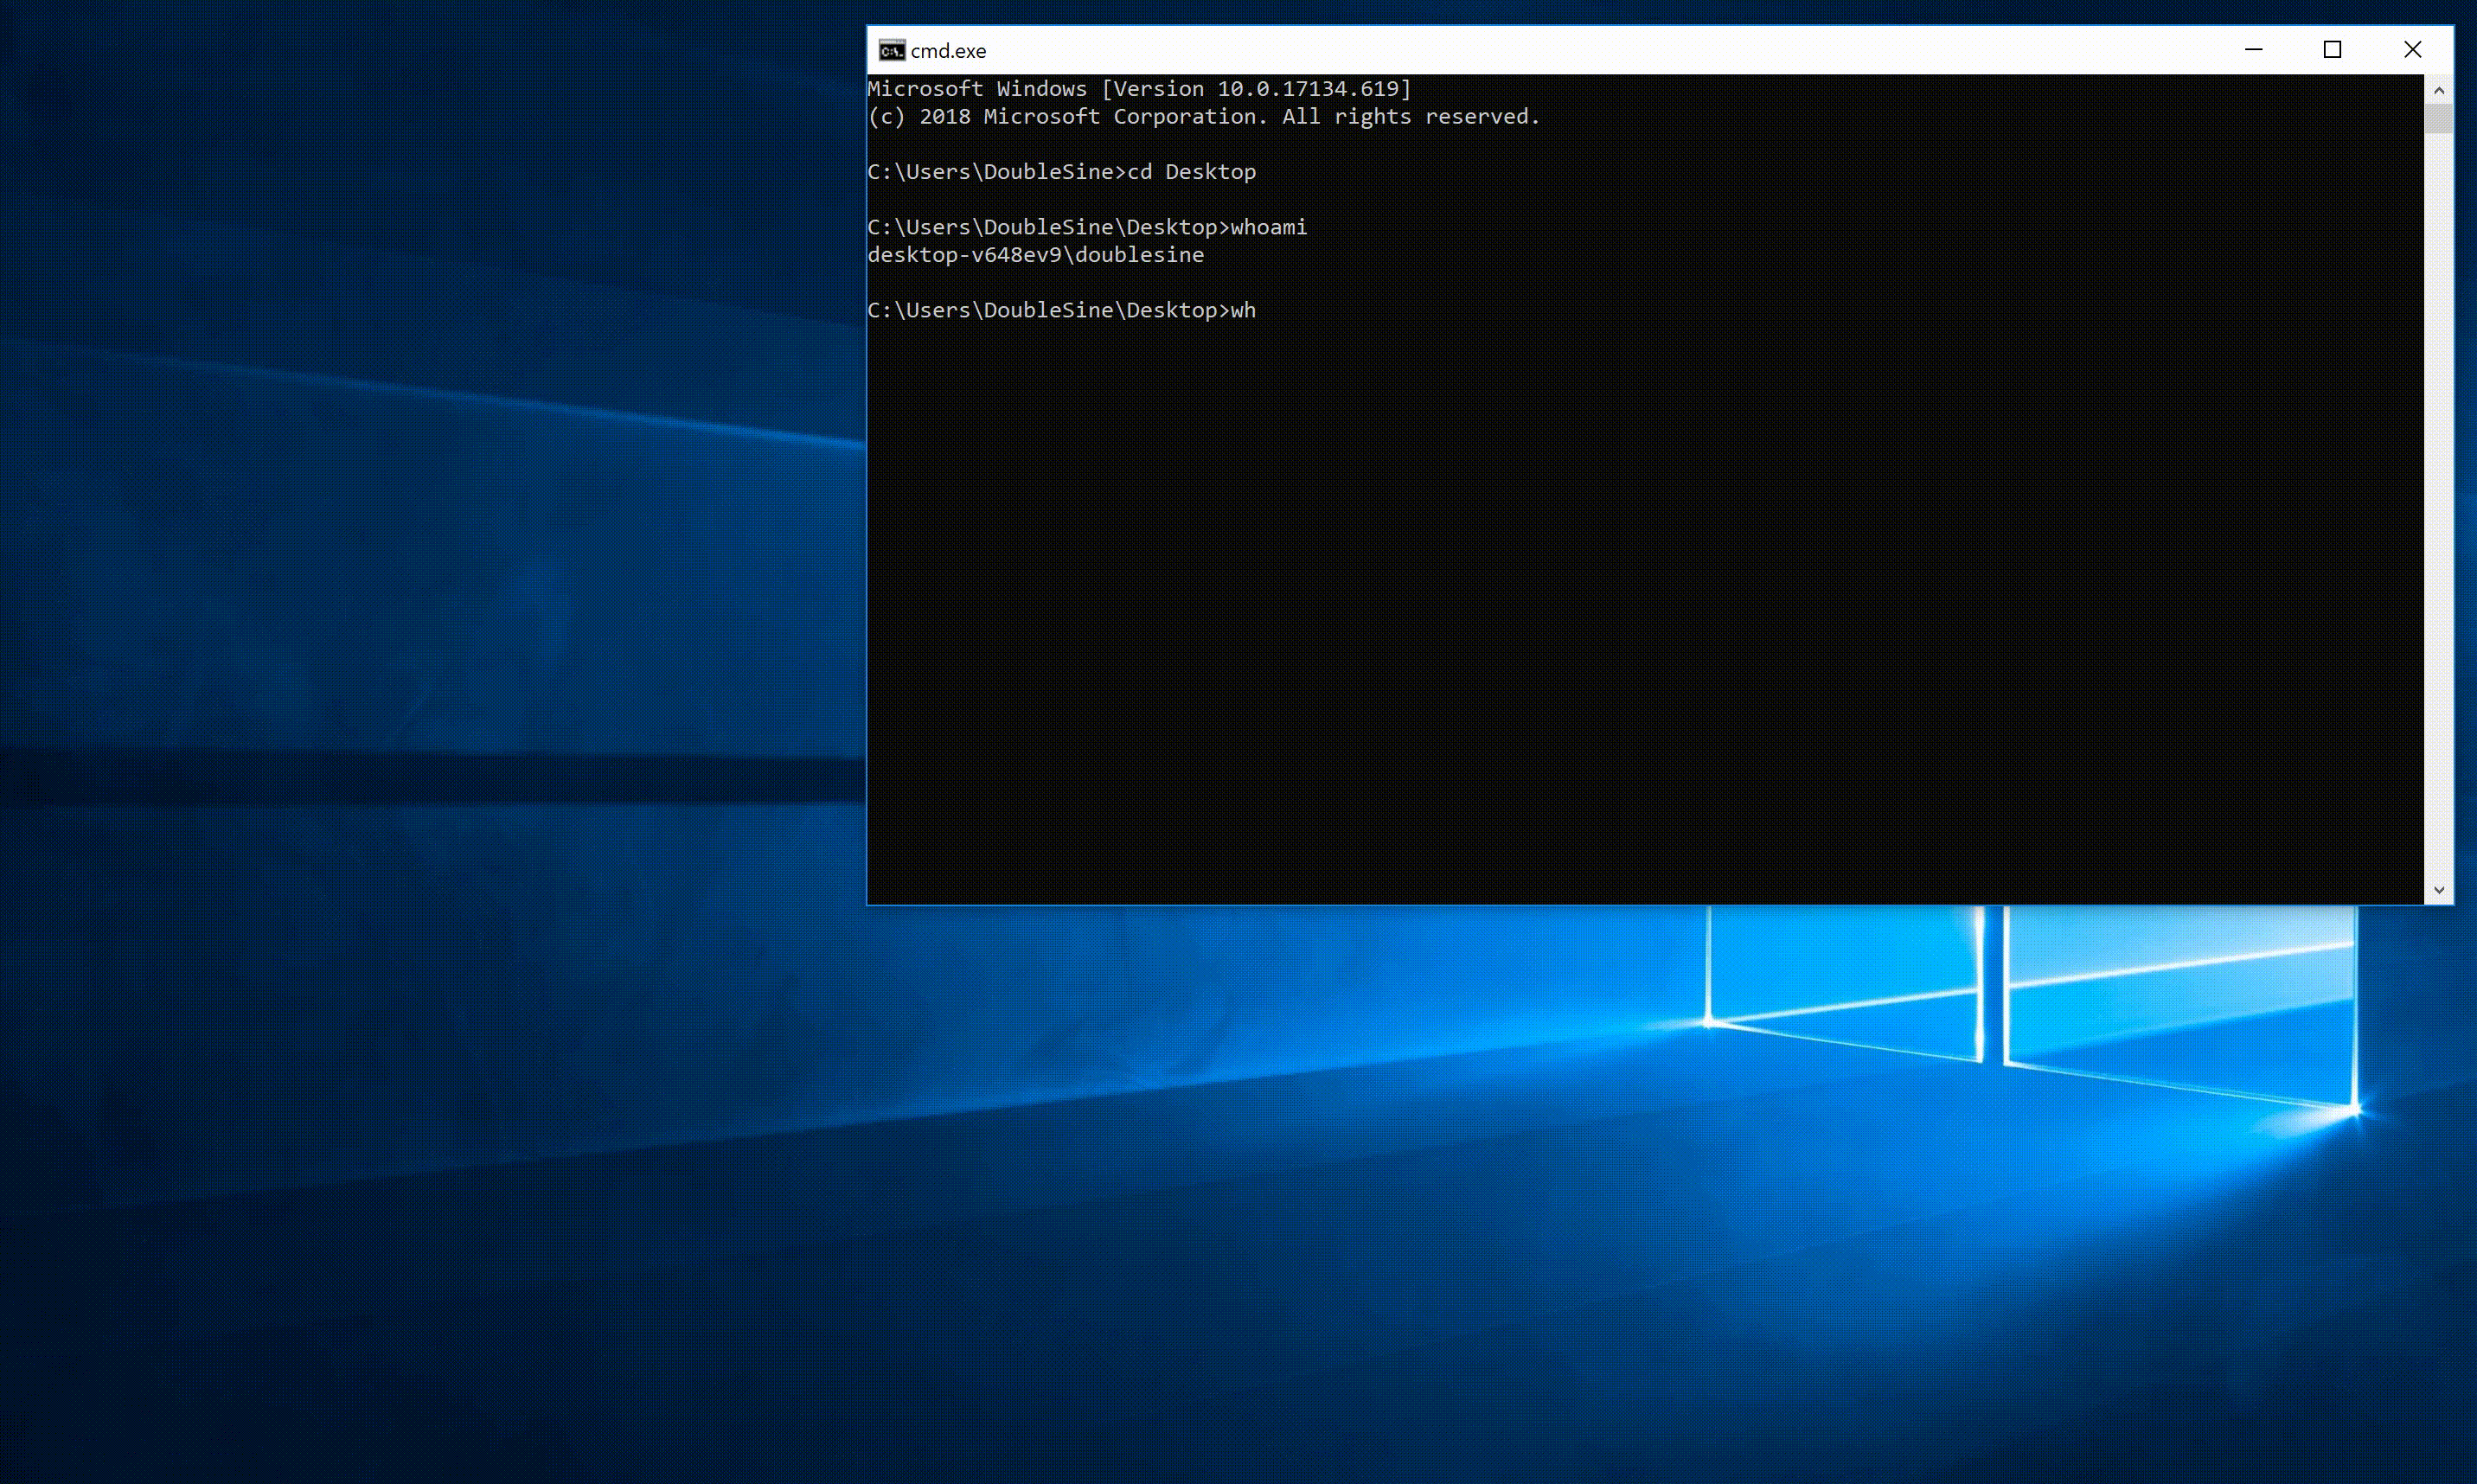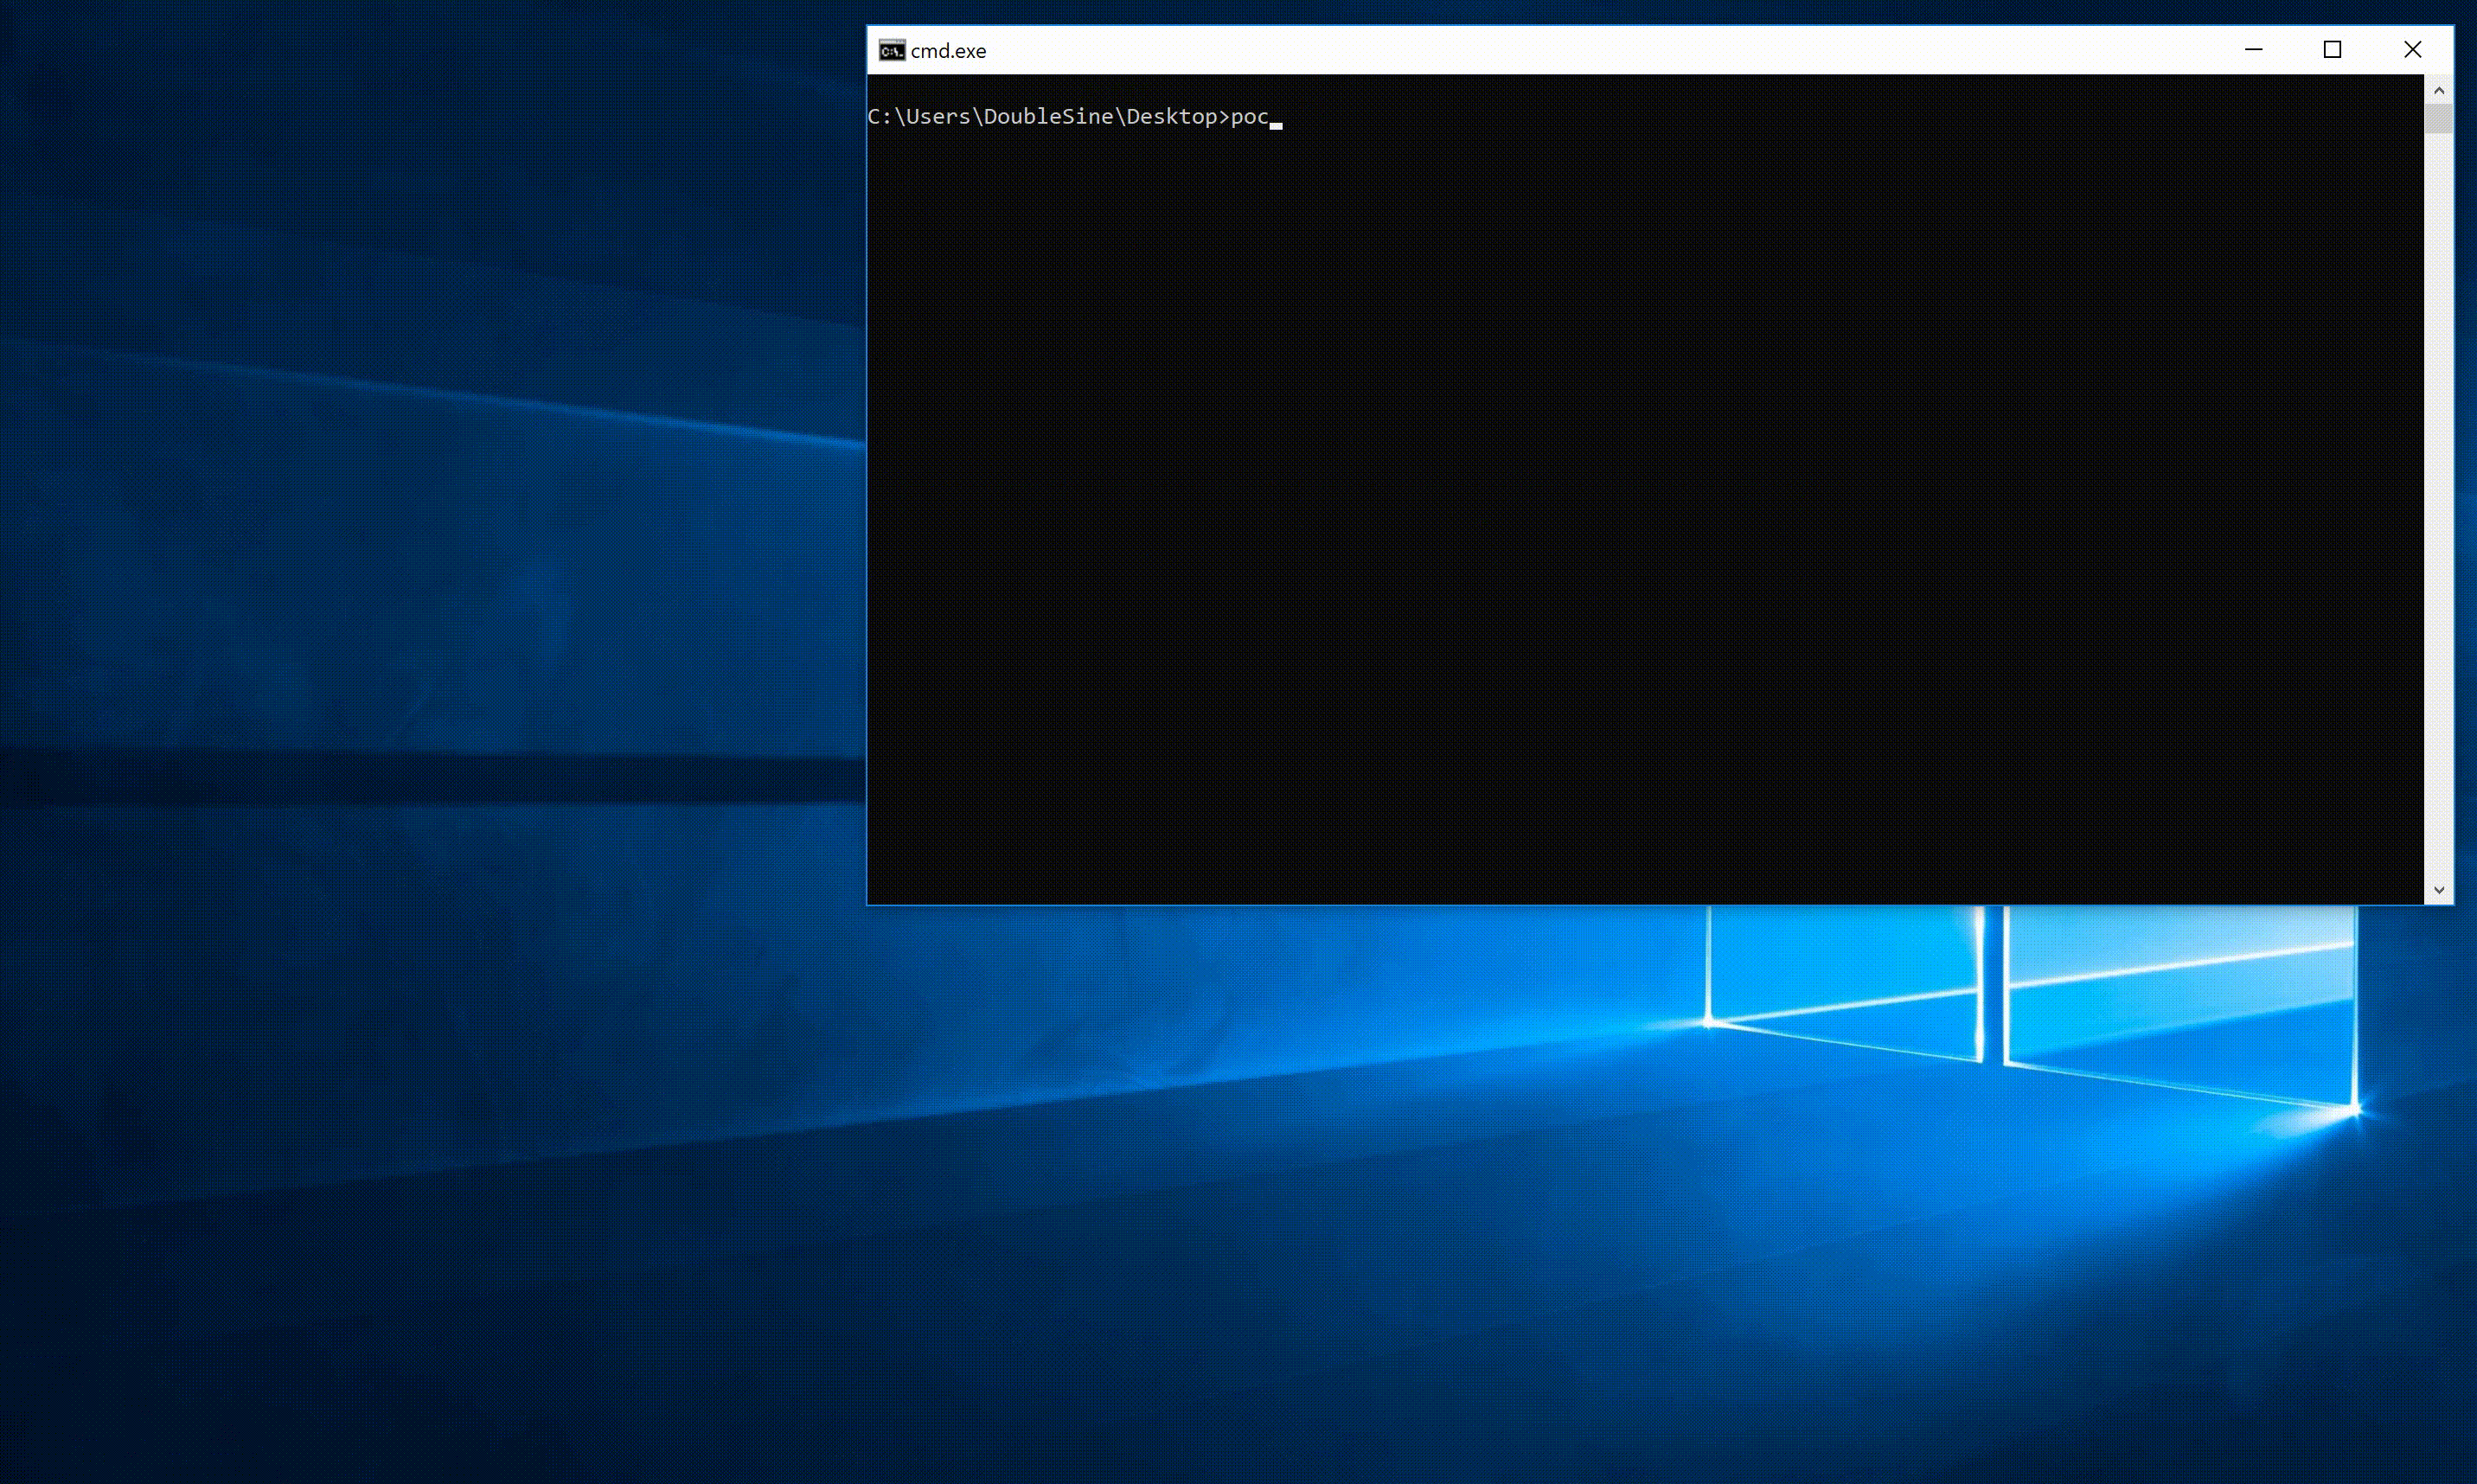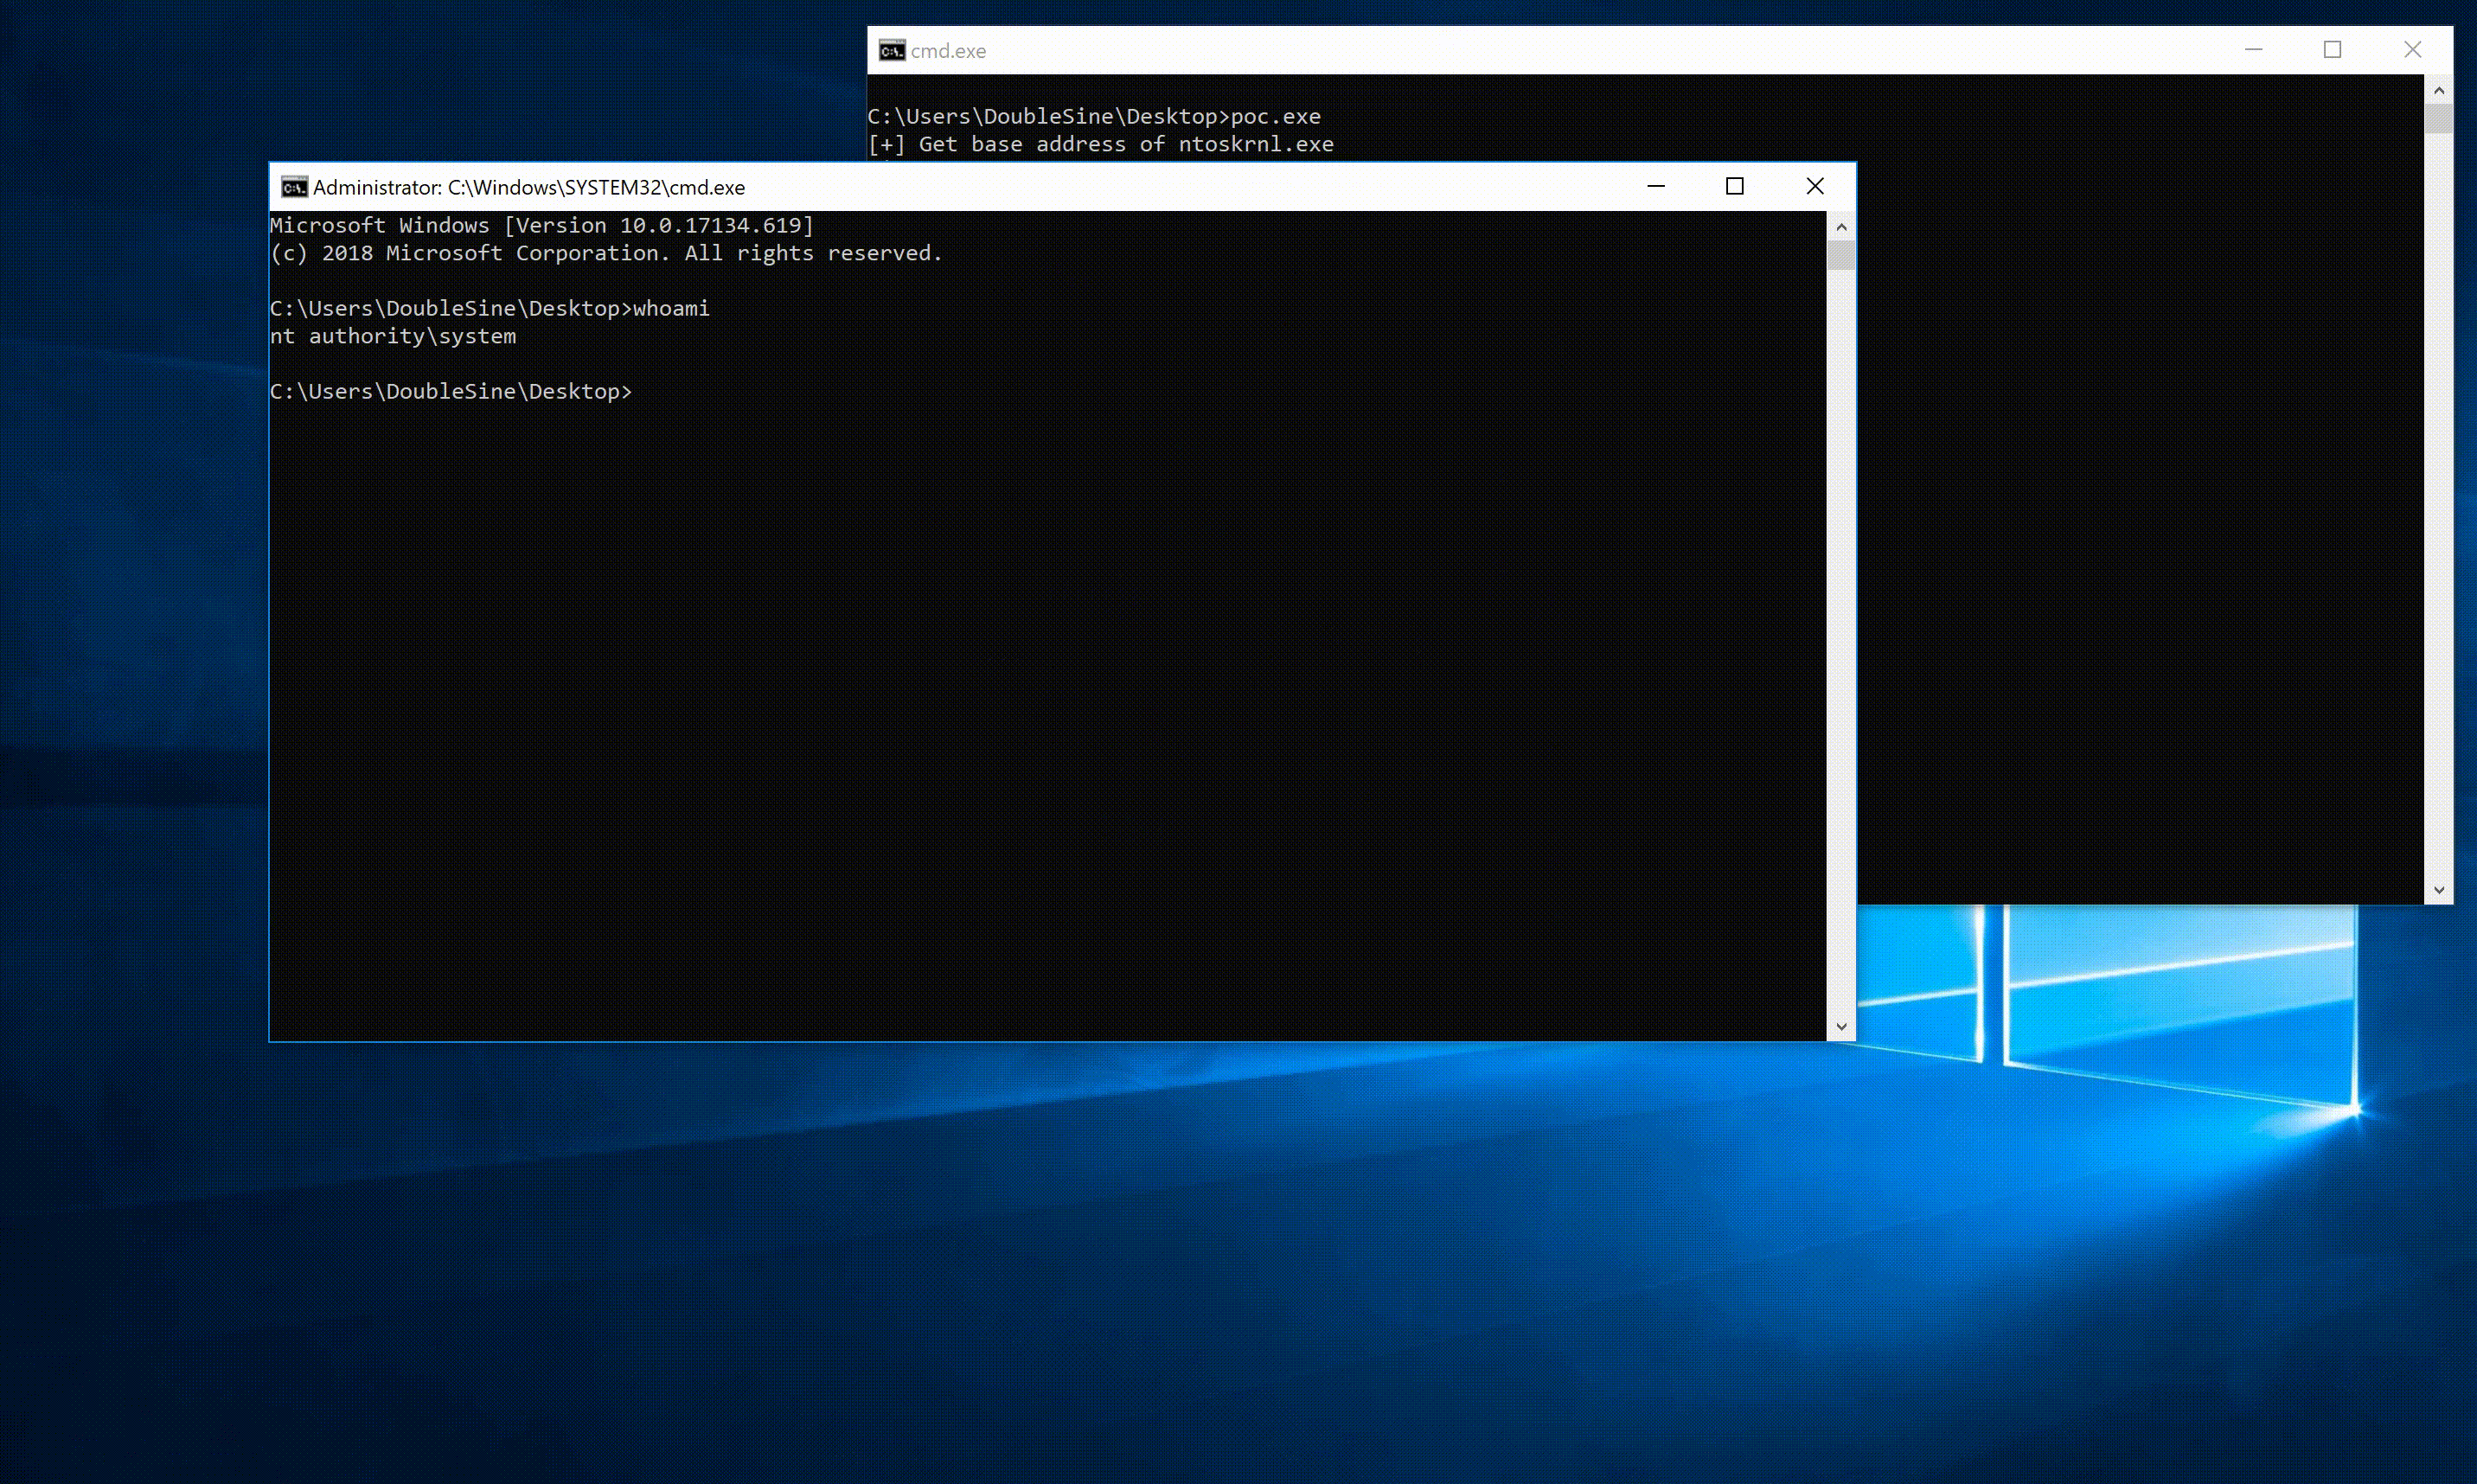
CVE-2019-9729. Transferred from https://github.com/DoubleLabyrinth/SdoKeyCrypt-sys-local-privilege-elevation
binary-exploitationexploitationprivilege-escalation+2
847 years ago
staged-DLL-Injection-SMB- preview

staged-DLL-Injection-SMB-

GitHubkasturixbm5/staged-dll-injection-smb-

Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).

educationexploitationlabs-practice+5
424 months ago
Previous12…17Next