
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
125 results
KDU preview

KDU

GitHubhfiref0x/kdu

Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…

binary-exploitationdefensive-toolsexploitation+8
2.8k
1 month ago
metasploit-framework preview

metasploit-framework

GitHubrapid7/metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

command-and-controldatabase-securitydata-exfiltration+20
38.8k14h 29m ago
TinyLoad preview

TinyLoad

GitHubiamsopotatoe-coder/tinyload

Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.

binary-analysisencryption-decryption-toolsexploitation+5
1802 months ago
FUD-C2-Framework preview

FUD-C2-Framework

GitHubx3r0day/fud-c2-framework

A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.

command-and-controlencryption-decryption-toolsids-ips-evasion+9
85 months ago
CVE-2024-31317-PoC-Deployer preview

CVE-2024-31317-PoC-Deployer

GitHubwebldix/cve-2024-31317-poc-deployer

Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.

android-securitybinary-exploitationexploitation+5
521 year ago
SysWhispers3 preview

SysWhispers3

GitHubklezvirus/syswhispers3

SysWhispers on Steroids - AV/EDR evasion via direct system calls.
defensive-toolsexploitationids-ips-evasion+5
1.6k2 years ago
Hollow preview

Hollow

GitHubchaelsoo/hollow

A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
binary-exploitationencryption-decryption-toolsexploitation+7
994 months ago
MSRKit preview

MSRKit

GitHubrurixis/msrkit

A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
binary-exploitationexploitationpayload-development+5
681 month ago
Graffiti preview

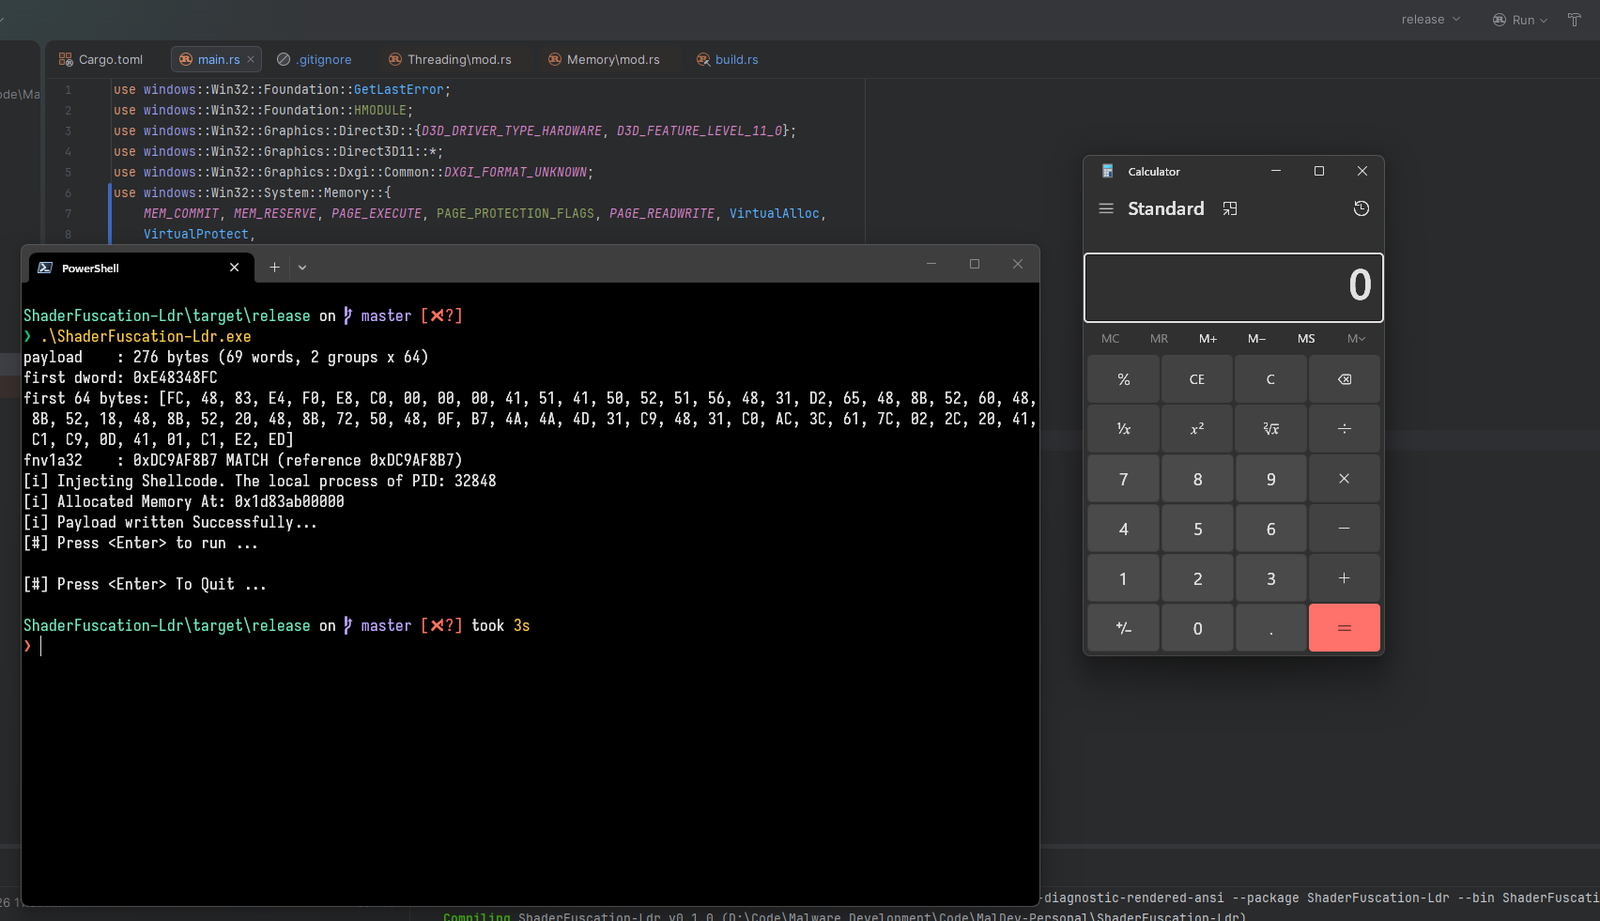
Graffiti

GitHubekultek/graffiti

A tool to generate obfuscated one liners to aid in penetration testing
payload-developmentpayload-generationpenetration-testing+1
1807 years ago
polychrome-rs preview

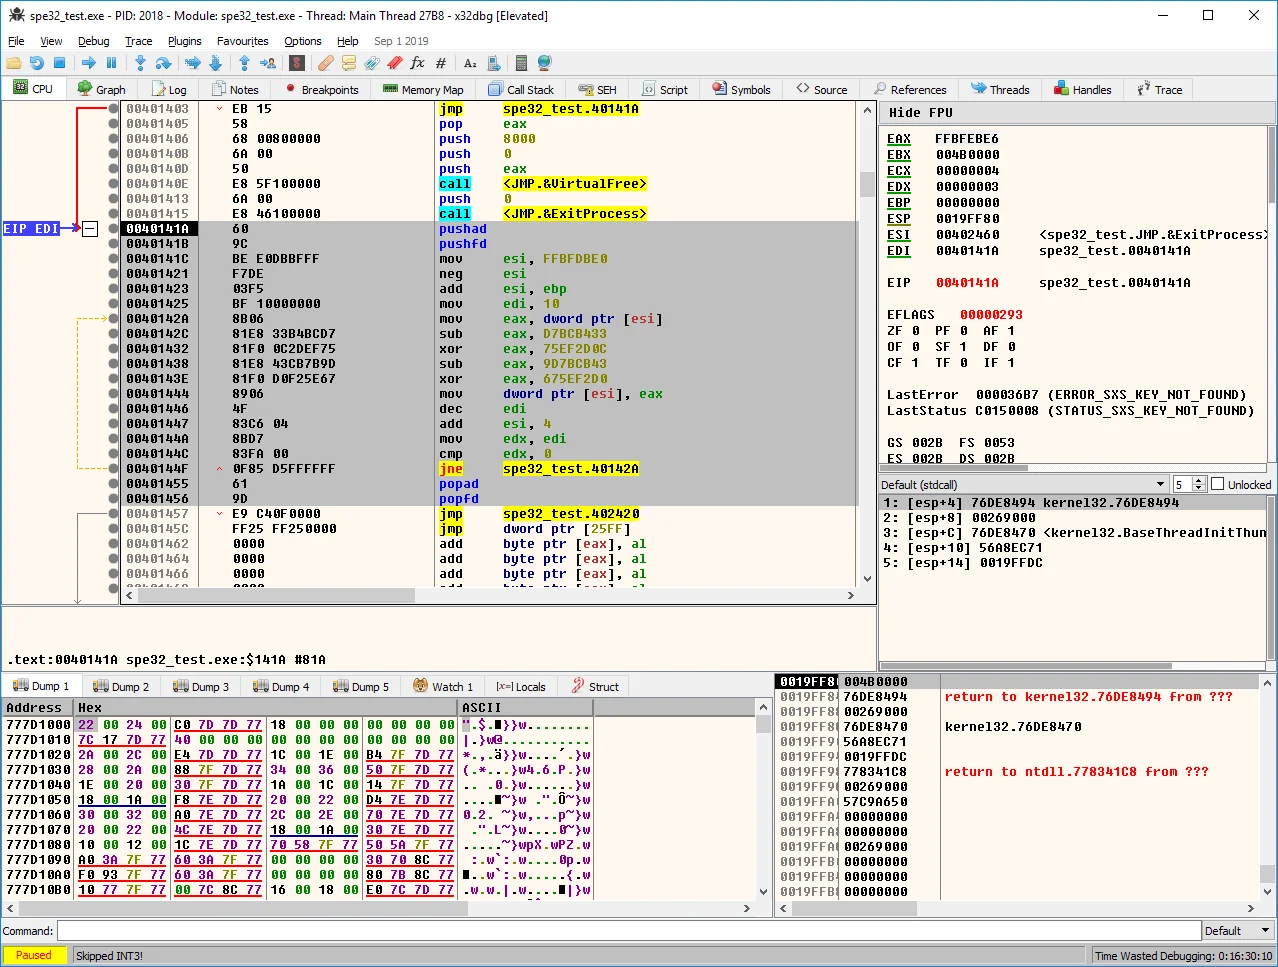
polychrome-rs

GitHubdovelus/polychrome-rs

A PoC on how to use a Compute Shader as Payload
defensive-toolsencryption-decryption-toolsexploitation+5
91 month ago
Simple-Polymorphic-Engine-SPE32 preview

Simple-Polymorphic-Engine-SPE32

GitHubpelock/simple-polymorphic-engine-spe32

Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written…

encryption-decryption-toolsmalware-analysisreverse-engineering+1
1613 years ago
LazZzy_Dump preview

LazZzy_Dump

GitHubtrustedsec/lazzzy_dump

Statically extracts and decrypts AES-CBC/XOR-obfuscated shellcode from laZzzy-wrapped PE binaries via signature matching and RIP-relative address…

binary-analysiscode-analysisdigital-forensics+6
11 month ago
BadAssMacros preview

BadAssMacros

GitHubinf0secrabbit/badassmacros

C# tool that generates malicious VBA macros with shellcode injection, VBA purging, and sandbox detection for red team operations.
exploit-frameworkspayload-generationred-teaming+1
4445 years ago
NimSyscallPacker preview

NimSyscallPacker

GitHubs3cur3th1ssh1t/nimsyscallpacker

Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…

binary-exploitationexploitationlateral-movement+7
2071 month ago
PythonAESObfuscate preview

PythonAESObfuscate

GitHuboffsecginger/pythonaesobfuscate

Obfuscates a Python Script and the accompanying Shellcode.
encryption-decryption-toolspayload-generationshellcode
556 years ago
hackEmbedded preview

hackEmbedded

GitHubdoudoudedi/hackembedded

This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
command-and-controlembedded-systems-securityencryption-decryption-tools+8
2073 months ago
Armor preview

Armor

GitHubtokyoneon/armor

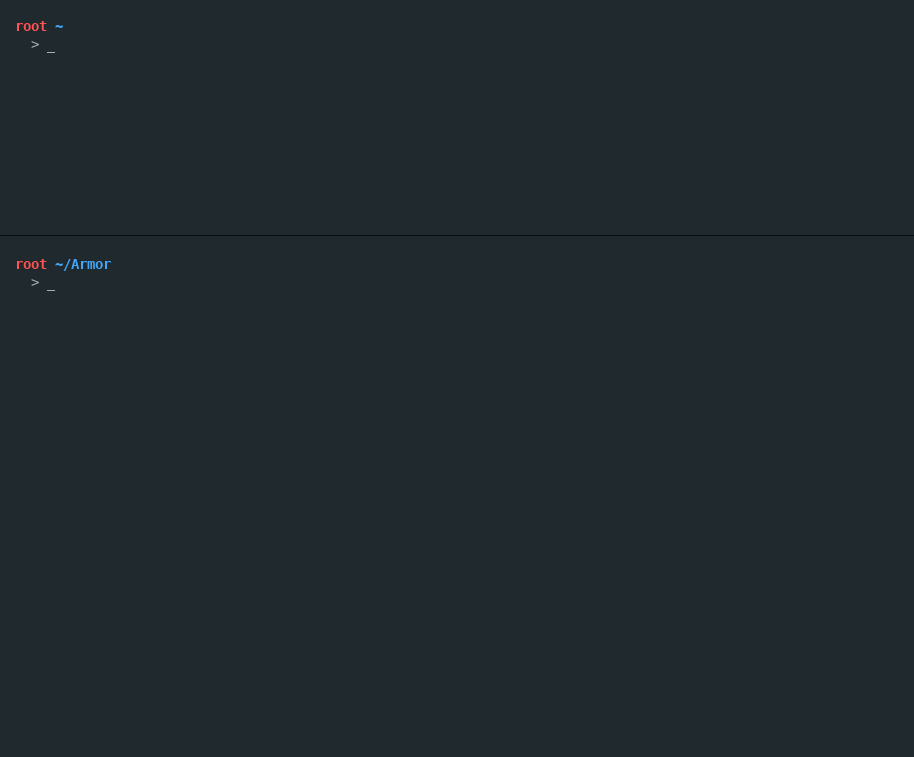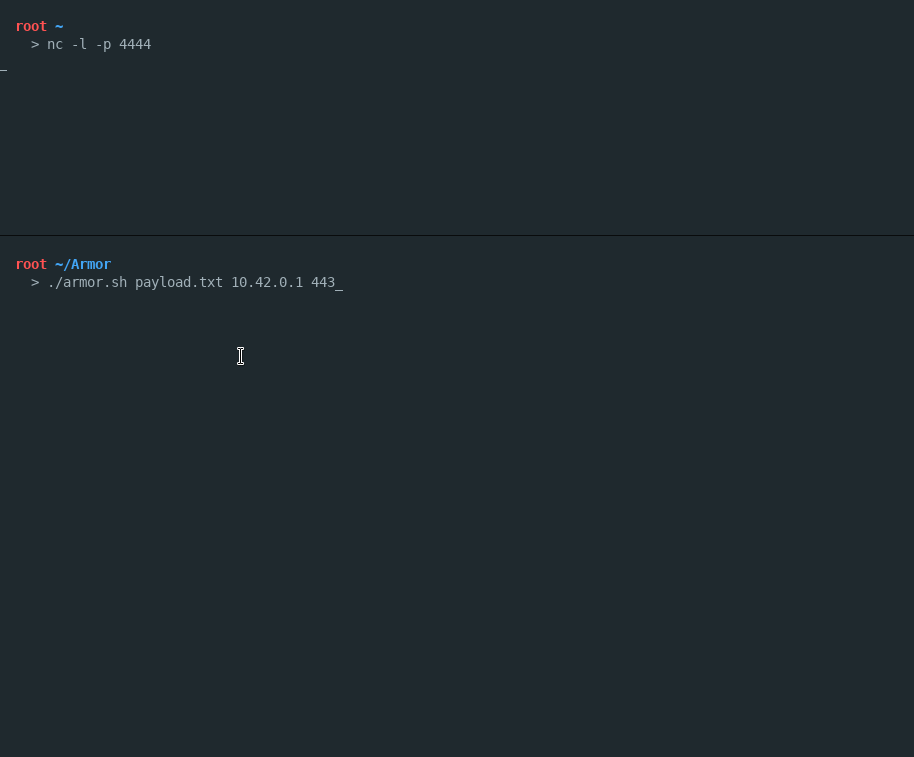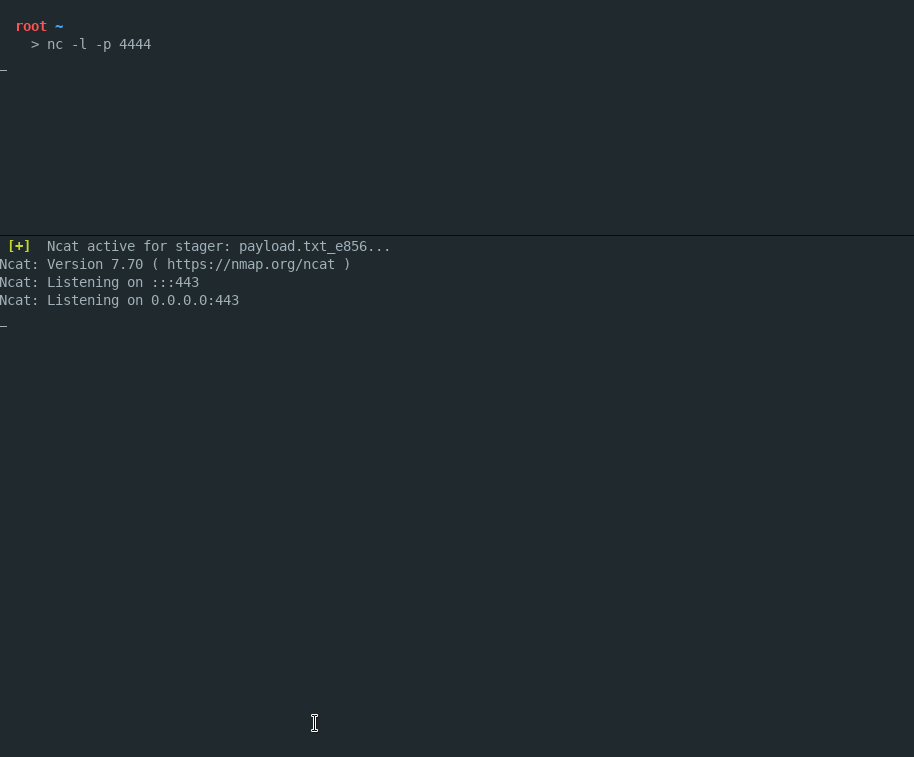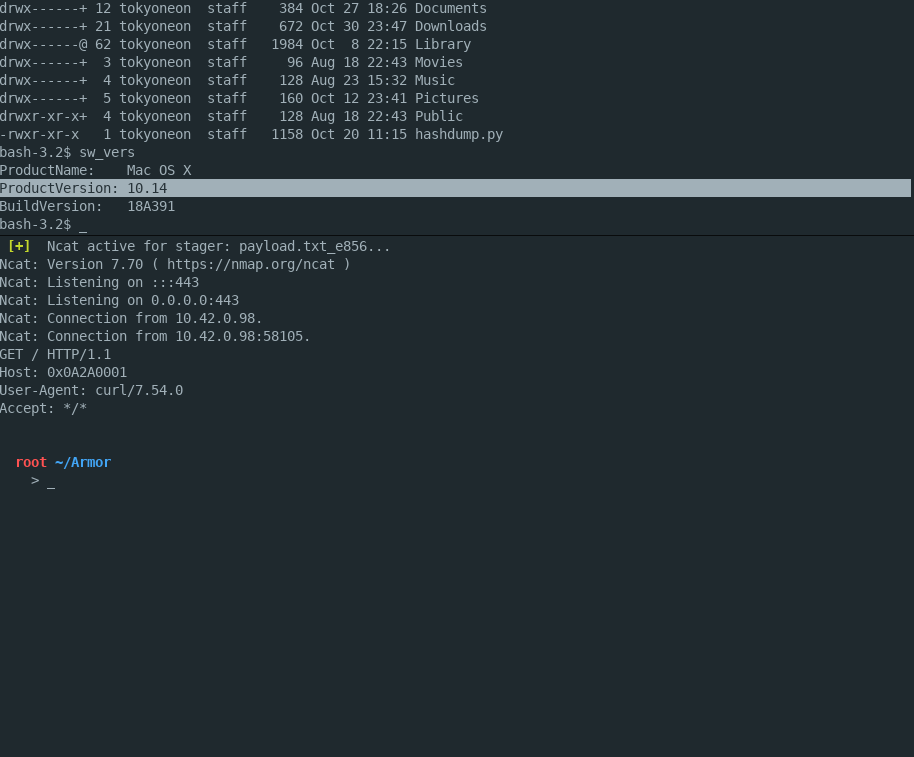
Armor is a simple Bash script designed to create encrypted macOS payloads capable of evading antivirus scanners.
encryption-decryption-toolspayload-developmentpayload-generation+3
2777 years ago
BadOutlook preview

BadOutlook

GitHubaahmad097/badoutlook

Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…

command-and-controlemail-securityexploitation+3
1375 years ago
Previous1234567Next