

pacu
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
cloud-infrastructure-securitycloud-securitydata-exfiltration+7
5.4k
rhinosecuritylabs/pacuThe AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
 bishopfox/cloudfox
Automating situational awareness for cloud penetration tests.
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 rhinosecuritylabs/cloudgoat
CloudGoat is Rhino Security Labs' "Vulnerable by Design" AWS deployment tool
 iknowjason/awesome-cloudsec-labs
Awesome free cloud native security learning labs. Includes CTF, self-hosted workshops, guided vulnerability labs, and research labs.
 fyoorer/shadowclone
Serverless task distribution framework that parallelizes CLI tools across thousands of cloud functions for rapid reconnaissance and data processing.
 airbnb/binaryalert
BinaryAlert: Serverless, Real-time & Retroactive Malware Detection.
 owasp/dvsa
a Damn Vulnerable Serverless Application
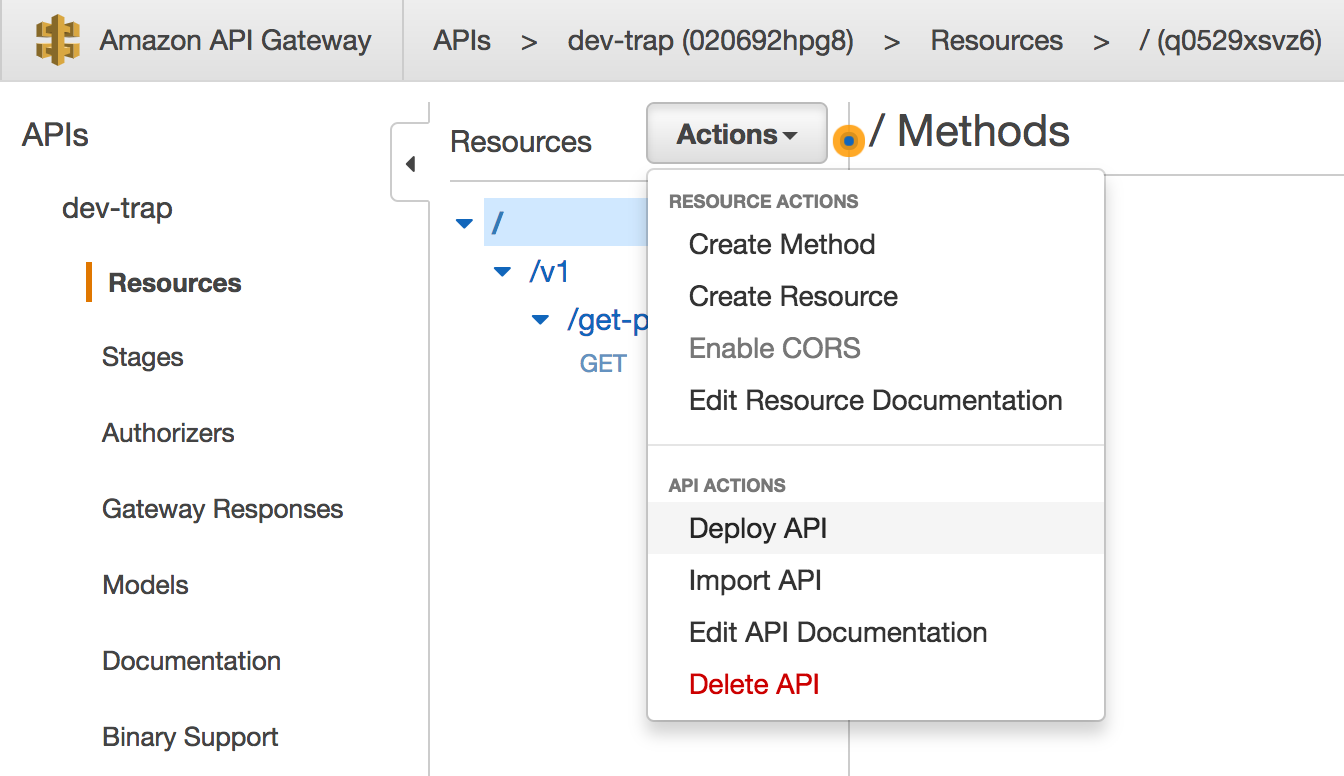 0x4d31/honeylambda
honeyλ - a simple, serverless application designed to create and monitor fake HTTP endpoints (i.e. URL honeytokens) automatically, on top of AWS…
 pumasecurity/serverless-prey
Serverless Functions for establishing Reverse Shells to Lambda, Azure Functions, and Google Cloud Functions
 capsulerun/capsule
Secure runtime to sandbox AI agent tasks. Run untrusted code in isolated WebAssembly environments.
 owasp/serverless-goat
OWASP ServerlessGoat: a serverless application demonstrating common serverless security flaws
 owasp/serverless-top-10-project
OWASP Serverless Top 10
 we45/dvfaas-damn-vulnerable-functions-as-a-service
Intentionally Vulnerable Serverless Functions to understand the specifics of Serverless Security Vulnerabilities
 jonrau1/syntheticsun
Serverless AWS security automation framework that ingests threat intelligence, applies ML-based anomaly detection (RCF, IP Insights), and enriches…
 rbidou/pyrasp
Runtime Application Self Protection for Python web servers, serverless functions and MCP servers, detecting attacks, prompt injection and data leaks…
 abraxas/cve-2026-15583
Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…
 uziii2208/cve-2026-86259
OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass