
cloud-custodian
Rules engine for cloud security, cost optimization, and governance, DSL in yaml for policies to query, filter, and take actions on resources

Rules engine for cloud security, cost optimization, and governance, DSL in yaml for policies to query, filter, and take actions on resources

Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Snyk CLI scans and monitors your projects for security vulnerabilities.

Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more

Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.

Secure and fast microVMs for serverless computing.

Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…

Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…

OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass

Docker lab reproducing the FOSSBilling pre-auth RCE chain (CVE-2026-27604 auth bypass + CVE-2026-28496 Twig SSTI) with a Python PoC and patched…

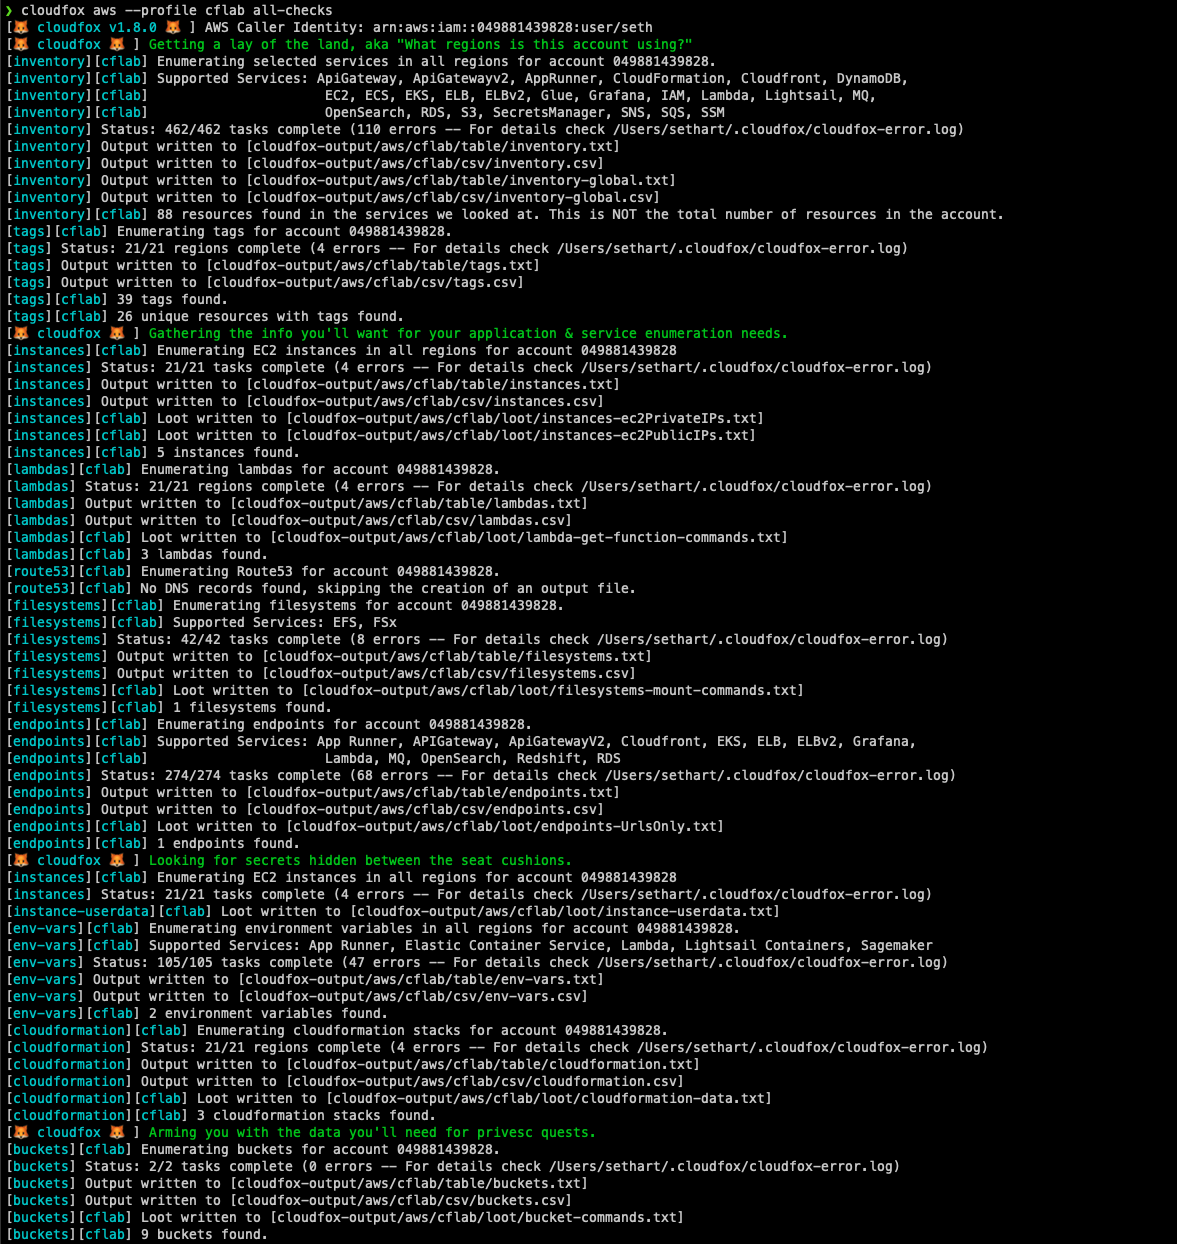
Automating situational awareness for cloud penetration tests.

Simulates CVE-2026-23007 serverless cold-start memory remanence; demonstrates how persistent global state across Lambda invocations can leak secrets…

PoC exploit for CVE-2026-21002 serverless cold-start credential leakage, demonstrating how reused Lambda /tmp directories expose AWS secrets to other…

Proof-of-concept exploit for CVE-2026-9999, demonstrating path traversal in serverless object storage events that overwrites function source code to…

SAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…

Secure runtime to sandbox AI agent tasks. Run untrusted code in isolated WebAssembly environments.

Cursor plugin for Hono v4 (TypeScript edge web framework). 59 LLM regressions with BAD/CORRECT pairs. Pinned to hono ^4.12.19 (>= 4.9.7 for…

The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.