
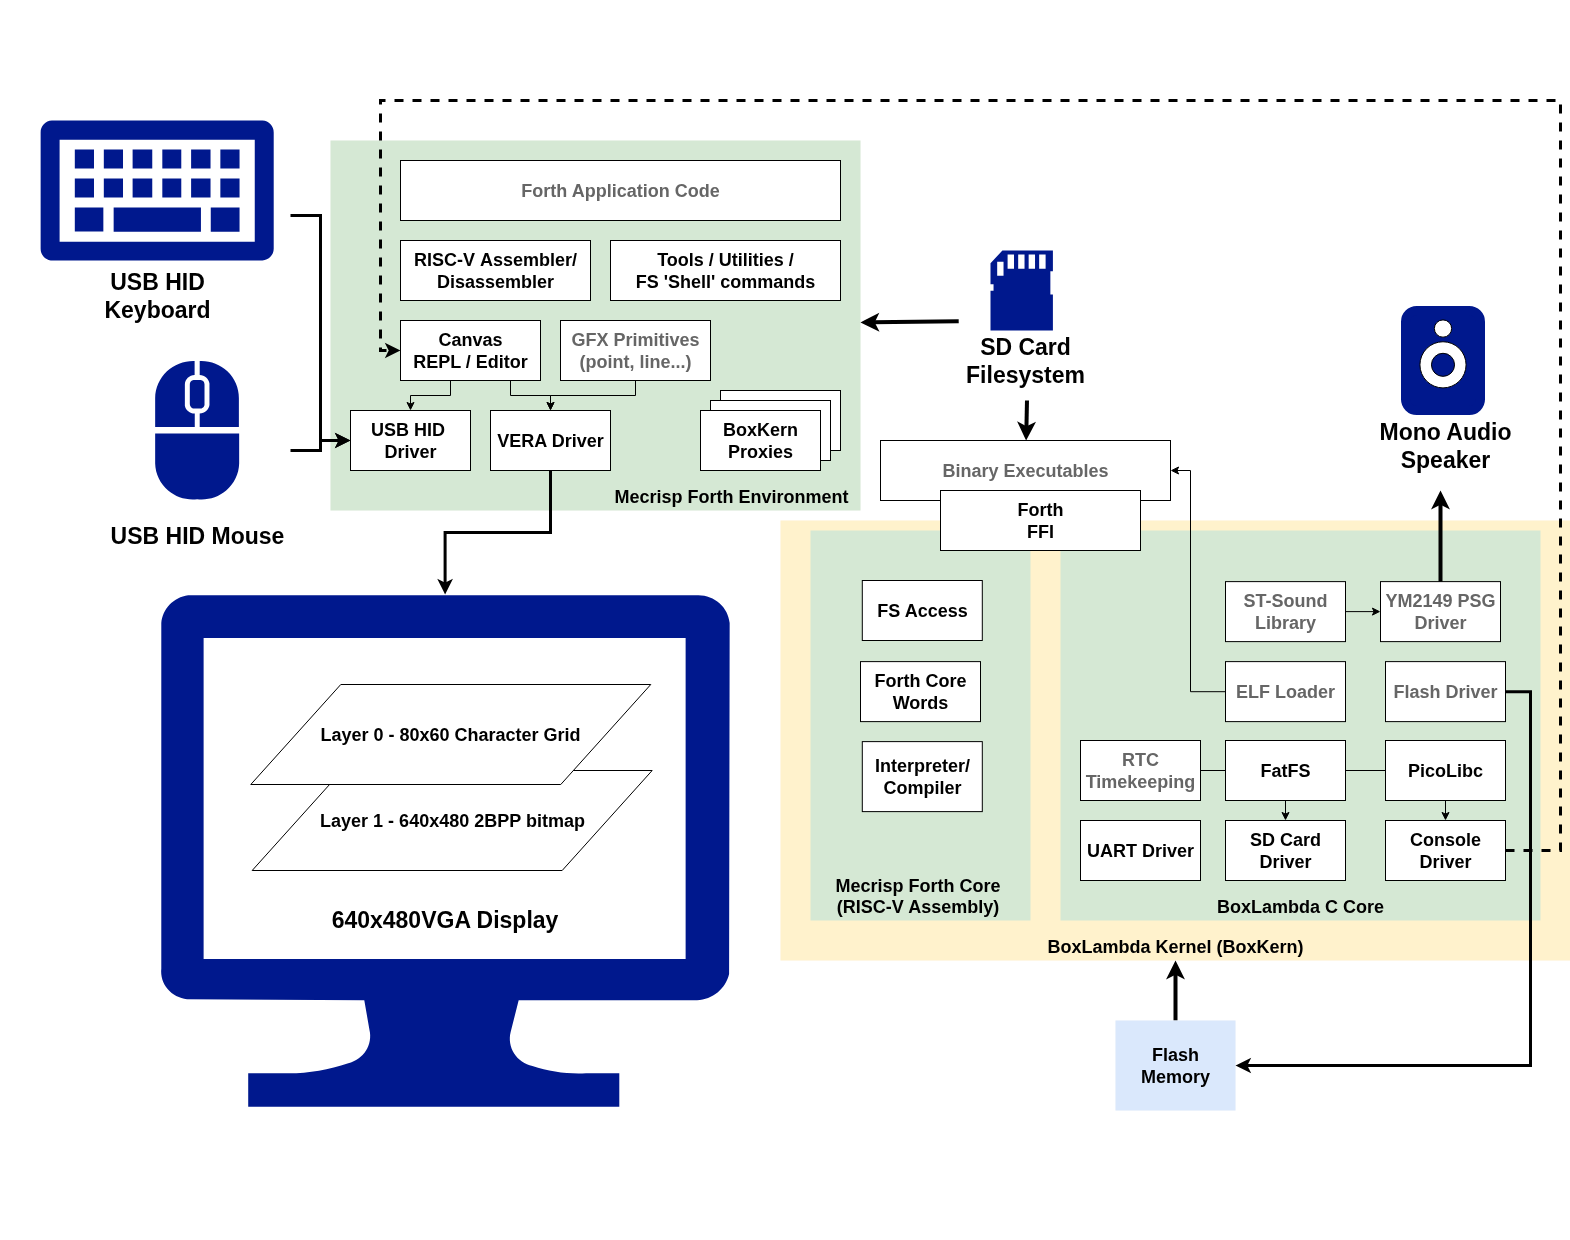
boxlambda
 epsilon537/boxlambda
FPGA based microcomputer sandbox for software and RTL experimentation
debuggerseducationembedded-systems-security+5
epsilon537/boxlambdaFPGA based microcomputer sandbox for software and RTL experimentation
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 mandiant/commando-vm
Customizable Windows-based virtual machine distribution pre-packaged with offensive security tools for penetration testing and red teaming operations.
 rapid7/metasploitable3
Metasploitable3 is a VM that is built from the ground up with a large amount of security vulnerabilities.
 momo5502/sogen
🪅 Windows & Linux userspace emulator
 sinakarvandi/hypervisor-from-scratch
Source code of a multiple series of tutorials about the hypervisor. Available at: https://rayanfam.com/tutorials
 withsecureopensource/see
Sandboxed Execution Environment
 cert-ee/cuckoo3
Open-source automated malware analysis sandbox that runs suspicious files and URLs in isolated VMs and generates detailed behavioral reports.
 intellabs/kafl
A fuzzer for full VM kernel/driver targets
 rex-rs/rex
Rex is a safe and usable kernel extension framework that allows loading and executing Rust kernel extension programs in the place of eBPF.
 awslabs/snapchange
Lightweight fuzzing of a memory snapshot using KVM
 schumilo/vusbf
A QEMU/KVM-based USB fuzzing framework that finds device-driver bugs via reproducible VM execution, multiprocessing, and XML testcase generation.
 google/kernel-research
Linux kernel exploitation toolkit providing an exploit-building library, ROP chain and stack pivot generators, kernel image runners, and a target…
 wkoszek/emuko
RISC-V emulator in Rust that boots Linux with JIT on ARM64/x86_64 and Sv39 virtual memory
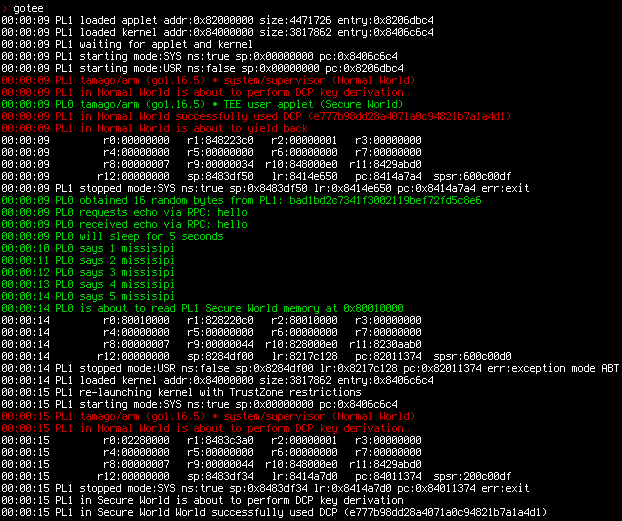 usbarmory/gotee-example
GoTEE - example application
 nishitm/gobox
GO sandbox to run untrusted code
 dovughs/velum-vmm
Windows x64 research hypervisor using Intel VT-x and per-CPU EPT hooks to intercept Nt/Ex/Mm routines, apply request policies, and stream live kernel…