
webvm
 leaningtech/webvm
Client-side Linux virtual machine running in the browser via WebAssembly, with Tailscale networking, Dockerfile-based custom images, and CTF…
cloud-securityctfdevsecops+3
17.4k15 days ago
leaningtech/webvmClient-side Linux virtual machine running in the browser via WebAssembly, with Tailscale networking, Dockerfile-based custom images, and CTF…
 cert-ee/cuckoo3
Open-source automated malware analysis sandbox that runs suspicious files and URLs in isolated VMs and generates detailed behavioral reports.
 harbor-framework/terminal-bench-2
Benchmark for evaluating AI agents on real-world tasks including vulnerability resolution, code debugging, and protein assembly in containerized…
 rex-rs/rex
Rex is a safe and usable kernel extension framework that allows loading and executing Rust kernel extension programs in the place of eBPF.
 getkern/kern
Rootless container runtime and sandbox that launches kernel-enforced OCI images in milliseconds with no daemon, featuring resource profiles, seccomp…
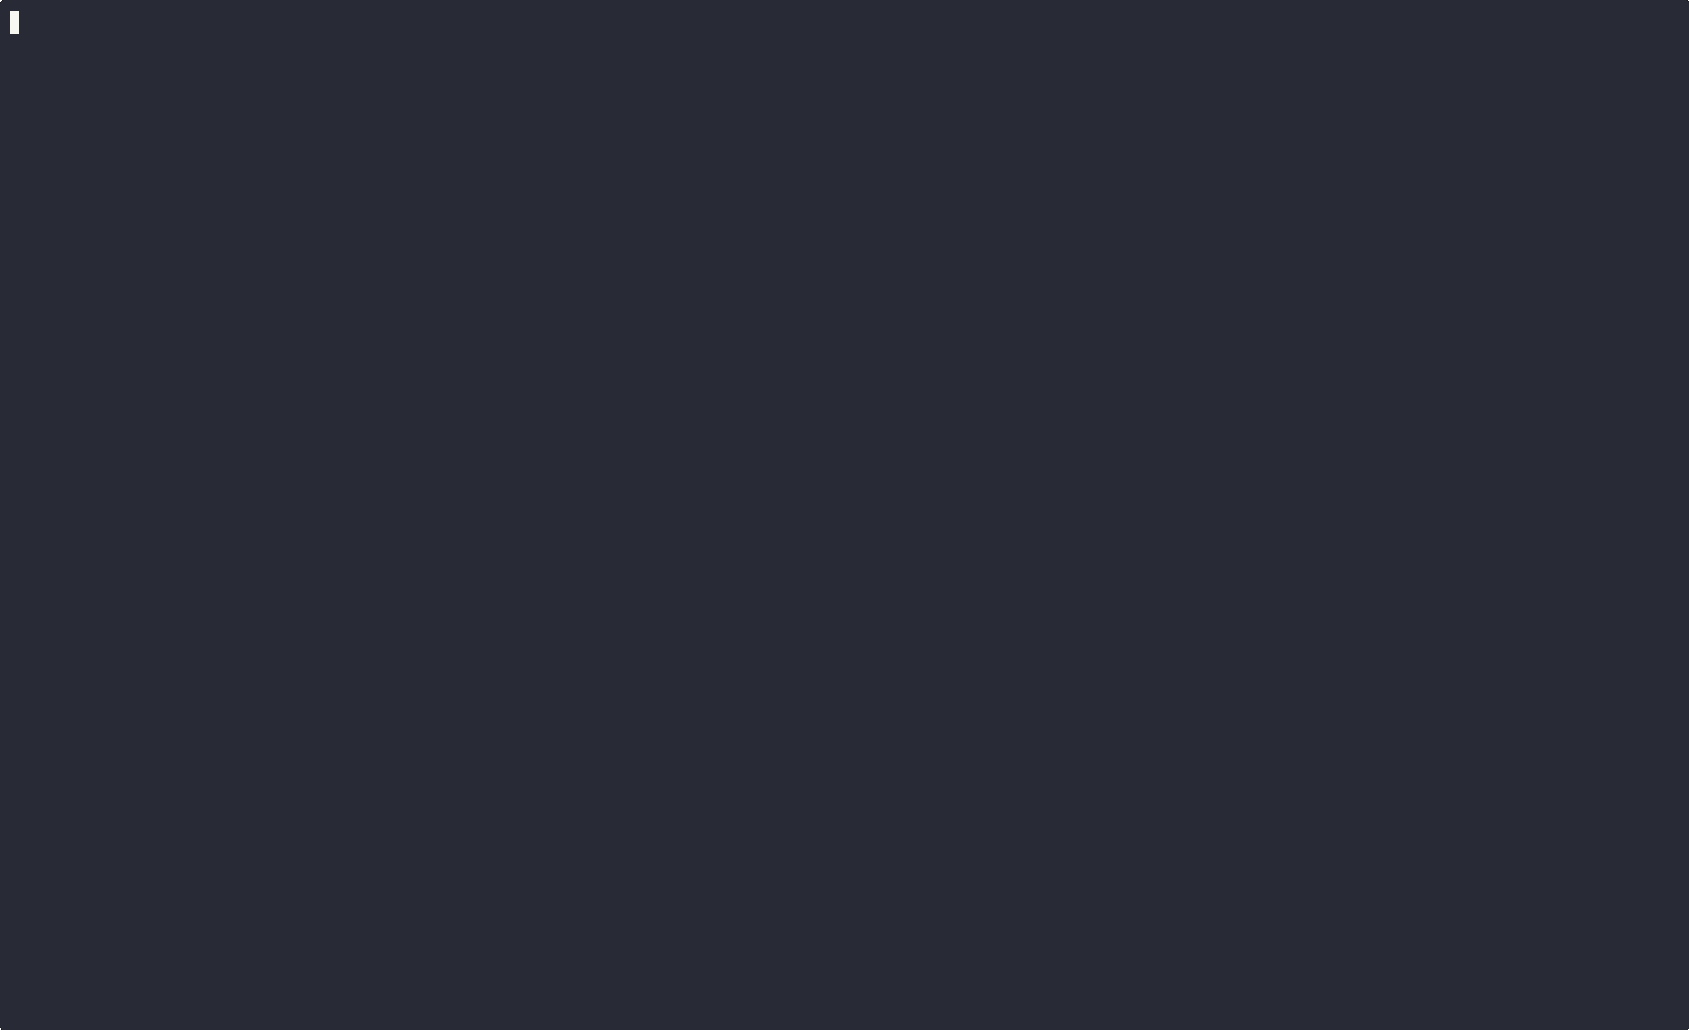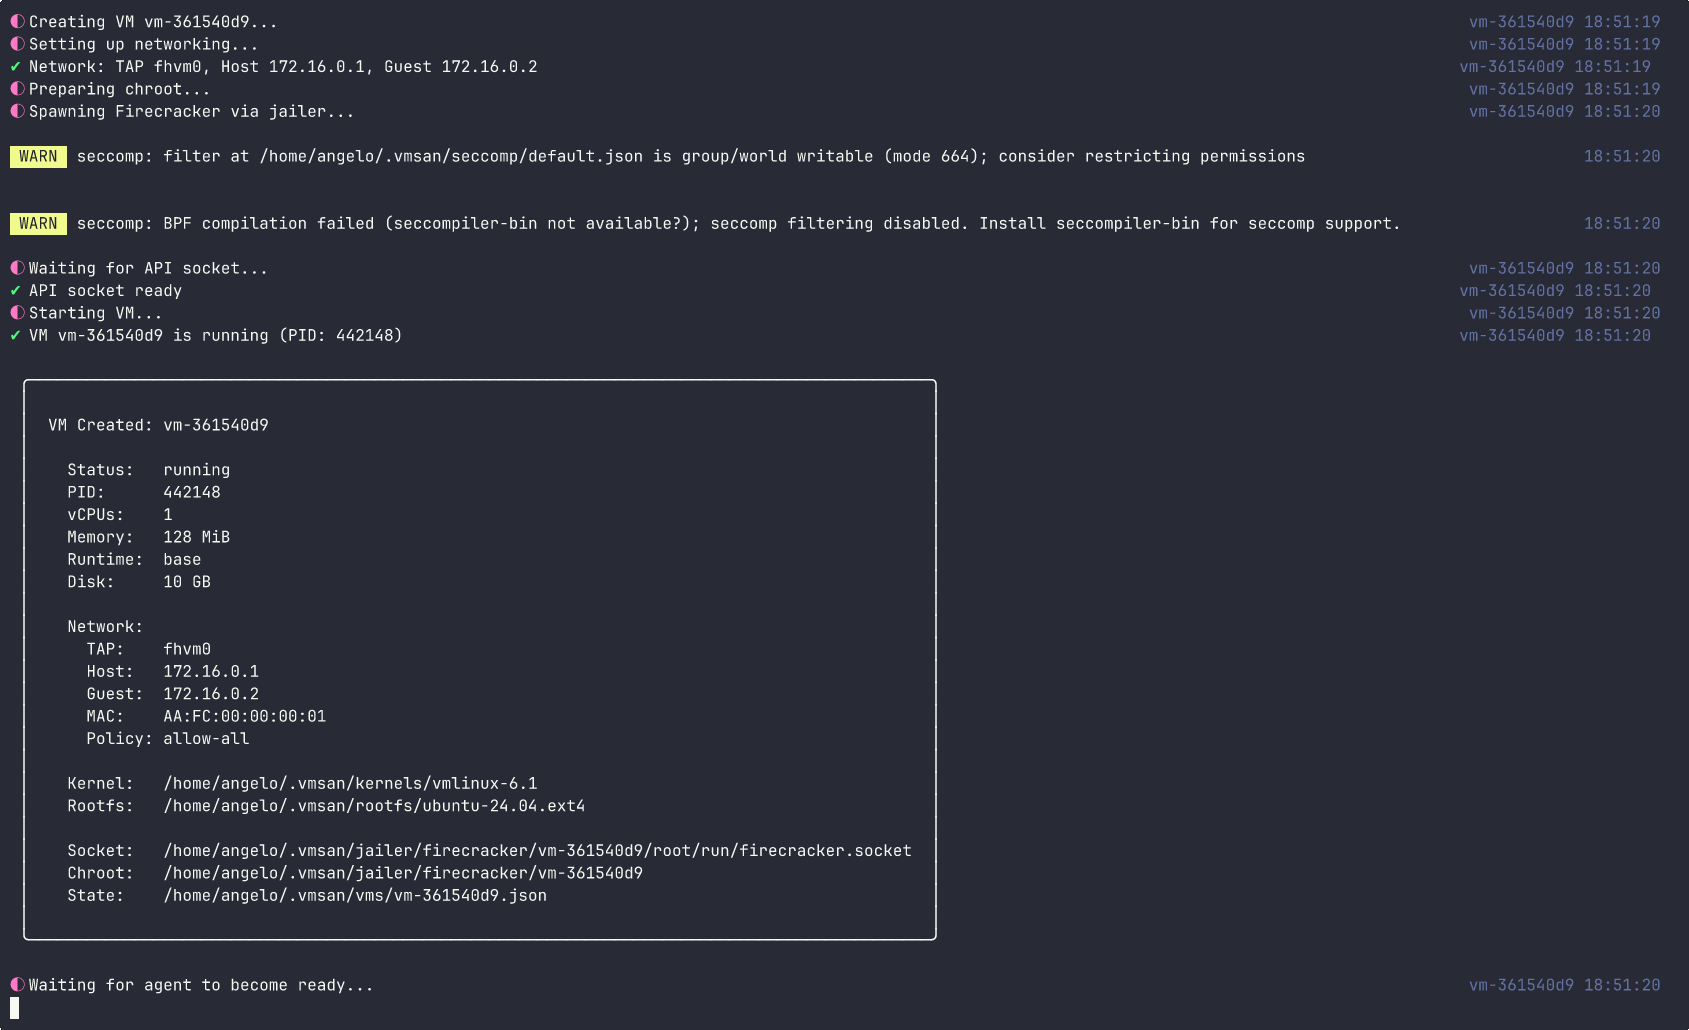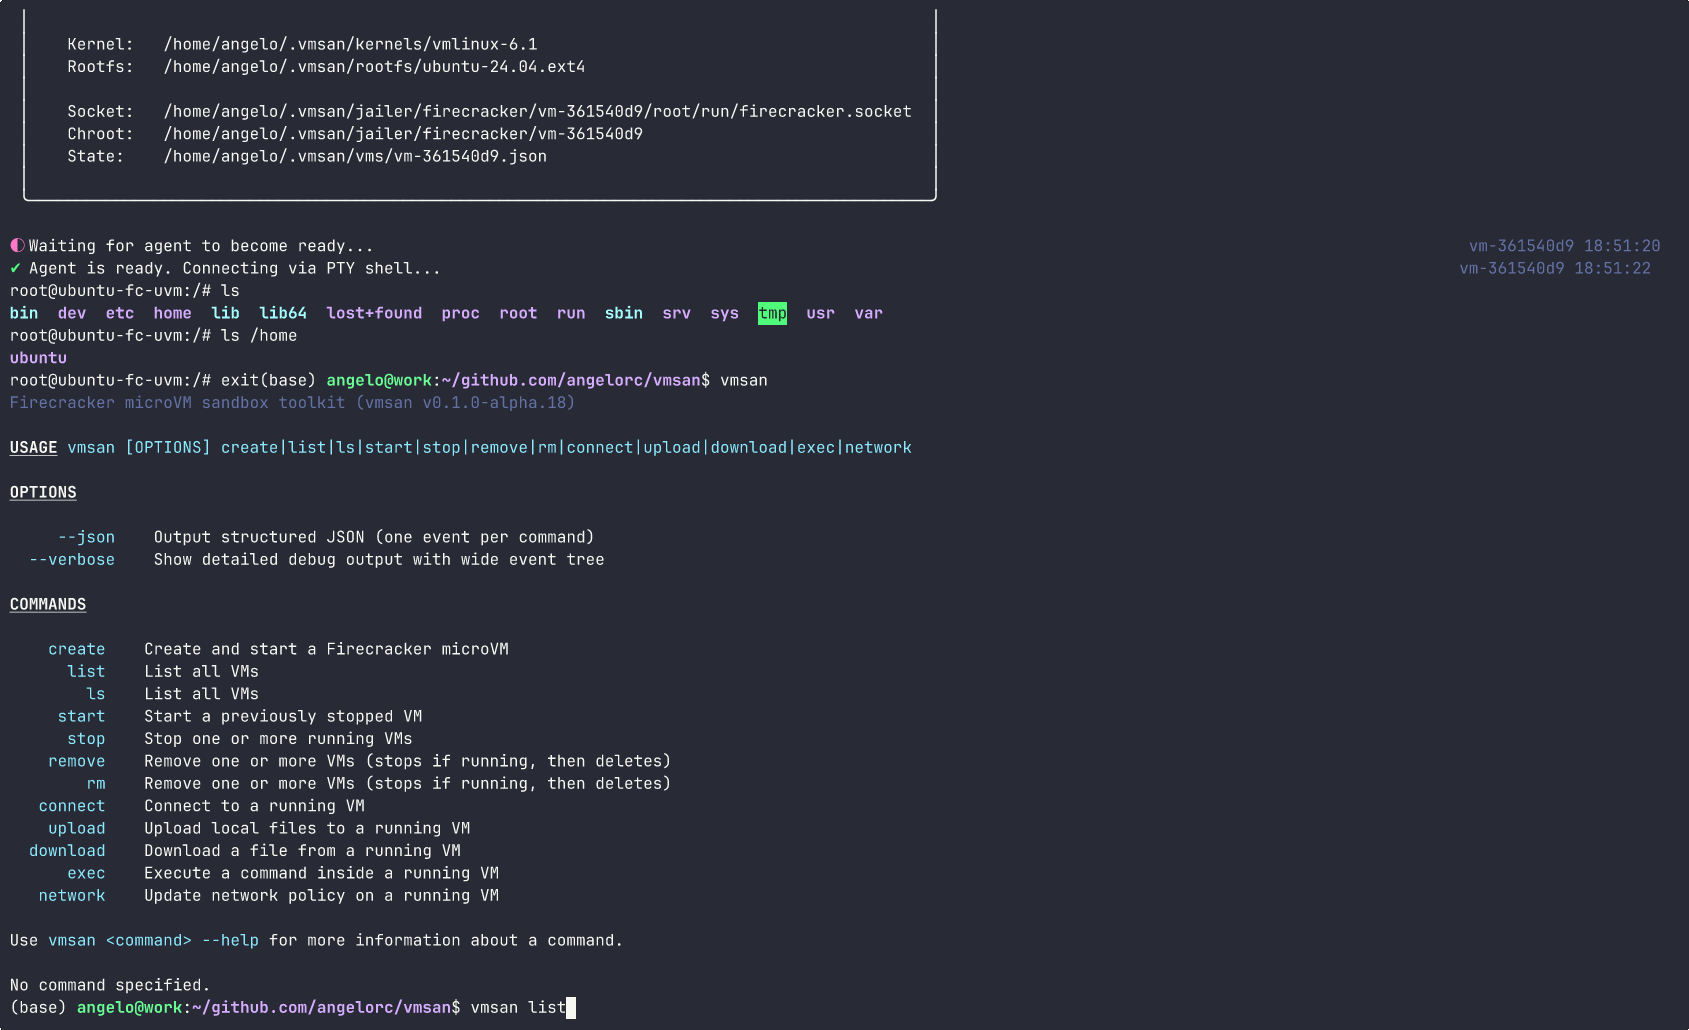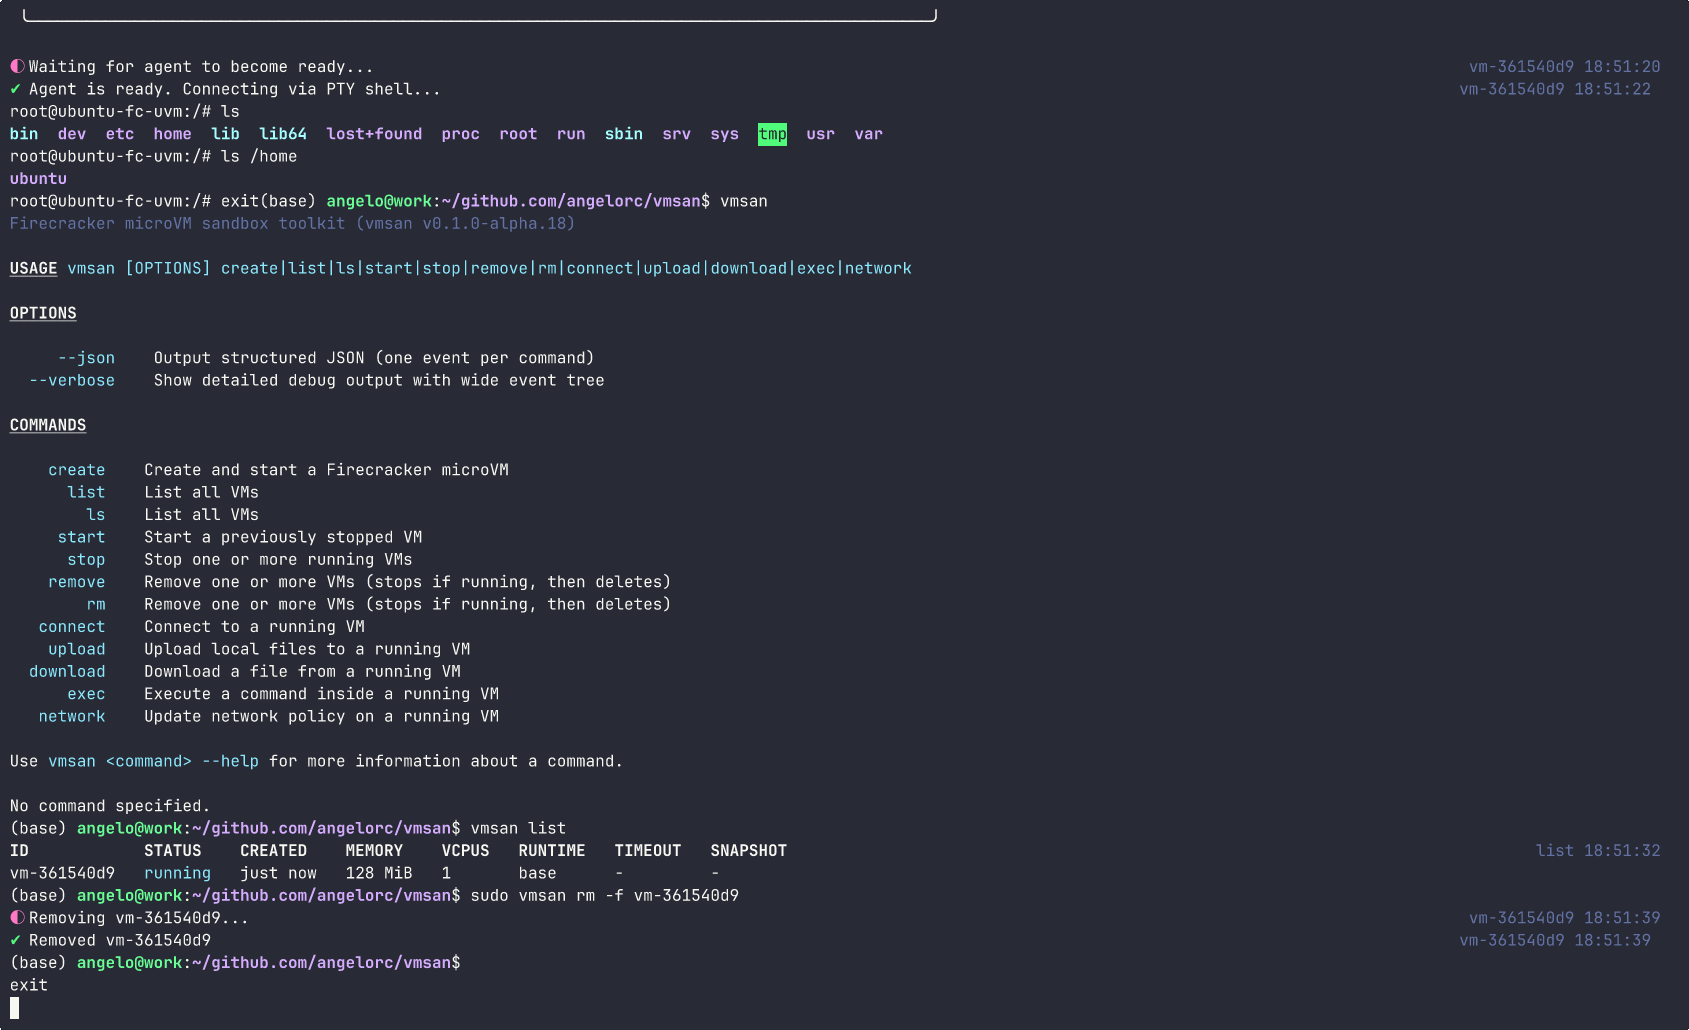 angelorc/vmsan
Firecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.
 rh-rahulshetty/log4shell-cve-2021-44228
Deliberately vulnerable Java/Maven fixture for testing Log4Shell (CVE-2021-44228) detection, code-impact classification, and remediation guidance in…
 trailofbits/claude-code-devcontainer
Sandboxed devcontainer for running Claude Code in bypass mode safely. Built for security audits and untrusted code review.
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 tandasat/hypervisor-101-in-rust
The materials of "Hypervisor 101 in Rust", a one-day long course, to quickly learn hardware-assisted virtualization technology and its application…
 jingkaihe/matchlock
Ephemeral microVM sandbox for AI agents with network allowlisting, secret injection via MITM proxy, and VM-level isolation. Boots in under a second,…
 capsulerun/capsule
Secure runtime to sandbox AI agent tasks. Run untrusted code in isolated WebAssembly environments.
 deathshotxd/comment2shell
Zero-click pre-auth WordPress CVE-2026-93485 exploit chain: stored XSS in wpautop() escalates to admin-session plugin upload and a self-deleting…
 ressl/cve-2026-87902-poc
PoC for CVE-2026-87902 — unauthenticated path traversal in WordPress page-template resolution (local PHP inclusion, conditional RCE) with a pinned…
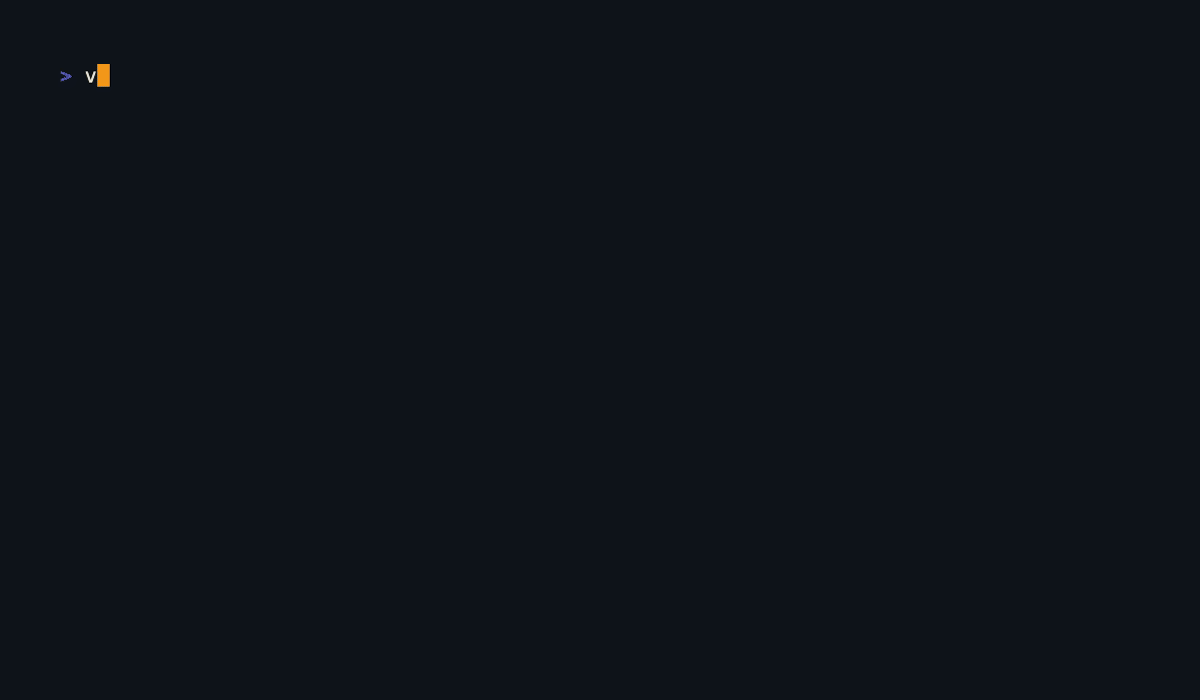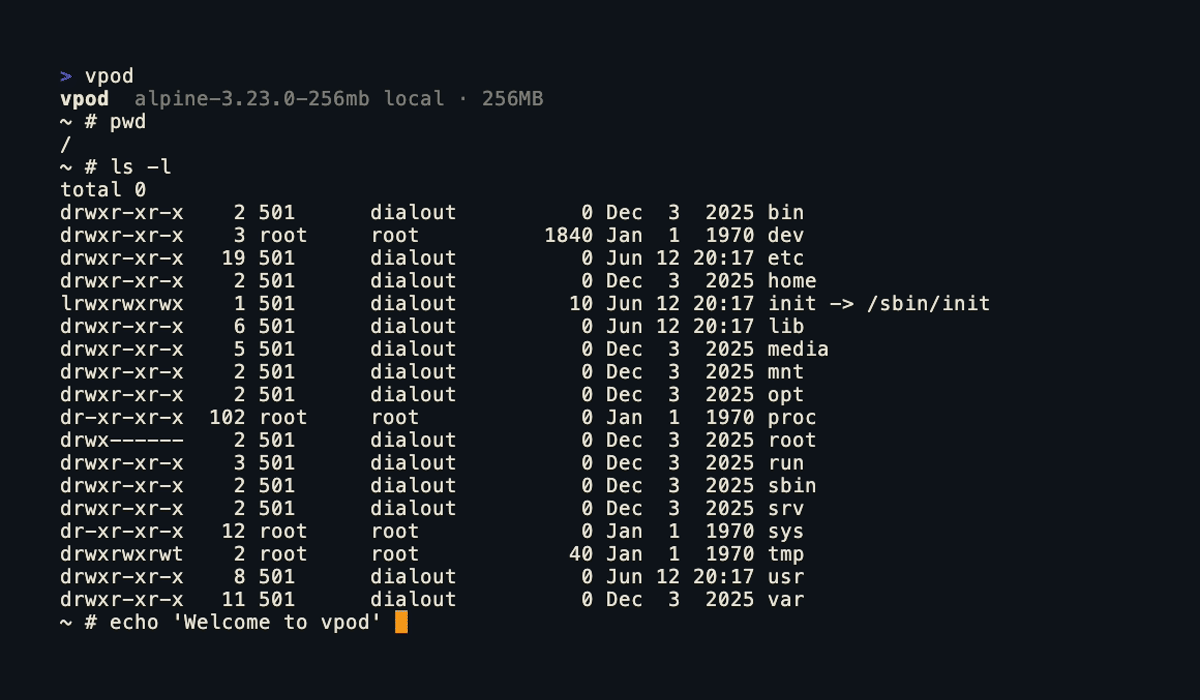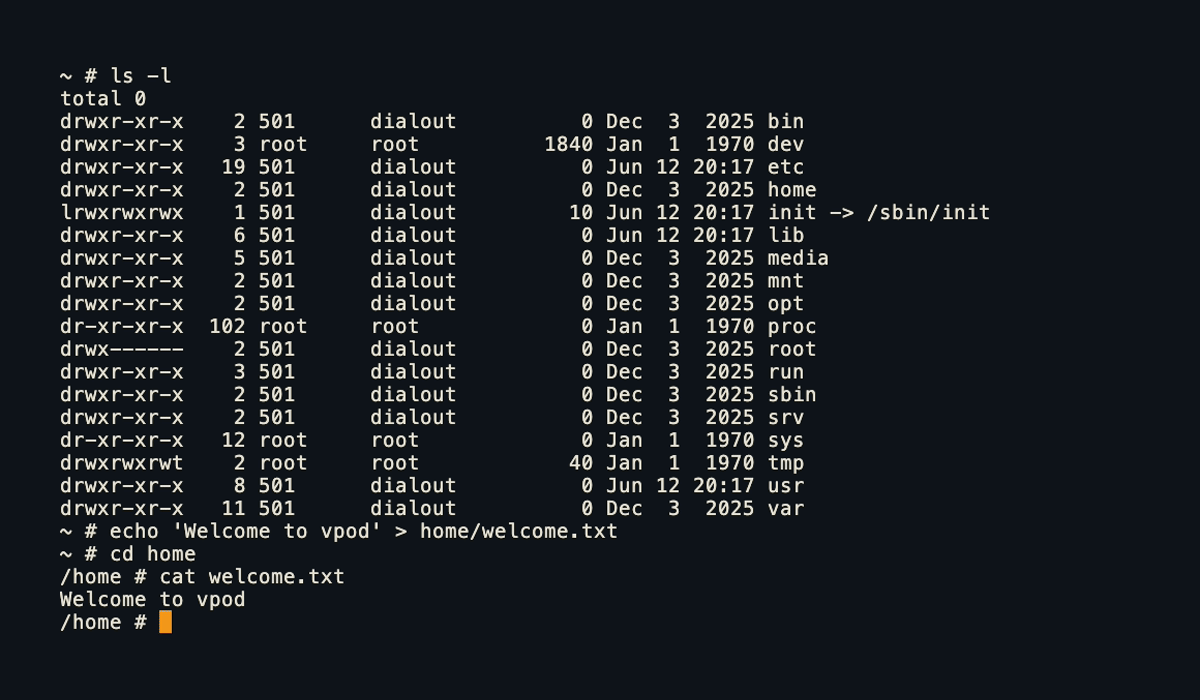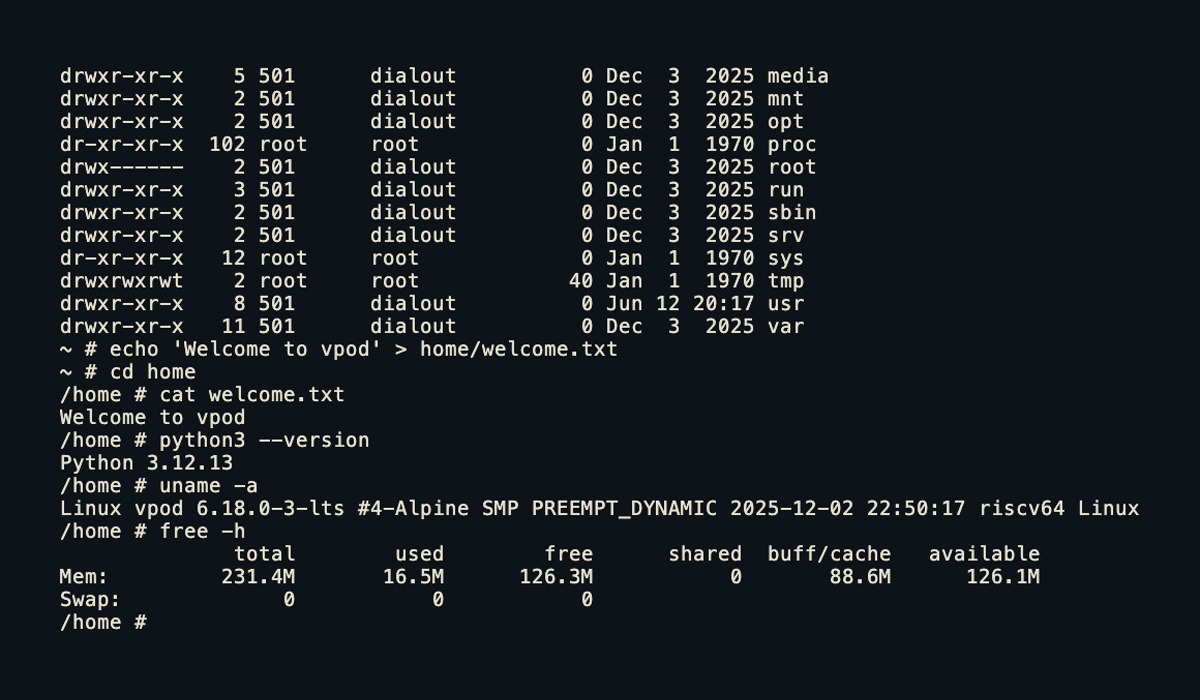 capsulerun/vpod
Lightweight, secure Linux sandboxes for untrusted processes. Runs in the browser and on the server.
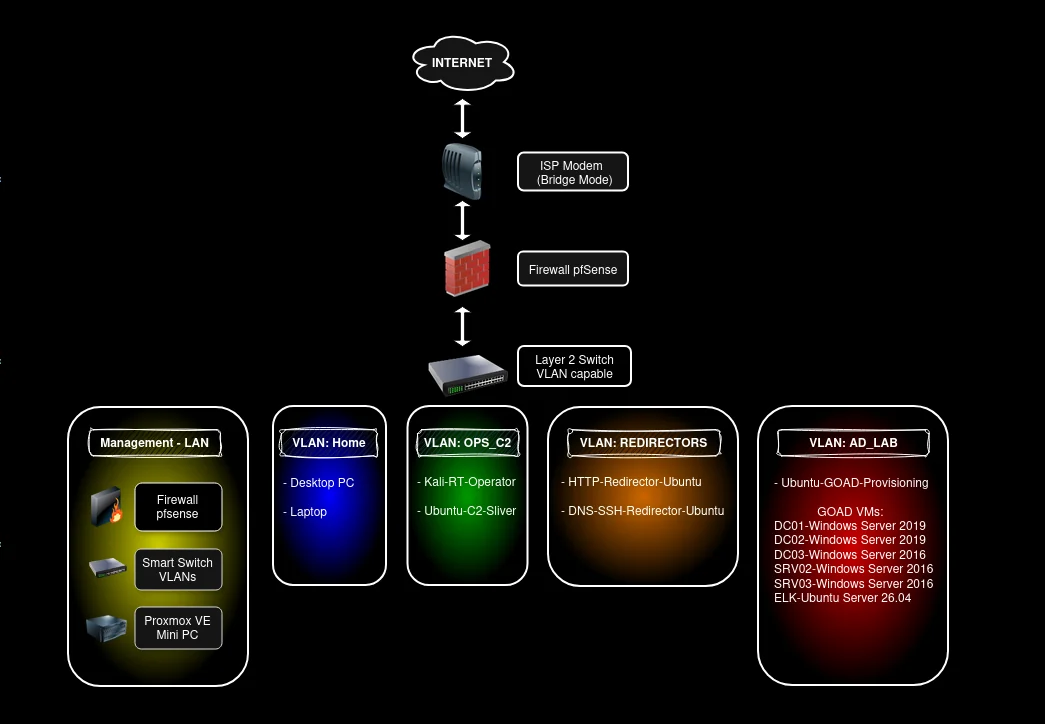 pho5nix/red-team-goad-lab-proxmox
Build guide for Red Teaming home lab. GOAD lab setup in Proxmox and pfSense, Operator/C2 and Redirectors.
 guneykabel/cve-2026-85706
Python PoC exploit for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE via Workhorse path-encoding bypass, with writeup and…
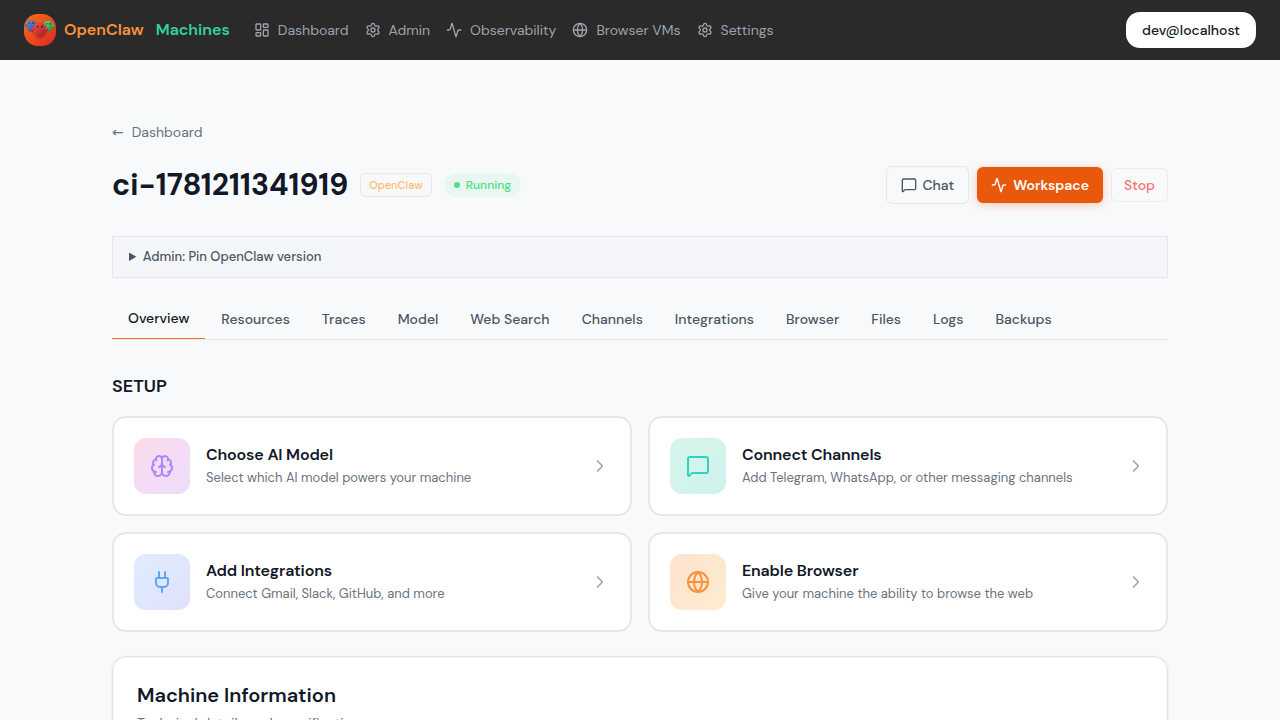 mathaix/openclawmachines
Manage OpenClaw in your team (Enterprise) by providing it compute infrastructure, tool integration, Authentication and security primitives