
gitea-artifact-v4-readall
 abraxas/gitea-artifact-v4-readall
Proof-of-concept and lab for a Gitea Actions artifact v4 DoS: unbounded io.ReadAll in parseProtobufBody lets a job token POST oversized…
exploitationlabs-practicesecurity-virtualization+2
abraxas/gitea-artifact-v4-readallProof-of-concept and lab for a Gitea Actions artifact v4 DoS: unbounded io.ReadAll in parseProtobufBody lets a job token POST oversized…
 jingkaihe/matchlock
Ephemeral microVM sandbox for AI agents with network allowlisting, secret injection via MITM proxy, and VM-level isolation. Boots in under a second,…
 guneykabel/cve-2026-85706
Python PoC exploit for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE via Workhorse path-encoding bypass, with writeup and…
 abraxas/cve-2026-52782
Reproduction pack and PoC script for CVE-2026-52782, an authenticated IDOR in OpenProject project storage settings that hijacks Nextcloud/OneDrive…
 abraxas/n8n-databricks-path-join
Proof-of-concept for an n8n path-traversal (CWE-22) in Databricks nodes: unauthenticated webhook input escapes the Genie path to leak workspace PAT…
 squeeze440/zotlit-poc
PoC — attachment import copies files from unapproved local paths in ZotLit (GHSA-4qh7-66xv-h329, CVE-2026-87000, CVSS 5.5).
 abraxas/cve-2026-15583
Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…
 leaningtech/webvm
Client-side Linux virtual machine running in the browser via WebAssembly, with Tailscale networking, Dockerfile-based custom images, and CTF…
 anthropics/oss-scanner
Service that builds enrolled open-source repositories in isolated offline VMs and scans them for security vulnerabilities, emailing findings with…
 cert-ee/cuckoo3
Open-source automated malware analysis sandbox that runs suspicious files and URLs in isolated VMs and generates detailed behavioral reports.
 harbor-framework/terminal-bench-2
Benchmark for evaluating AI agents on real-world tasks including vulnerability resolution, code debugging, and protein assembly in containerized…
 rex-rs/rex
Rex is a safe and usable kernel extension framework that allows loading and executing Rust kernel extension programs in the place of eBPF.
 getkern/kern
Rootless container runtime and sandbox that launches kernel-enforced OCI images in milliseconds with no daemon, featuring resource profiles, seccomp…
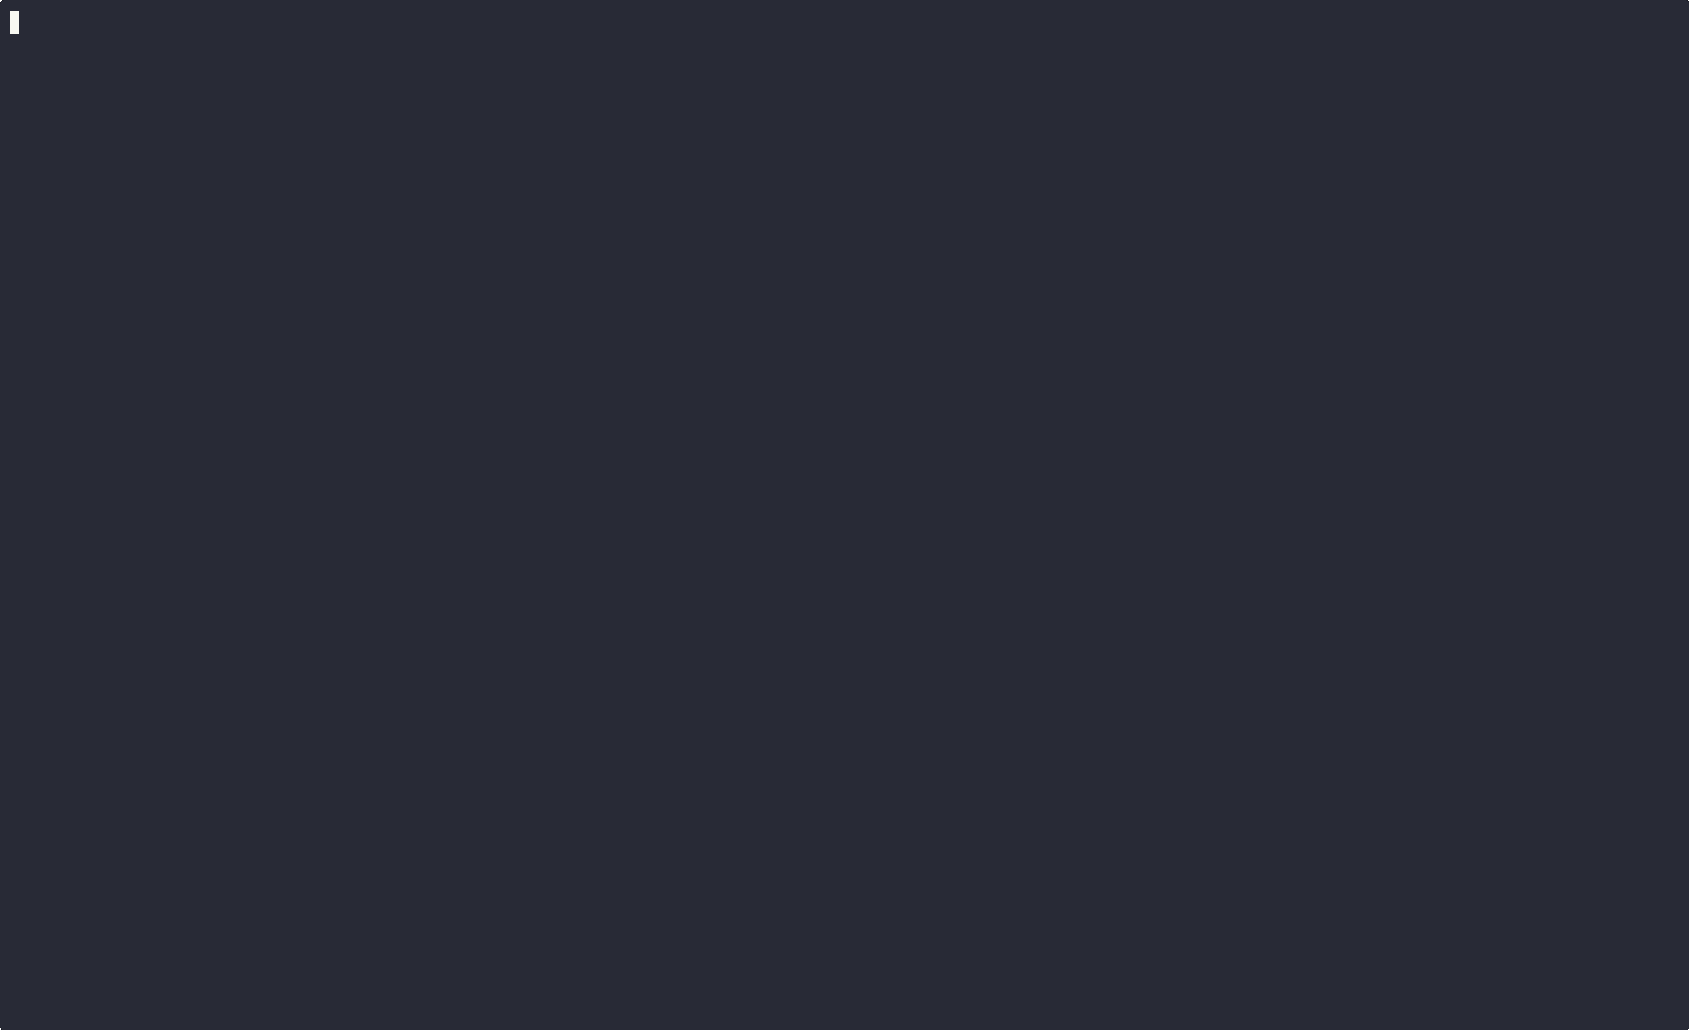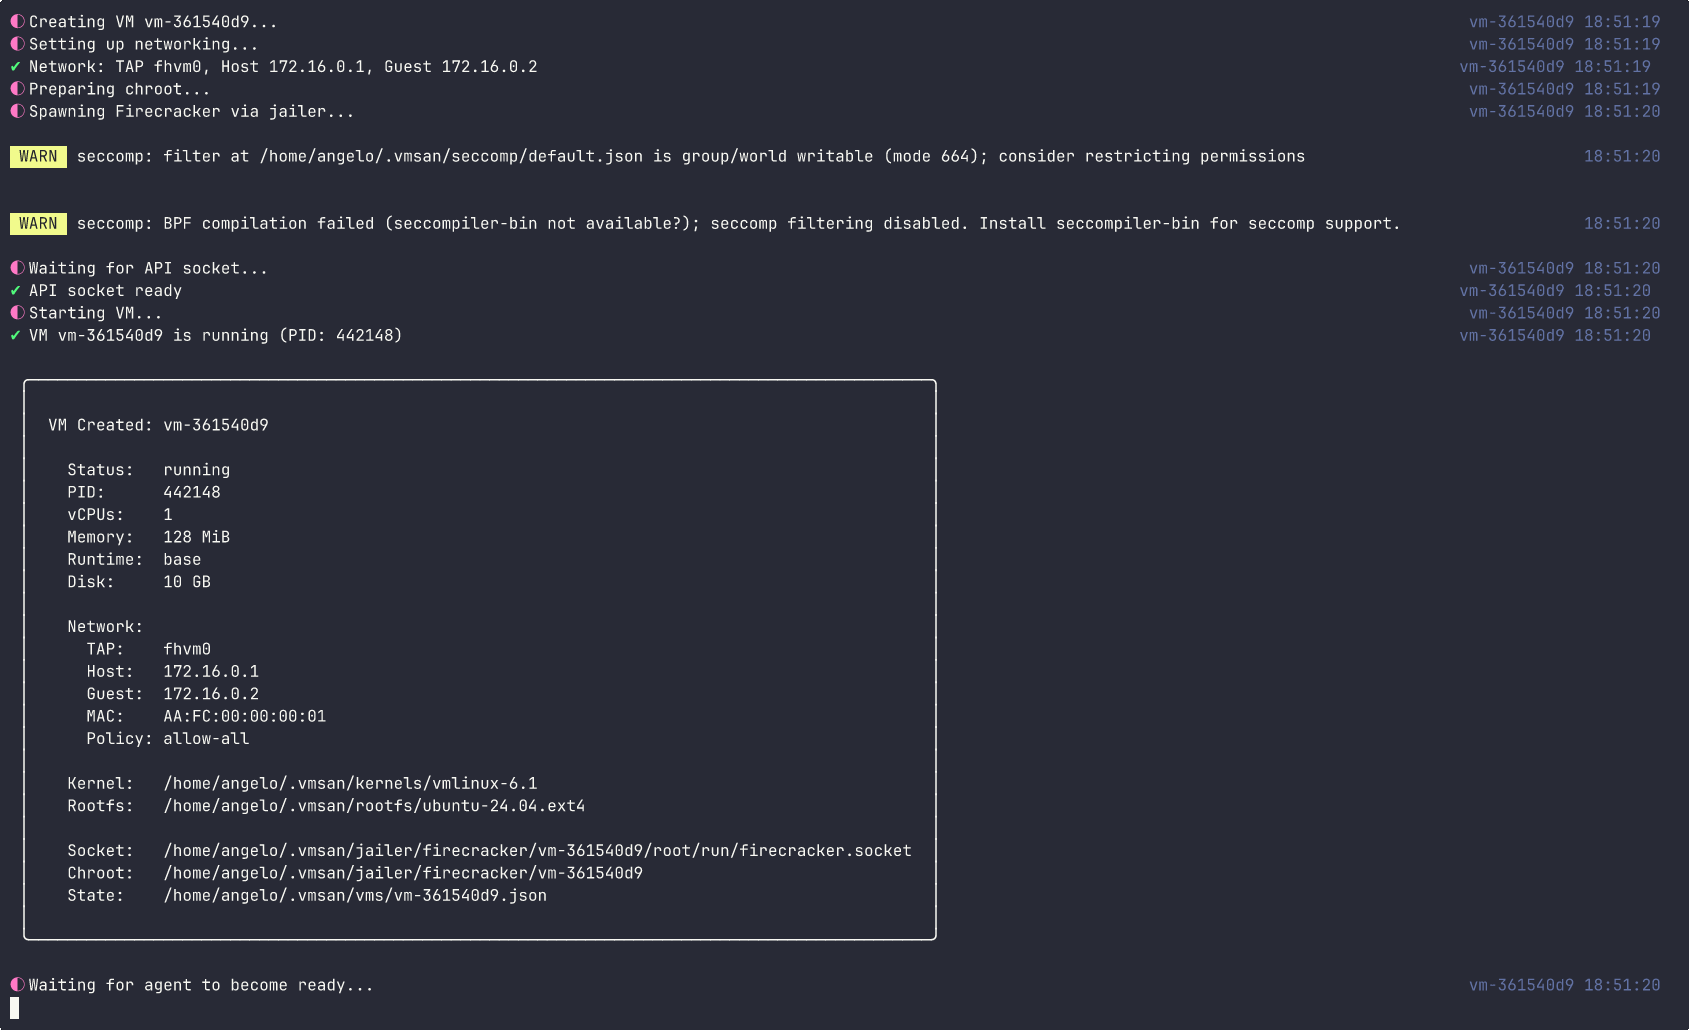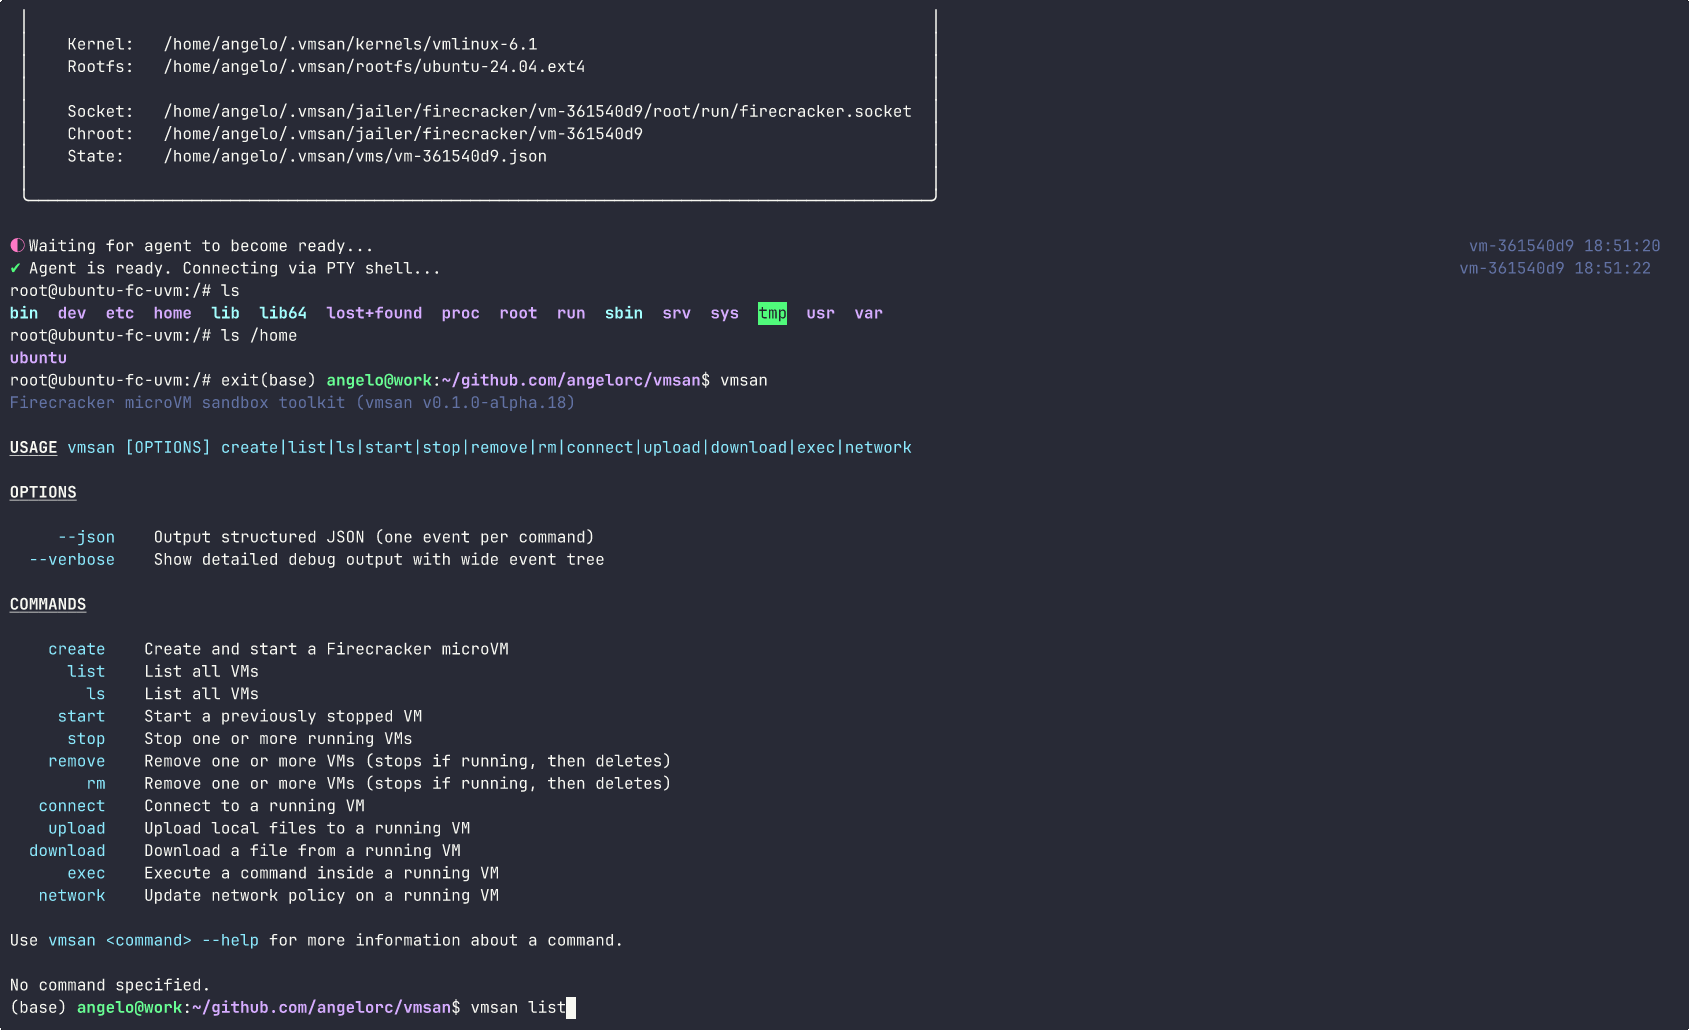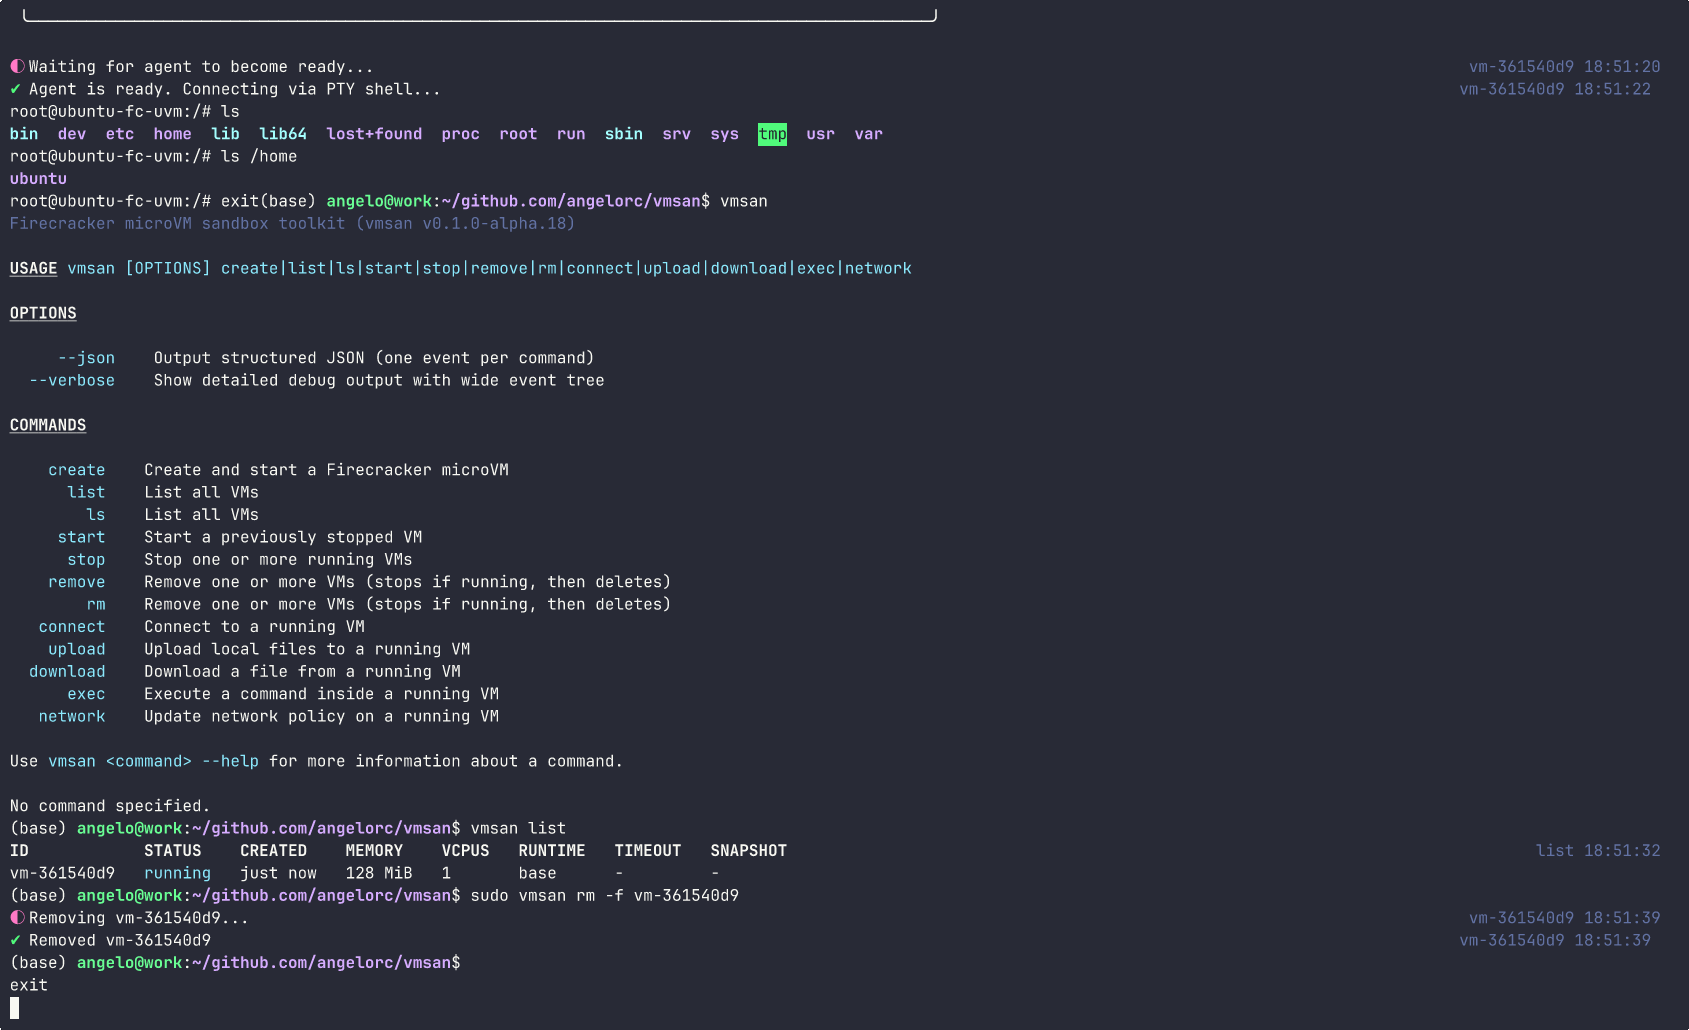 angelorc/vmsan
Firecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.
 rh-rahulshetty/log4shell-cve-2021-44228
Deliberately vulnerable Java/Maven fixture for testing Log4Shell (CVE-2021-44228) detection, code-impact classification, and remediation guidance in…
 opengrep/opengrep
🔎 Static code analysis engine to find security issues in code.
 project-oak/oak
Meaningful control of data in distributed systems.
 tandasat/hypervisor-101-in-rust
The materials of "Hypervisor 101 in Rust", a one-day long course, to quickly learn hardware-assisted virtualization technology and its application…