
vmsan
 angelorc/vmsan
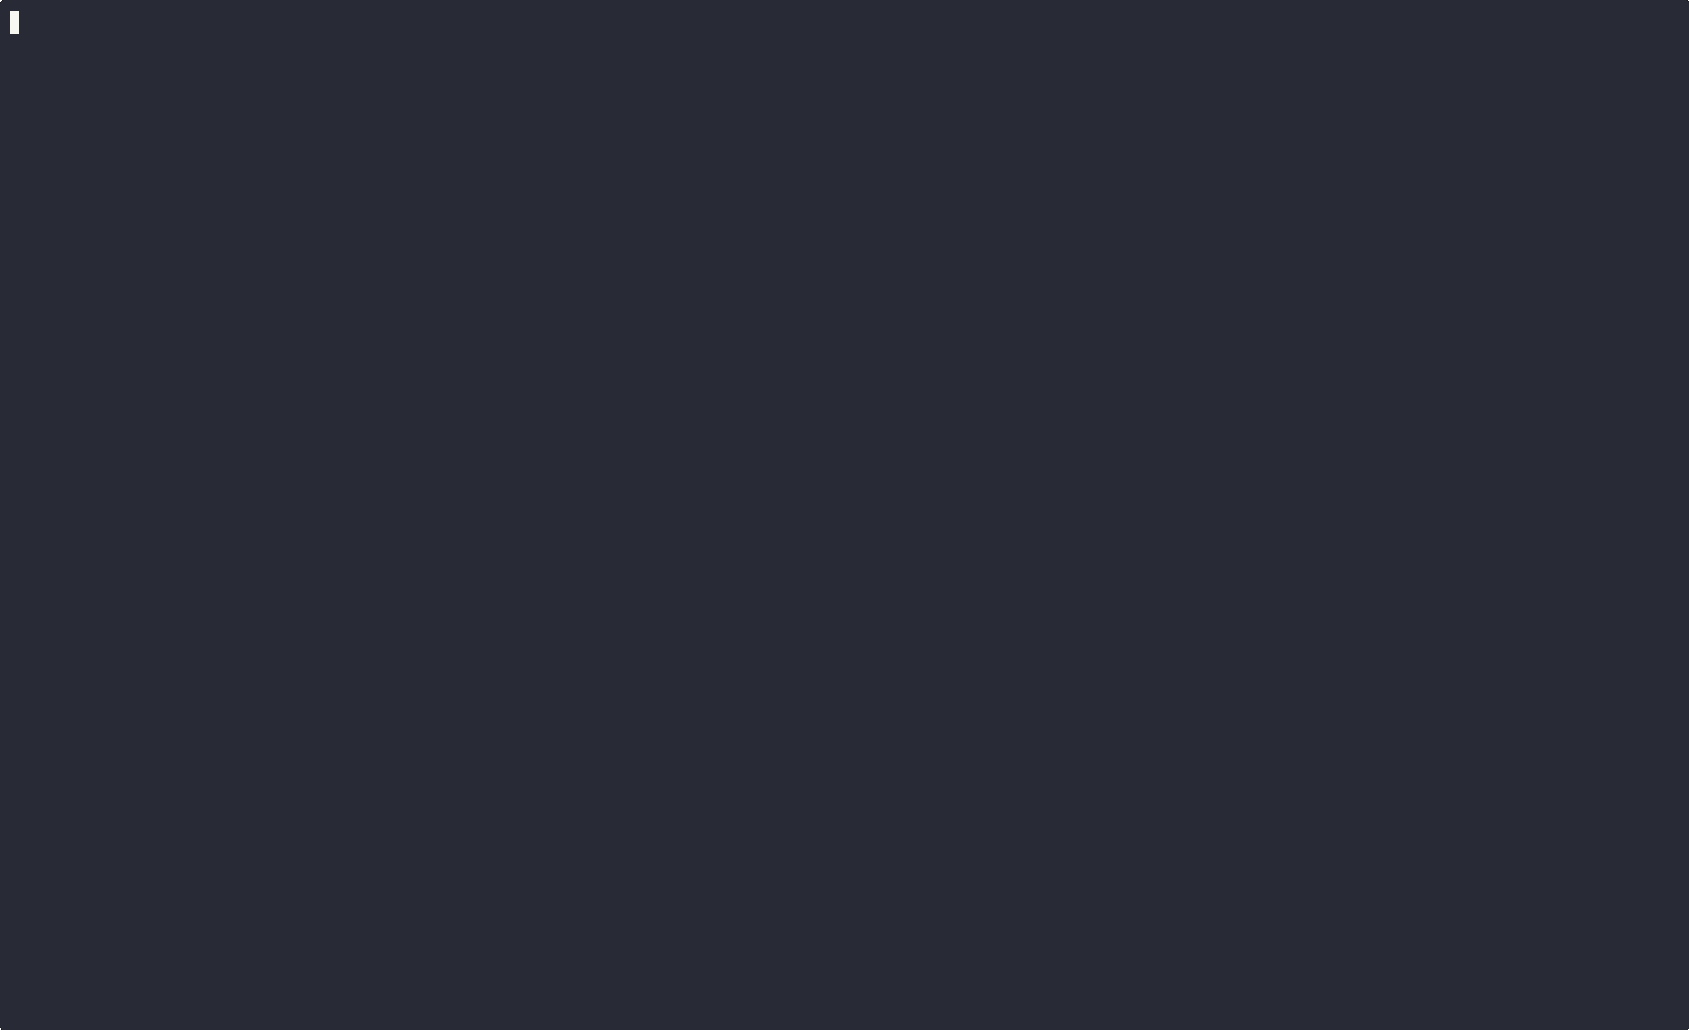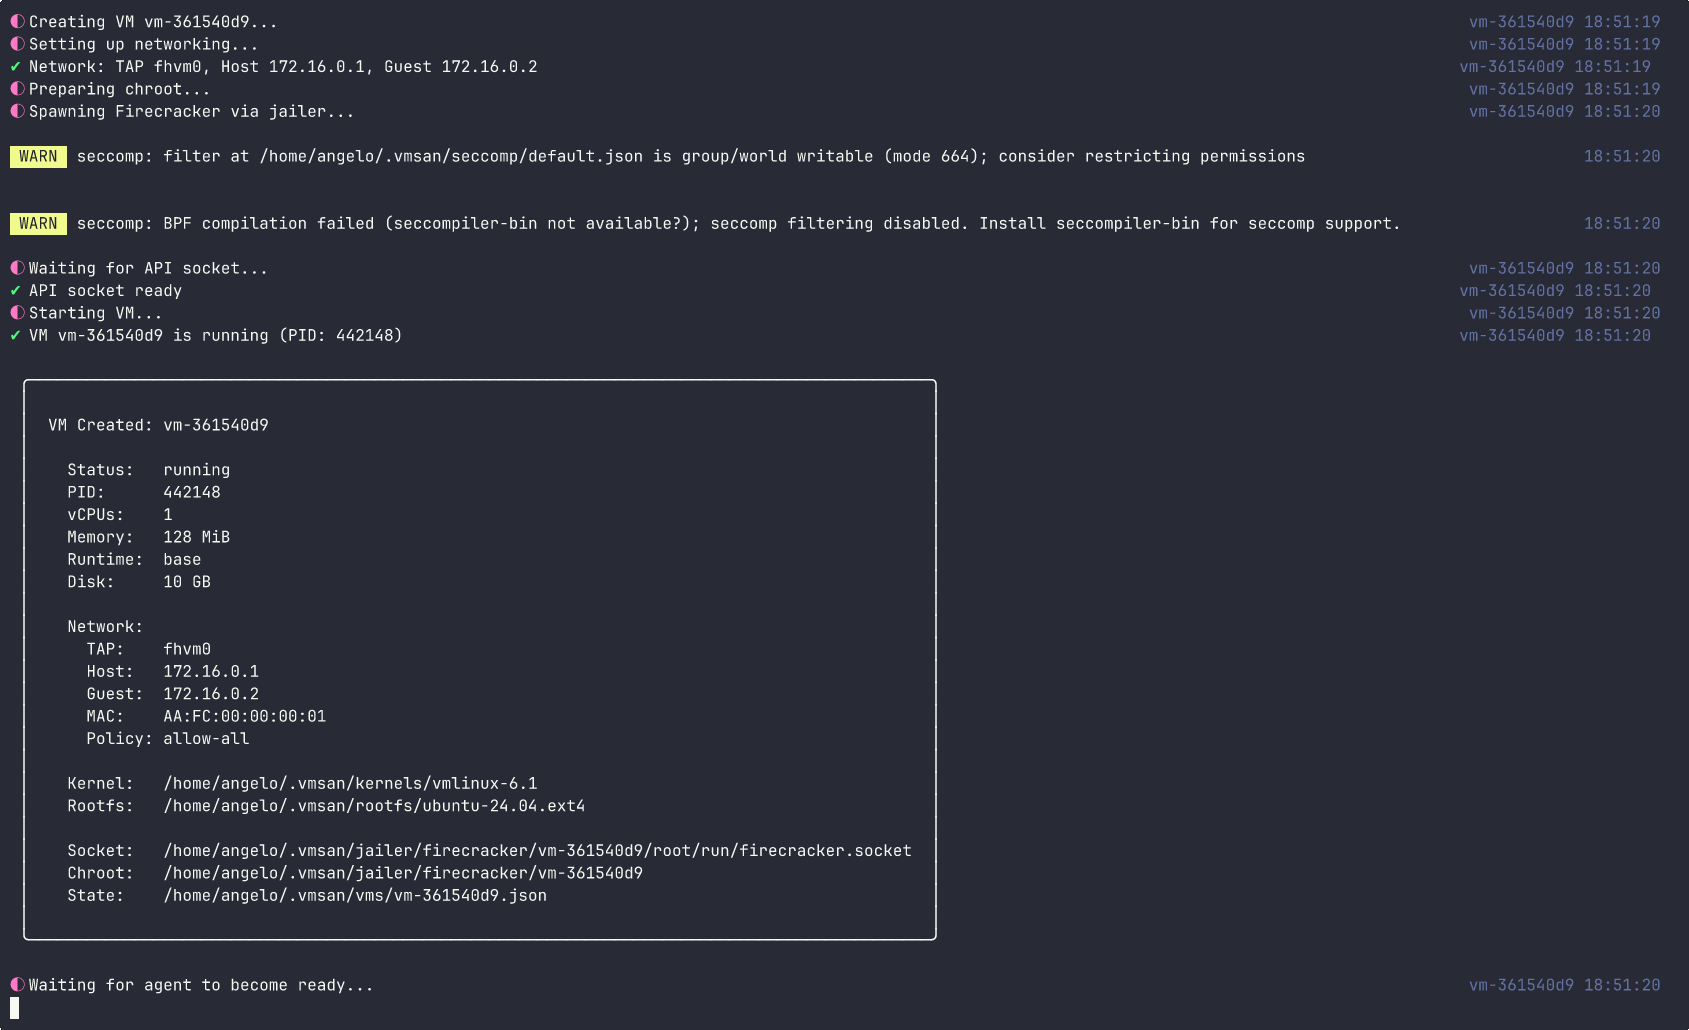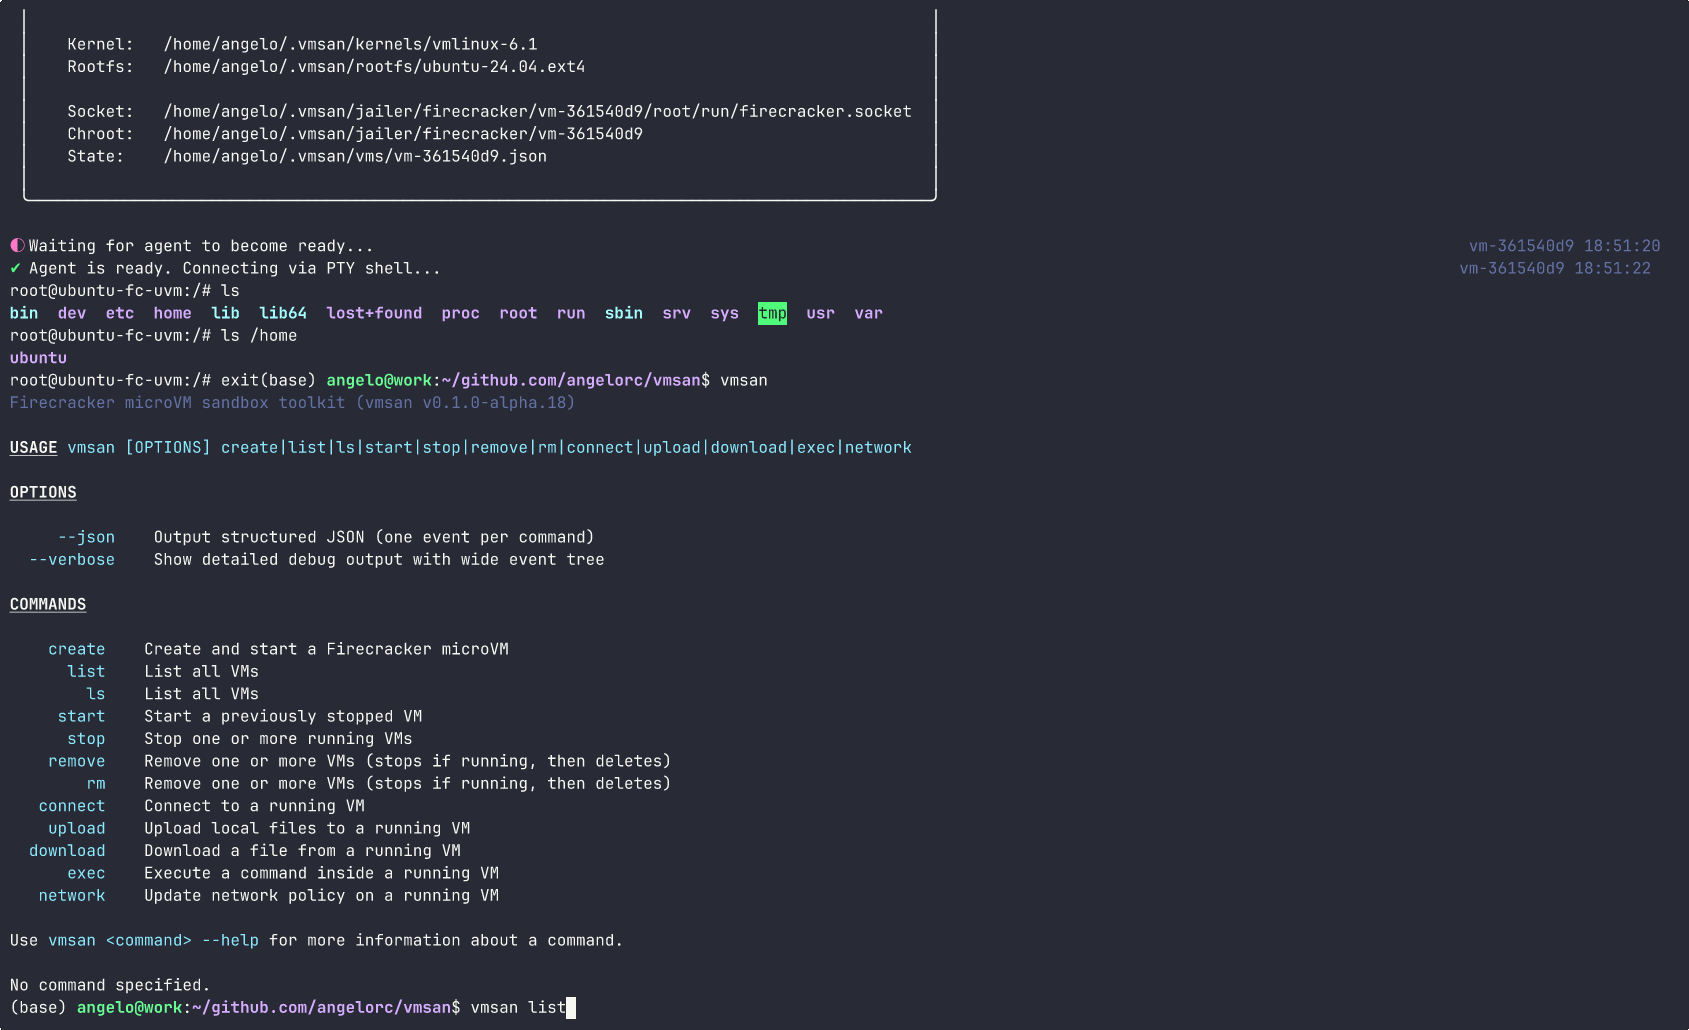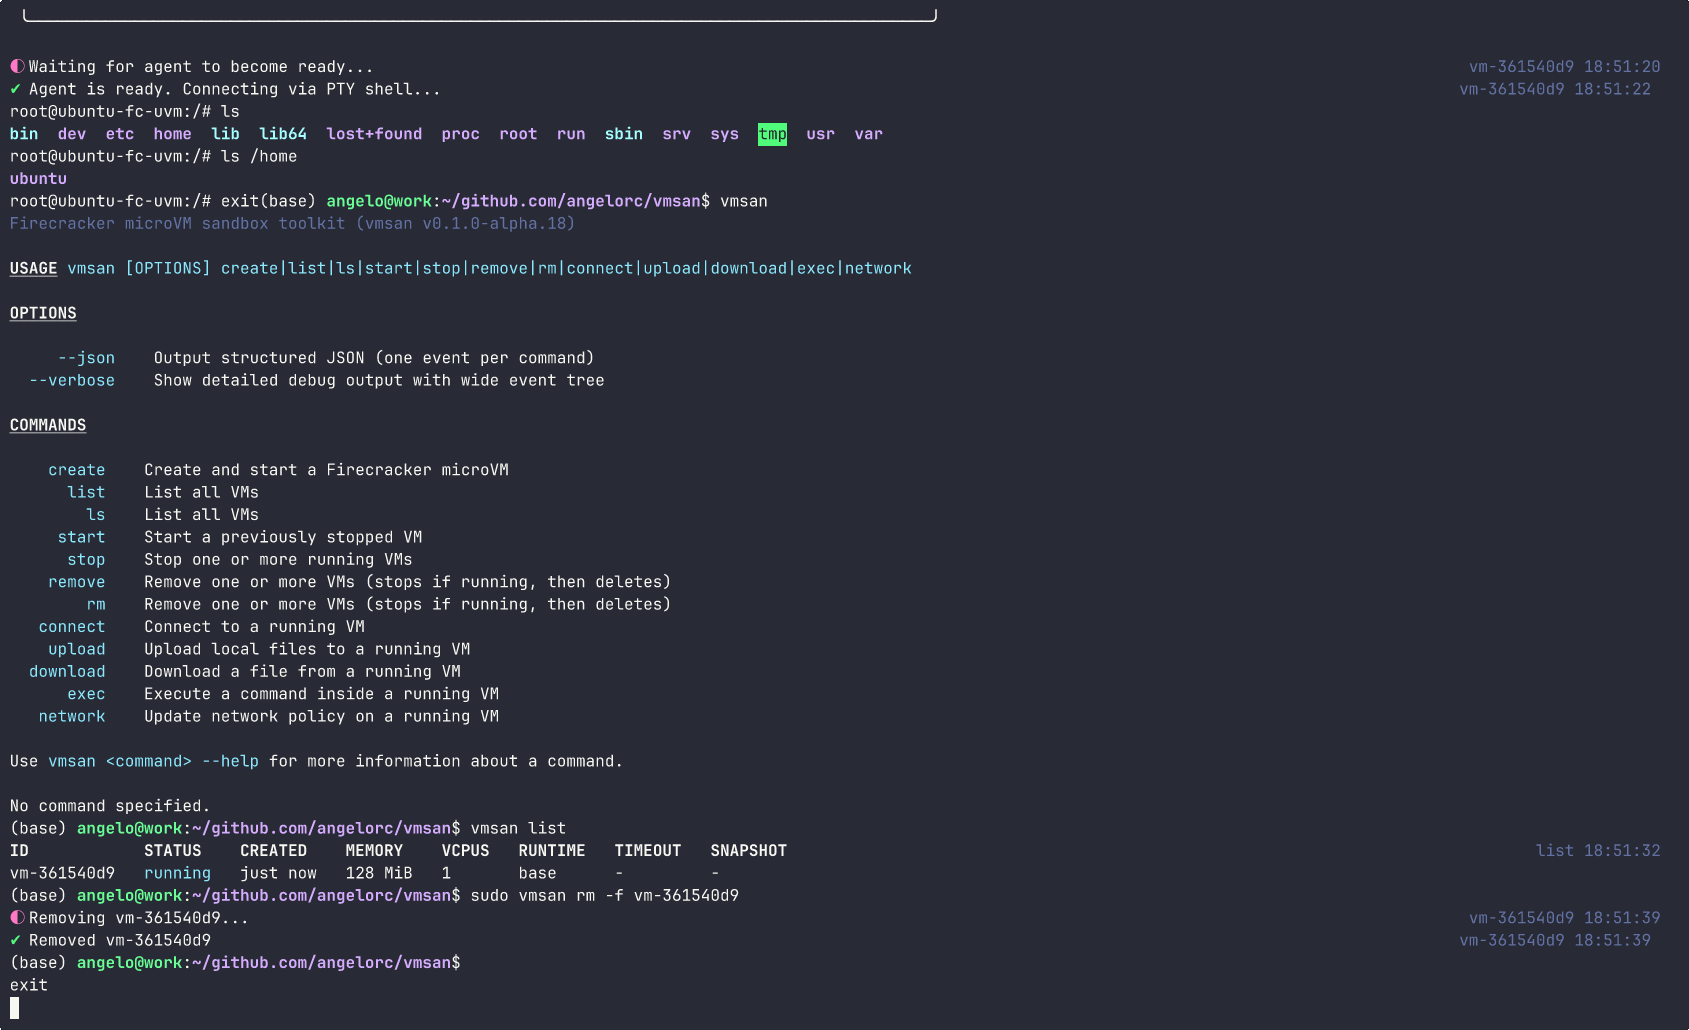
Firecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.
cloud-infrastructure-securitycontainer-securitydevsecops+3
85
angelorc/vmsanFirecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.
 phalanx-ccs/copy-fail
Passive diagnostic tool that checks if a Linux system is vulnerable to CVE-2026-31431 by testing AF_ALG socket reachability, providing mitigation…
 deathshotxd/comment2shell
Zero-click pre-auth WordPress CVE-2026-93485 exploit chain: stored XSS in wpautop() escalates to admin-session plugin upload and a self-deleting…
 abhishek2512mishra/claude-code-security-audit
Security scanner auditing Claude Code environments for CVE-2026-21852 pre-trust execution, hook hijacking, and eBPF lockdown.
 clickswave/limeyard
Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…
 dockur/windows
Run Windows inside a Docker container with KVM acceleration, automatic installation, and customizable resources. Supports multiple Windows versions,…
 firecracker-microvm/firecracker
Secure and fast microVMs for serverless computing.
 google/gvisor
Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 kata-containers/kata-containers
Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…
 blackarch/blackarch
An ArchLinux based distribution for penetration testers and security researchers.
 containers/bubblewrap
Low-level unprivileged sandboxing tool used by Flatpak and similar projects
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 flatpak/flatpak
Linux application sandboxing and distribution framework
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 clong/detectionlab
Automate the creation of a lab environment complete with security tooling and logging best practices
 anthropic-experimental/sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.