
vpod
 capsulerun/vpod
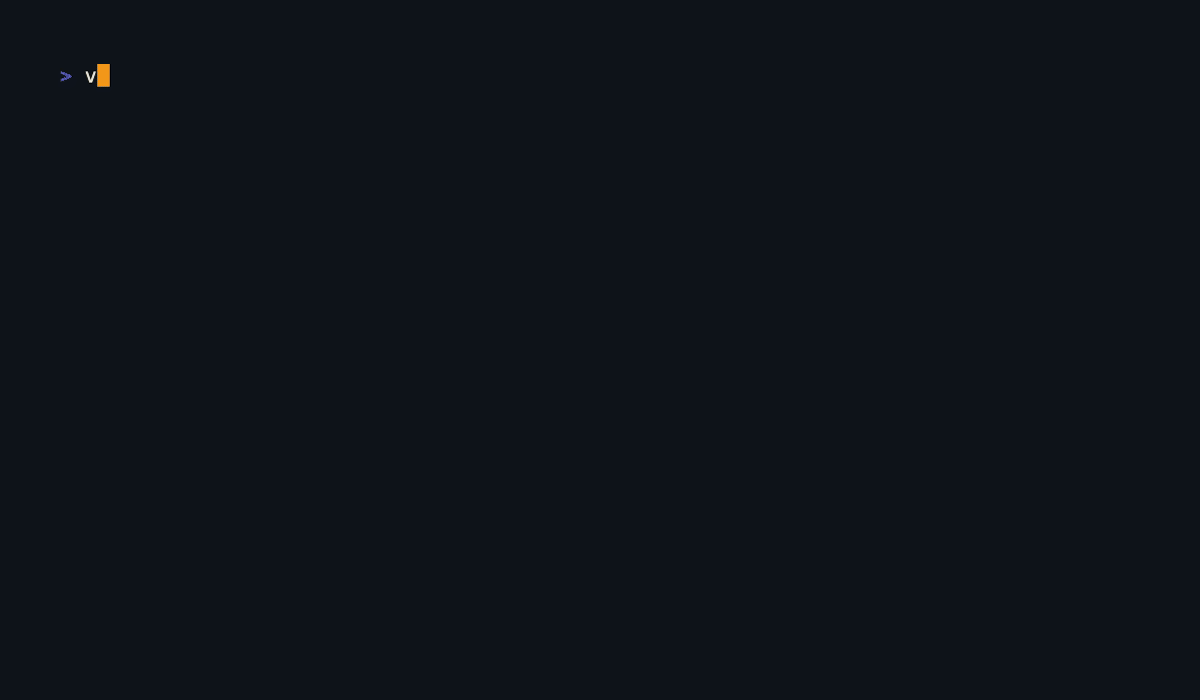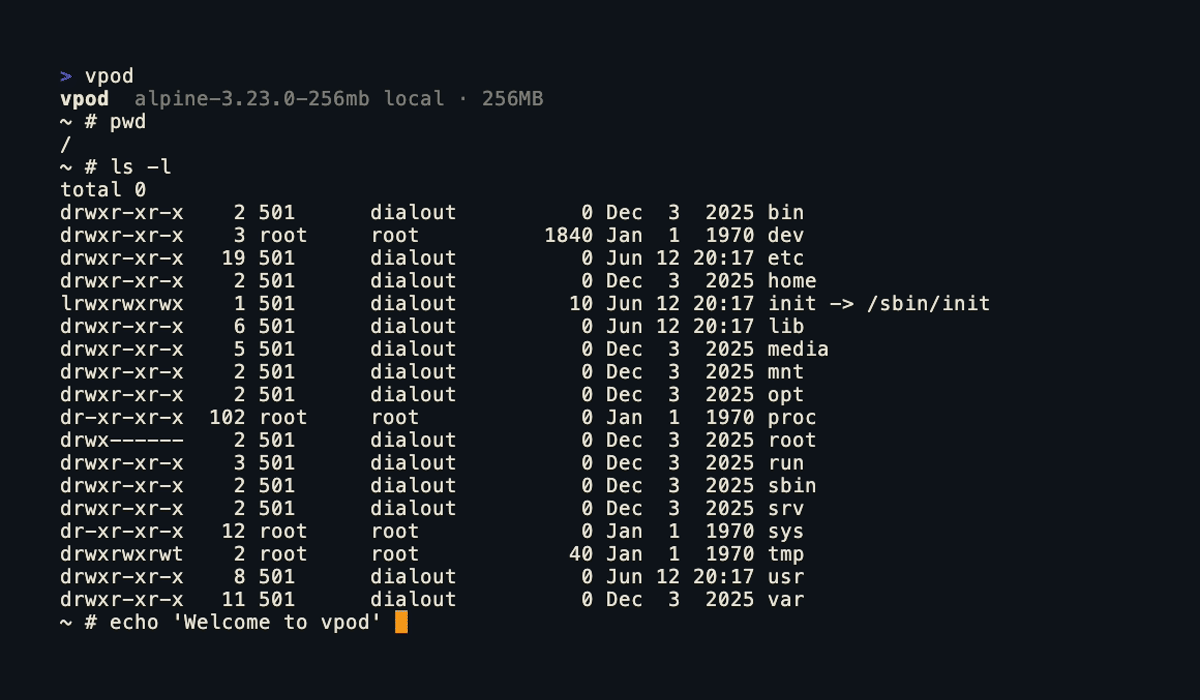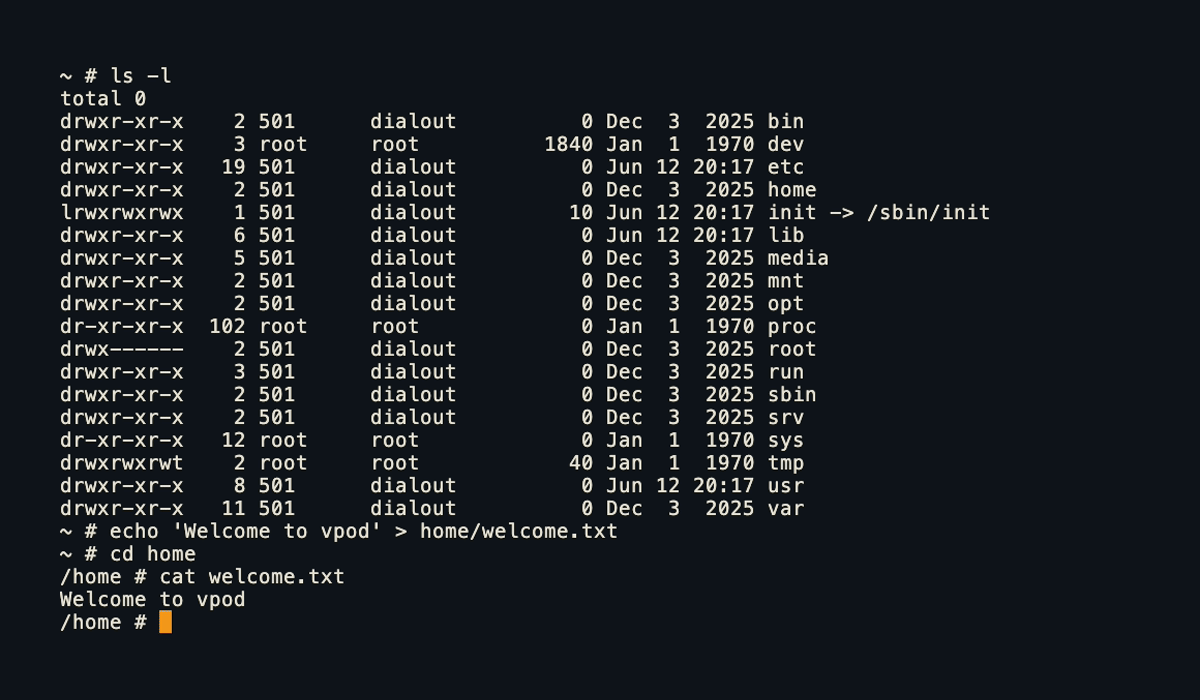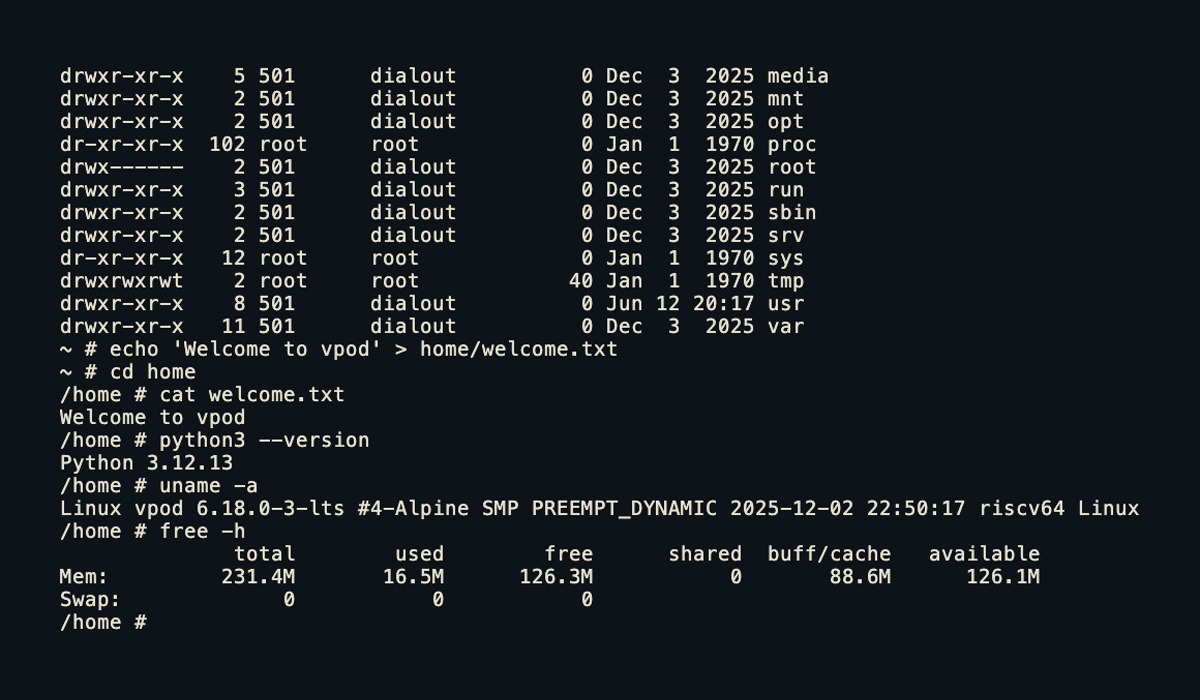
Lightweight, secure Linux sandboxes for untrusted processes. Runs in the browser and on the server.
ai-securitycontainer-securitydefensive-tools+3
capsulerun/vpodLightweight, secure Linux sandboxes for untrusted processes. Runs in the browser and on the server.
 nicolasriverocorvalan/cloud-sniper
Virtual Security Operations Center
 michaels1011/ephemora-cell
Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
 lfi-project/lfi
Top-level repository for LFI: Practical, Efficient, and Secure Software-based Sandboxing
 guneykabel/cve-2026-85706
Python PoC exploit for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE via Workhorse path-encoding bypass, with writeup and…
 mathaix/openclawmachines
Manage OpenClaw in your team (Enterprise) by providing it compute infrastructure, tool integration, Authentication and security primitives
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 armourbird/csf
ArmourBird CSF - Container Security Framework
 zephrfish/ludus-defender-lab
MDE/MDI Defender setup for Ludus
 asteroid-belt/skulto
Offline and security-first tool for syncing and managing agent skills
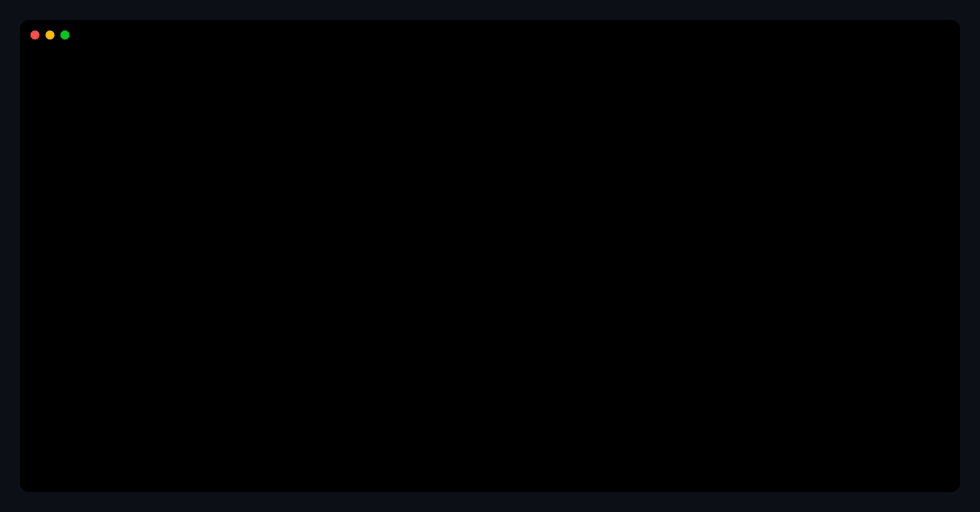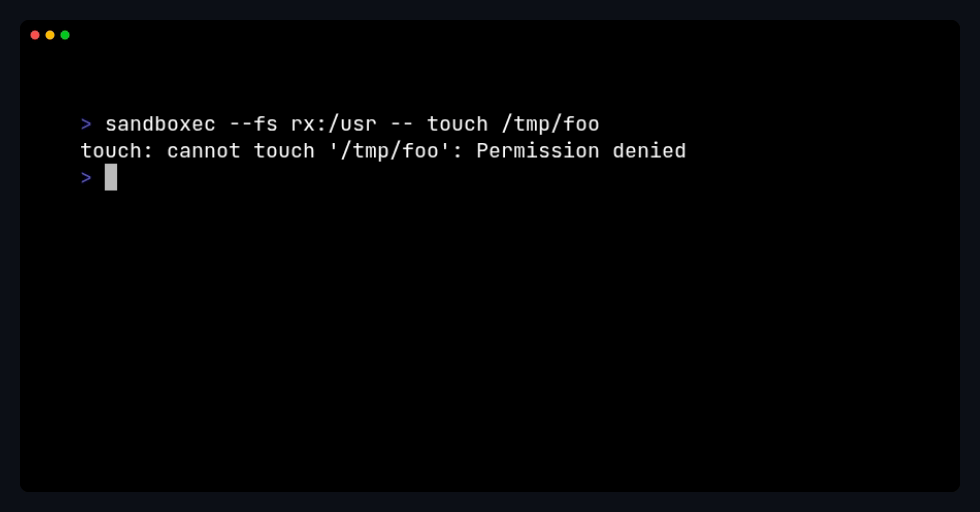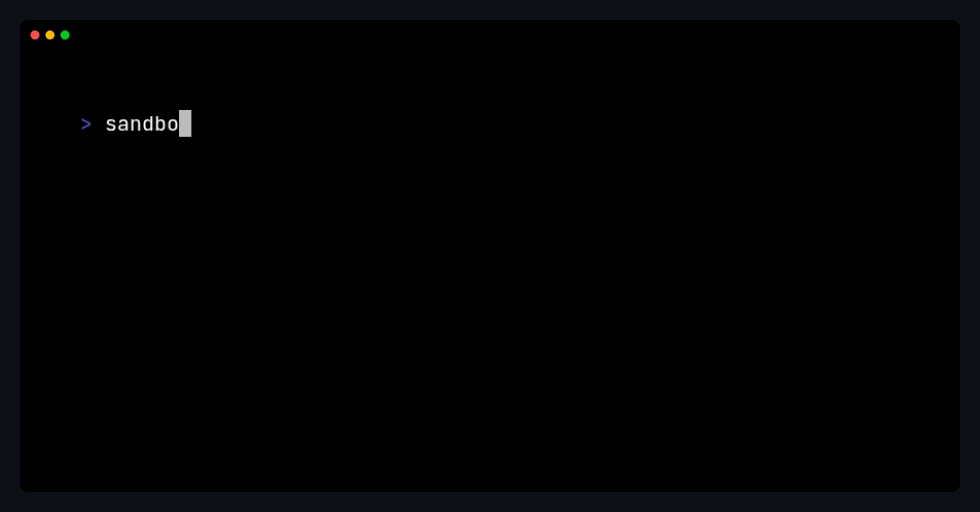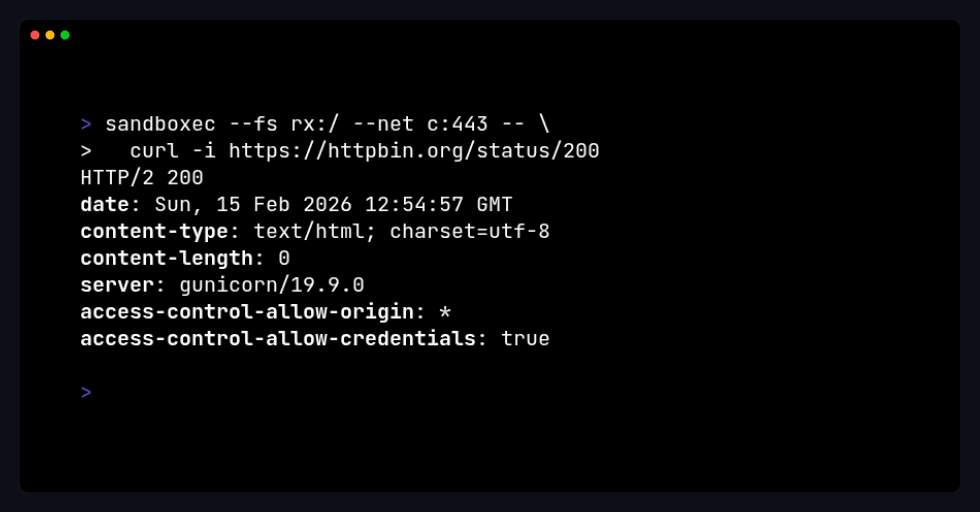 sandboxec/sandboxec
A lightweight command sandbox for Linux, secure-by-default, built on Landlock.
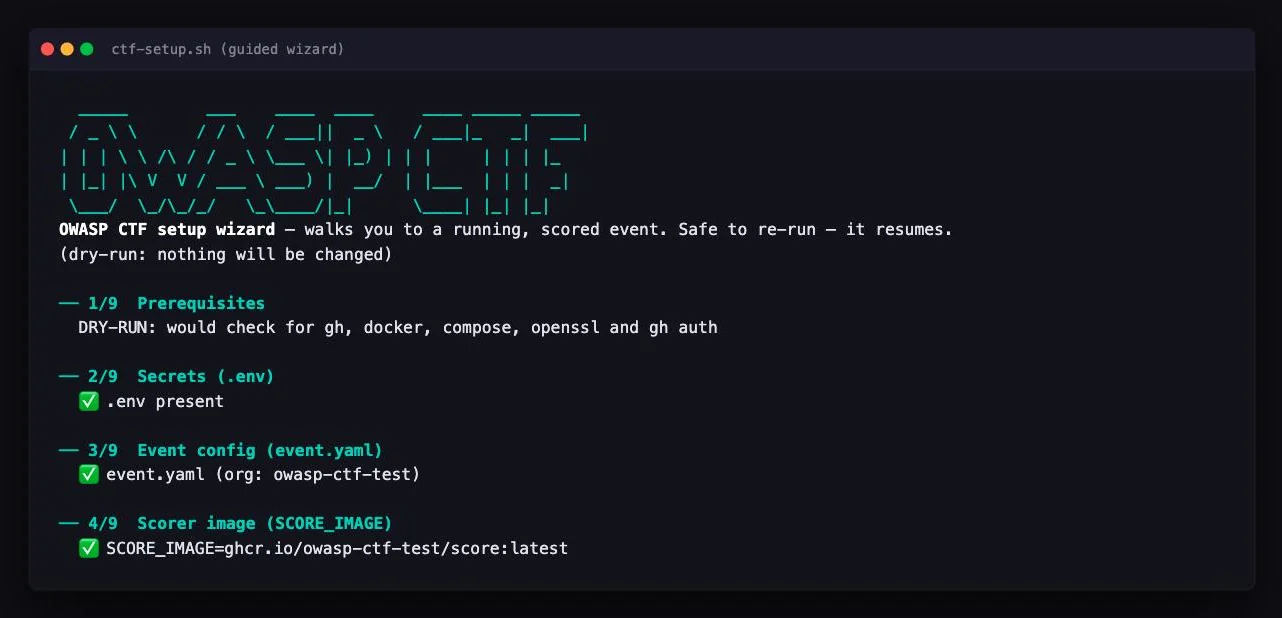 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
 withsecurelabs/amsidetection
Proof-of-concept tool for detecting AMSI (Antimalware Scan Interface) bypasses and malicious in-memory script activity on Windows endpoints.
 infobyte/distro_checker
Cross Distribution Exploit Testing
 fastfire/ioc_attack_esxi_feb_2023
Collection of IoCs available and related to attacks on ESXi infrastructures that occurred as of Friday February 3, 2023.
 javuto/nbox-pwnage
Here comes the paintrain!
 hassham1/cve-2026-89274-wp-recipe-maker-poc
Docker validation lab and Python PoC for CVE-2026-89274, proving arbitrary shortcode execution in WP Recipe Maker <= 10.8.1 via rating-comment…