
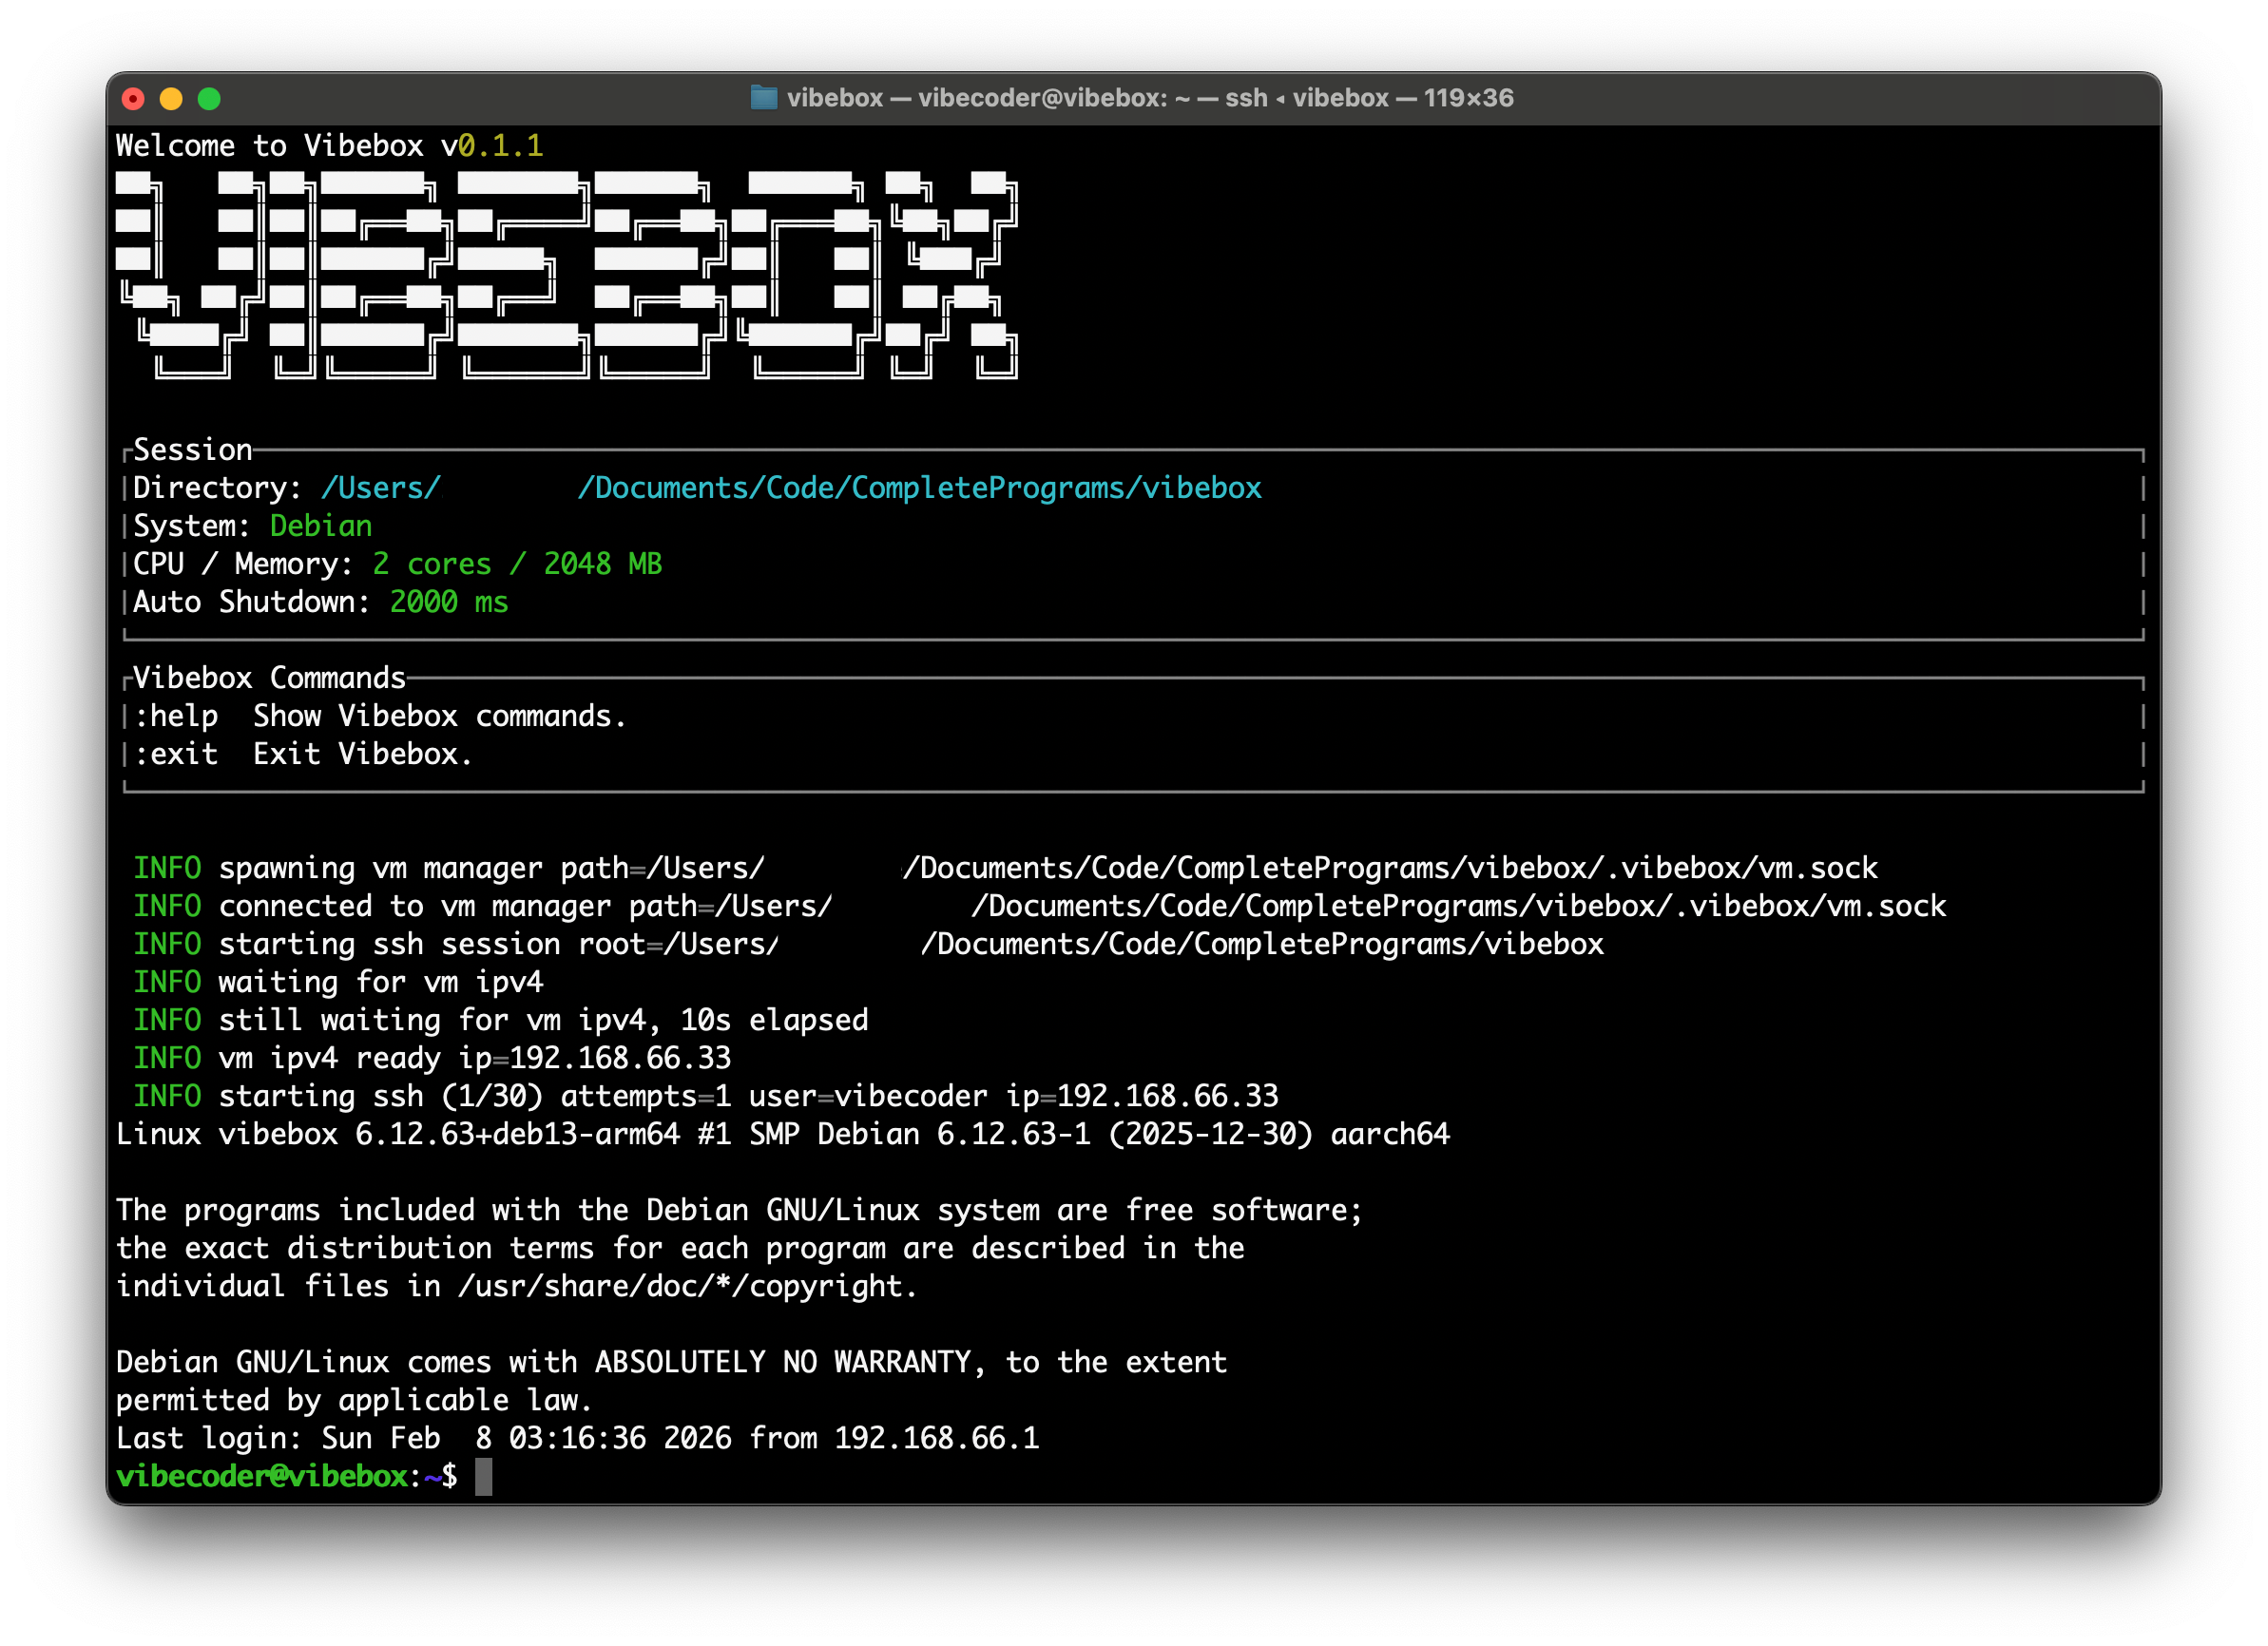
vibebox
 robcholz/vibebox
Ultrafast CLI on Apple Silicon macOS for fast, sandboxed development and LLM agents.
ai-securitycontainer-securitydevsecops+3
robcholz/vibeboxUltrafast CLI on Apple Silicon macOS for fast, sandboxed development and LLM agents.
 michaels1011/ephemora-cell
Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
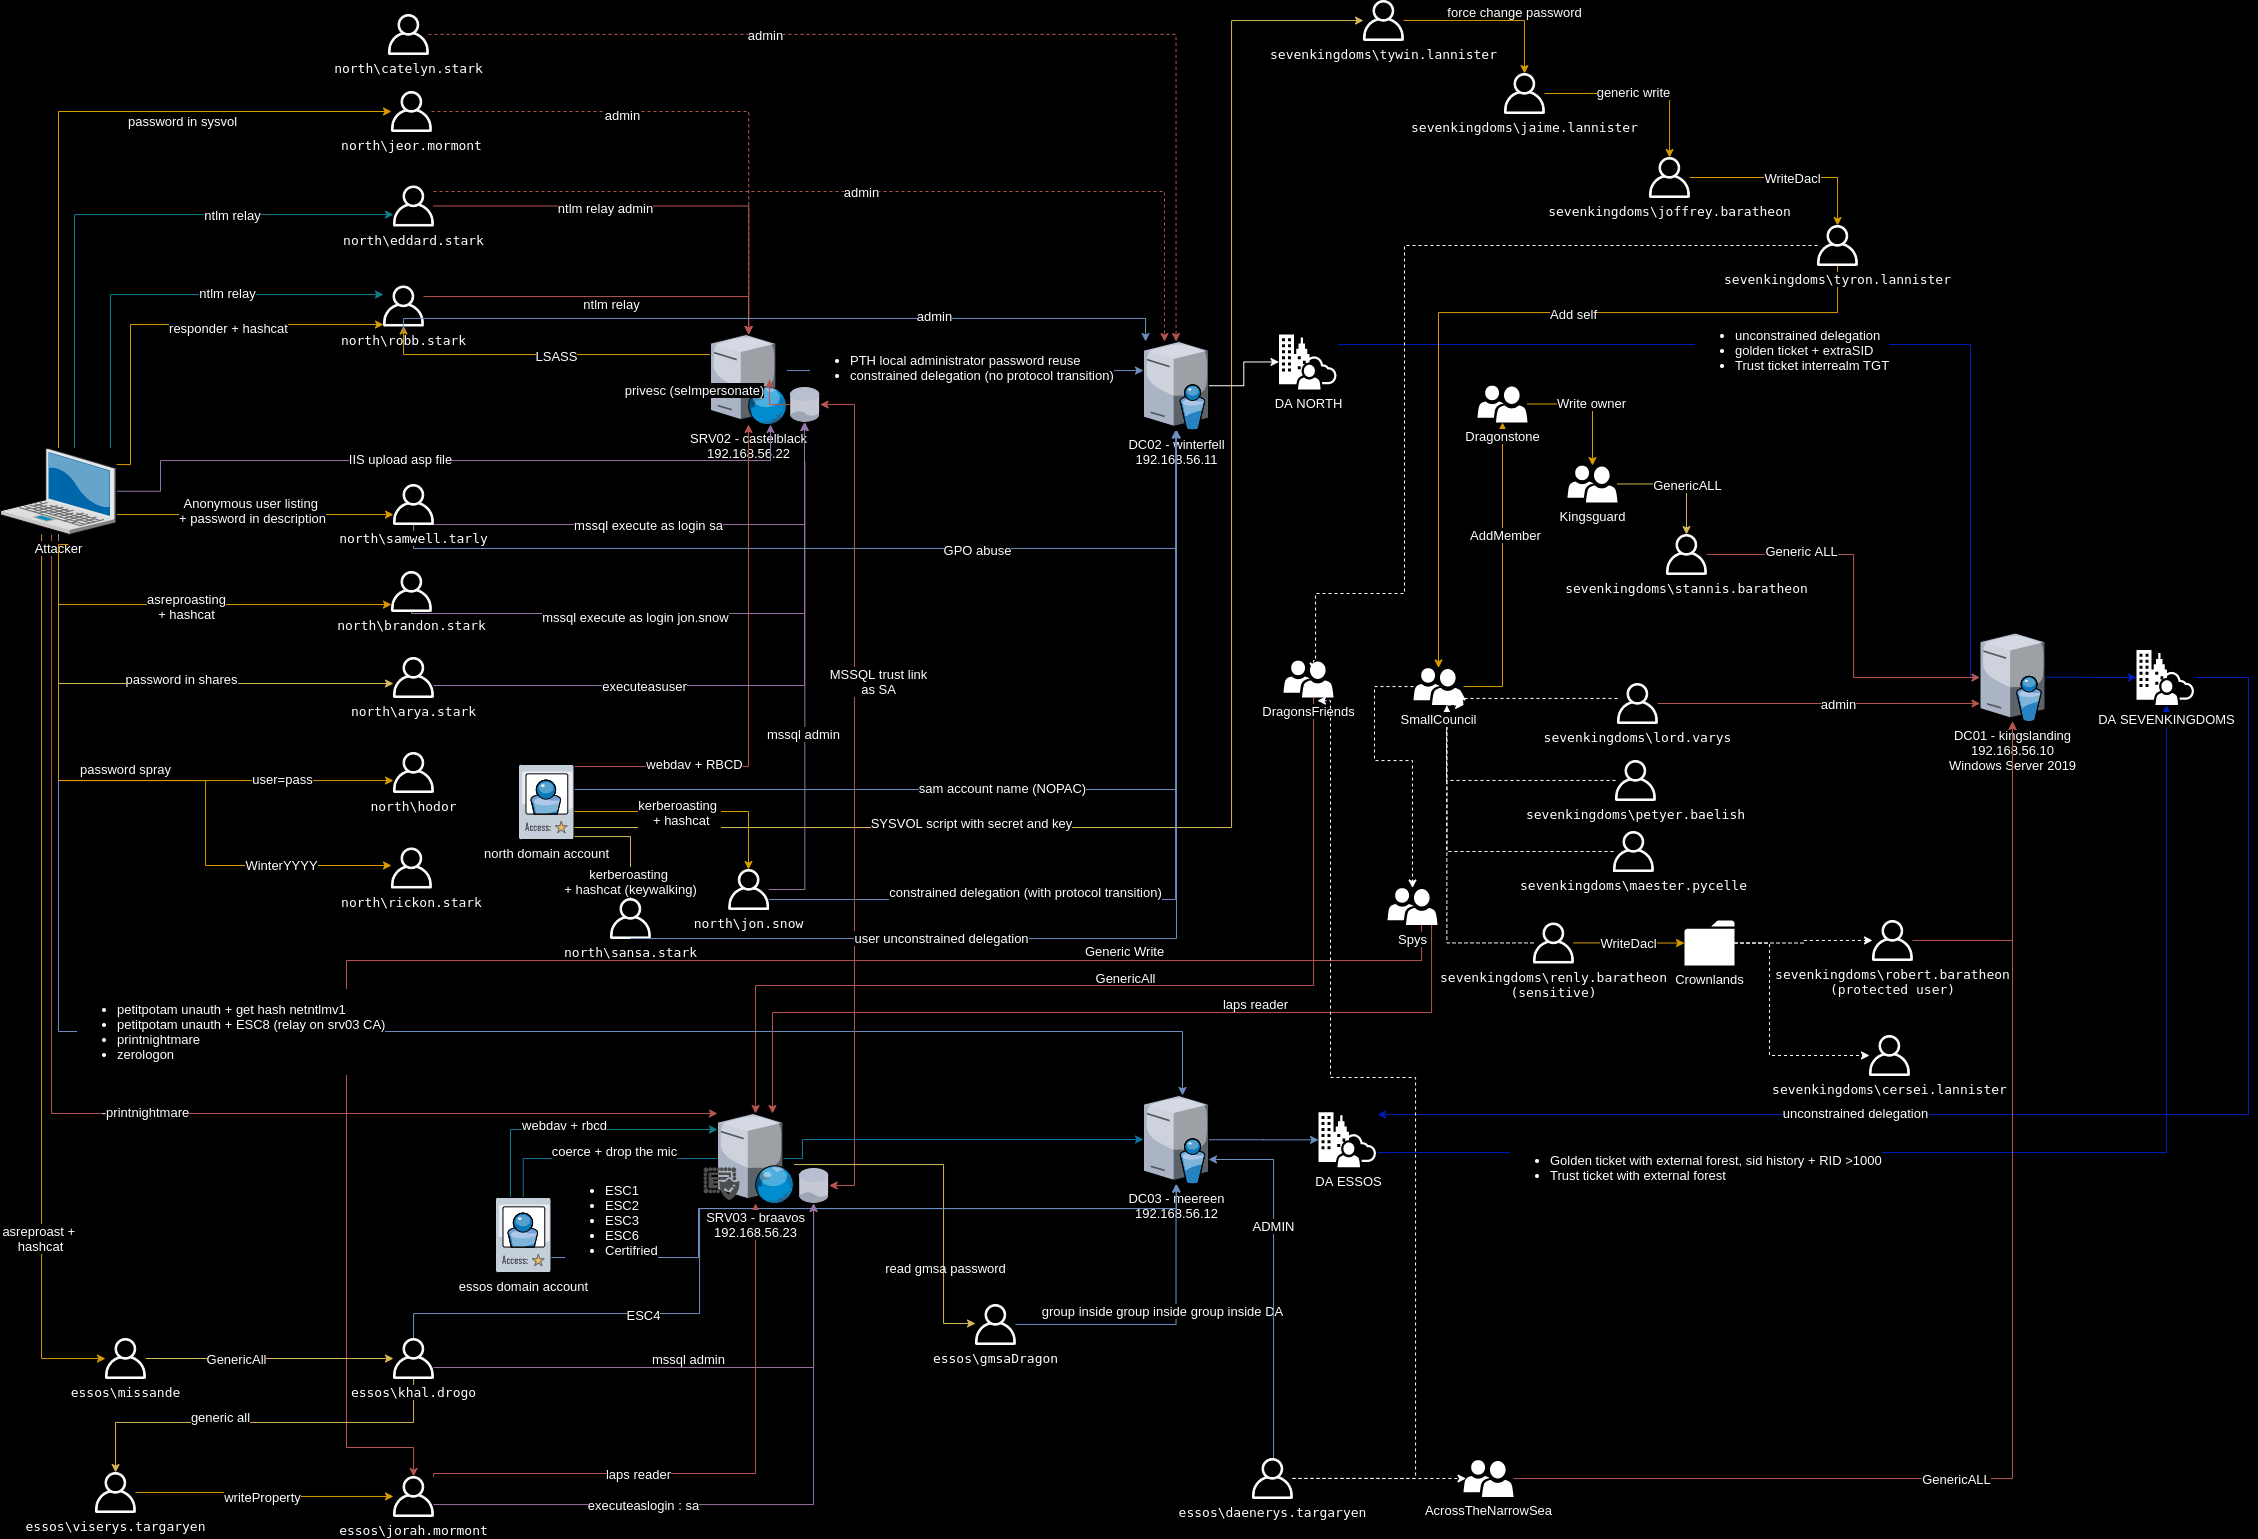 lkarlslund/deploy-goad
Script to install prerequisites for deploying GOAD on Ubuntu Linux 22.04
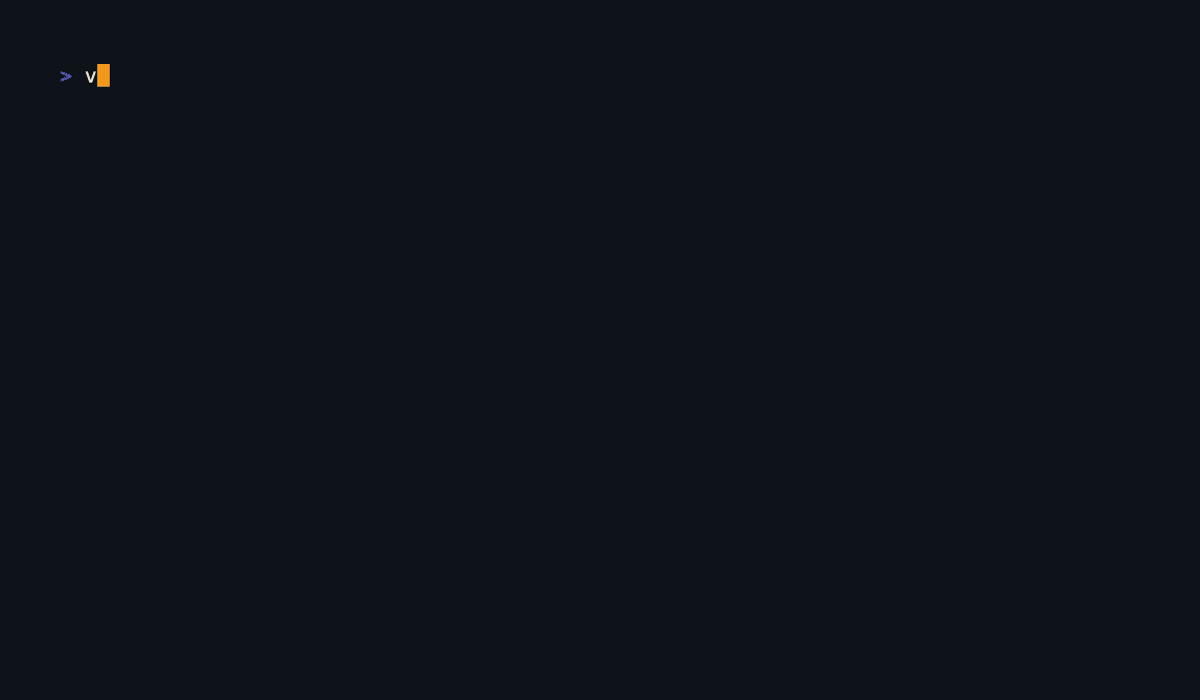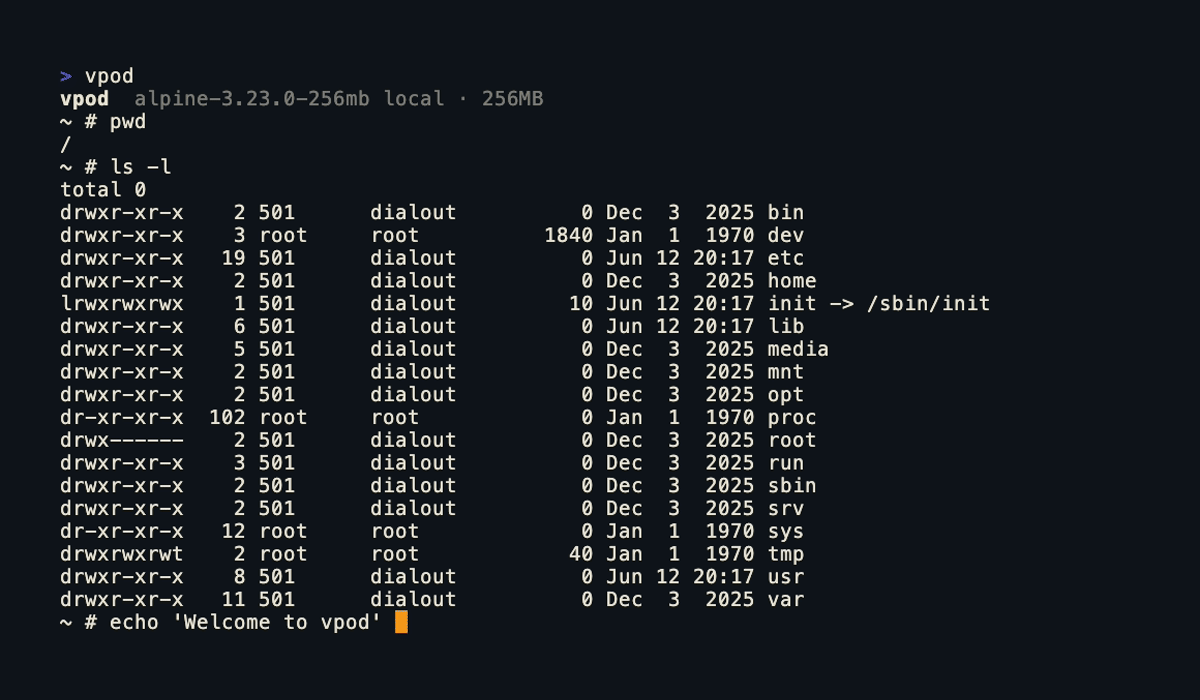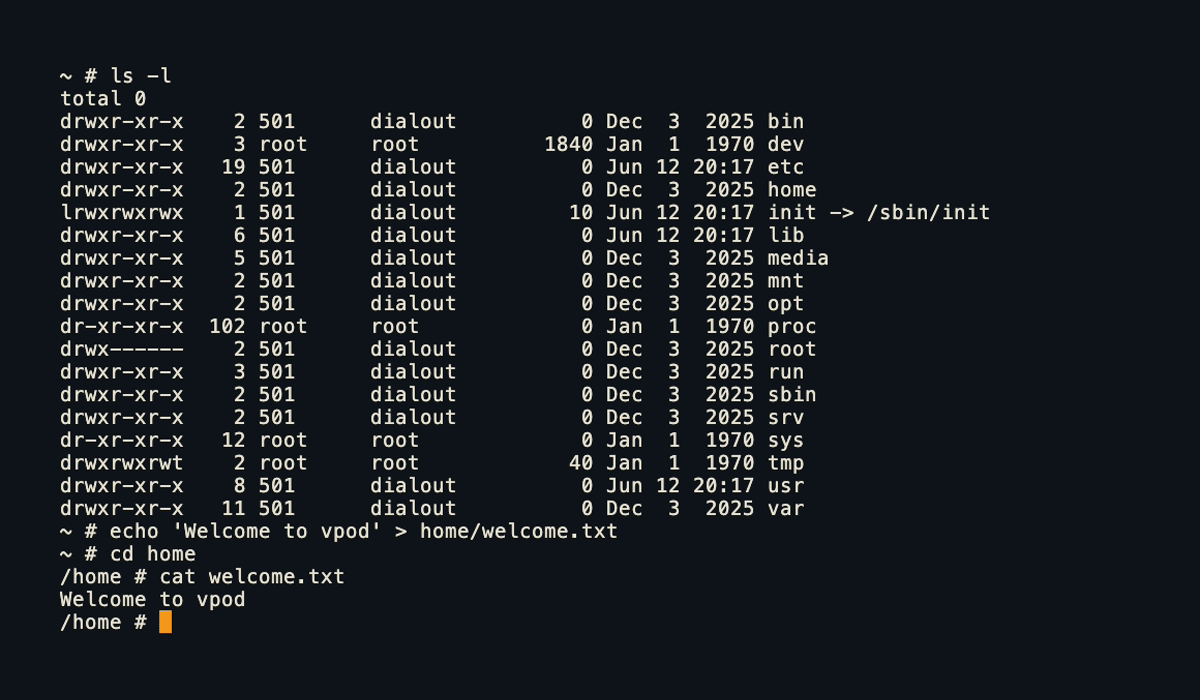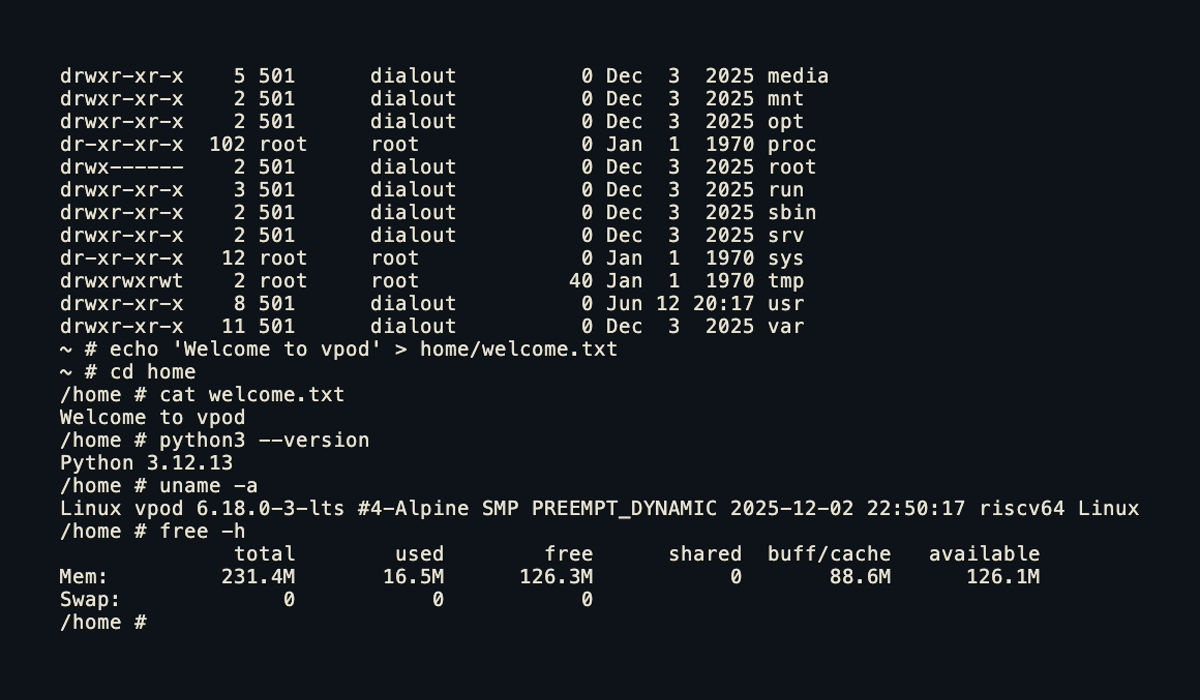 capsulerun/vpod
Lightweight, secure Linux sandboxes for untrusted processes. Runs in the browser and on the server.
 pho5nix/red-team-goad-lab-proxmox
Build guide for Red Teaming home lab. GOAD lab setup in Proxmox and pfSense, Operator/C2 and Redirectors.
 synacktiv/mofos
Virtual machines manipulation framework
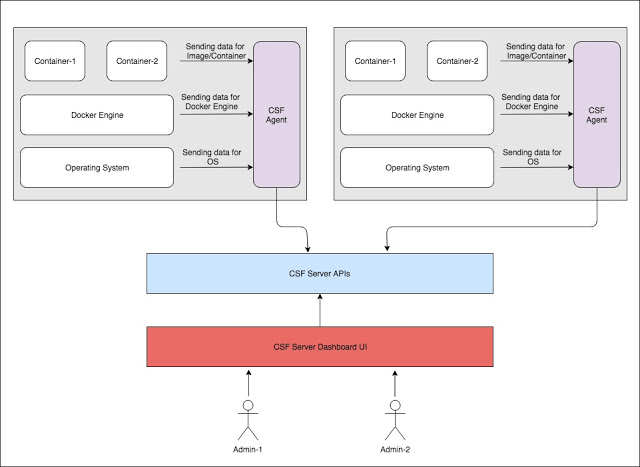 armourbird/csf
ArmourBird CSF - Container Security Framework
 angelorc/vmsan
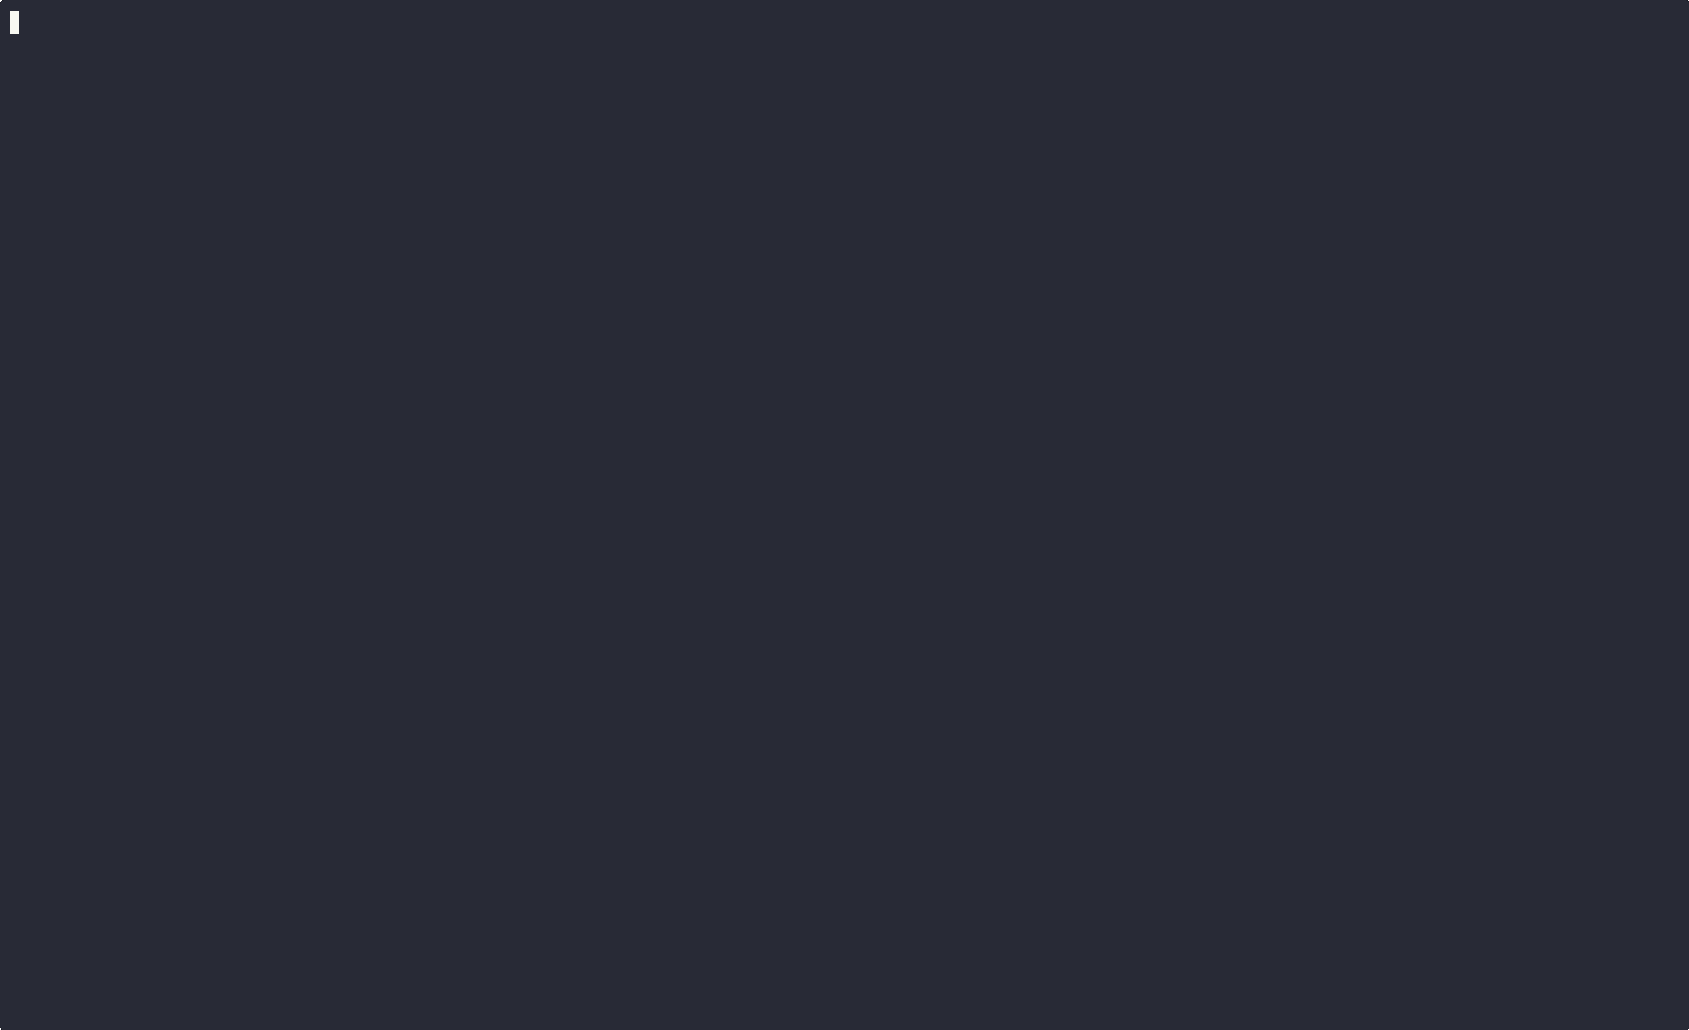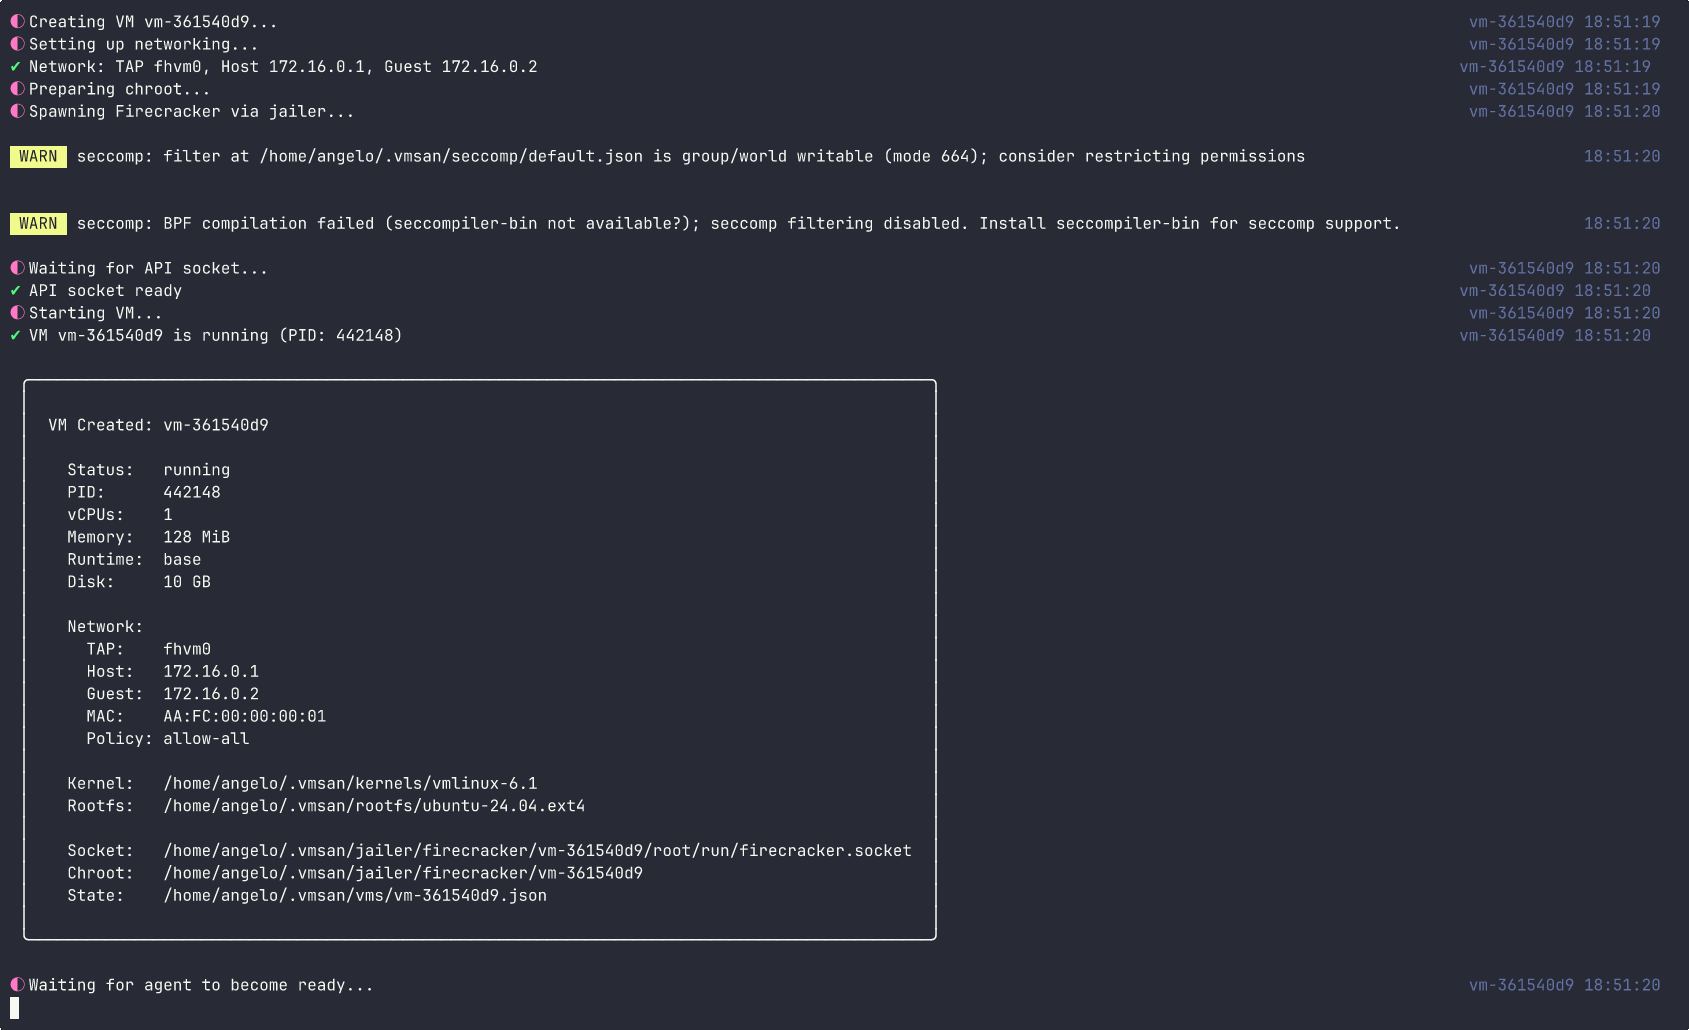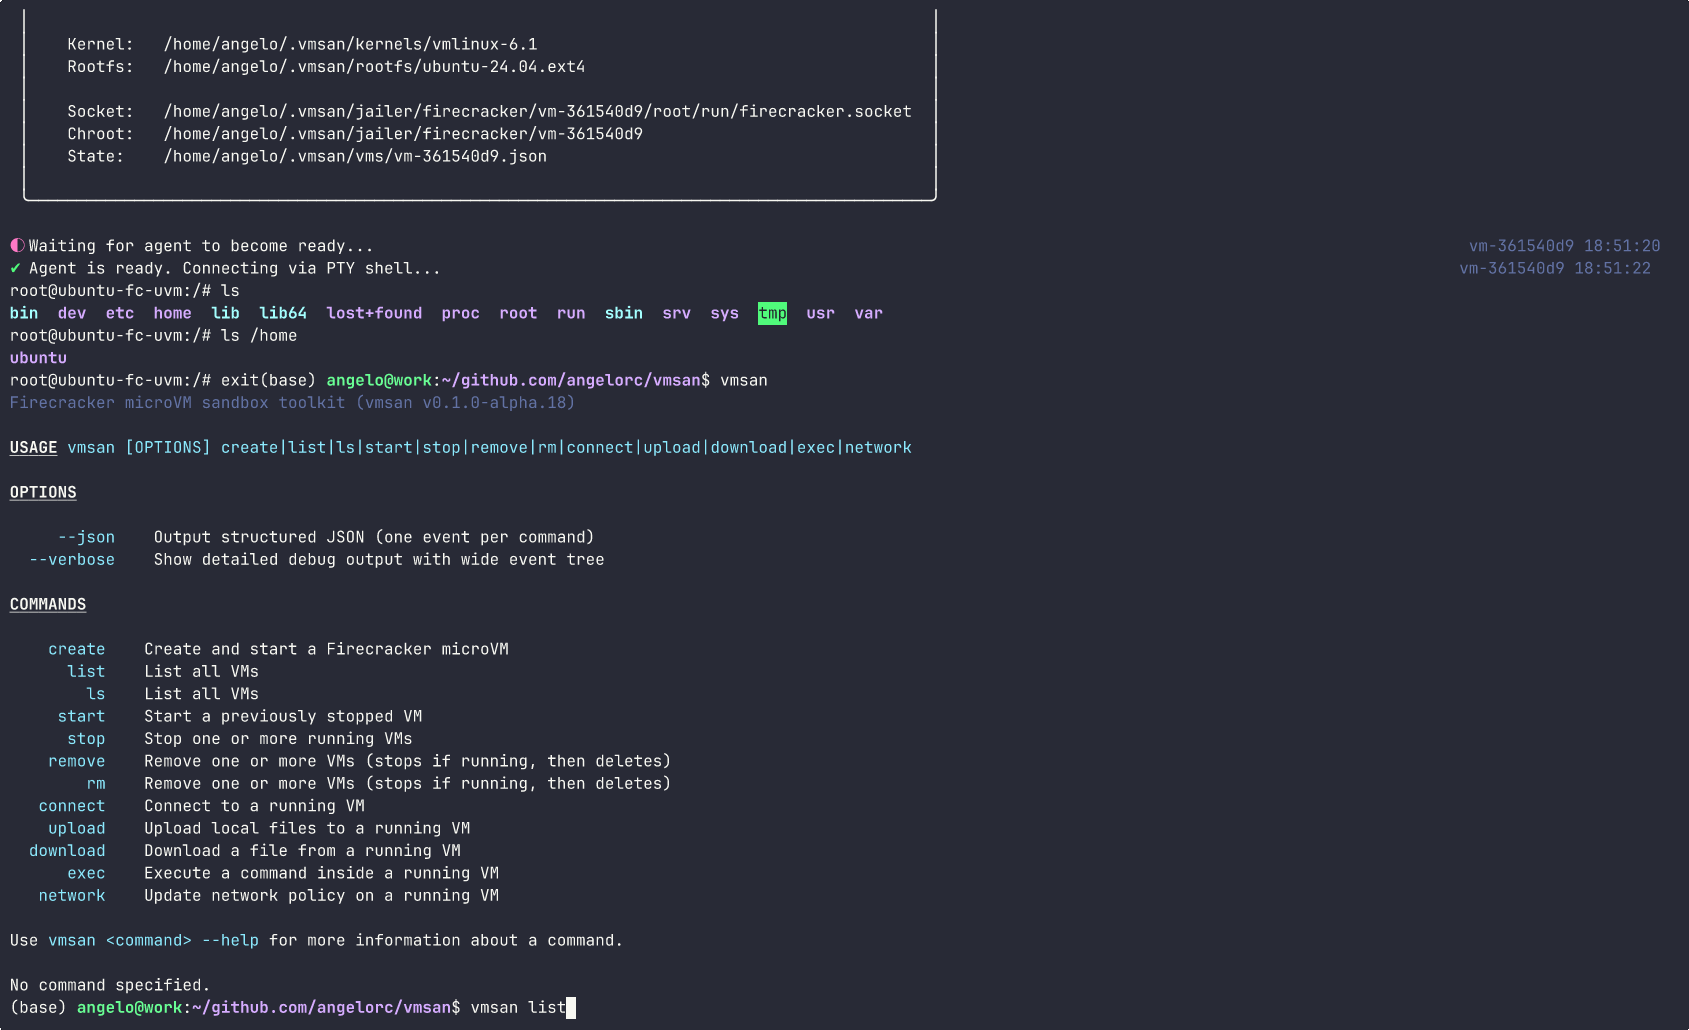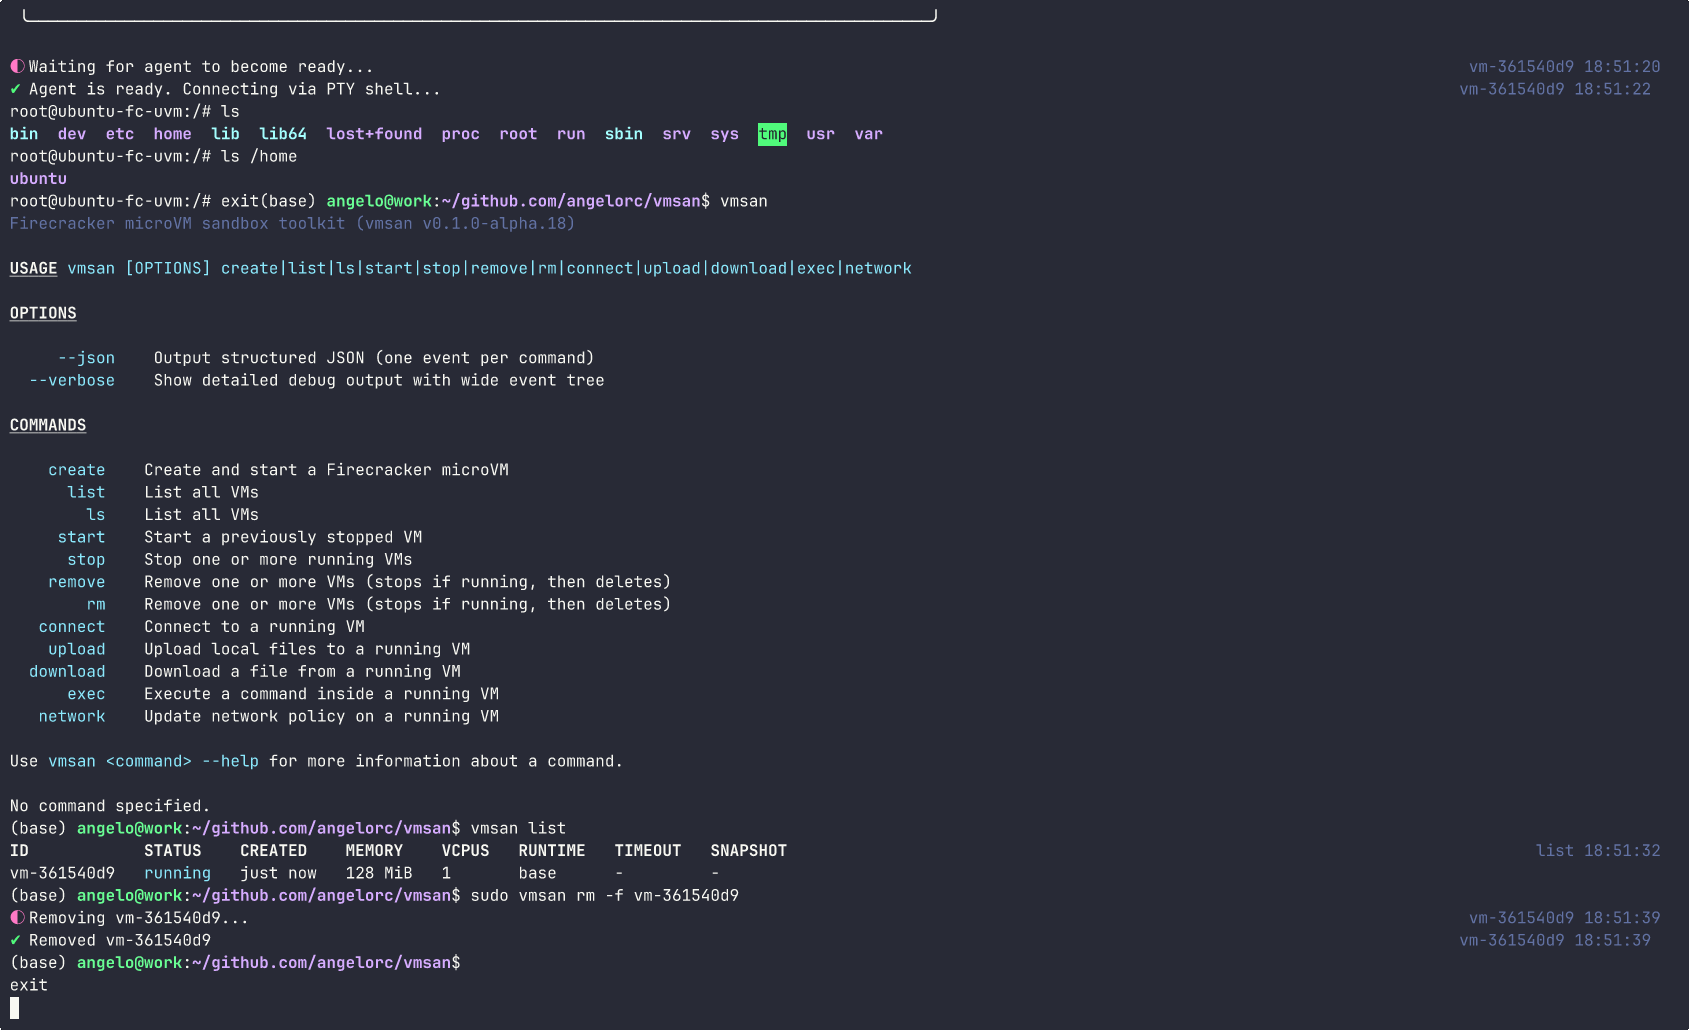
Firecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.
 mathaix/openclawmachines
Manage OpenClaw in your team (Enterprise) by providing it compute infrastructure, tool integration, Authentication and security primitives
 guneykabel/cve-2026-85706
Python PoC exploit for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE via Workhorse path-encoding bypass, with writeup and…
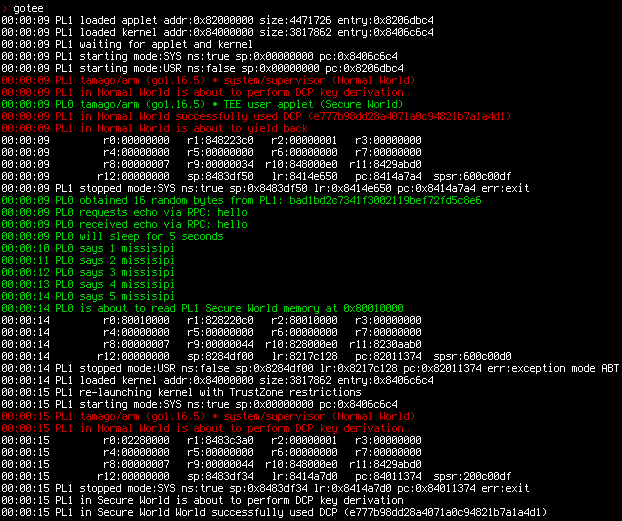 usbarmory/gotee-example
GoTEE - example application
 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
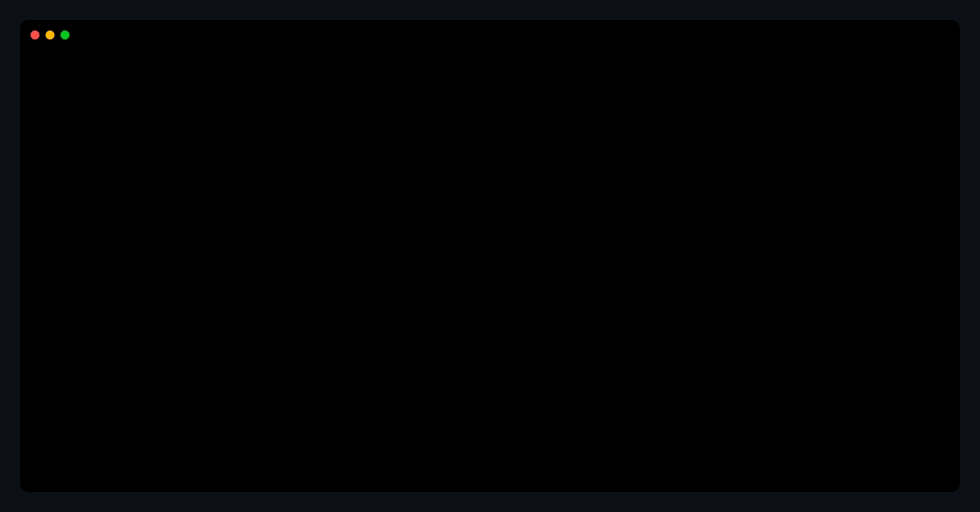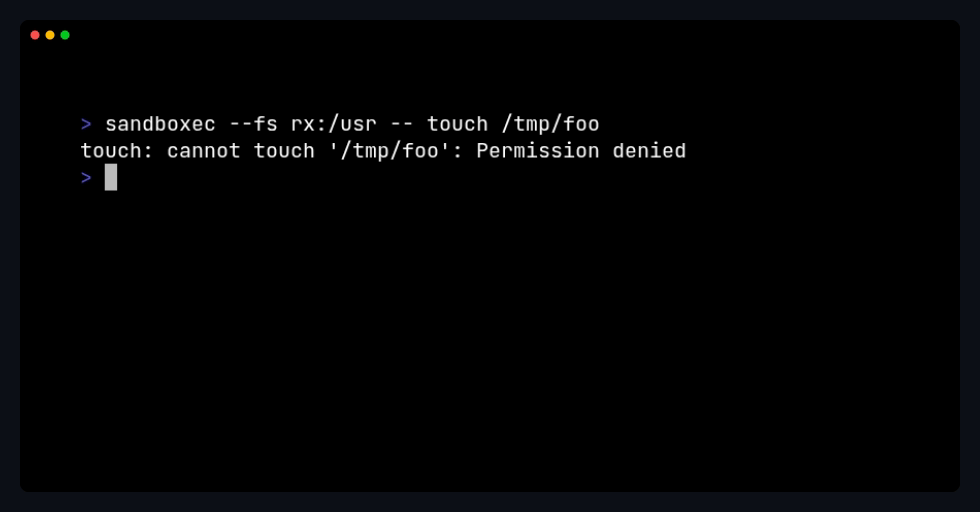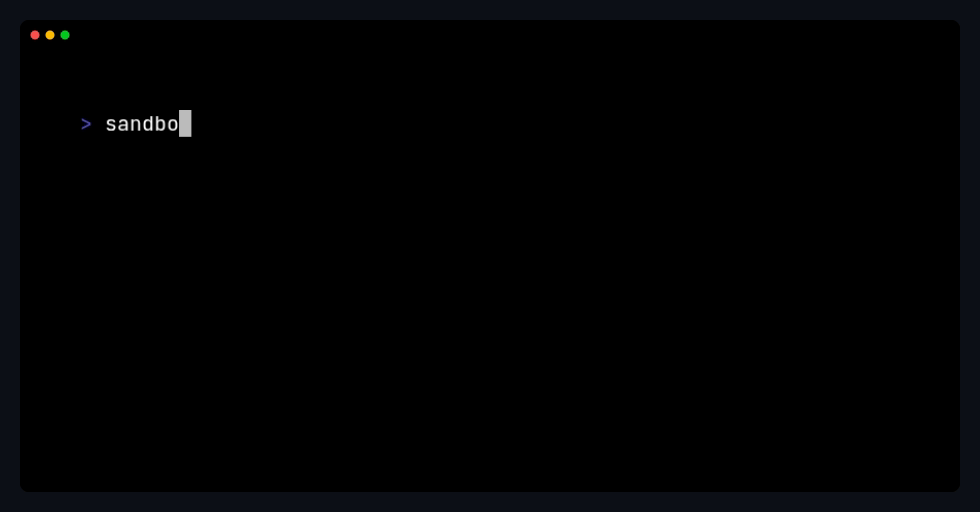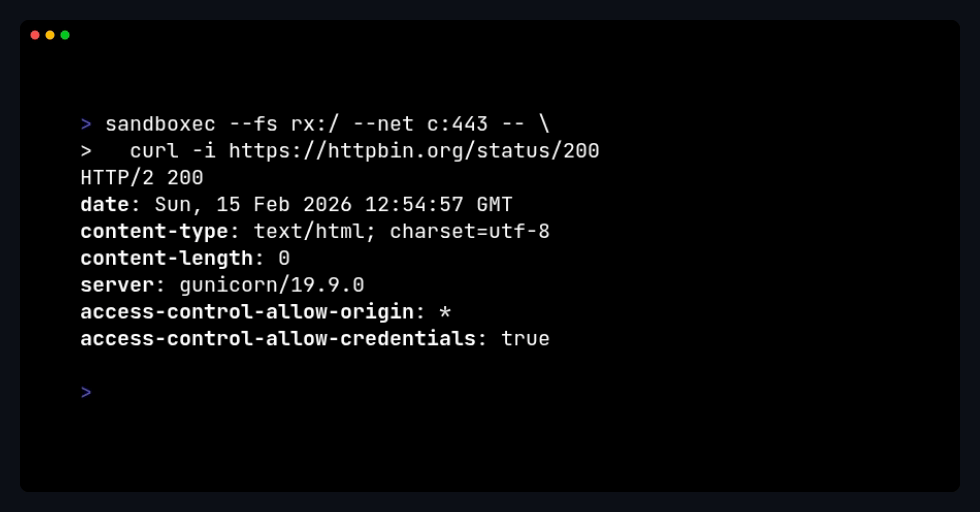 sandboxec/sandboxec
A lightweight command sandbox for Linux, secure-by-default, built on Landlock.
 falconforceteam/falcondash
Azure workbook dashboard that visualizes and explores detection performance metrics, helping security teams measure and proactively maintain their…
 top-celestial-company-ltd/dros-vep-lite
Open-source, 100% reproducible AI Agent Runtime Security Benchmark & Sandbox Environment (RFC-010 Draft Protocol).
 tc4dy/cve-2026-82329-poc-exploit
Exploit and detection toolkit for CVE-2026-82329, a JFrog Artifactory auth bypass. Forges join JWTs to mint admin tokens; includes a non-intrusive…