
vpod
 capsulerun/vpod
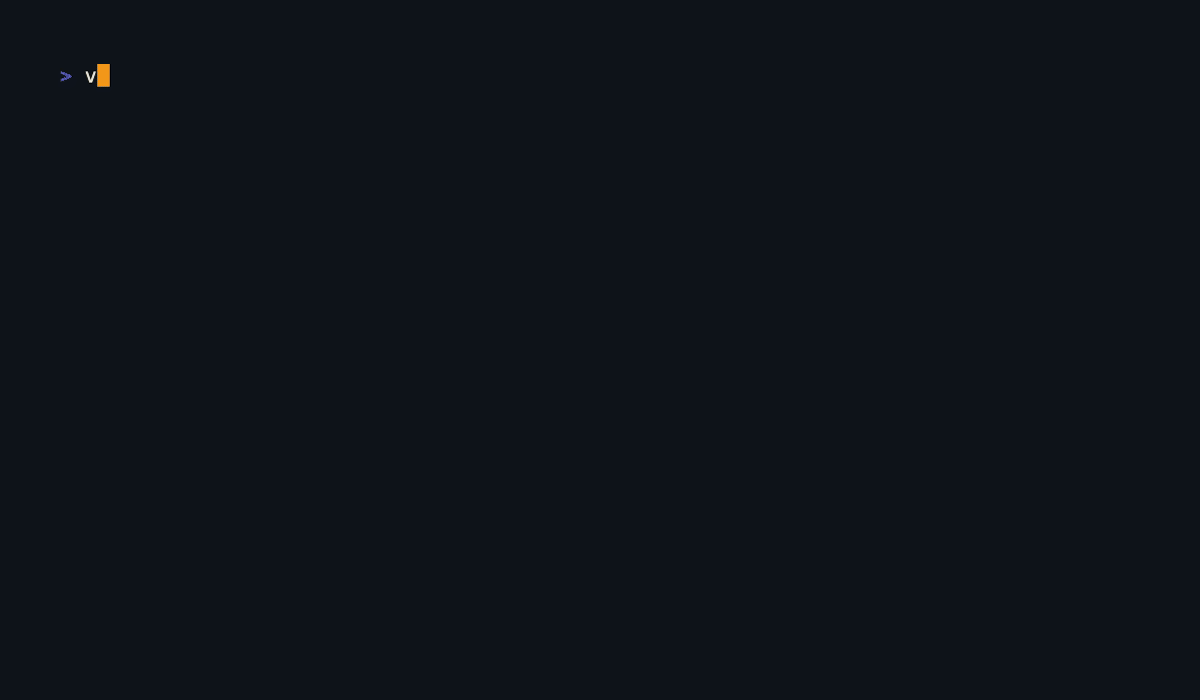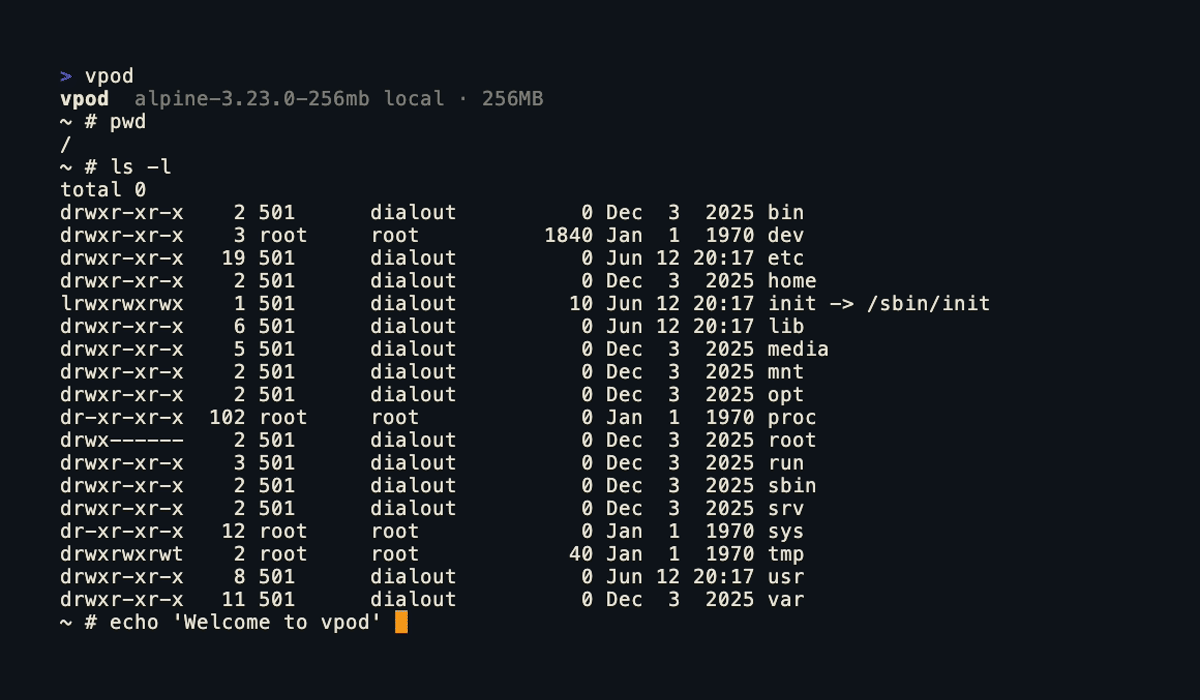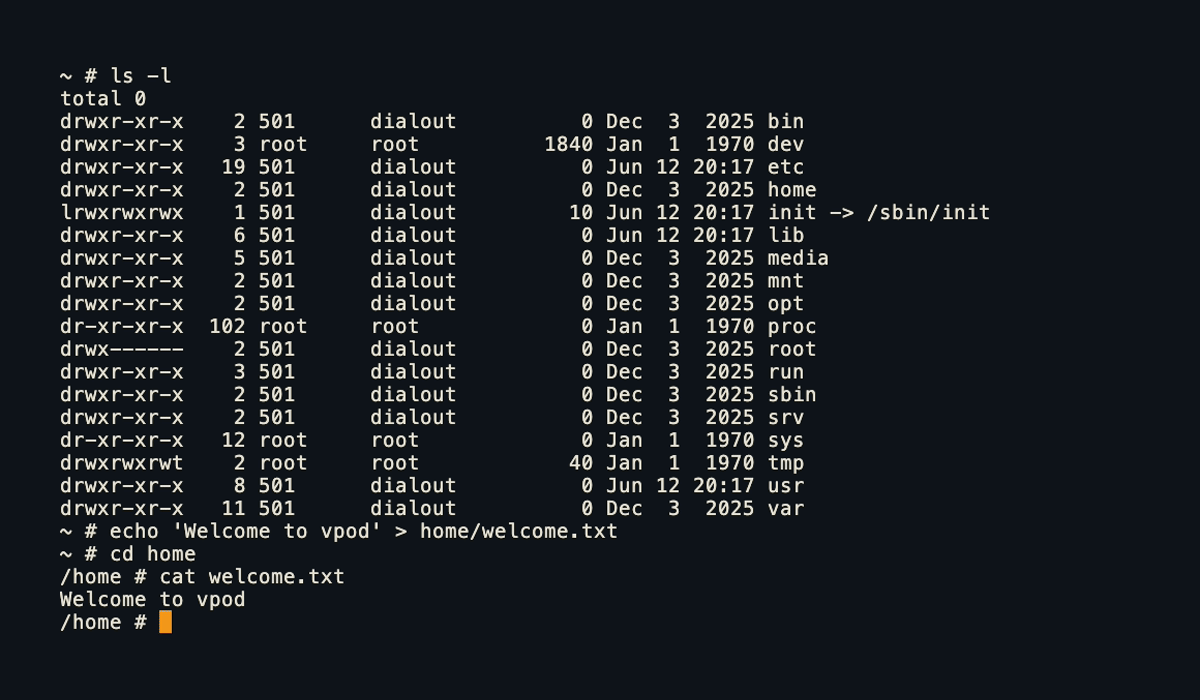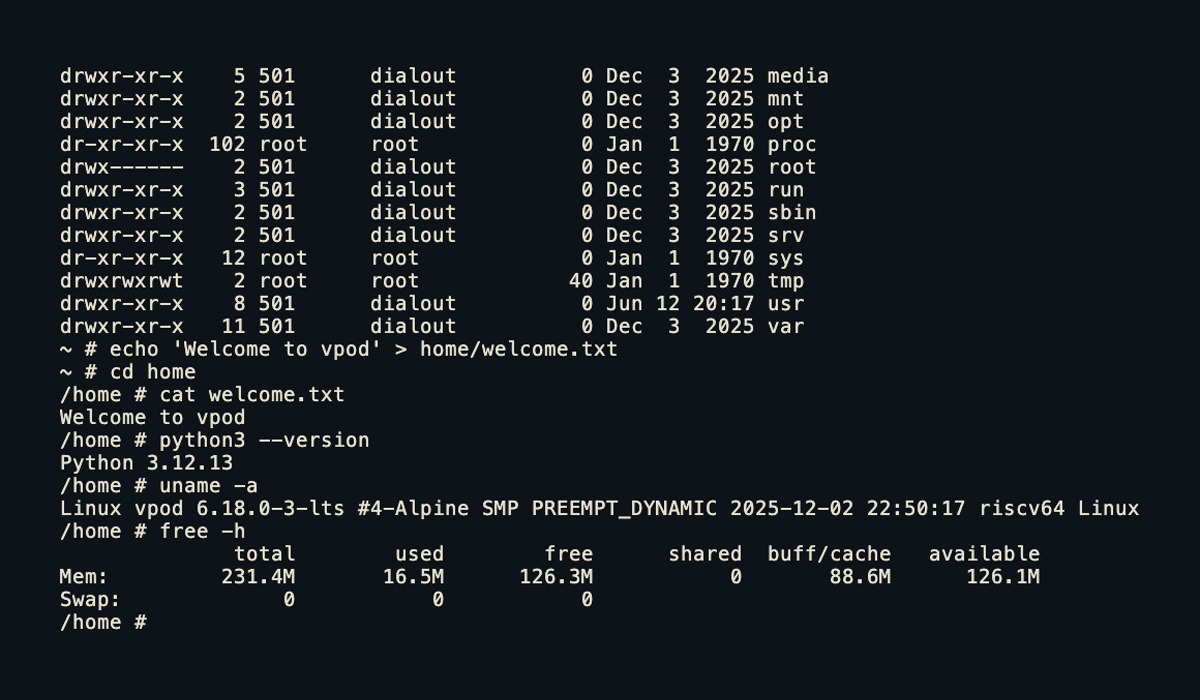
Lightweight, secure Linux sandboxes for untrusted processes. Runs in the browser and on the server.
ai-securitycontainer-securitydefensive-tools+3
capsulerun/vpodLightweight, secure Linux sandboxes for untrusted processes. Runs in the browser and on the server.
 wkoszek/emuko
RISC-V emulator in Rust that boots Linux with JIT on ARM64/x86_64 and Sv39 virtual memory
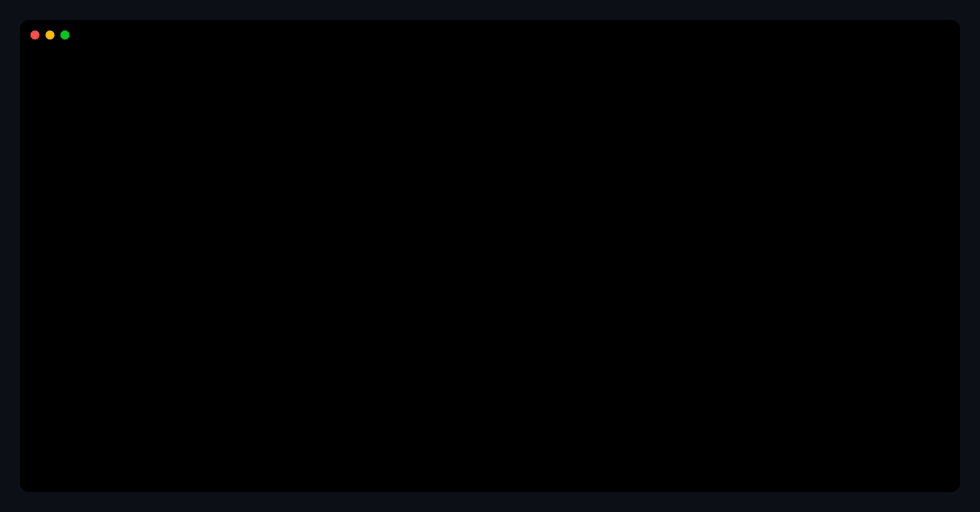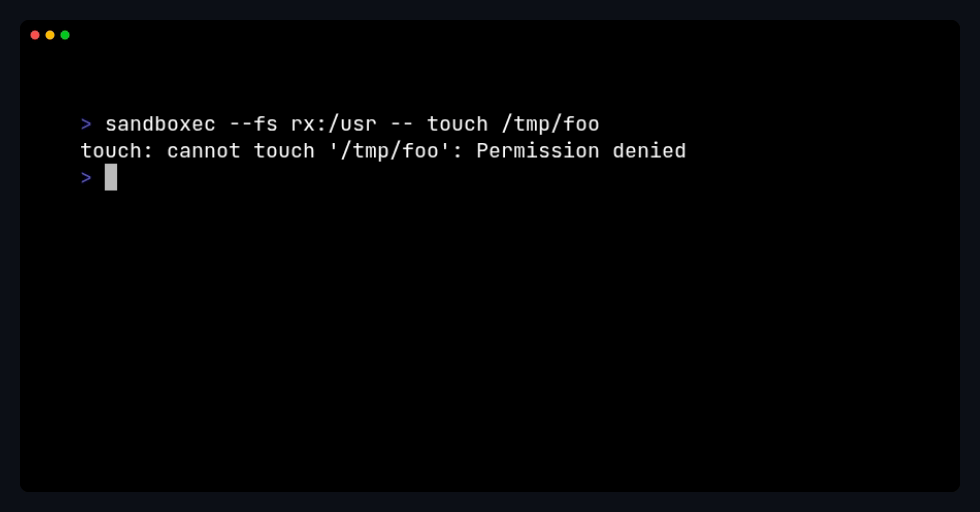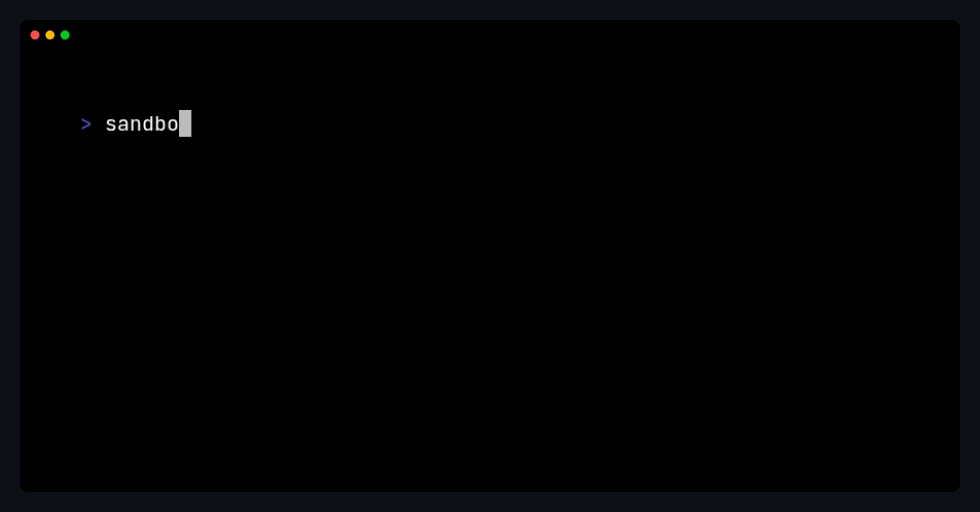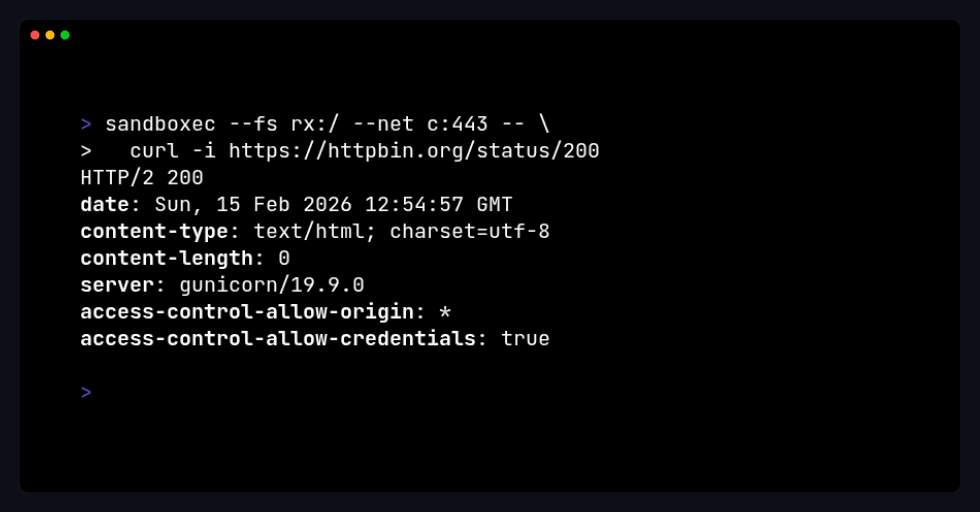 sandboxec/sandboxec
A lightweight command sandbox for Linux, secure-by-default, built on Landlock.
 withsecurelabs/amsidetection
Proof-of-concept tool for detecting AMSI (Antimalware Scan Interface) bypasses and malicious in-memory script activity on Windows endpoints.
 fastfire/ioc_attack_esxi_feb_2023
Collection of IoCs available and related to attacks on ESXi infrastructures that occurred as of Friday February 3, 2023.
 trustsig-eu/wasm2c-tableflip
wasm2c sandbox escape. An untrusted WebAssembly module breaks out of the generated C sandbox and executes an arbitrary shell command on the host.
 trungnguyen1909/qemu-t8030
iPhone 11 emulated on QEMU
 opposum0112/cusimanse
Composable research-contract and YAML-recipe framework for agent-operated security experiments on disposable compute
 vishnunandan555/cordon
Run any command inside a restricted filesystem view on Linux
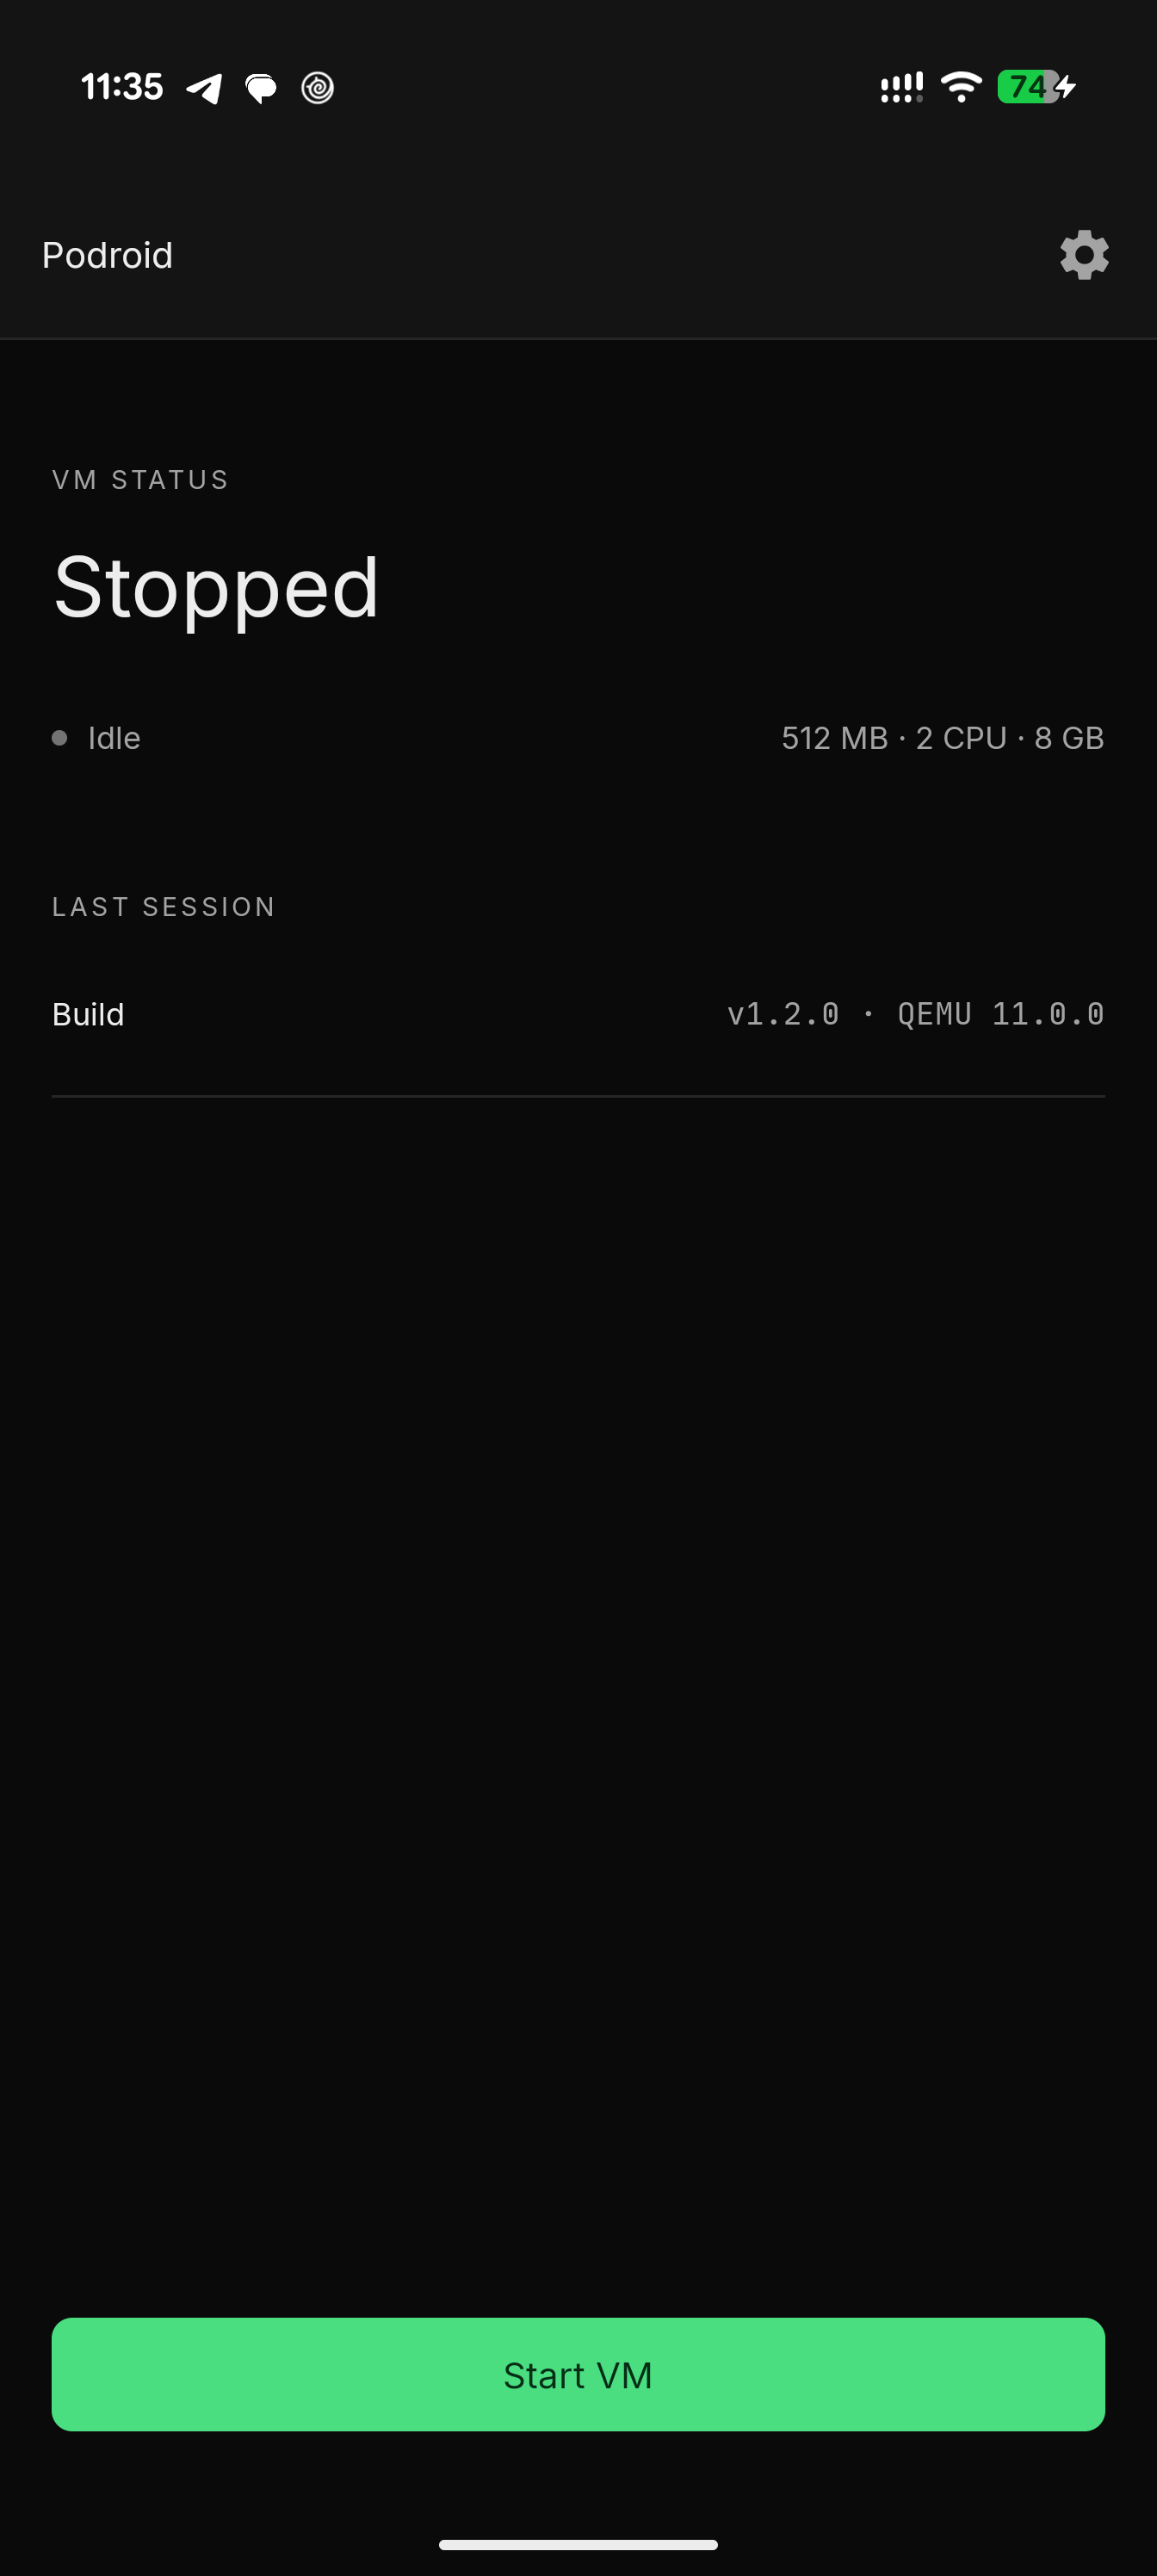 extv/podroid
A rootless Android app that boots Alpine Linux: run containers (Podman/Docker/LXC) and GUI desktop apps.
 flatpak/flatpak
Linux application sandboxing and distribution framework
 cypherpunkarmory/userland
Main UserLAnd Repository
 sinakarvandi/hypervisor-from-scratch
Source code of a multiple series of tutorials about the hypervisor. Available at: https://rayanfam.com/tutorials
 zerobootdev/zeroboot
Sub-millisecond VM sandboxes for AI agents via copy-on-write forking
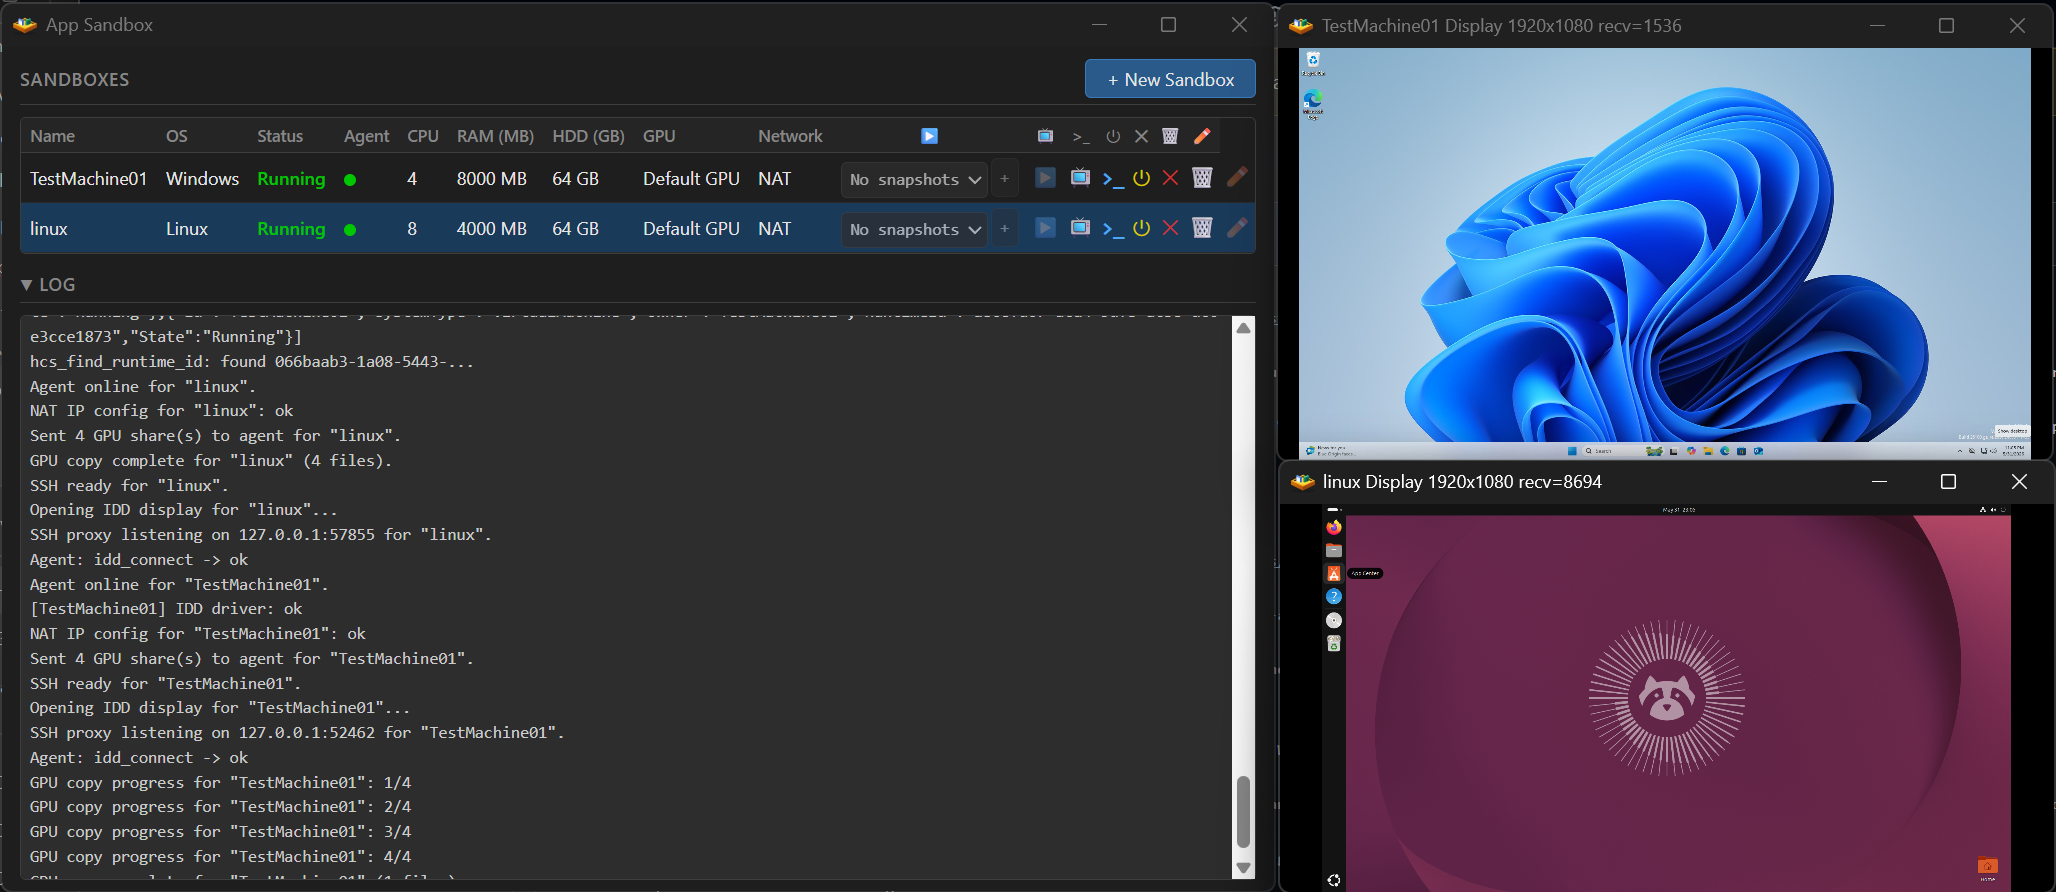 jamesstringer90/appsandbox
Easily create full virtual machines that are sandboxed for development or computer use models.
 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
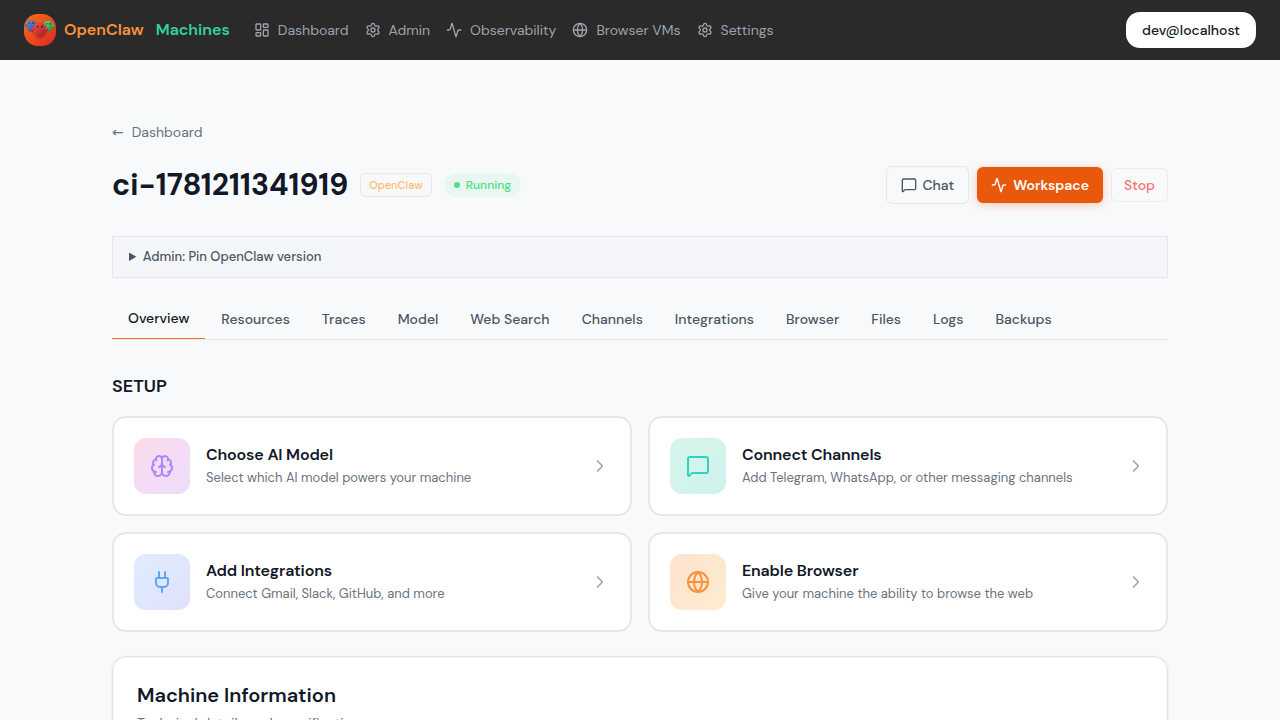 mathaix/openclawmachines
Manage OpenClaw in your team (Enterprise) by providing it compute infrastructure, tool integration, Authentication and security primitives
 eqstlab/cve-2026-49869
PoC and Docker lab for CVE-2026-49869, an unauthenticated RCE in Kestra OSS via an AuthenticationFilter path bypass that allows flow creation and…