
APatch
 bmax121/apatch
The patching of Android kernel and Android system
android-securitymobile-securitypayload-development+4
bmax121/apatchThe patching of Android kernel and Android system
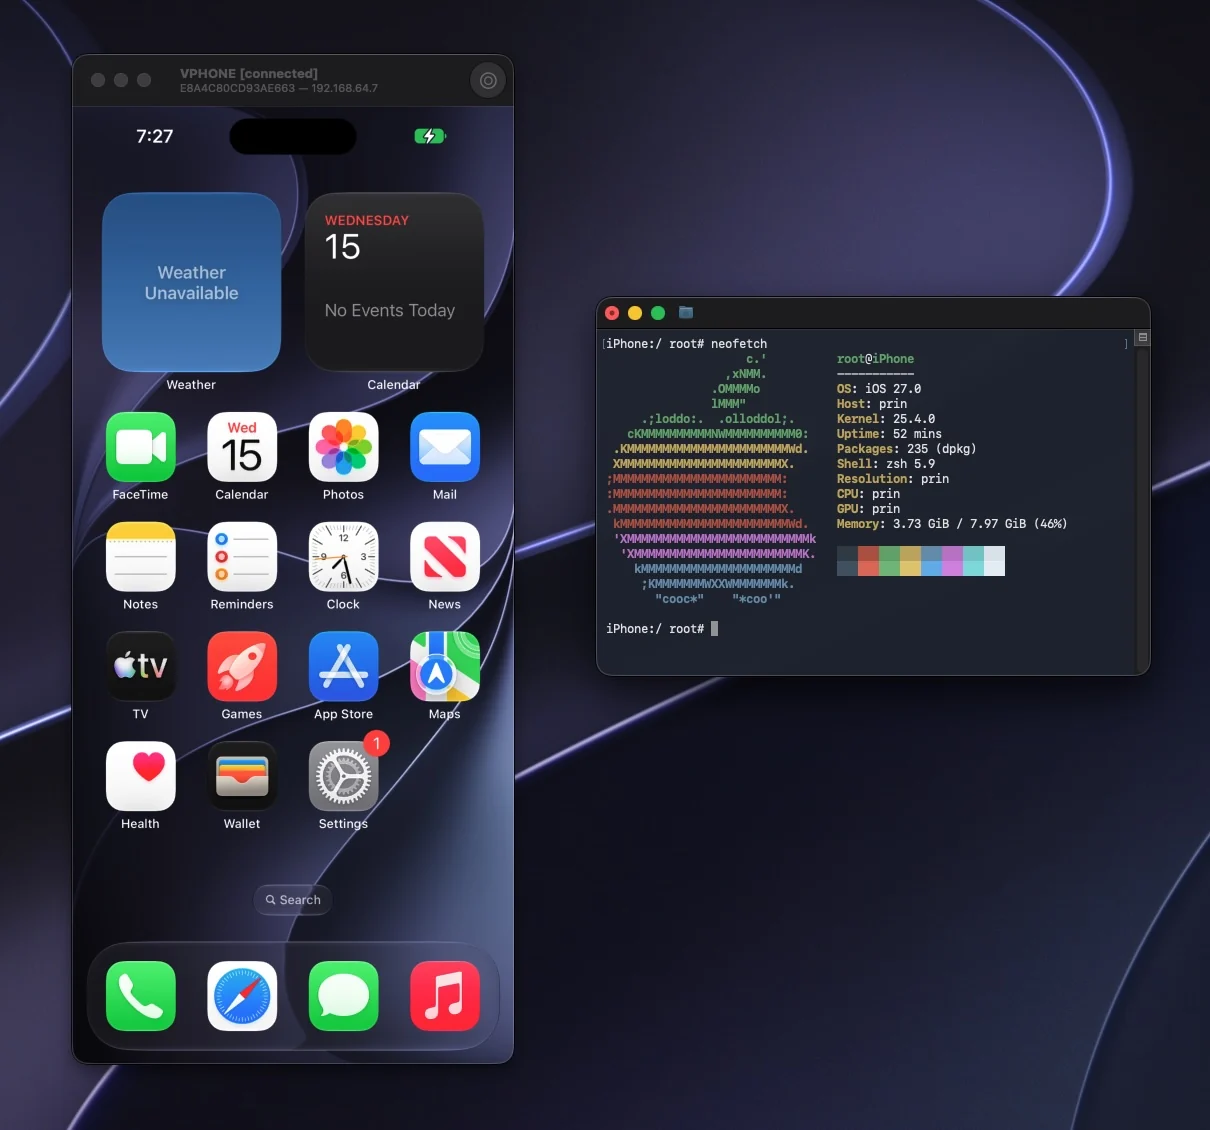 lakr233/vphone-cli
Boot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
 microsoft/litebox
A security-focused library OS supporting kernel- and user-mode execution
 michaels1011/ephemora-cell
Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
 qubesos/qubes-core-admin
Manages the core lifecycle of Qubes OS domains via a Python admin API, handling secure compartmentalization with Xen and exposing an event system for…
 netblue30/firejail
Linux namespaces and seccomp-bpf sandbox
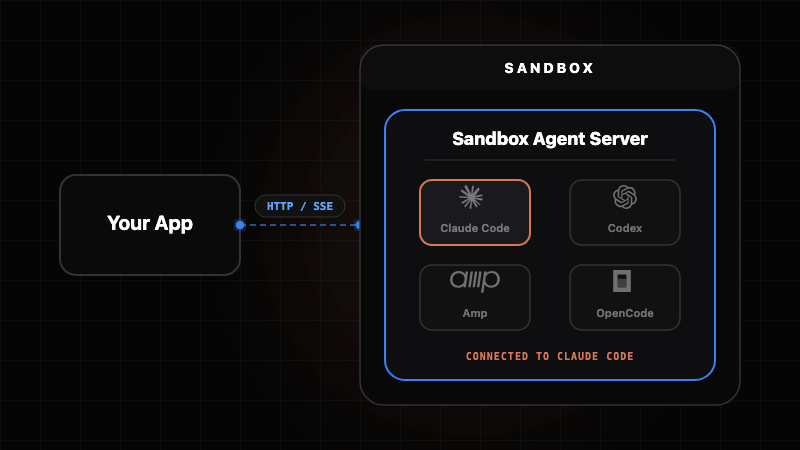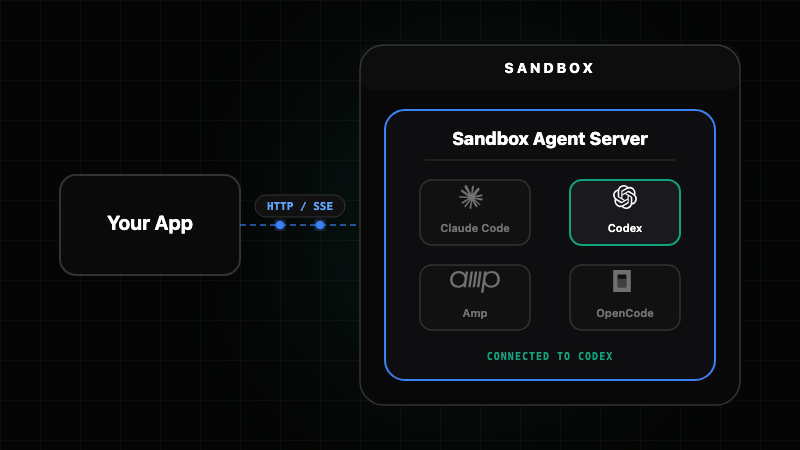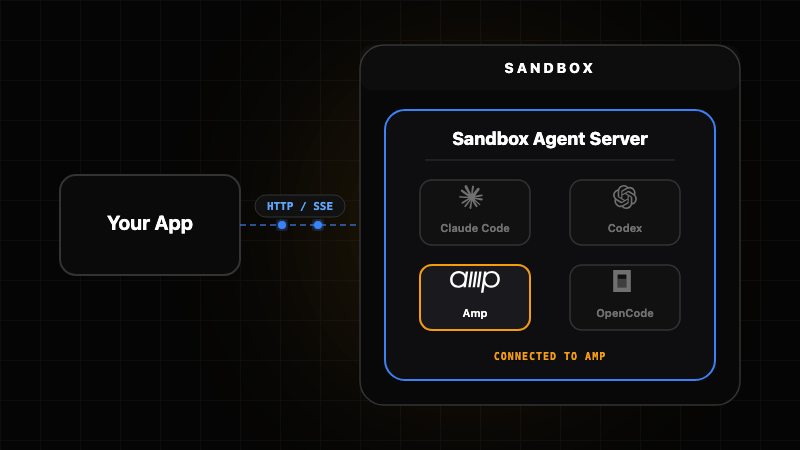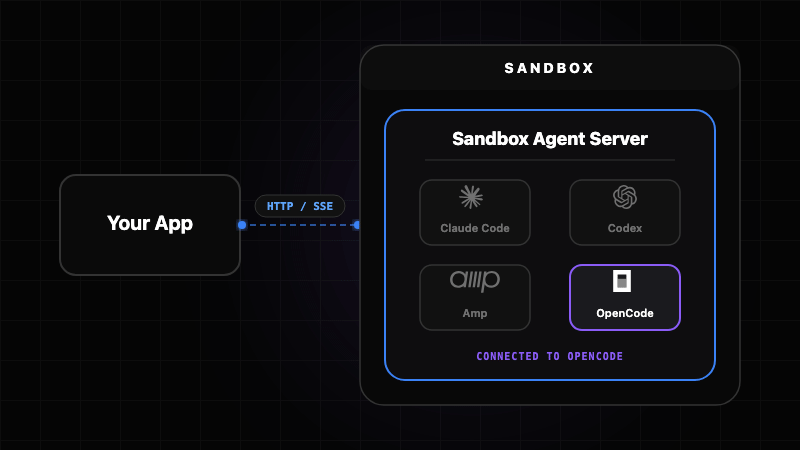 rivet-dev/sandbox-agent
A durable process per agent, with memory that survives restarts
 monad-developers/ultrafuzz
End-to-end agentic smart contract fuzzing and threat hunting
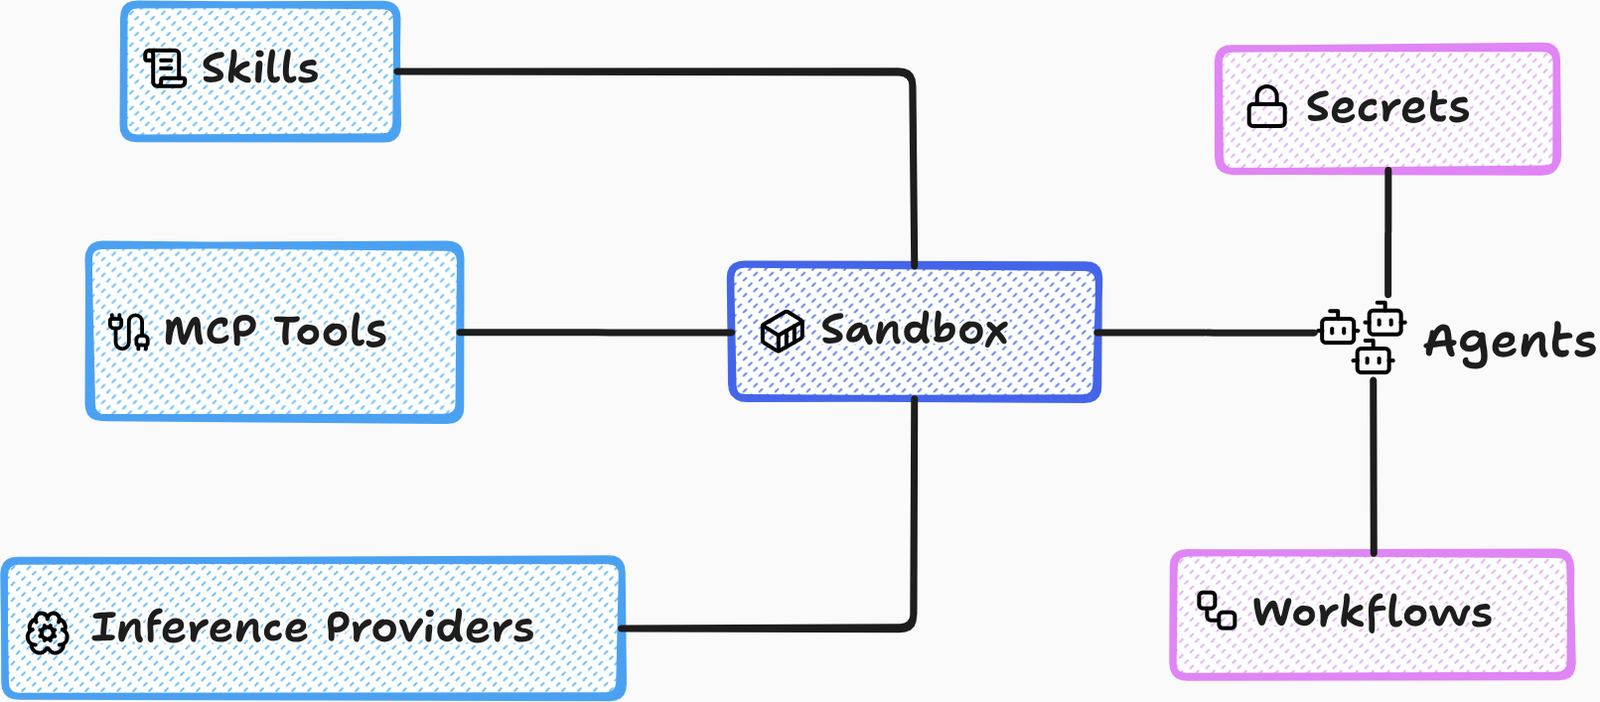 accuknox/agentz
Zero-trust agentic AI platform. Supports SaaS and OnPrem (airgapped) deployments.
 ahmed-alnassif/androsh
AndroSH No-Root Multi-Distro Linux on Android via Shizuku/ADB - Run Arch, Fedora, Alpine, Debian, Ubuntu, Kali, Void, Manjaro, OpenSUSE & Chimera…
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 leaningtech/webvm
Client-side Linux virtual machine running in the browser via WebAssembly, with Tailscale networking, Dockerfile-based custom images, and CTF…
 abraxas/cve-2026-96512
Disclosure pack and PoC for CVE-2026-96512, a sudo NOTBEFORE/NOTAFTER TZ time-window bypass enabling local privilege escalation, with lab…
 abraxas/cve-2026-22599
Python PoC and Docker lab for CVE-2026-22599, an authenticated SQL injection in Strapi's Content-Type Builder write API via Knex raw defaultTo.
 abraxas/cve-2026-15583
Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…
 suominen/januscape
Tracking Januscape (CVE-2026-53359), the KVM/x86 guest-to-host escape
 pentoo/pentoo-overlay
Gentoo overlay for security tools as well as the heart of the Pentoo Livecd