

eviltree
 t3l3machus/eviltree
A python3 remake of the classic "tree" command with the additional feature of searching for user provided keywords/regex in files, highlighting those…
information-gatheringpost-exploitationprivilege-escalation+3
t3l3machus/eviltreeA python3 remake of the classic "tree" command with the additional feature of searching for user provided keywords/regex in files, highlighting those…
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
 streaak/keyhacks
Curated collection of commands to validate leaked API keys from bug bounty programs and penetration tests, covering 80+ services including AWS,…
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 byt3hx/jsleak
Concurrent CLI tool for discovering secrets, API keys, and links in JavaScript files during web reconnaissance, with custom regex pattern support and…
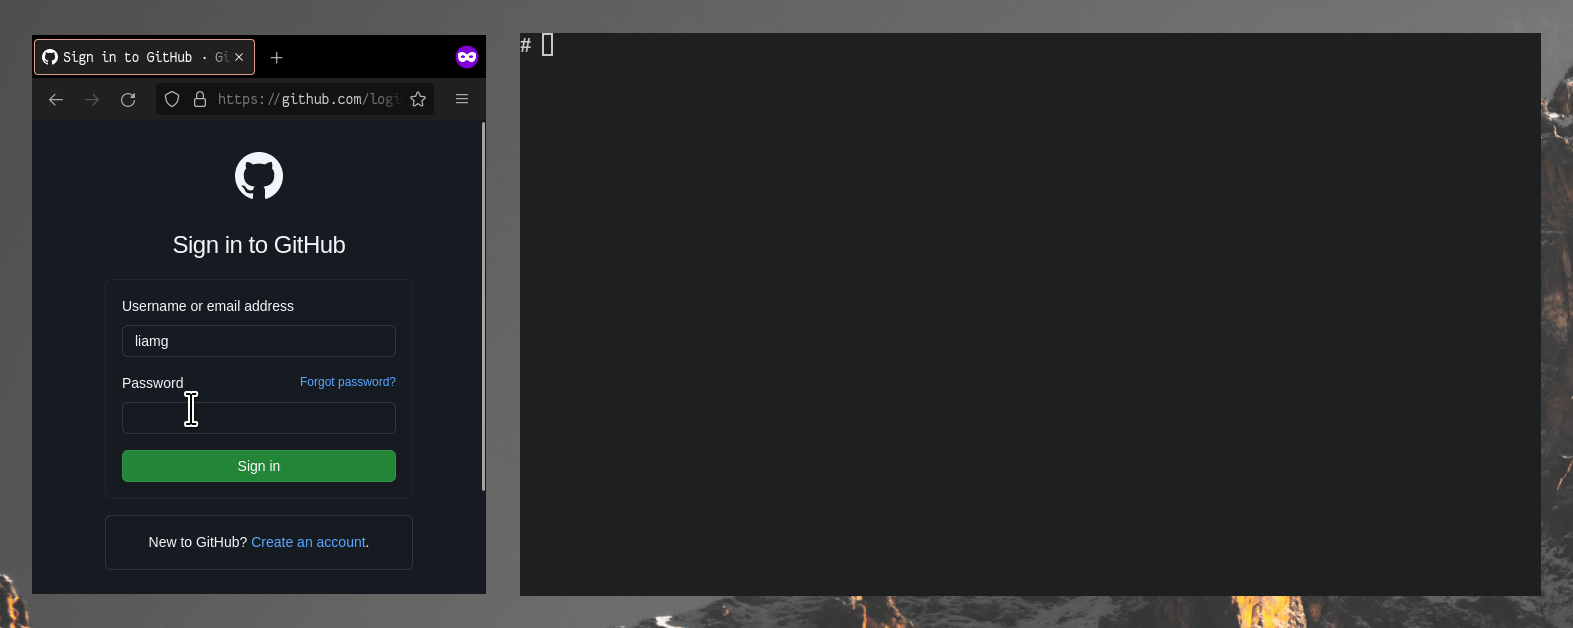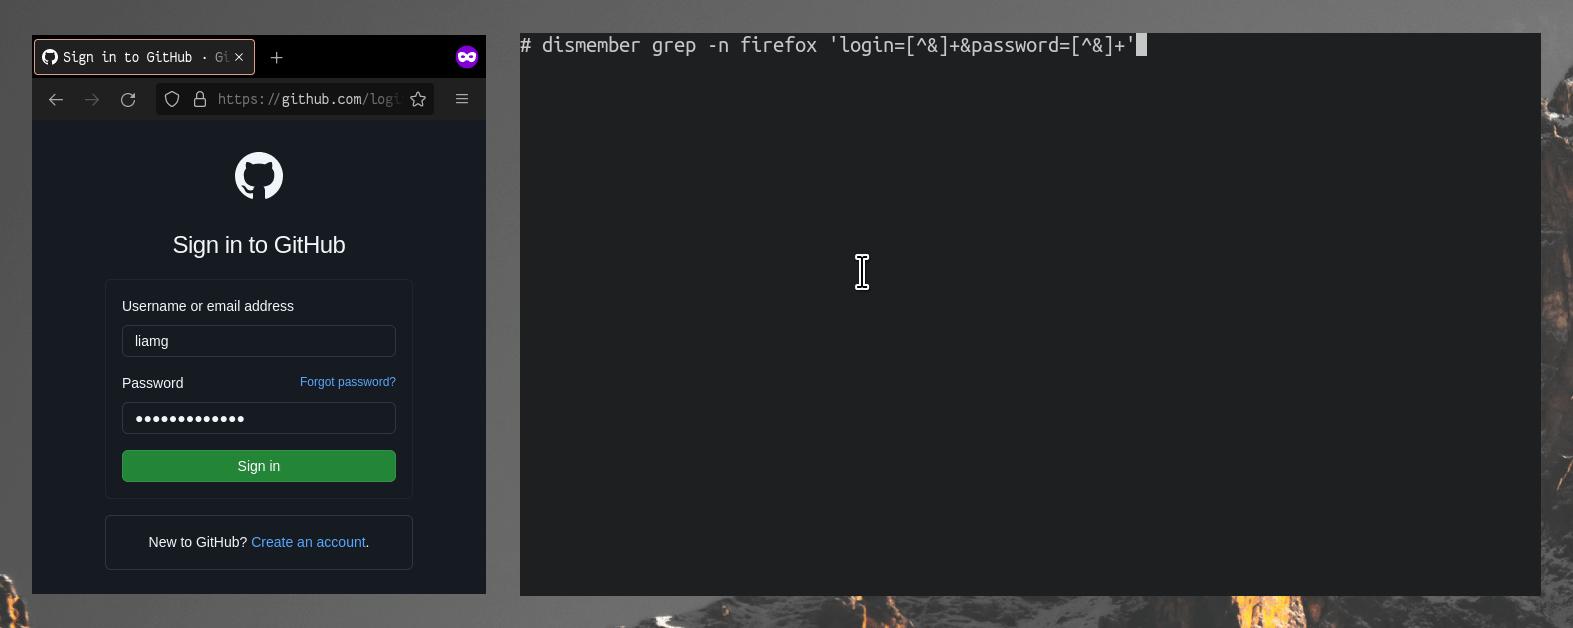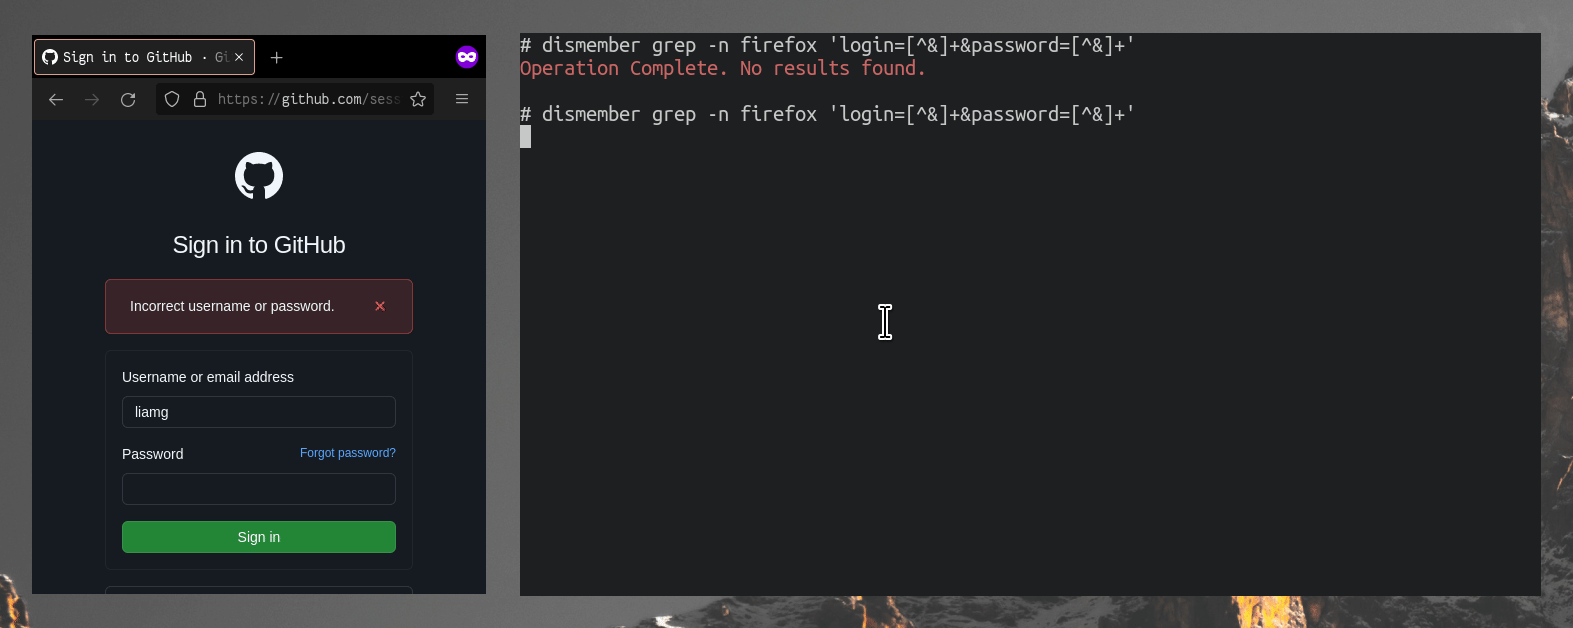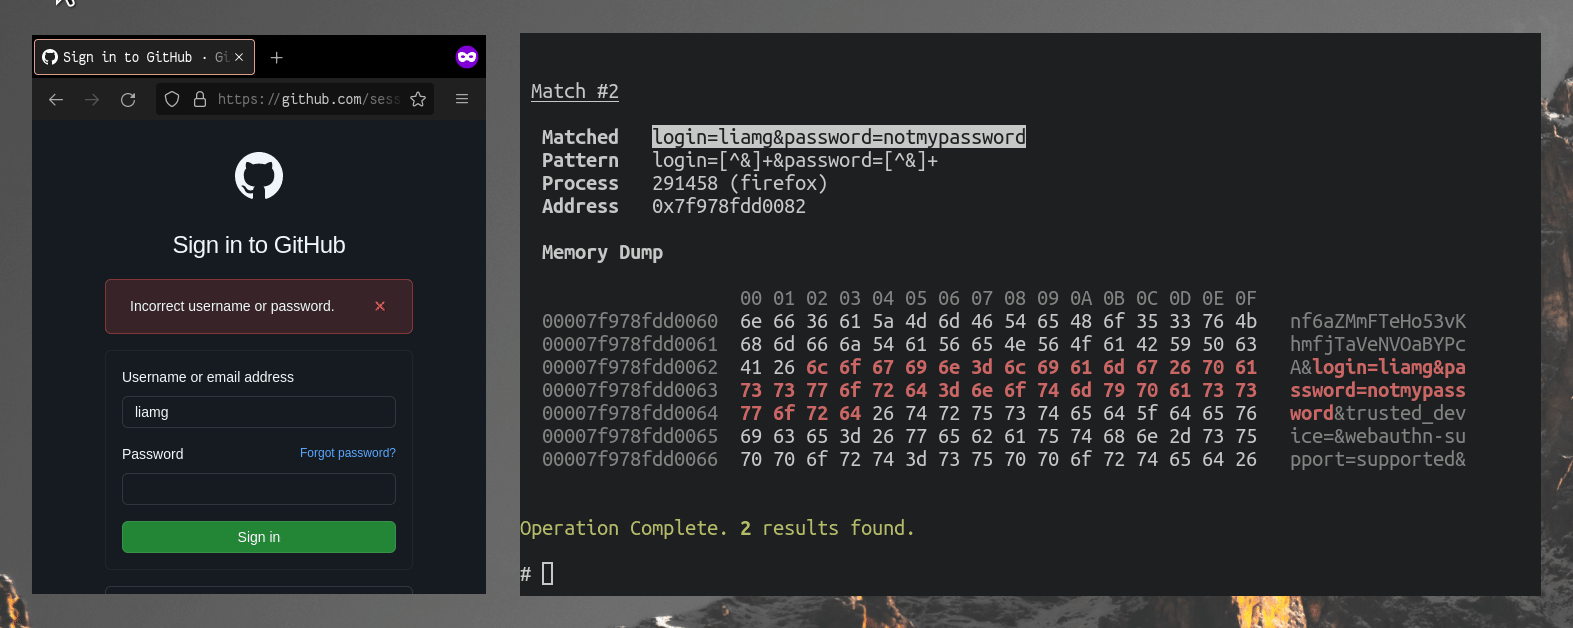 liamg/dismember
:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.
 daddycocoaman/dumpscan
Finding secrets in kernel and user memory
 manuelschipper/nah
a guard that blocks catastrophic agent actions
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 bishopfox/jsluice
Extract URLs, paths, secrets, and other interesting bits from JavaScript
 crissyfield/troll-a
Extracts secrets (passwords, API keys, tokens) from WARC web archives using Gitleaks rules. Supports HTTP, S3, local files, and compressed archives…
 cappricio-securities/behat-config-leaks
BeHat Configuration file leaking
 cappricio-securities/appspec-yaml-leaks
Appspec YML and YAML leaks
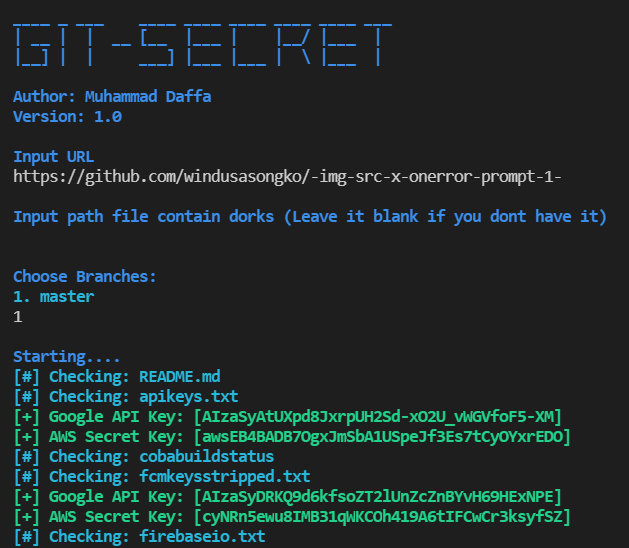 daffainfo/git-secret
Go scripts for finding sensitive data like API key / some keywords in the github repository
 tellerops/teller
Cloud native secrets management for developers - never leave your command line for secrets.
 kriskimmerle/wheelaudit
Python Wheel File Security Scanner — scan .whl files for security issues before installation. Detects path traversal (CVE-2026-24049), RECORD…
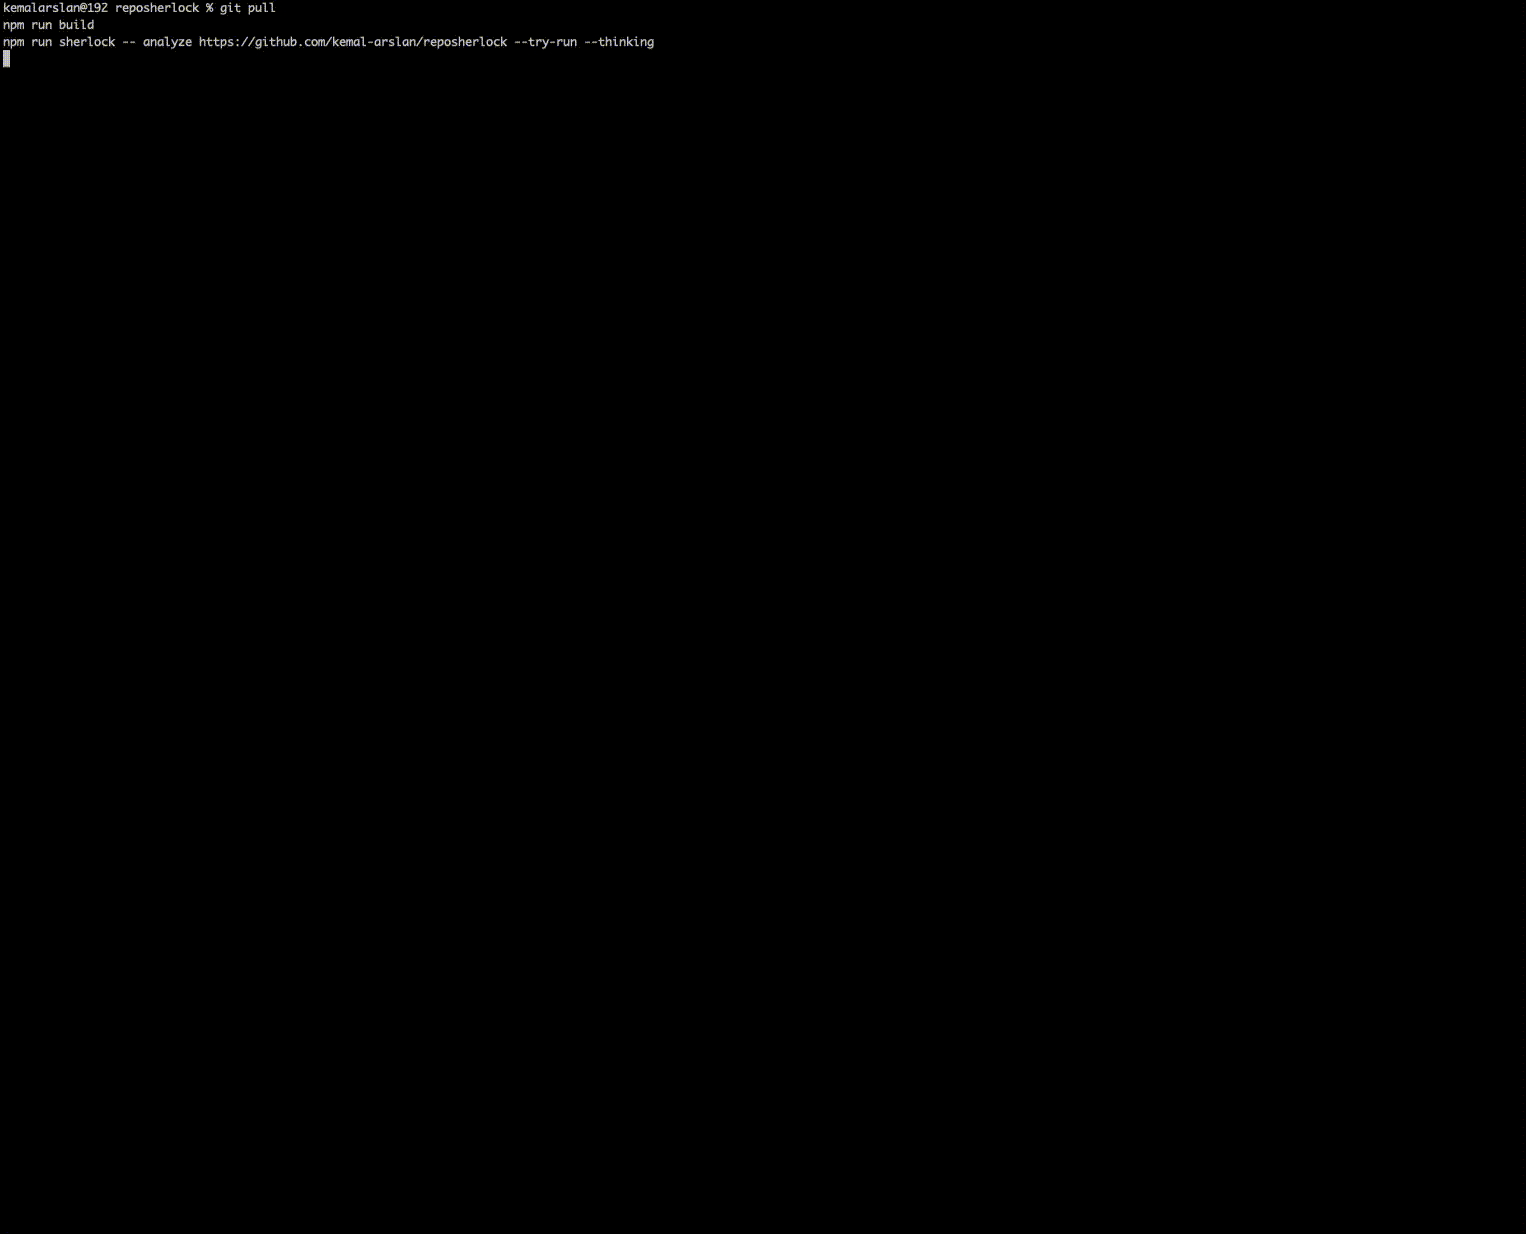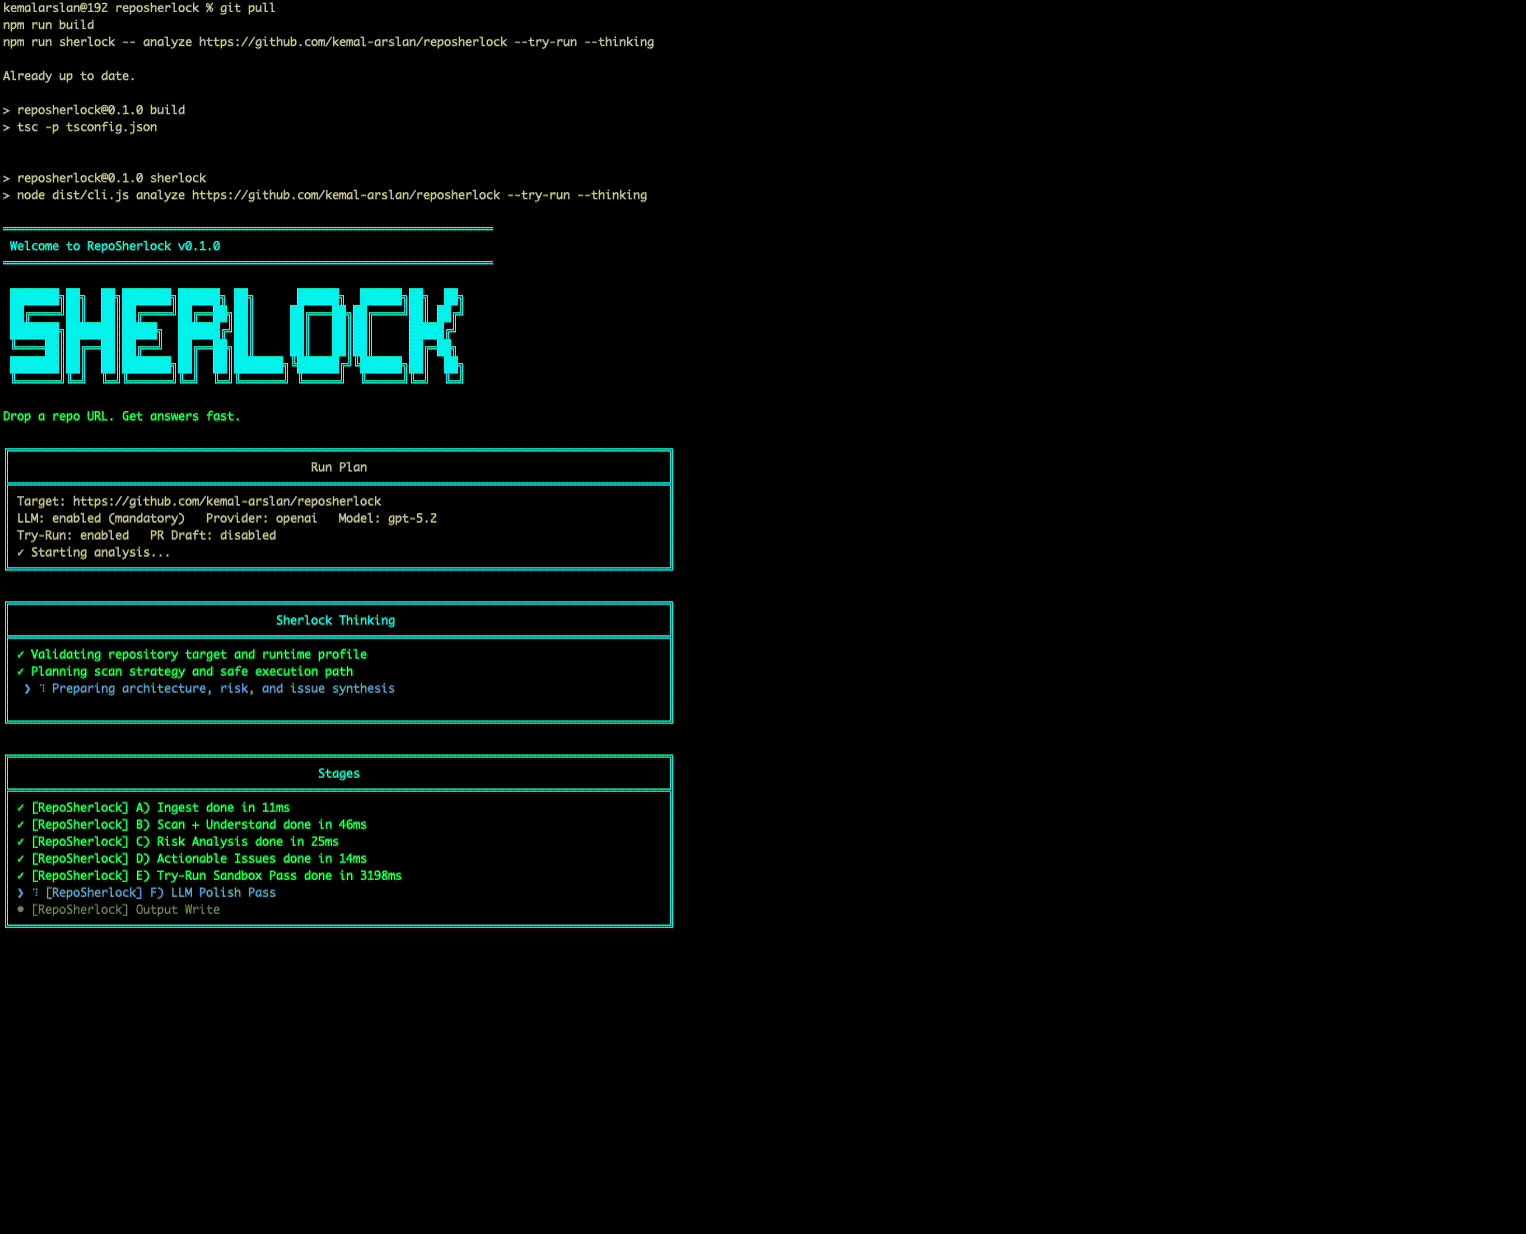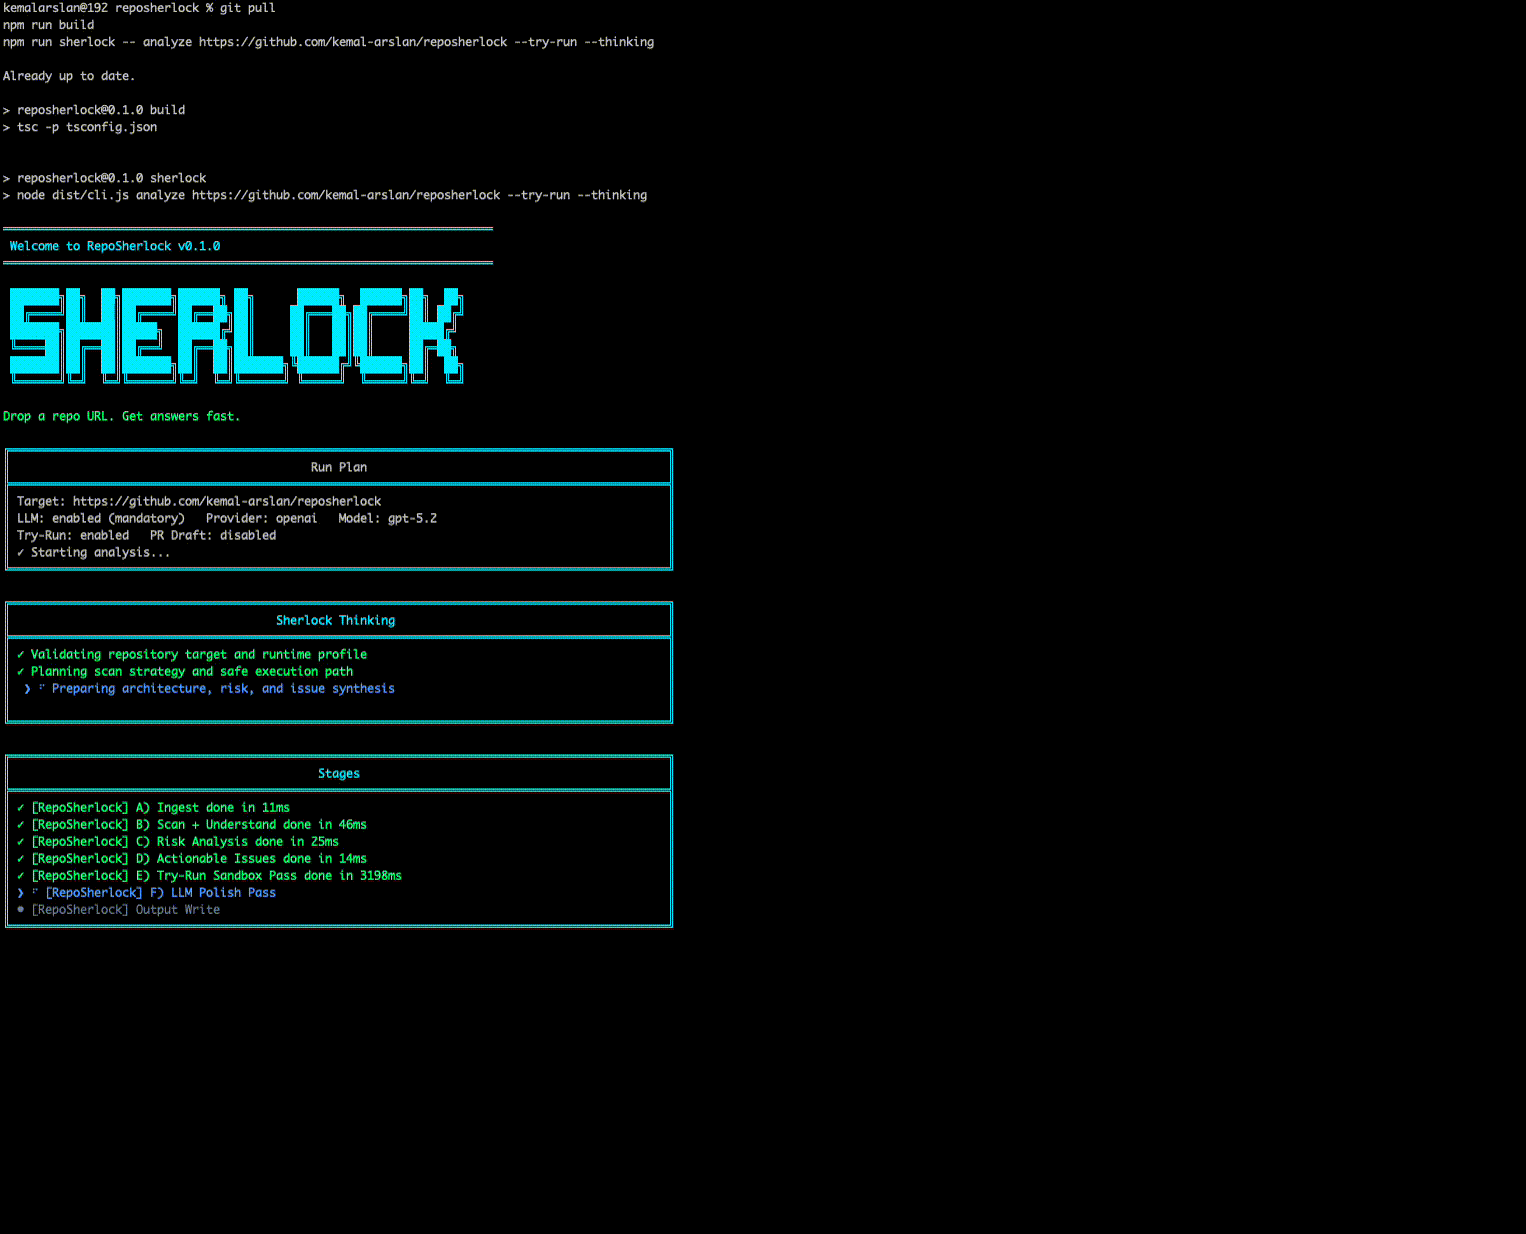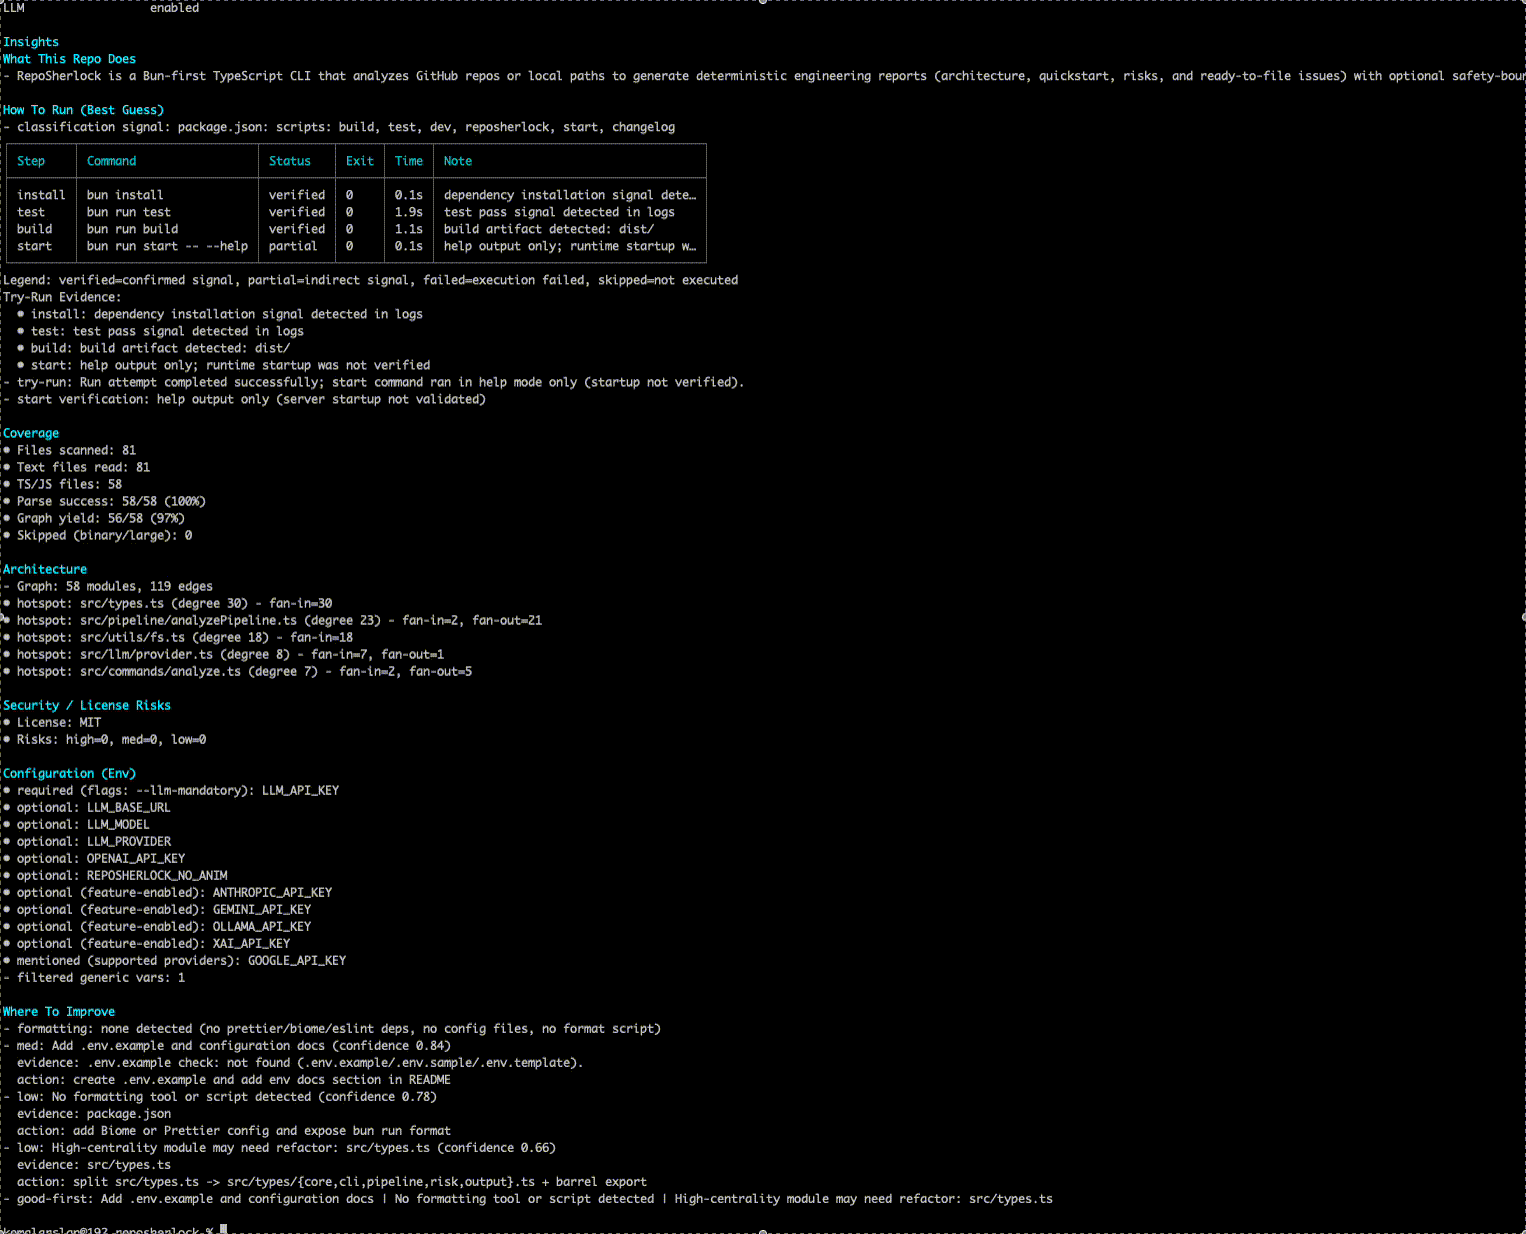 kemal-arslan/reposherlock
Analyze any GitHub repo (URL or local path) → architecture map, verified run commands, risks, and actionable issues - in minutes.
 w4r10ck423/envvisualizer
Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…