
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
jsleak — Concurrent CLI tool for discovering secrets, API keys, and links in JavaScript files during web reconnaissance, with custom regex pattern support and URL status checking. | Kitploit
Tools/GitHubGitHub/byt3hx/jsleak
ReconnaissanceInformation GatheringWeb SecuritySecret Detection
GitHubbyt3hx/jsleak

jsleak

Concurrent CLI tool for discovering secrets, API keys, and links in JavaScript files during web reconnaissance, with custom regex pattern support and URL status checking.

View Repository
59369341 year agoReviewed by Kitploit
Share

Description

I was developing jsleak during most of my free time for my own need.It is easy-to-use command-line tool designed to uncover secrets and links in JavaScript files or source code. The jsleak was inspired by Linkfinder and regexes are collected from multiple sources.

Features:

  • Discover secrets in JS files such as API keys, tokens, and passwords.
  • Identify links in the source code.
  • Complete Url Function
  • Concurrent processing for scanning of multiple Urls
  • Check status code if the url is alive or not

Latest Update

Jsleak now supports regex patterns from secrets-patterns-db https://github.com/mazen160/secrets-patterns-db.

If you want to use your own custom regex patterns, you can place them in a YAML file following the template below.

patterns:
  - pattern:
      name: Amazon MWS Auth Token
      regex: "amzn\\.mws\\.[0-9a-f]{8}-[0-9a-f]{4}-[0-9a-f]{4}-[0-9a-f]{4}-[0-9a-f]{12}"
      confidence: low

Installation

If you are using old version of golang (go 1.15, 1.16) , use the following command to install jsleak.

go get github.com/channyein1337/jsleak

If you are using latest version of go (1.17+) , use the following command to install.

go install github.com/channyein1337/jsleak@latest

Usage

Choose a YAML file from the secrets-patterns-db. If you’re not sure which one to pick, consider using: https://raw.githubusercontent.com/mazen160/secrets-patterns-db/refs/heads/master/datasets/trufflehog-v3.yaml

Run jsleak with Your Selected Regex File

echo "http://testphp.vulnweb.com/" | jsleak -t trufflehog-v3.yaml -s

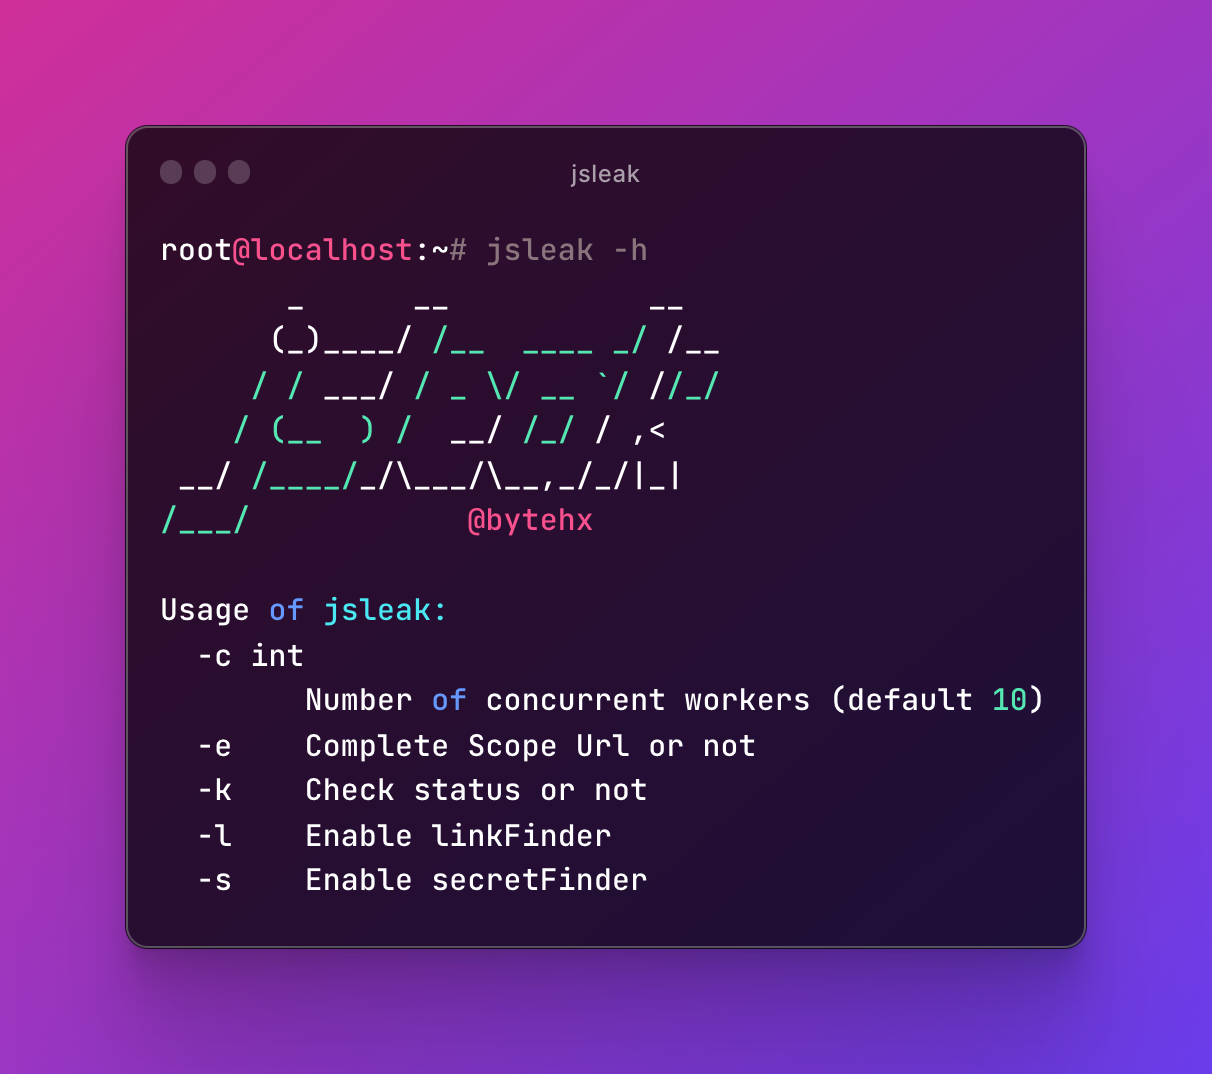
To display help message

jsleak -h
Secret Finder

echo http://testphp.vulnweb.com/ | jsleak  -t secret.yaml -s

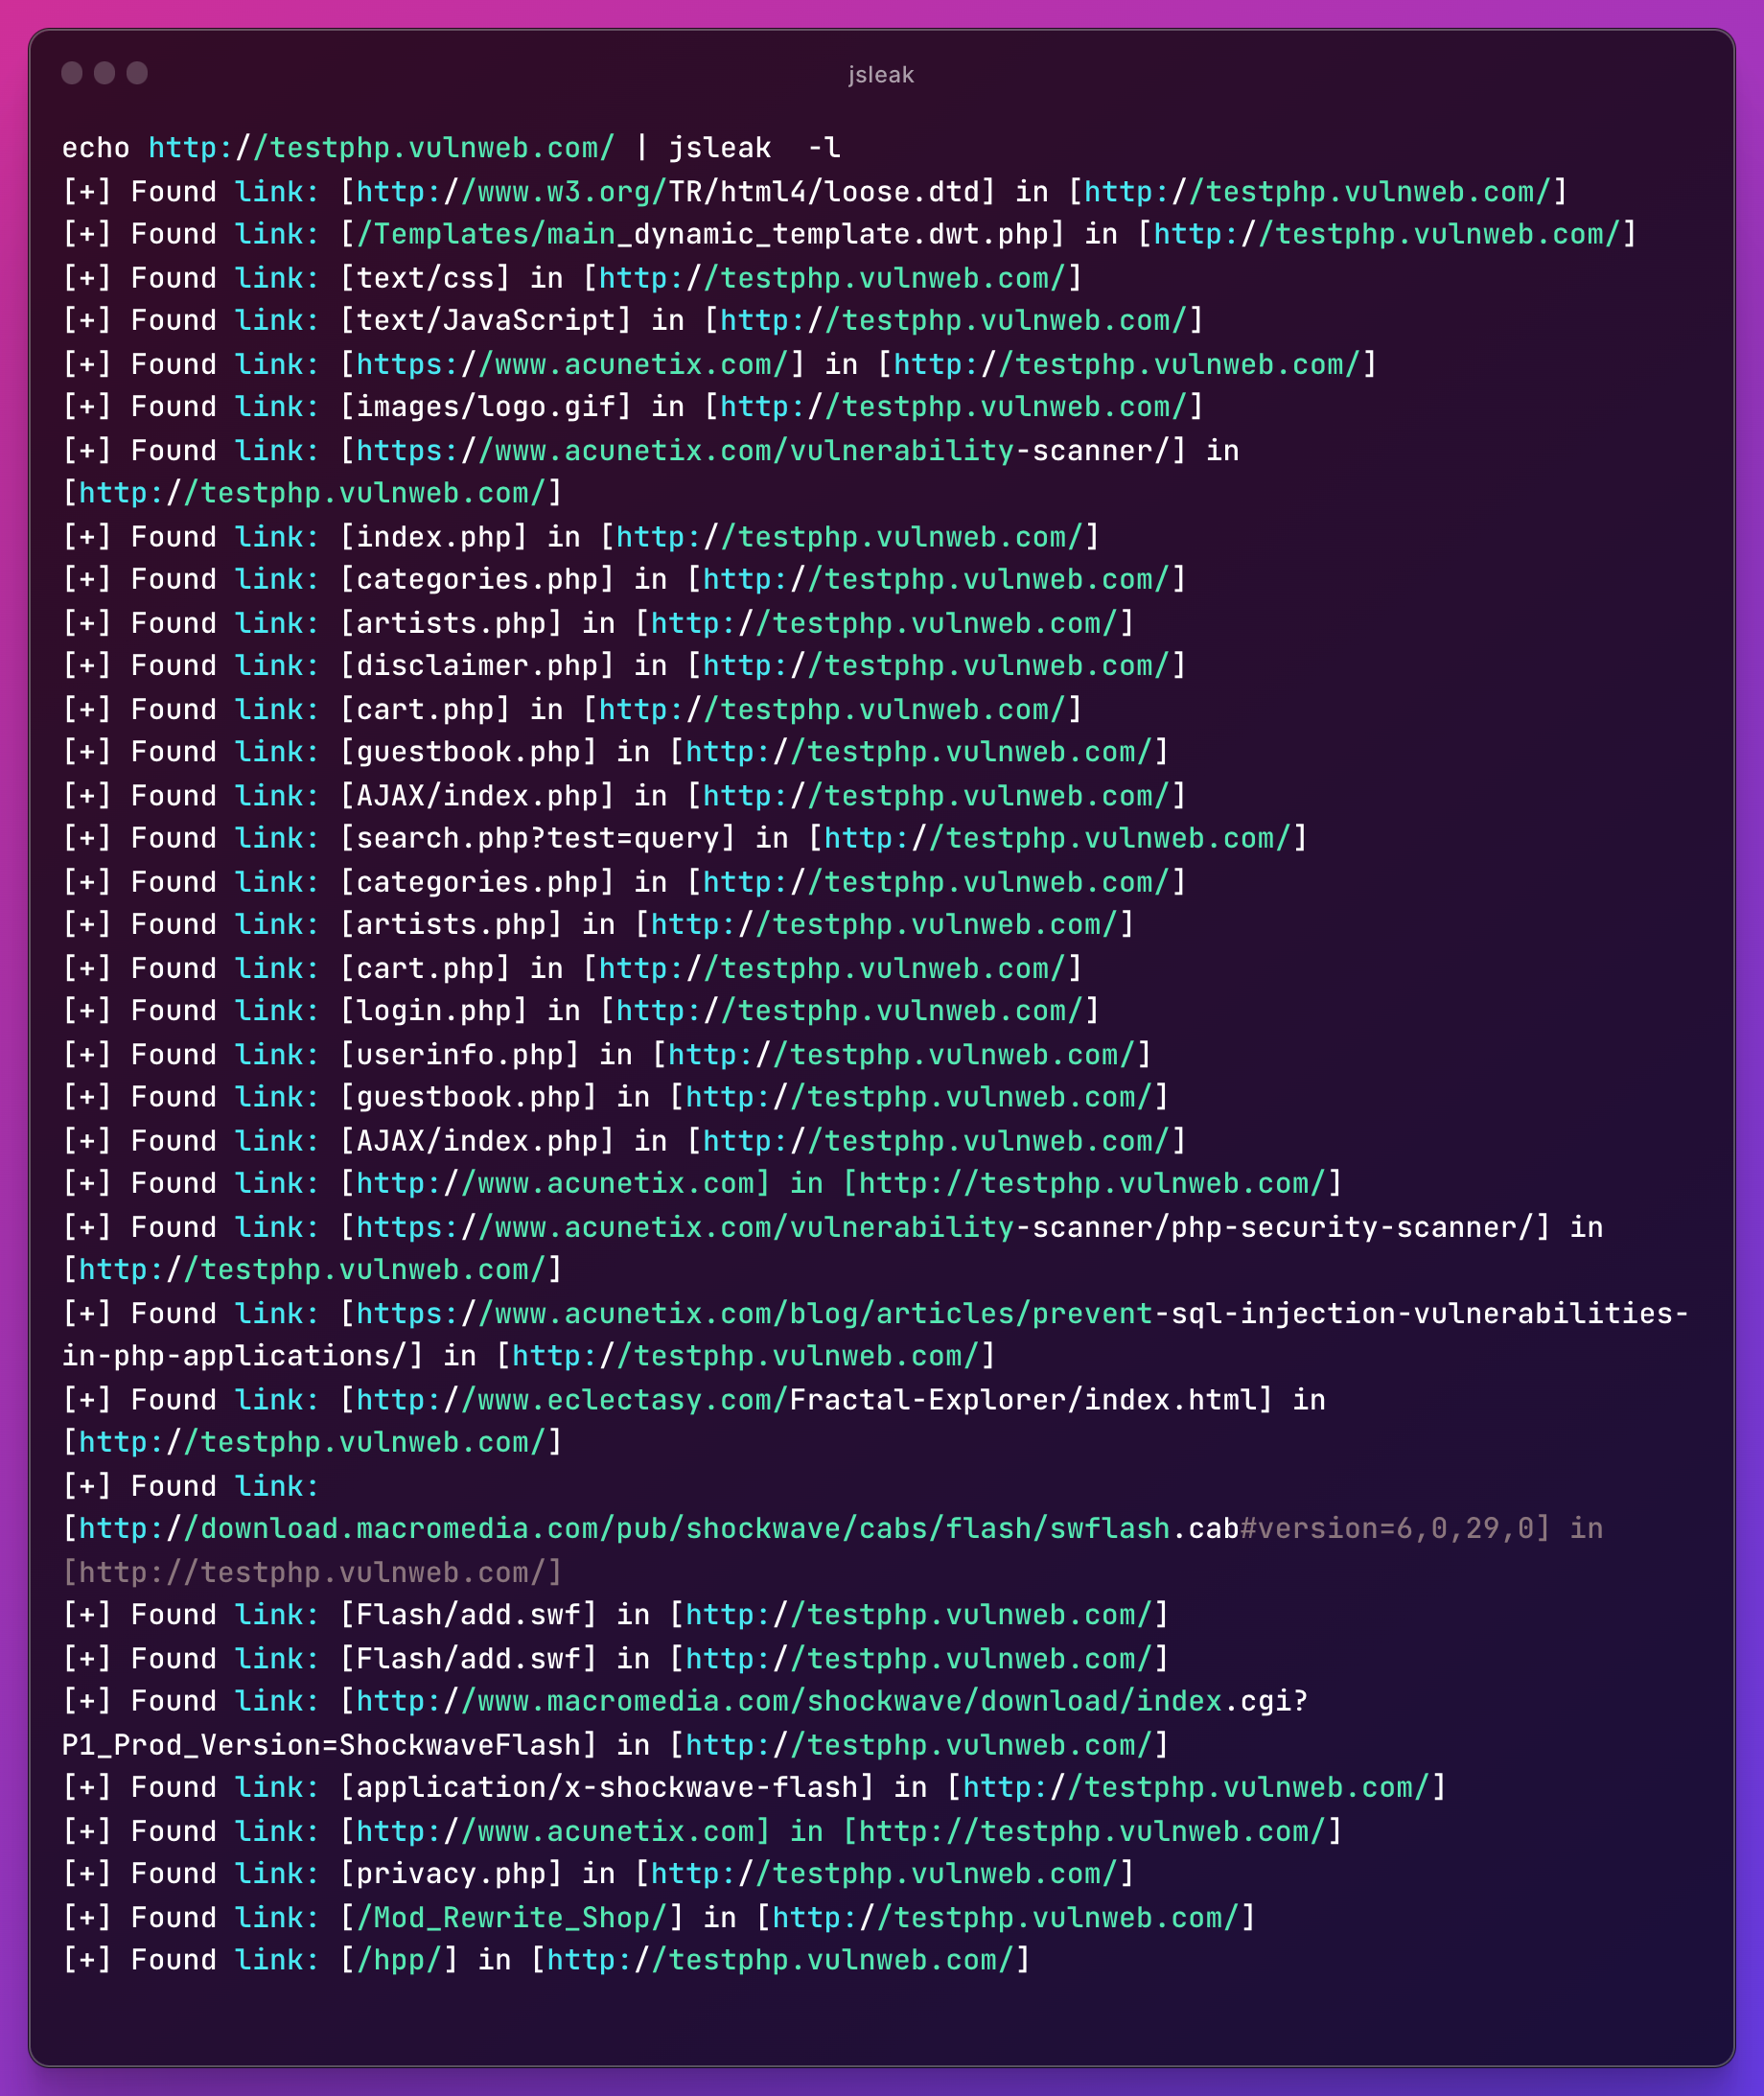
Link Finder

echo http://testphp.vulnweb.com/ | jsleak -l
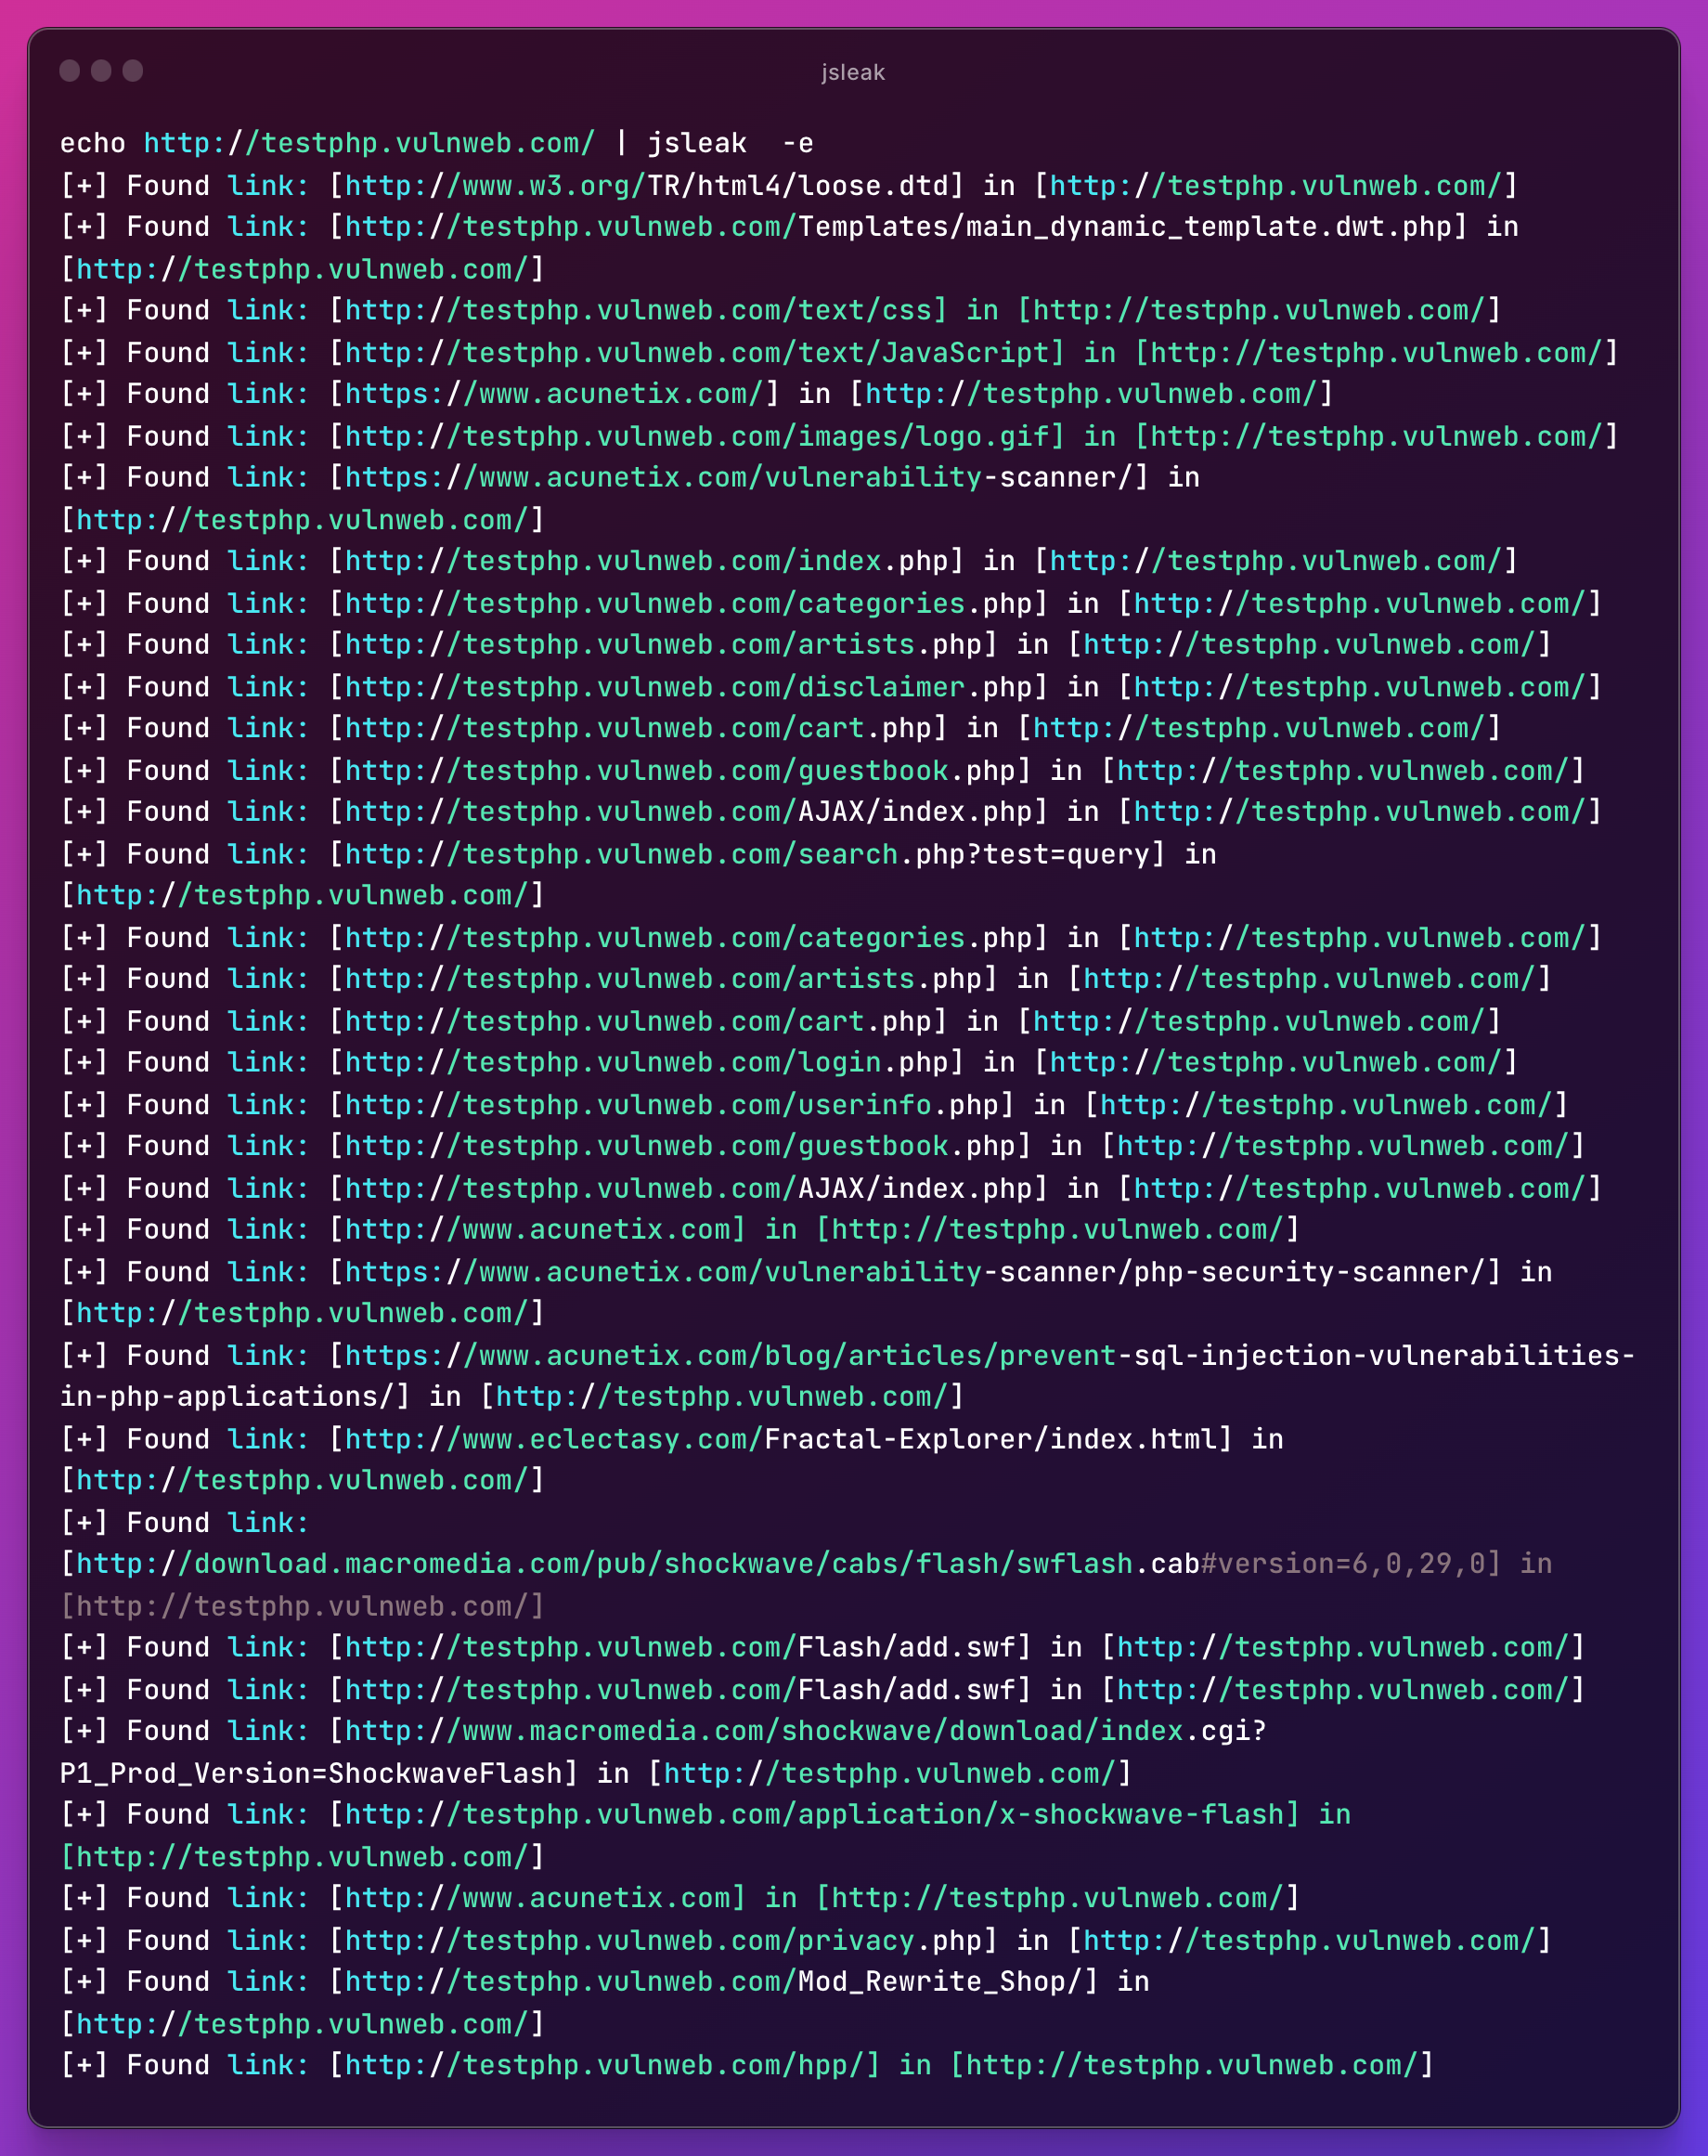
Complete Url

echo http://testphp.vulnweb.com/ | jsleak -e
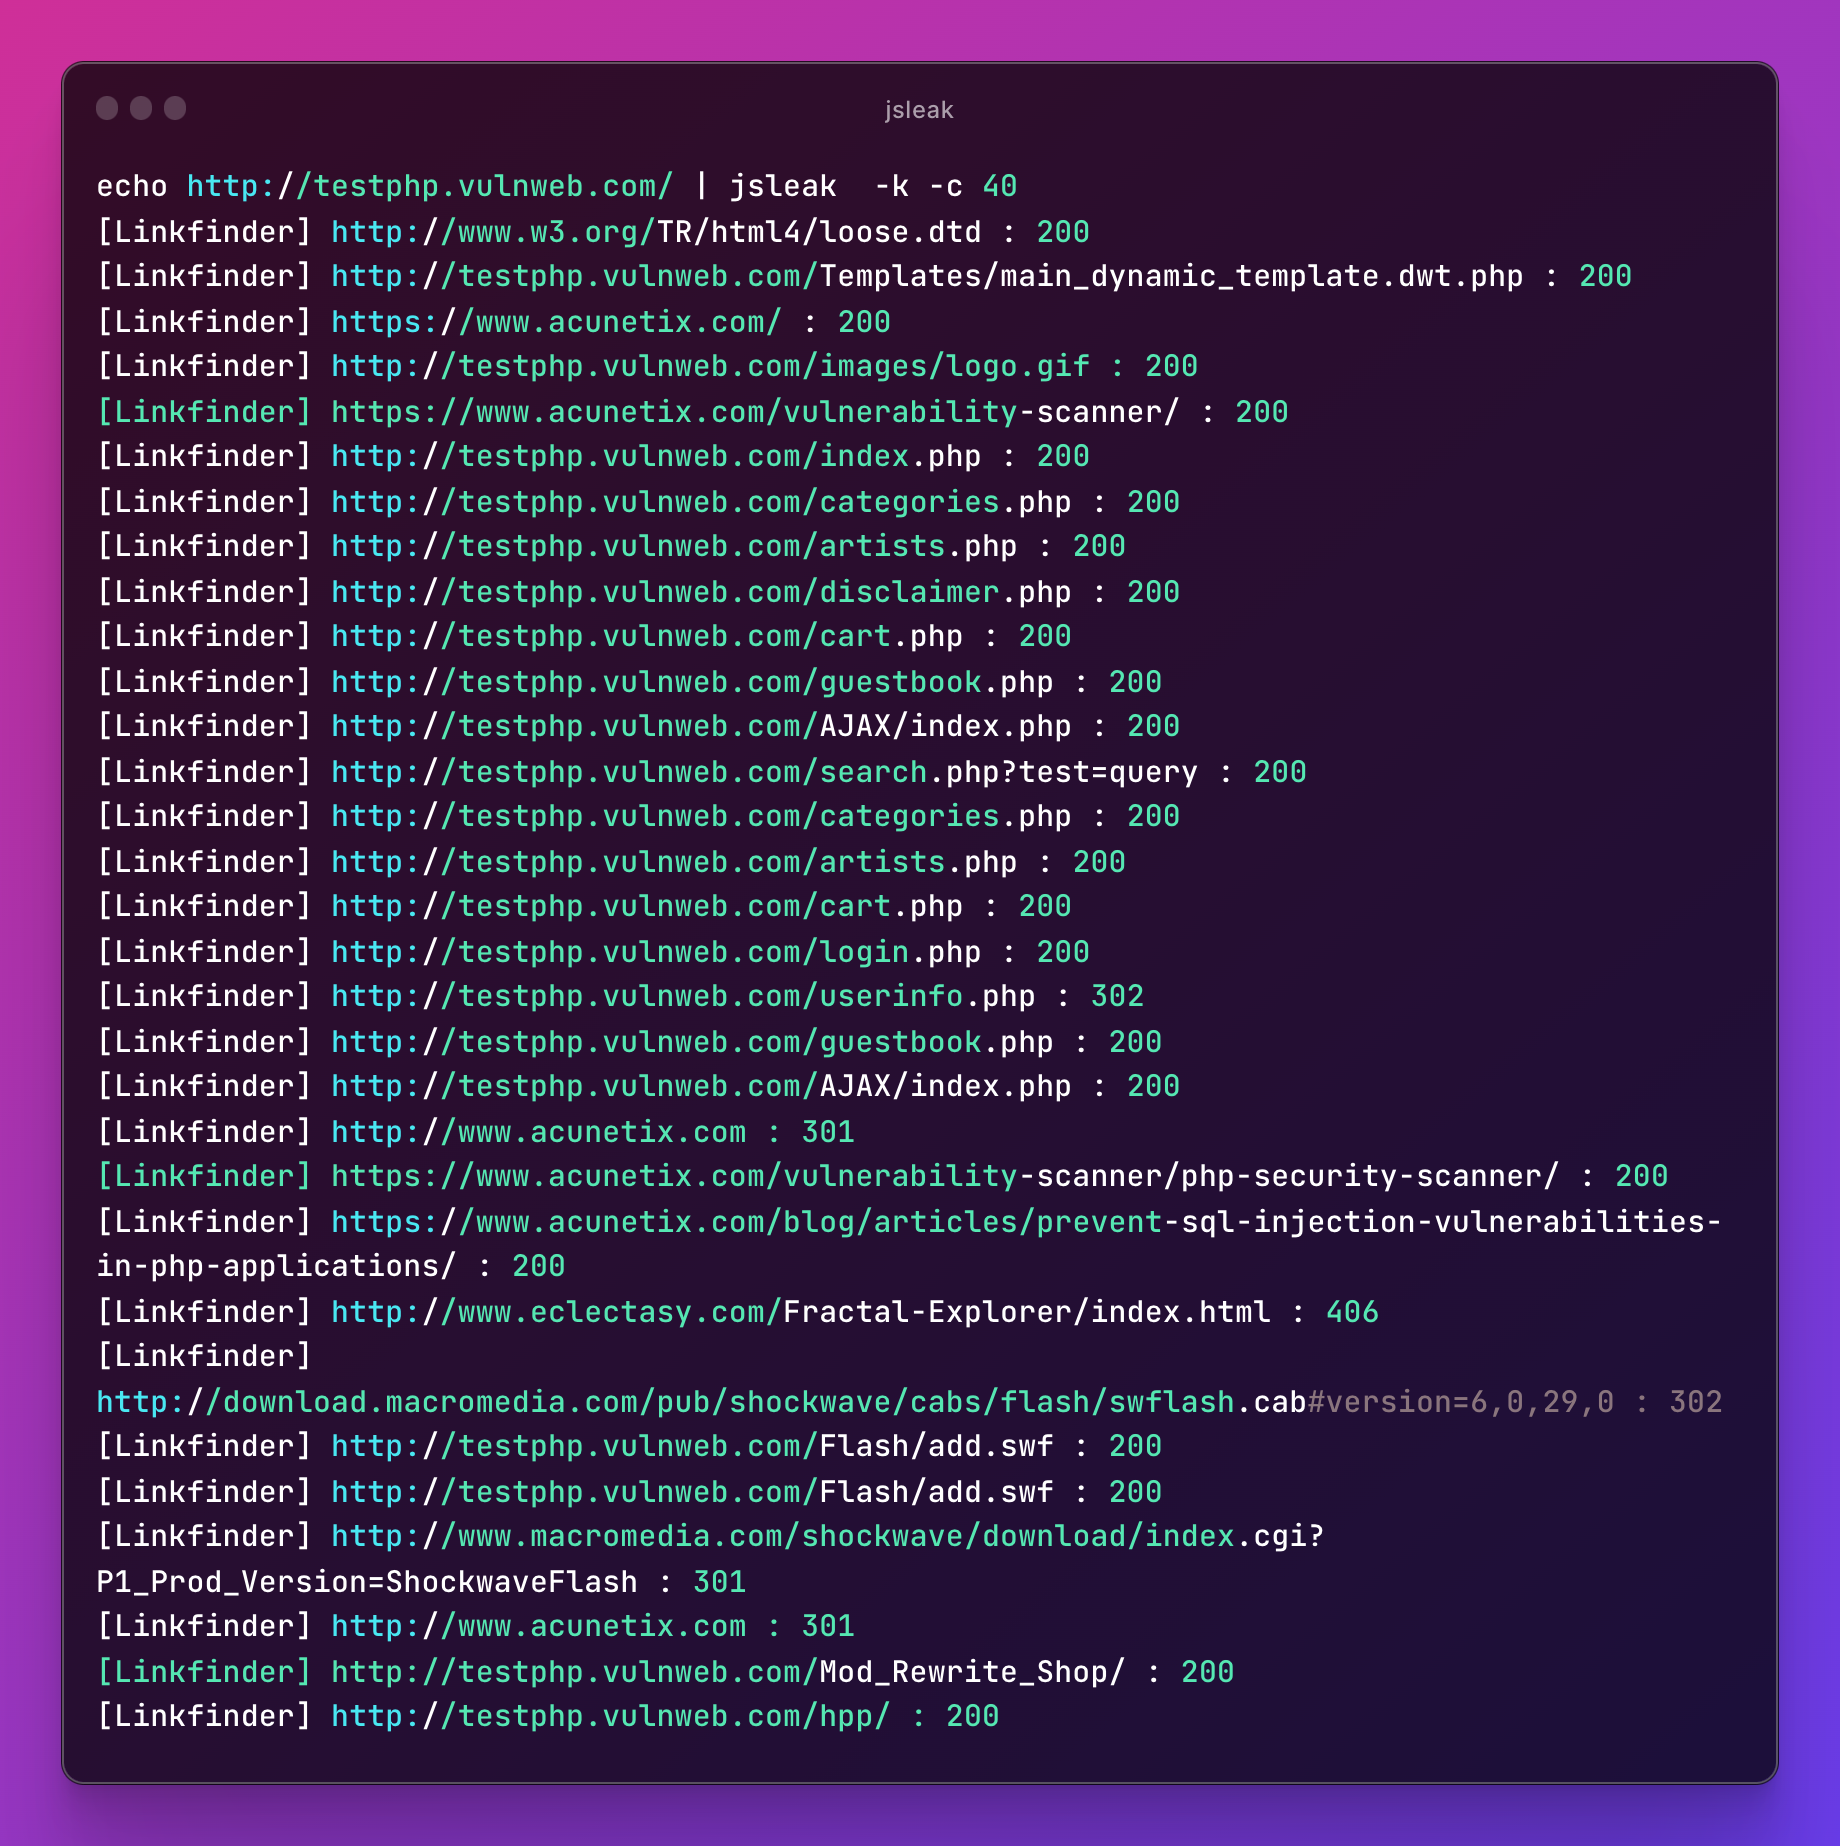
Check Status

echo http://testphp.vulnweb.com/ | jsleak -c 20 -k
You can also use multiple flags

echo http://testphp.vulnweb.com/ | jsleak -c 20 -l -s 
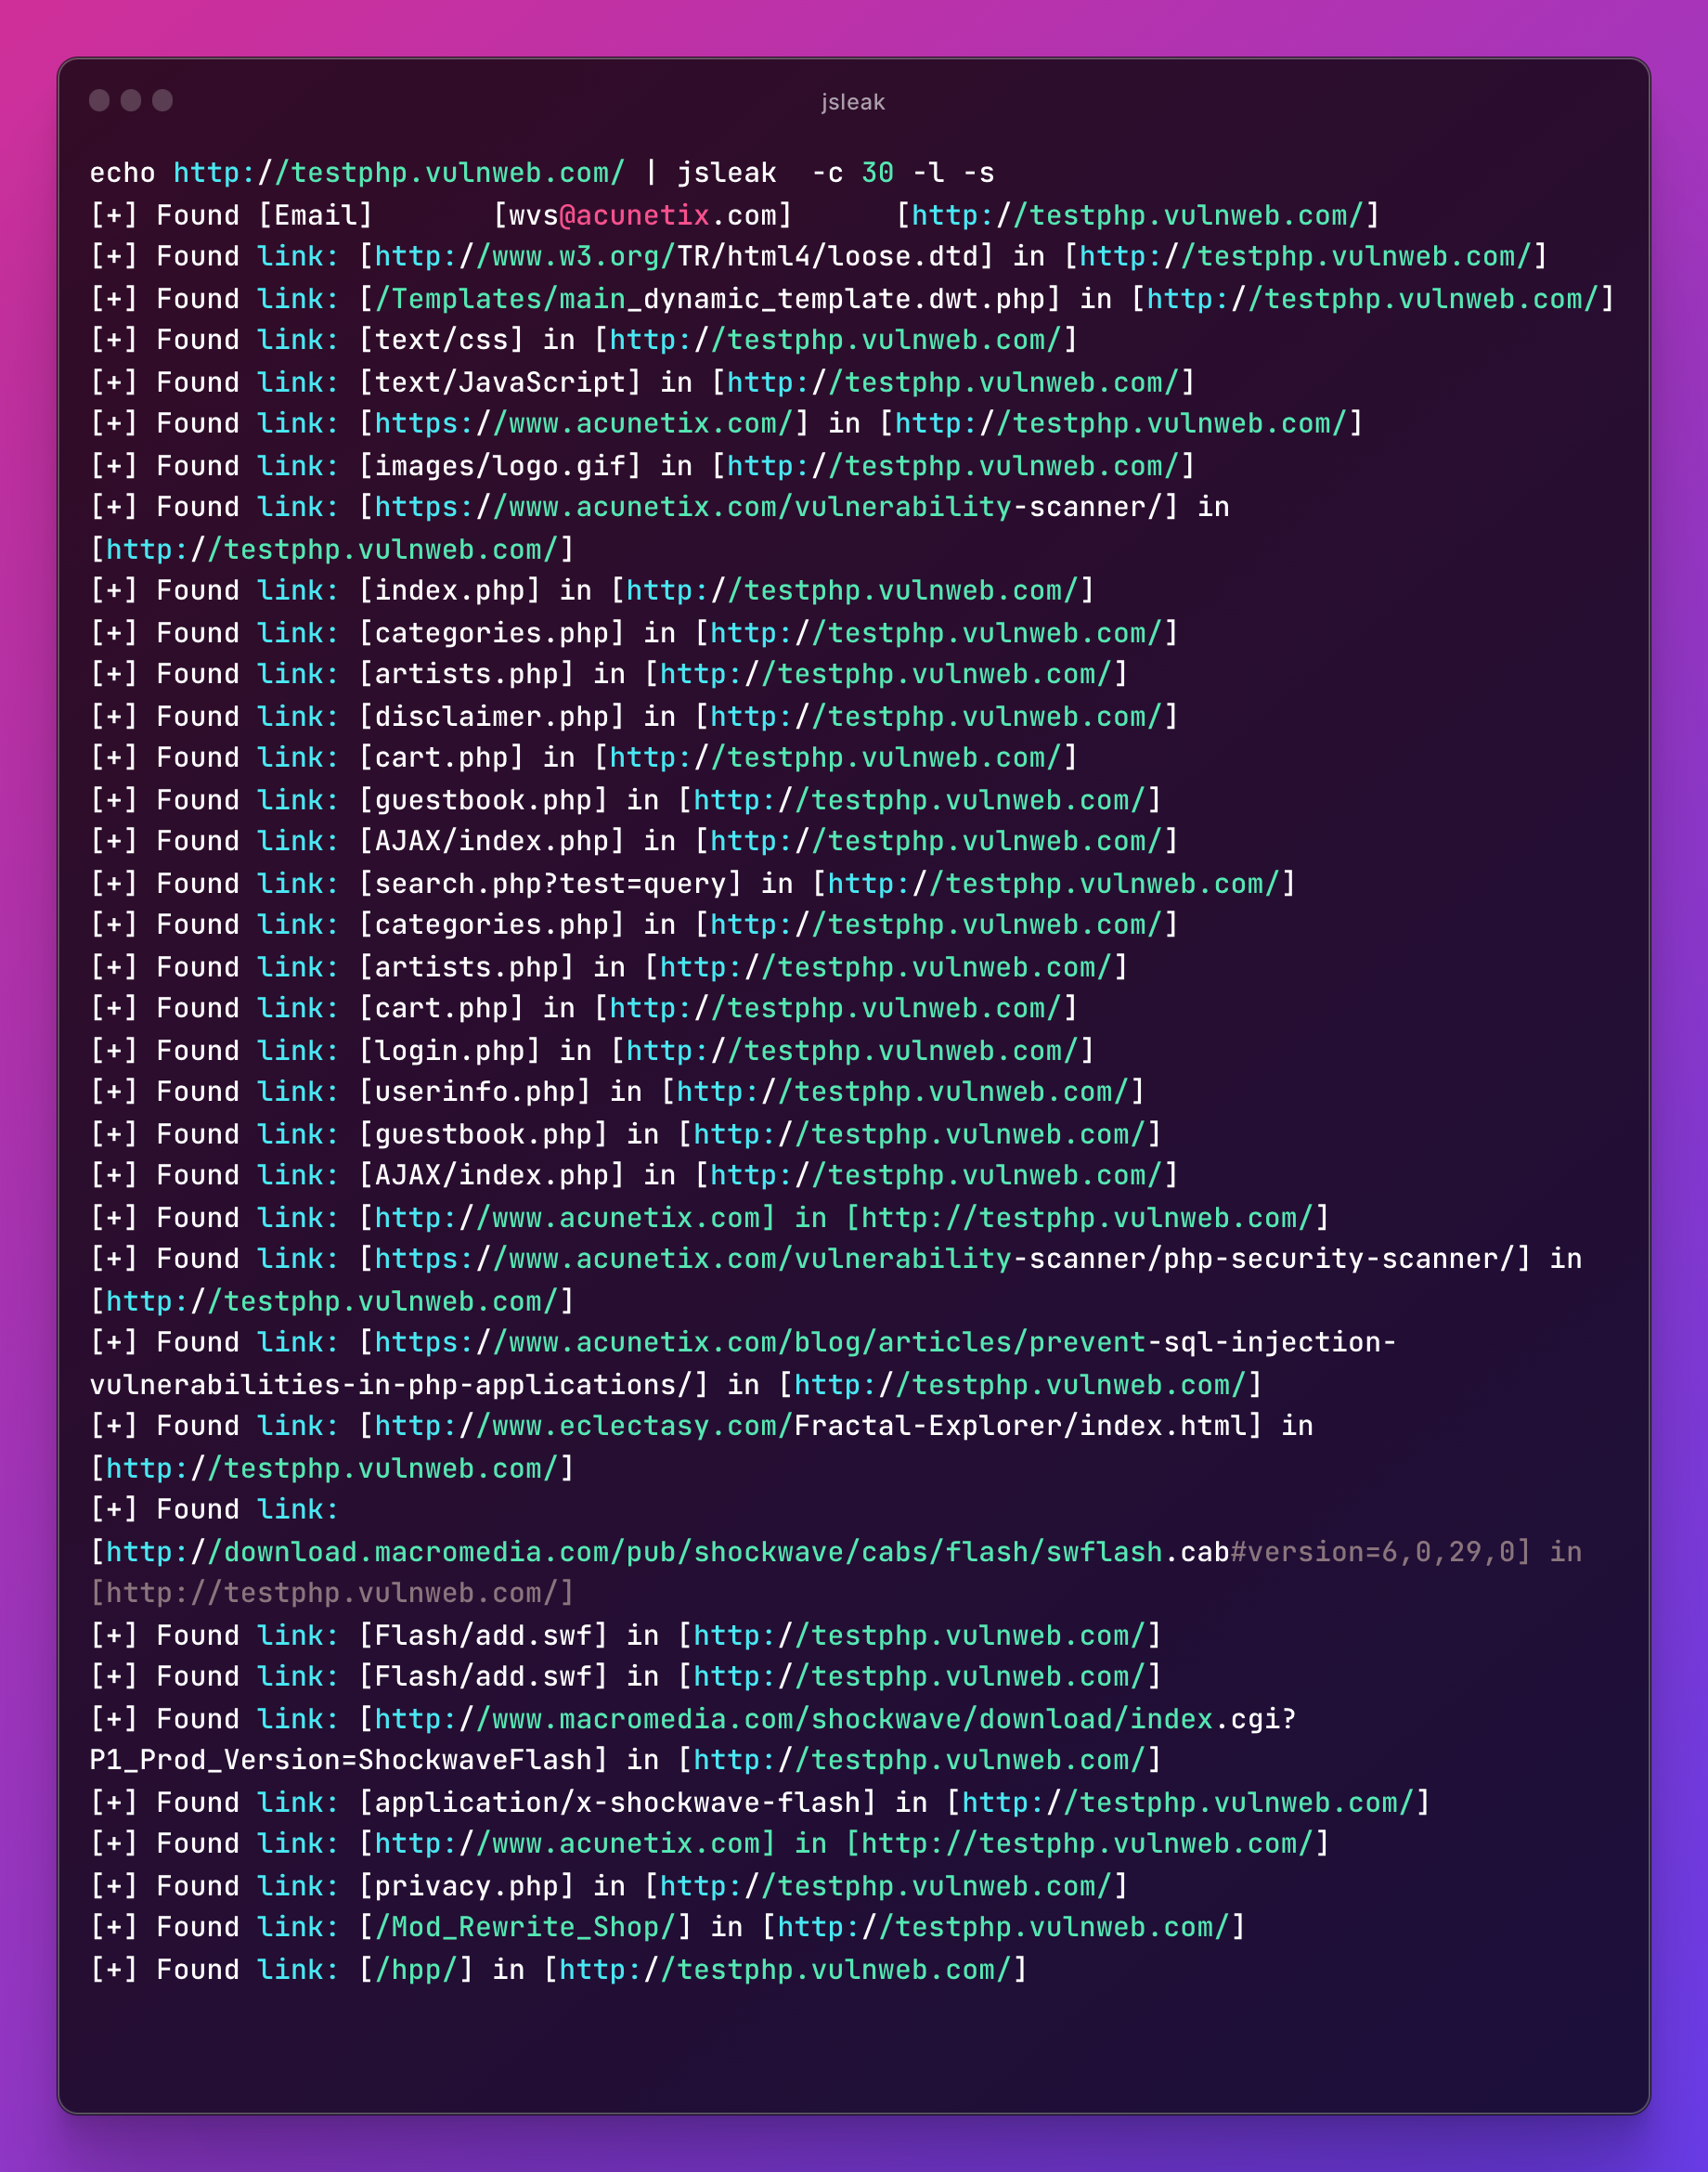
Running with Urls

cat urls.txt | jsleak -l -s -c 30

To Do

  • Scan secret on completeURL with 200 response.
  • Add Version flag.
  • Support scanning local files.
  • Support scanning apk files.
  • Update Regex.
  • Support mulitple user agents.
  • Support color output

Credit and thanks to all the following resources

  • https://github.com/GerbenJavado/LinkFinder
  • https://github.com/0xsha/GoLinkFinder
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    927
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    555
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    360
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    357
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    324
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools →






