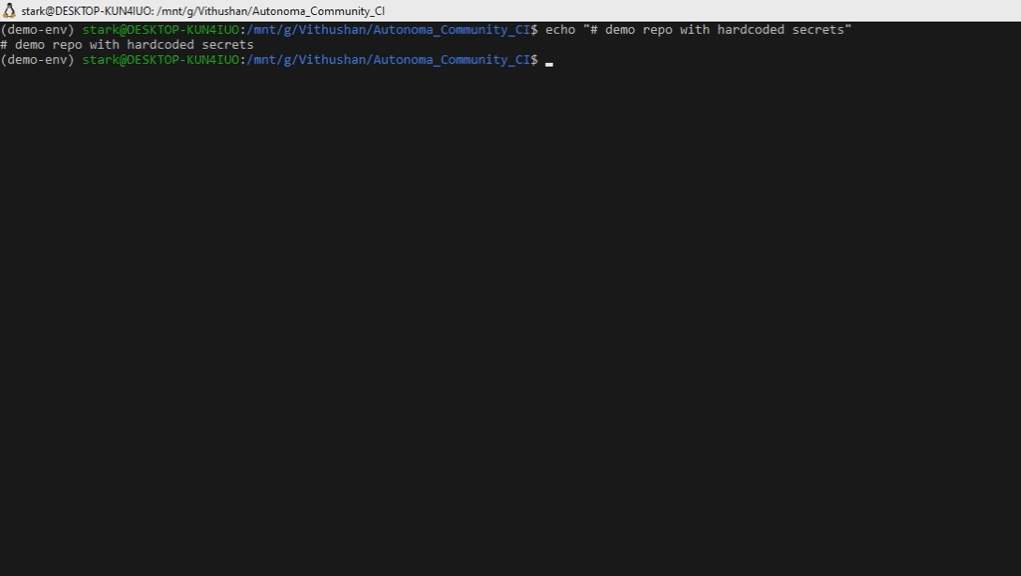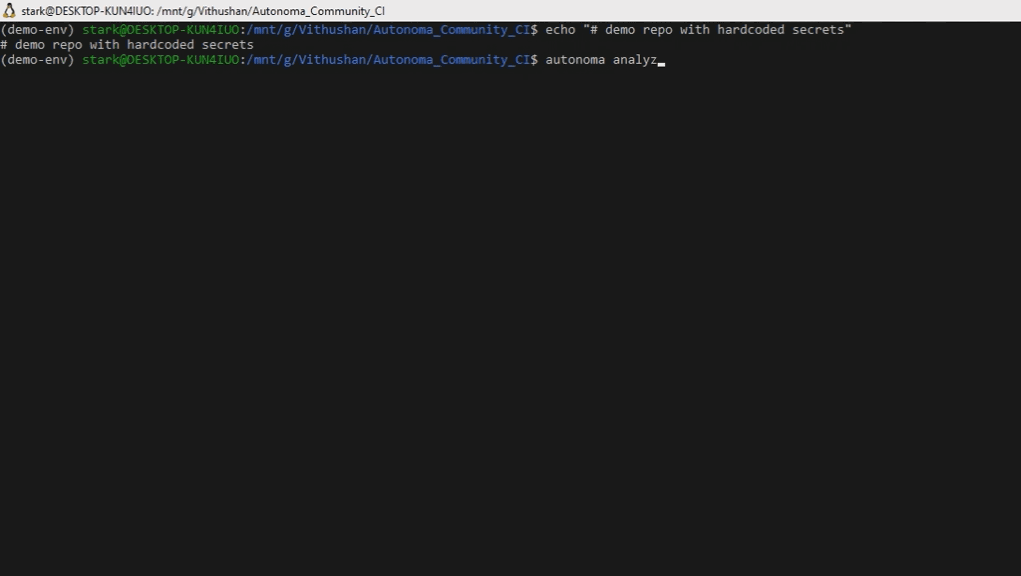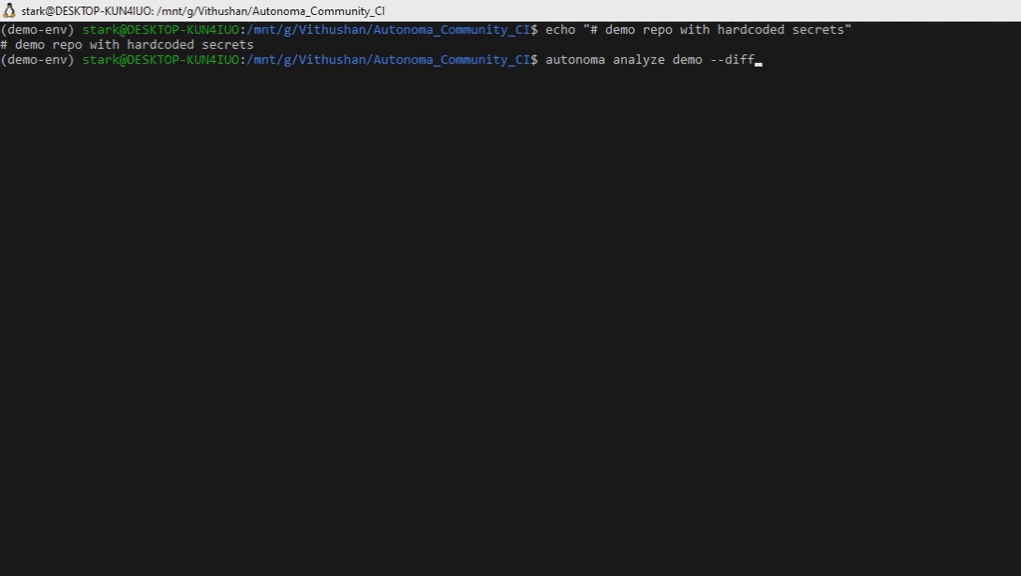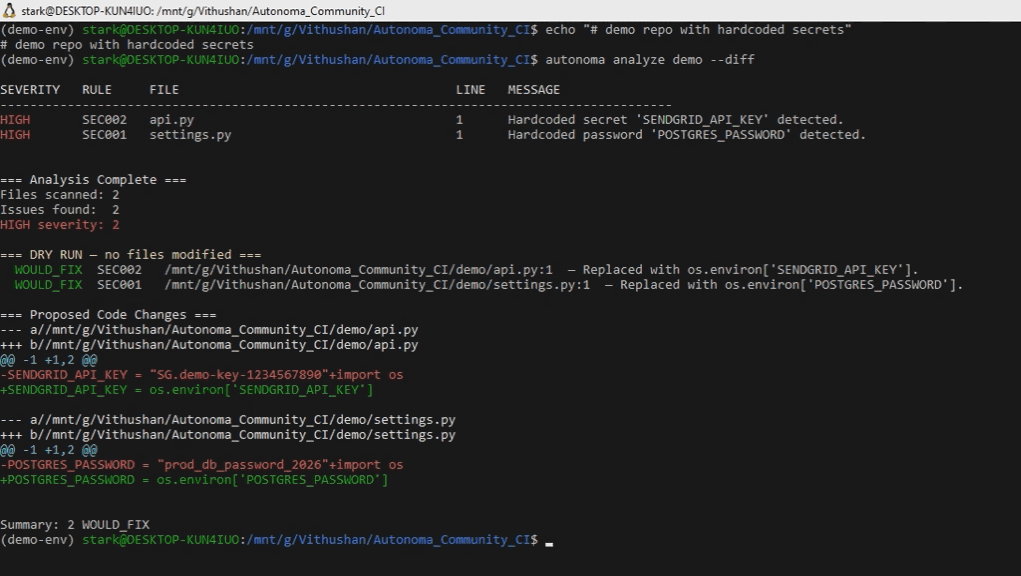
autonoma
 vihaaninnovations/autonoma
Detects and auto-fixes hardcoded secrets in Python repos — refuses when the fix could break your code
code-analysisdevsecopssecret-detection+3
2
vihaaninnovations/autonomaDetects and auto-fixes hardcoded secrets in Python repos — refuses when the fix could break your code
 shivang0/guardmodel
GitHub Action that scans ML model files for malicious code and security vulnerabilities
 checkmarx/checkmarx-cve-2025-30066-detection-tool
Scans GitHub workflows and logs for indicators of CVE-2025-30066, detecting malicious actions and exposed secrets using Checkmarx 2ms integration.
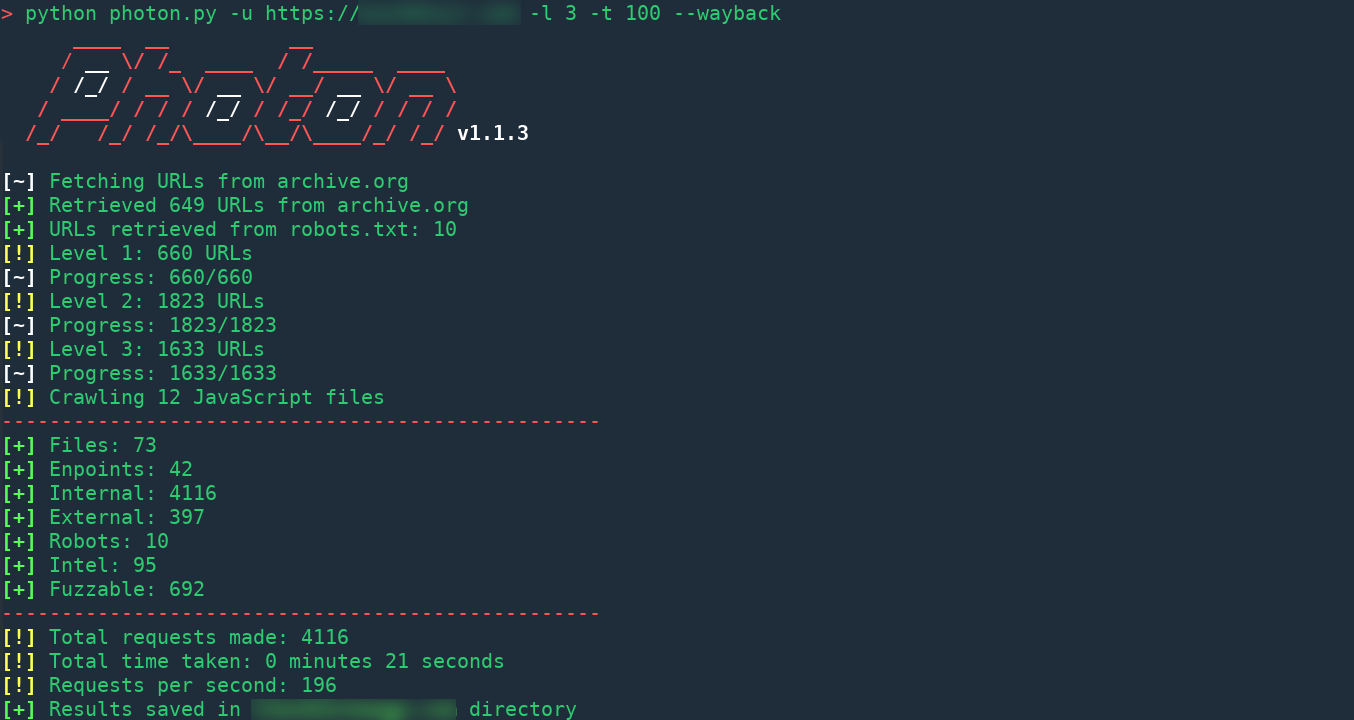 s0md3v/photon
Incredibly fast crawler designed for OSINT.
 proviesec/google-dorks
Useful Google Dorks for WebSecurity and Bug Bounty
 sheeki03/tirith
Terminal security for developers and AI agents. Intercepts homograph URLs, pipe-to-shell, ANSI injection, obfuscated payloads, data exfiltration, and…
 j3ssie/metabigor
OSINT reconnaissance tool for network discovery, subdomain enumeration, IP enrichment, and secret detection via certificate logs, Shodan, and GitHub…
 bountystrike/bountystrike-sh
Poor (rich?) man's bug bounty pipeline https://dubell.io
 daffainfo/oneliner-bugbounty
A collection oneliner scripts for bug bounty
 hilmiazizi/oorecon
Terminal UI for attack surface discovery: DNS recon, subdomain enumeration, port scanning, reverse IP, leaked login URLs, and JavaScript secret…
 git-akki/cso-vibecheck
Senior-CSO security audit skill for vibe-coded apps. 22-check audit anchored to real 2026 incidents (Moltbook, Lovable CVE-2025-48757). Drop-in…