
scan-shai-hulud
 qi-scape/scan-shai-hulud
Detect CVE-2026-45321 Mini Shai-Hulud supply chain compromise — scans for 170 npm + 2 PyPI poisoned packages across TanStack, Mistral AI, UiPath,…
forensicsincident-responseioc-management+6
1
qi-scape/scan-shai-huludDetect CVE-2026-45321 Mini Shai-Hulud supply chain compromise — scans for 170 npm + 2 PyPI poisoned packages across TanStack, Mistral AI, UiPath,…
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 pigyon/mcpwner
Model Context Protocol server for autonomous vulnerability discovery
 anchore/grype
A vulnerability scanner for container images and filesystems
 gautamvarmadatla/mcpsafetywarden
Proxy server that wraps MCP servers with behavioral profiling, security scanning, risk gating, and safe execution. Detects prompt injection,…
 jchable/miasma-toolkit
Detection & remediation toolkit for the Miasma / Shai-Hulud worm and CVE-2026-35603 (AI-agent/IDE config injection)
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
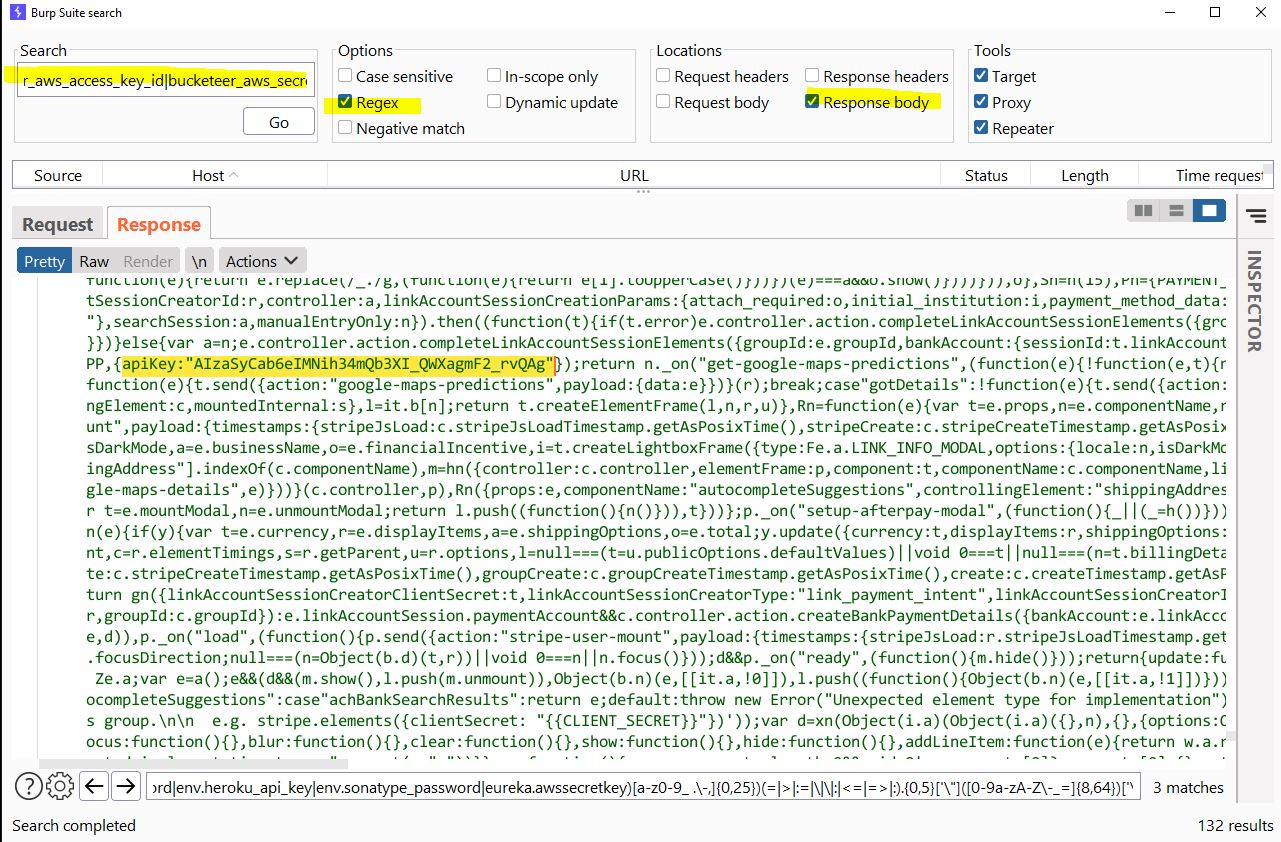 h4x0r-dz/leaked-credentials
how to look for Leaked Credentials !
 jingkaihe/matchlock
Ephemeral microVM sandbox for AI agents with network allowlisting, secret injection via MITM proxy, and VM-level isolation. Boots in under a second,…
 crissyfield/troll-a
Extracts secrets (passwords, API keys, tokens) from WARC web archives using Gitleaks rules. Supports HTTP, S3, local files, and compressed archives…
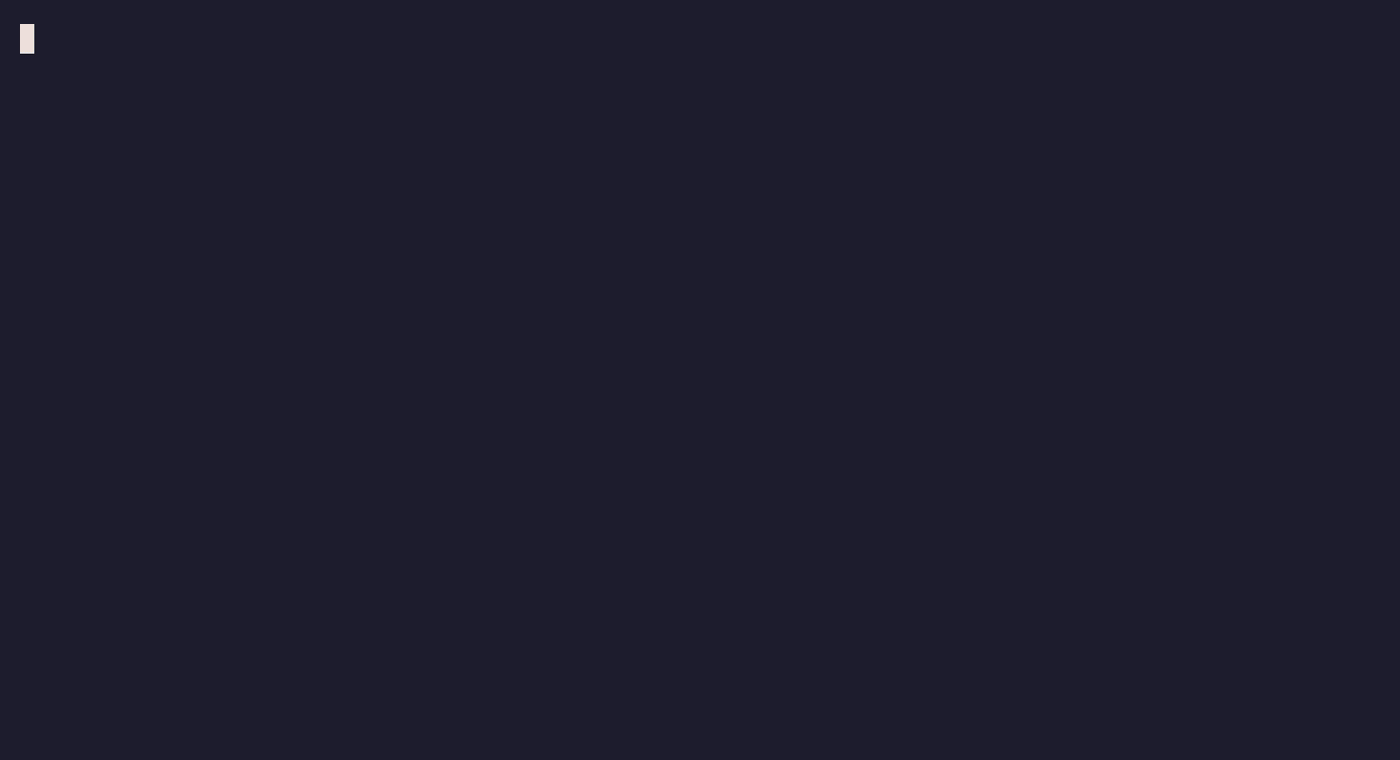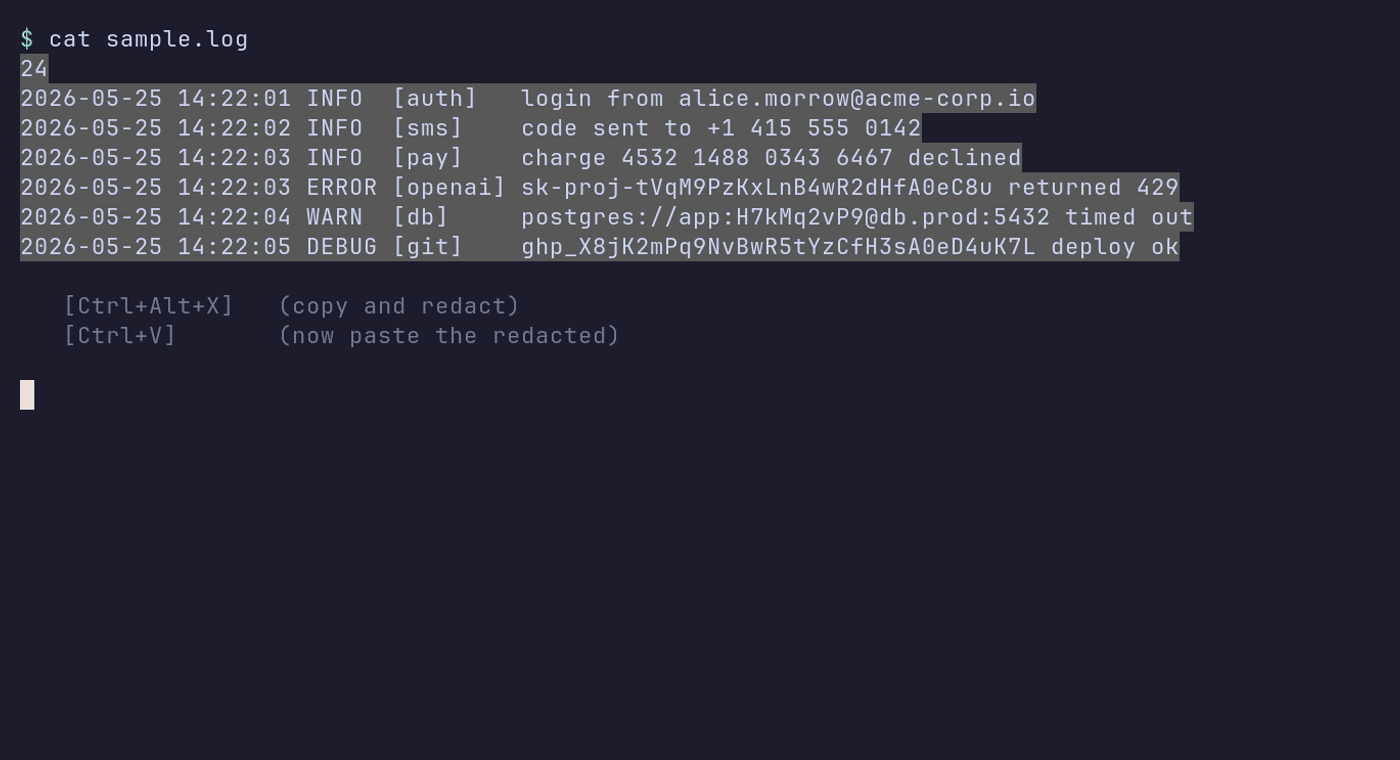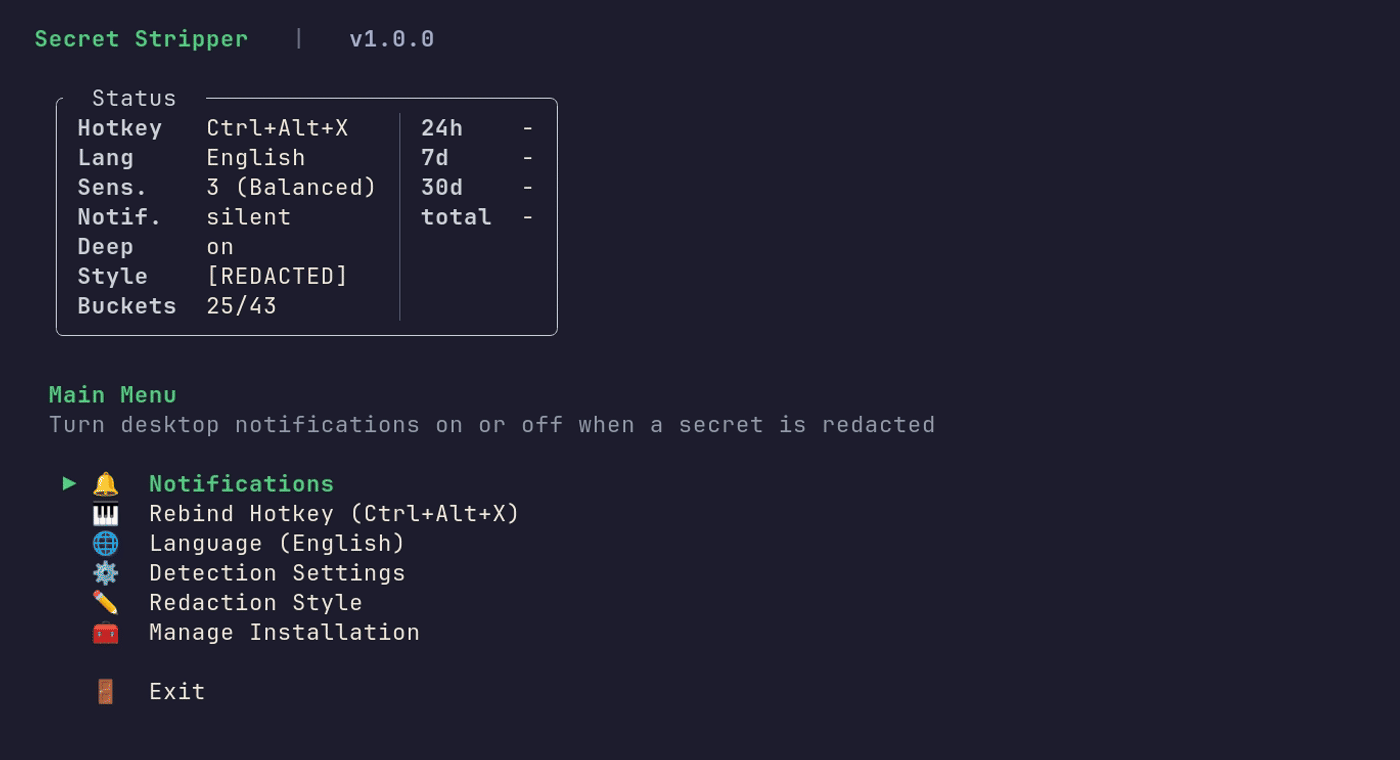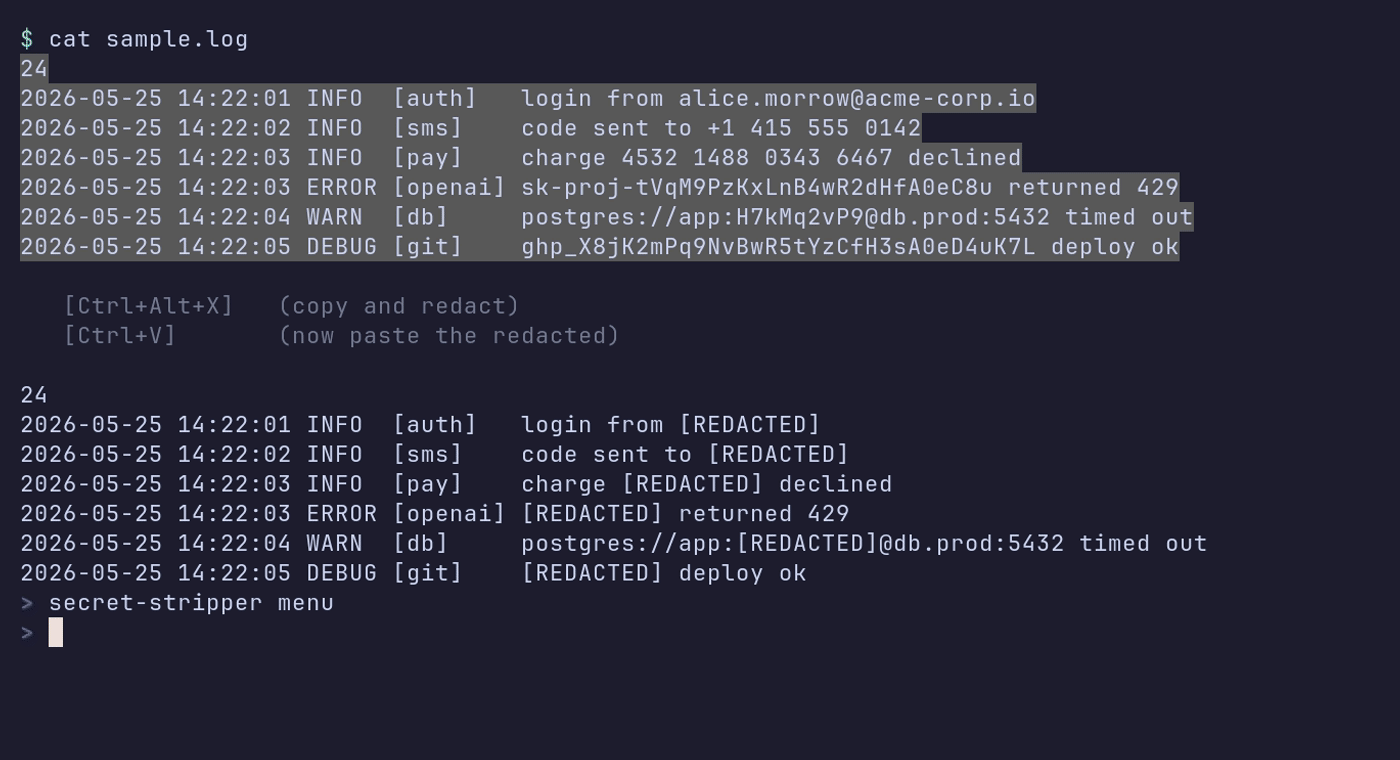 kalix127/secret-stripper
A small Rust CLI that strips secrets from your clipboard on demand.
 yeee3642/edu-recon
Authorized education-sector recon & triage orchestrator (nmap/dirsearch/sqlmap/hydra + CVE-2024-4577, secret/API-key leak, XSS, wp2shell) with a web…
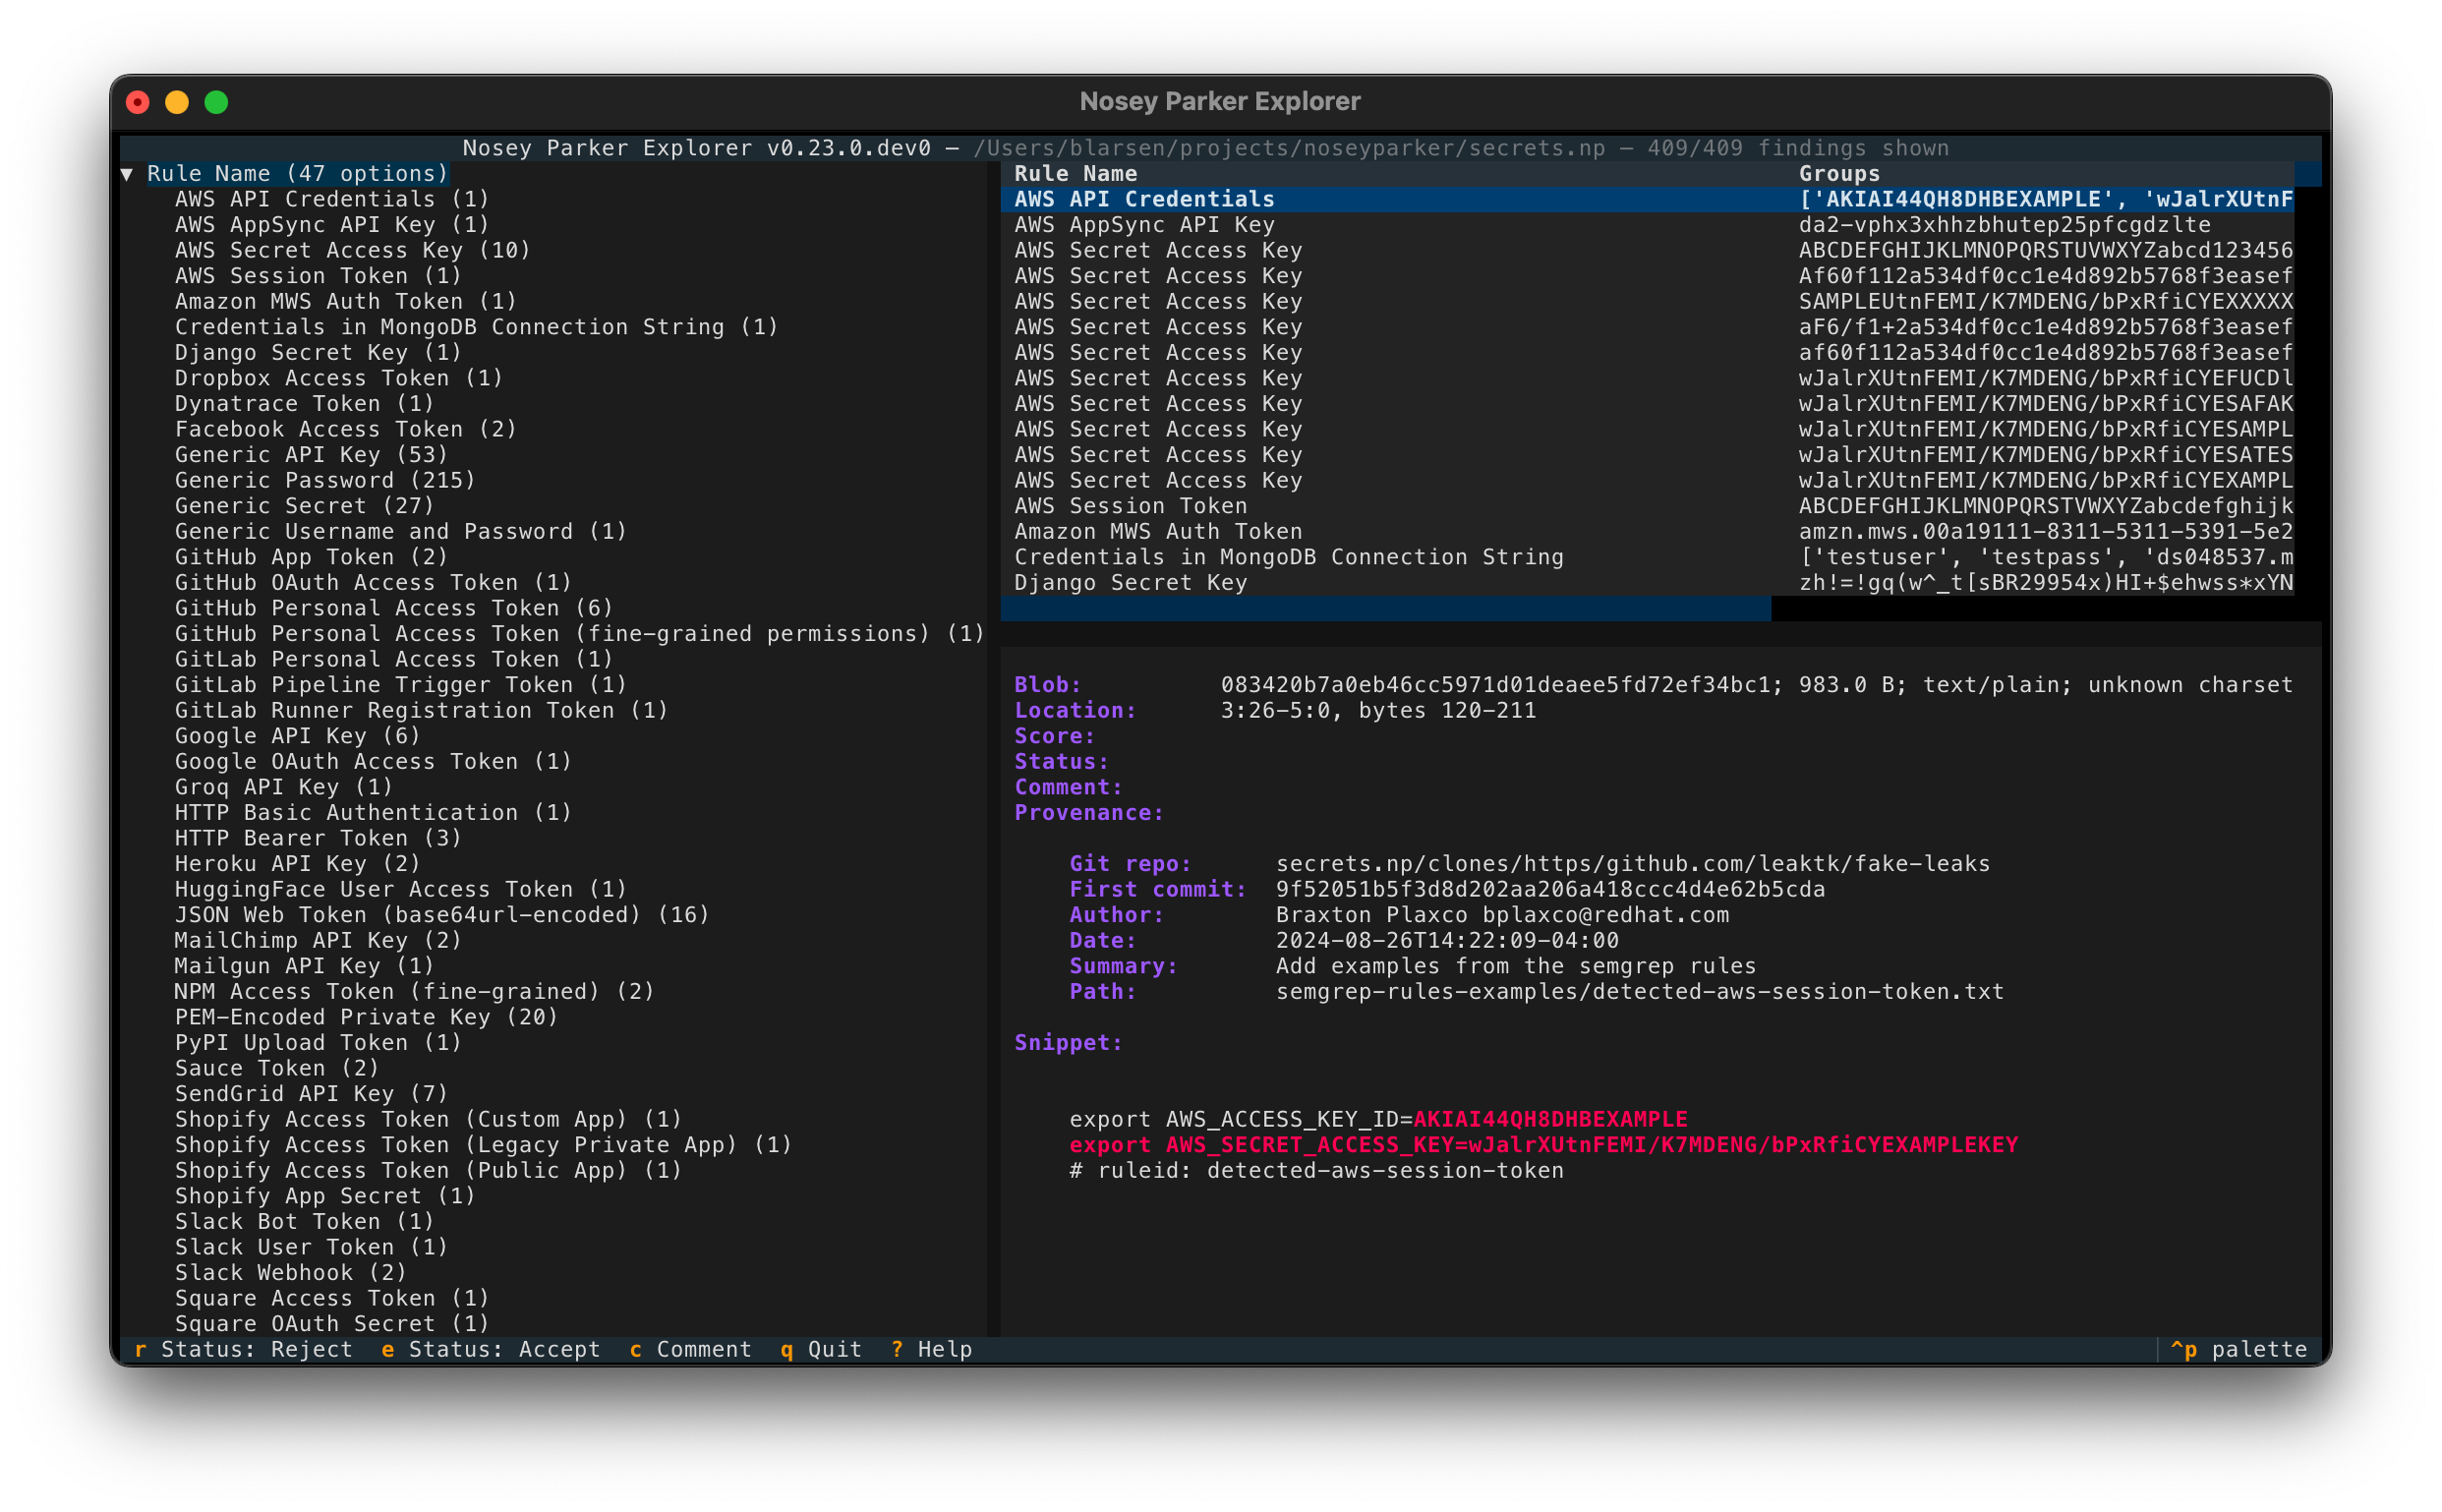 praetorian-inc/noseyparker
Nosey Parker is a command-line tool that finds secrets and sensitive information in textual data and Git history.
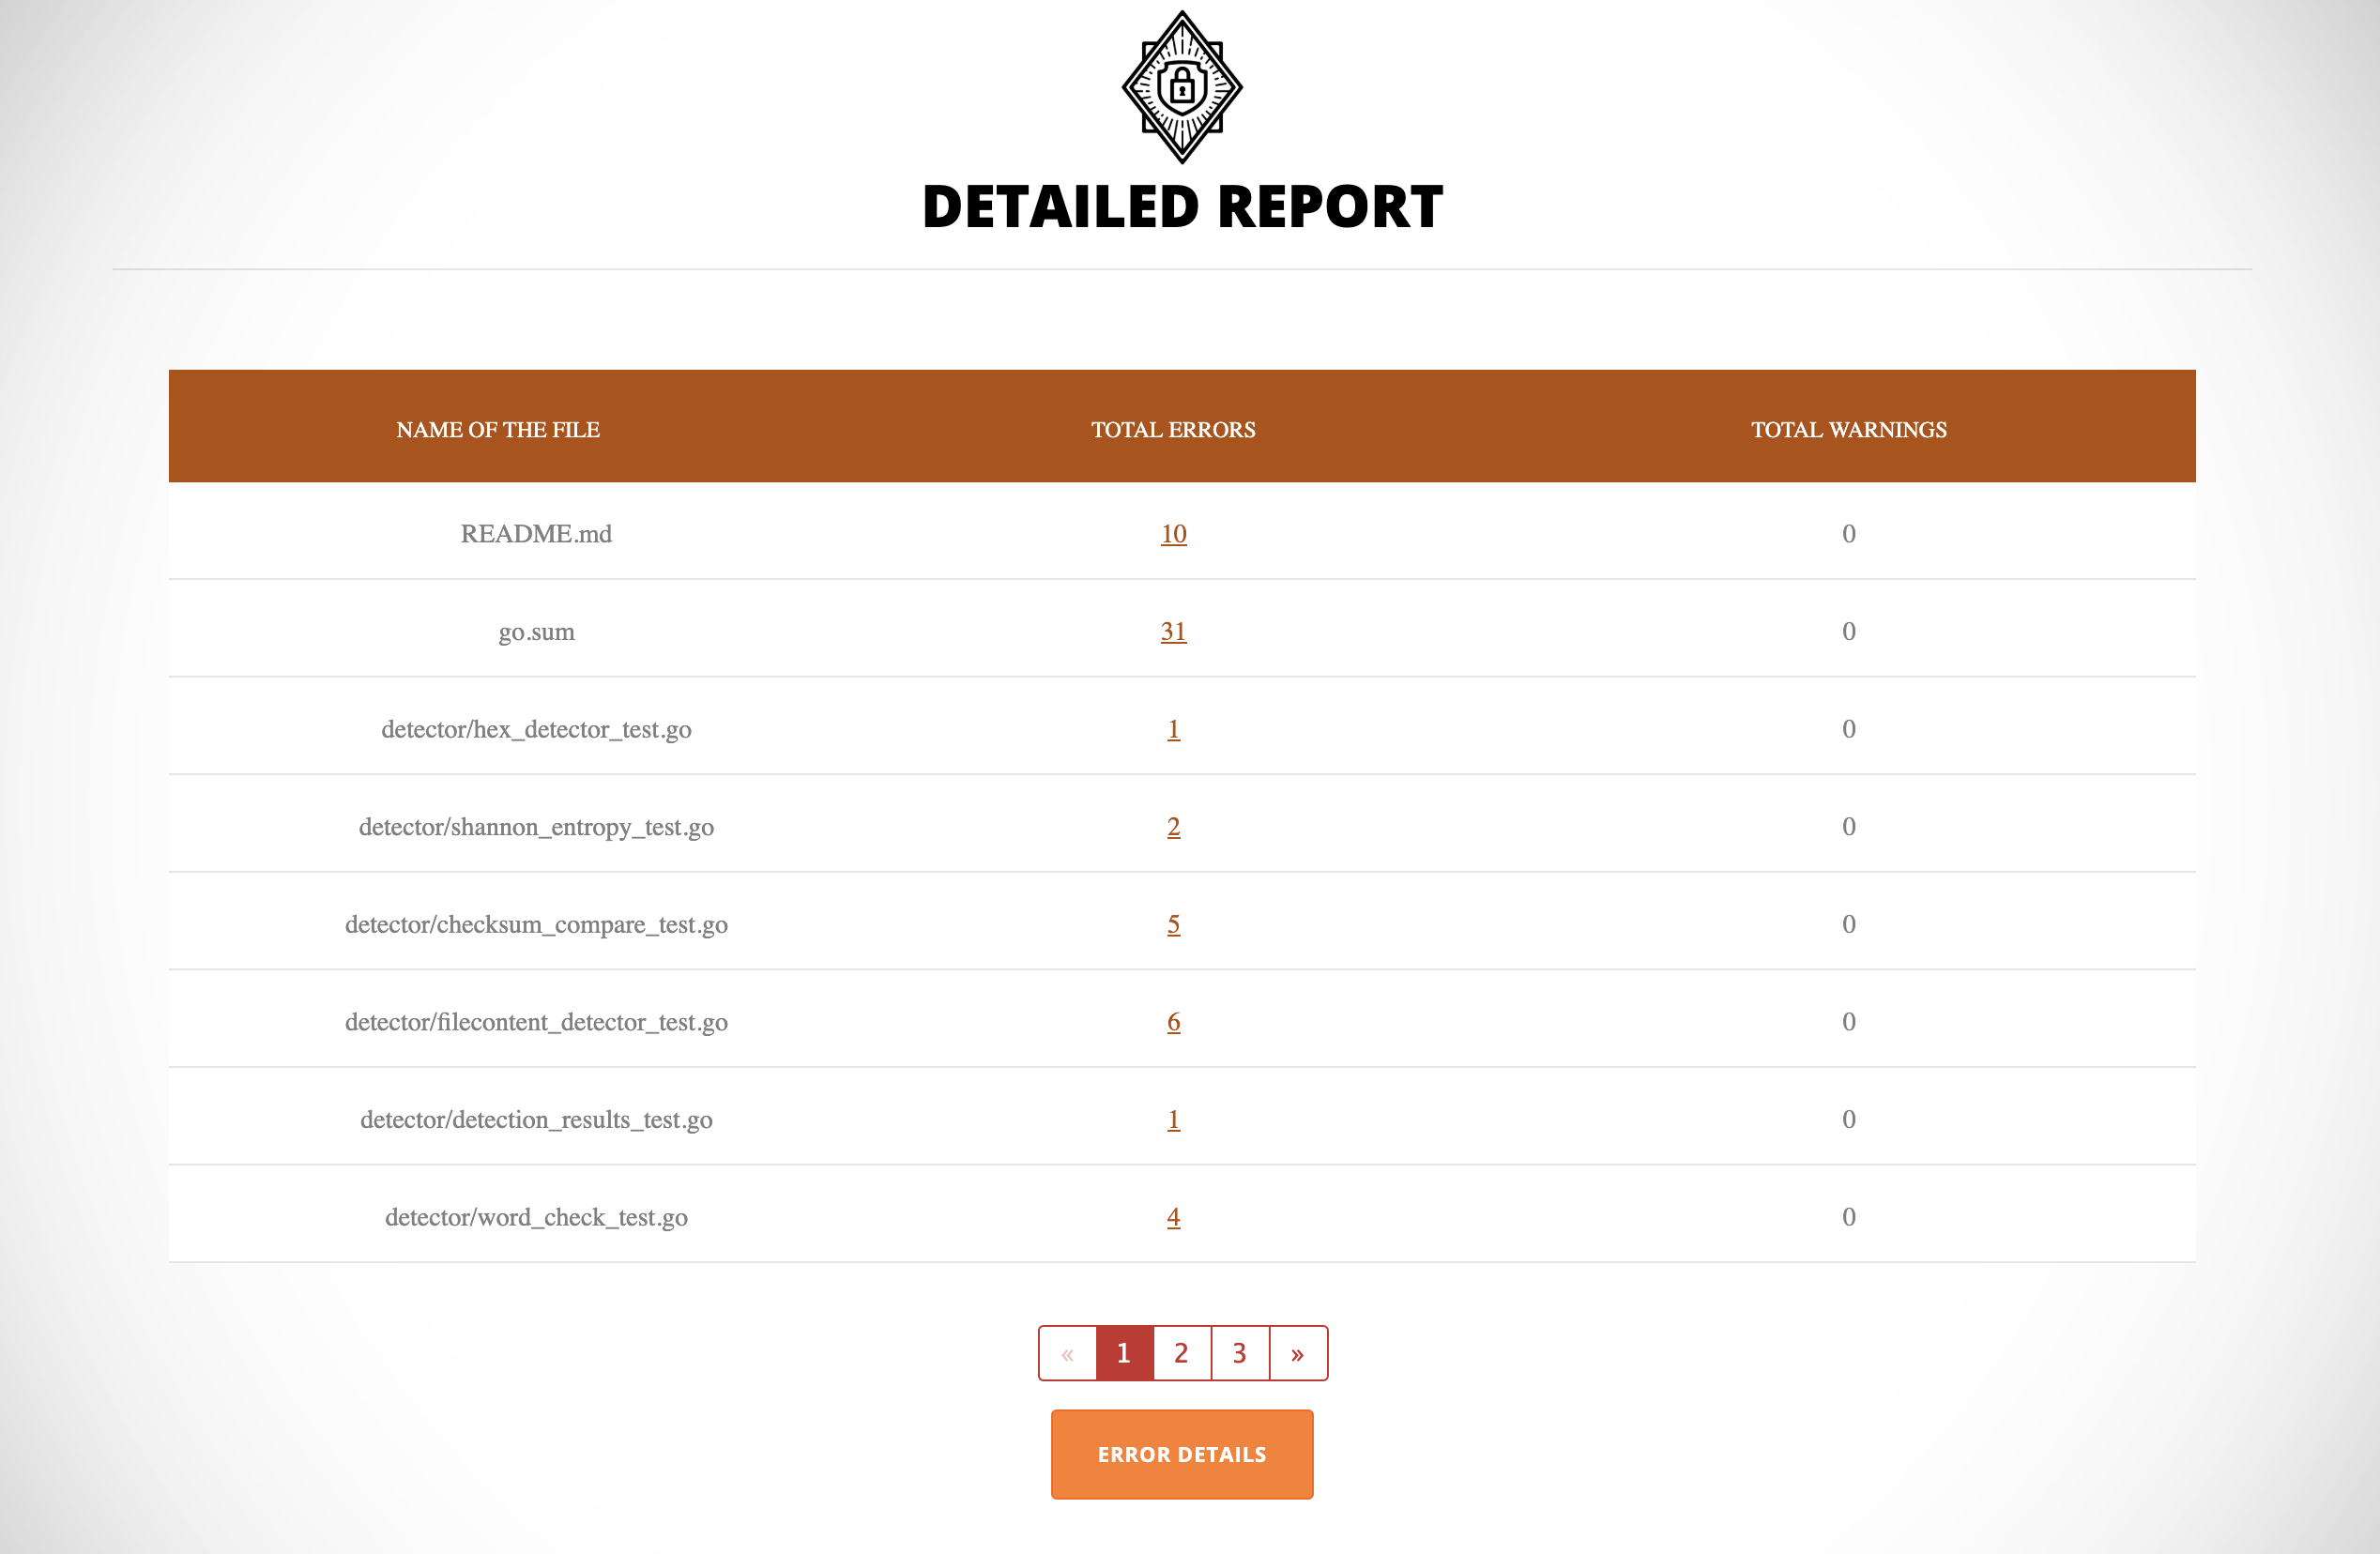 thoughtworks/talisman
Git hook-based secret scanner that detects tokens, passwords, and private keys in outgoing changesets, preventing sensitive data from being committed…
 synacktiv/nord-stream
Nord Stream is a tool that allows you to extract secrets stored inside CI/CD environments by deploying malicious pipelines. It currently supports…
 greatscott/enject
enject: Hide .env secrets from prAIng eyes: secrets live in local encrypted stores (per project) and are injected directly into apps at runtime,…