
vinifera
 zomato/vinifera
A GitHub recon/monitoring tool for finding internal leaks belonging to your organisation.
incident-responseinformation-gatheringosint+2
95
zomato/viniferaA GitHub recon/monitoring tool for finding internal leaks belonging to your organisation.
 arsbr/veritensor
The Anti-Virus for AI Artifacts & RAG Firewall. A static analysis tool scanning Models and Notebooks for RCE, Datasets and RAG docs for Data…
 msaad00/agent-bom
Open security scanner and self-hosted control plane for AI, MCP, and cloud. One evidence model — run scans in your environment, centralize findings,…
 davidcarliez/cover
Keep private data, internal infrastructure and secrets out of cloud coding agents without breaking your workflow.
 farenhytee/database-sentinel
Claude Skill that audits your projects for RLS misconfigurations, exposed keys, auth bypasses, and storage vulnerabilities. 27 anti-patterns sourced…
 tech4242/aquaman
🔱 The only independent credential proxy for AI agents: bring-your-own-vault isolation & least-privilege request policies. Your keys stay where you…
 mohamed--abdel-maksoud/pisiguard
PISIGuard runs entirely in your browser. It spots names, email addresses, phone numbers, credit card numbers, passwords, API keys, and more, replaces…
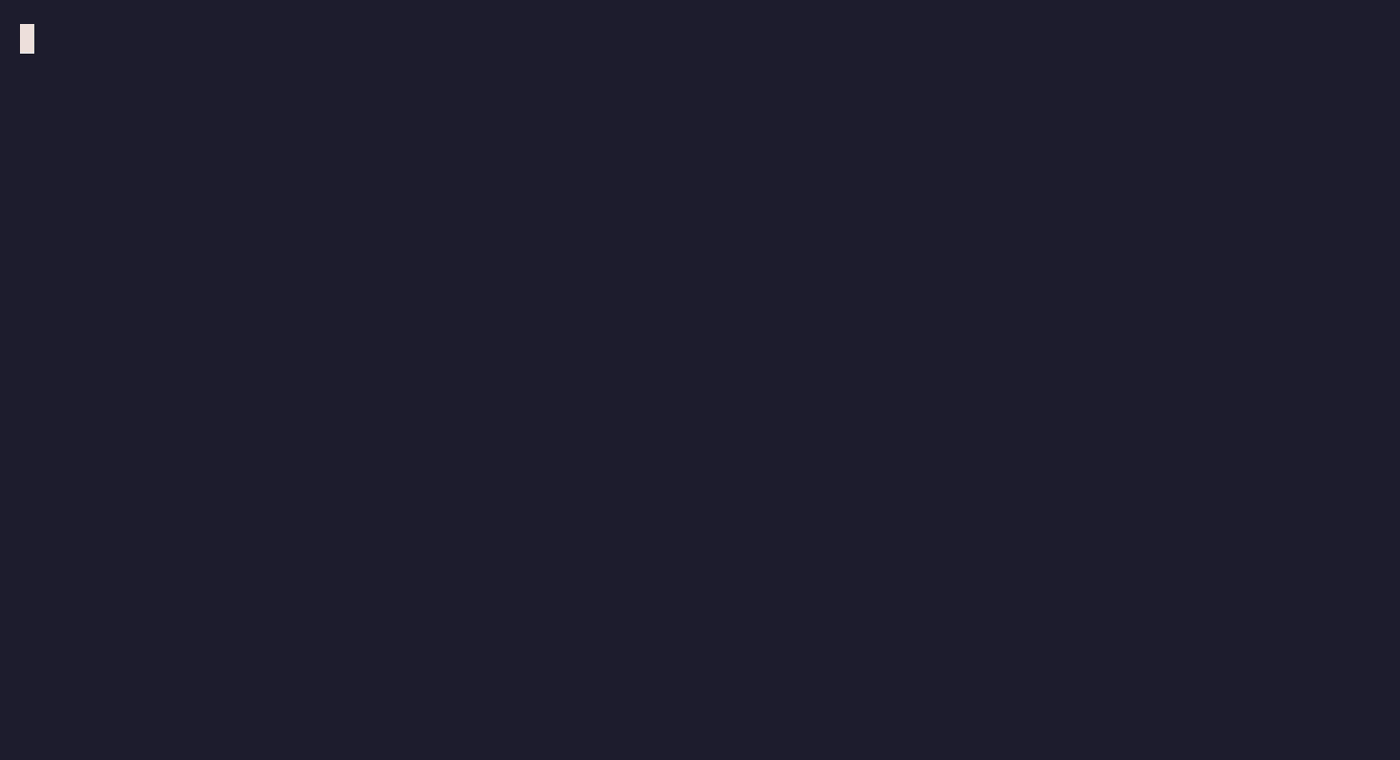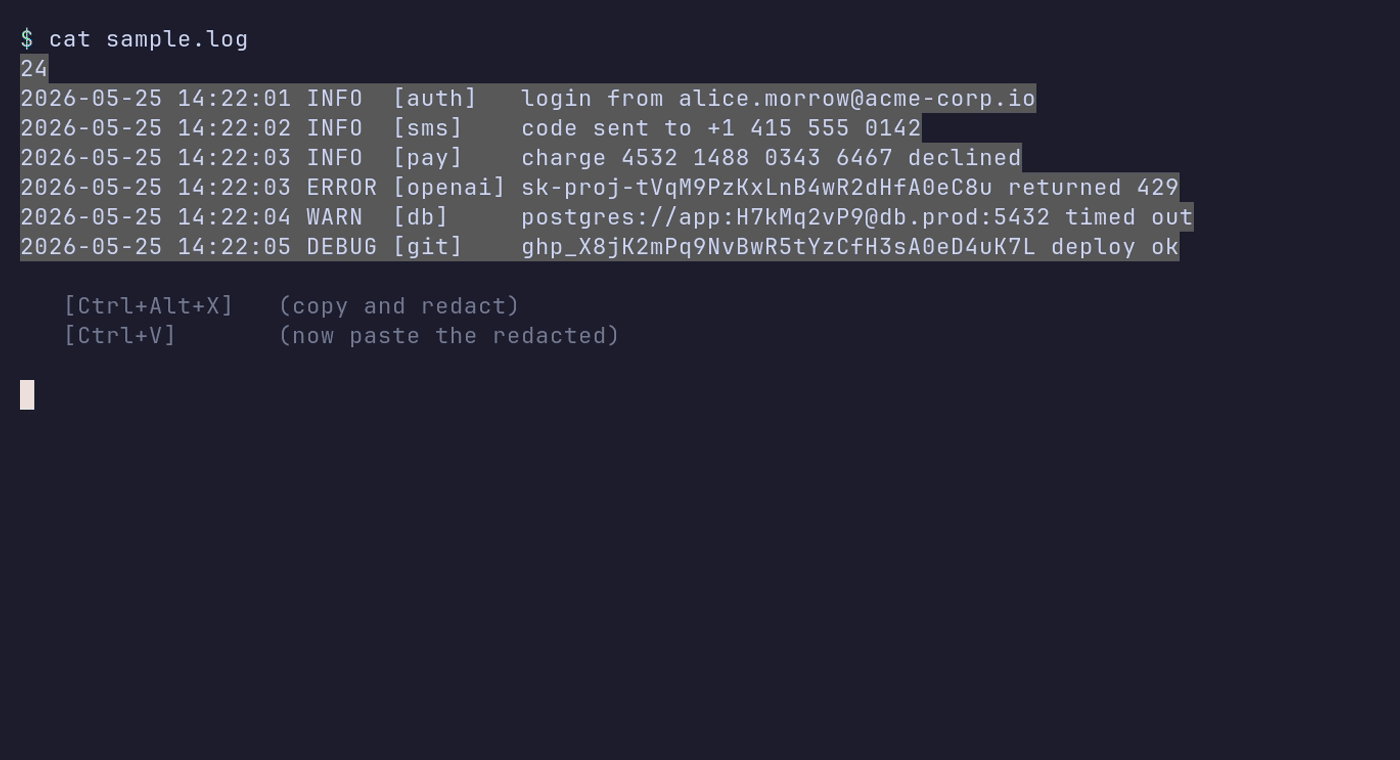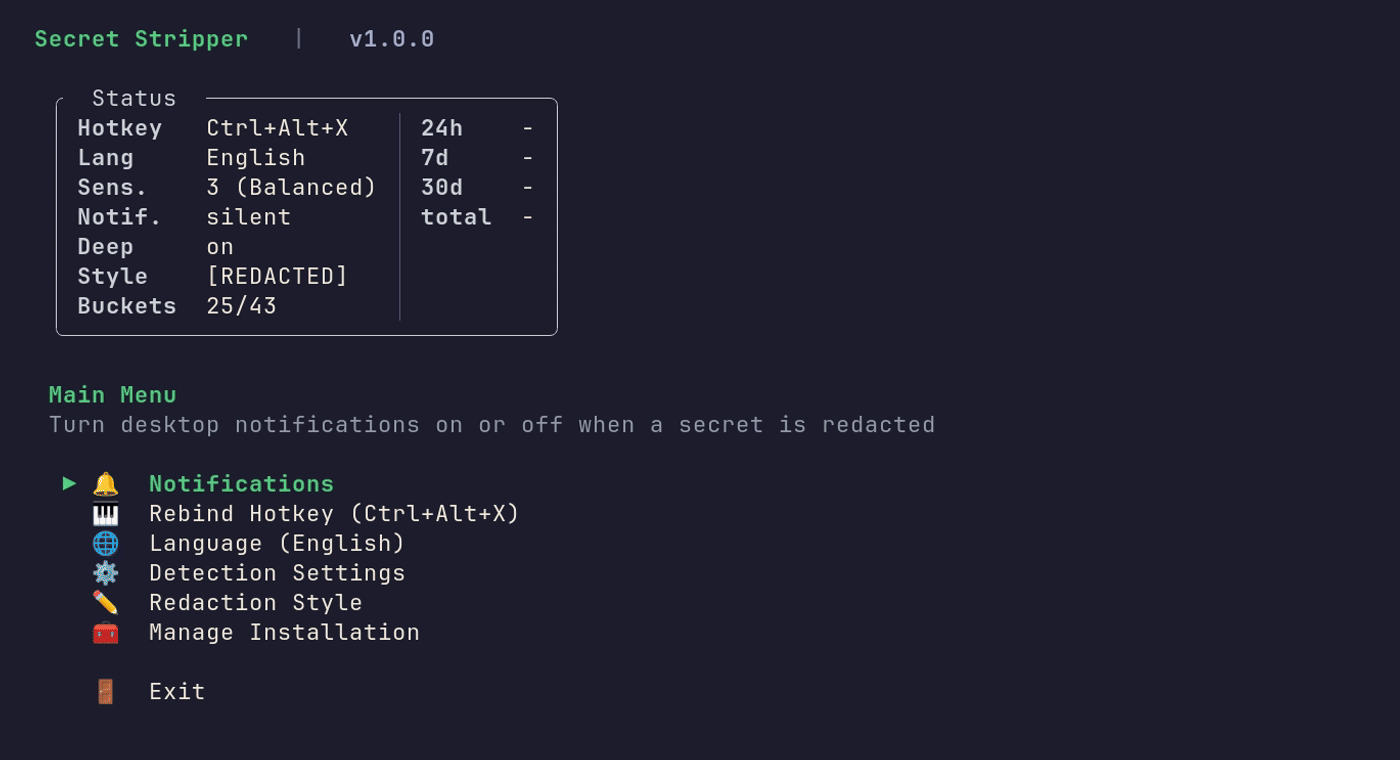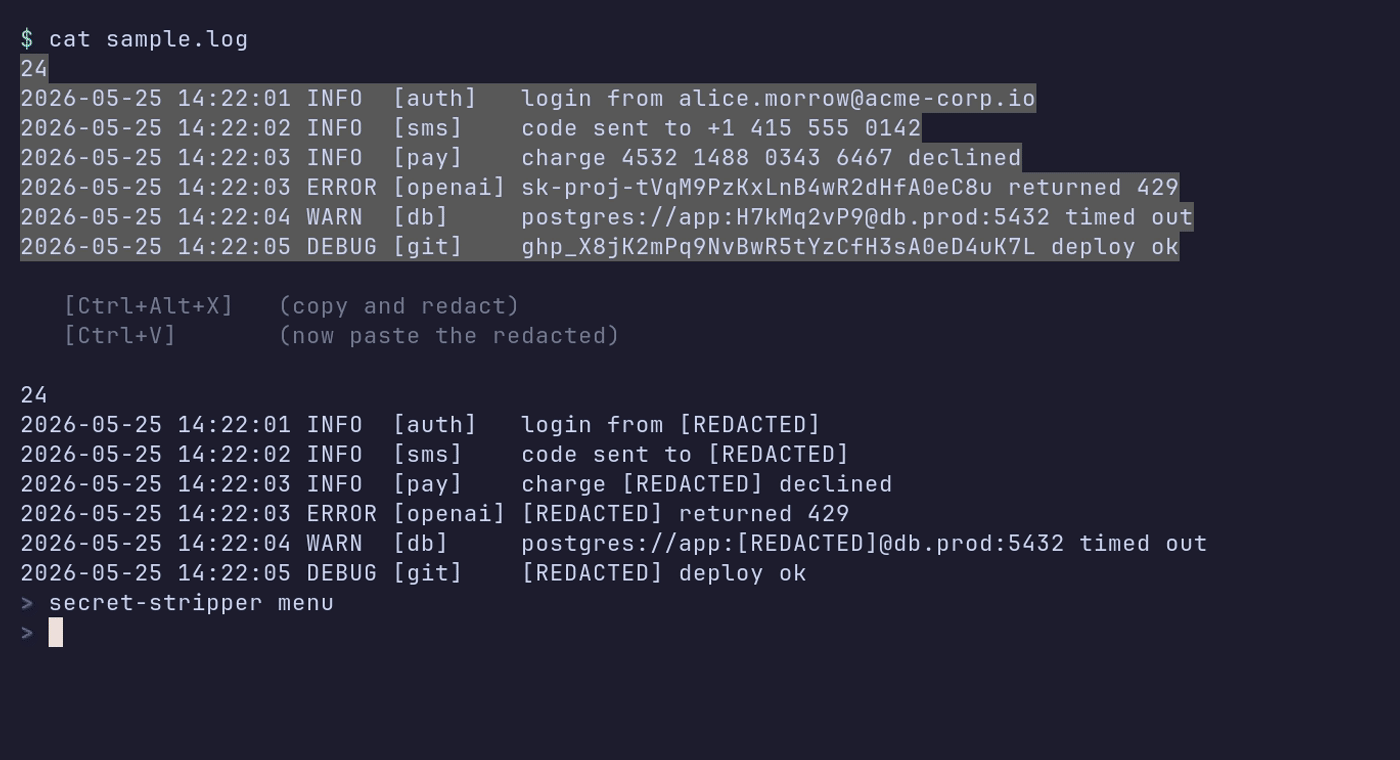 kalix127/secret-stripper
A small Rust CLI that strips secrets from your clipboard on demand.
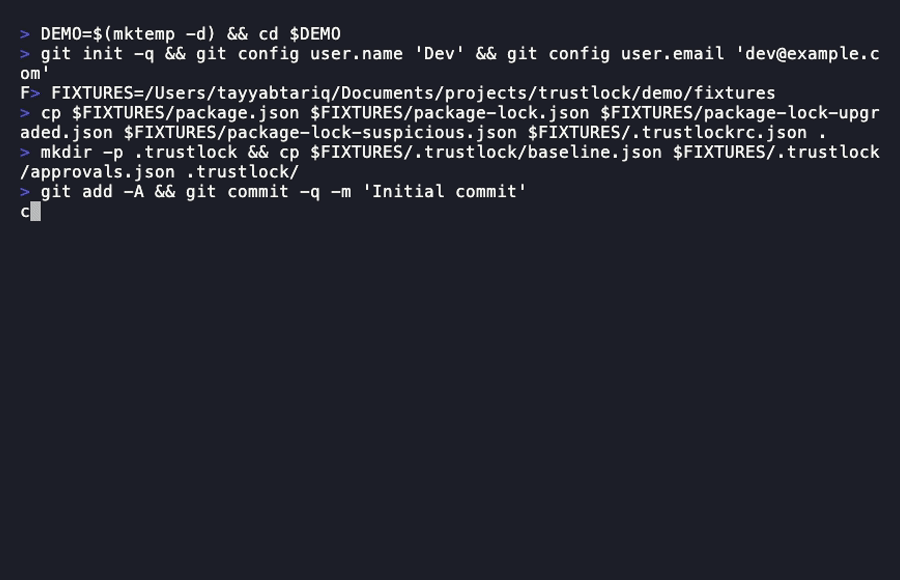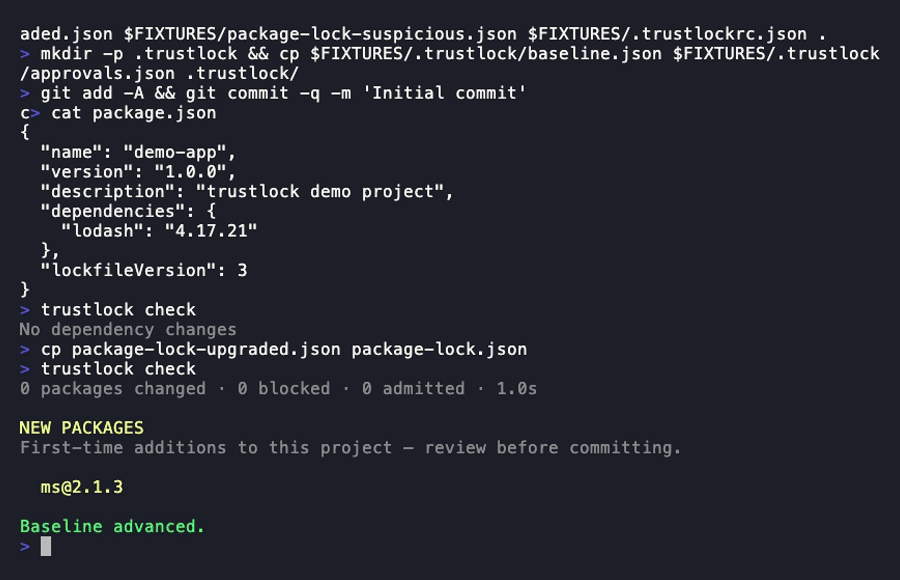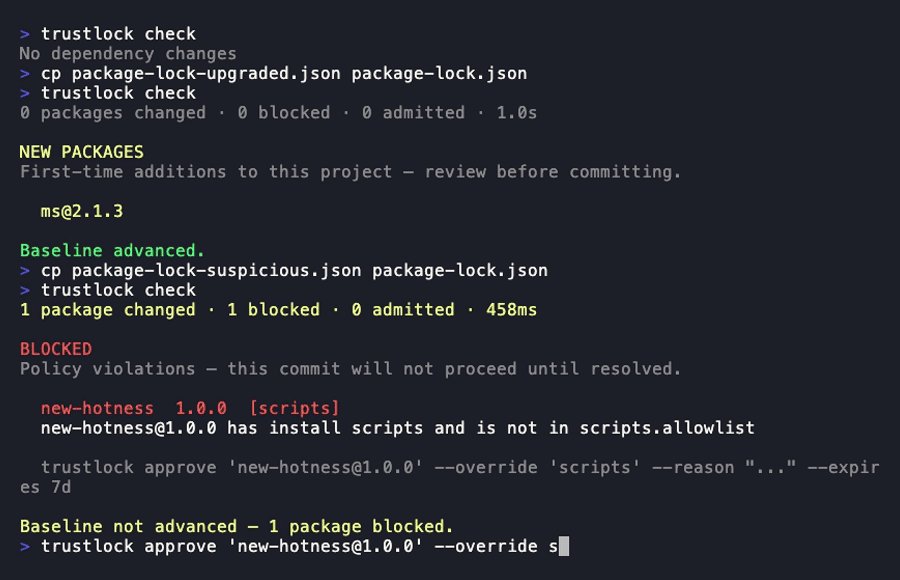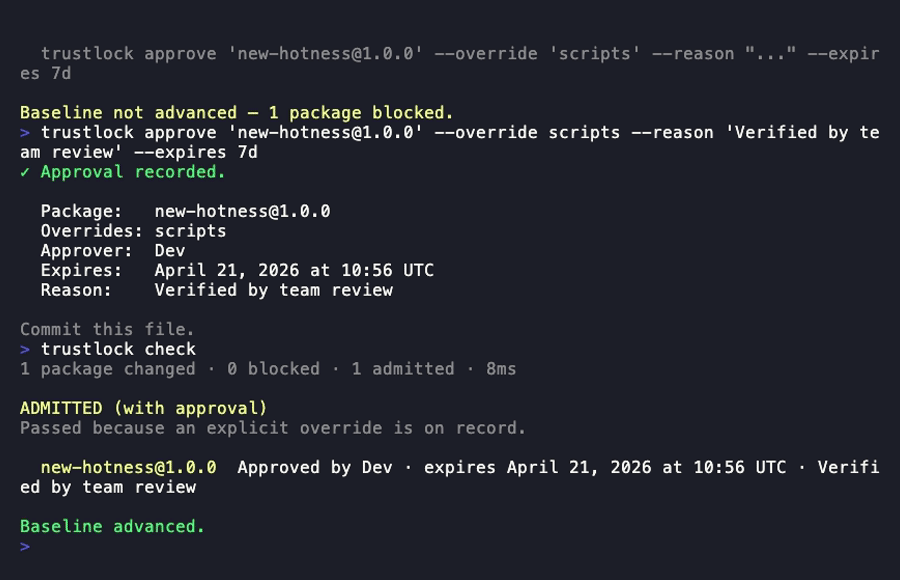 tayyabt/trustlock
A Git-native dependency admission controller. Evaluates trust signals on every dependency change and blocks commits or builds when packages fail your…
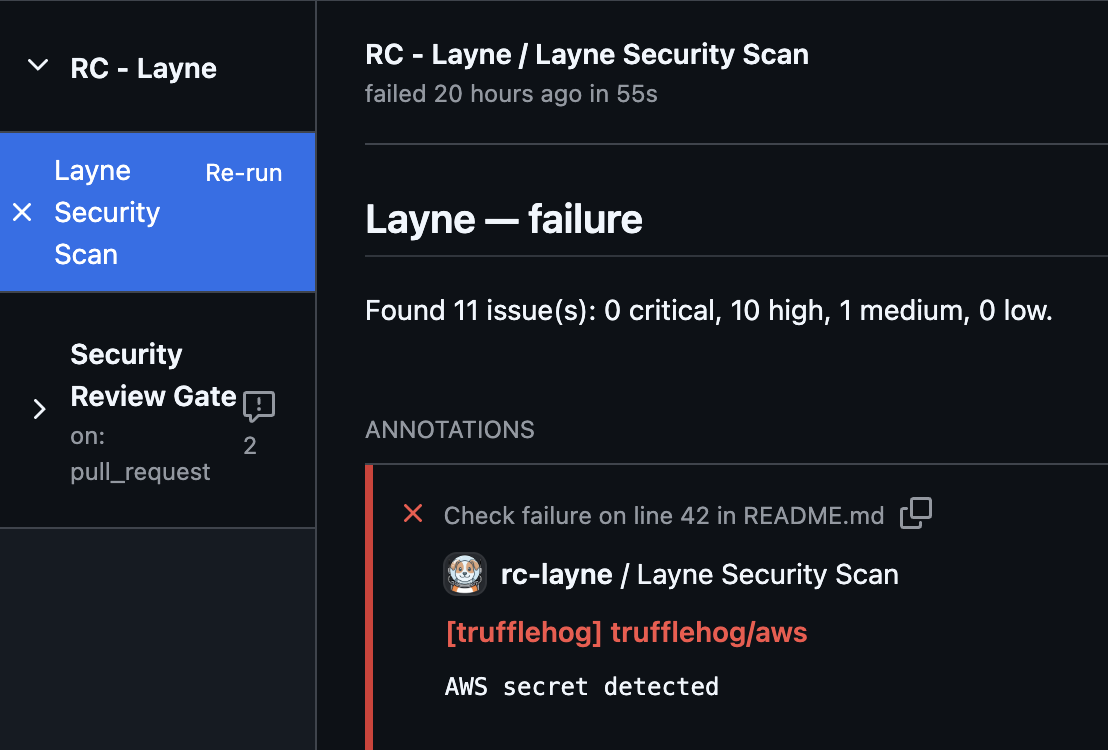 rocketchat/layne
A doggo that helps look for security issues in your repositories.
 anee769/conduit
On-prem API gateway for AI coding agents with per-engineer cost attribution, hard budgets, egress governance (secrets/entity scanning), context-rot…
 adversis/screenscrub
Find credentials in screenshots, save them to your secret manager, and irreversibly redact them from the image — local, offline, OCR-based.
 tanmayshahane/kyubisweep
A lightweight, cross-platform CLI tool that scans your filesystem to detect exposed secrets, API keys, and tokens. Built with Go for maximum…
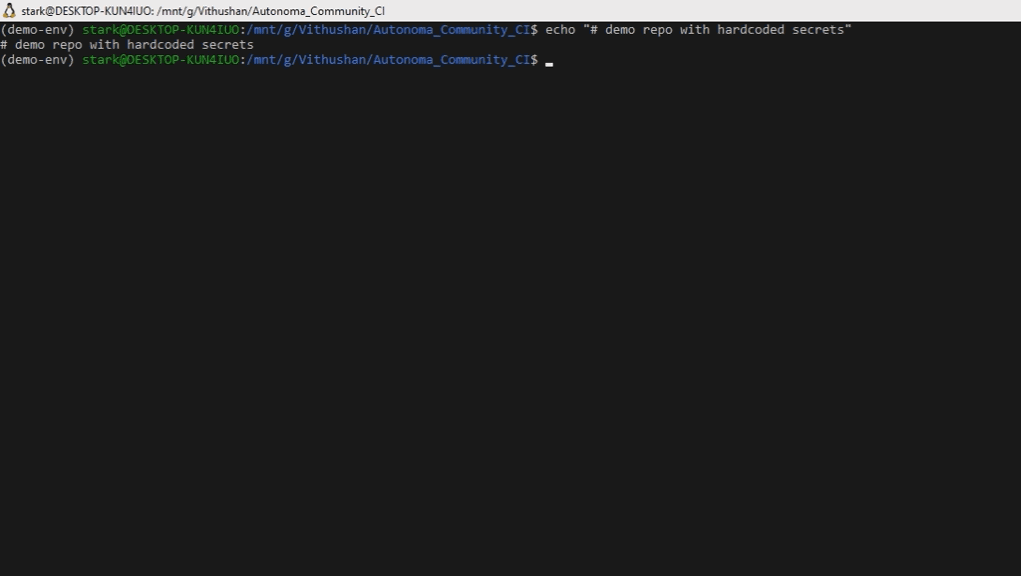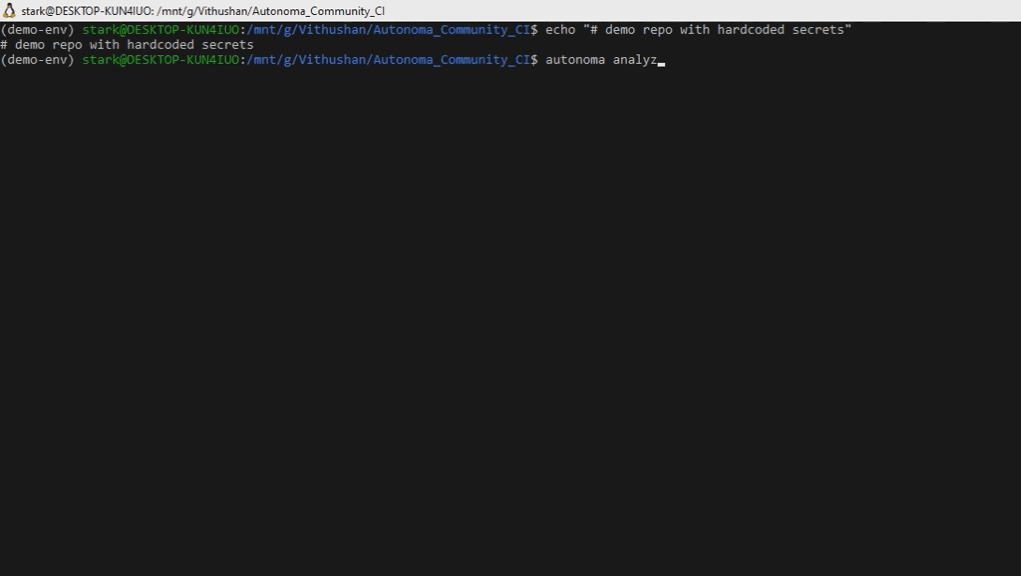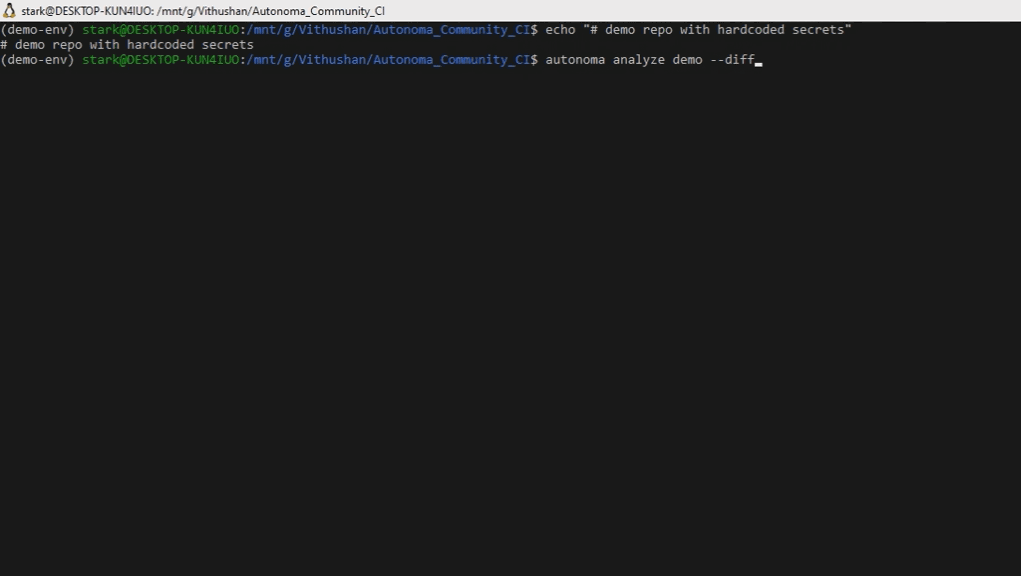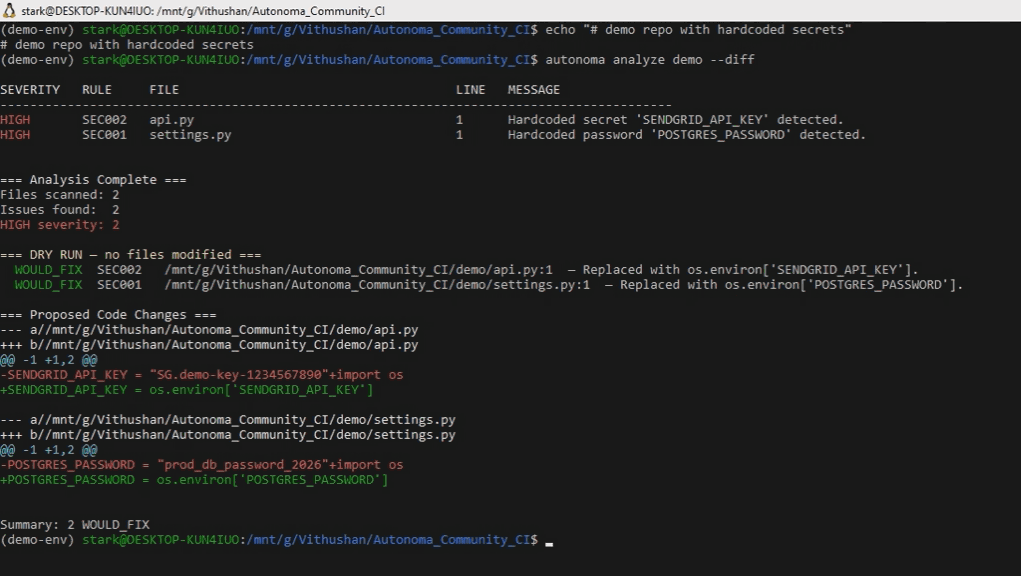 vihaaninnovations/autonoma
Detects and auto-fixes hardcoded secrets in Python repos — refuses when the fix could break your code
 cybergabisoft/depalert
DepAlert is an open-source security gate for your CI/CD pipeline. It analyzes SBOMs against malware intelligence data and quickly tells you whether…
 shakilkhatri/scanner-for-cve-2025-55182-vulnerability
CVE-2025-55182 Detector. Find which of your GitHub repositories are exposed to the critical React/Next.js RCE vulnerability and generate a clean…
 gmh5225/actions-secrets
Adding this GitHub Action will scan your repository for sensitive data in your source code. We find things like passwords, server host strings, API…
 maweil/bidi_char_detector
Checks your files for existence of Unicode BIDI characters which can be misused for supply chain attacks. See CVE-2021-42574