

trufflehog
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
cloud-securitycode-analysisdevsecops+6
trufflesecurity/trufflehogFind, verify, and analyze leaked credentials
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
 nolabs-ai/nono
agent runtime security - zero trust, zero setup, zero latency agent sandboxing
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
 snyk/cli
Snyk CLI scans and monitors your projects for security vulnerabilities.
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 xddxdd/nixos-config
Lan Tian's NixOS Configuration
 hashgraph-online/hol-guard
Open-source antivirus and firewall for AI agents: block risky tools, secret access, prompt injection, malicious packages, MCP servers, plugins, and…
 nvidia/skillspector
Security scanner for AI agent skills. Detect vulnerabilities, malicious patterns, security risks, prompt injection, data exfiltration, and…
 sheeki03/tirith
Terminal security for developers and AI agents. Intercepts homograph URLs, pipe-to-shell, ANSI injection, obfuscated payloads, data exfiltration, and…
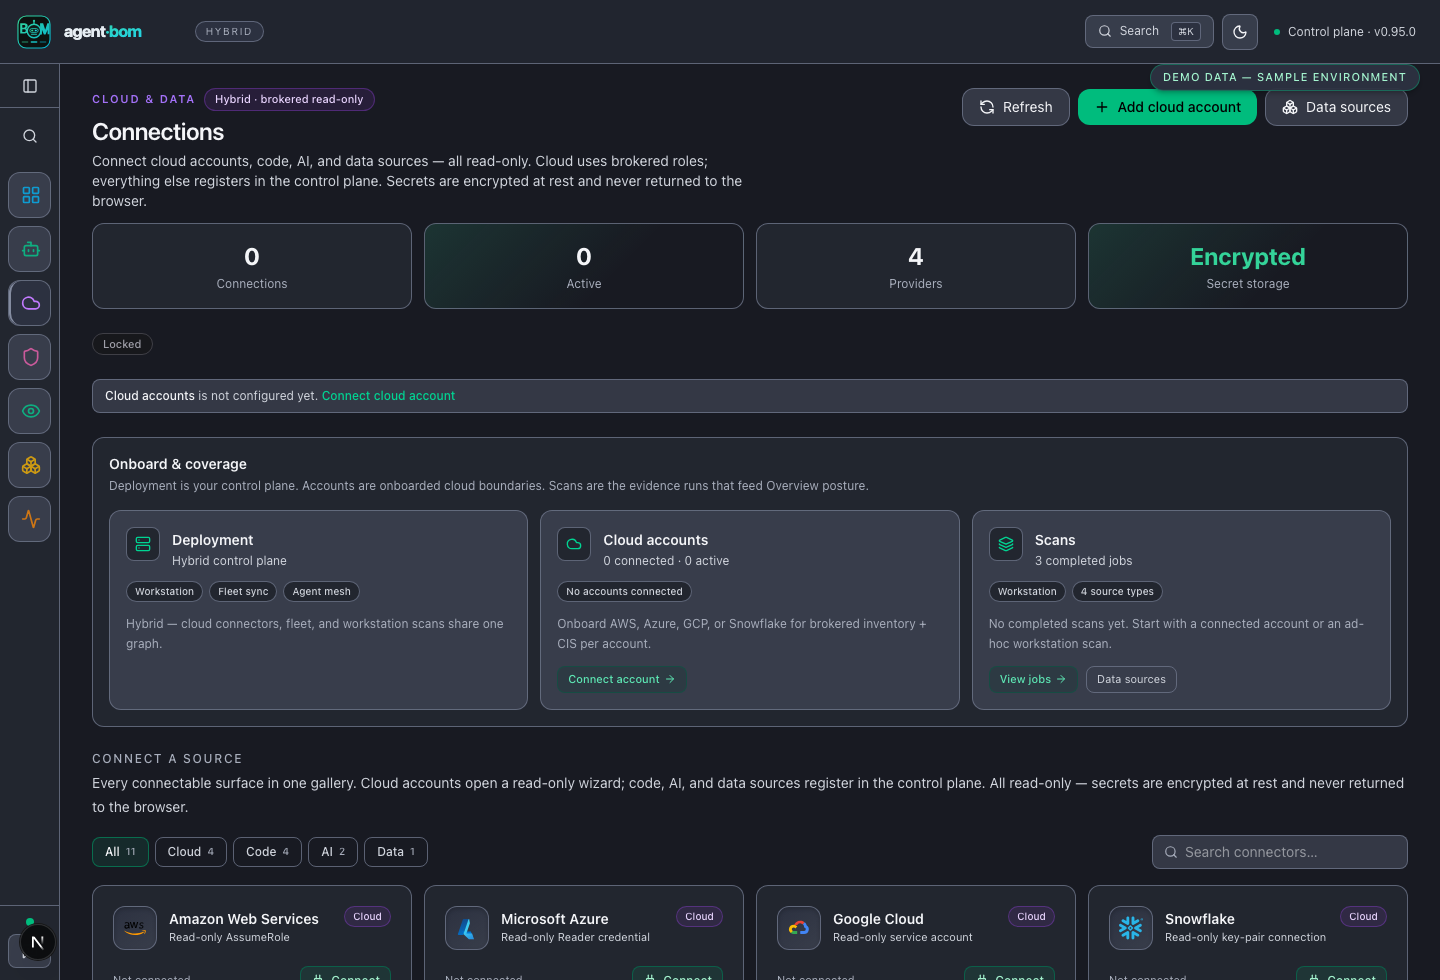 msaad00/agent-bom
AI supply-chain BOM: every agent, MCP server and AI package, and what each one can reach. Open-source scanner and self-hosted control plane for code,…
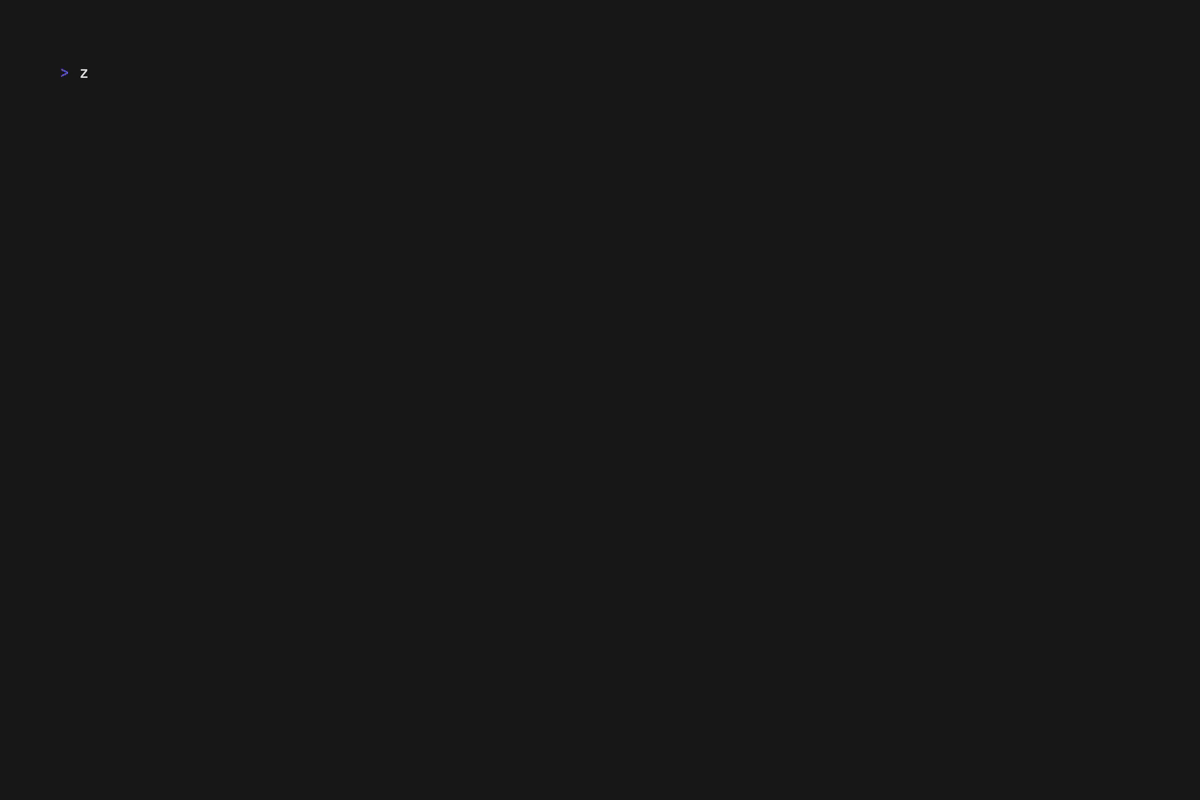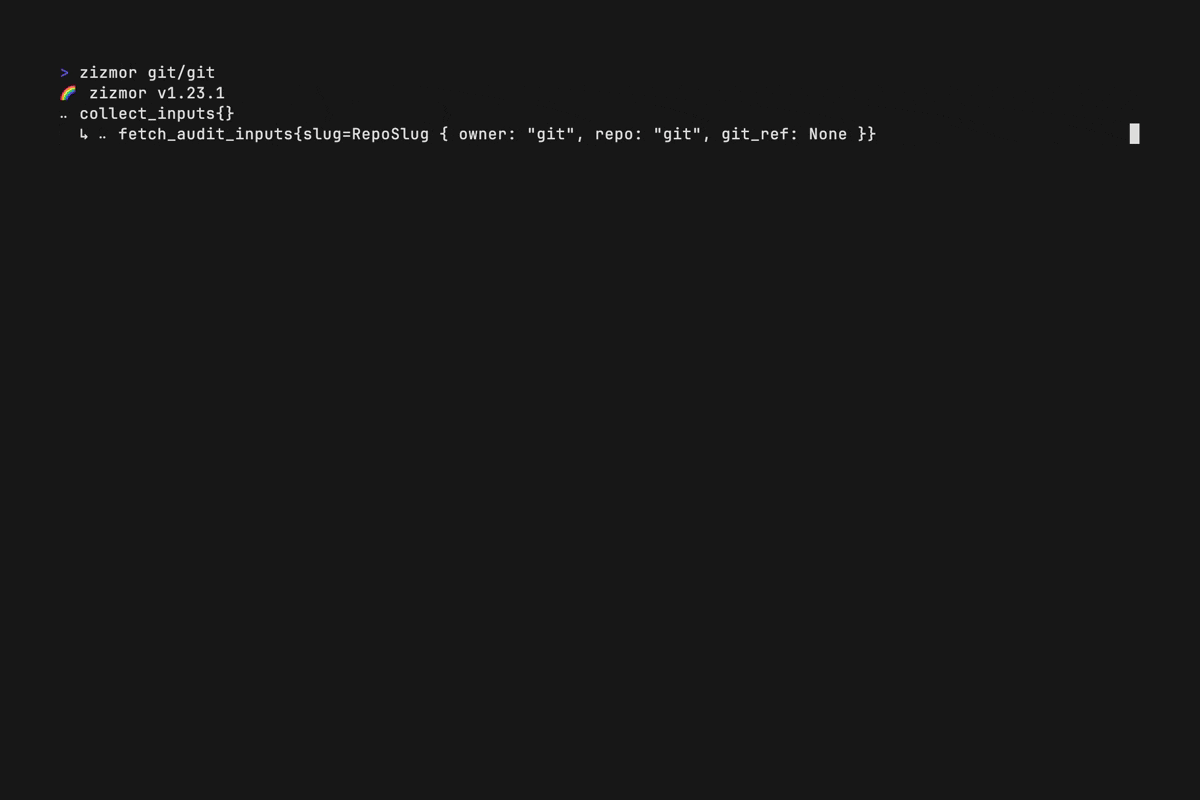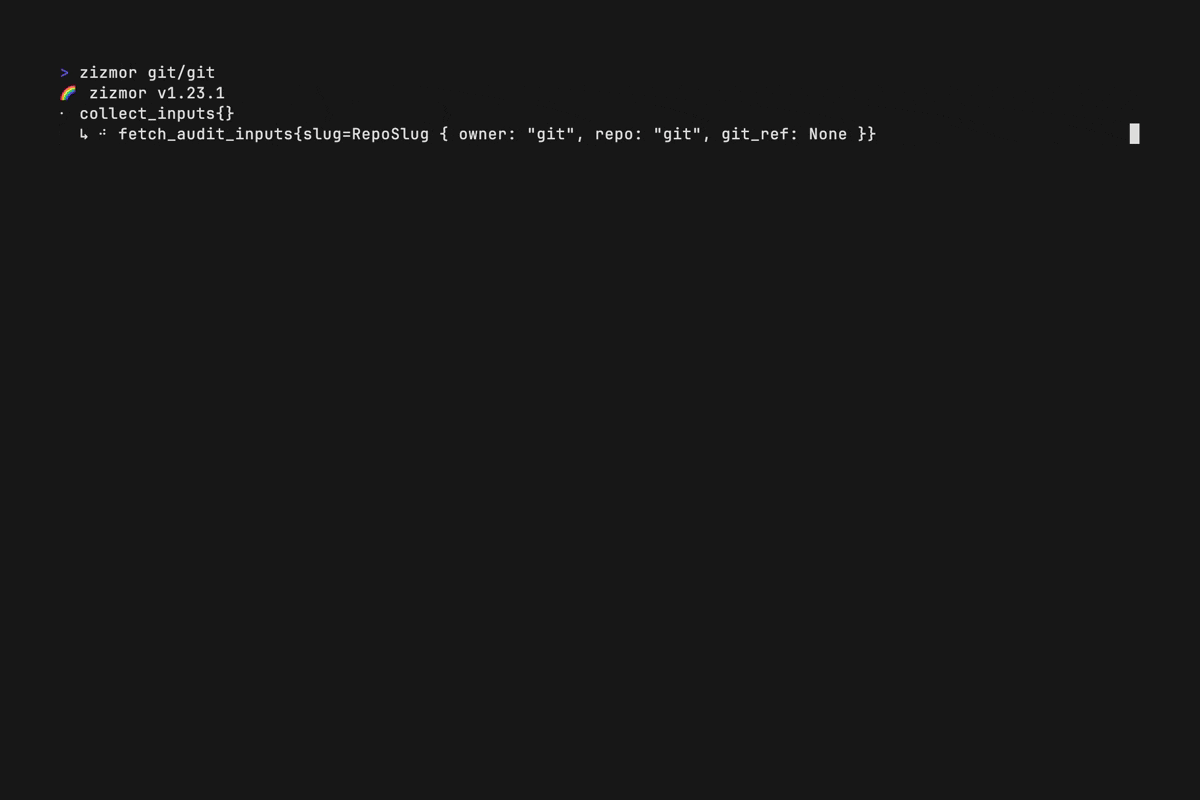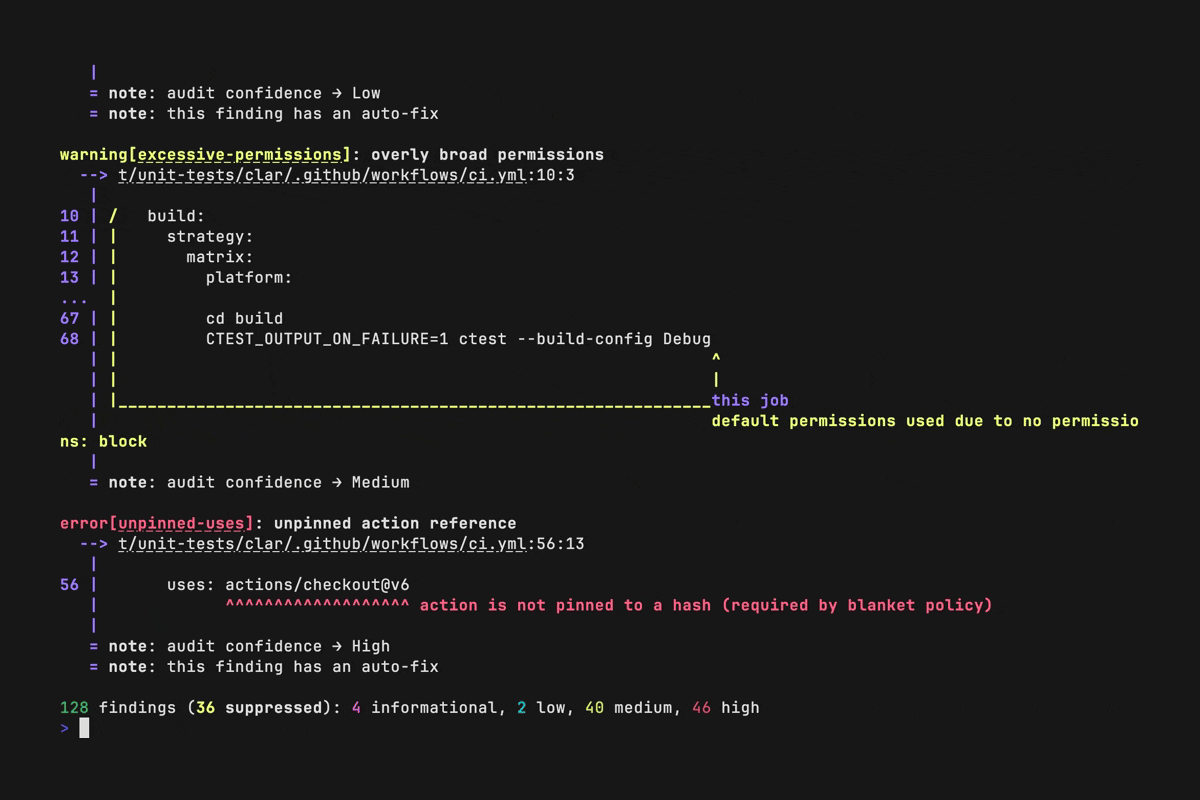 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
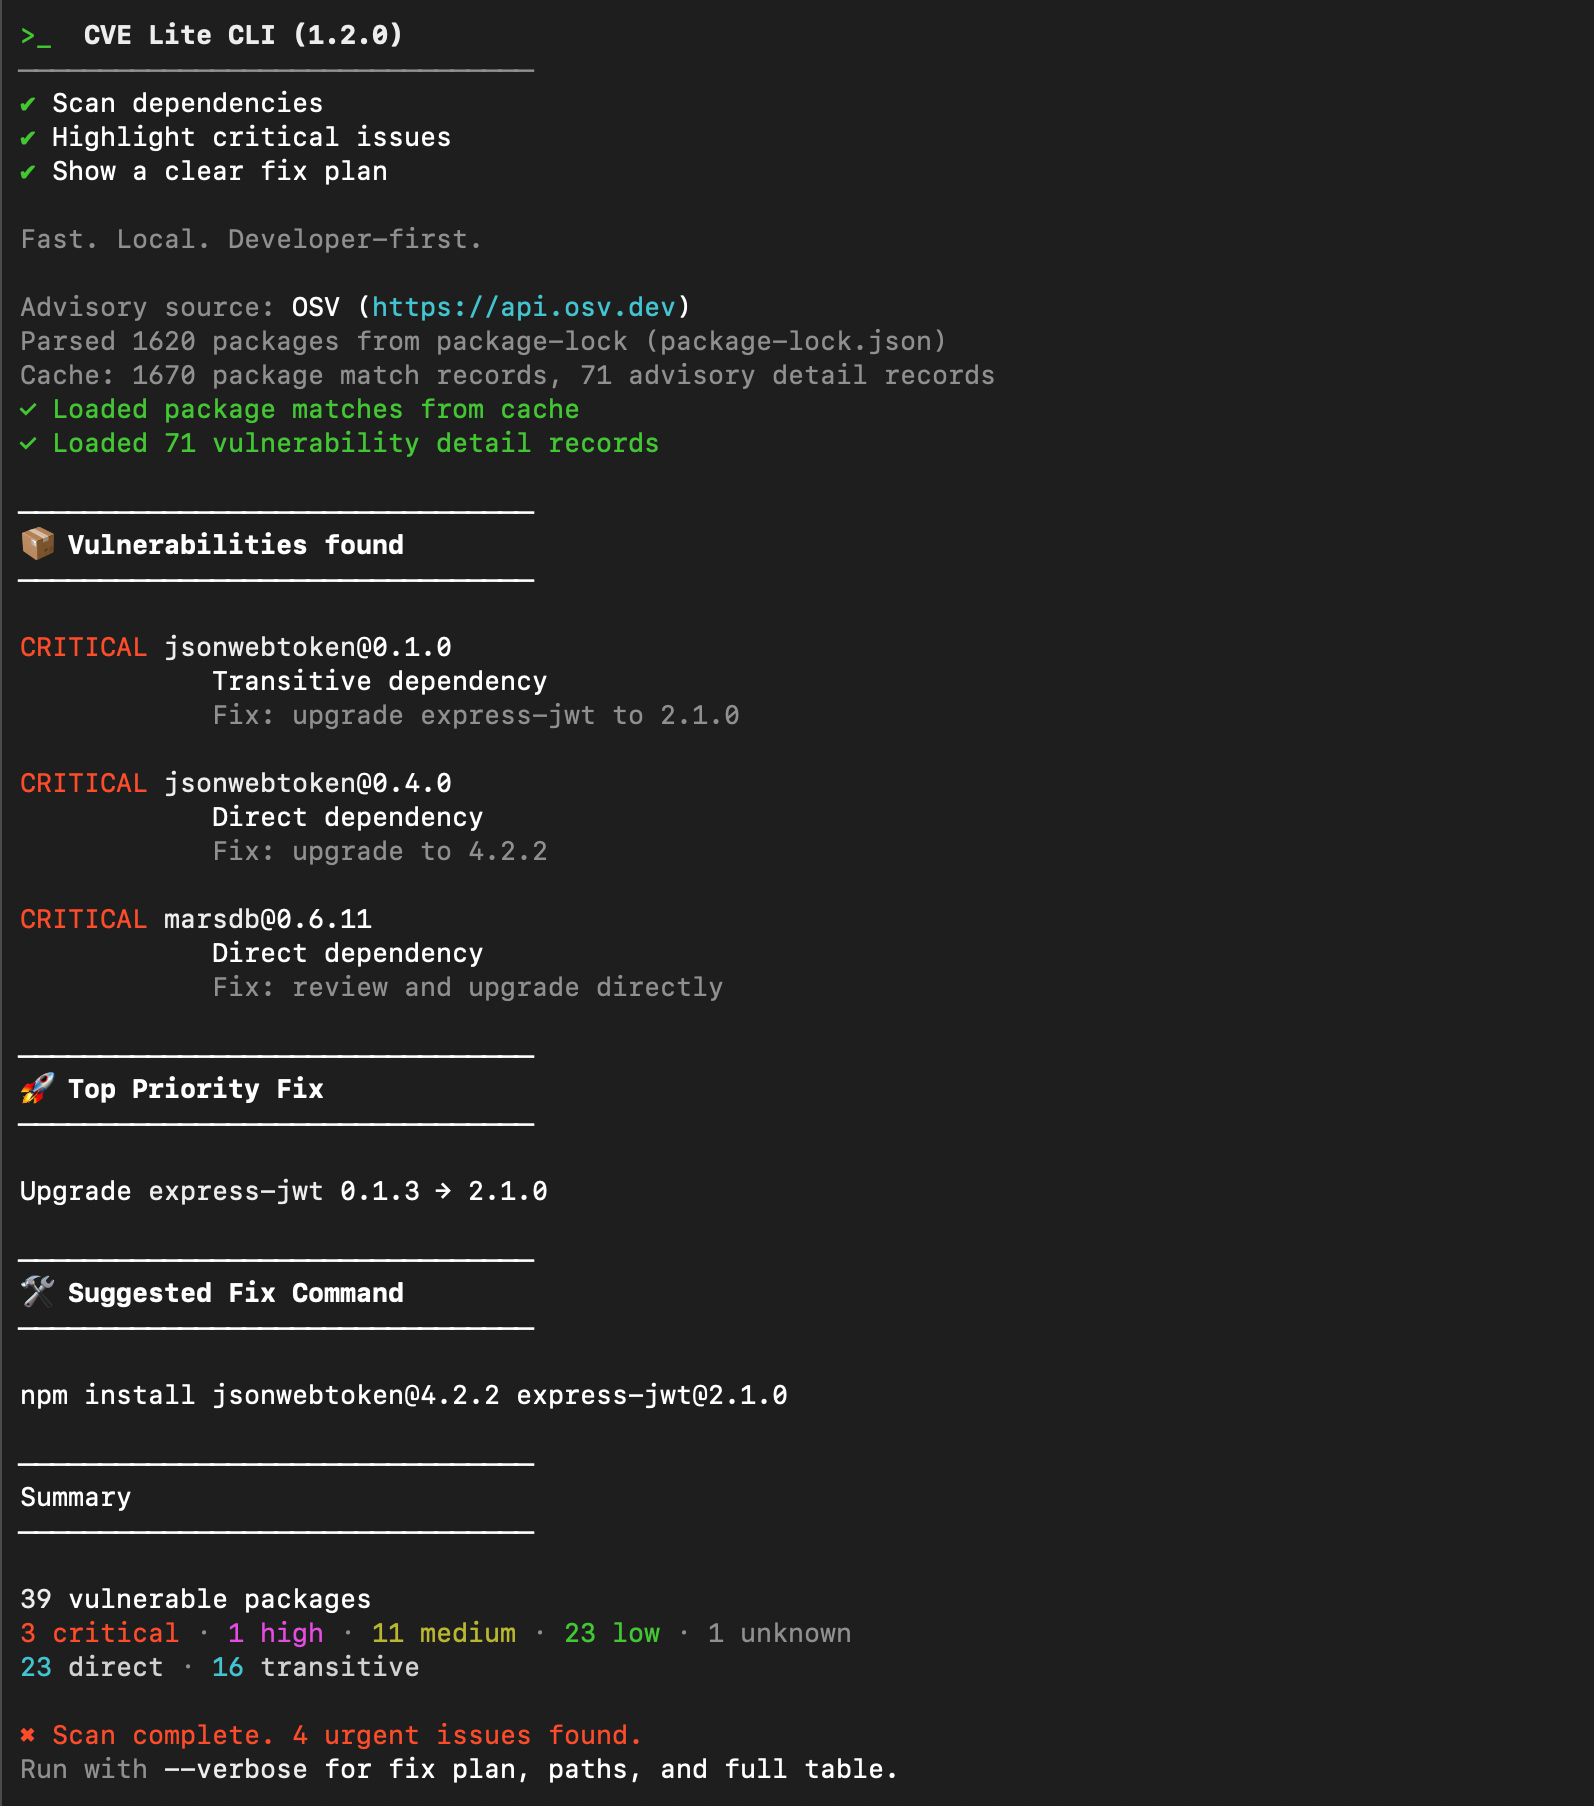 owasp/cve-lite-cli
Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
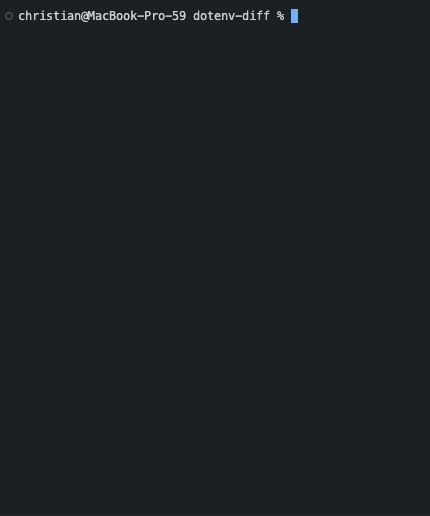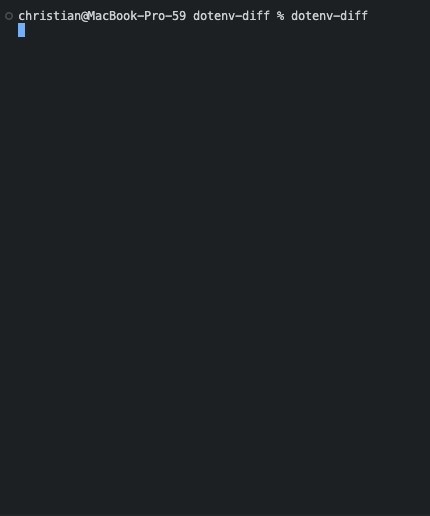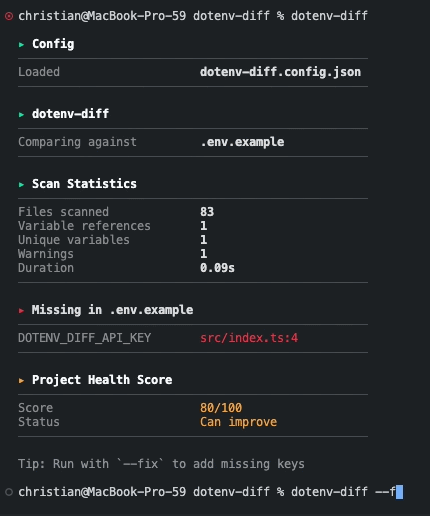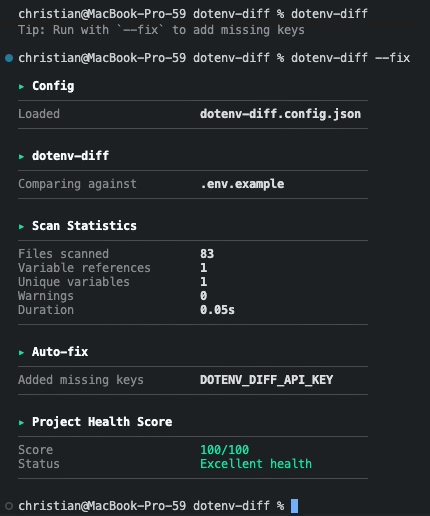 chrilleweb/dotenv-diff
Validate environment variable usage in codebase
 ag3ntsc4rn/autorun-audit
Find code that runs without you asking: repo files that execute on folder open (VS Code tasks, agent hooks, MCP, devcontainers) and Python…