

APIHarvester
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
api-securityapi-security-testingcrawler+9
32
piratesshield/apiharvesterThe one shot API attacker tool - finds the API url from the given root simulate the automated attacks
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 fauxrougee/smartscanner-source
Web vulnerability scanner built with C++17 and Qt 6, featuring a GUI, CLI, configurable crawling, and JSON reports. Reconstructed for educational…
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 yeee3642/edu-recon
Authorized education-sector recon & triage orchestrator (nmap/dirsearch/sqlmap/hydra + CVE-2024-4577, secret/API-key leak, XSS, wp2shell) with a web…
 awarexone/agentic-bug-hunter
AI-powered bug bounty hunting toolkit that works with or without subscription.
 tomnomnom/gf
A wrapper around grep, to help you grep for things
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 cybertix-pvt-ltd/one-liner-collections
This Repositories contains list of One Liners with Descriptions and Installation requirements
 daffainfo/oneliner-bugbounty
A collection oneliner scripts for bug bounty
 gquere/pwn_jenkins
Notes about attacking Jenkins servers
 asamassekou10/ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
 hackspeak/cve-2026-66066
CVE-2026-66066 (KindaRails2Shell) PoC - Rails Active Storage/libvips arbitrary file read to RCE; for authorized security testing
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 gal-nagli/shockwave-oss
Curated collection of bug bounty tips, one-liners, and automation workflows for recon, fuzzing, and web exploitation, with private nuclei templates…
 cappricio-securities/appspec-yaml-leaks
Appspec YML and YAML leaks
 cappricio-securities/behat-config-leaks
BeHat Configuration file leaking
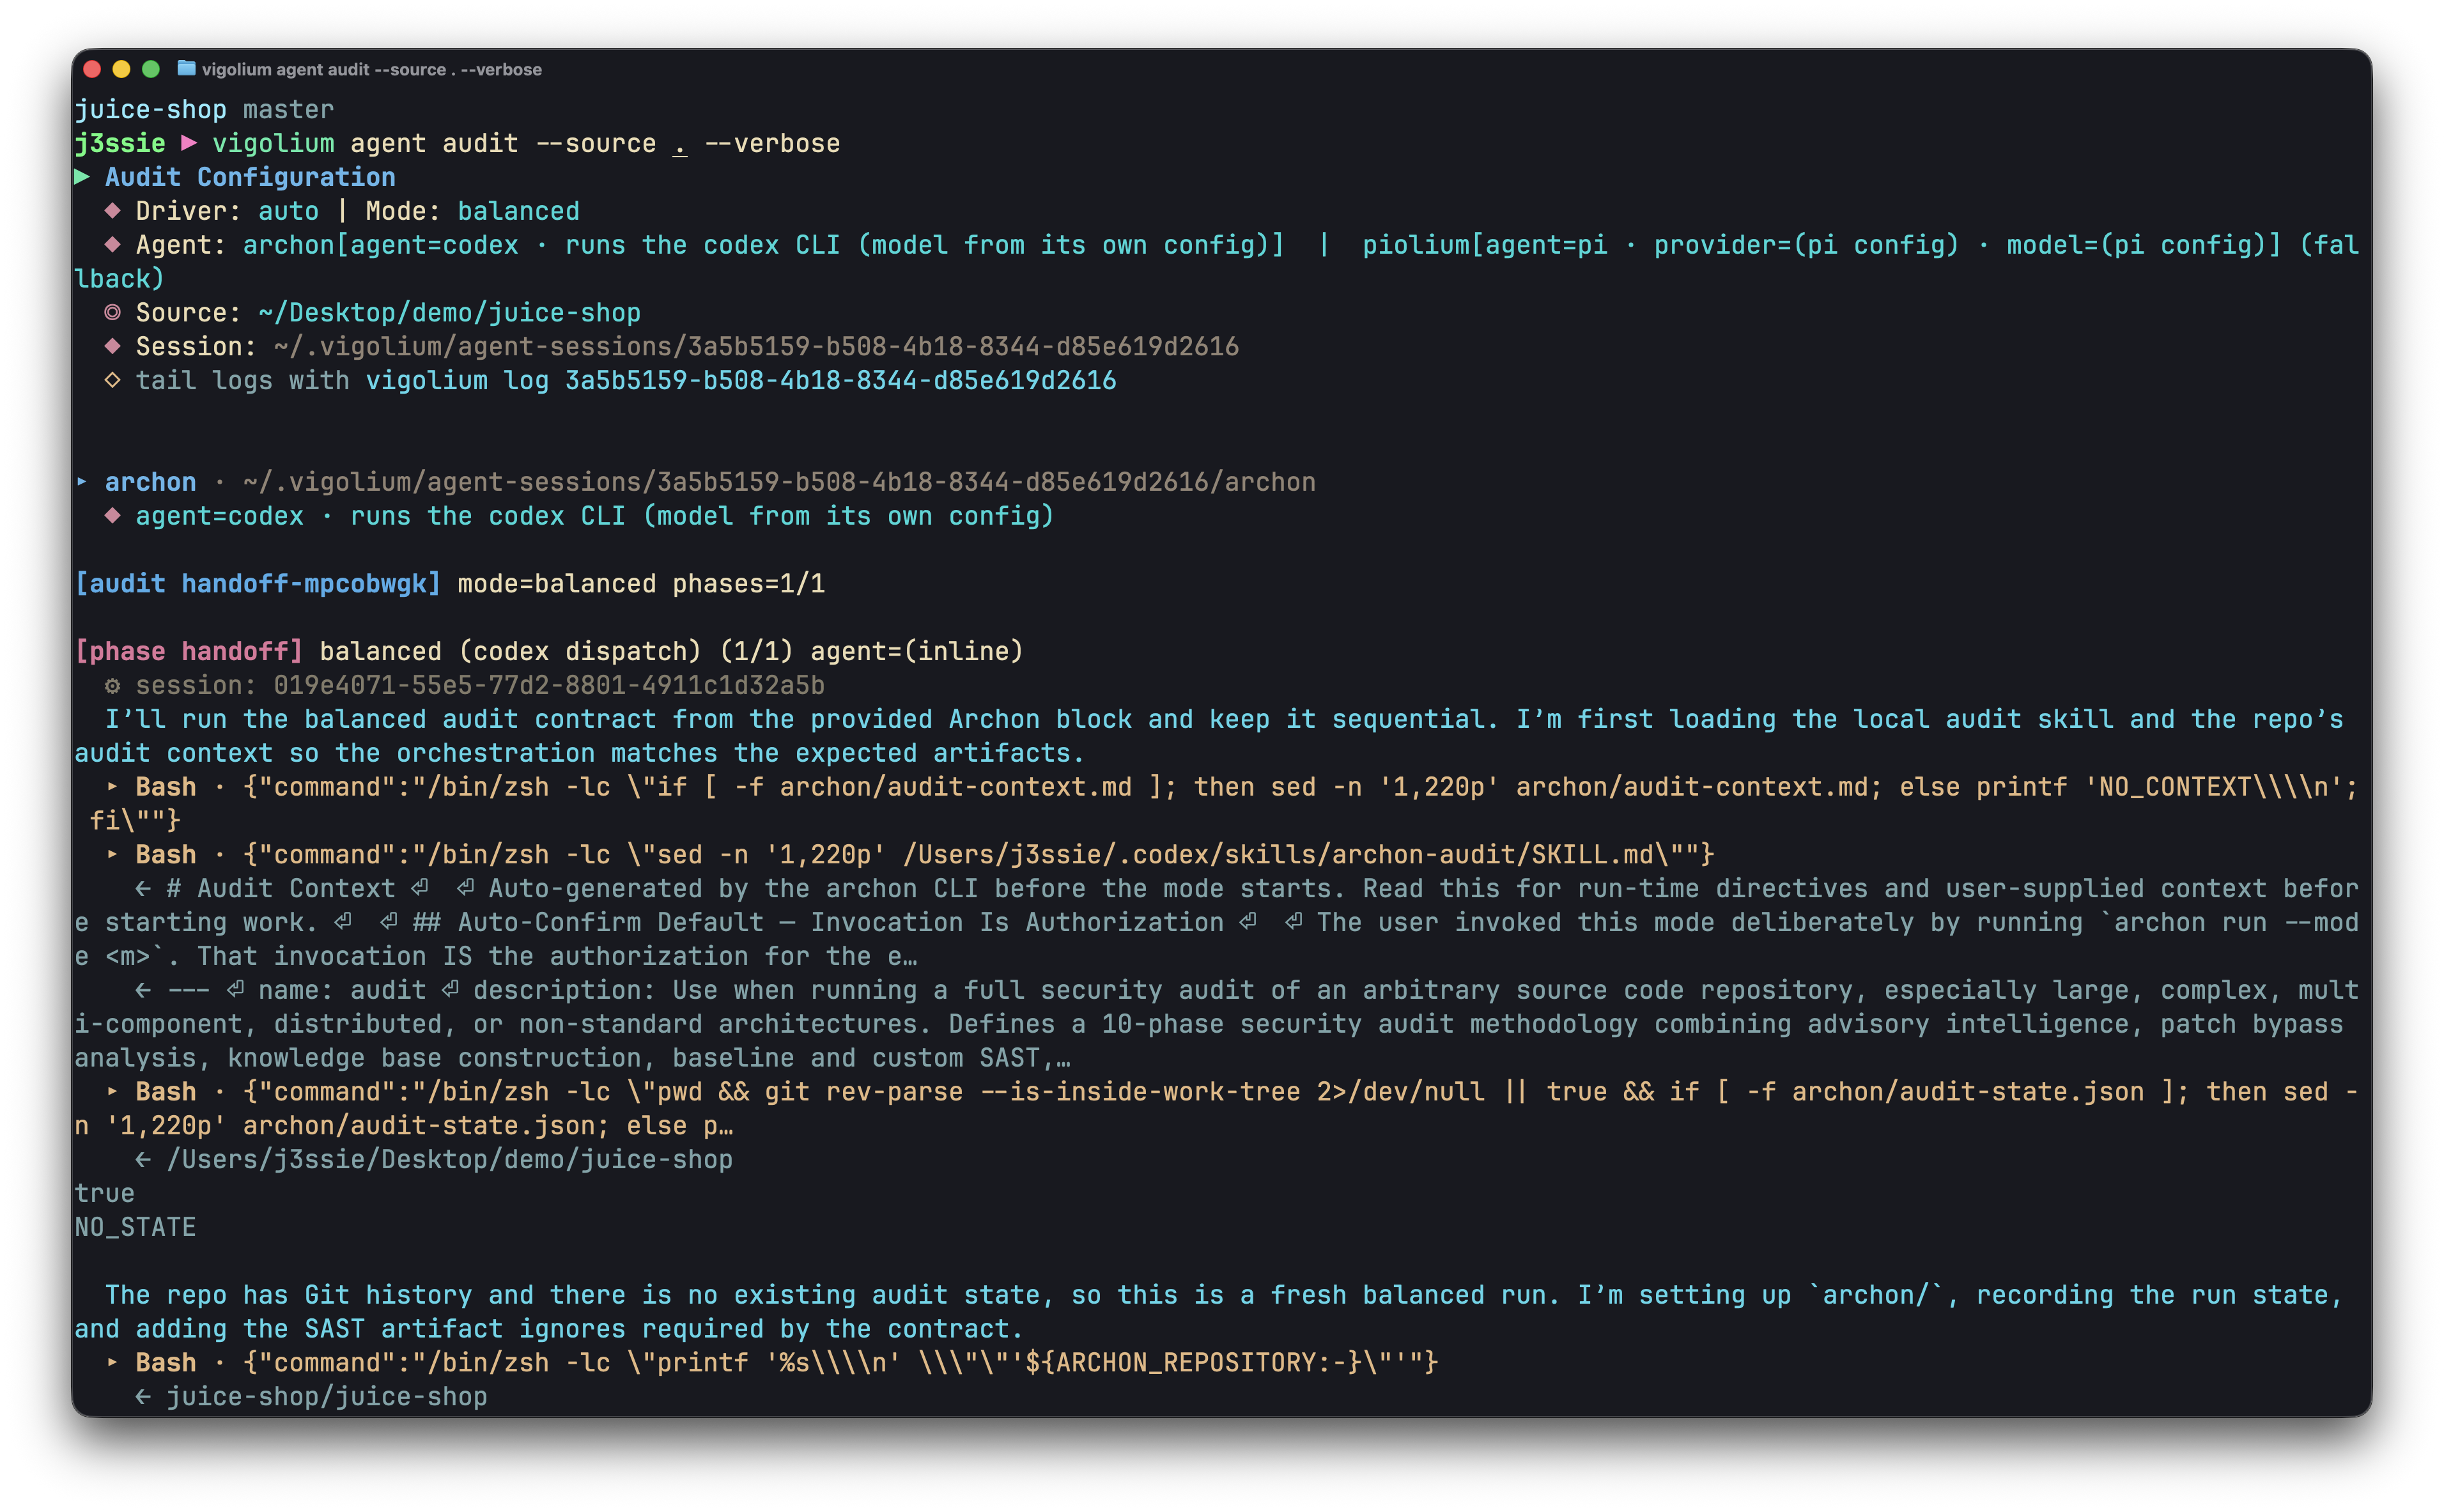 vigolium/vigolium
Vigolium - High-fidelity vulnerability scanner fusing agentic AI with native speed, modularity, and precision