

PIIHunter
 owasp/piihunter
Scans PostgreSQL databases and Jira issues for PII using regex, NER/ML, and optional self-hosted LLM detection, with redacted reports and audit…
ai-securitydatabase-securitydata-exfiltration+6
owasp/piihunterScans PostgreSQL databases and Jira issues for PII using regex, NER/ML, and optional self-hosted LLM detection, with redacted reports and audit…
 mbanyamer/llama-stack-0.4.0rc3-local-cve-2026-25211
Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…
 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
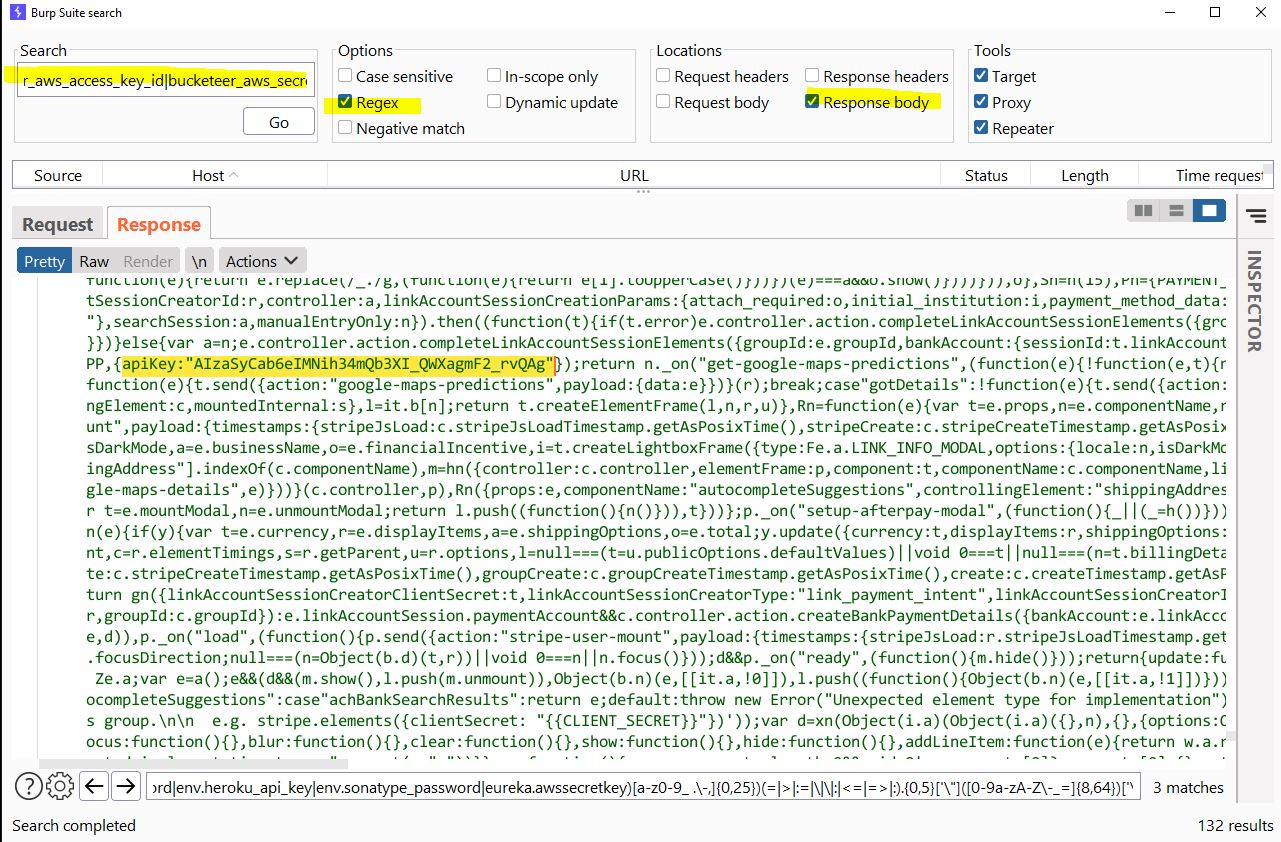 h4x0r-dz/leaked-credentials
how to look for Leaked Credentials !
 randomrobbiebf/static-file-checker
Checks Djangos /static/staticfiles.json for exposed creds using nuclei
 cappricio-securities/appspec-yaml-leaks
Appspec YML and YAML leaks
 cappricio-securities/behat-config-leaks
BeHat Configuration file leaking
 randomrobbiebf/chart-down
Extracts all the chart lists from ChartMuseum
 atlassian/git-secrets-scan
Scans Git repositories for hardcoded secrets, keys, and passwords using Gitleaks, integrating security into Bitbucket Pipelines with Code Insights…
 reverseclabs/azuredevops-enum
Read-only Azure DevOps enumeration tool that queries the REST API to surface projects, repositories, service connections, builds, pipeline secrets,…
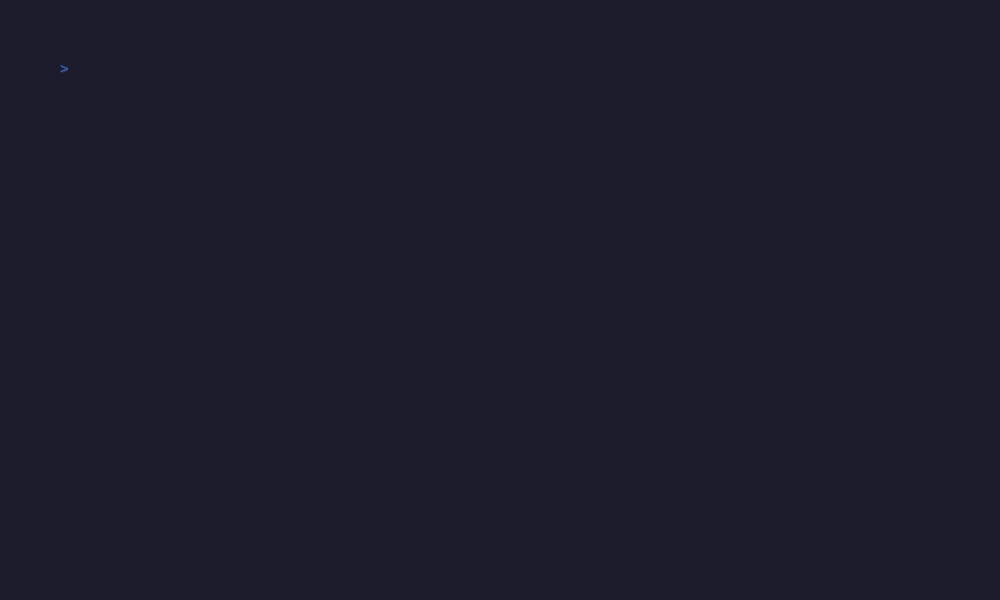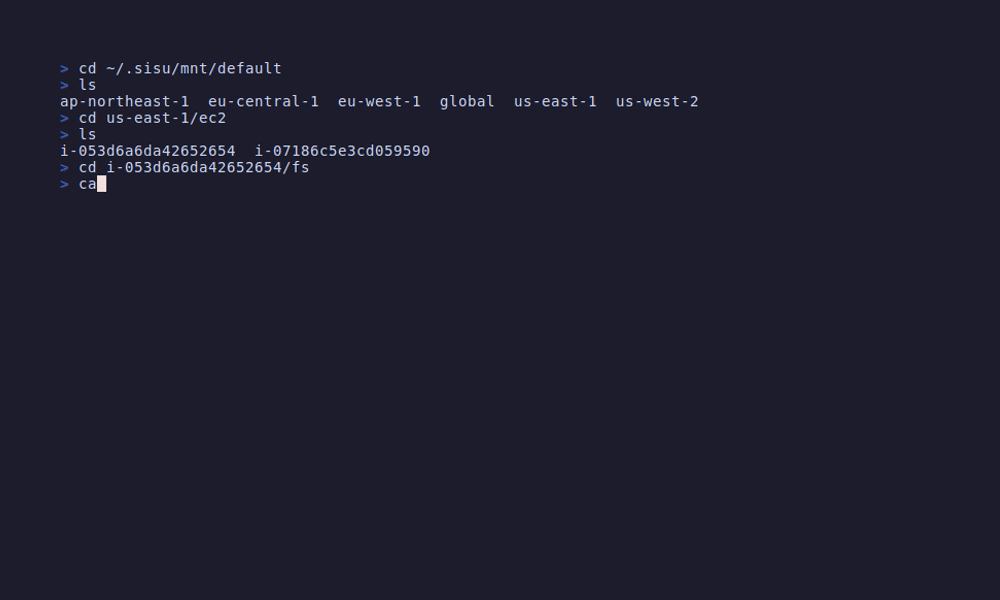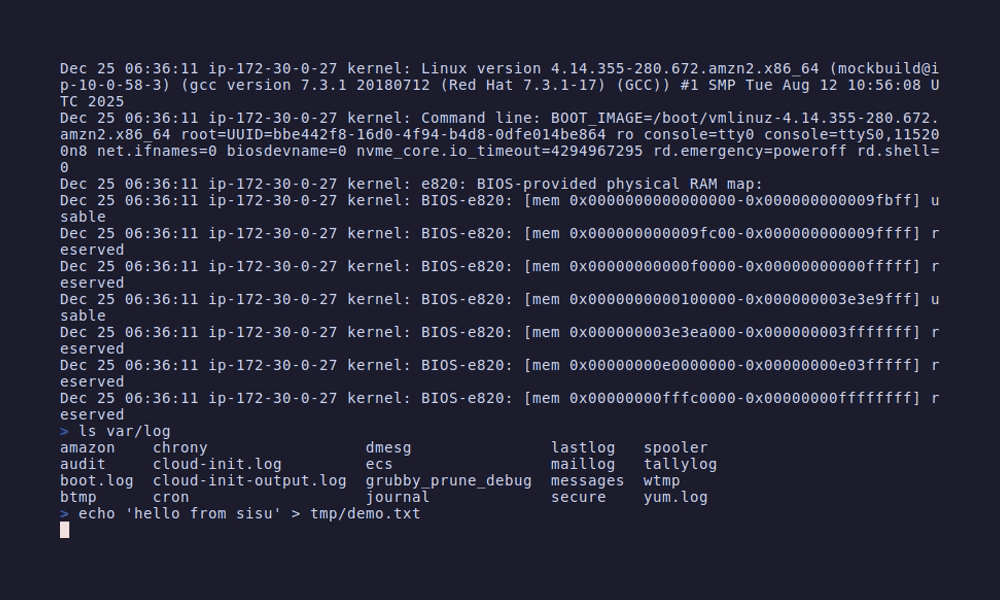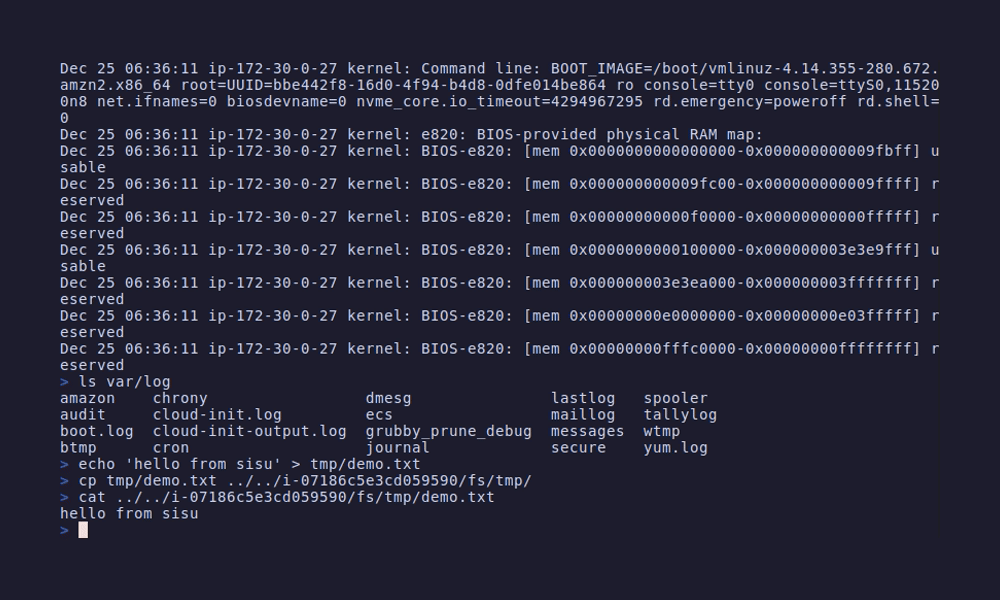 semonte/sisu
Mounts AWS resources as a local filesystem for infrastructure exploration, security auditing, and configuration analysis using standard Unix tools…
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
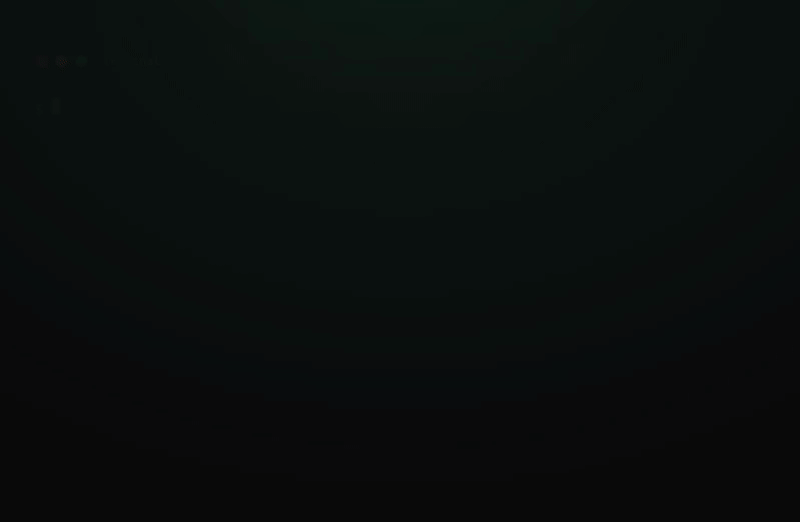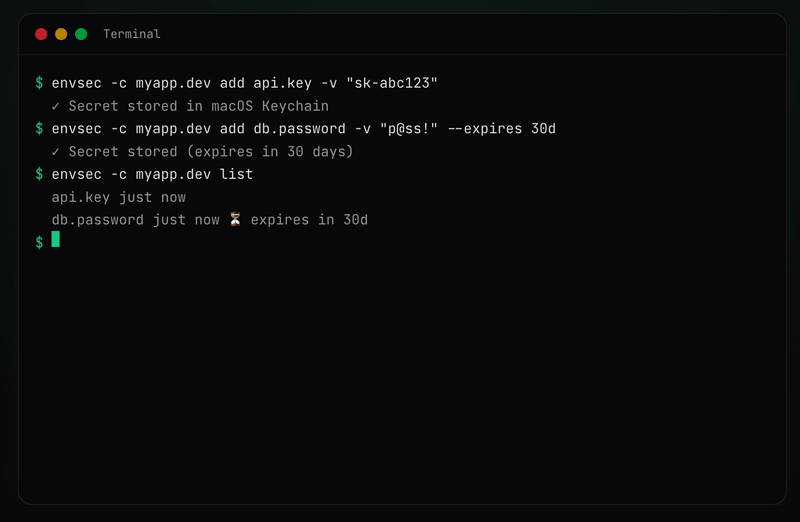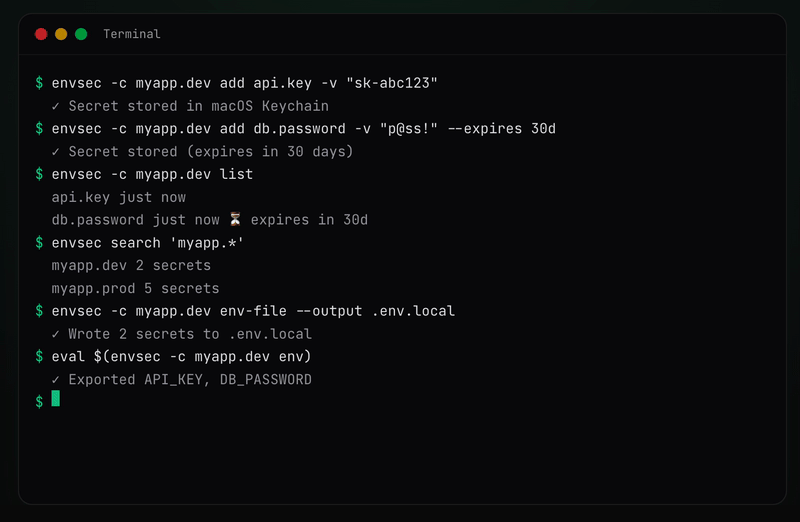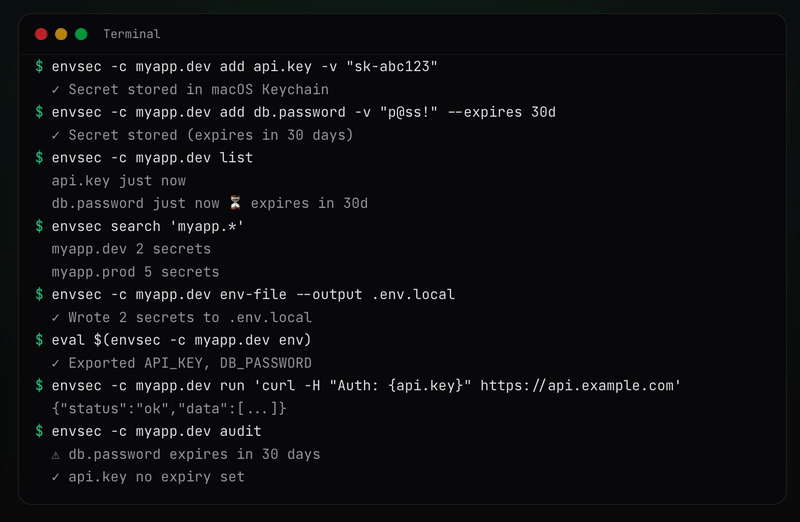 davidnussio/envsec
Secure CLI tool for managing environment secrets using native OS credential stores (macOS Keychain, Linux Secret Service, Windows Credential Manager)
 cgv-dev/metasploit-module-tfm
Module written in Ruby with the objective of exploiting vulnerabilities CVE-2023-2728 and CVE-2024-3177, both related to the secret mount policy in a…
 checkmarx/checkmarx-cve-2025-30066-detection-tool
Scans GitHub workflows and logs for indicators of CVE-2025-30066, detecting malicious actions and exposed secrets using Checkmarx 2ms integration.
 raoufmaklouf/jsecret
Fast Go-based static scanner for detecting sensitive data (API keys, tokens, passwords) in JavaScript files and source code using regex patterns.
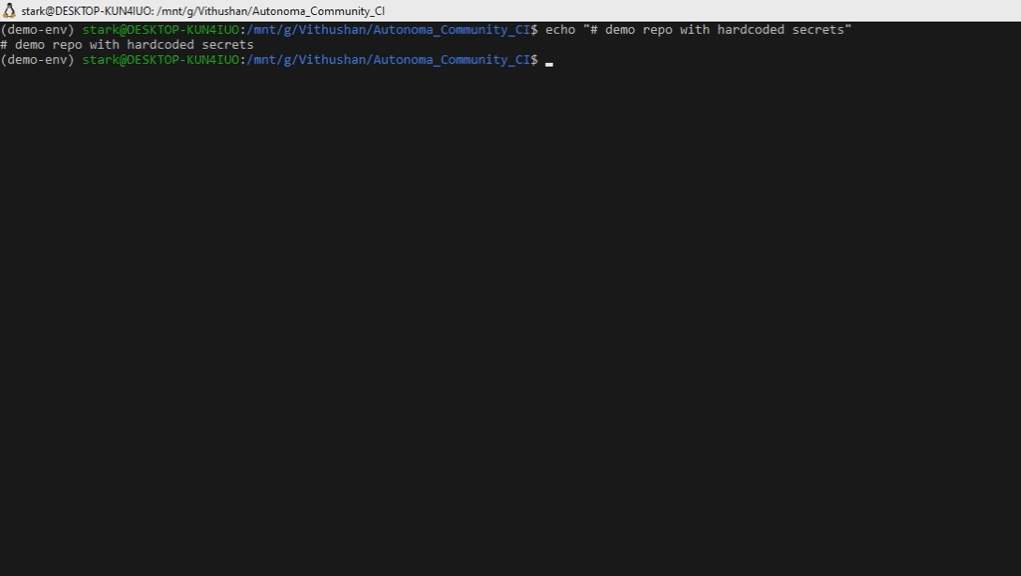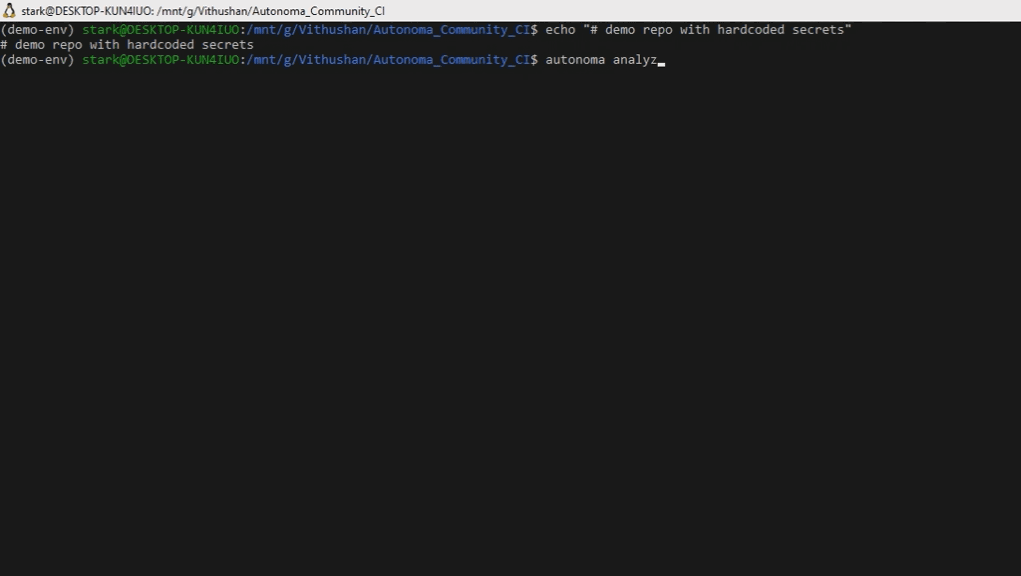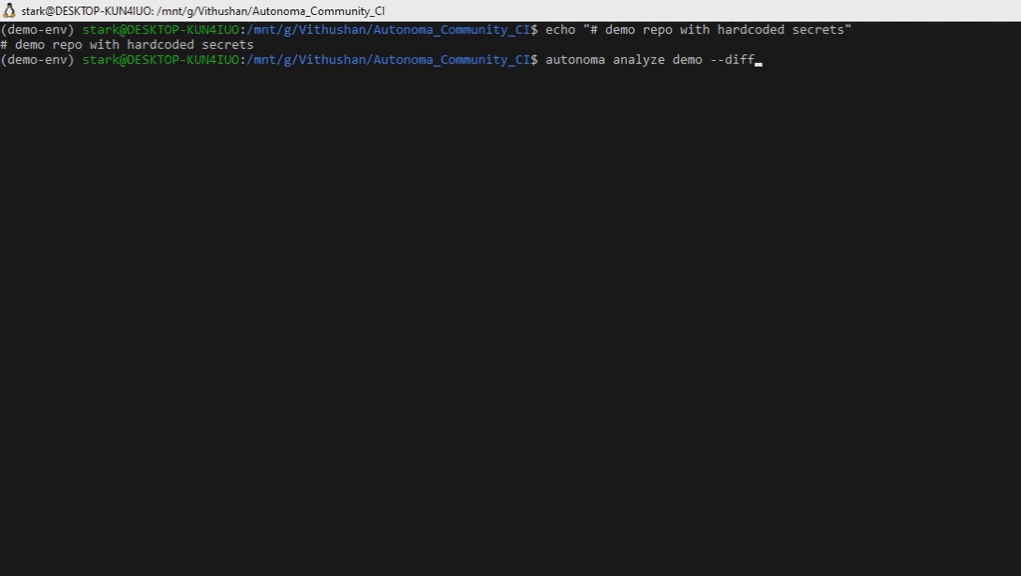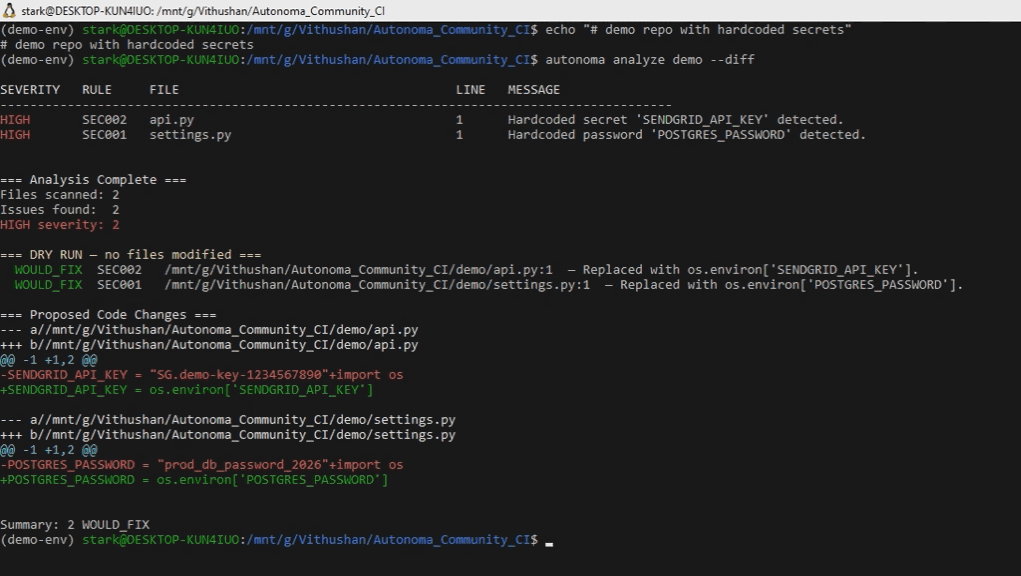 vihaaninnovations/autonoma
Detects and auto-fixes hardcoded secrets in Python repos — refuses when the fix could break your code
 corgea/sighthound
Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…