

ZSC
 owasp/zsc
OWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/
encryption-decryption-toolsexploit-frameworkspayload-generation+5
owasp/zscOWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
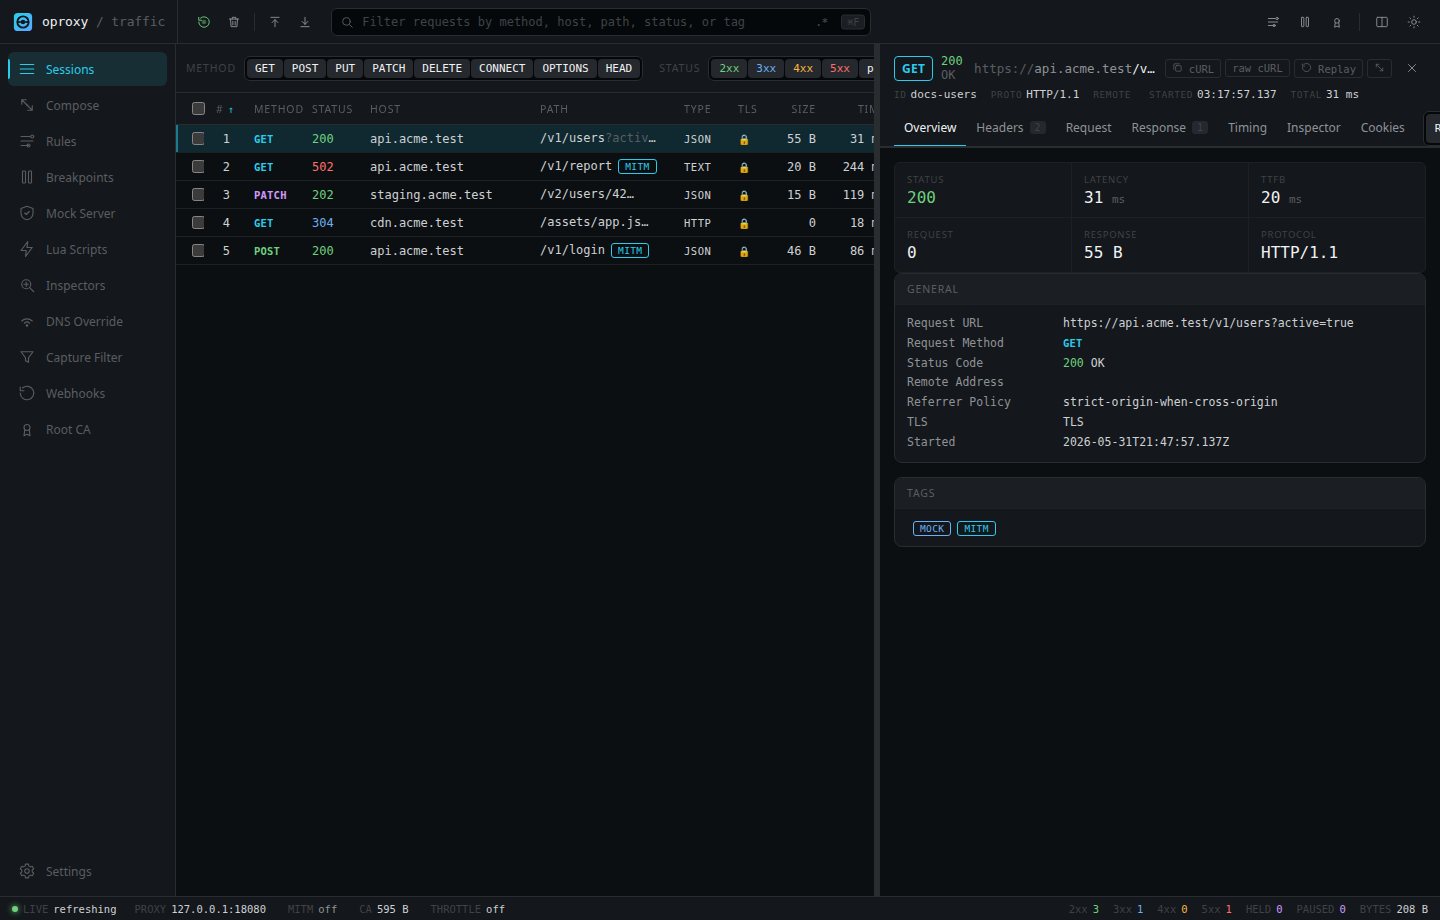 sauravrao637/oproxy
Open-source MITM proxy to intercept, inspect, and mock network traffic.
 pentestgeek/burpcommander
Ruby command-line interface to Burp Suite's REST API
 vmware-archive/burp-rest-api
REST/JSON API to the Burp Suite security tool.
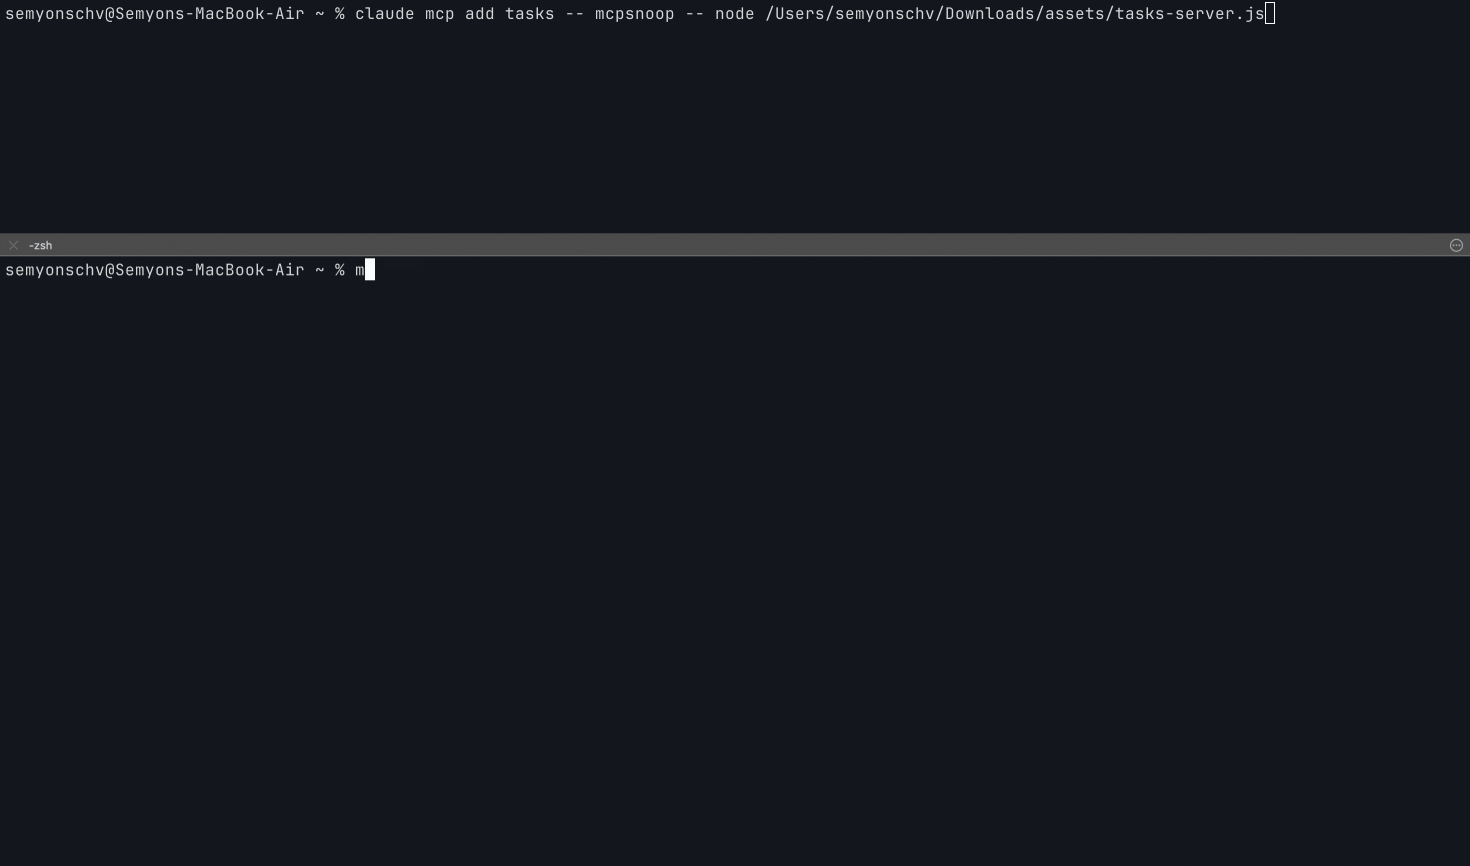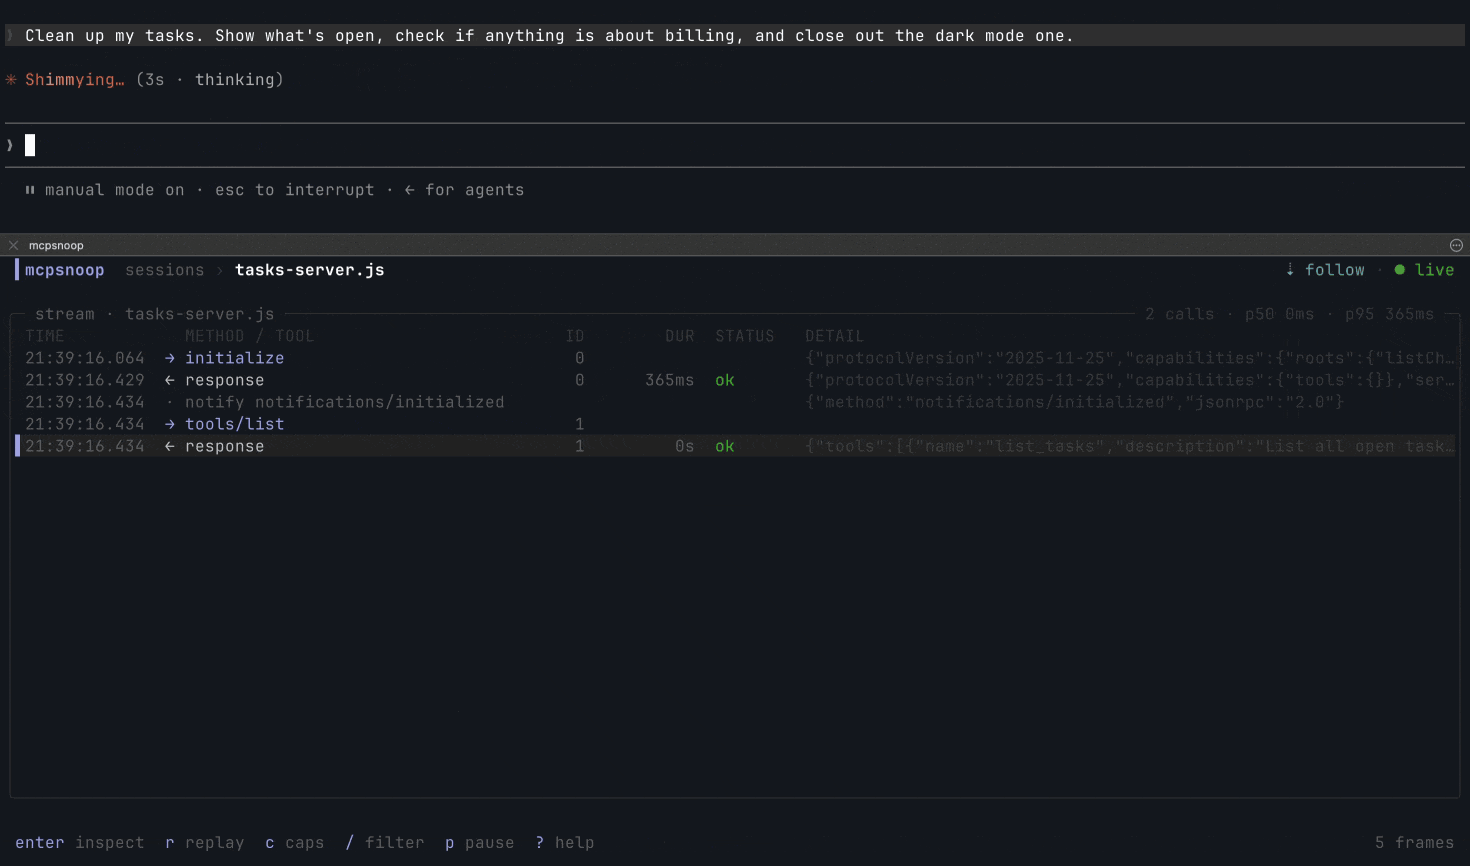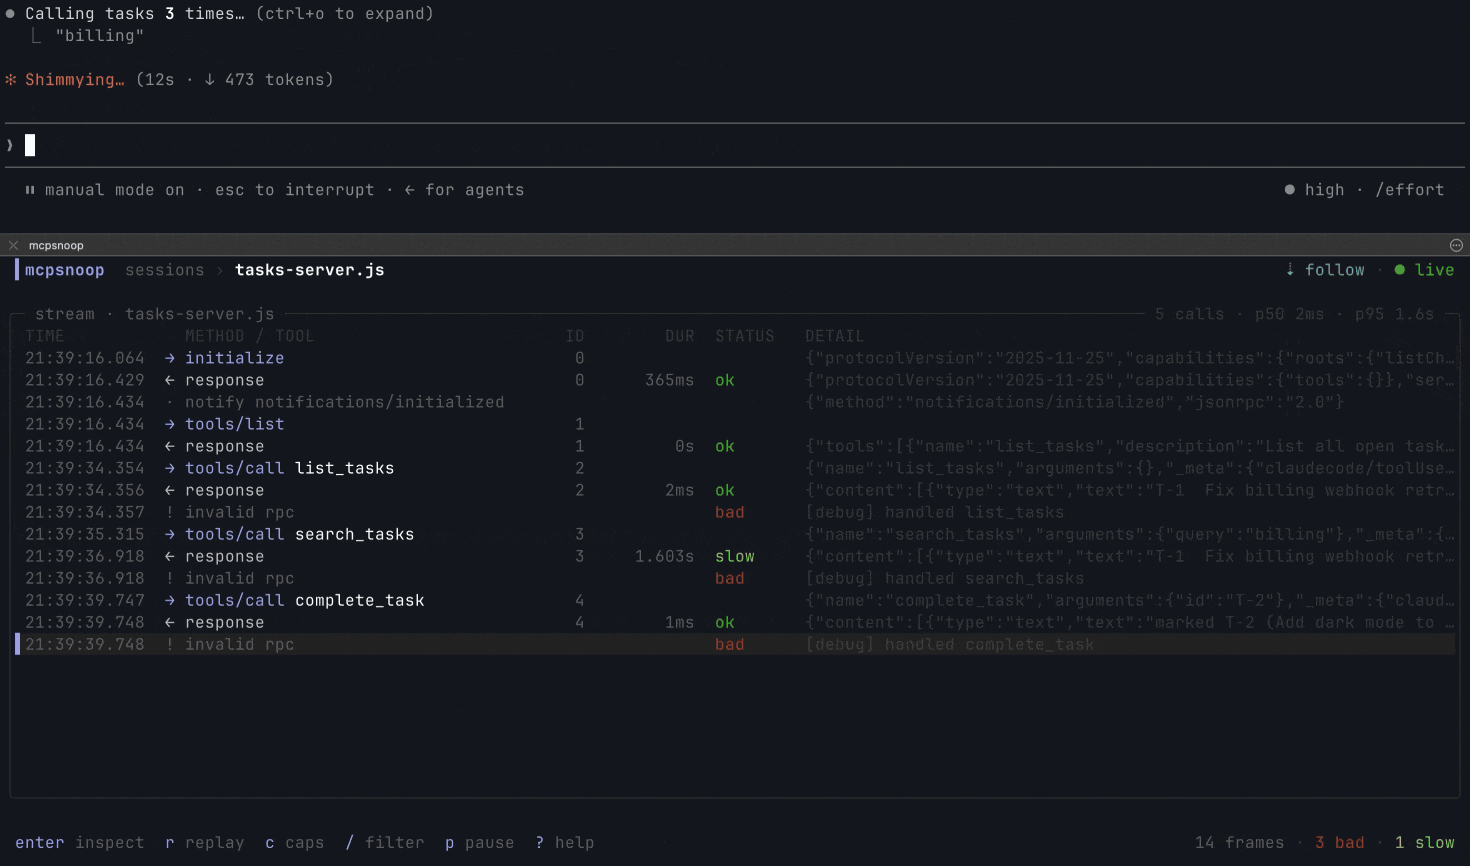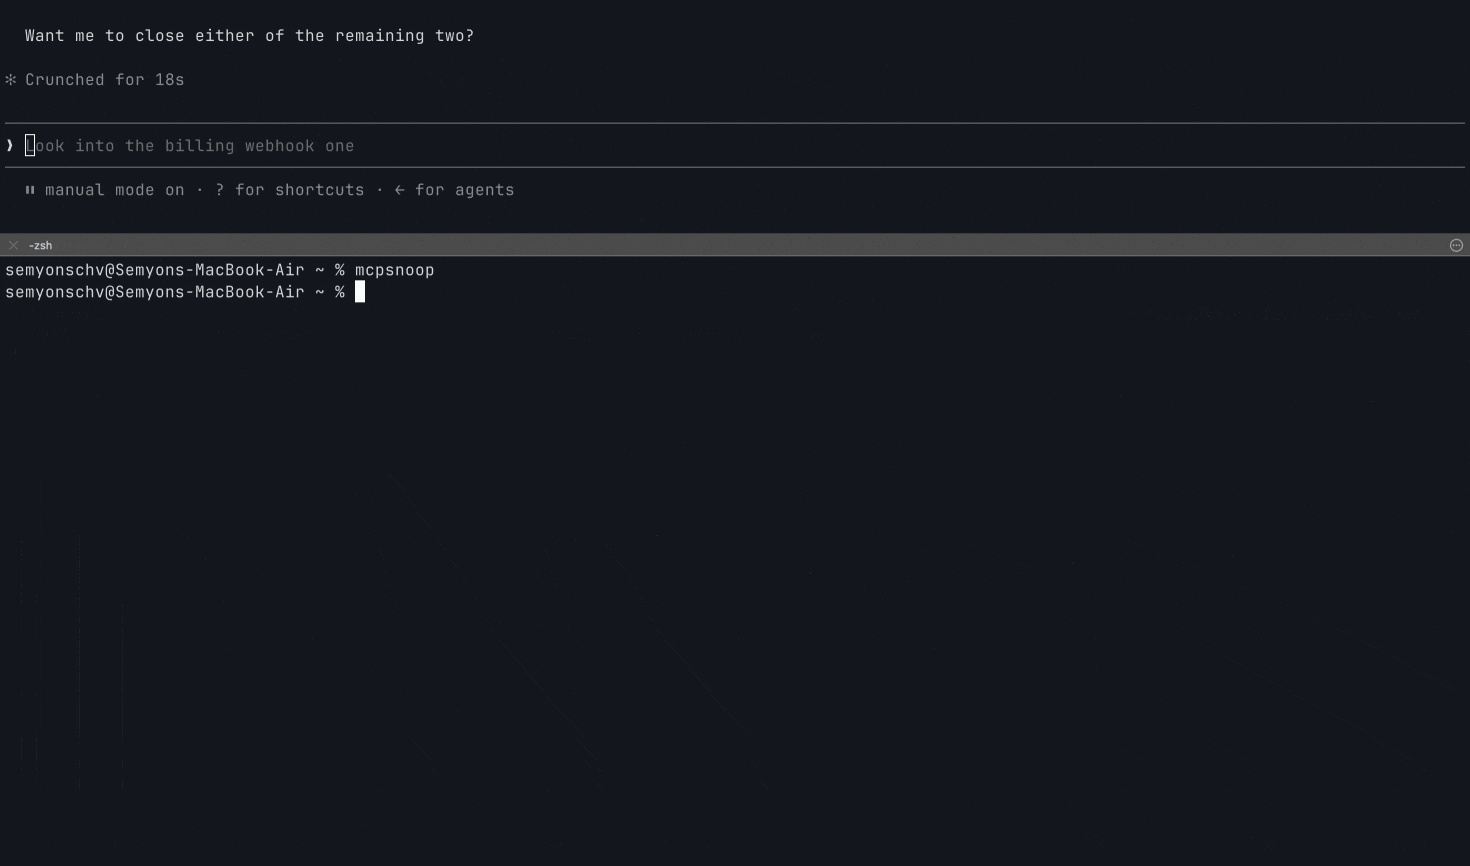 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…
 use-tusk/tusk-cli
Automated testing suite with live traffic record and replay
 portswigger/burp-extensions-montoya-api-examples
Sample Burp Suite extensions demonstrating the Montoya API, covering HTTP and proxy handlers, custom scan checks, Intruder payloads, WebSocket…
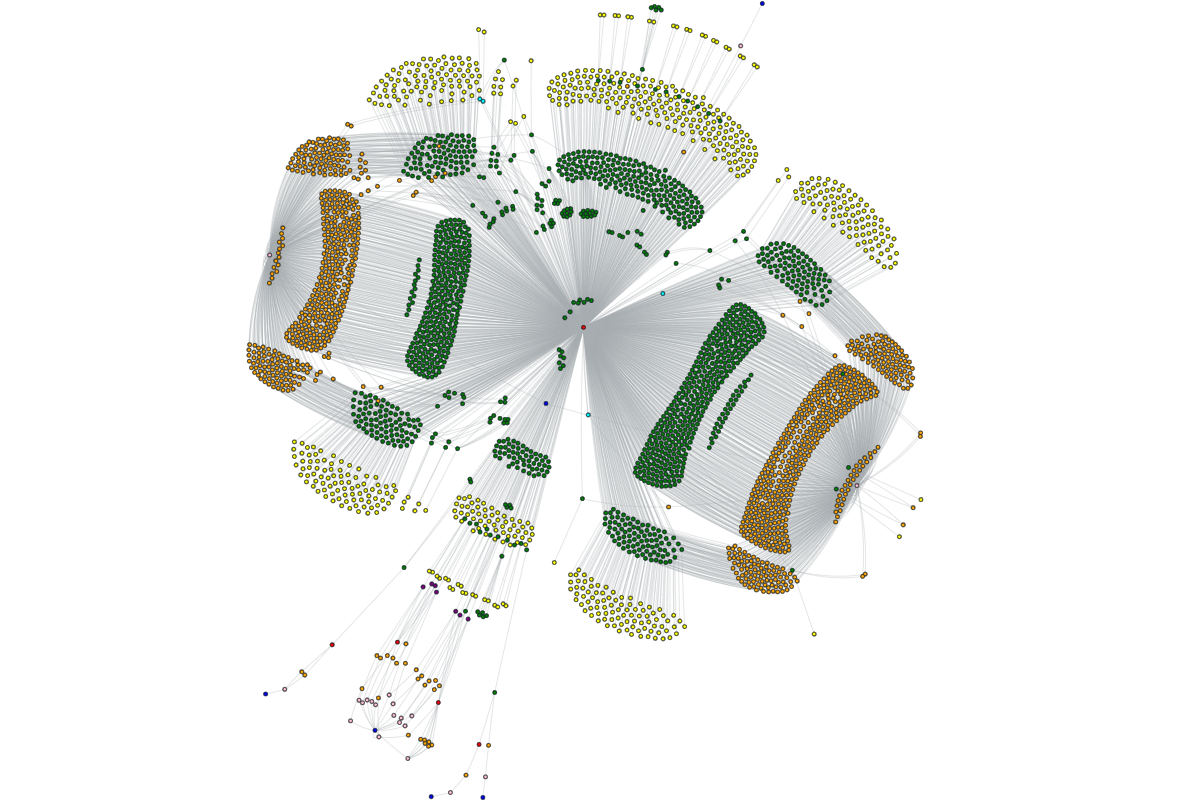 owasp-amass/amass
In-depth attack surface mapping and asset discovery
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
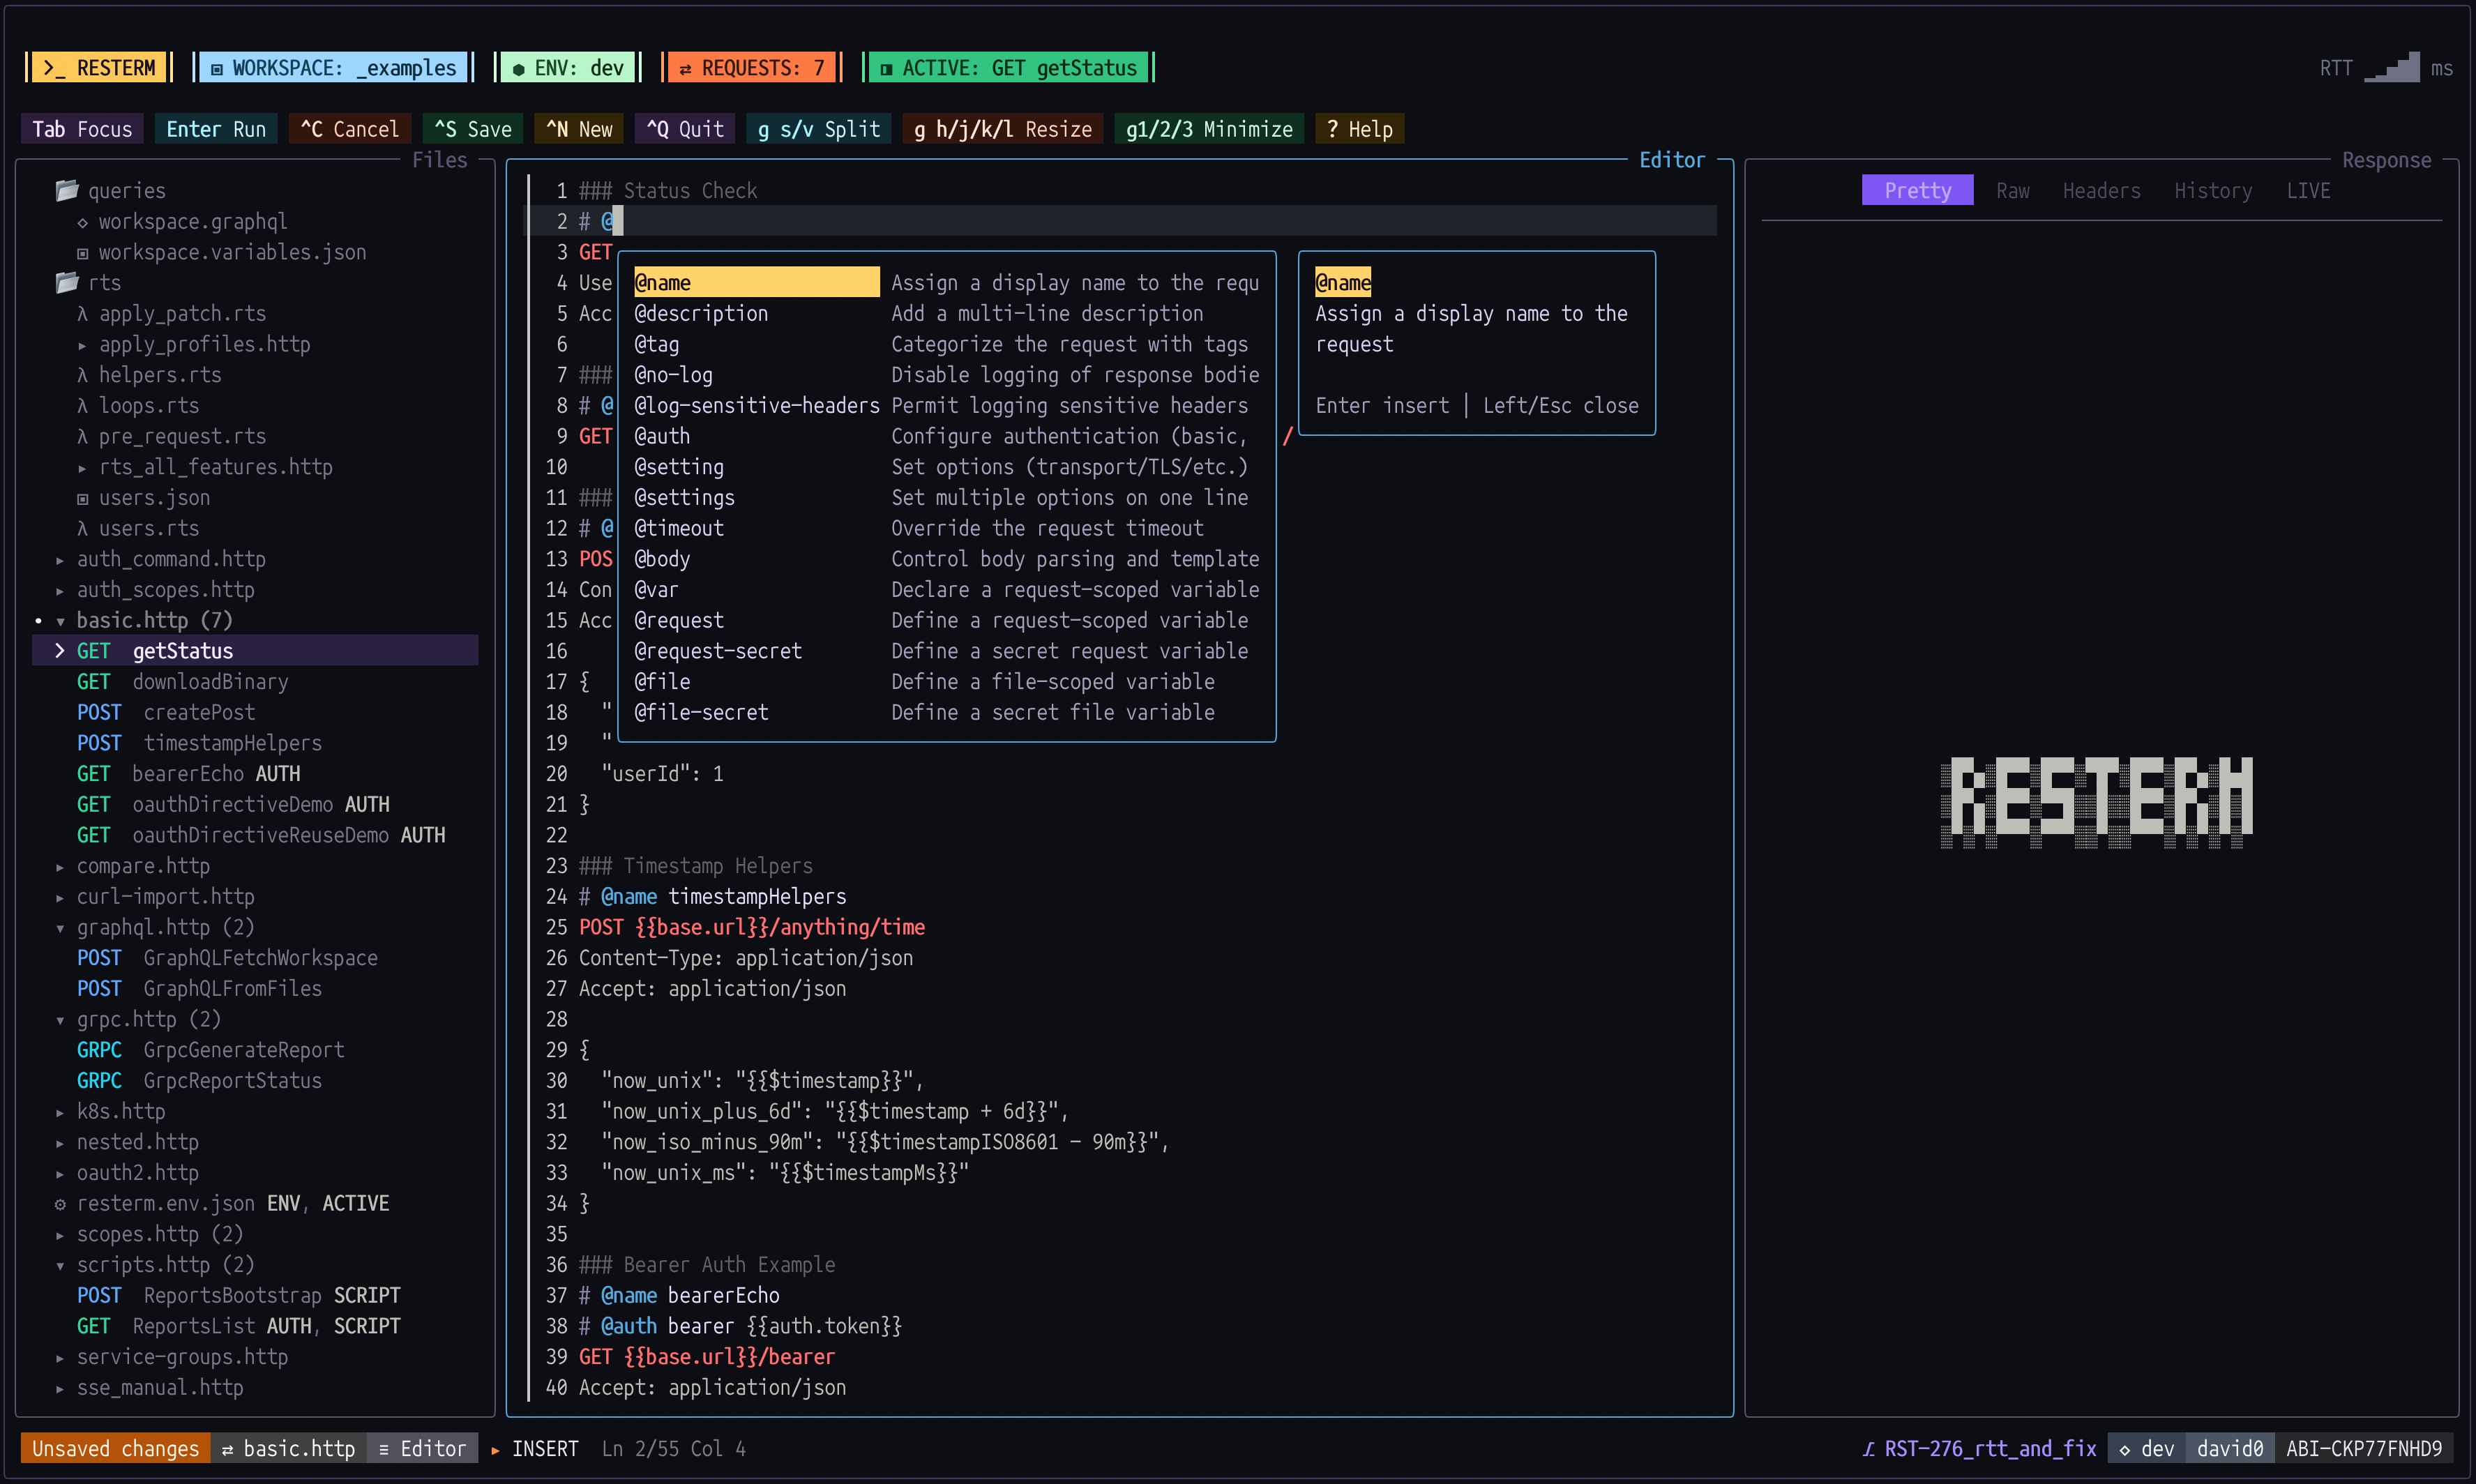 unkn0wn-root/resterm
Terminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…
 saffron-health/libretto
The AI toolkit for building reliable browser automations
 devcop95/bugbounty-lab101
A complete bug bounty workspace for HackerOne researchers. Includes scope enforcement, automated recon/vuln pipeline (400+ tools), report templates,…
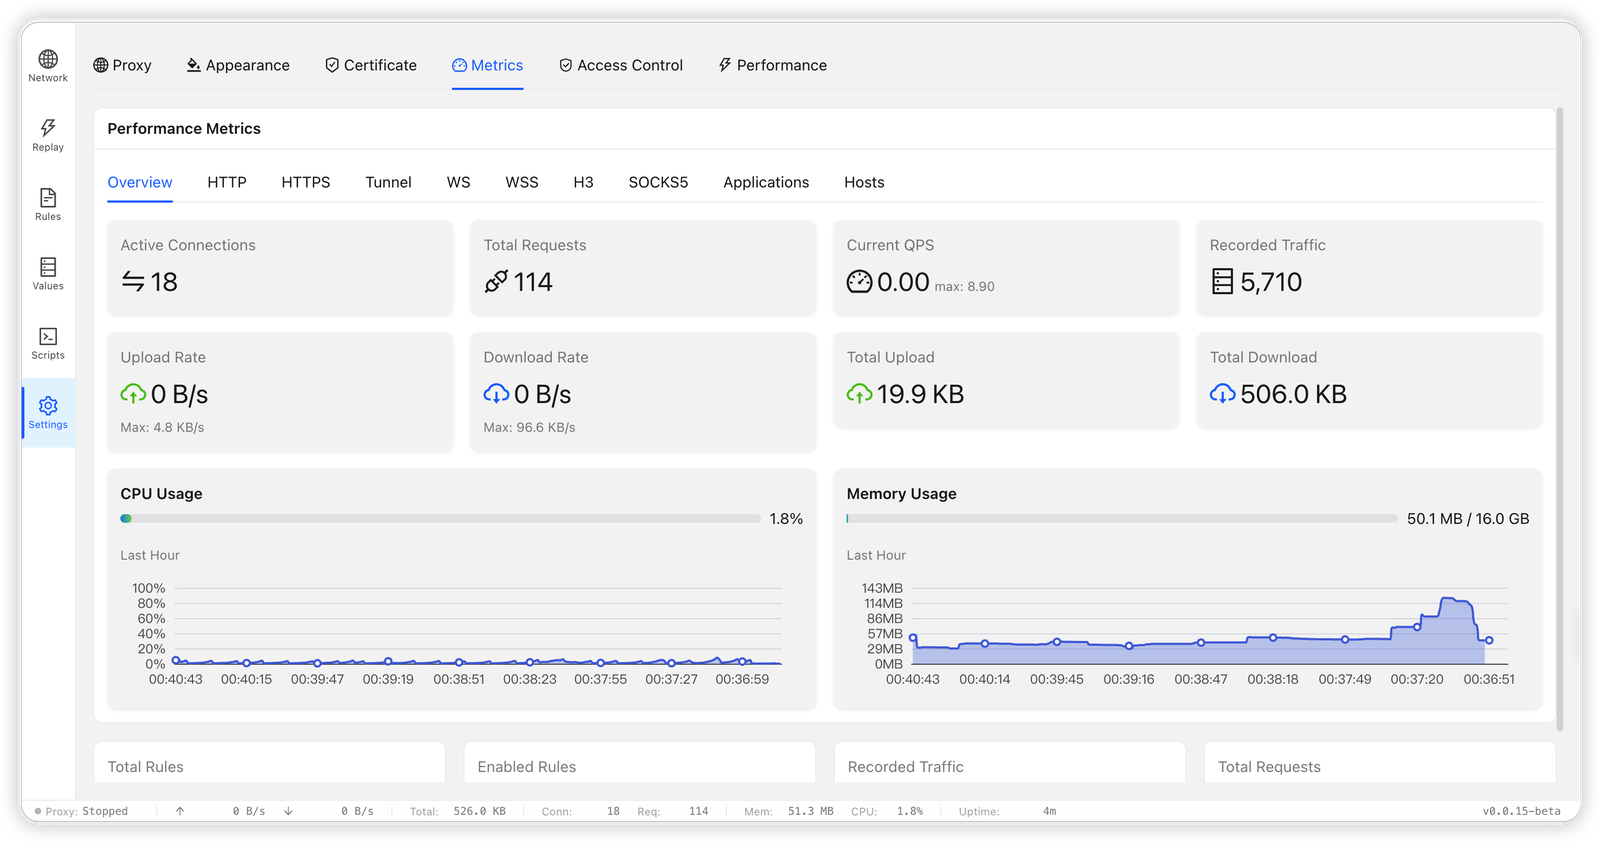 bifrost-proxy/bifrost
High-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
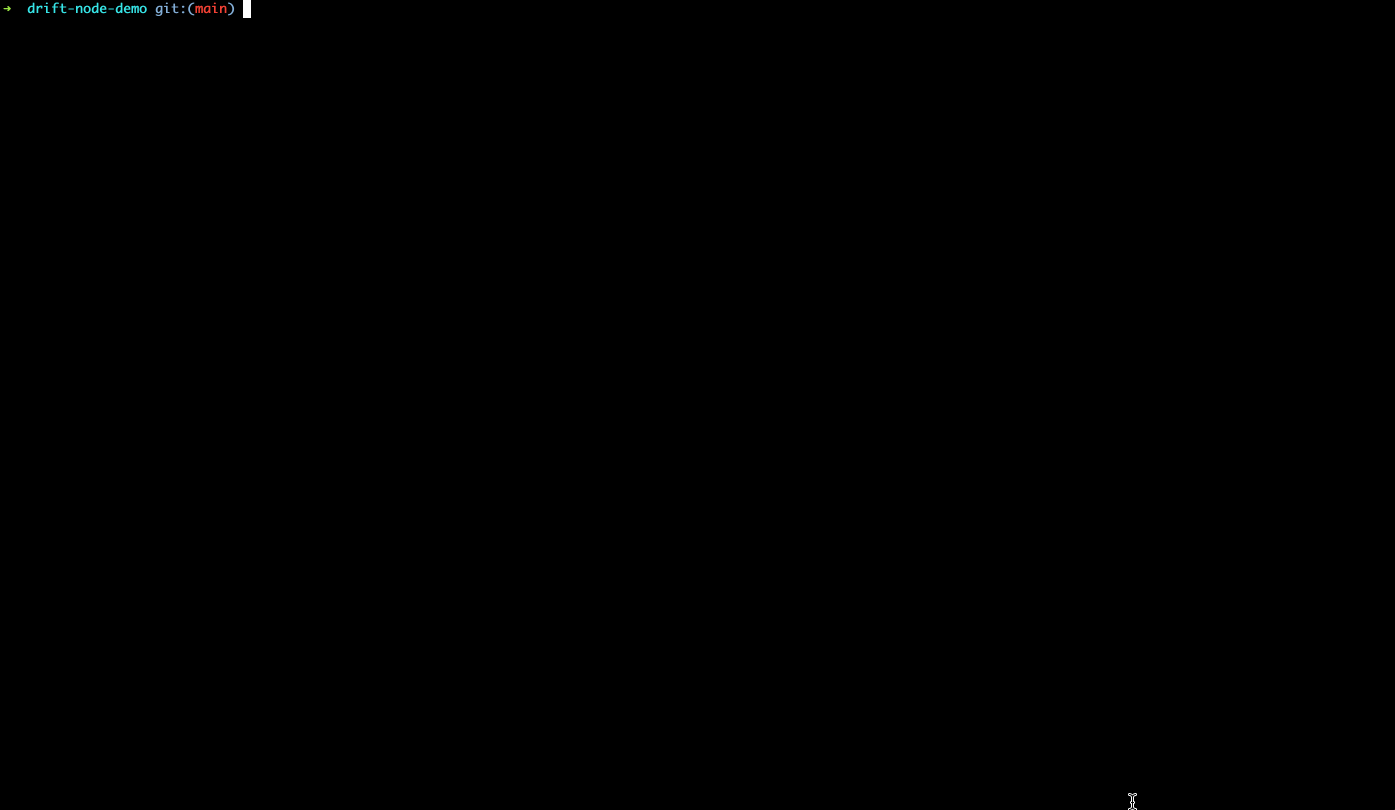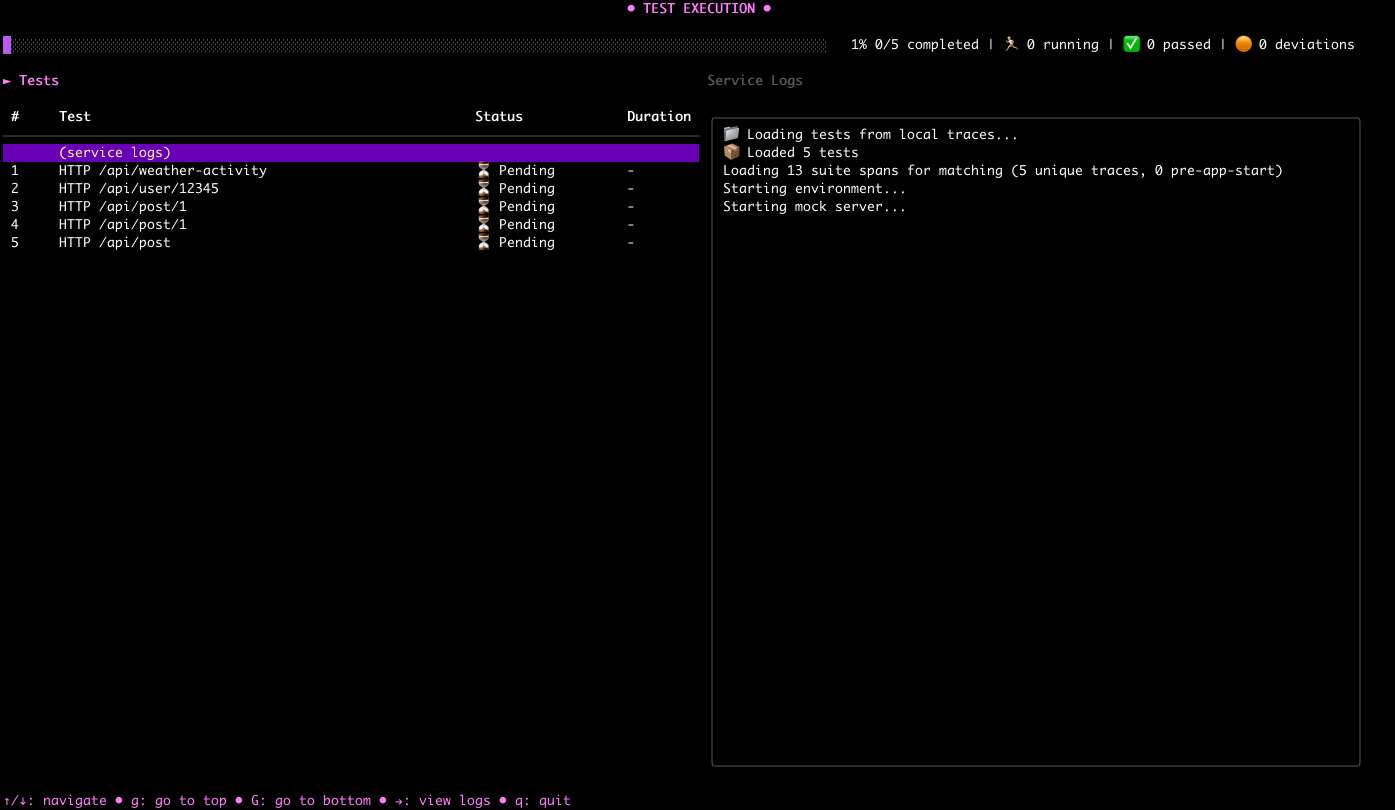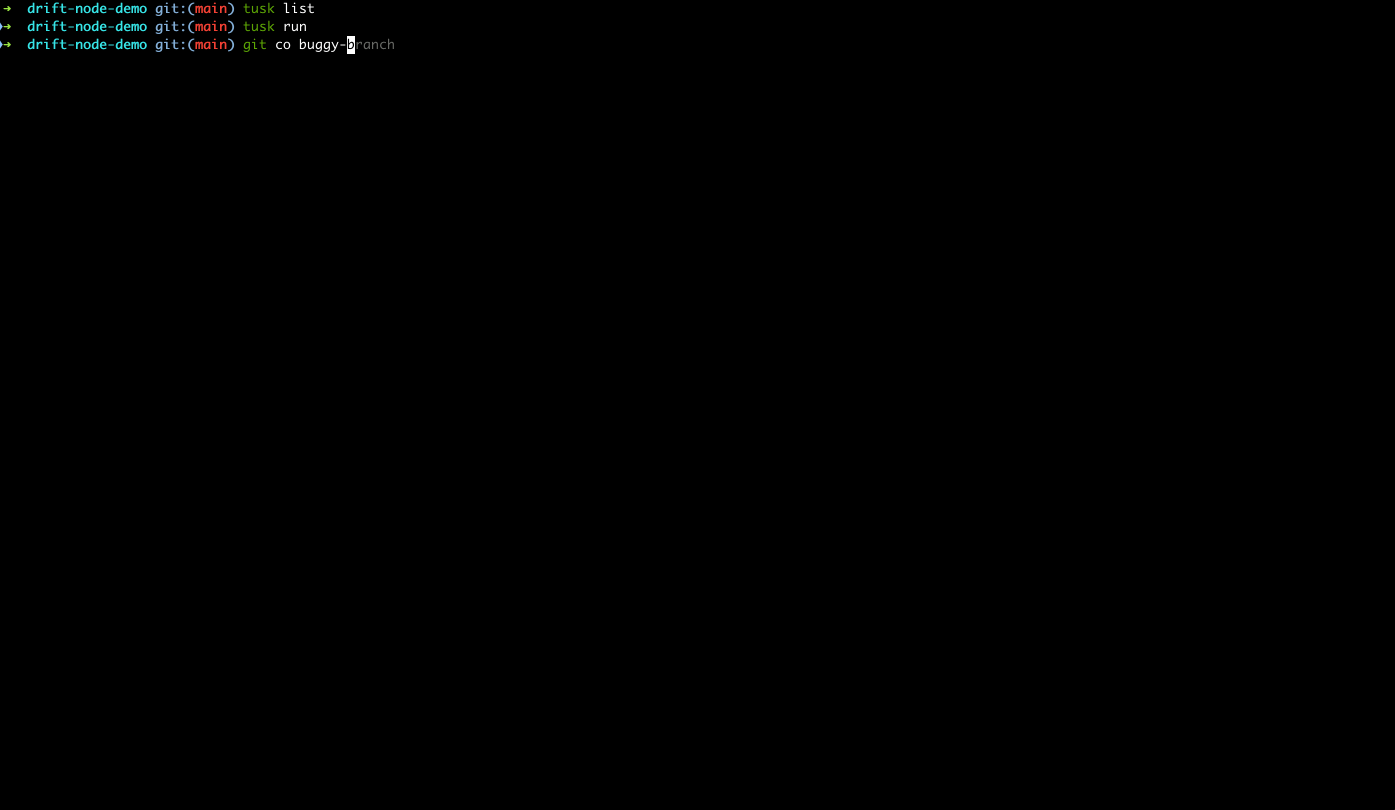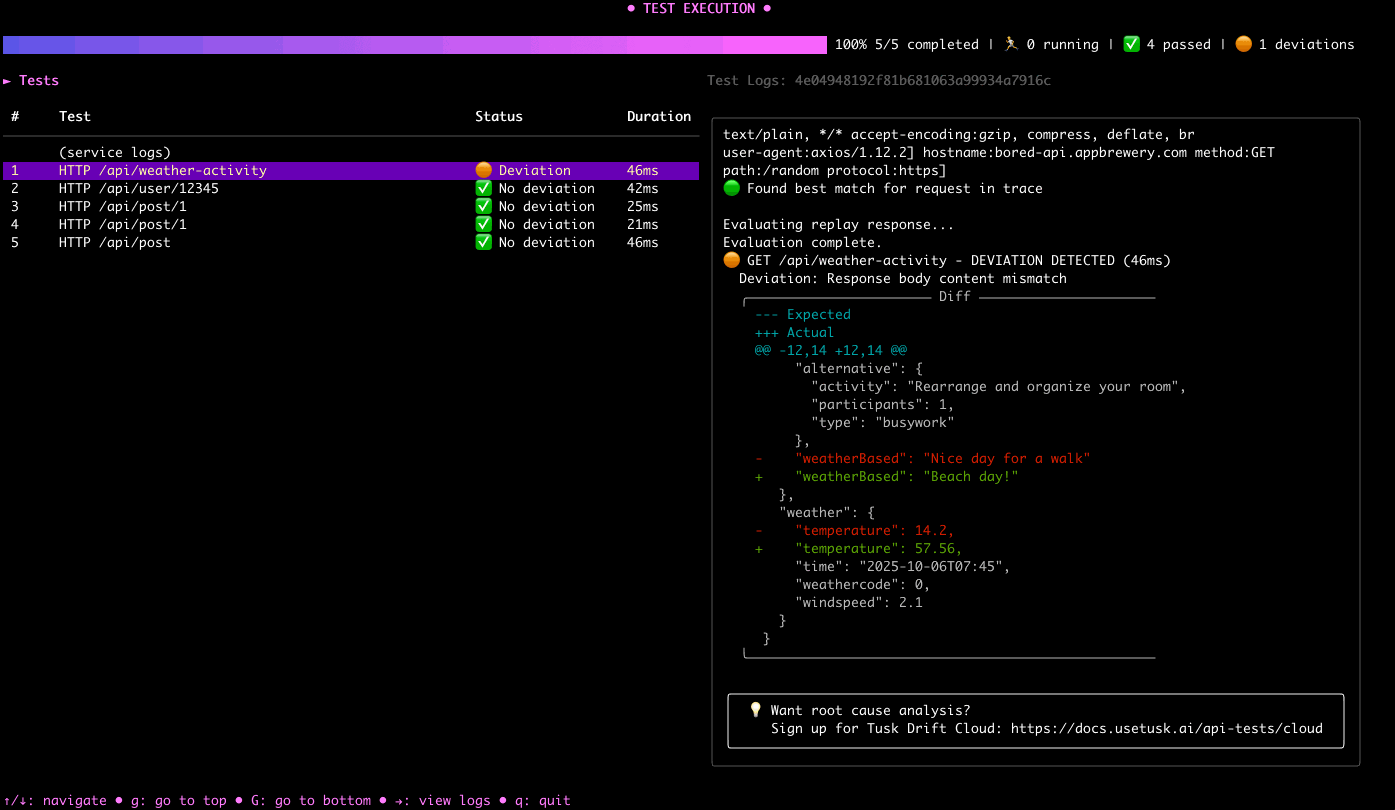 use-tusk/drift-node-sdk
Node.js SDK for capturing and replaying API calls made to/from your service
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
 shaniidev/bug-reaper
Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.