
DivideAndScan
 snovvcrash/divideandscan
Divide full port scan results and use it for targeted Nmap runs
network-mappingpenetration-testingport-scanning+2
snovvcrash/divideandscanDivide full port scan results and use it for targeted Nmap runs
 murrez/cve-2026-101894
Python PoC for CVE-2026-101894: symlink-chain path traversal in @xhmikosr/decompress. Includes local Node lab, lockfile version scan, and mass…
 bountystrike/bountystrike-sh
Poor (rich?) man's bug bounty pipeline https://dubell.io
 hpfeeds/hpfeeds
Honeynet Project generic authenticated datafeed protocol
 pompelmi/pompelmi
ClamAV antivirus scanning for Node.js — scan file uploads with a single function call. Zero dependencies. Typed Symbol verdicts. Local or…
 bee-san/rustscan
🤖 The Modern Port Scanner 🤖
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 raskrebs/sonar
CLI tool for inspecting and managing services listening on localhost ports
 stevenaldinger/decker
Declarative penetration testing orchestration framework
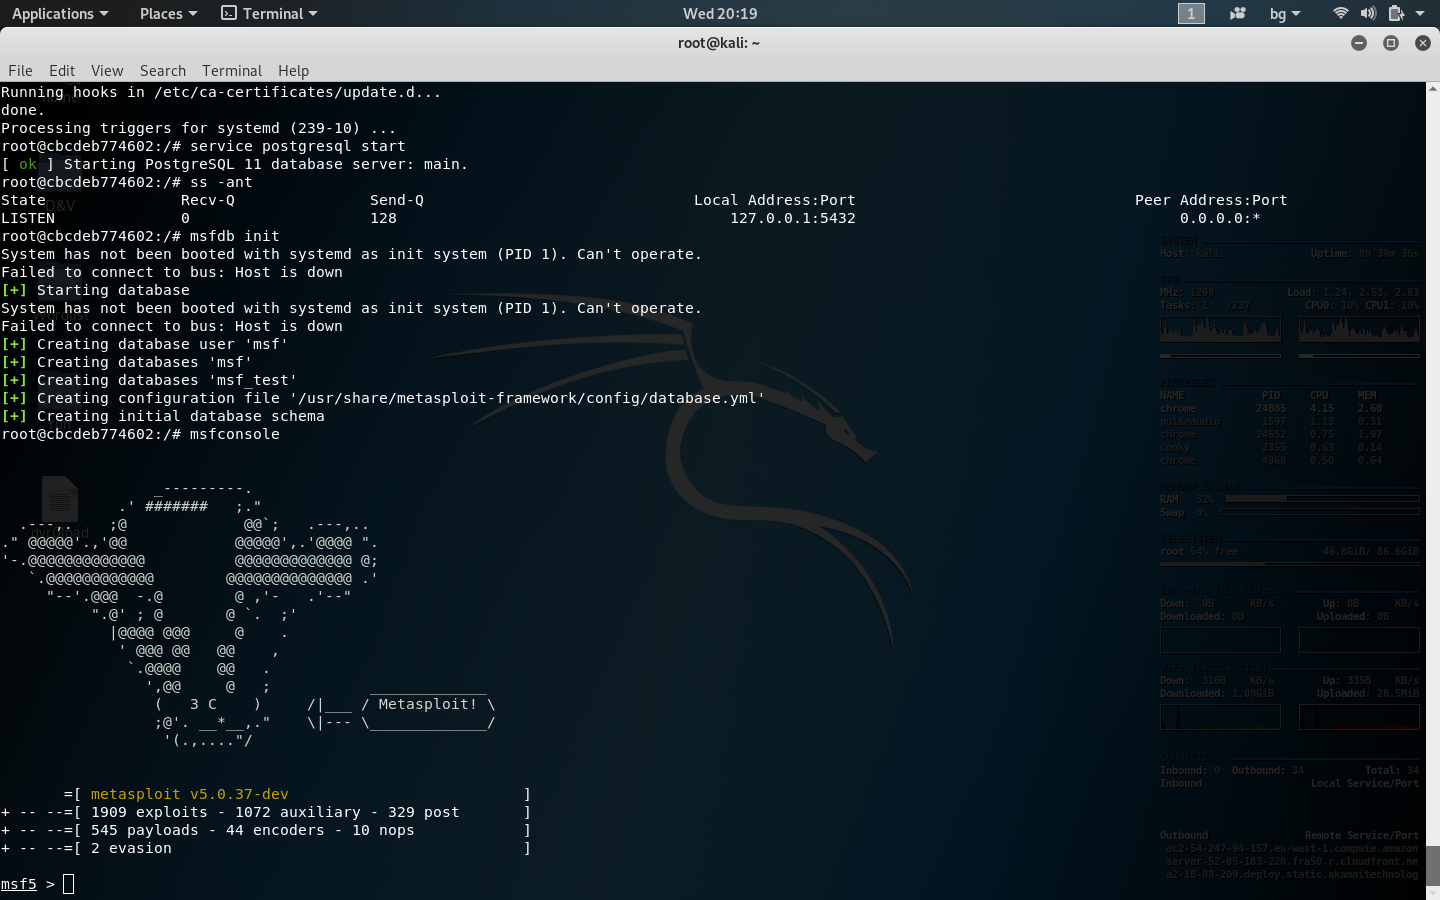 nu11secur1ty/kali-linux-docker
kali-linux-docker
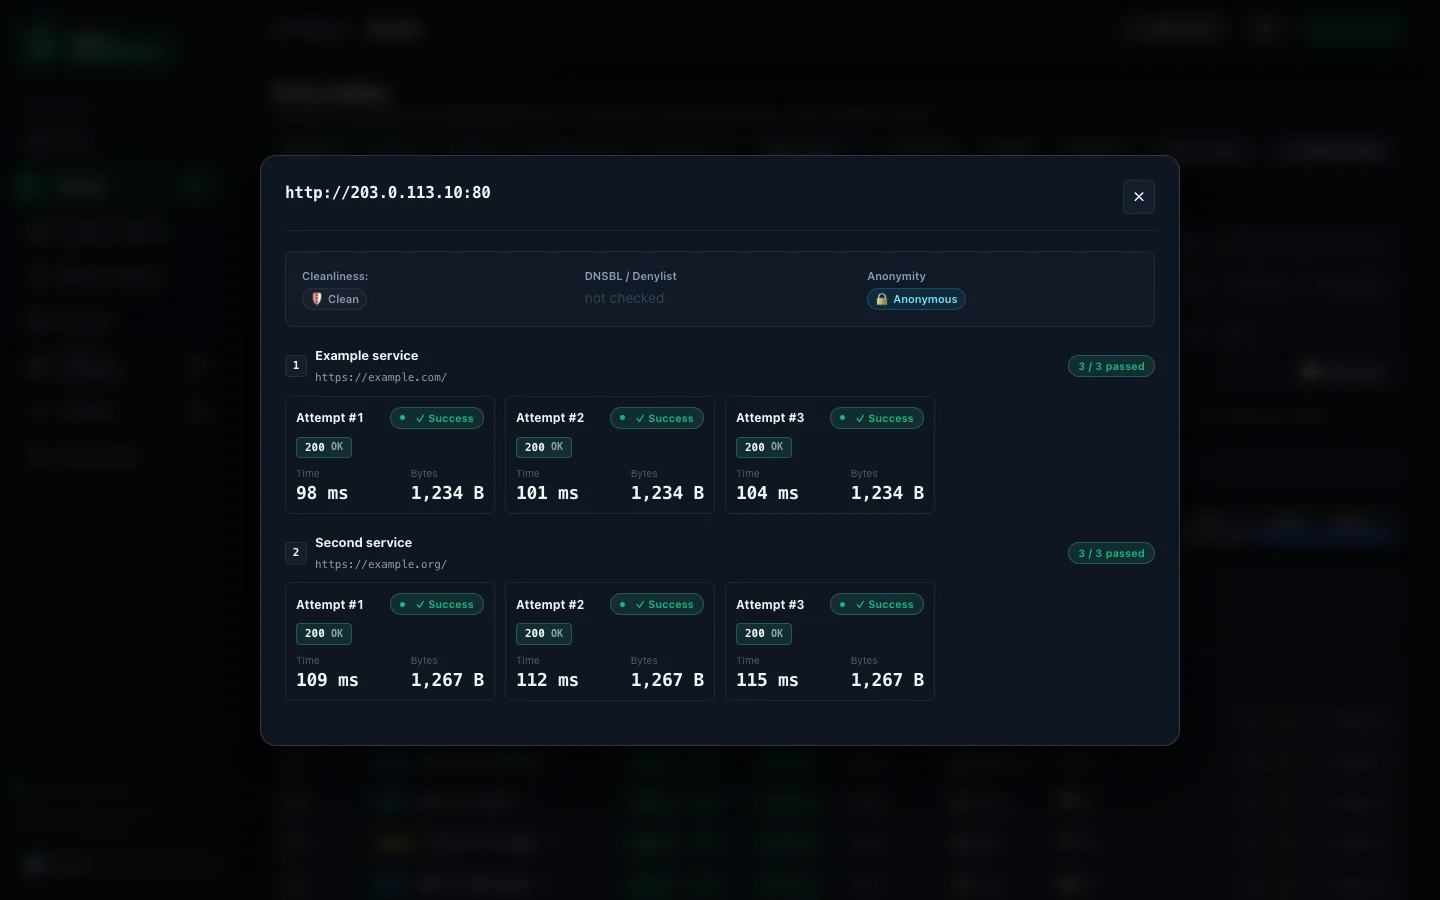 davidvoitenko/proxy-workbench
Collects, checks and ranks public HTTP/SOCKS proxies against your own targets, then serves them via ranked exports, pools, a rotating gateway and a…


 smicallef/spiderfoot
Automates OSINT data collection and analysis for threat intelligence, attack surface mapping, and reconnaissance. Integrates 200+ modules for DNS,…
 bugbasesecurity/pentest-copilot
AI-driven penetration testing agent that connects to a Kali box, autonomously runs security tools, analyzes results, and iterates through…
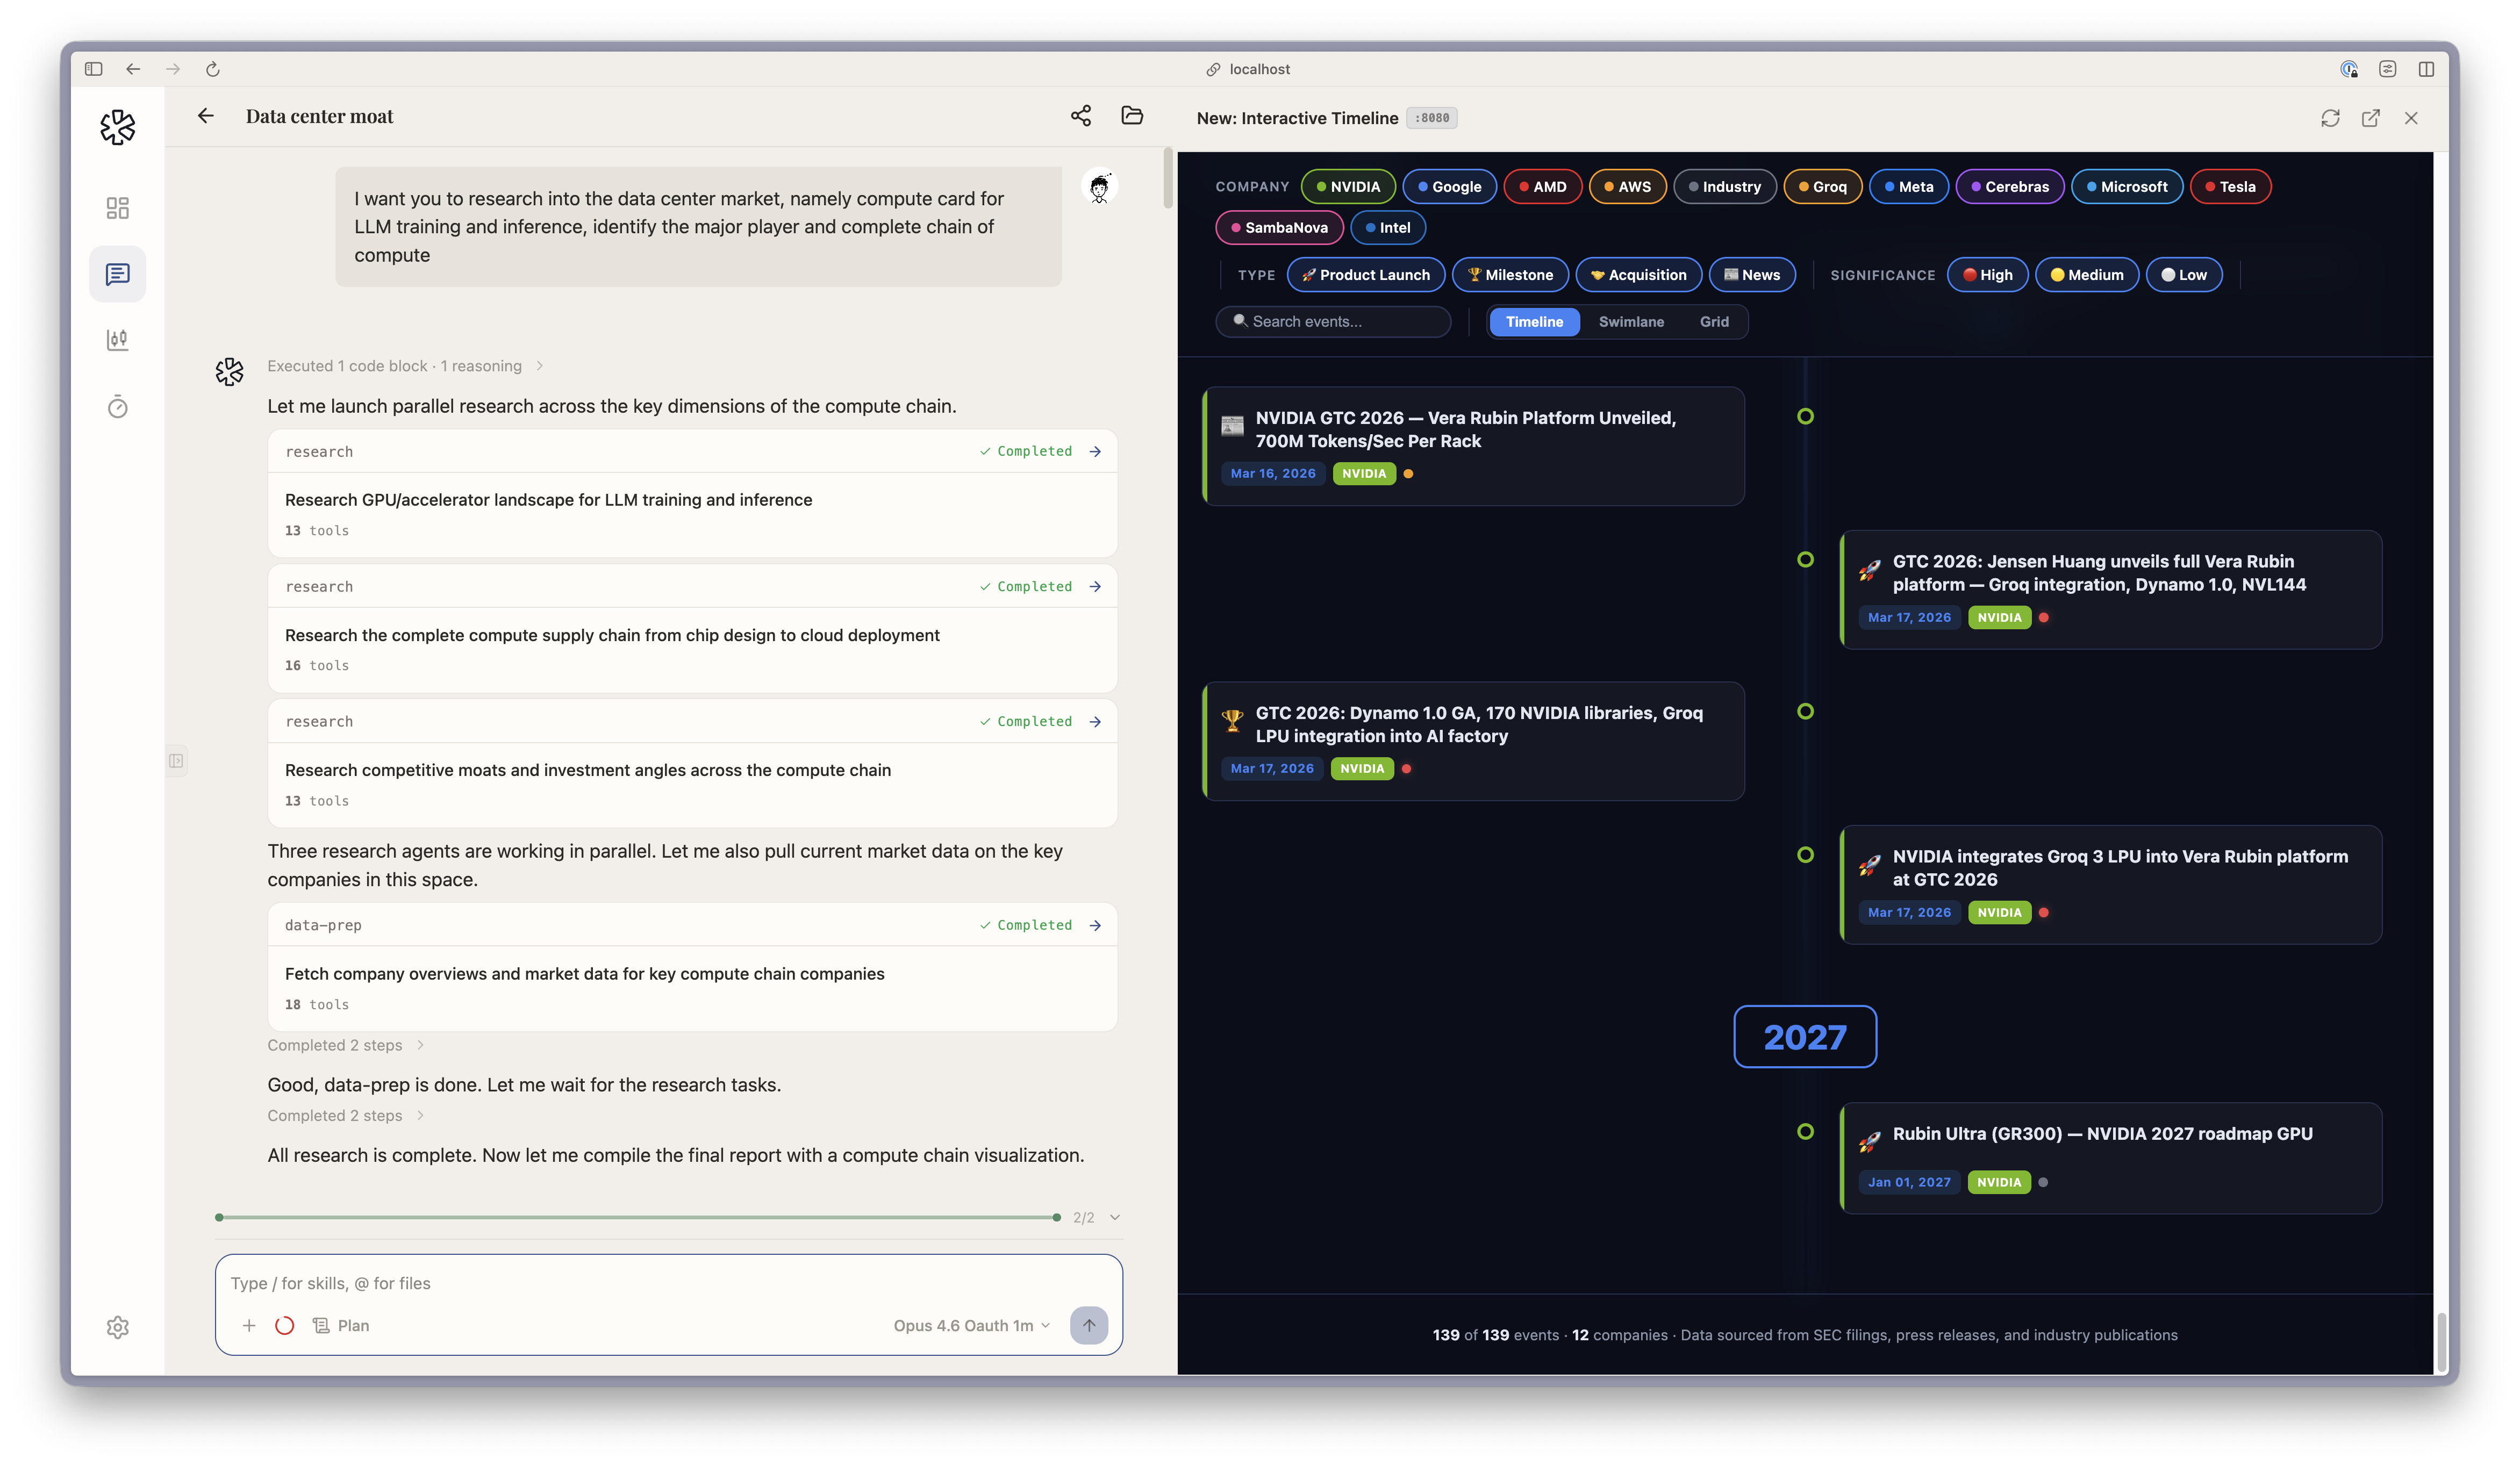 ginlix-ai/langalpha
Automated OSINT framework for reconnaissance, data harvesting, and threat intelligence gathering with modular crawlers, scanners, and extraction…
 rhynorater/cve-2018-15473-exploit
Exploit written in Python for CVE-2018-15473 with threading and export formats
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…