
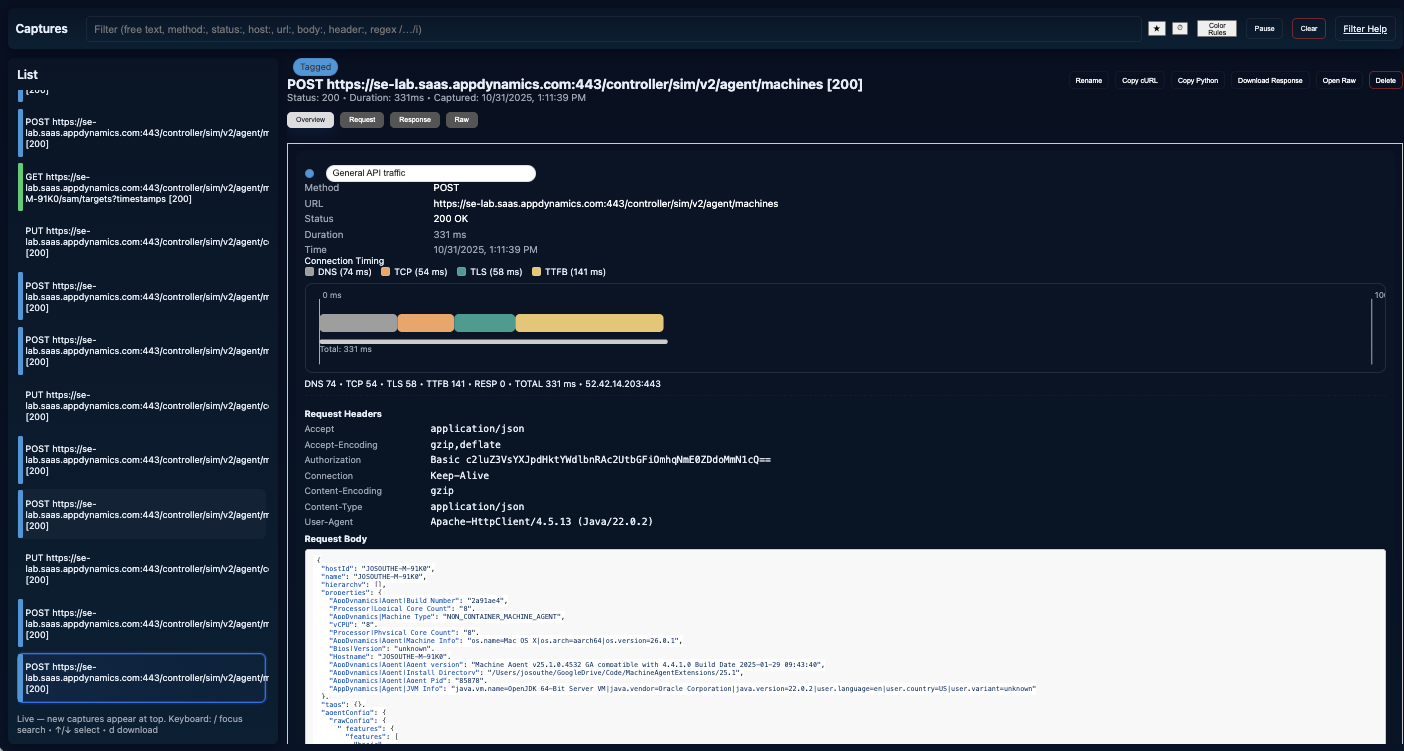
http-breakout-proxy
 jbsouthe/http-breakout-proxy
HTTP Proxy Analysis for reverse engineering protocol communication
api-security-testinginformation-gatheringlog-analysis+5
jbsouthe/http-breakout-proxyHTTP Proxy Analysis for reverse engineering protocol communication
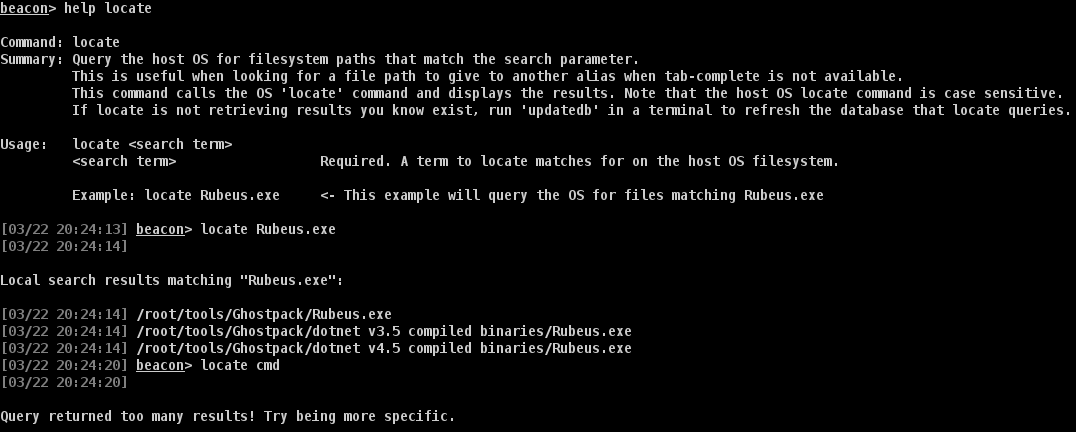 octoberfest7/aggressor_snippets
A collection of random small Aggressor snippets that don't warrant their own repo
 guokers/aioscan_cve-2020-0796
基于asyncio(协程)的CVE-2020-0796 速度还是十分可观的,方便运维师傅们对内网做下快速检测。
 vichhka-git/renef-skills
Agent Skill for operating renef.io — Android ARM64 dynamic instrumentation: hook native/Java, patch memory, trace syscalls, bypass SSL pinning/root…
 ianxtianxt/sleuthql
SleuthQL是基于python3所开发的一款,用于批量爬行站点可能存在sql的地址。并且可以配合burp+sqlmap进行批量注入。 对比sqlmap手动单线程一个一个注入点的去识别,方便了很多。
 5gstudent/cve-2021-22005-
CVE-2021-22005批量验证python脚本
 vertexcover-io/strot
API Scraper Agent for Web API's
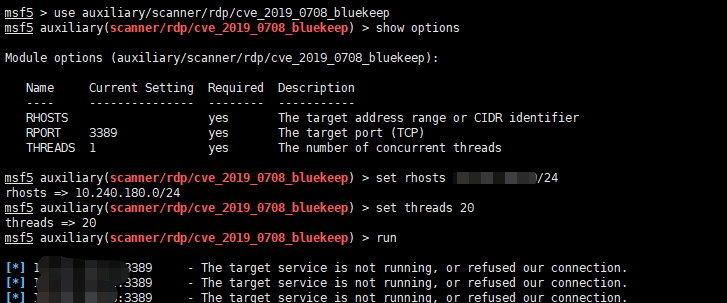 pa55w0rd/cve-2019-0708
CVE-2019-0708批量检测
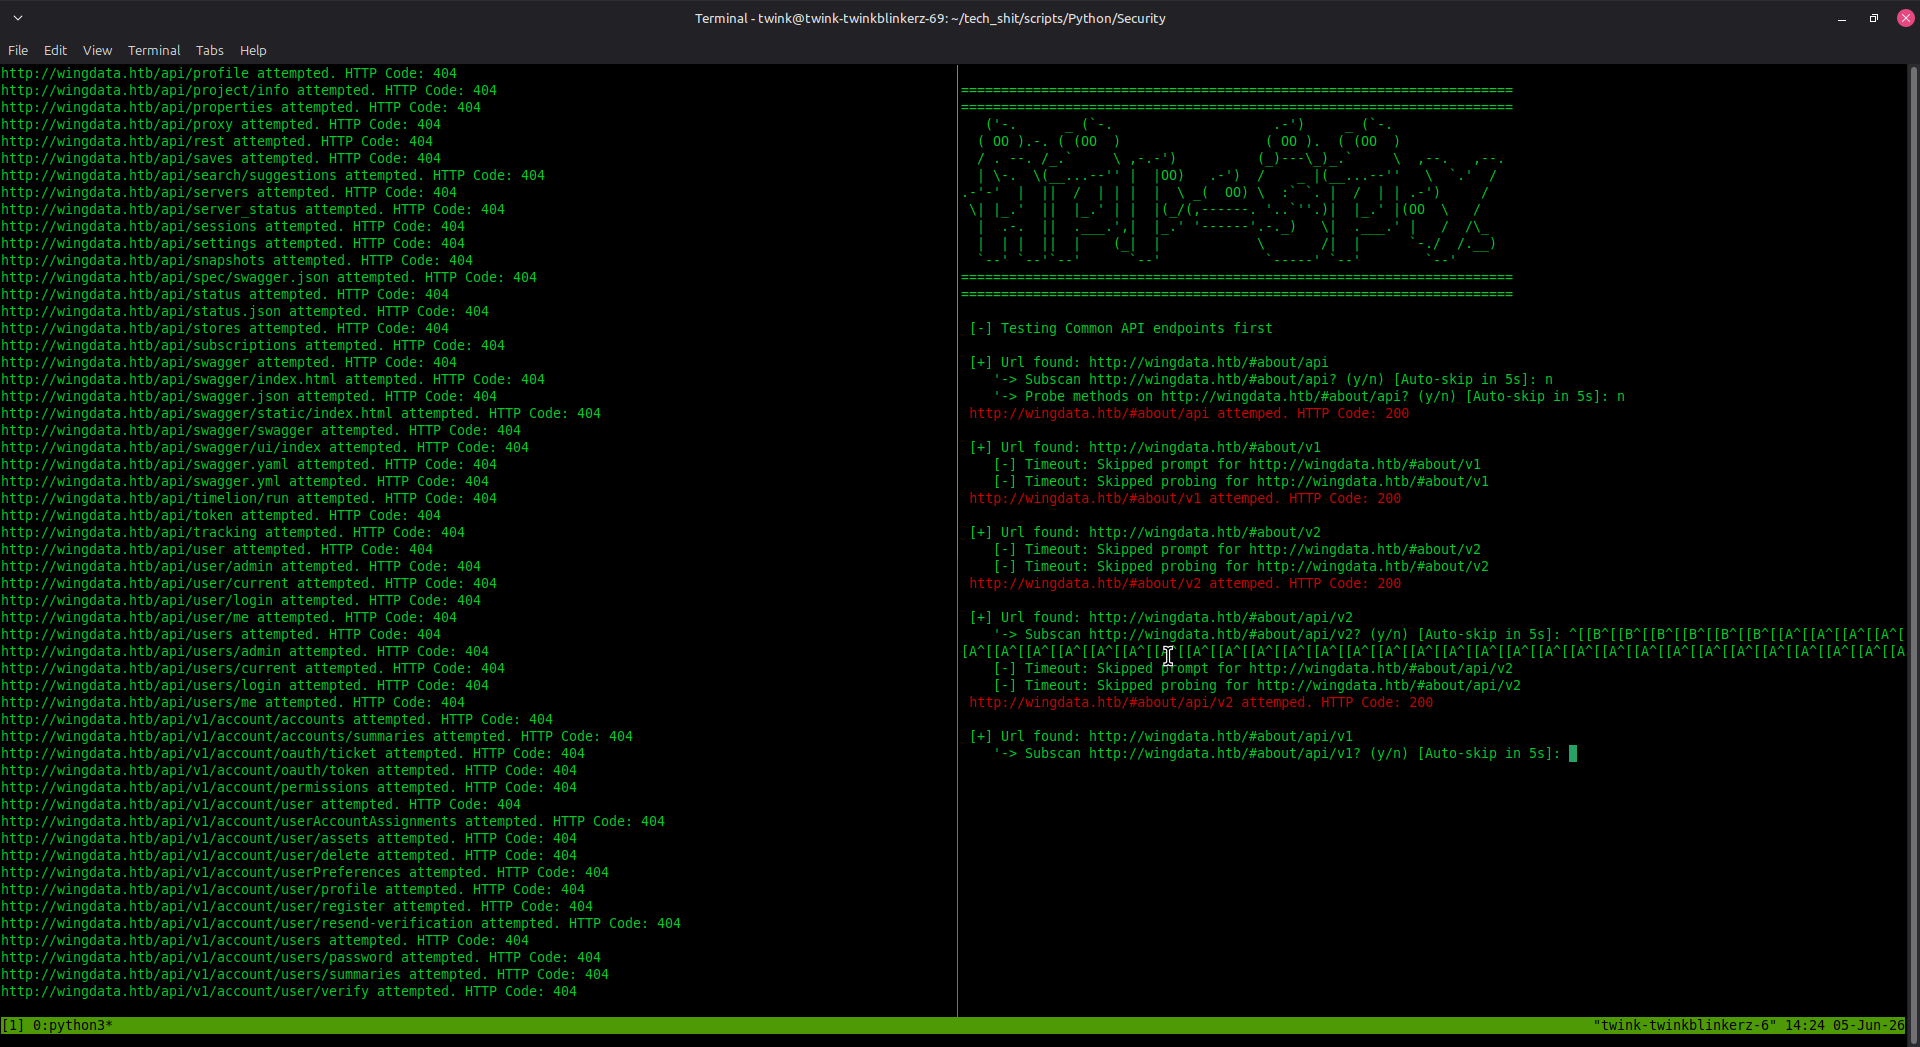 austinjump-sec/api-spy-api-probe
A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
 oleg-fiksel/ansible_cve-2016-5195_check
Ansible playbook to test systems for the Dirty COW privilege escalation vulnerability (CVE-2016-5195) with automated local exploitation checks.
 larrypeseckis/burp-cc-bridge
REST API automation for Burp Suite Community Edition. Drop-in Java extension exposing send/repeat/history endpoints over a local HTTP API.
 abhishekghosh/freak-attack-cve-2015-0204-testing-script
Basic BASH Script to Automate OpenSSL based testing for FREAK Attack (CVE-2015-0204) as advised by Akamai.
 infobyte/alexafaraday
Alexa skill example for Faraday API
 repo4chu/cve-2026-78804_dolibarr_authenticated_sql_injection
The action responsible for setting the per-warehouse stock alert threshold (`seuil_stock_alerte`) accepts user-controlled input and later…
 0xbartita/cookie-swapper
Burp Suite extension that auto-replaces cookies and headers in requests using configurable rules. Eliminates manual copy-pasting of session tokens…
 johenlastgen-jlg/cve-2026-18351
Mass exploit tool for CVE-2026-18351, an unauthenticated arbitrary file upload to RCE in Elementor Forms <= 1.6.0, with passive probing, shell…