

gori
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
api-security-testingfuzzinginformation-gathering+8
hahwul/goriA fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 unkn0wn-root/resterm
Terminal API client for HTTP, GraphQL, gRPC, WebSocket and SSE. Plain .http files you can diff and version, with scripted tests, workflows, mocks,…
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 owasp-amass/amass
In-depth attack surface mapping and asset discovery
 owasp/xpsd
Reachability triage for vulnerability scans. Feeds scanner findings to an LLM agent that reads your source and decides which CVEs are actually…
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 bifrost-proxy/bifrost
High-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…
 owasp/agentic-vulnerability-discovery-and-validation-harness
Agentic harness that automates vulnerability discovery and validation, orchestrating AI-driven analysis workflows to confirm exploitable findings.
 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…
 devcop95/bugbounty-lab101
A complete bug bounty workspace for HackerOne researchers. Includes scope enforcement, automated recon/vuln pipeline (400+ tools), report templates,…
 brutelogic/unkover
Bash 403/401 access bypass tester that probes a URL with header spoofing, method tampering, path normalization, and encoding techniques, returning a…
 kamalx06/xxeripper
Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
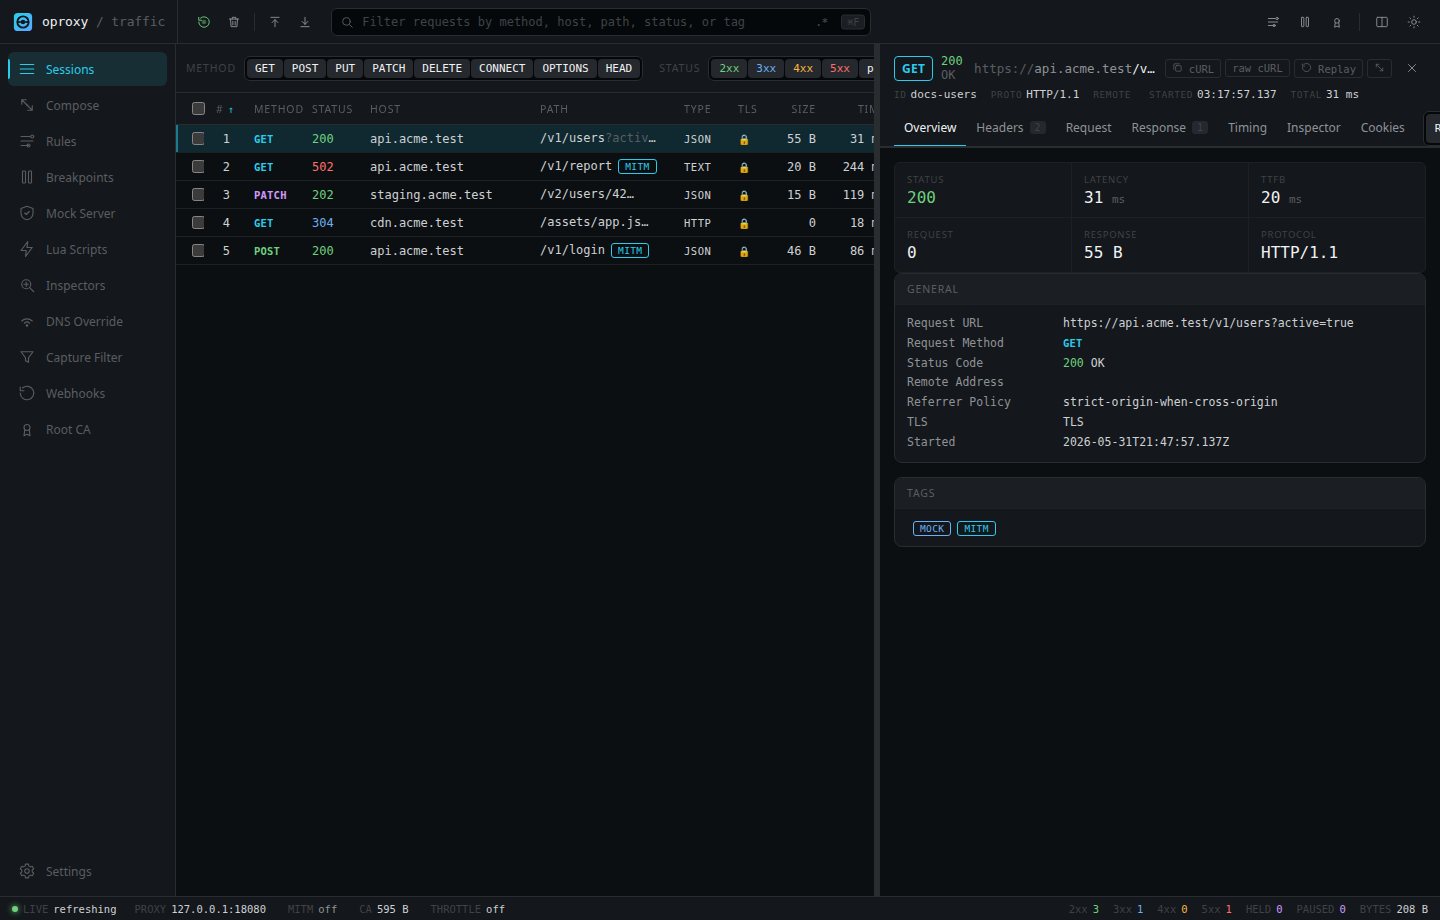 sauravrao637/oproxy
Open-source MITM proxy to intercept, inspect, and mock network traffic.
 saffron-health/libretto
The AI toolkit for building reliable browser automations
 portswigger/burp-extensions-montoya-api-examples
Sample Burp Suite extensions demonstrating the Montoya API, covering HTTP and proxy handlers, custom scan checks, Intruder payloads, WebSocket…
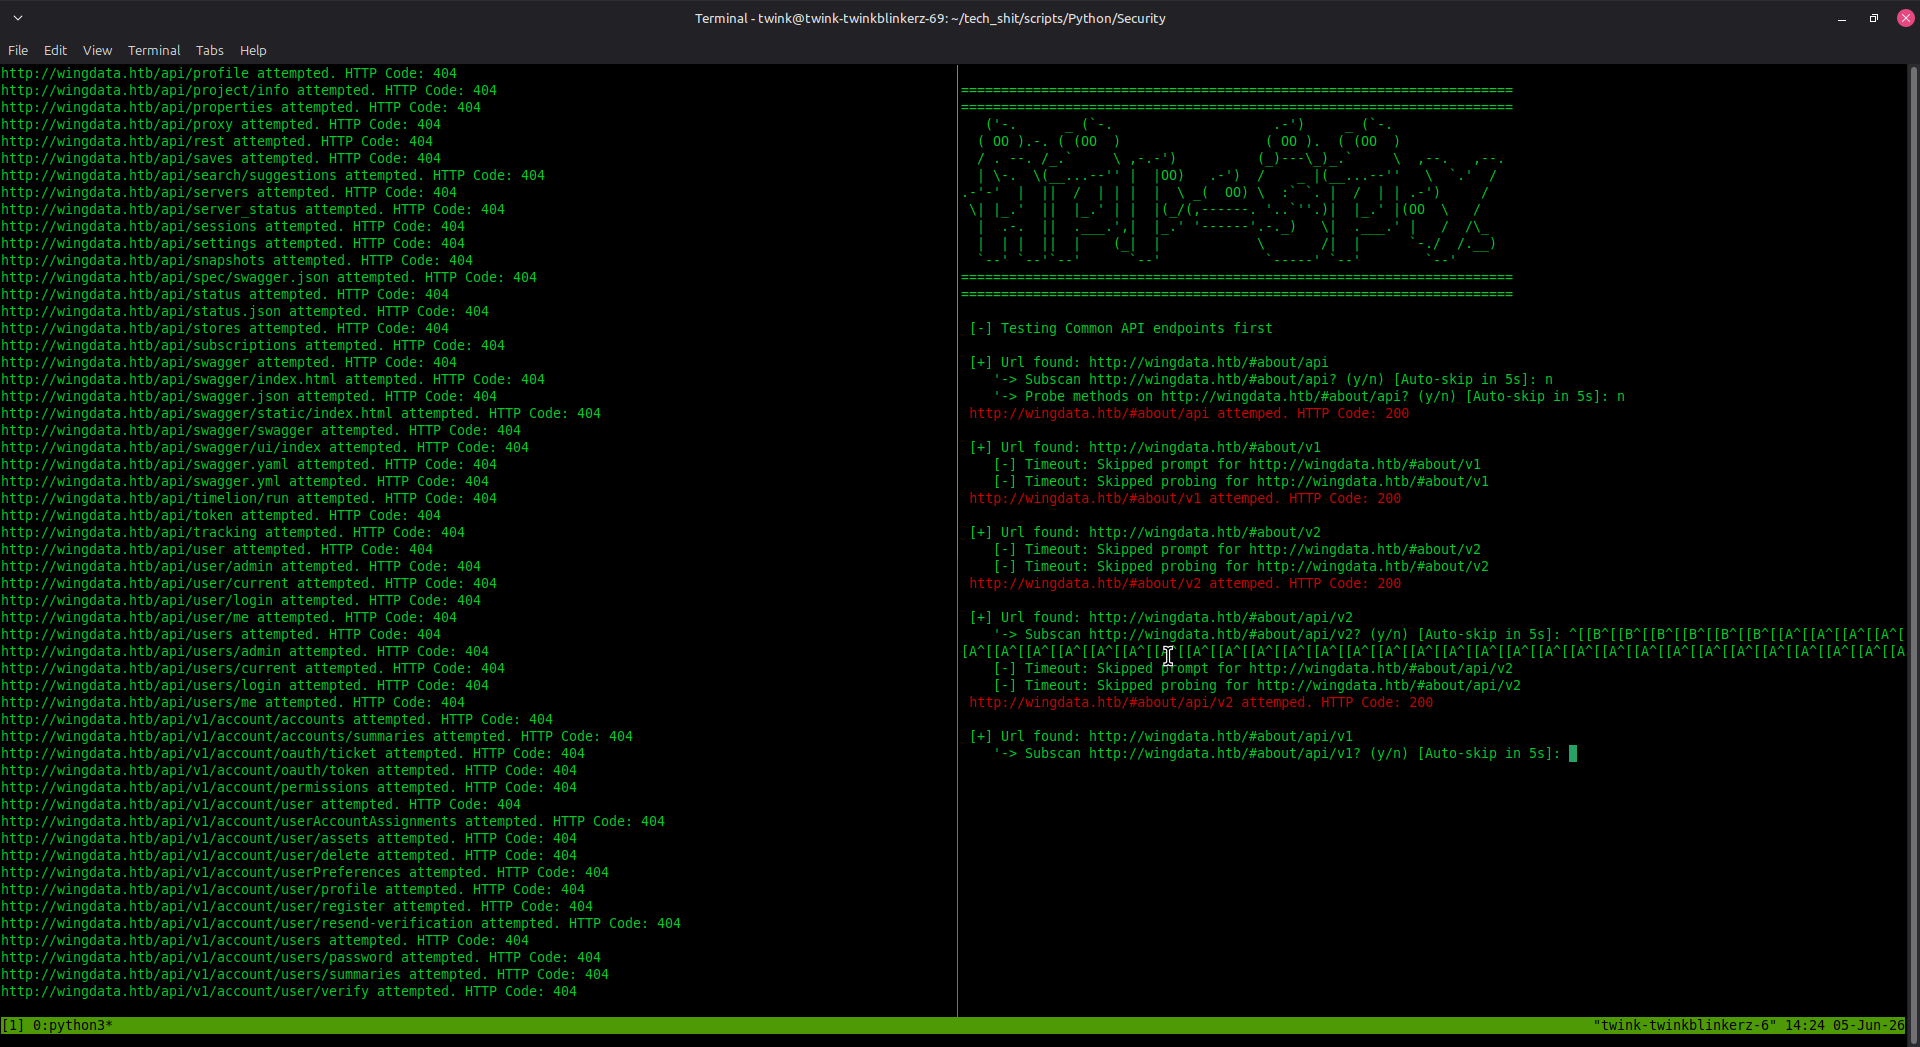 austinjump-sec/api-spy-api-probe
A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…
 larrypeseckis/burp-cc-bridge
REST API automation for Burp Suite Community Edition. Drop-in Java extension exposing send/repeat/history endpoints over a local HTTP API.