
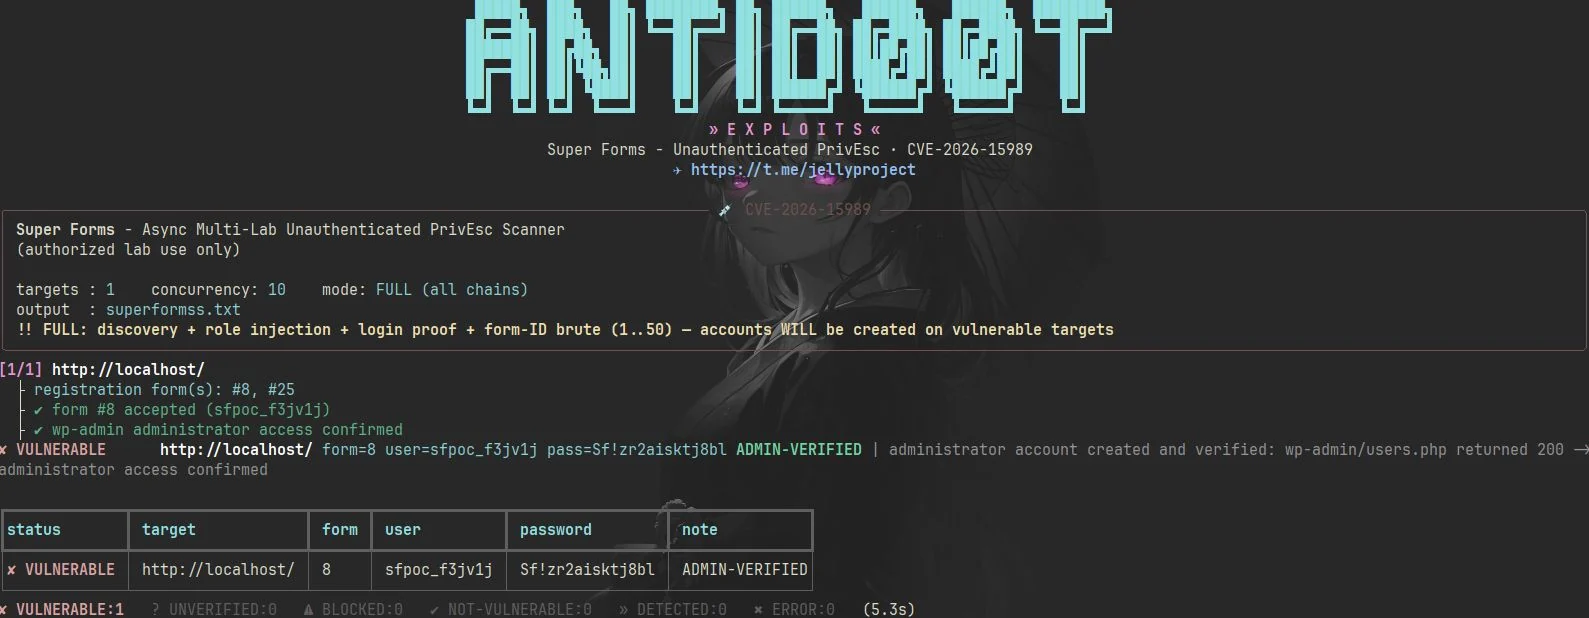
CVE-2026-15989
 antid00t/cve-2026-15989
Python PoC scanner for CVE-2026-15989, exploiting unauthenticated role injection in WordPress Super Forms to create admin accounts and verify access.
exploitationpassword-attackspenetration-testing+6
1
antid00t/cve-2026-15989Python PoC scanner for CVE-2026-15989, exploiting unauthenticated role injection in WordPress Super Forms to create admin accounts and verify access.
 mordavid/bruteforceai
Advanced LLM-powered brute-force tool combining AI intelligence with automated login attacks
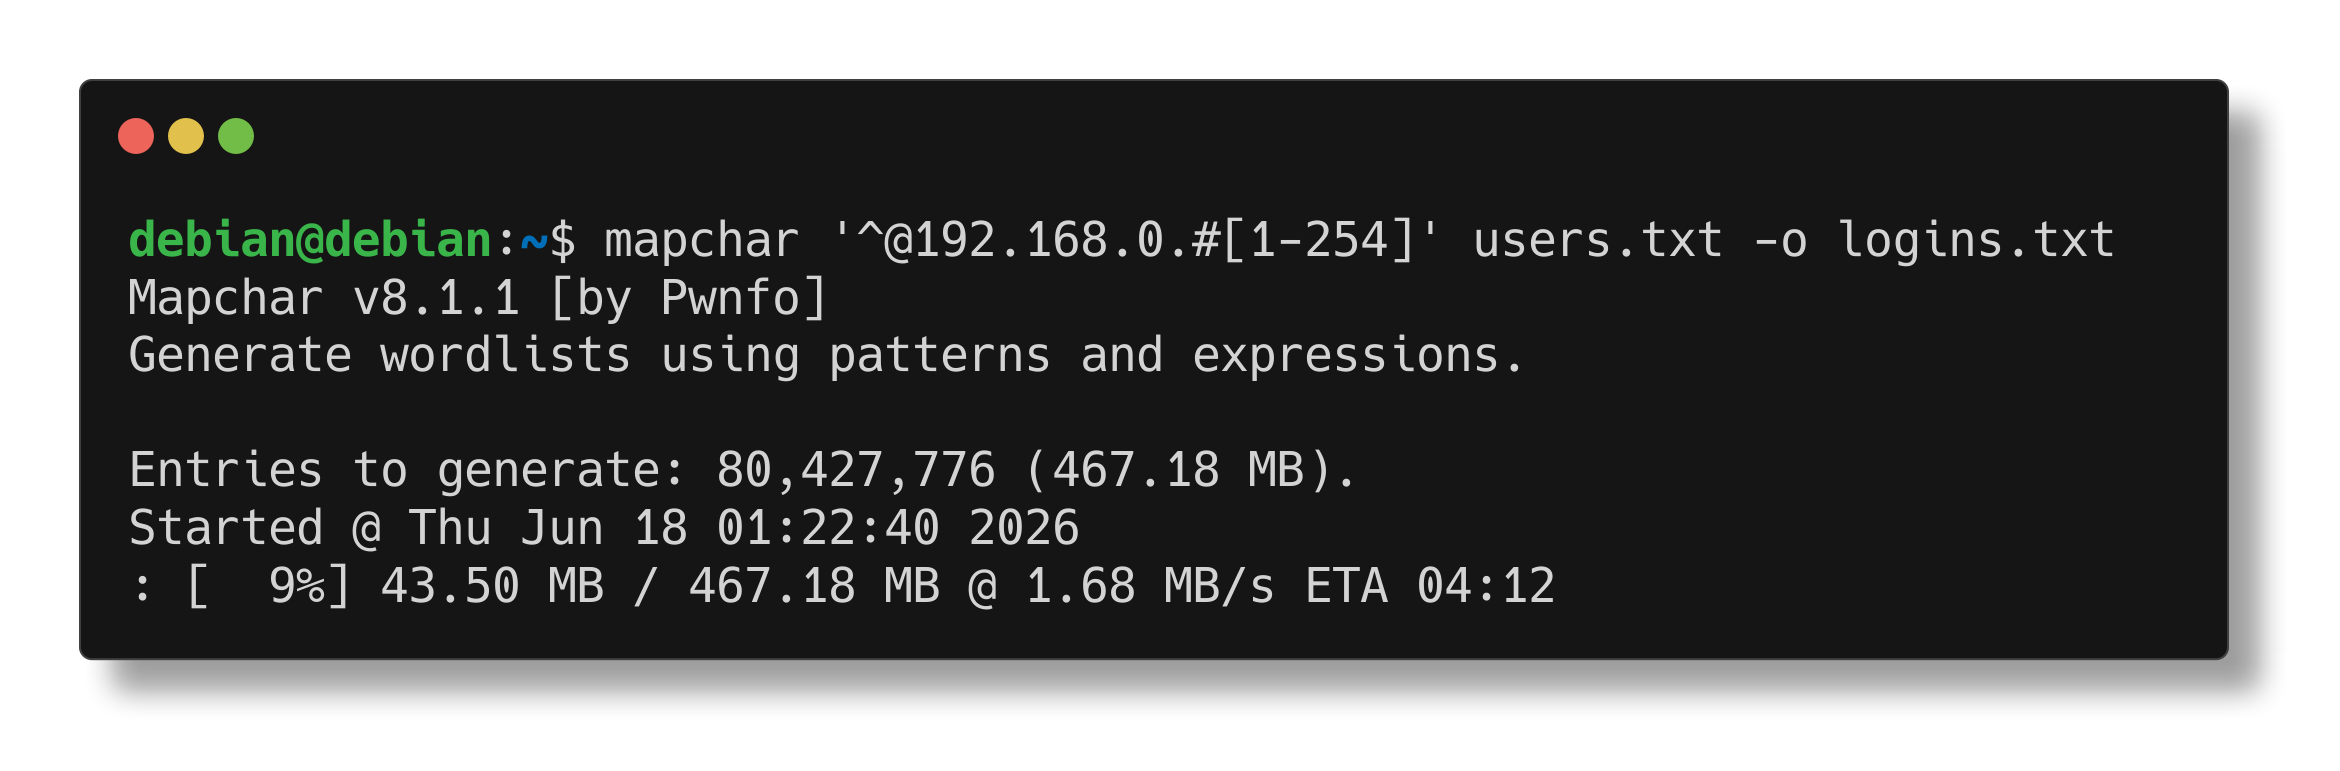 pwnfo/mapchar
Generate wordlists using pattern logic and expressions.
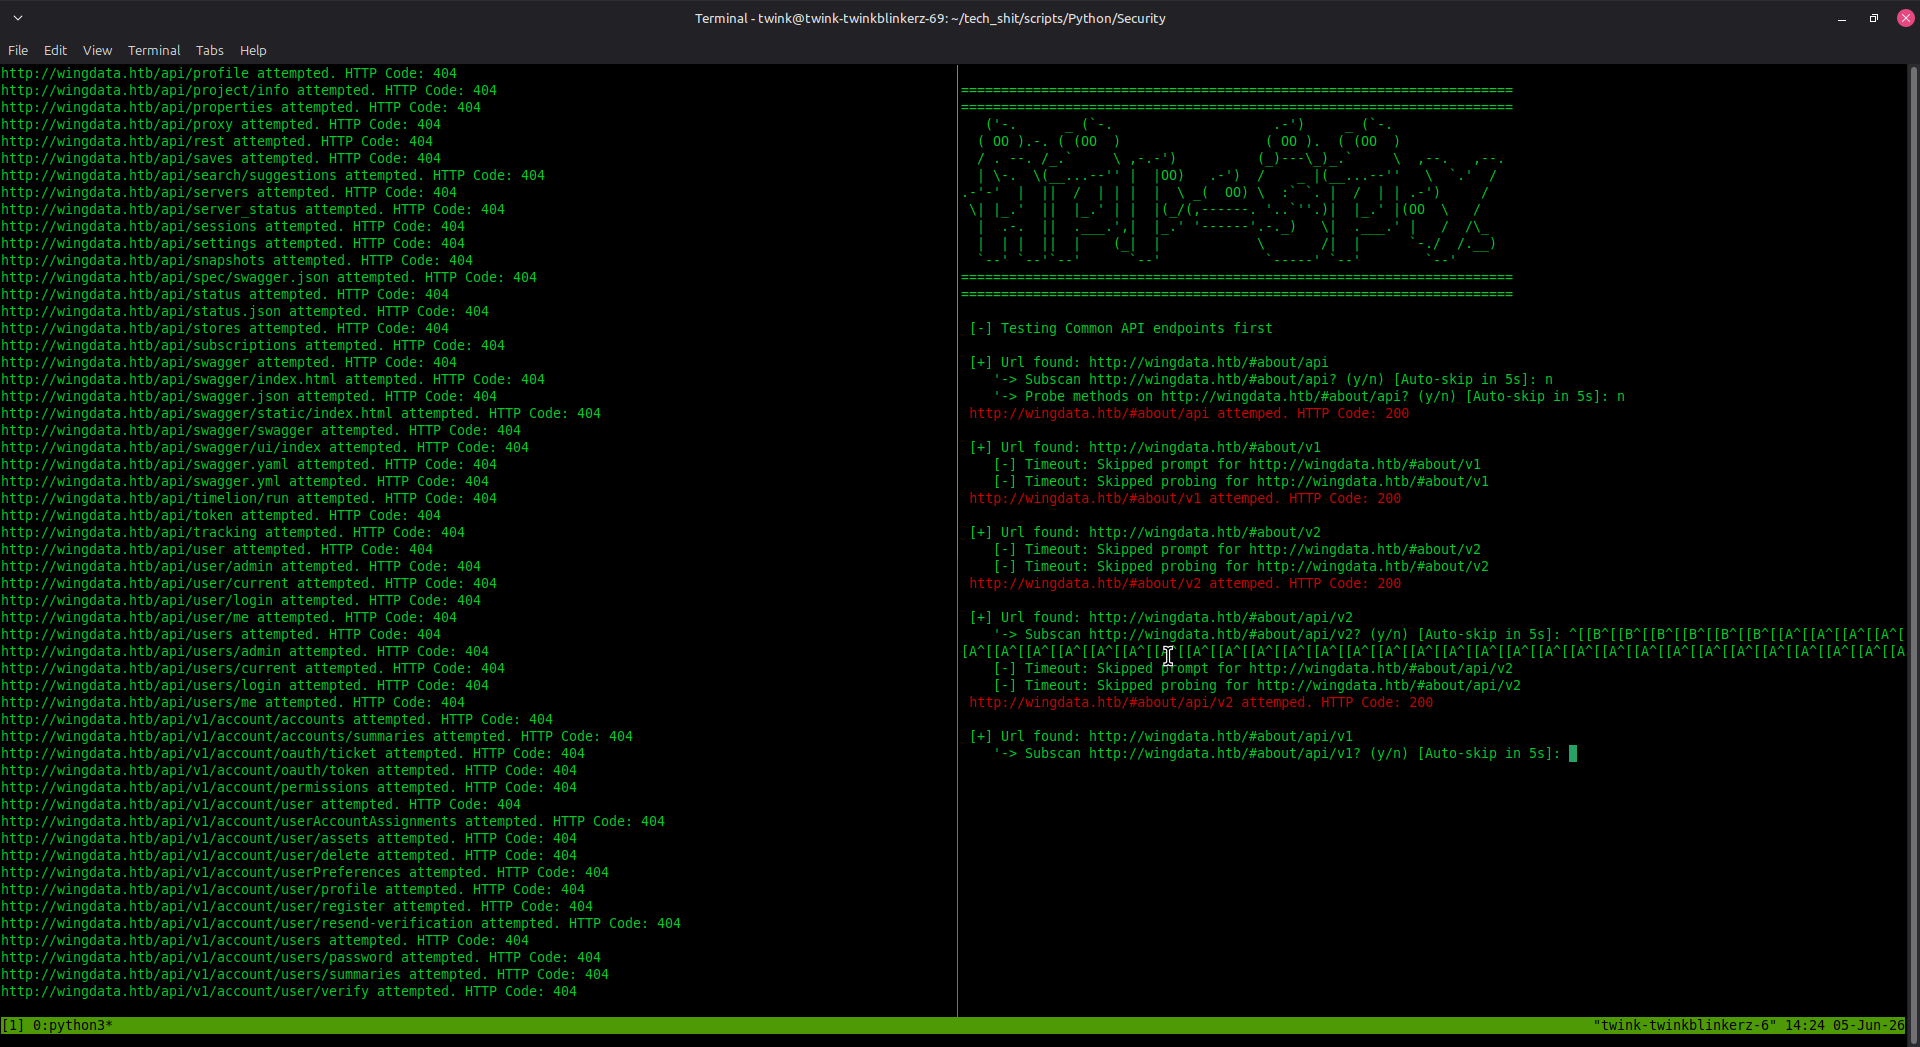 austinjump-sec/api-spy-api-probe
A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…
 jenderal92/prepos-login-checker
Prepostseo Login Checker
 jdormannn/secureops-lab
Performed a live cybersecurity assessment on a university Linux server. During analysis, active attack activity was identified, including brute-force…
 hackingyseguridad/smb
Shell script collection for SMB protocol auditing, vulnerability detection (EternalBlue, SMBGhost), null session enumeration, credential brute-force,…
 evildevill/devil
Menu-driven shell framework bundling brute-force login attacks, friendlist and profile data harvesting, and automated Facebook account-grabbing…
 xpn/randomtsscripts
Collection of RedTeam engagement scripts including Pre2K default credential checks via TGS, LAPSv2 password decryption, and IIS App Pool credential…
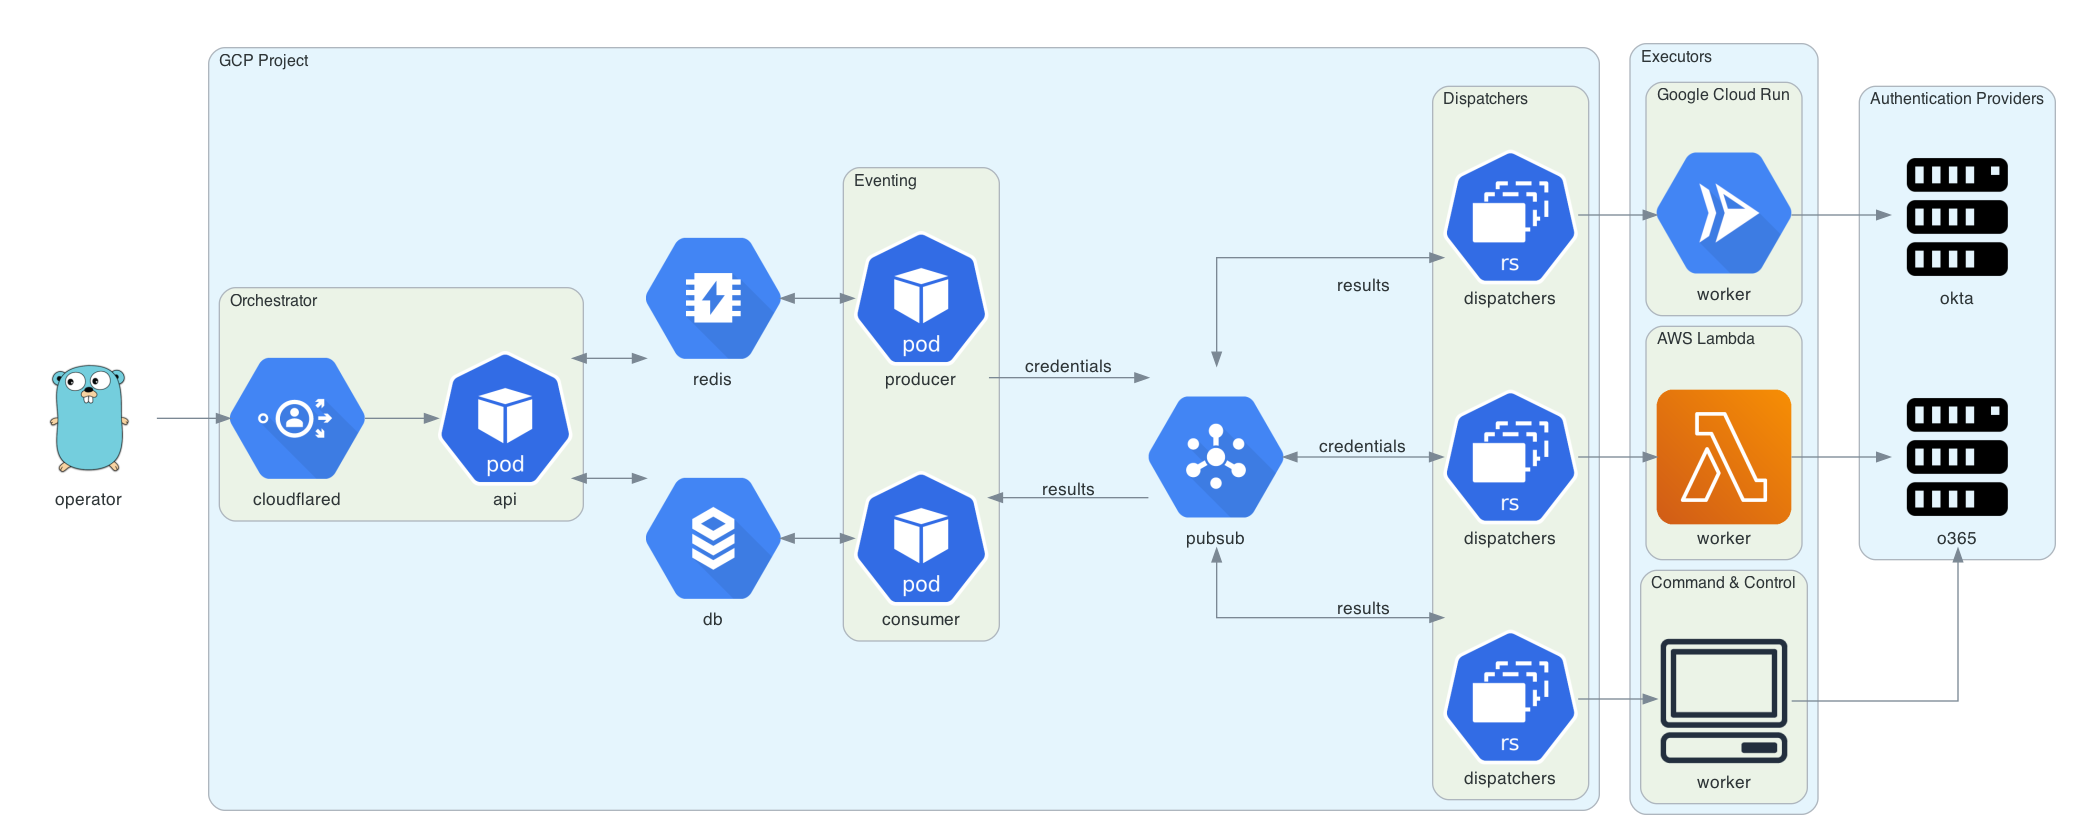 praetorian-inc/trident
automated password spraying tool
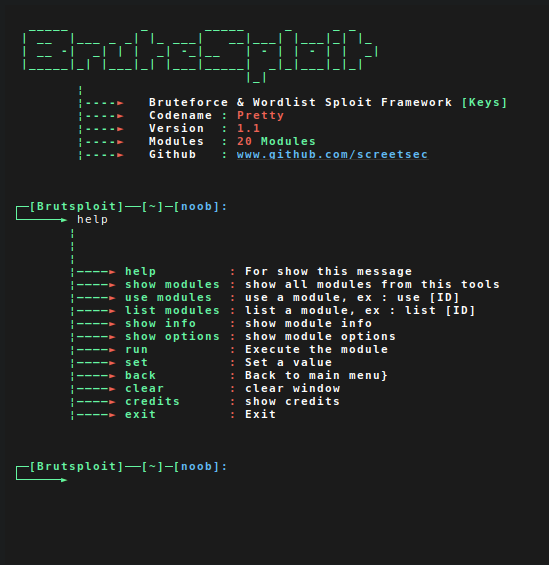 screetsec/brutesploit
BruteSploit is a collection of method for automated Generate, Bruteforce and Manipulation wordlist with interactive shell. That can be used during a…
 eddiejibson/limitrr-php
Better PHP rate limiting using Redis.
 ustayready/credking
Password spraying using AWS Lambda for IP rotation
 timbo05sec/autocrack
Hashcat wrapper to help automate the cracking process