

MCP-God-Mode
 gmh5225/mcp-god-mode
Did you ever just want it to do everything? 148 POWERFUL Infosec/Admin tools on a single MCP server.
command-and-controlhardware-iot-securityinformation-gathering+9
1
gmh5225/mcp-god-modeDid you ever just want it to do everything? 148 POWERFUL Infosec/Admin tools on a single MCP server.
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
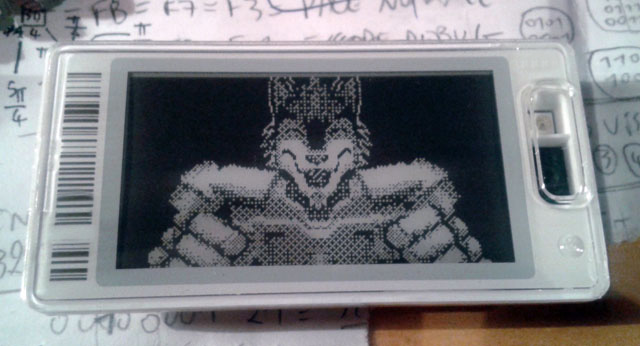 furrtek/precir
Open-source hardware and software toolkit for reverse-engineering and communicating with infrared-based electronic shelf labels. Includes custom…
 flipperdevices/flipperzero-firmware
Flipper Zero firmware source code
 ottoyrocky/phantom-brain
Red portatil de reconocimiento inteligente con IA offline
 nfc-tools/libnfc
Platform independent Near Field Communication (NFC) library
 greatscottgadgets/hackrf
Low-cost open-source software-defined radio platform with hardware designs and firmware for RF transmission, reception, and signal analysis from 1…
 geo-tp/esp32-bit-pirate
A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
 greatscottgadgets/ubertooth
BLE sniffer and Bluetooth experimentation platform with open hardware, firmware, and limited Classic BR packet capture for wireless security work.
 rfidtool/esp-rfid-tool
A tool for logging data/testing devices with a Wiegand Interface. Can be used to create a portable RFID reader or installed directly into an existing…
 electroniccats/catsniffer-firmware
Firmware repository for CatSniffer, a multi-protocol IoT security research board supporting BLE, Zigbee, Sub-1 GHz, and more, with version-specific…
 gentilkiwi/st25tb_kiemul
ST25TB / SRx NFC Emulator / Initiator based on TI TRF7970A with MSP430
 atao/raspberrypi-setup
Ansible playbook for rapid Raspberry Pi setup with modular roles for wireless security testing, RFID/NFC tools, SDR, Docker, Tor proxy, and standard…
 yslxotwod/wifisting
GTK4 wireless security toolkit with 57 standalone shell modules for Wi-Fi, Bluetooth, RF, Zigbee, NFC and router-side attacks, plus MITM, recon,…
 brucedevices/firmware
Predatory ESP32 Firmware
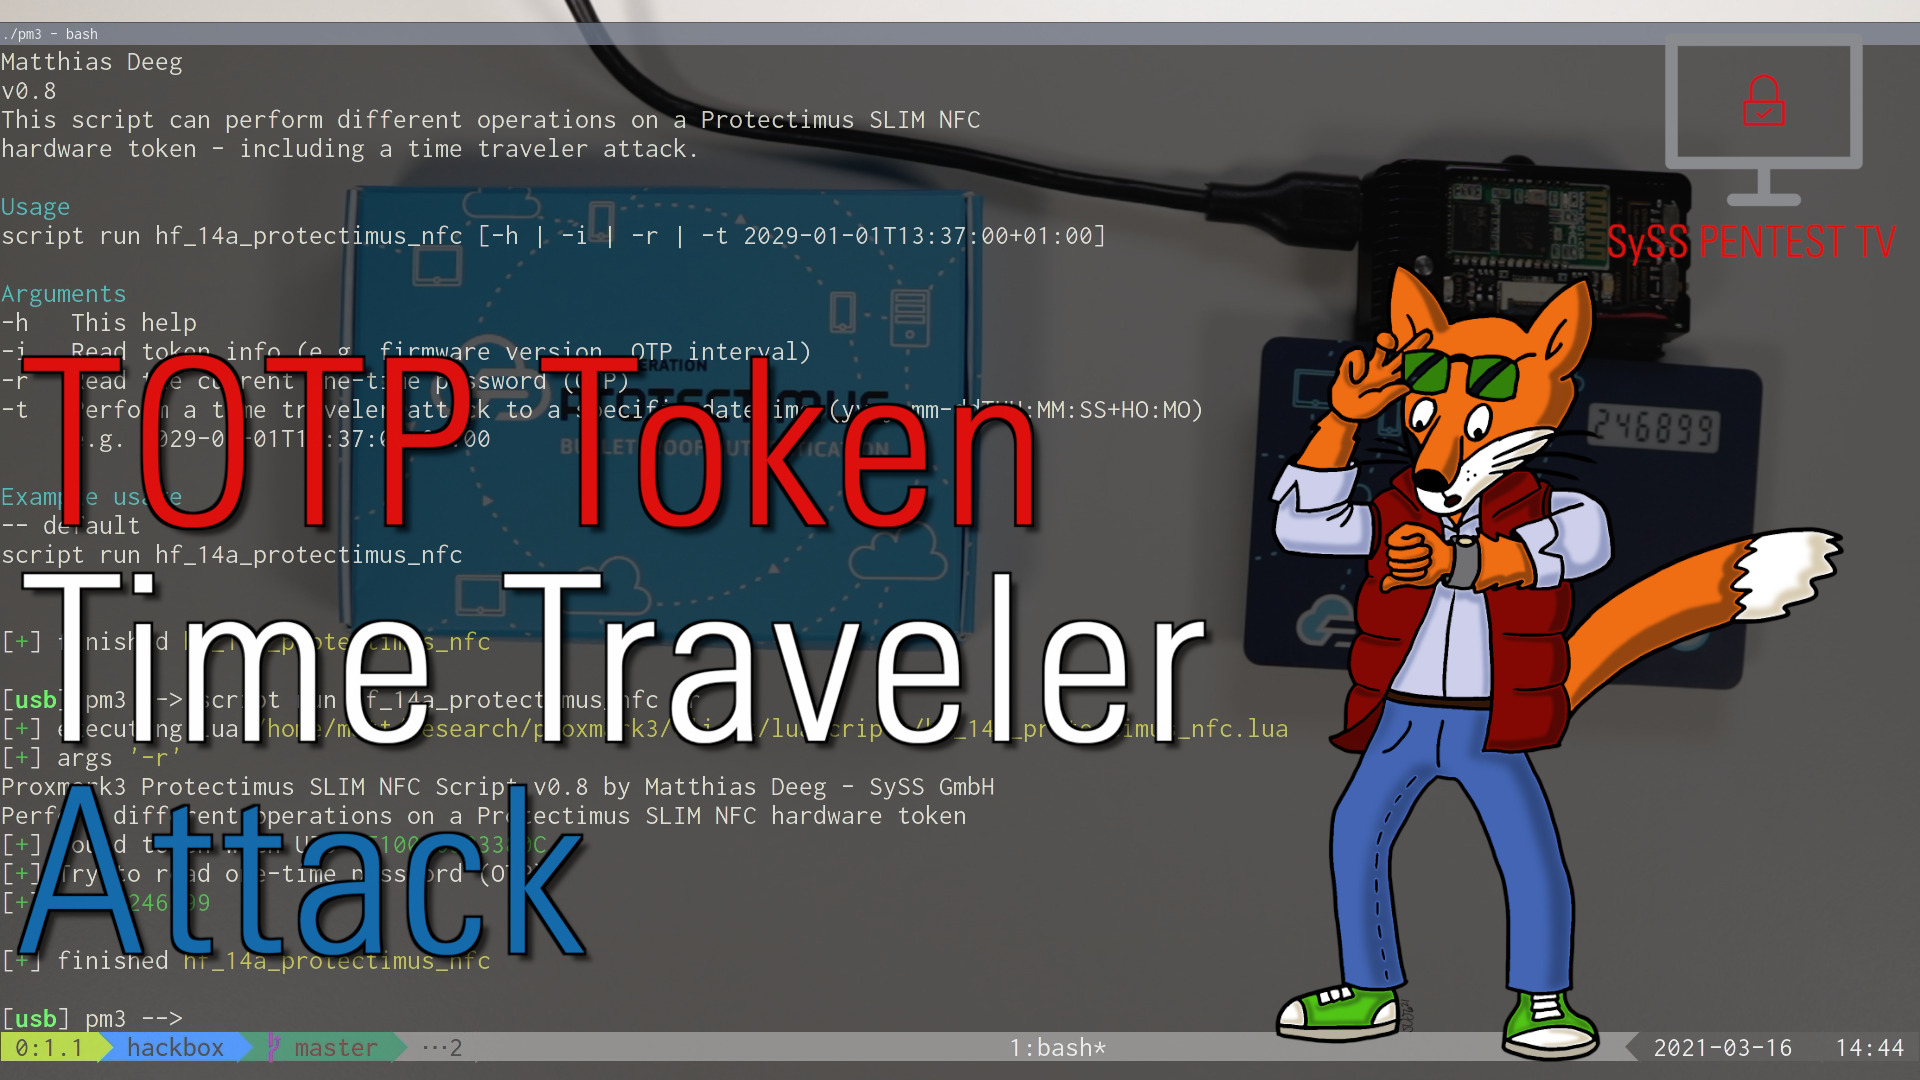 syss-research/protectimus-slim-proxmark3
Proxmark3 Lua script for attacking vulnerable Protectimus SLIM NFC TOTP hardware tokens
 jopohl/urh
Universal Radio Hacker: Investigate Wireless Protocols Like A Boss
 uberguidoz/flipper
Playground (and dump) of stuff I make or modify for the Flipper Zero