

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
454 results
objection preview

objection

GitHubsensepost/objection

Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
android-securitydynamic-analysis-sandboxingexploitation+9
9.4k
7 days ago
shlol preview

shlol

GitHubandreiverse/shlol

do common hacking tasks with a simple menu
payload-generationpenetration-testingred-teaming+1
45 years ago
ghidra2frida preview

ghidra2frida

GitHubfedericodotta/ghidra2frida

Ghidra extension bridging static and dynamic analysis via Frida, enabling scriptable runtime instrumentation for reverse engineering binaries on…
android-securitybinary-analysisdynamic-analysis-sandboxing+3
1355 years ago
workshop_firmware_reverse_engineering preview

workshop_firmware_reverse_engineering

GitHubemproof-com/workshop_firmware_reverse_engineering

Workshop on firmware reverse engineering
binary-analysiseducationembedded-systems-security+6
4510 years ago
stringsifter preview

stringsifter

GitHubmandiant/stringsifter

A machine learning tool that ranks strings based on their relevance for malware analysis.
binary-analysismachine-learningmalware-analysis+2
7633 years ago
winmagic_sd preview

winmagic_sd

GitHubpatois/winmagic_sd

Technical Write-Up on and PoC Exploit for CVE-2020-11519 and CVE-2020-11520
binary-exploitationeducationexploitation+4
123 years ago
matrix-rs preview
Archived

matrix-rs

GitHubmemn0ps/matrix-rs

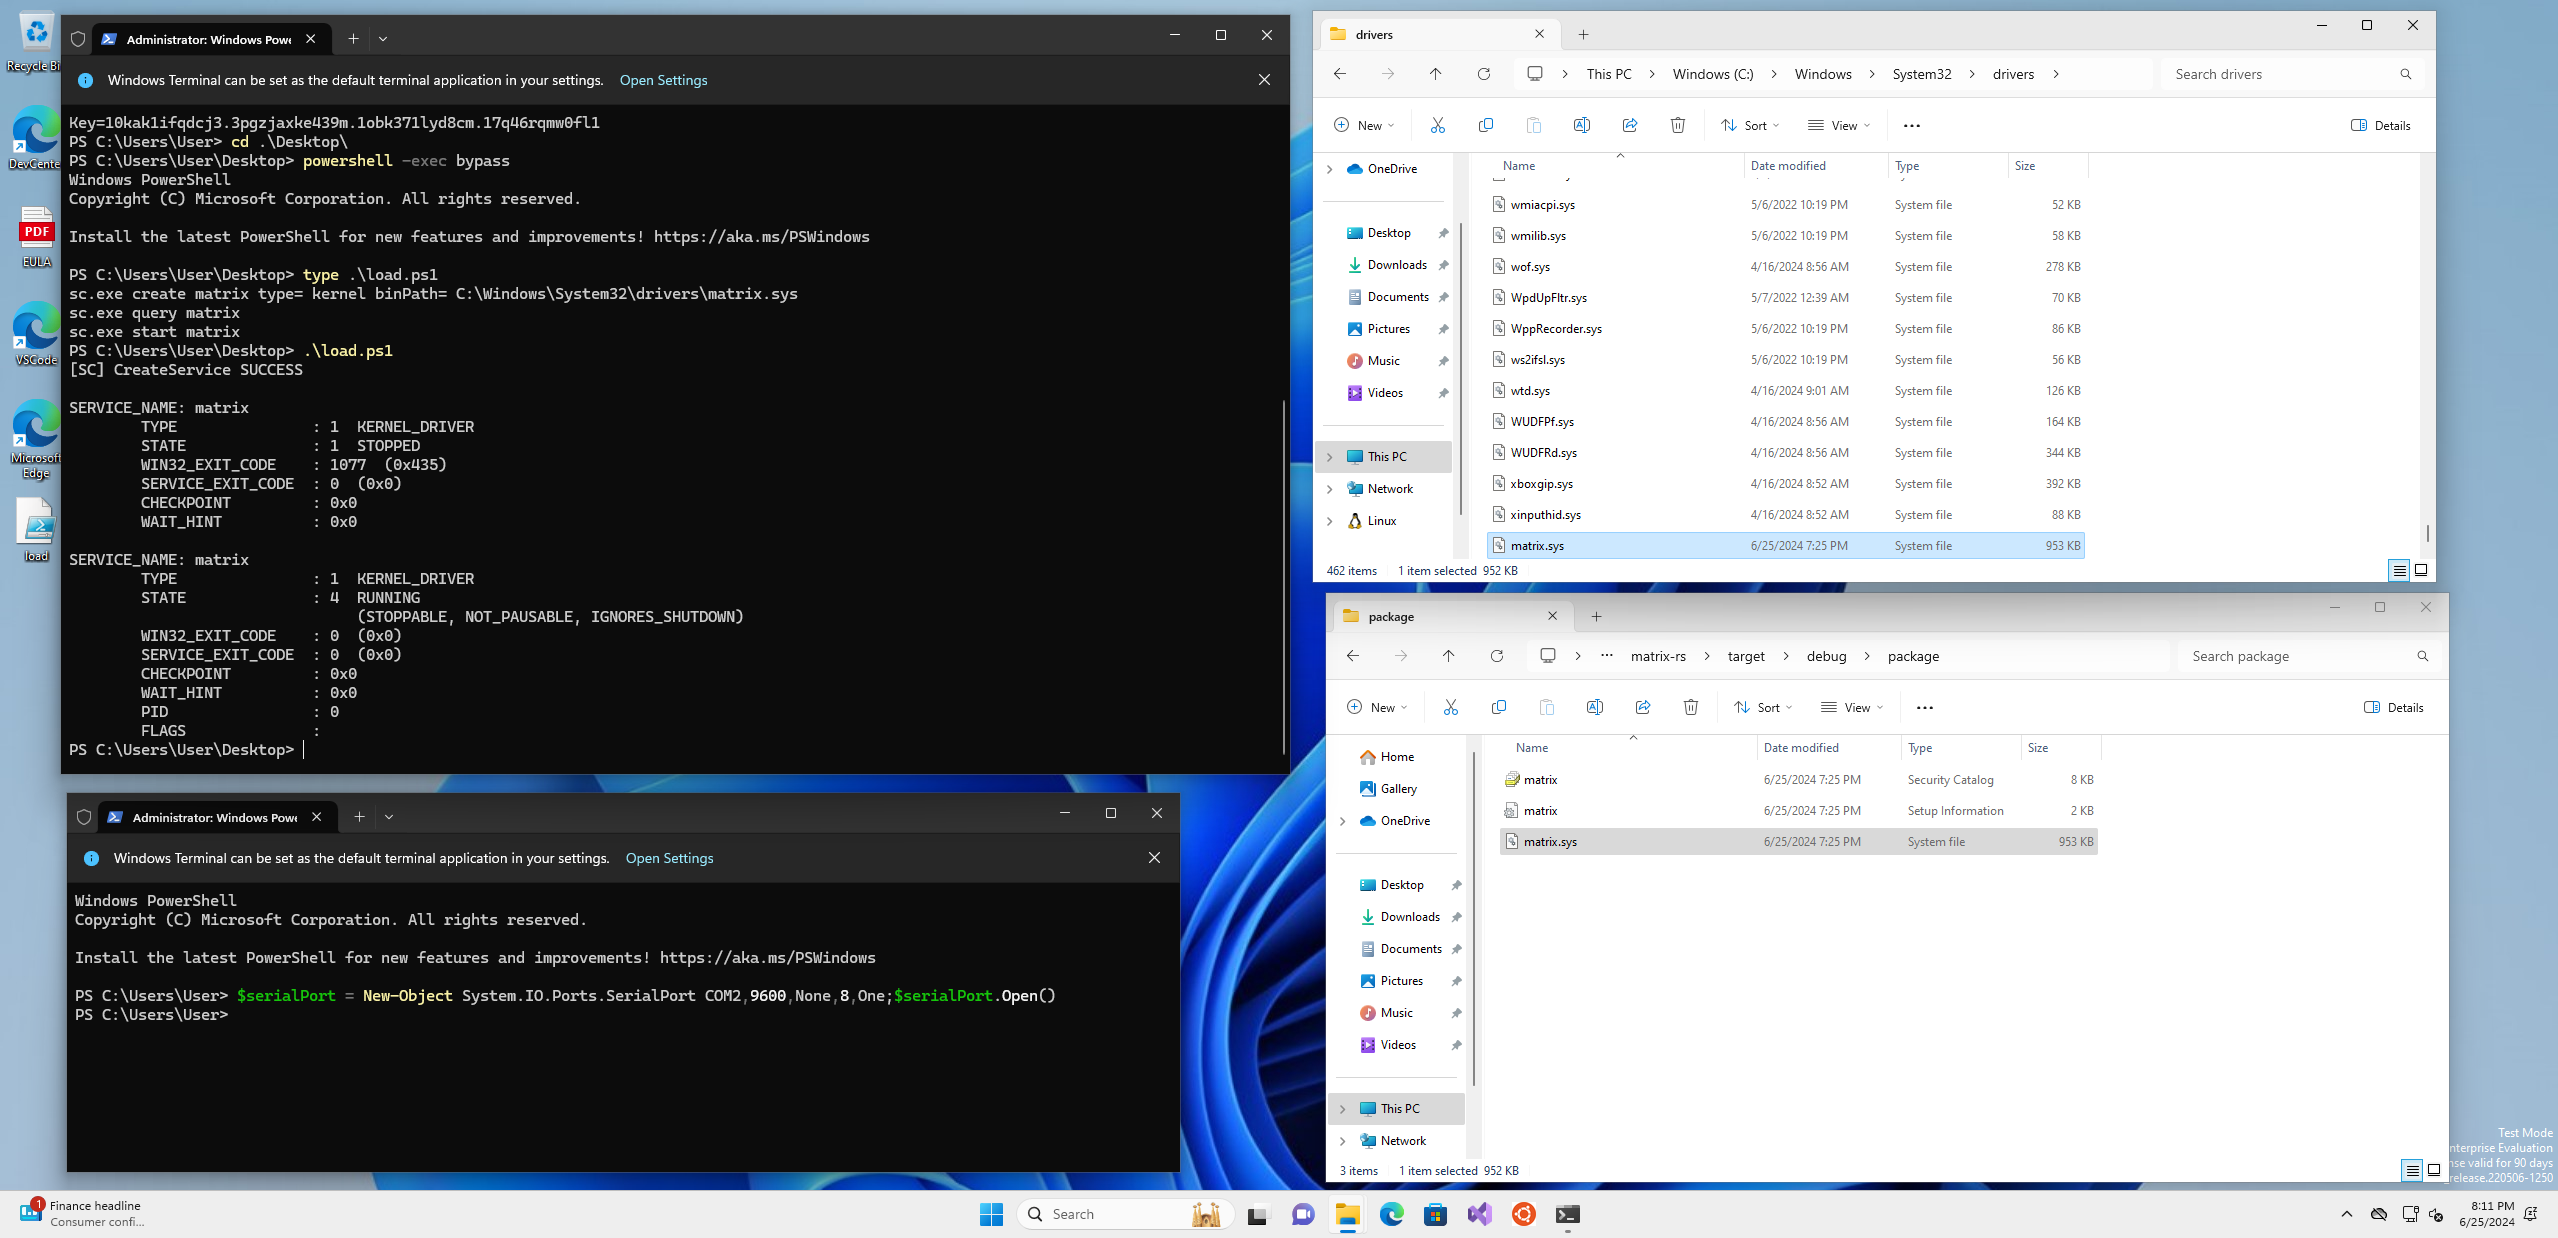
Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)
dynamic-code-analysiseducationids-ips-evasion+3
3594 months ago
dd preview

dd

GitHubricccrd/dd

JIT-based userspace Linux kernel that runs containers natively on Apple Silicon macOS without a VM. Drop-in Docker Engine API replacement with…
binary-analysiscontainer-securitydevsecops+3
2608 days ago
Freeloader preview

Freeloader

GitHubauthrequest/freeloader

Plex Unlocker

binary-analysiscontainer-securitydebuggers+8
953 months ago
distro preview

distro

GitHubremnux/distro

Provides supplemental files and Debian package sources for a specialized Linux distro focused on malware analysis, reverse engineering, and digital…

digital-forensicsdynamic-analysis-sandboxingforensics+5
1171 month ago
MagicArch preview

MagicArch

GitLabmagicbytes/magicarch

MagicArch is a comprehensive post-installation script built with Ansible, designed to transform a basic Arch Linux installation into a fully equipped…
exploit-frameworksforensicsinformation-gathering+8
22 years ago
CVE-2022-24481-analysis preview

CVE-2022-24481-analysis

GitHubuname1able/cve-2022-24481-analysis

Deep-dive analysis of Windows CLFS type confusion (CVE-2022-24481) with root-cause explanation, exploitation flow, kernel gadget details, and working…

binary-exploitationexploitationprivilege-escalation+2
1 month ago
flare-vm preview

flare-vm

GitHubmandiant/flare-vm

A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
binary-analysisdebuggersdigital-forensics+10
9.1k3 months ago
mhf preview

mhf

GitHubstuxctf/mhf

Mobile Helper Framework (mhf) is a tool that automates the process of identifying the framework/technology used to create a mobile application.…
android-securityinformation-gatheringios-security+5
289 months ago
rtl_433 preview

rtl_433

GitHubmerbanan/rtl_433

Program to decode radio transmissions from devices on the ISM bands (and other frequencies)

hardware-iot-securityinformation-gatheringreverse-engineering+1
7.8k6h 55m ago
BinAbsInspector preview

BinAbsInspector

GitHubkeensecuritylab/binabsinspector

Static binary vulnerability scanner using abstract interpretation on Ghidra Pcode. Detects CWE classes like buffer overflows, use-after-free, and…

binary-analysisfuzzingreverse-engineering+2
1.7k2 years ago
Hypervisor-From-Scratch preview

Hypervisor-From-Scratch

GitHubsinakarvandi/hypervisor-from-scratch

Source code of a multiple series of tutorials about the hypervisor. Available at: https://rayanfam.com/tutorials

dynamic-analysis-sandboxingeducationlearning-paths-courses+2
2.7k4 months ago
frida-ios-hook preview

frida-ios-hook

GitHubnoobpk/frida-ios-hook

A tool that helps you easy trace classes, functions, and modify the return values of methods on iOS platform

binary-analysisdynamic-analysis-sandboxingios-security+3
1.2k7 months ago
Previous12…26Next