

LFISuite
 d35m0nd142/lfisuite
Totally Automatic LFI Exploiter (+ Reverse Shell) and Scanner
exploitationpayload-generationpenetration-testing+3
d35m0nd142/lfisuiteTotally Automatic LFI Exploiter (+ Reverse Shell) and Scanner
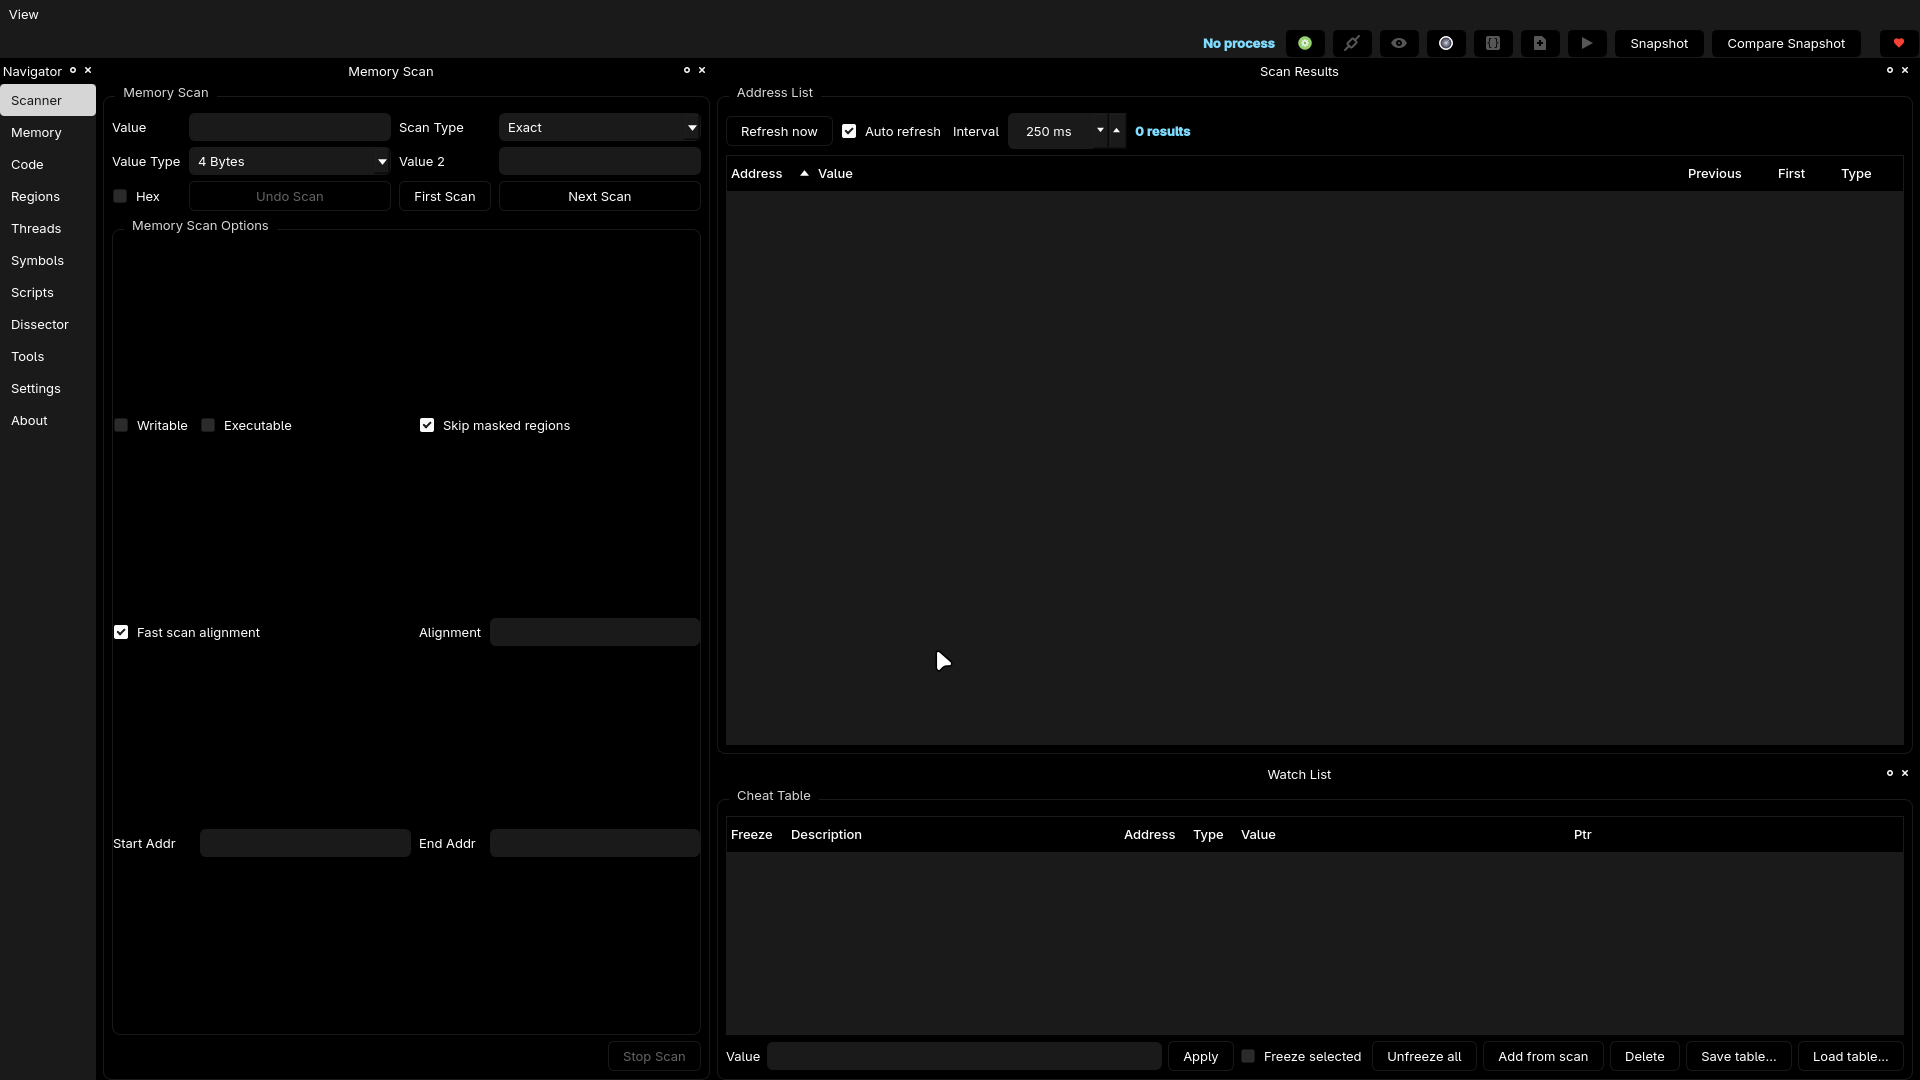 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 enaqx/awesome-pentest
A collection of awesome penetration testing resources and tools
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…
 0xdea/frida-scripts
A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 microsoft/windbg-samples
Sample extensions, scripts, and API uses for WinDbg.
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 swdunlop/andbug
Scriptable debugger for Android Dalvik VM using JDWP/DDM interfaces to hook methods, inspect process state, and modify runtime behavior without…
 tothi/pwn-hisilicon-dvr
Proof-of-concept exploit and vulnerability disclosure for HiSilicon hi3520d DVR/NVR devices. Demonstrates RCE via web interface, backdoor…
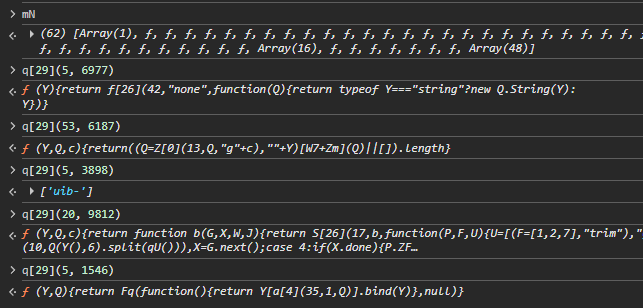 elyelysiox/recaptcha
Documentation and reverse engineering of reCAPTCHA
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 reverseclabs/gwtmap
Maps attack surface of GWT applications by extracting obfuscated RPC endpoints and generating serialized request payloads for security testing.
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 nccgroup/dibf
Windows NT ioctl bruteforcer and modular fuzzer