
Startup-SBOM
 morpheuslord/startup-sbom
A tool to reverse engineer and inspect the RPM and APT databases to list all the packages along with executables, service, versions and CVE.
cloud-securityconfiguration-auditingcontainer-security+4
19
morpheuslord/startup-sbomA tool to reverse engineer and inspect the RPM and APT databases to list all the packages along with executables, service, versions and CVE.
 nowsecure/fsmon
Filesystem monitor tool for Linux/Android iOS/macOS
 0x48piraj/incarcero
Incarcero is a tool that creates Virtual Machines (VMs) preconfigured with malware analysis tools and security settings tailored for malware analysis…
 dzmitry-savitski/android-pentest-tool
Android penetration testing tool for Kali linux
 gjduck/e9patch
A powerful static binary rewriting tool
 paolomonti42/salt
SALT - SLUB ALlocator Tracer for the Linux kernel
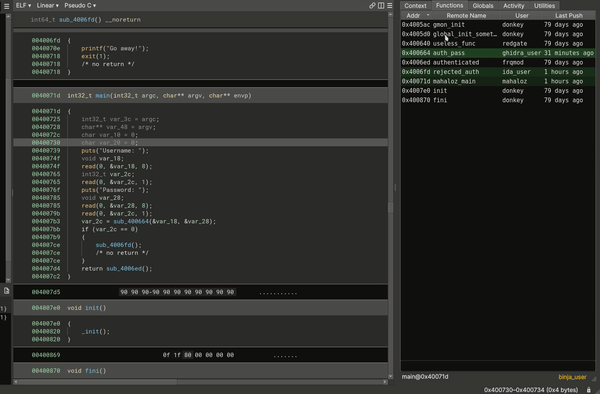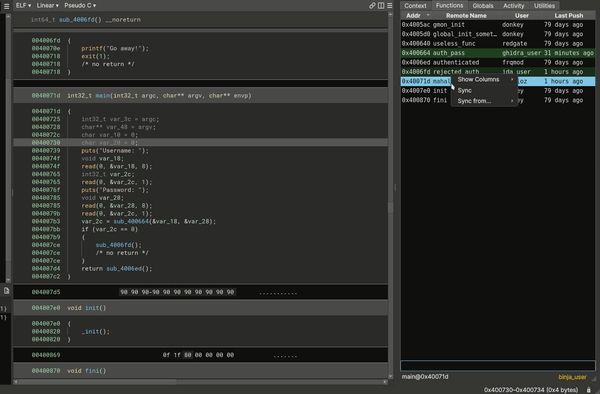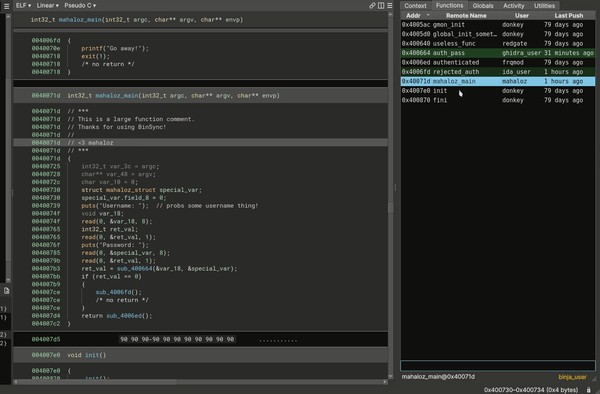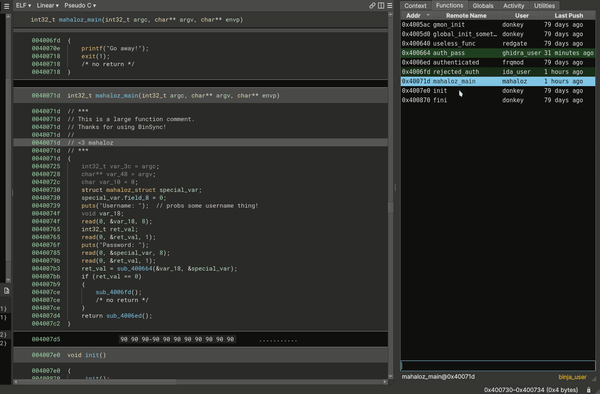 binsync/binsync
A reversing plugin for cross-decompiler collaboration, built on git.
 hasherezade/pe-sieve
Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 lautarovculic/frida-ipa-extract
Robust Frida-based tool to dump decrypted iOS apps as .ipa from a jailbroken device supports App Store, sideloaded and system.
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
 mandiant/flare-qdb
Command-line and Python debugger for instrumenting and modifying native software behavior on Windows and Linux.
 steven-michaud/hookcase
Tool for reverse engineering macOS/OS X
 forentfraps/pe-signgen
Universal signature generation for any system function from all Windows Builds using Winbindex
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, watchOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS…
 marin-m/vmlinux-to-elf
A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices