

elfxtract
 m0n1x90/elfxtract
Automated ELF binary analysis tool for CTF/PWN challenges. Extracts security mitigations, ROP gadgets, PLT/GOT tables, and decompiles ASM to C using…
binary-analysiseducationexploitation+2
73
m0n1x90/elfxtractAutomated ELF binary analysis tool for CTF/PWN challenges. Extracts security mitigations, ROP gadgets, PLT/GOT tables, and decompiles ASM to C using…
 cmu-sei/pharos
Automated static analysis tools for binary programs
 mandiant/flare-emu
Scriptable binary emulation framework integrating IDA Pro/Radare2 with Unicorn engine for automated malware analysis, string decryption, and code…
 byteray-ai/drift-corpus
Curated repository of Windows kernel patch diffs with automated vulnerability analysis, exploit primitive mapping, and debugging aids for security…
 revng/revng-c
Core binary-lifting library that translates executable code to LLVM IR and reconstructs C-like source for reverse engineering and automated binary…
 mrexodia/titanhide
Windows kernel driver that hooks Nt* SSDT functions to hide debuggers and processes from anti-debug checks, with an x64dbg plugin for stealth…
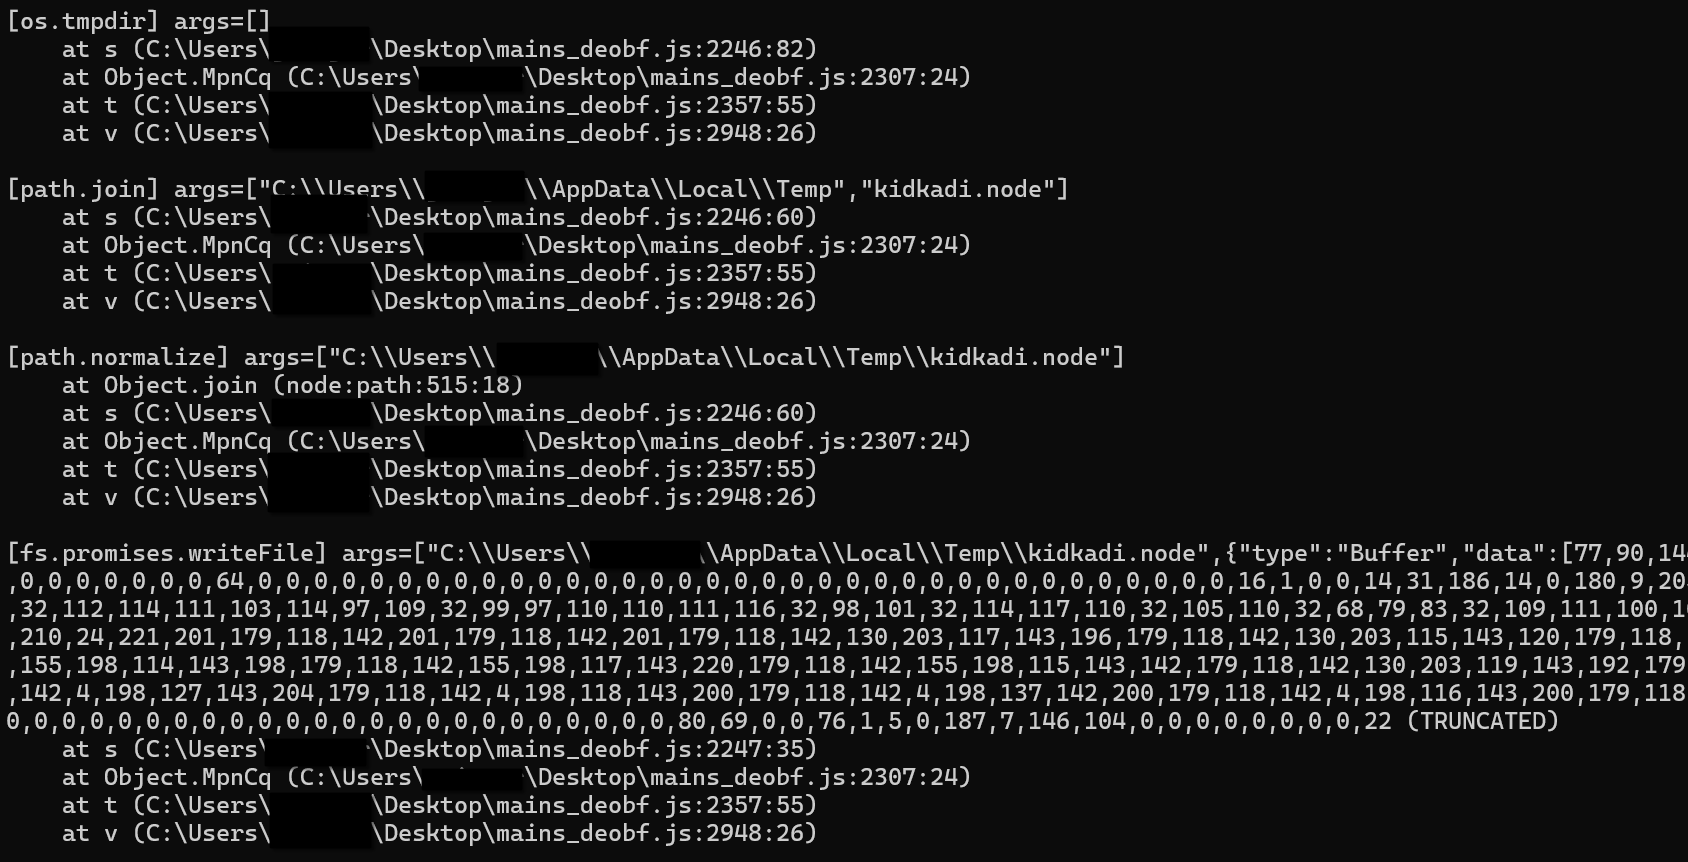 checkpointsw/nodejs-tracer
Runtime tracer for Node.js malware analysis that hooks core modules, logs calls, spoofs anti-analysis checks, and captures file writes and HTTP…
 matheuzsecurity/nullsection
ELF anti-reversing tool that overwrites section headers with nullbytes to prevent static analysis by disassemblers and debuggers, rendering functions…
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
 manjustice/datadome-vm-internals
Analysis of DataDome's custom obfuscated VM and bytecode format, revealing string encryption, S-box ciphers, and browser fingerprinting signals for…
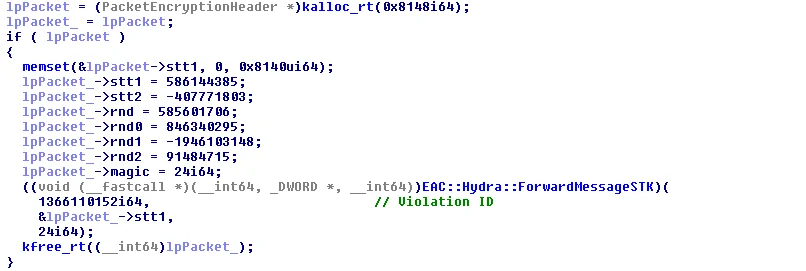 gmh5225/eac-kernel-packet-fucker
Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…
 elyelysiox/recaptcha
Documentation and reverse engineering of reCAPTCHA
 burrowers/garble
Obfuscates Go builds by wrapping the Go toolchain, replacing identifiers, package paths, and position data with hashes and stripping debug and build…
 justasmasiulis/lazy_importer
library for importing functions from dlls in a hidden, reverse engineer unfriendly way
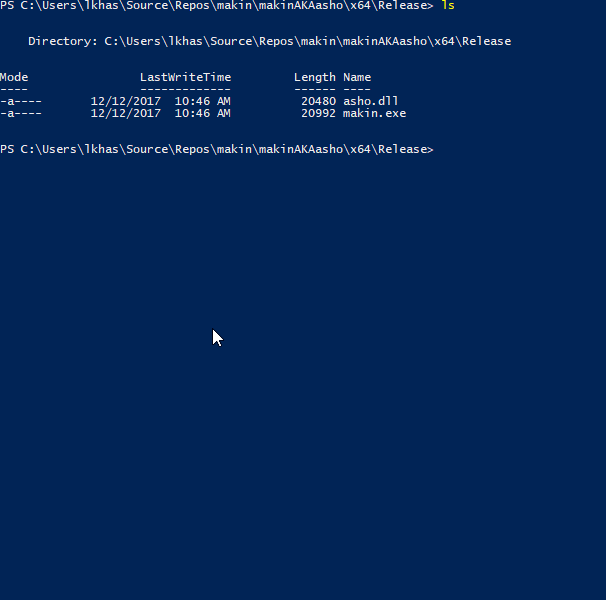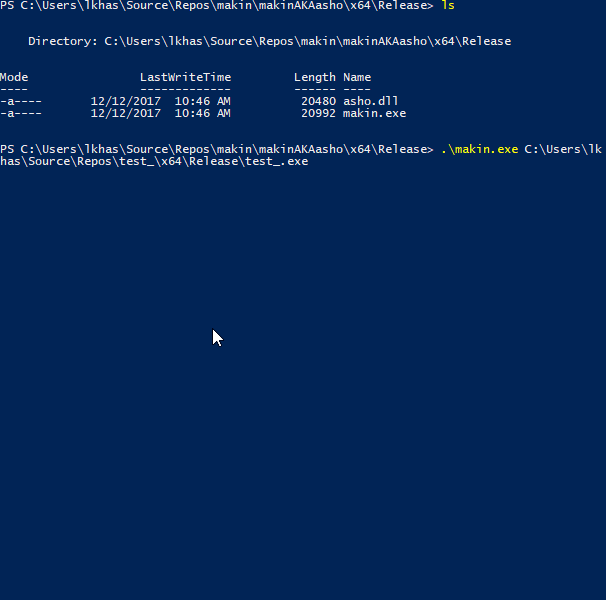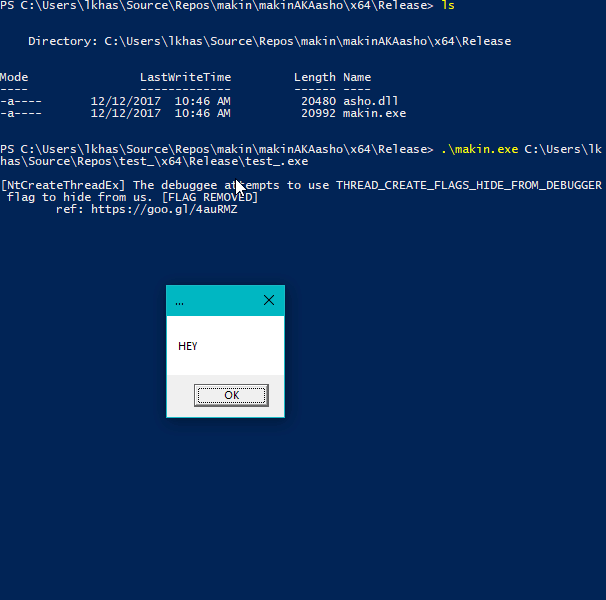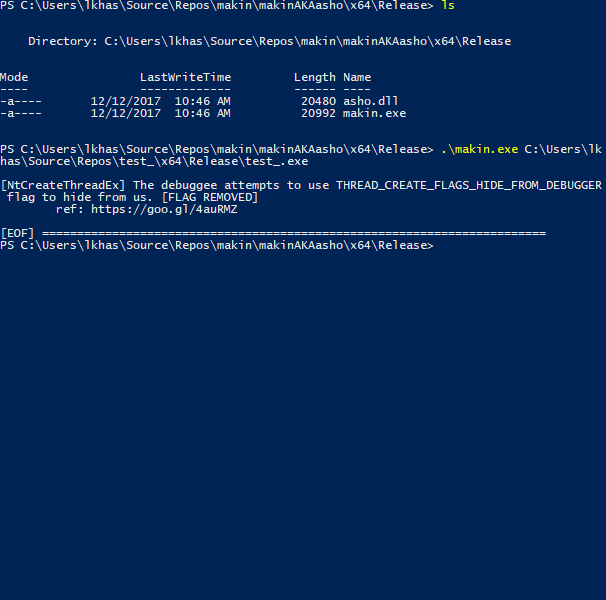 secrary/makin
makin - reveal anti-debugging and anti-VM tricks [This project is not maintained anymore]
 leochen-coremind/vmpacker
ARM64 ELF Virtual Machine Protection System
 komimoe/arkari
Yet another llvm based obfuscator based on goron.
 notrequiem/antidbg
A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering