
pefile
 erocarrera/pefile
pefile is a Python module to read and work with PE (Portable Executable) files
binary-analysisforensicsmalware-analysis+3
erocarrera/pefilepefile is a Python module to read and work with PE (Portable Executable) files
 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
 rampagex/firmware-mod-kit
Automatically exported from code.google.com/p/firmware-mod-kit
 pstirparo/machofile
machofile is a module to parse Mach-O binary files
 fuzzinglabs/octopus
Security Analysis tool for WebAssembly module (wasm) and Blockchain Smart Contracts (BTC/ETH/NEO/EOS)
 theopolis/uefi-firmware-parser
Parse BIOS/Intel ME/UEFI firmware related structures: Volumes, FileSystems, Files, etc
 ac-pm/inspeckage
Android Package Inspector - dynamic analysis with api hooks, start unexported activities and more. (Xposed Module)
 mattifestation/powershellarsenal
A PowerShell Module Dedicated to Reverse Engineering
 dsecurity/efiseek
Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…
 adelapie/ghidra-evm
Ghidra module for disassembling, decompiling, and analyzing Ethereum smart contract bytecode. Detects insecure instructions, extracts hidden methods,…
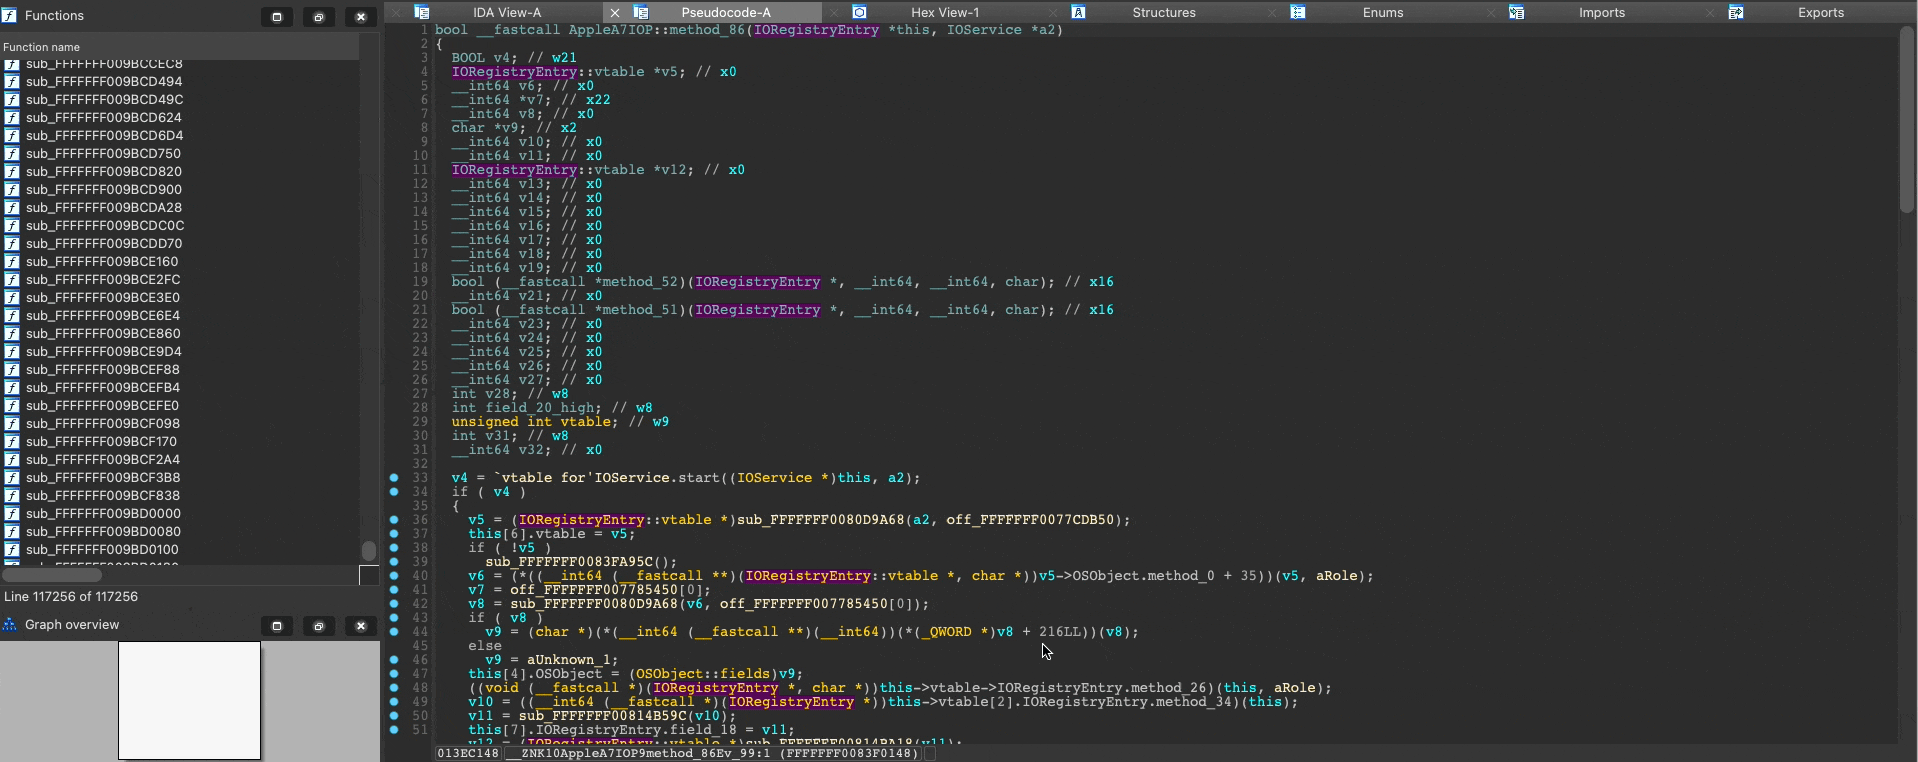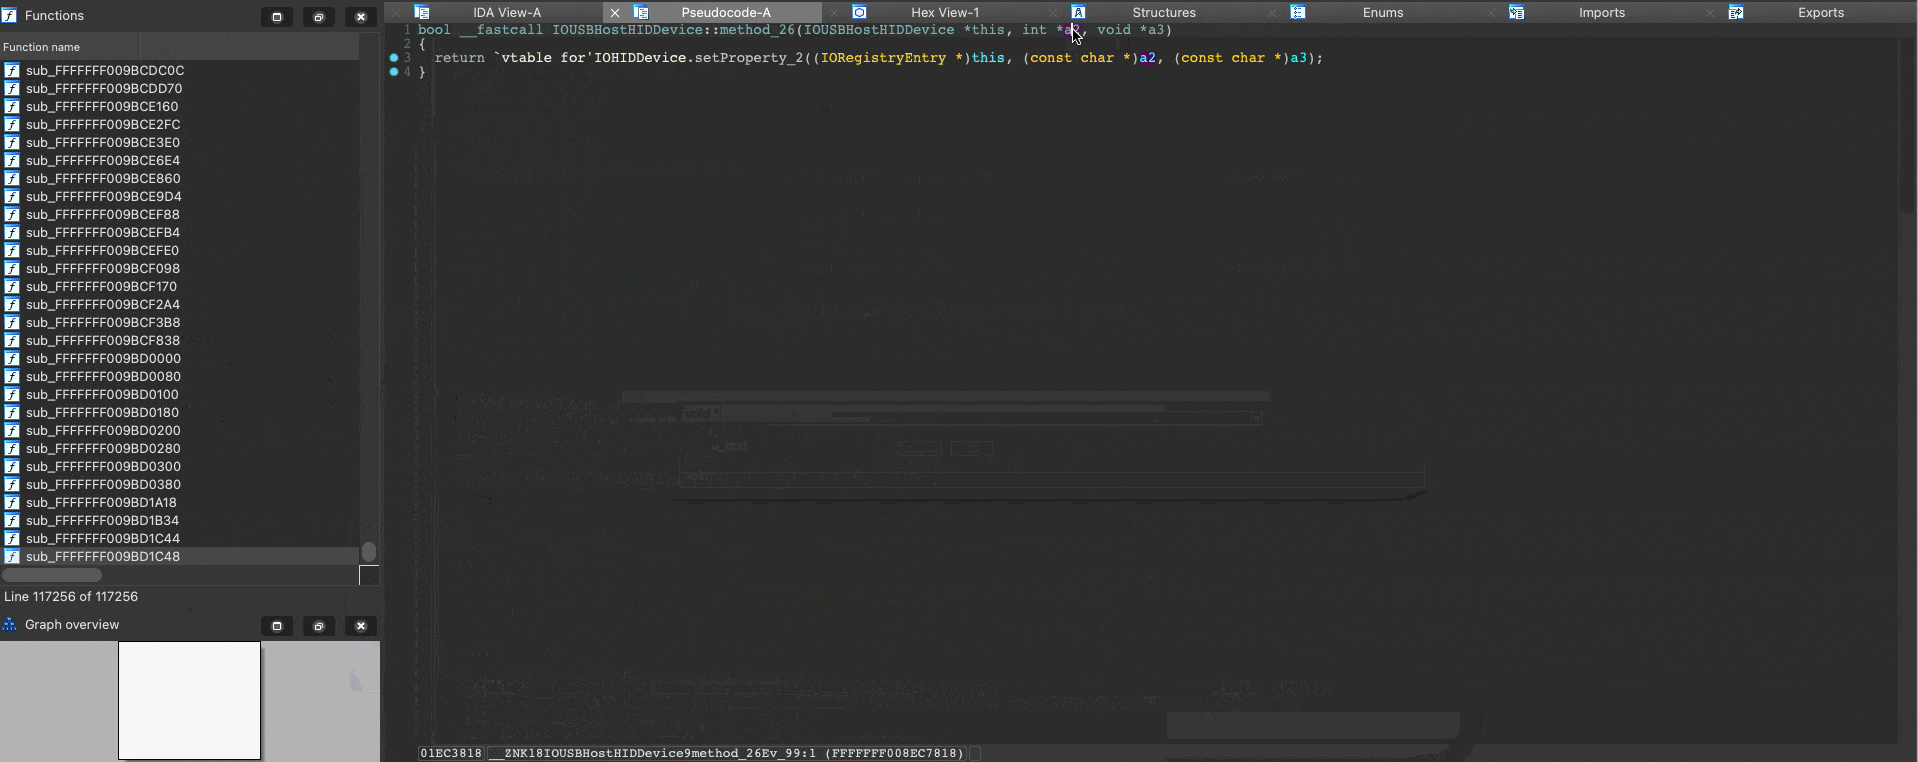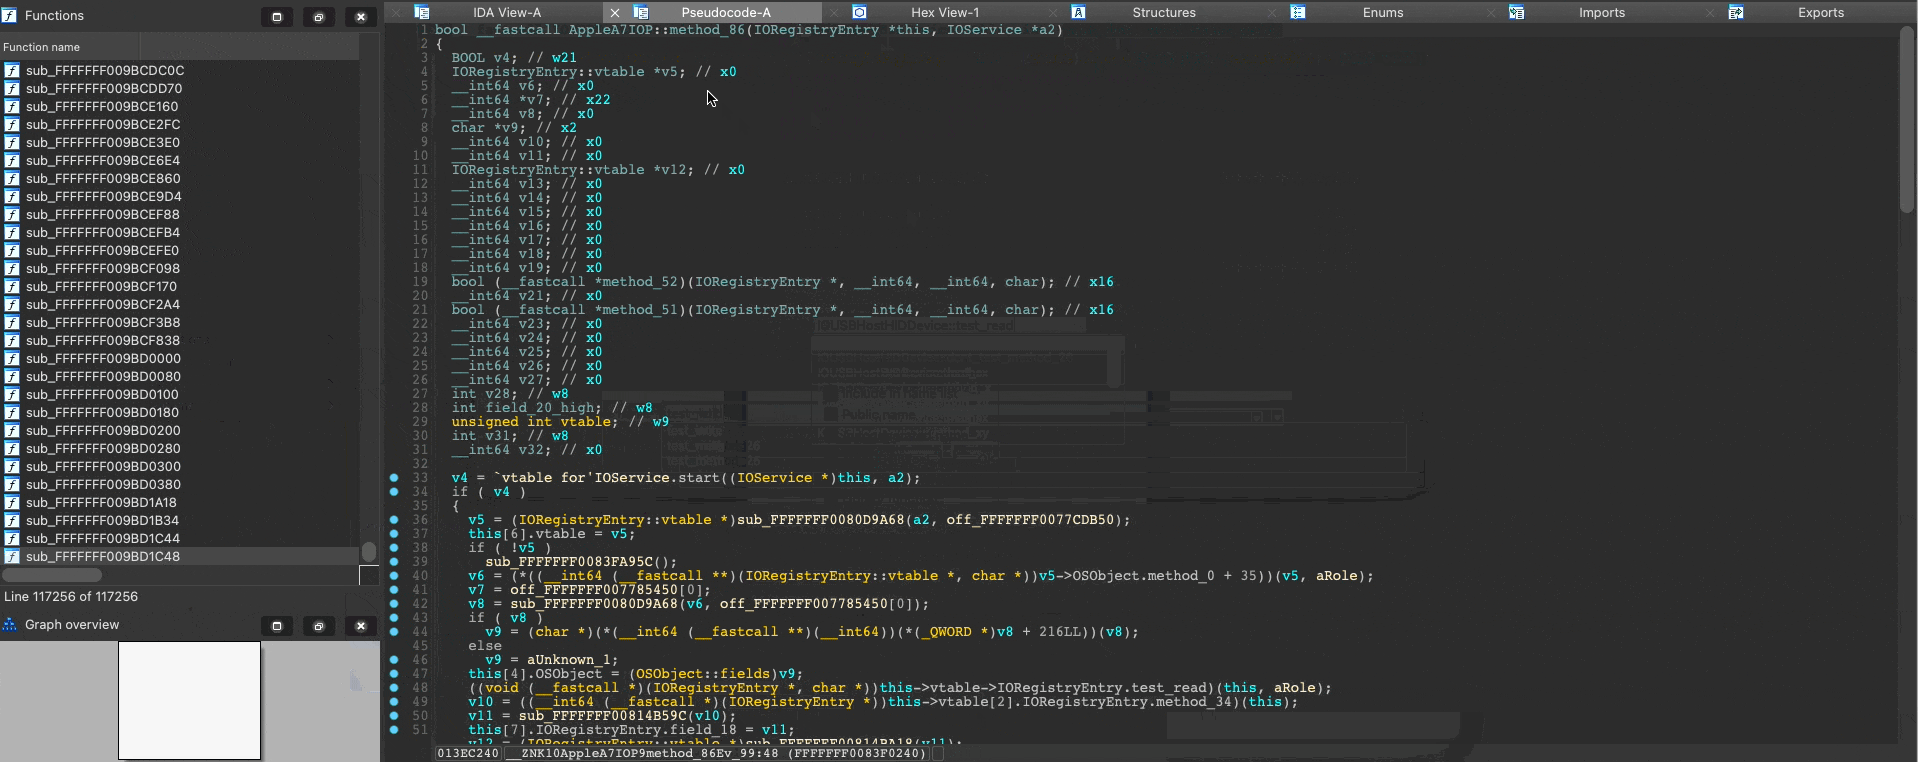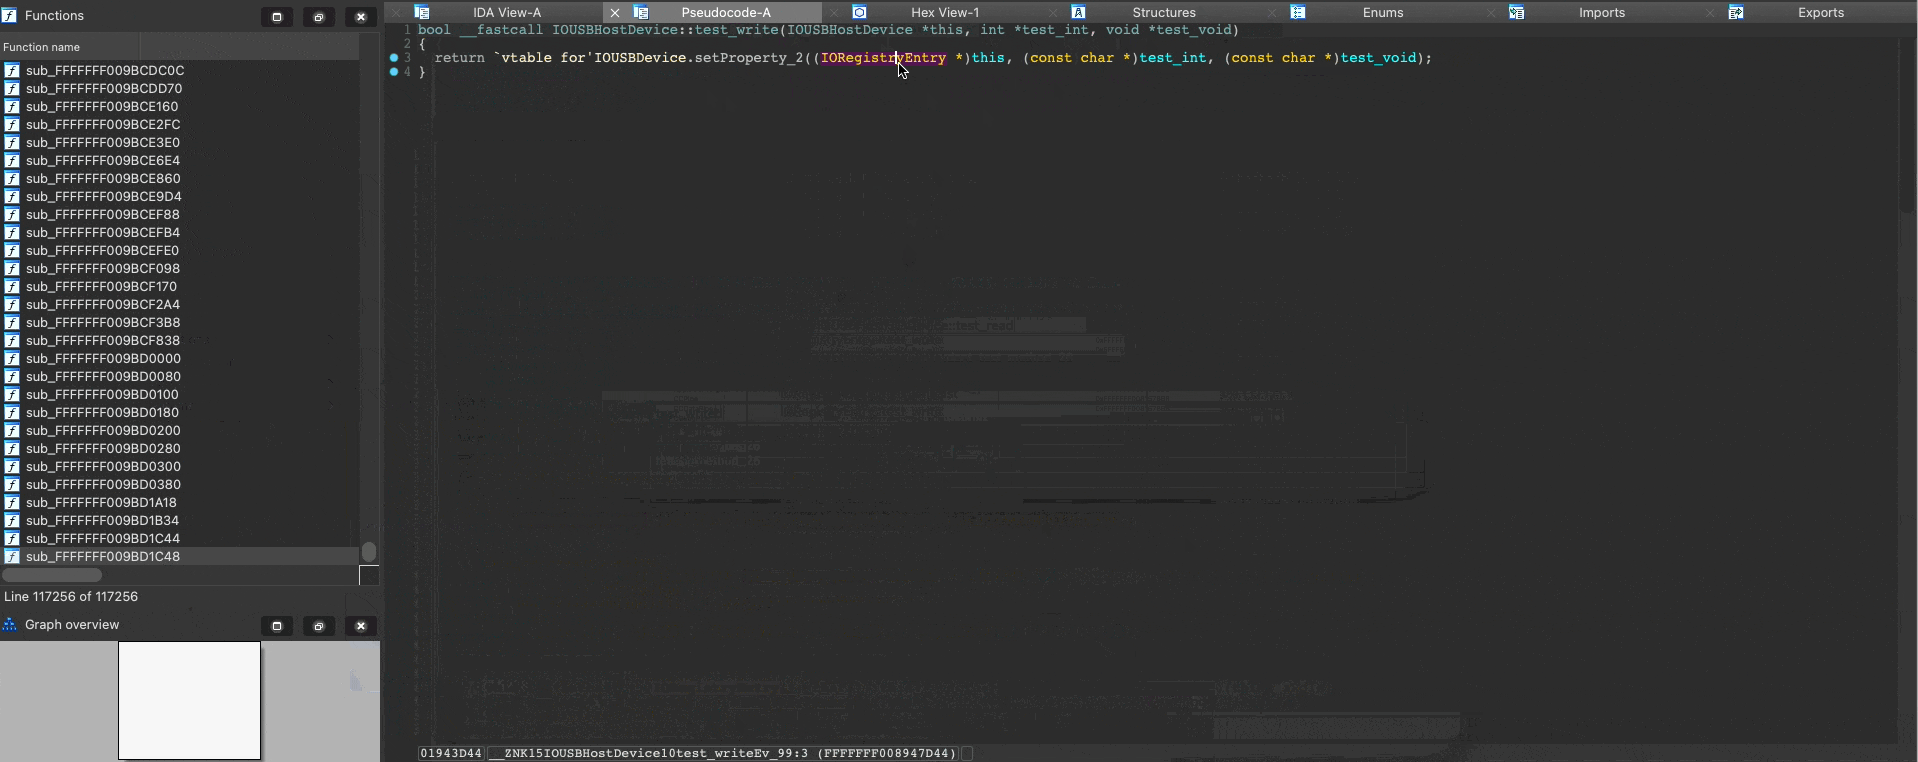 cellebrite-labs/ida_kcpp
An IDAPython module for enhancing c++ support on top of ida_kernelcache
 dump-guy/get-pdinvokeimports
PowerShell module for automatic detection of P/Invoke, Dynamic P/Invoke, and D/Invoke in .NET assemblies. Reveals unmanaged API calls, MDTokens, and…
 theshinigami/mafrida
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
 nccgroup/ghidra-nanomips
nanoMIPS module for Ghidra
 eversinc33/drvtrace
WinDbg plugin to trace module transitions from a debugged driver.
 vichhka-git/magisk-renef
Magisk module that auto-packages renef_server (dynamic instrumentation for Android)
 ymsniper/umbra
External read-only game overlay for Linux. Derived offsets, composed skeletons, optional kernel module for ptrace-independent memory reads and…
 kaandemir993/advanced-loader-reverse-engineering
"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…