
malware-samples
 fabrimagic72/malware-samples
A collection of malware samples caught by several honeypots i manage
binary-analysiscurated-resourcesdigital-forensics+4
1.9k
fabrimagic72/malware-samplesA collection of malware samples caught by several honeypots i manage
 taielab/awesome-hacking-lists
A curated collection of top-tier penetration testing tools and productivity utilities across multiple domains. Join us to explore, contribute, and…
 furrtek/precir
Open-source hardware and software toolkit for reverse-engineering and communicating with infrared-based electronic shelf labels. Includes custom…
 blacksnufkin/rusty-playground
Some Rust program I wrote while learning Malware Development
 farukalpay/neurocore
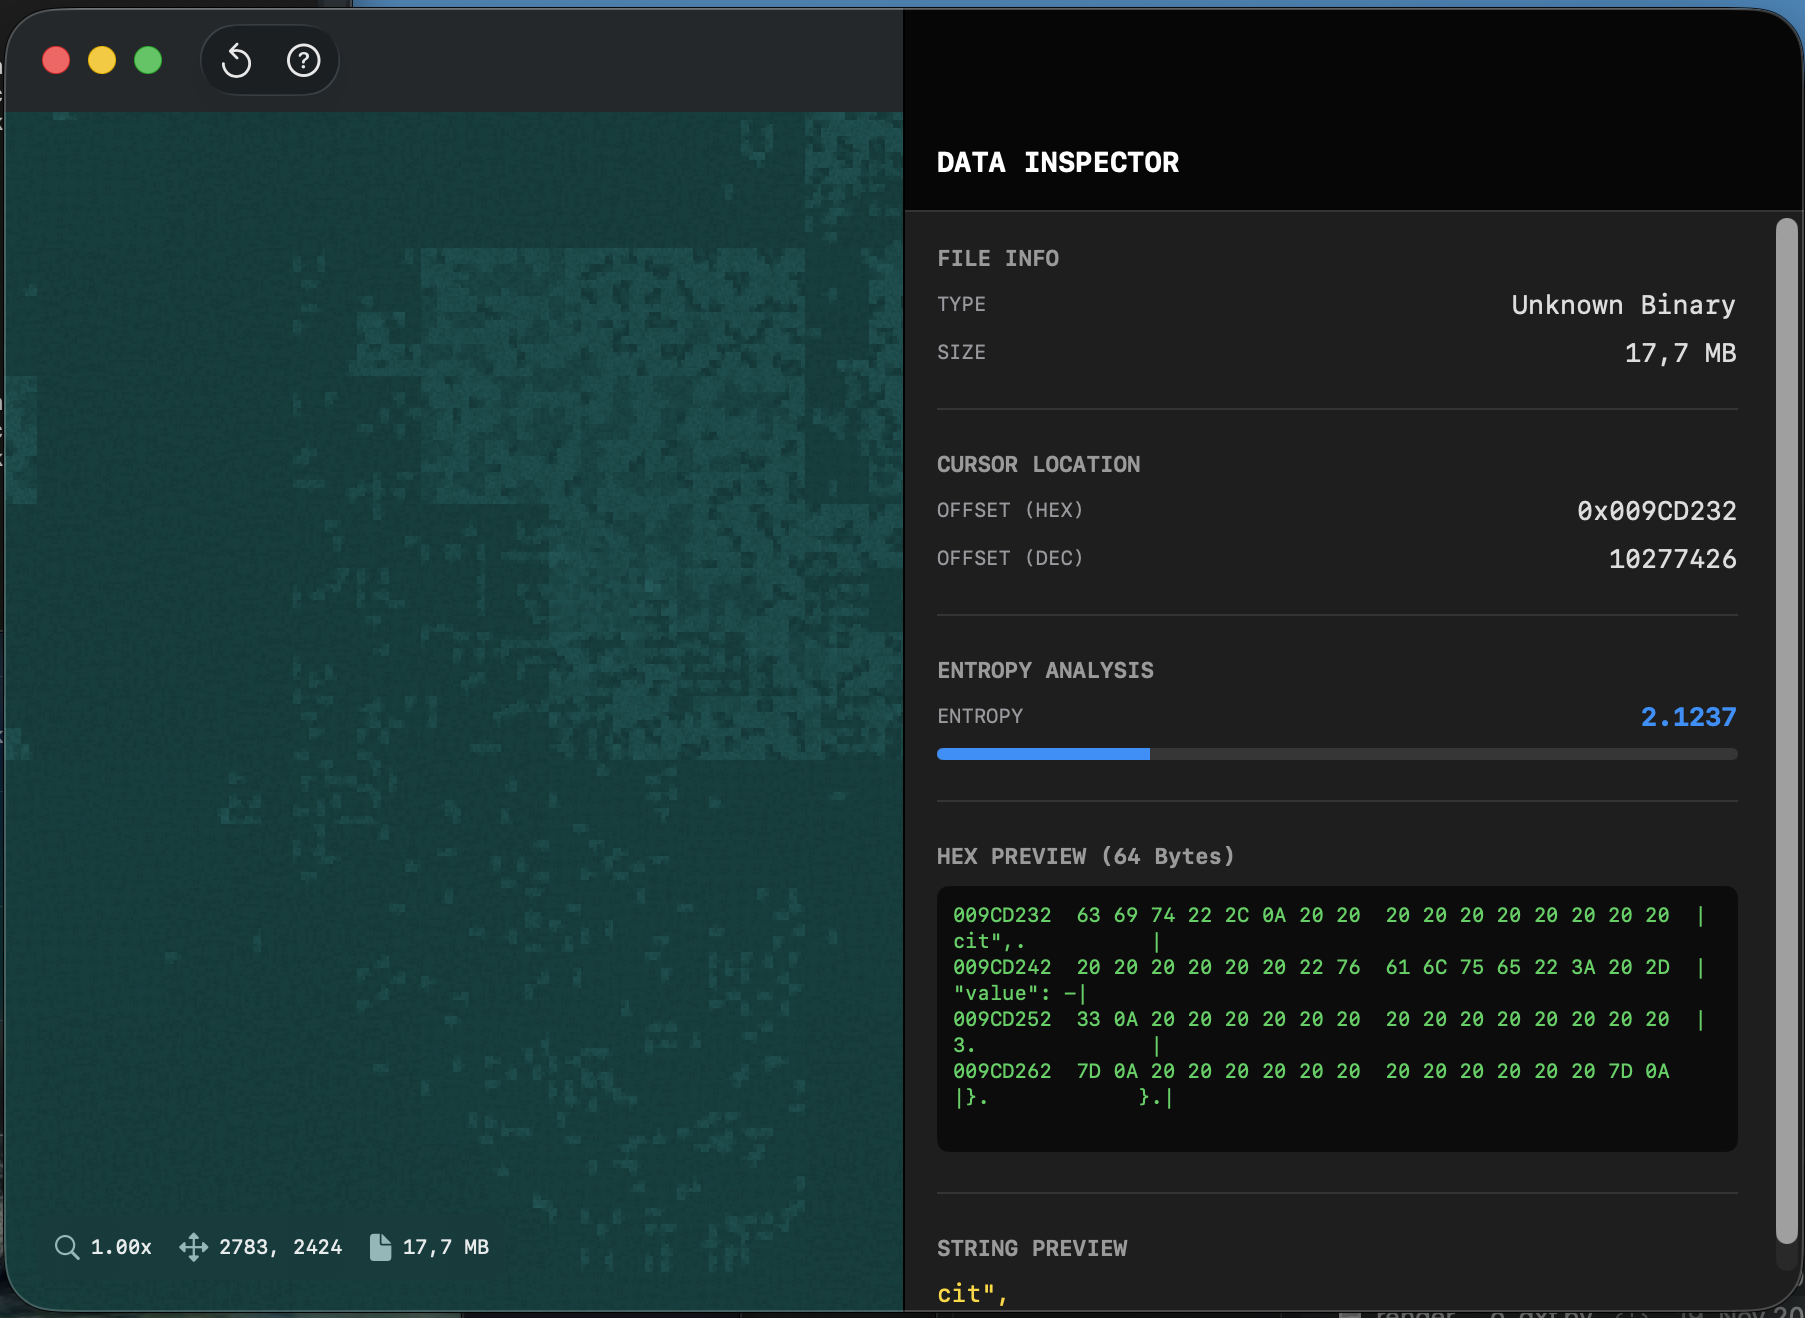
NeuroCore is a native macOS application that visualizes the internal structure of binary files using a Hilbert Curve mapping and Shannon Entropy…

 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
 seekbytes/ipa
GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 secrary/andromeda
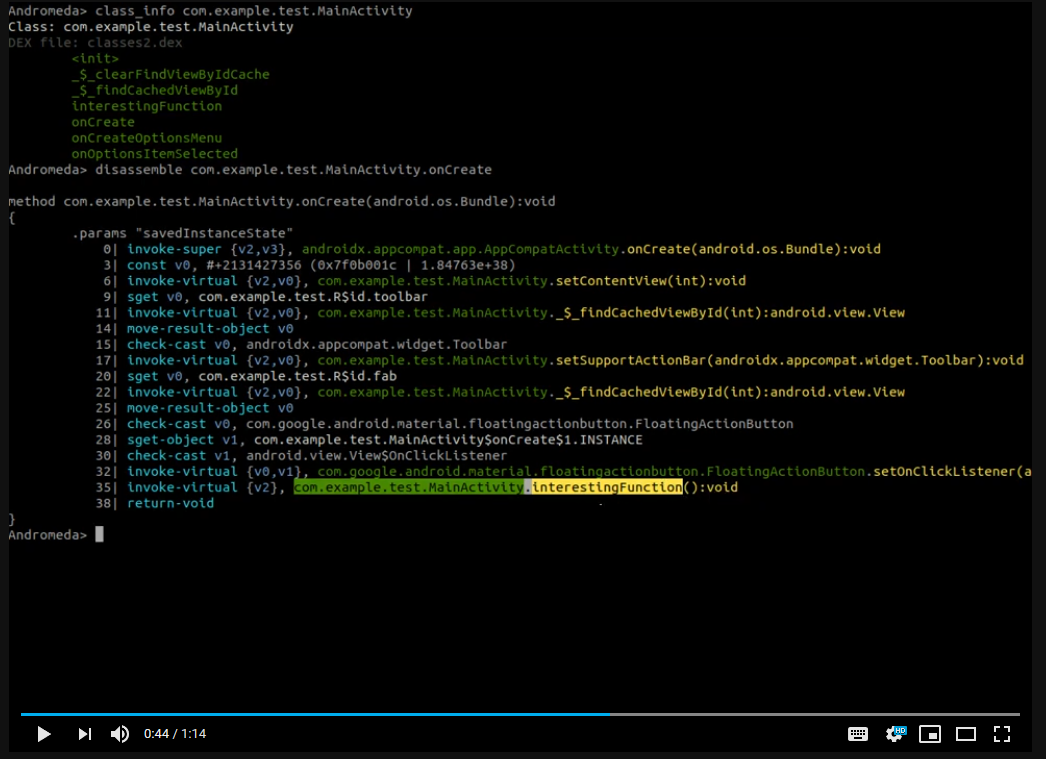
C/C++ interactive reverse engineering tool for Android applications, enabling fast static analysis and binary inspection of APK files.
 mandiant/flashmingo
Automatic analysis of SWF files based on some heuristics. Extensible via plugins.
 jjyg/metasm
This is the main repository for metasm, a free assembler / disassembler / compiler written in ruby
 adamkadaban/ctfs
CTF Cheat Sheet + Writeups / Files for some of the Security CTFs that I've done
 nygard/class-dump
Generate Objective-C headers from Mach-O files.
 pealeap/cve-2026-21045_and_cve-2026-21048
Generates crafted TIFF/DNG files to trigger out-of-bounds writes in Samsung's libimagecodec.quram.so, including binary analysis and reproduction…
 sandi-go/cve-2018-12798
Proof-of-concept exploit for CVE-2018-12798, a heap overflow in Adobe Acrobat Reader that enables remote code execution via malicious PDF files.
 dsecurity/efiseek
Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…
 ejfkdev/ddc
DEX → Java decompiler in Rust — fast, progressive analysis, bilingual CLI