
ThreatResearch
Python config extractors for malware families including PlugX, Remcos, templateX, and RedLine Stealer, supporting C2 configuration extraction for…

Python config extractors for malware families including PlugX, Remcos, templateX, and RedLine Stealer, supporting C2 configuration extraction for…

Datajack Proxy allows you to intercept TLS traffic in native x86 applications across platforms

Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…

Python parser for extracting CobaltStrike Beacon configurations from PE files, memory dumps, and C2 URLs using heuristic XOR decryption and…

Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…

Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…

"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…

In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…

A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…

"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…

Analysis of malware found on a server compromised via CVE-2025-55182, including obfuscated dropper, C2 communication, persistence mechanisms, and…

The graph functionality of DeimosC2 v1.1.0-Beta is vulnerable to Stored Cross-Site Scripting (XSS), allowing the theft of session cookie and…

Reverse engineering write-up of Python shellcode that APC-injects into AnyDesk, exfiltrates to a C2 over HTTPS with AES/RSA, and persists via…

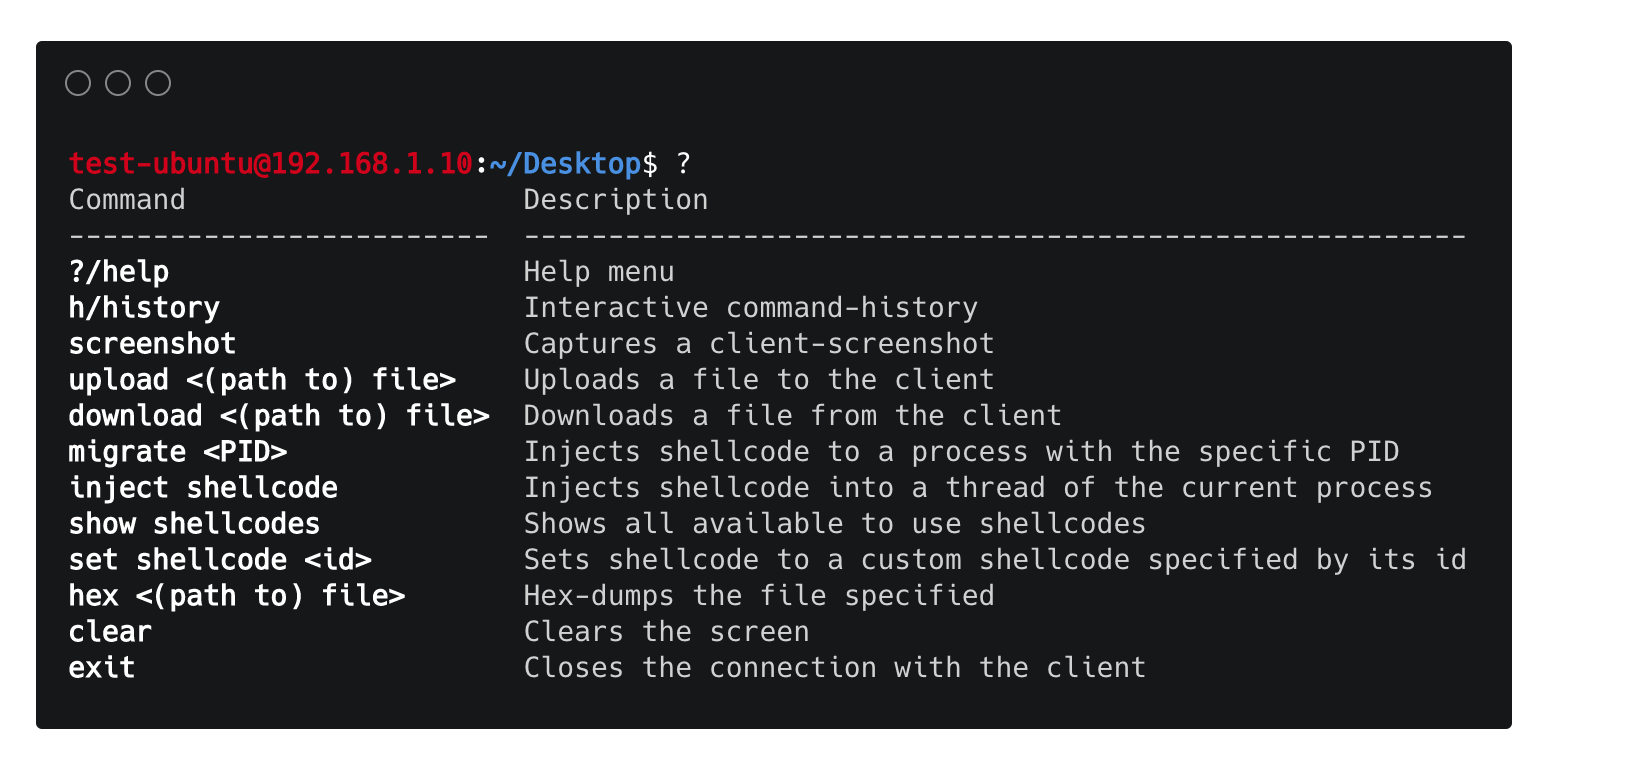
HRShell is an HTTPS/HTTP reverse shell built with flask. It is an advanced C2 server with many features & capabilities.

Cobalt Strike C2 Reverse proxy that fends off Blue Teams, AVs, EDRs, scanners through packet inspection and malleable profile correlation

Collection of scripts for malware analysis, deobfuscation, and configuration extraction. Supports static analysis, unpacking, shellcode conversion,…