
MaFrida
 theshinigami/mafrida
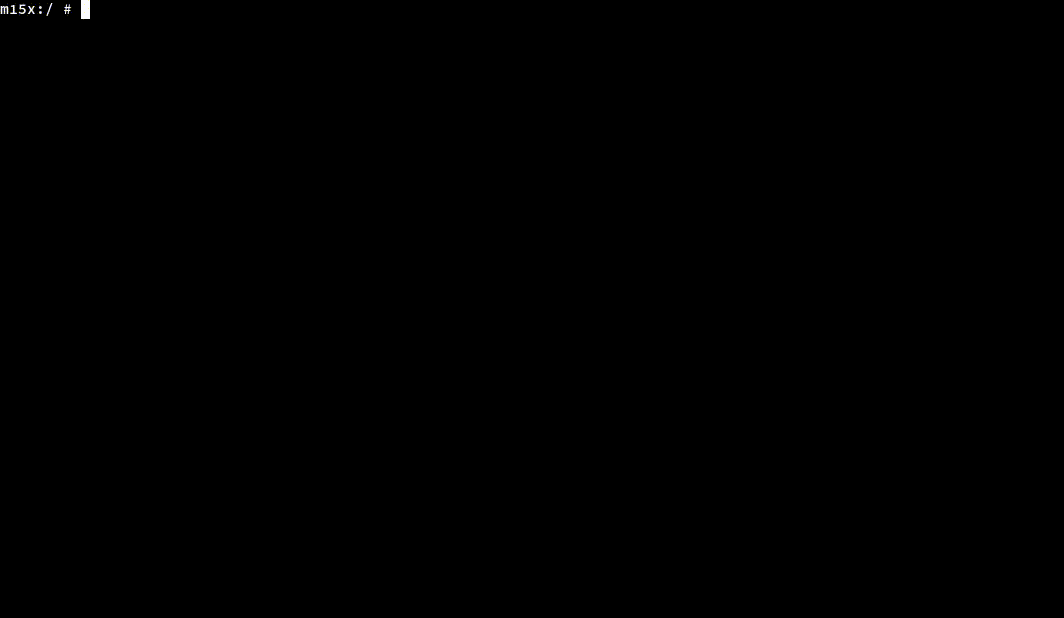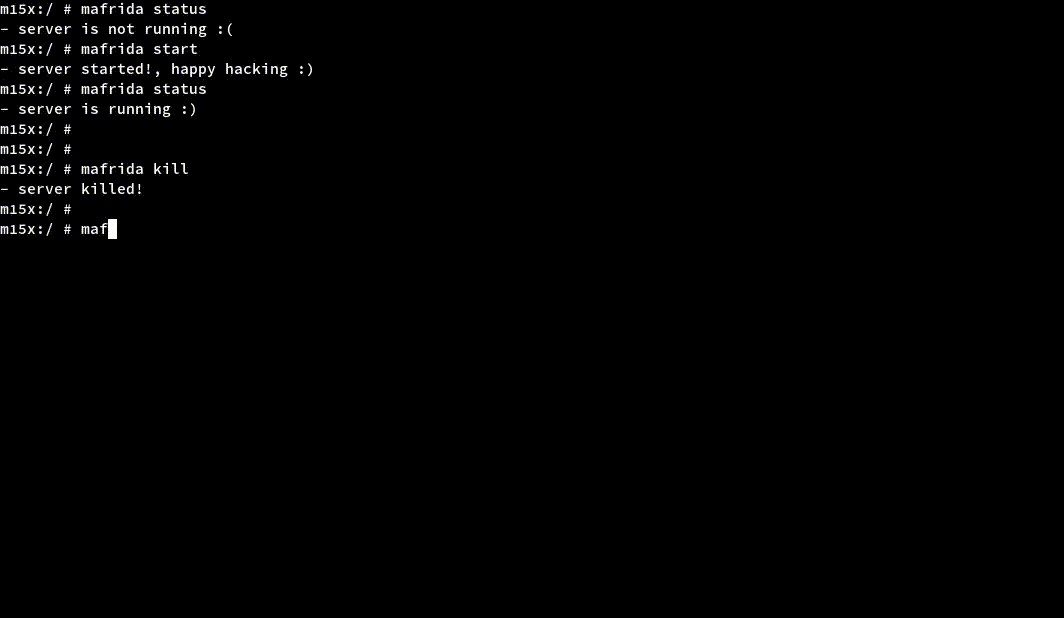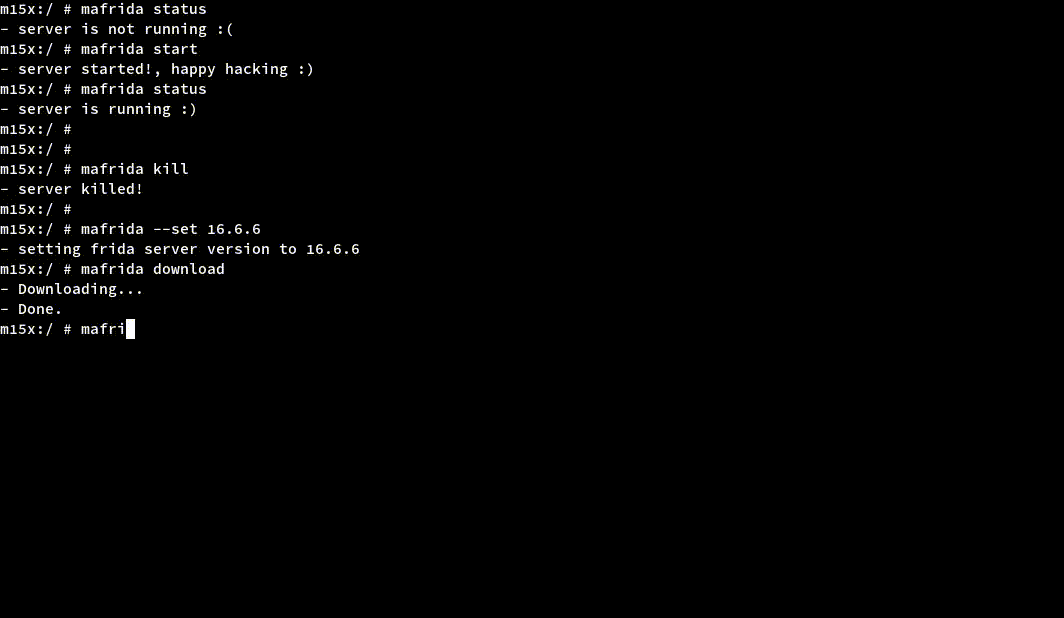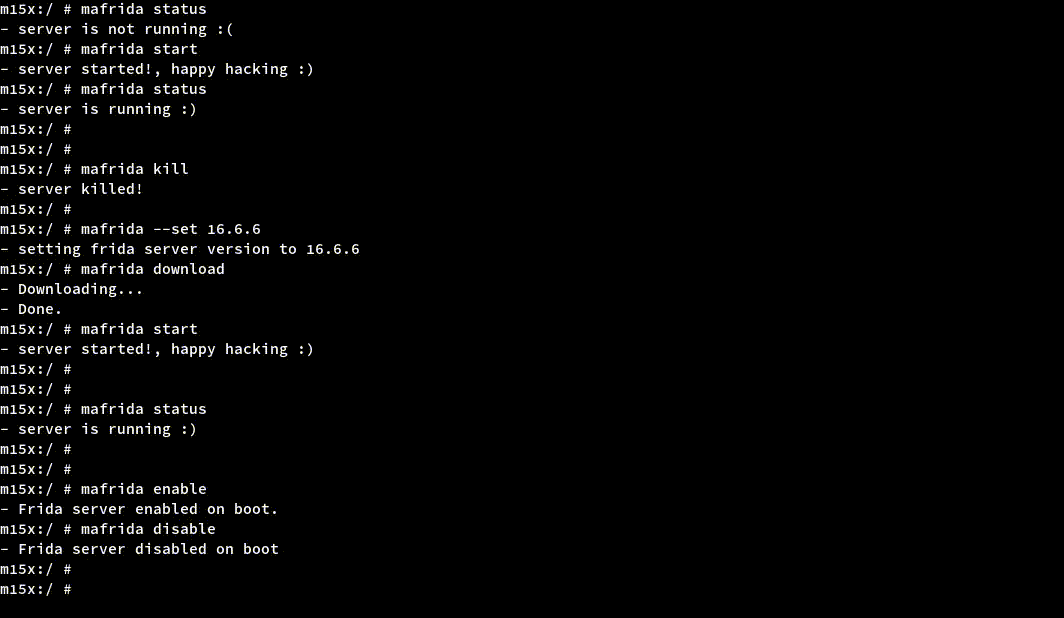
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
android-securitydynamic-analysis-sandboxingdynamic-code-analysis+5
40
theshinigami/mafridaA Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
 erocarrera/pefile
pefile is a Python module to read and work with PE (Portable Executable) files
 ac-pm/inspeckage
Android Package Inspector - dynamic analysis with api hooks, start unexported activities and more. (Xposed Module)
 mattifestation/powershellarsenal
A PowerShell Module Dedicated to Reverse Engineering
 dsecurity/efiseek
Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…
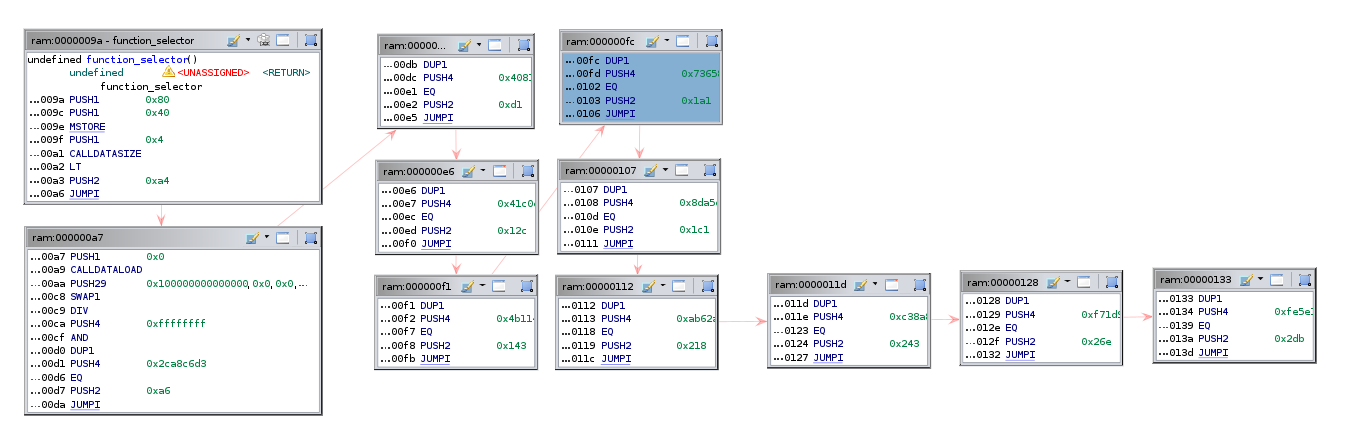 adelapie/ghidra-evm
Ghidra module for disassembling, decompiling, and analyzing Ethereum smart contract bytecode. Detects insecure instructions, extracts hidden methods,…
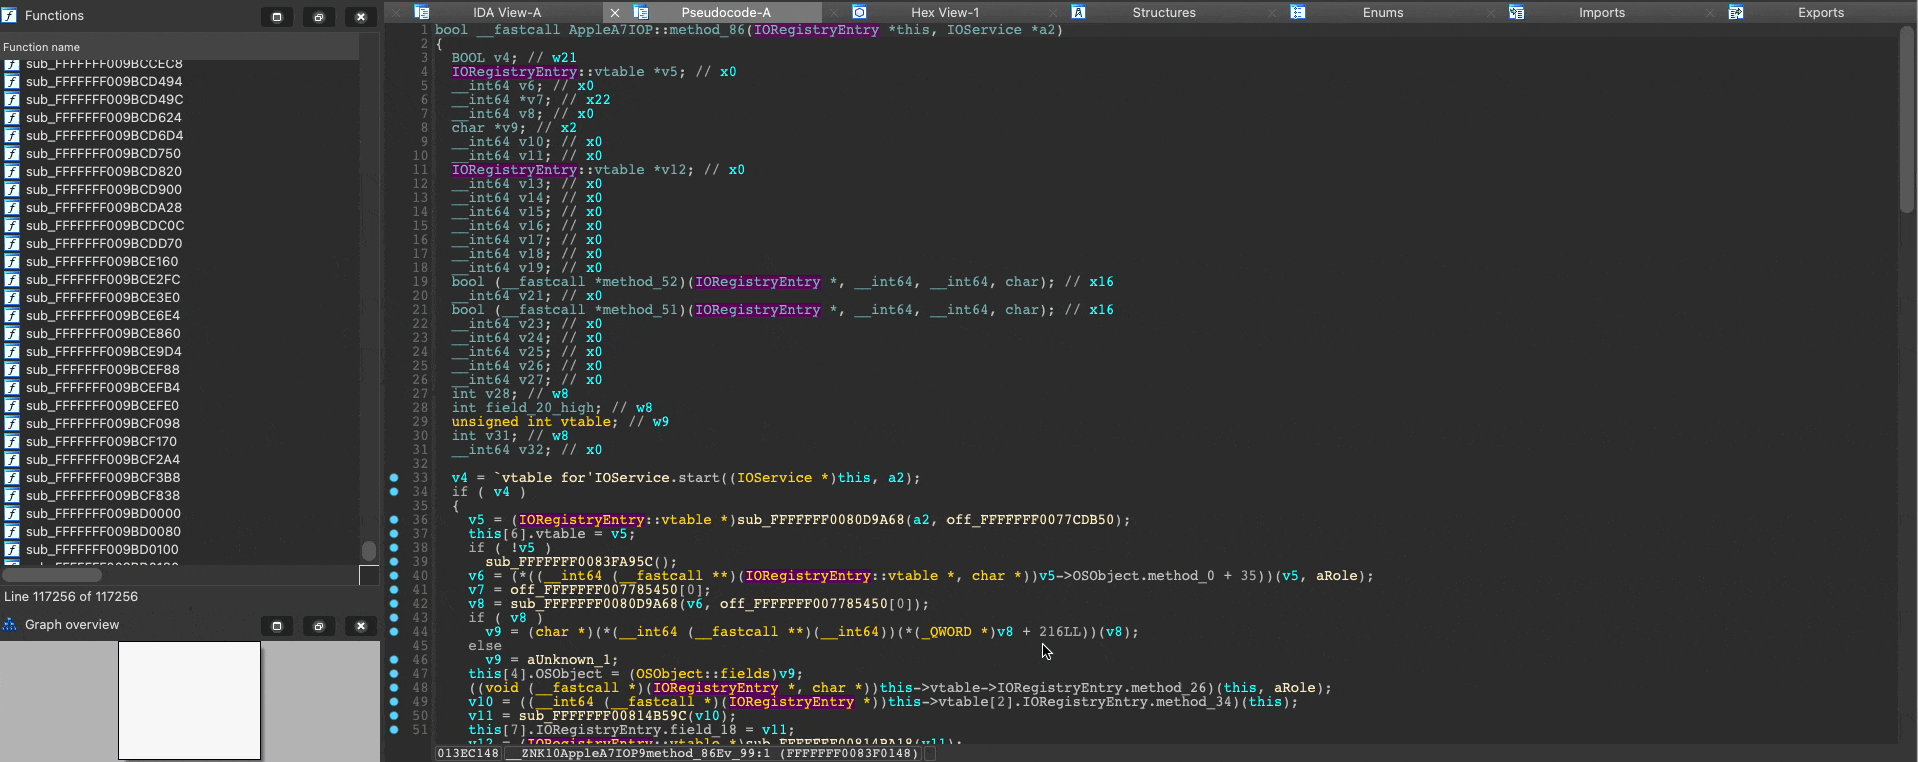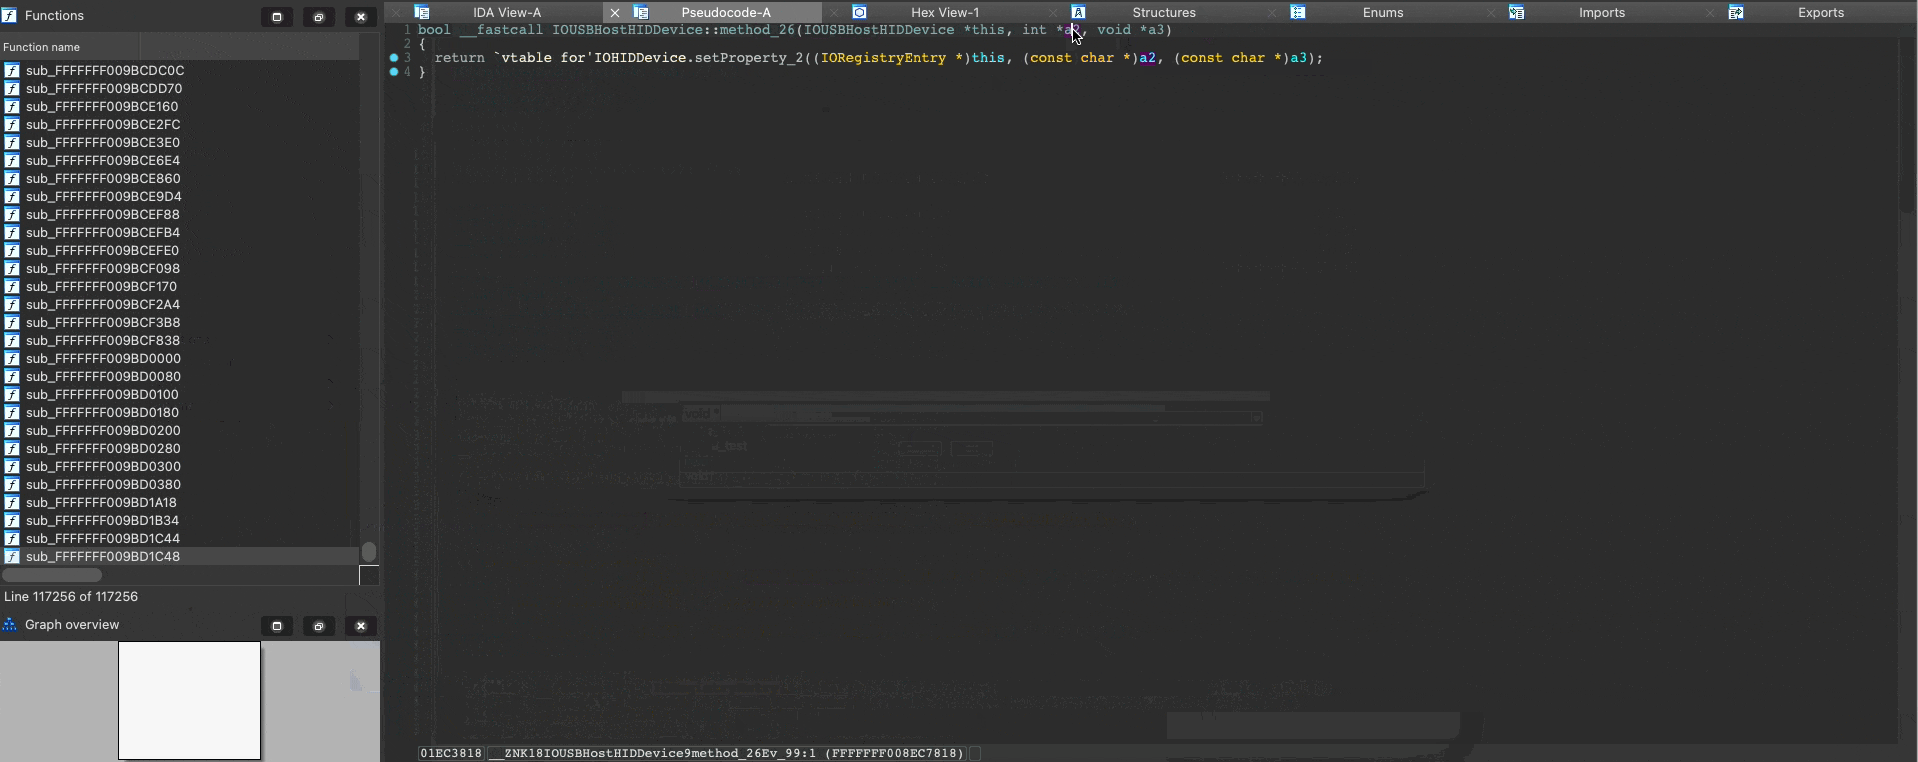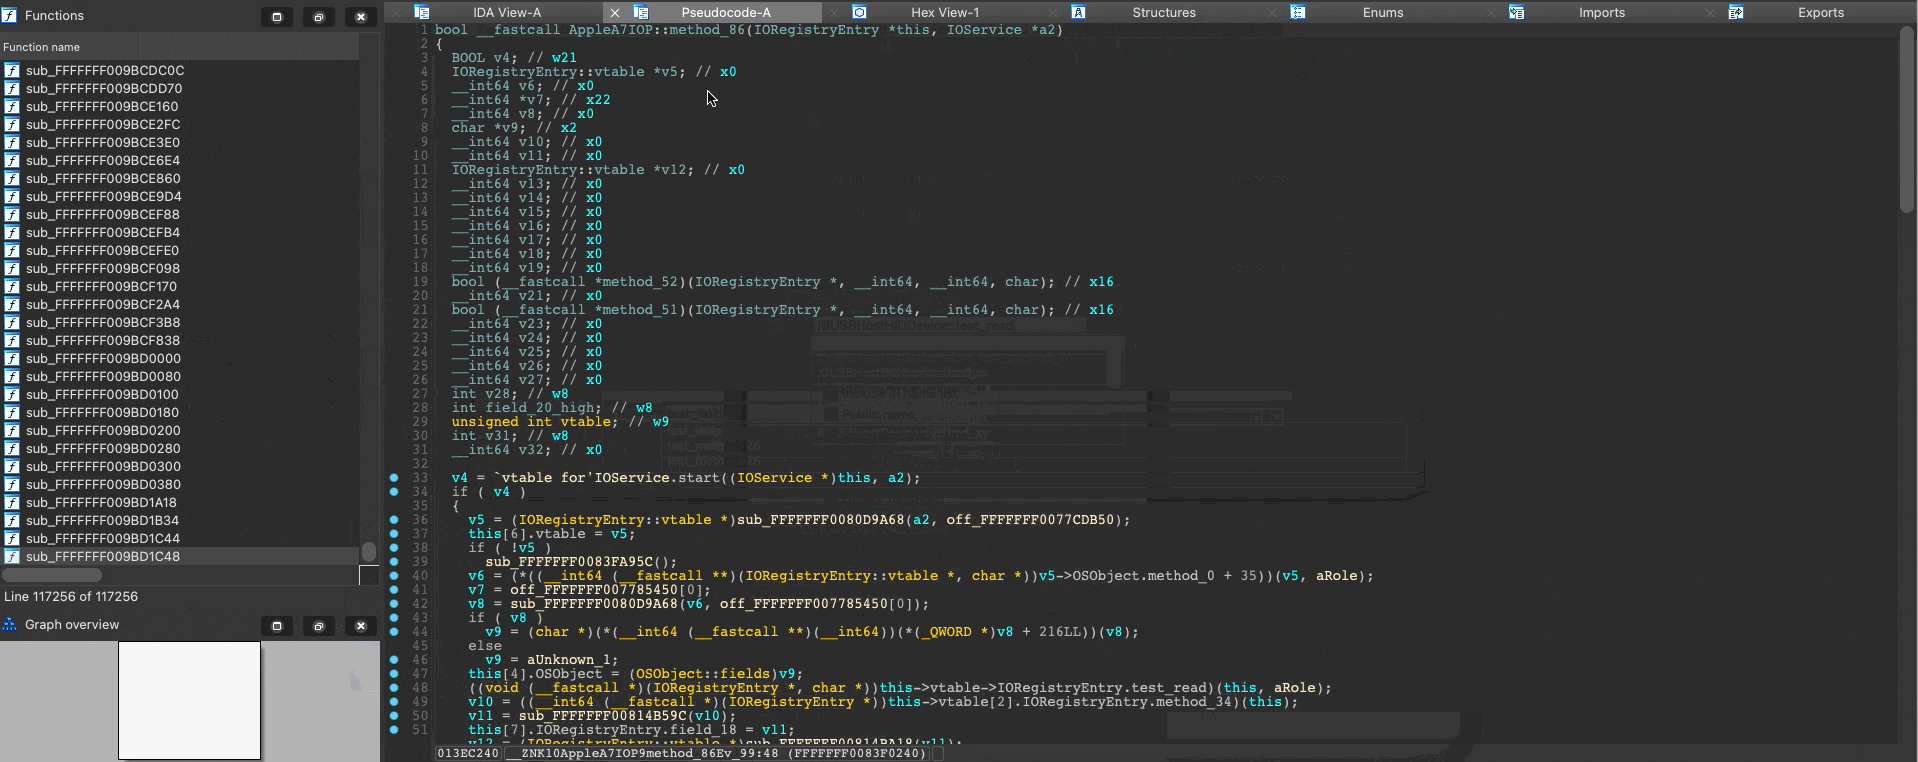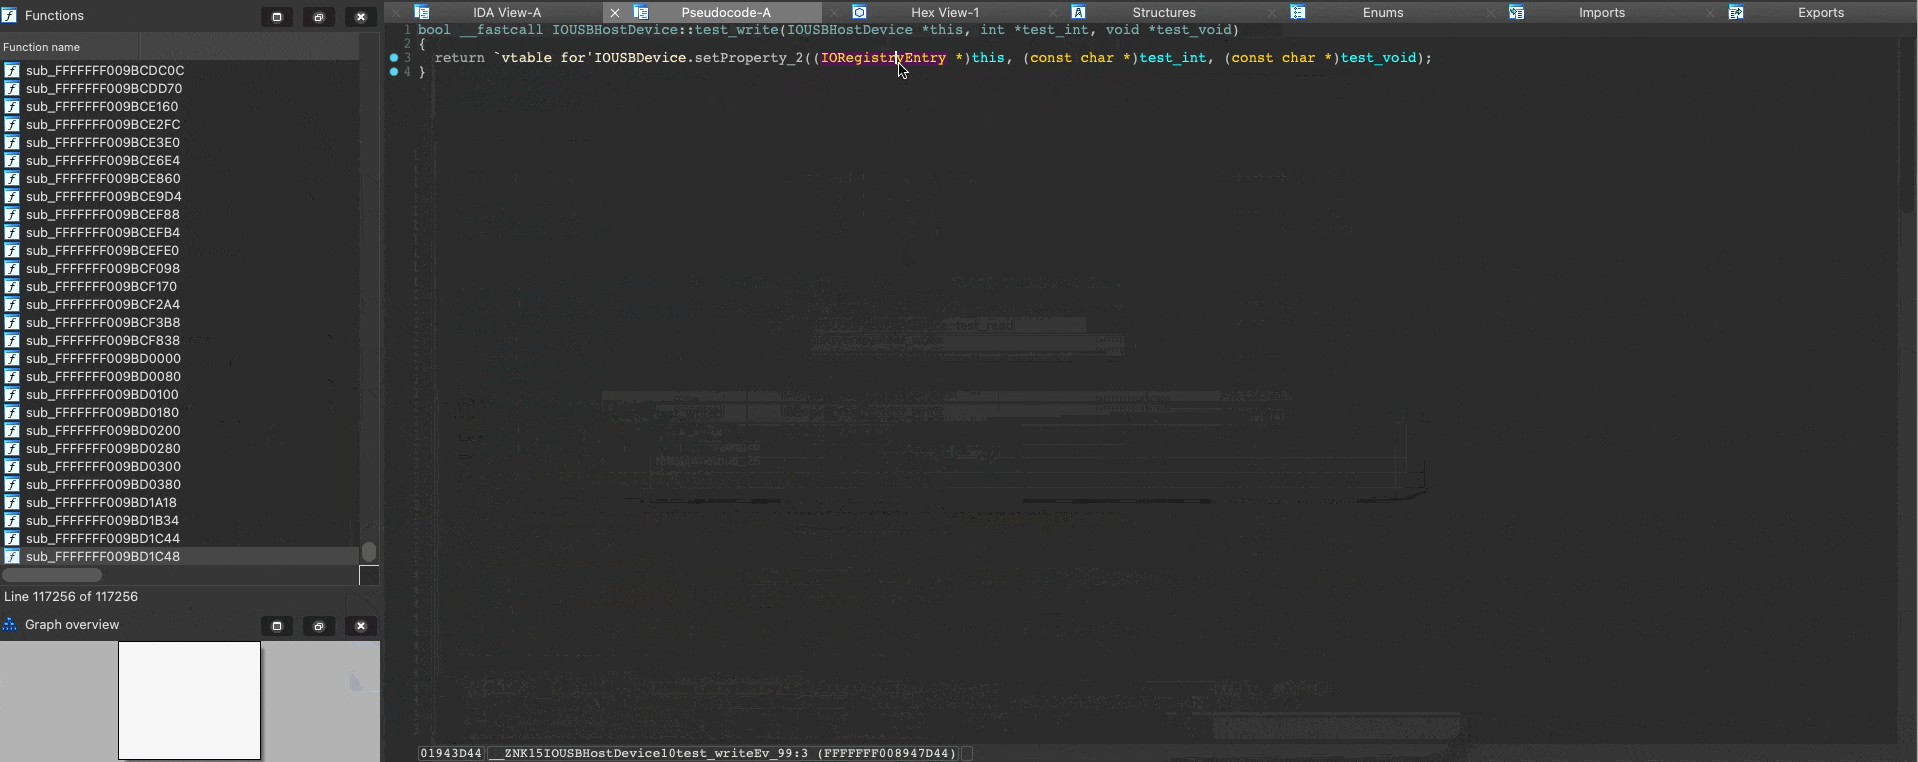 cellebrite-labs/ida_kcpp
An IDAPython module for enhancing c++ support on top of ida_kernelcache
 pstirparo/machofile
machofile is a module to parse Mach-O binary files
 dump-guy/get-pdinvokeimports
PowerShell module for automatic detection of P/Invoke, Dynamic P/Invoke, and D/Invoke in .NET assemblies. Reveals unmanaged API calls, MDTokens, and…
 nccgroup/ghidra-nanomips
nanoMIPS module for Ghidra
 eversinc33/drvtrace
WinDbg plugin to trace module transitions from a debugged driver.
 vichhka-git/magisk-renef
Magisk module that auto-packages renef_server (dynamic instrumentation for Android)
 ymsniper/umbra
External read-only game overlay for Linux. Derived offsets, composed skeletons, optional kernel module for ptrace-independent memory reads and…
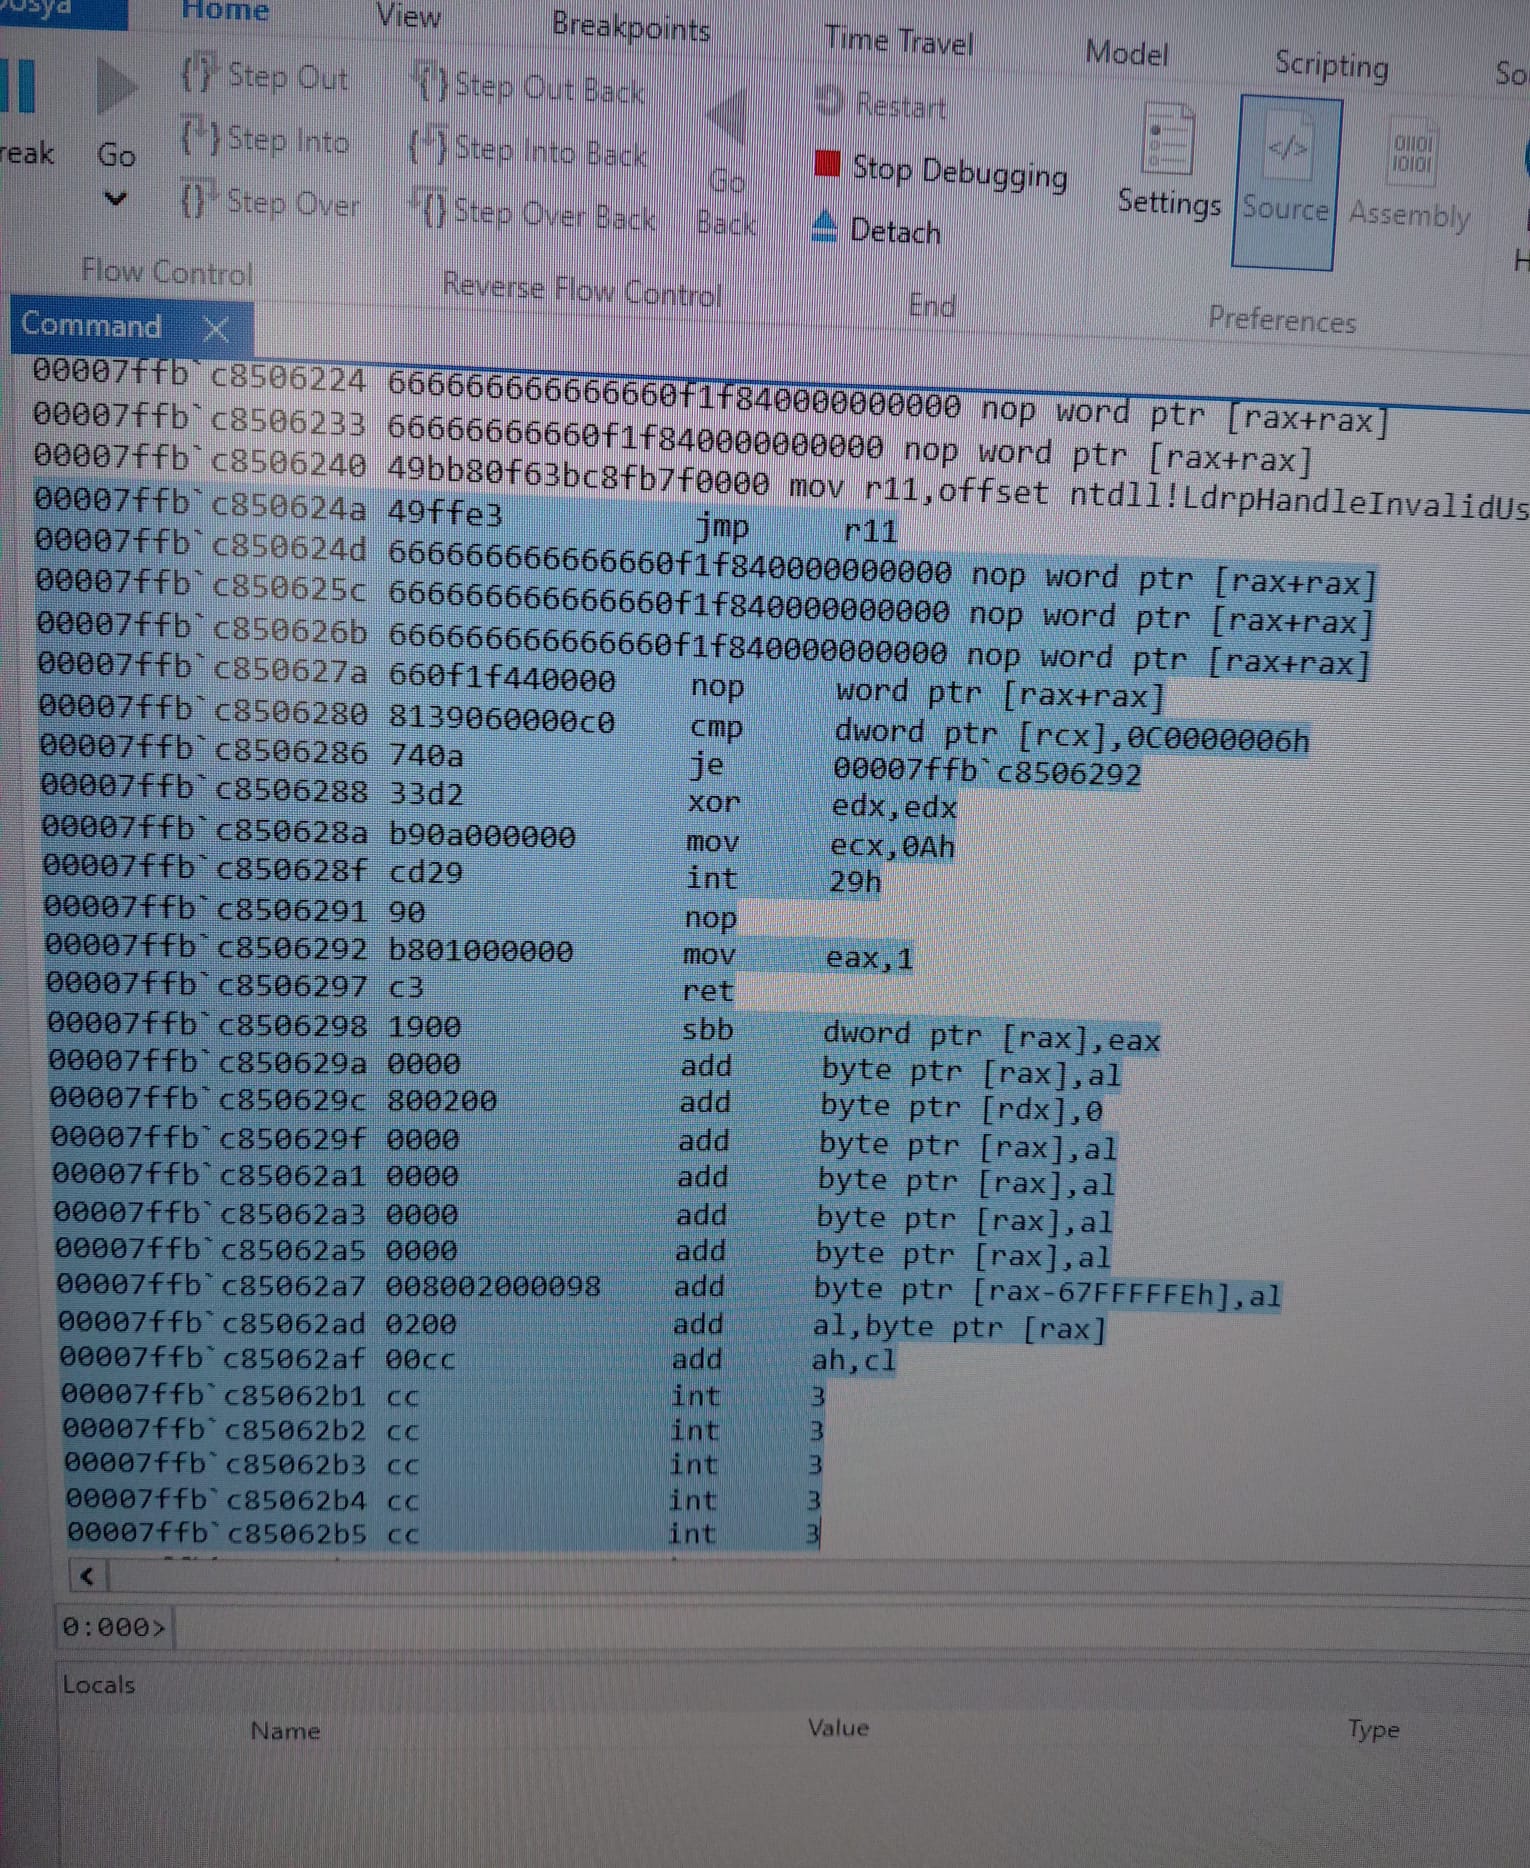 kaandemir993/advanced-loader-reverse-engineering
"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…
 jacobsoo/malconfig
This is part of a module for the framework that i'm constantly developing. Currently only information of the C2 are disclosed here.
 20enderdude20/ghidra_v810_v830
Ghidra processor description module for NEC/Renesas v810 and v830 families
 theatha/yara_for_config_extraction
Tutorial and source code for building a custom YARA module in C to extract malware configurations, with a practical Danabot example and reusable…
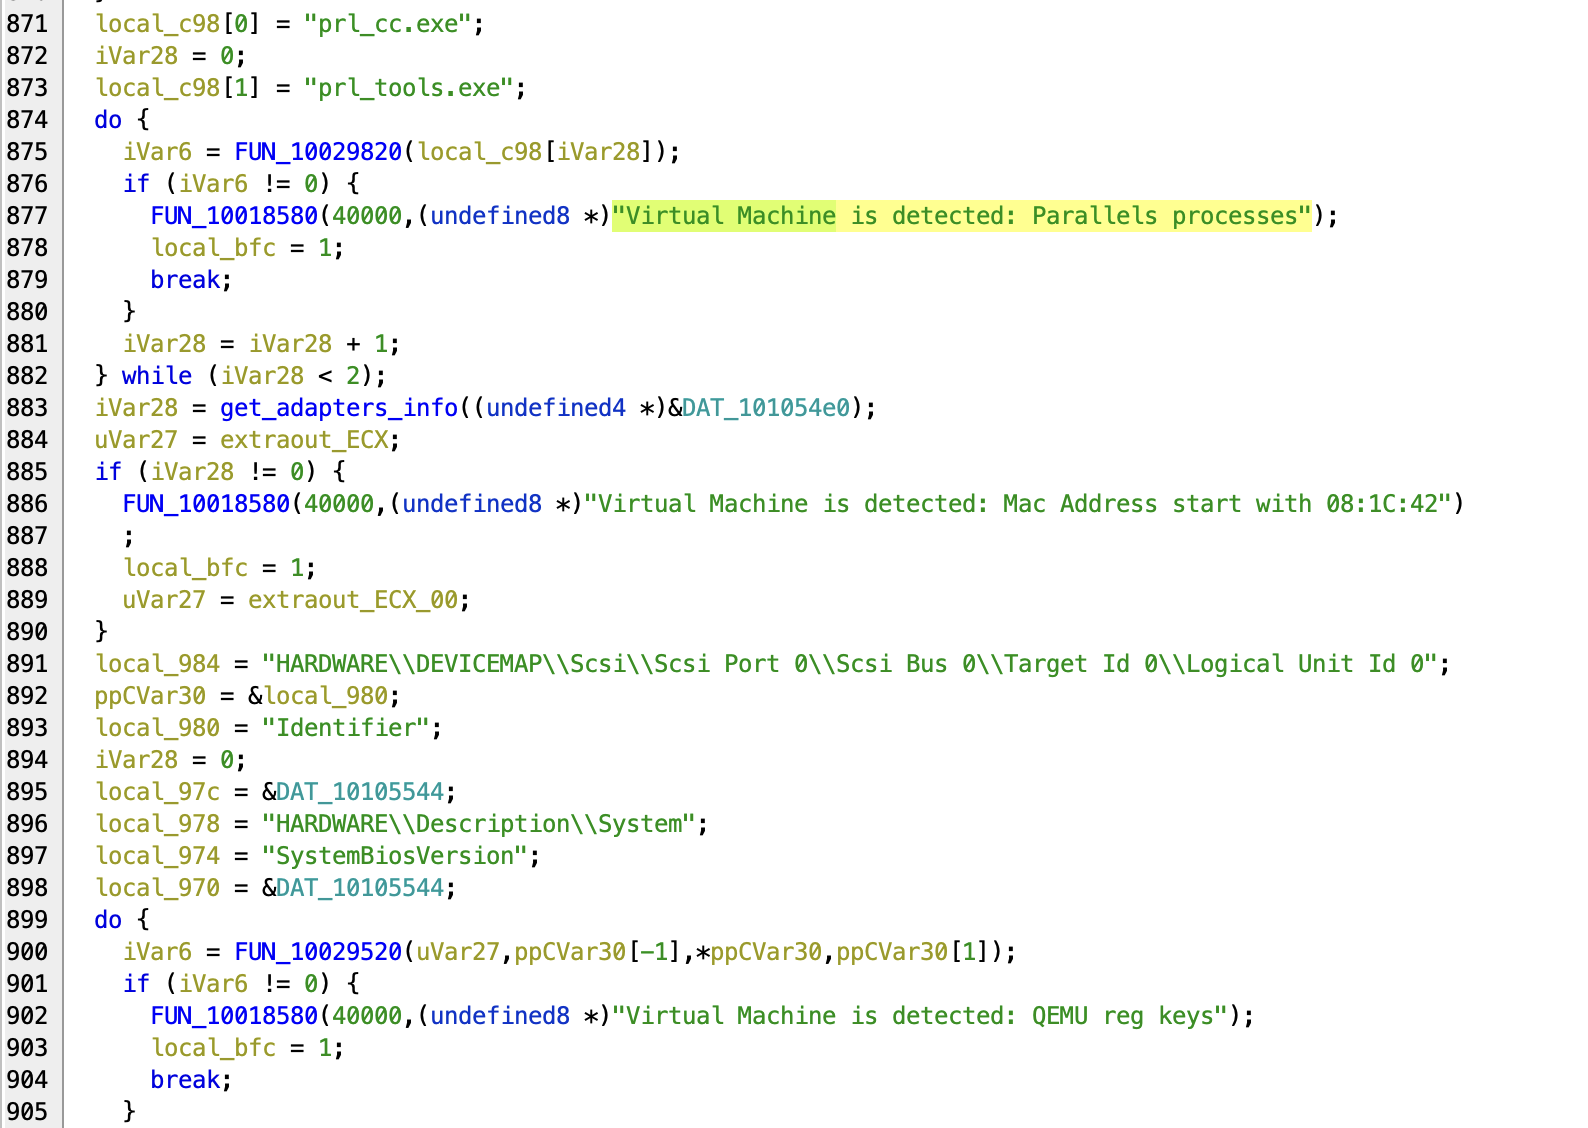 lodi-g/cve-2023-33668
Technical analysis and proof-of-concept bypass for CVE-2023-33668 in DigiExam proctoring software, demonstrating weak VM detection and native module…