
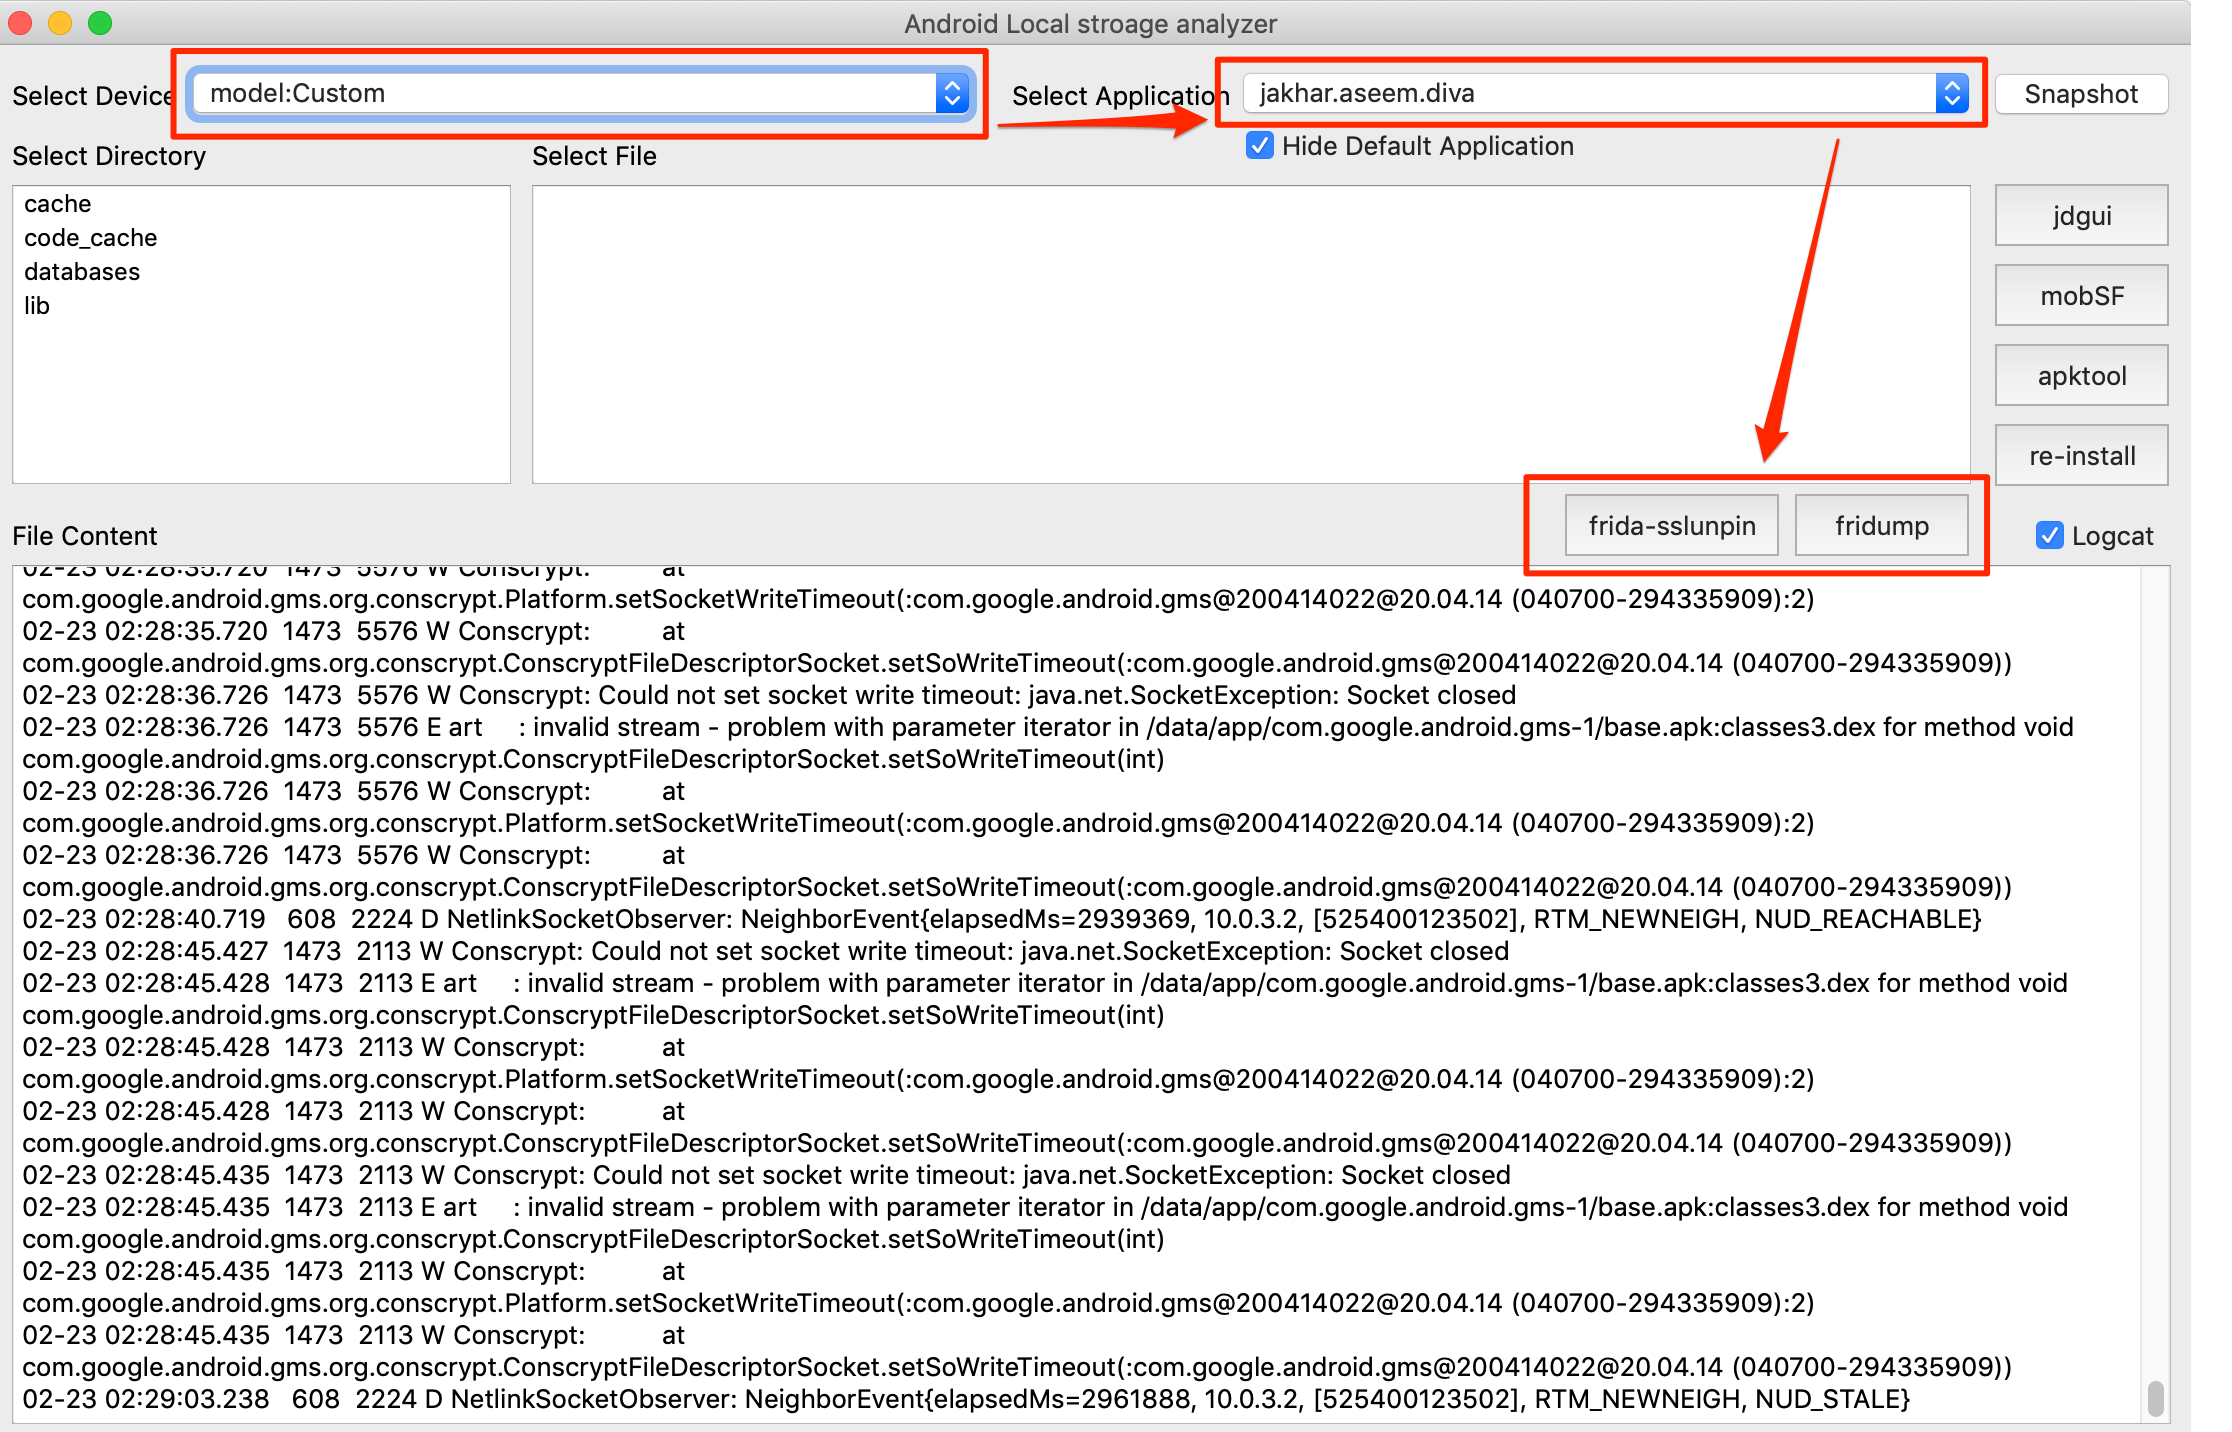
android_application_analyzer
 notsosecure/android_application_analyzer
The tool is used to analyze the content of the android application in local storage.
android-securitydynamic-analysis-sandboxingmobile-app-pentesting+2
notsosecure/android_application_analyzerThe tool is used to analyze the content of the android application in local storage.
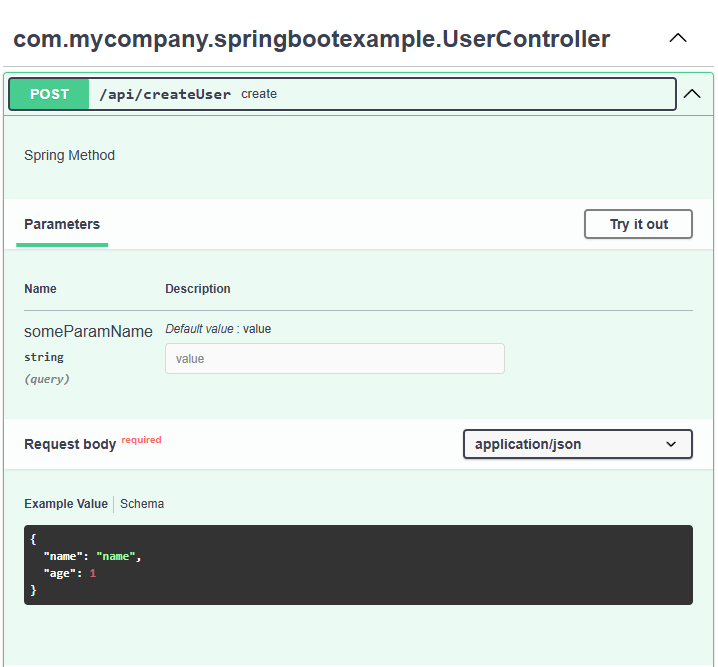 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
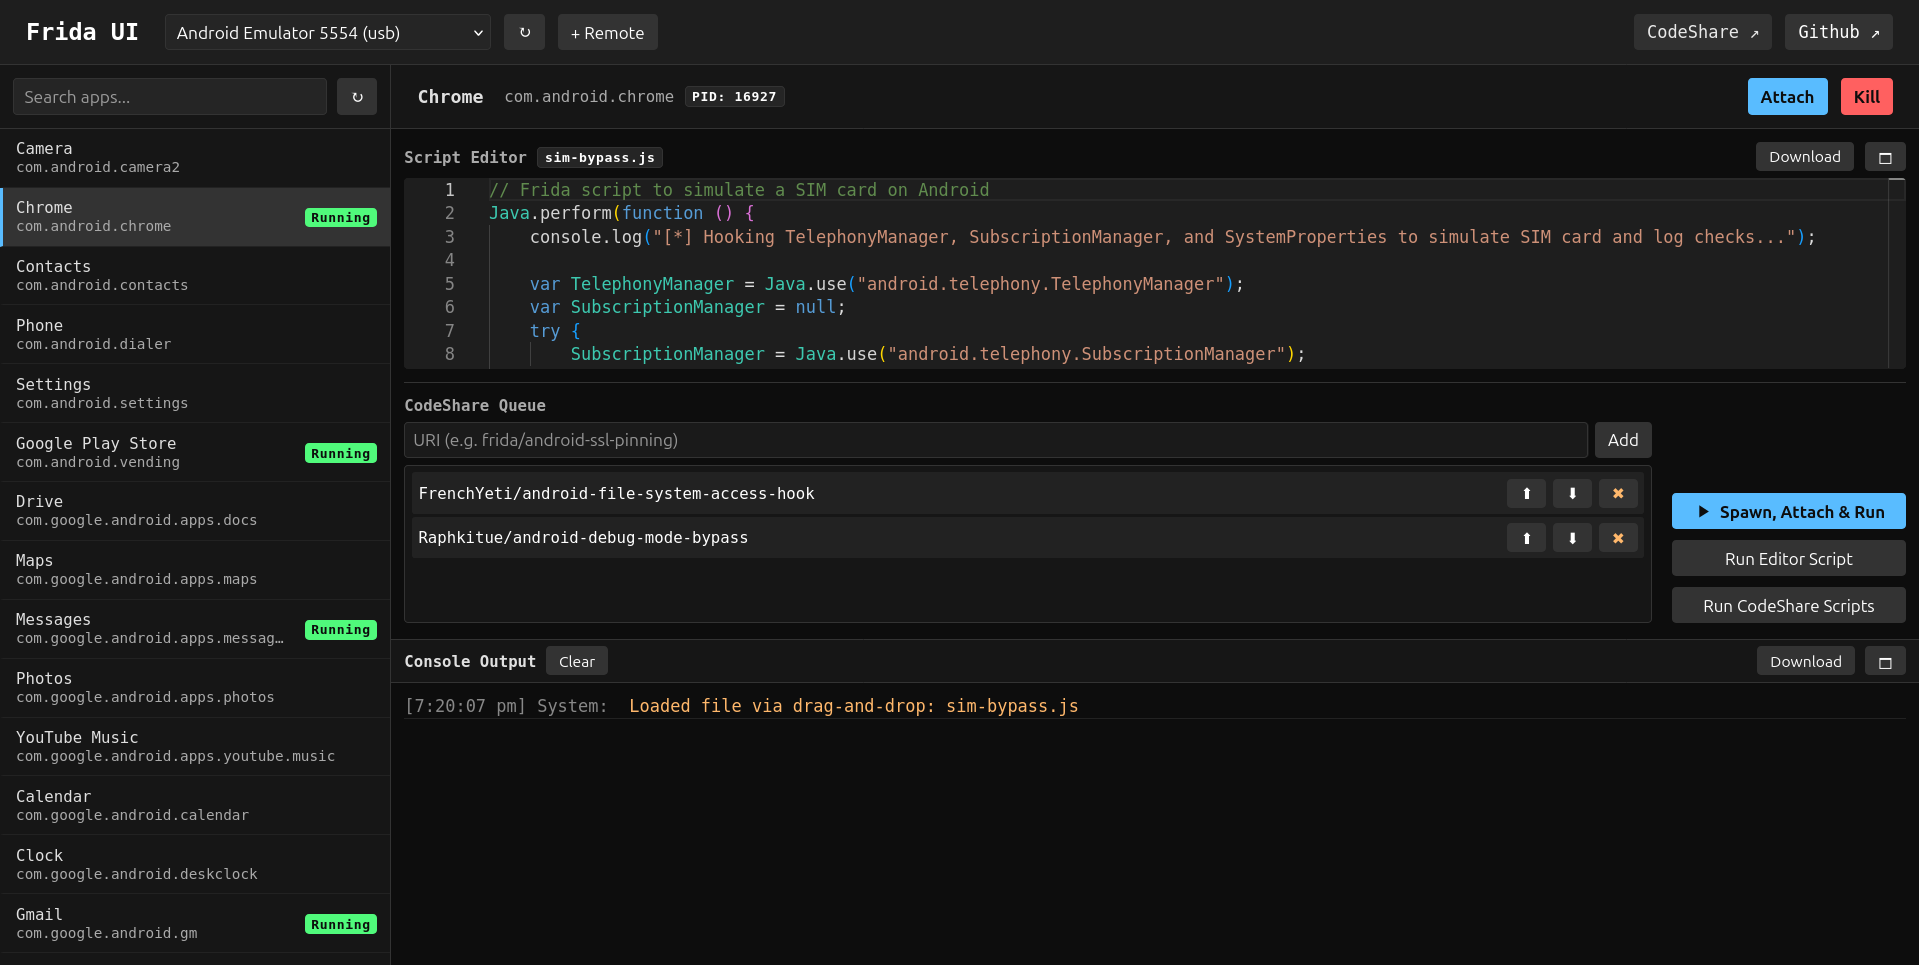 adityatelange/frida-ui
Interact with Frida devices, processes, and scripts directly from your browser.
 ultrasina/androidreverse
Android reverse engineering entirely on-device. Radare2 binary analysis, 8 Java decompilers, Flutter & Unity il2cpp support.
 project-artist/artist
Open-source instrumentation framework for Android apps and Java middleware, modifying code during on-device compilation via the ART compiler.…
 user1342/obfu-de-scate
Fuzzy comparison tool for deobfuscating Android APKs by identifying renamed functions across versions, generating mapping files and interactive HTML…
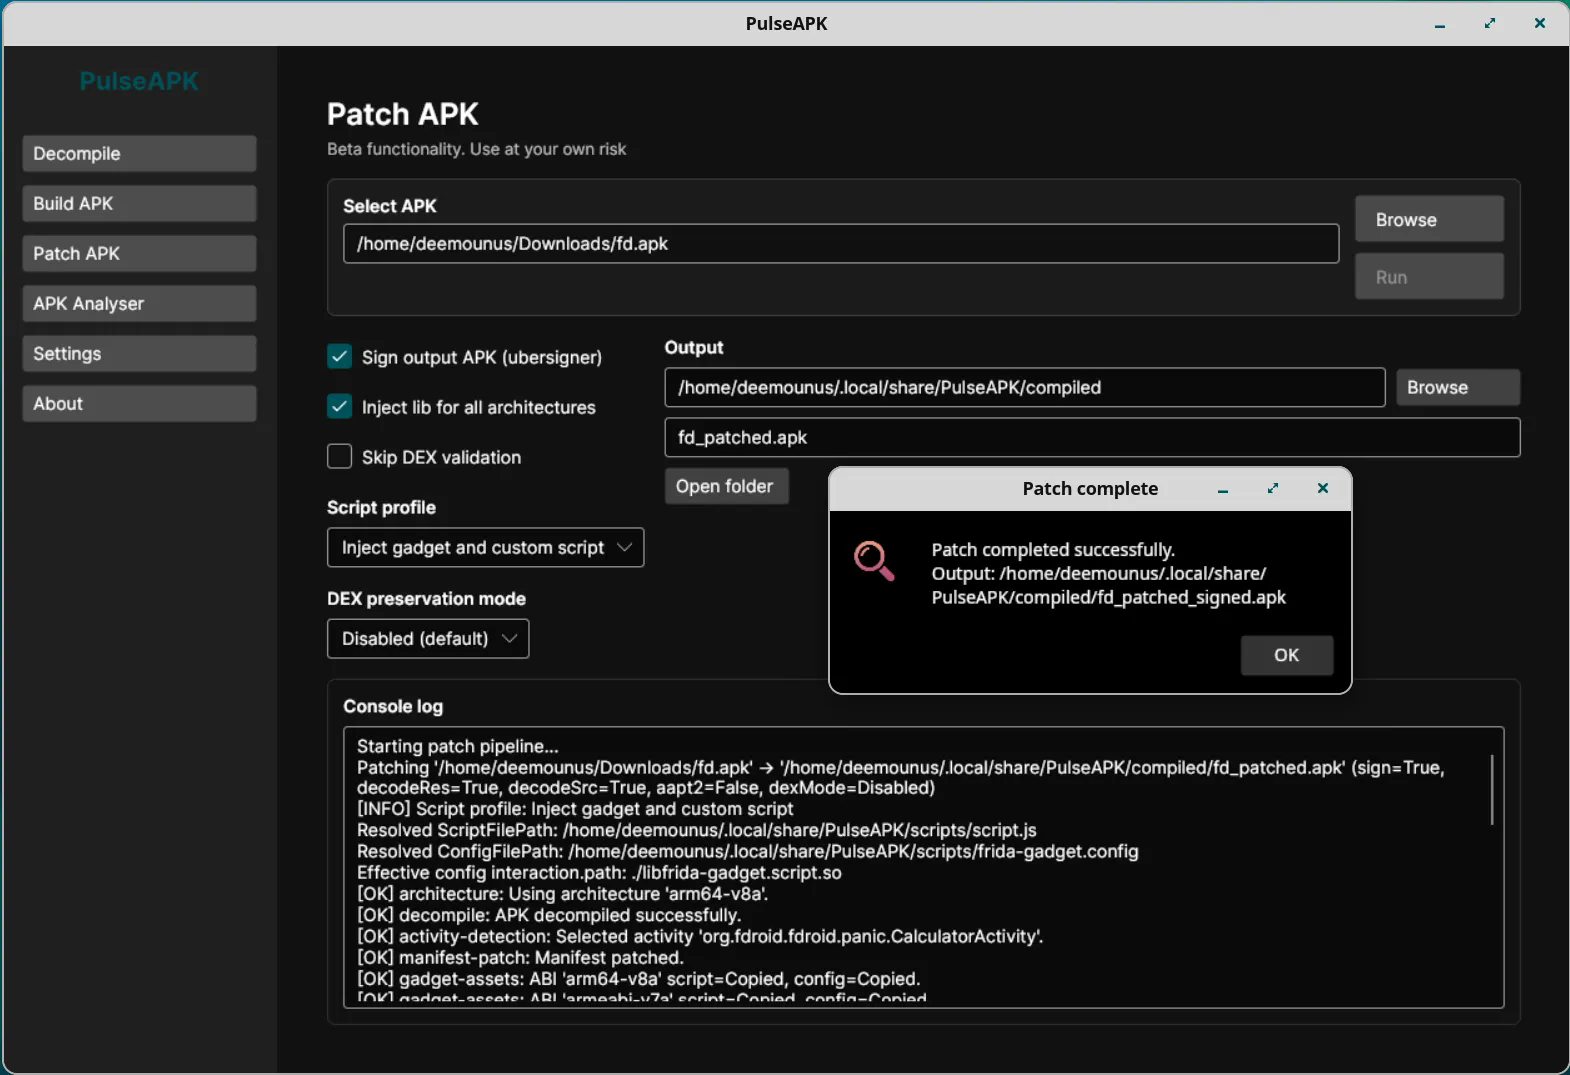 deemoun/pulseapk-core
PulseAPK Core: Cross-Platform tool for working with APK files: Decompilation, Analysis, Building
 thannikudam/topazterminator
C-based tool exploiting the vulnerable wsftprm.sys kernel driver to terminate protected EDR/AV processes on Windows, including PPL processes, via…
 pubglite55/oppo-ghostlock
OPPO Find N2 GhostLock (CVE-2026-43499) exploit adaptation
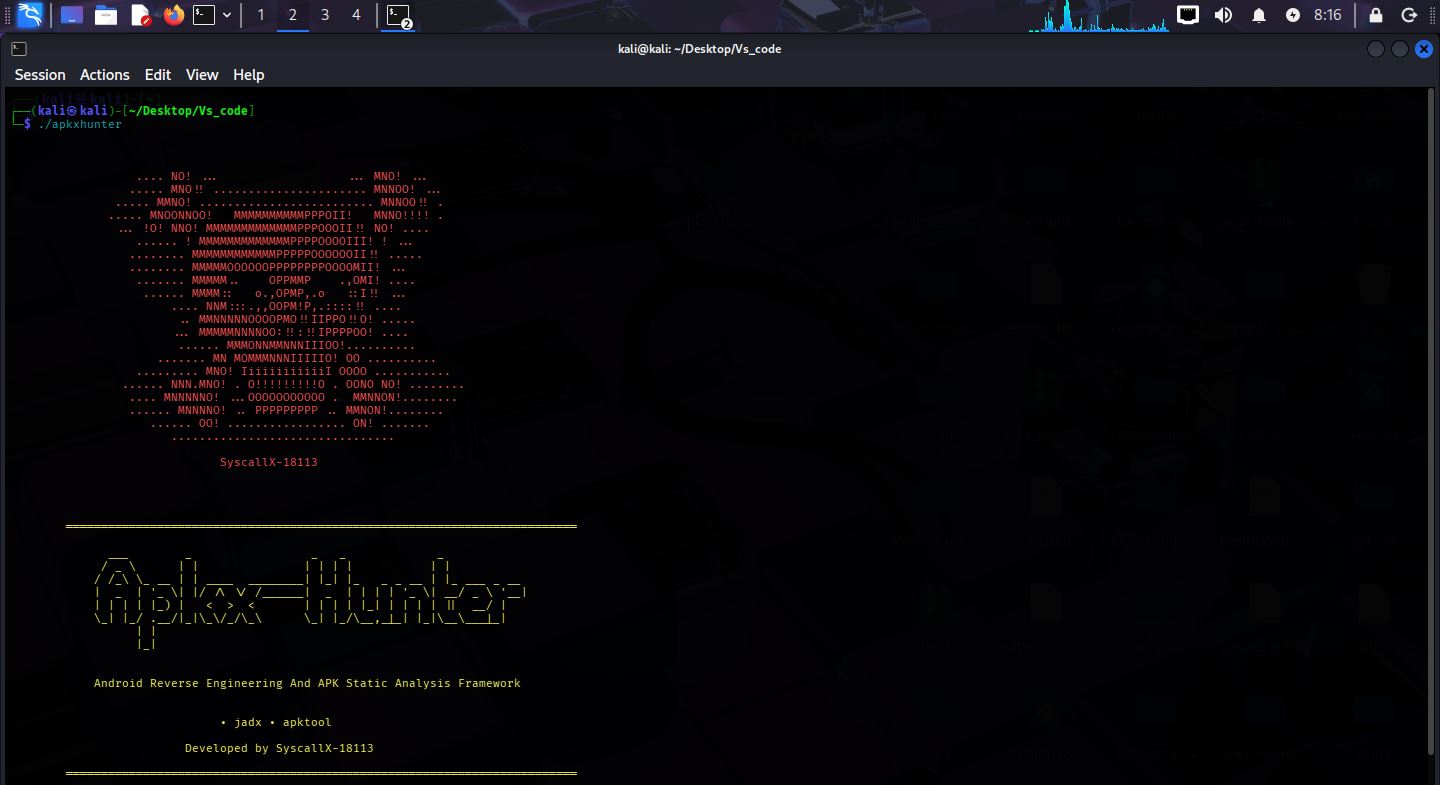 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 0x742/noia
Web-based tool for browsing mobile application sandboxes, previewing SQLite databases and binary files, and downloading app data via Frida…
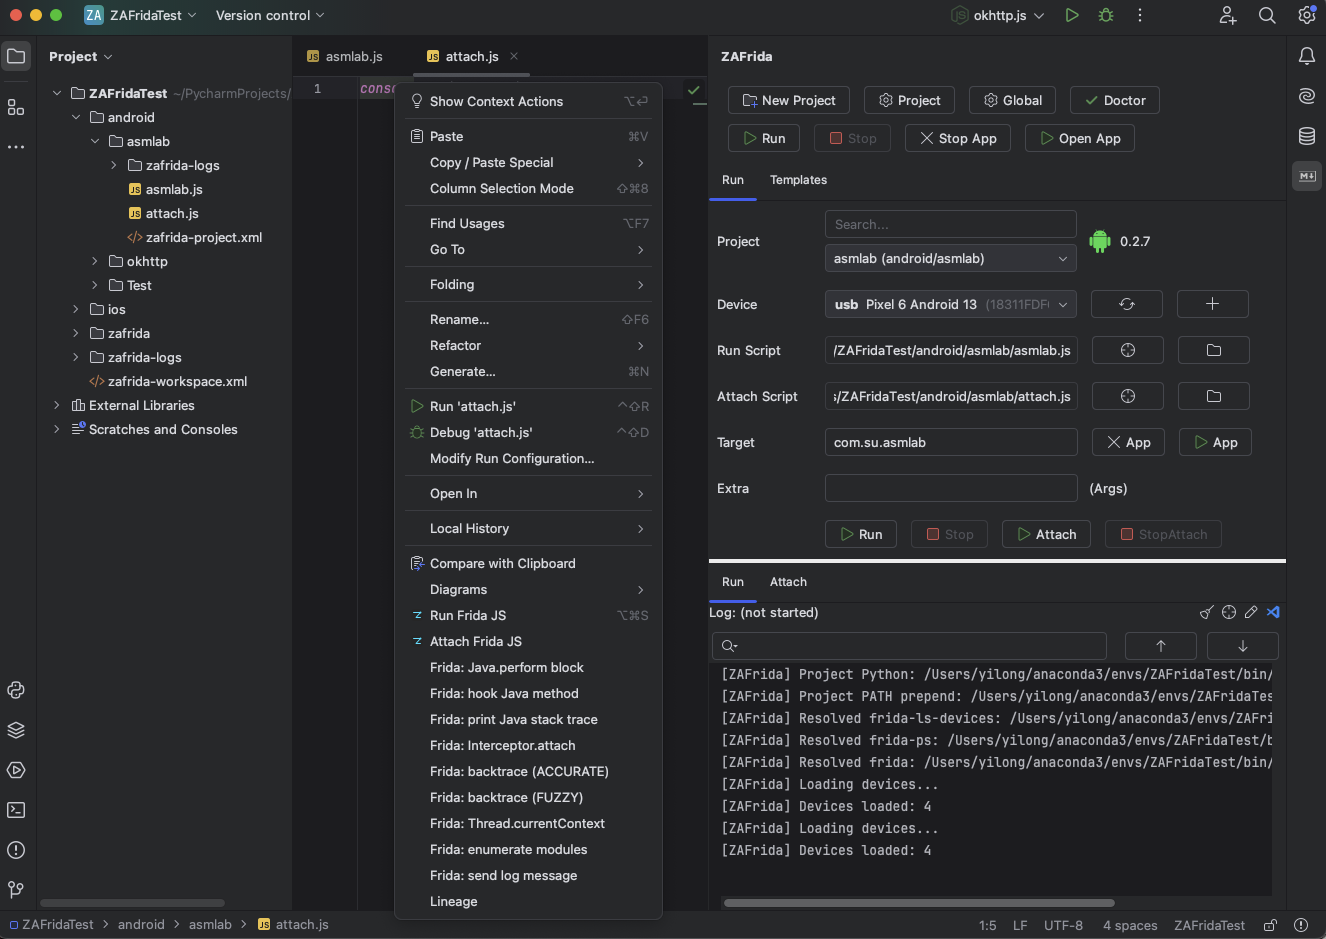 yilongmd/zafrida-ui
A Frida UI tool window inside PyCharm / JetBrains IDEs.
 stefan2200/aparoid
Static and dynamic Android application security analysis
 brnpl/flutter-reverse-engineering-labs
Hands-on challenges for learning how to reverse engineer Flutter applications.
 nccgroup/datajackproxy
Datajack Proxy allows you to intercept TLS traffic in native x86 applications across platforms
 federicodotta/ghidra2frida
Ghidra extension bridging static and dynamic analysis via Frida, enabling scriptable runtime instrumentation for reverse engineering binaries on…
 nccgroup/assethook
LD_PRELOAD magic for Android's AssetManager
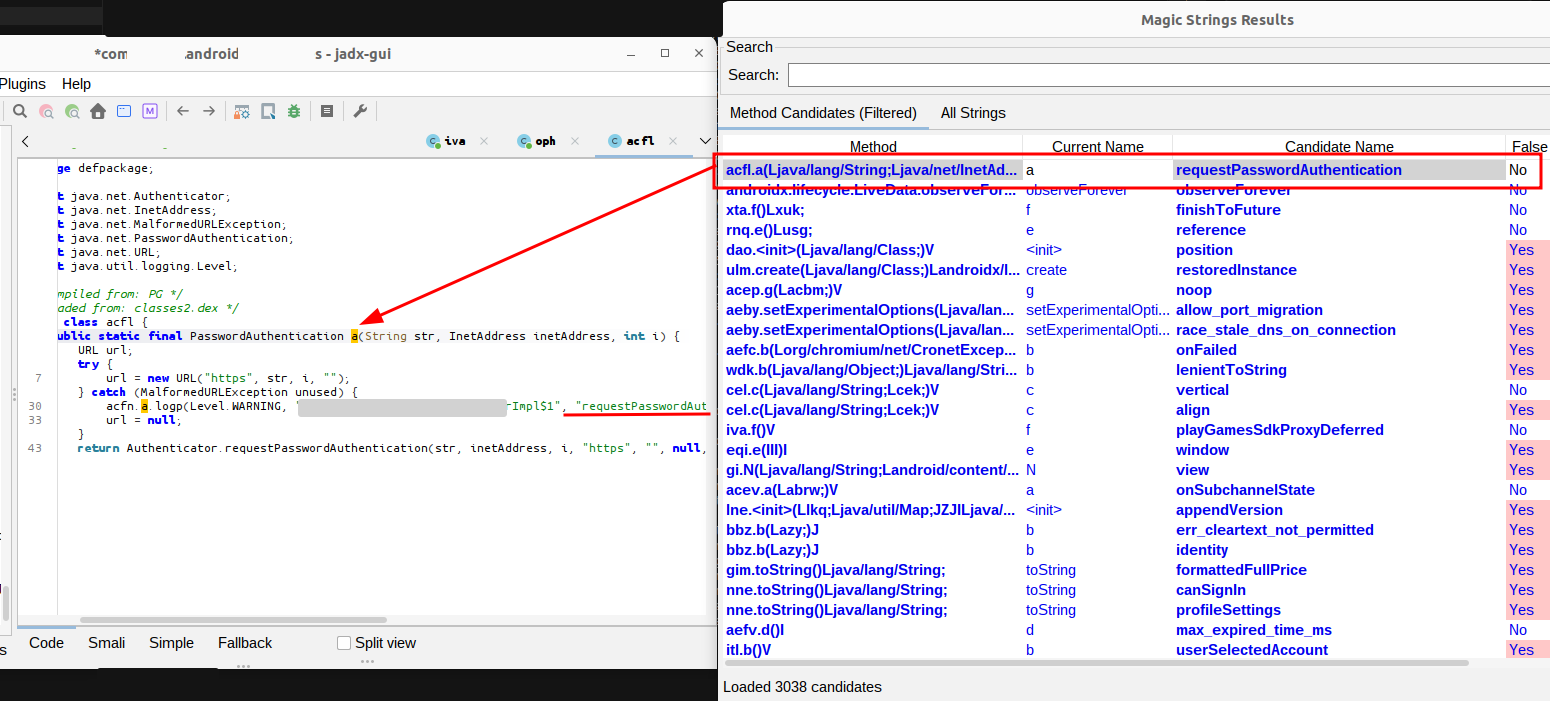 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.