
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
94 results
windiff preview

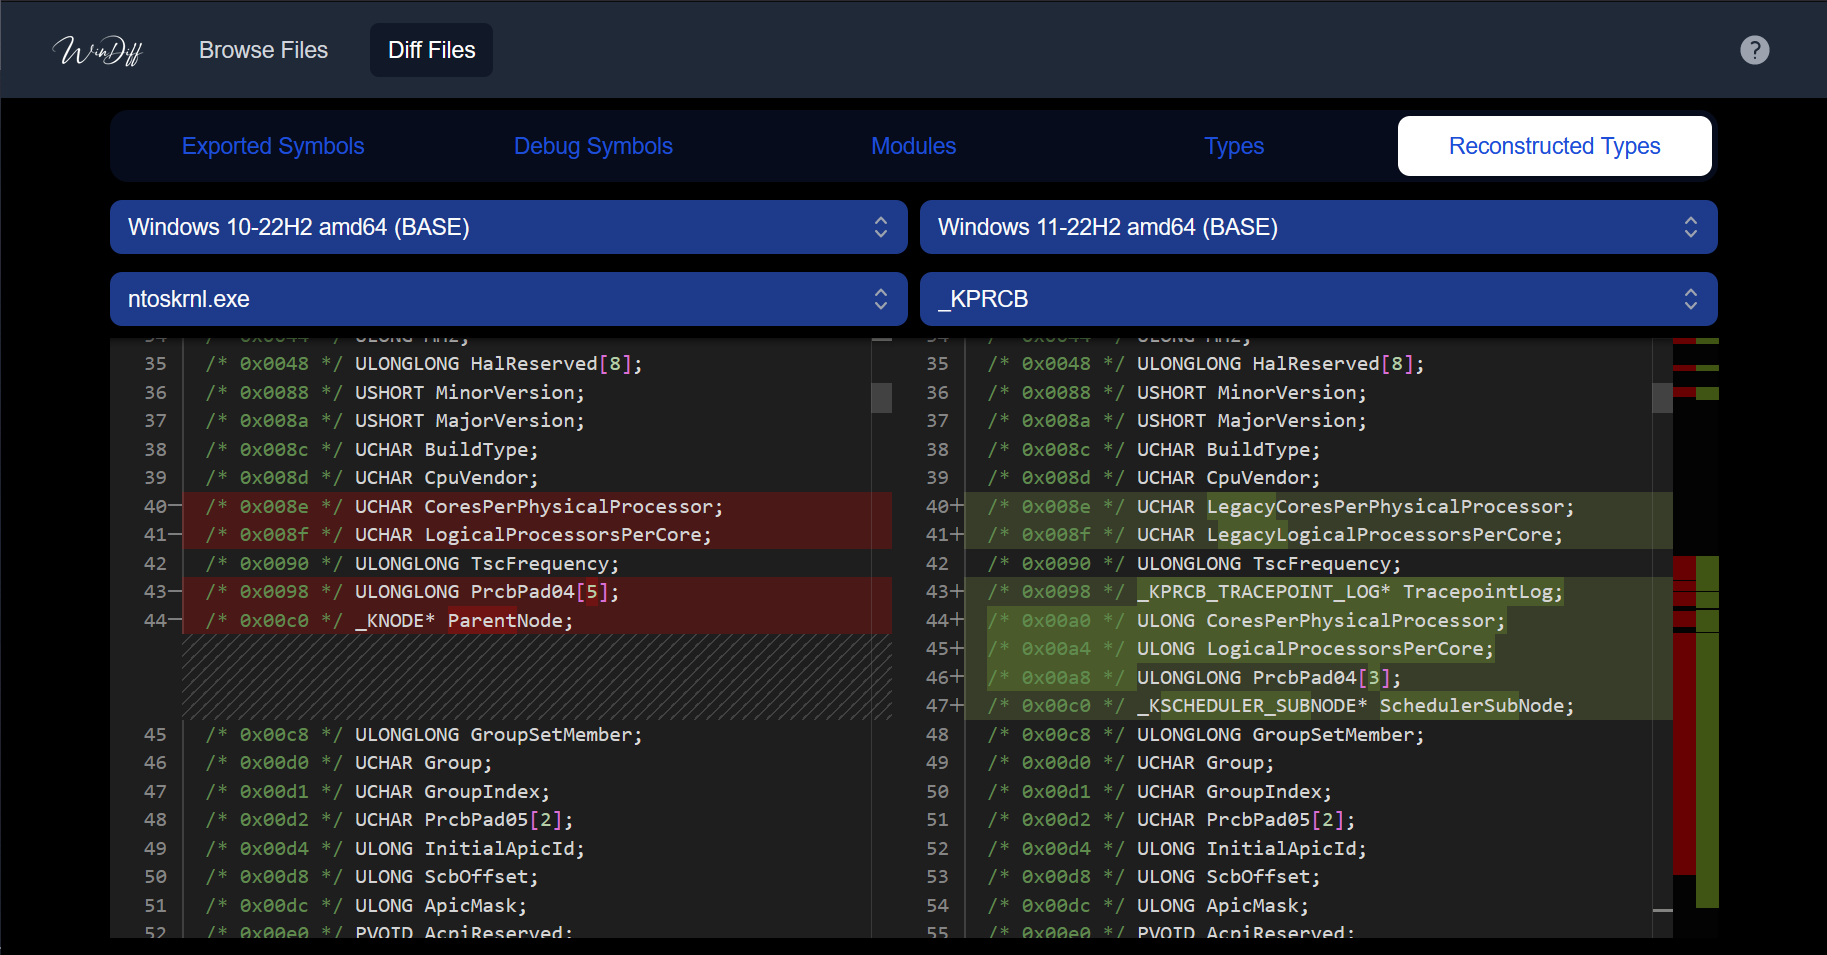
windiff

GitHubergrelet/windiff

Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…

binary-analysisinformation-gatheringreverse-engineering+1
39022h 48m ago
Thick-Client-Pentest-Checklist preview

Thick-Client-Pentest-Checklist

GitHubhari-prasaanth/thick-client-pentest-checklist

A OWASP Based Checklist With 80+ Test Cases
binary-analysiscurated-resourceseducation+5
2053 years ago
LazyDroid preview

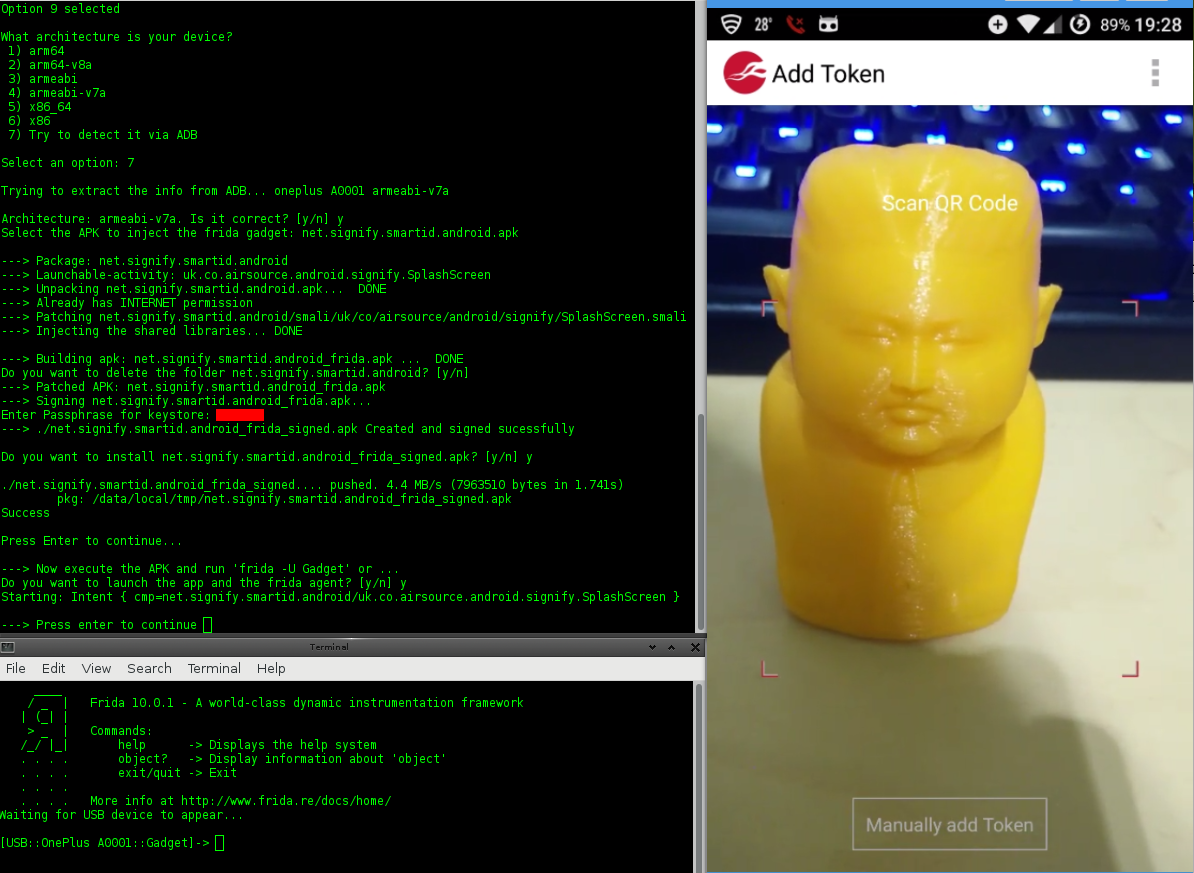
LazyDroid

GitHubnccgroup/lazydroid

bash script to facilitate some aspects of an Android application assessment
android-securitydynamic-analysis-sandboxinginformation-gathering+3
1605 years ago
frida-android-libbinder preview

frida-android-libbinder

GitHubhamz-a/frida-android-libbinder

PoC Frida script to view Android libbinder traffic
android-securitybinary-analysisdynamic-analysis-sandboxing+3
1432 years ago
DracOS preview

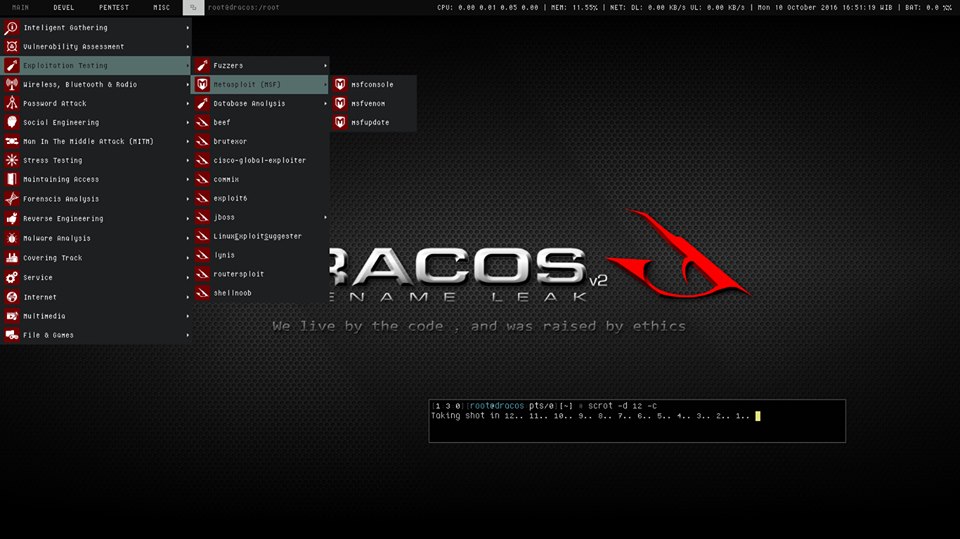
DracOS

GitHubscreetsec/dracos

Dracos Linux ( www.dracos-linux.org ) is the Linux operating system from Indonesian
educationexploitationforensics+8
589 years ago
frida-ipa-extract preview

frida-ipa-extract

GitHublautarovculic/frida-ipa-extract

Robust Frida-based tool to dump decrypted iOS apps as .ipa from a jailbroken device supports App Store, sideloaded and system.
information-gatheringios-securitymobile-app-pentesting+3
1296 months ago
usbsnoop preview

usbsnoop

GitHubyeet-src/usbsnoop

Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…
debuggersdynamic-analysis-sandboxingembedded-systems-security+7
872 months ago
dexfinder preview

dexfinder

GitHubjunelegency/dexfinder

Cross-platform APK/DEX method finder with call chain tracing, ProGuard deobfuscation, and hidden API detection
android-securitybinary-analysiscode-analysis+6
1085 months ago
jadx-magic-strings preview

jadx-magic-strings

GitHub0rshemesh/jadx-magic-strings

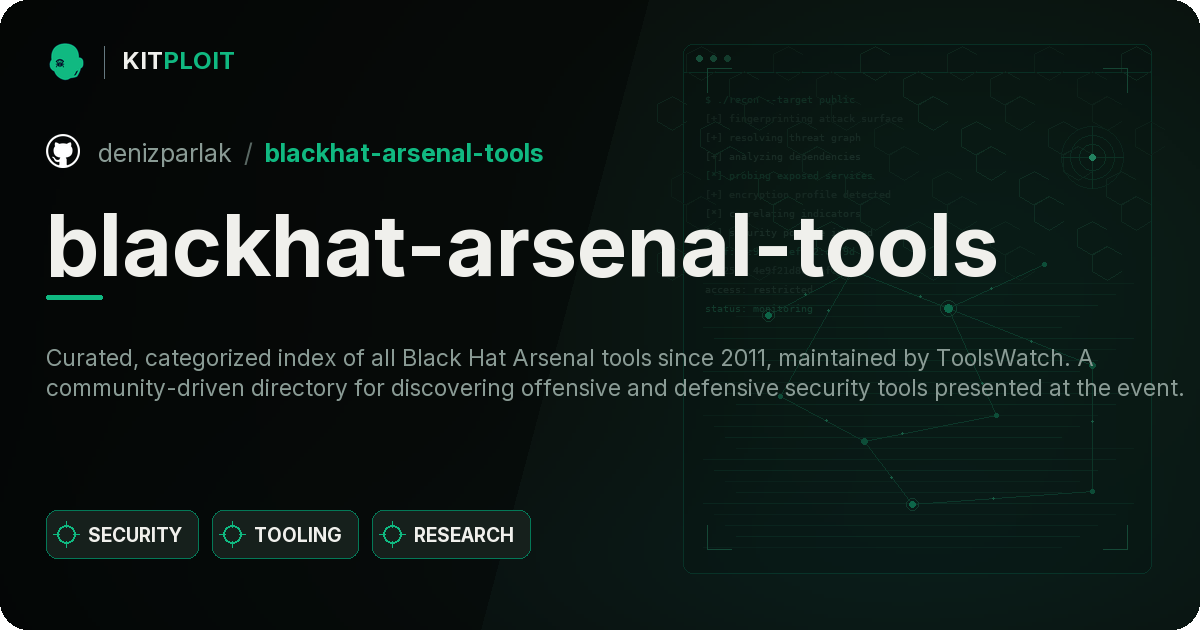
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
android-securitybinary-analysiscode-analysis+5
461 month ago
blackhat-arsenal-tools preview

blackhat-arsenal-tools

GitHubdenizparlak/blackhat-arsenal-tools

Black Hat Arsenal Tools Official Account
curated-resourceseducationexploit-frameworks+6
89 years ago
RPC-Triage preview

RPC-Triage

GitHubtalha-nazeef-ahmed/rpc-triage

A zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.

binary-analysisreconnaissancered-teaming+3
141 month ago
Formbook-Payload-Extraction-XOR-Decryption-Net-Assembly-Analysis preview

Formbook-Payload-Extraction-XOR-Decryption-Net-Assembly-Analysis

GitHubkaandemir993/formbook-payload-extraction-xor-decryption-net-assembly-analysis

Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…
binary-analysisdebuggersdigital-forensics+6
611 days ago
apkSneeze preview

apkSneeze

GitHubhumoud/apksneeze

A tool that automates the mundane tasks of pentesting Android apps. It uses APKTool and Dex2Jar.

android-securityinformation-gatheringmobile-app-pentesting+2
116 years ago
StealC-Stealer-RuntimeBroker-Hollowing-C2-Extraction-Payload-Extraction-Analysis preview

StealC-Stealer-RuntimeBroker-Hollowing-C2-Extraction-Payload-Extraction-Analysis

GitHubkaandemir993/stealc-stealer-runtimebroker-hollowing-c2-extraction-payload-extraction-analysis

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

command-and-controldata-exfiltrationdigital-forensics+7
326 days ago
cve-2024-30350-research-notes preview

cve-2024-30350-research-notes

GitHublmx-071028/cve-2024-30350-research-notes

Research notes documenting CVE-2024-30350, an out-of-bounds read in Foxit PDF Reader annotation handling, covering triage, disclosure, and defensive…
curated-resourceseducationinformation-gathering+3
28 days ago
machscope preview

machscope

GitHubm10ust/machscope

macOS IPC, launchd, Mach-O, and trust relationship explorer — zero-dependency terminal-native forensic tool
binary-analysisdigital-forensicsforensics+7
11 month ago
CVE-2025-39247 preview

CVE-2025-39247

GitHubsita-technologies/cve-2025-39247

HikCentral Professional - Pre-Auth License ActiveCode Leak
binary-analysiscryptographyexploitation+6
4 months ago
TwoMillion-Machine-Writeup preview

TwoMillion-Machine-Writeup

GitHubanxs3c/twomillion-machine-writeup

From deobfuscating code.js to root, CVE-2023-0386

ctfeducationexploitation+7
4 months ago
Previous123456Next