
flare-vm
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
binary-analysisdebuggersdigital-forensics+10
9.1k
mandiant/flare-vmA collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, watchOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS…
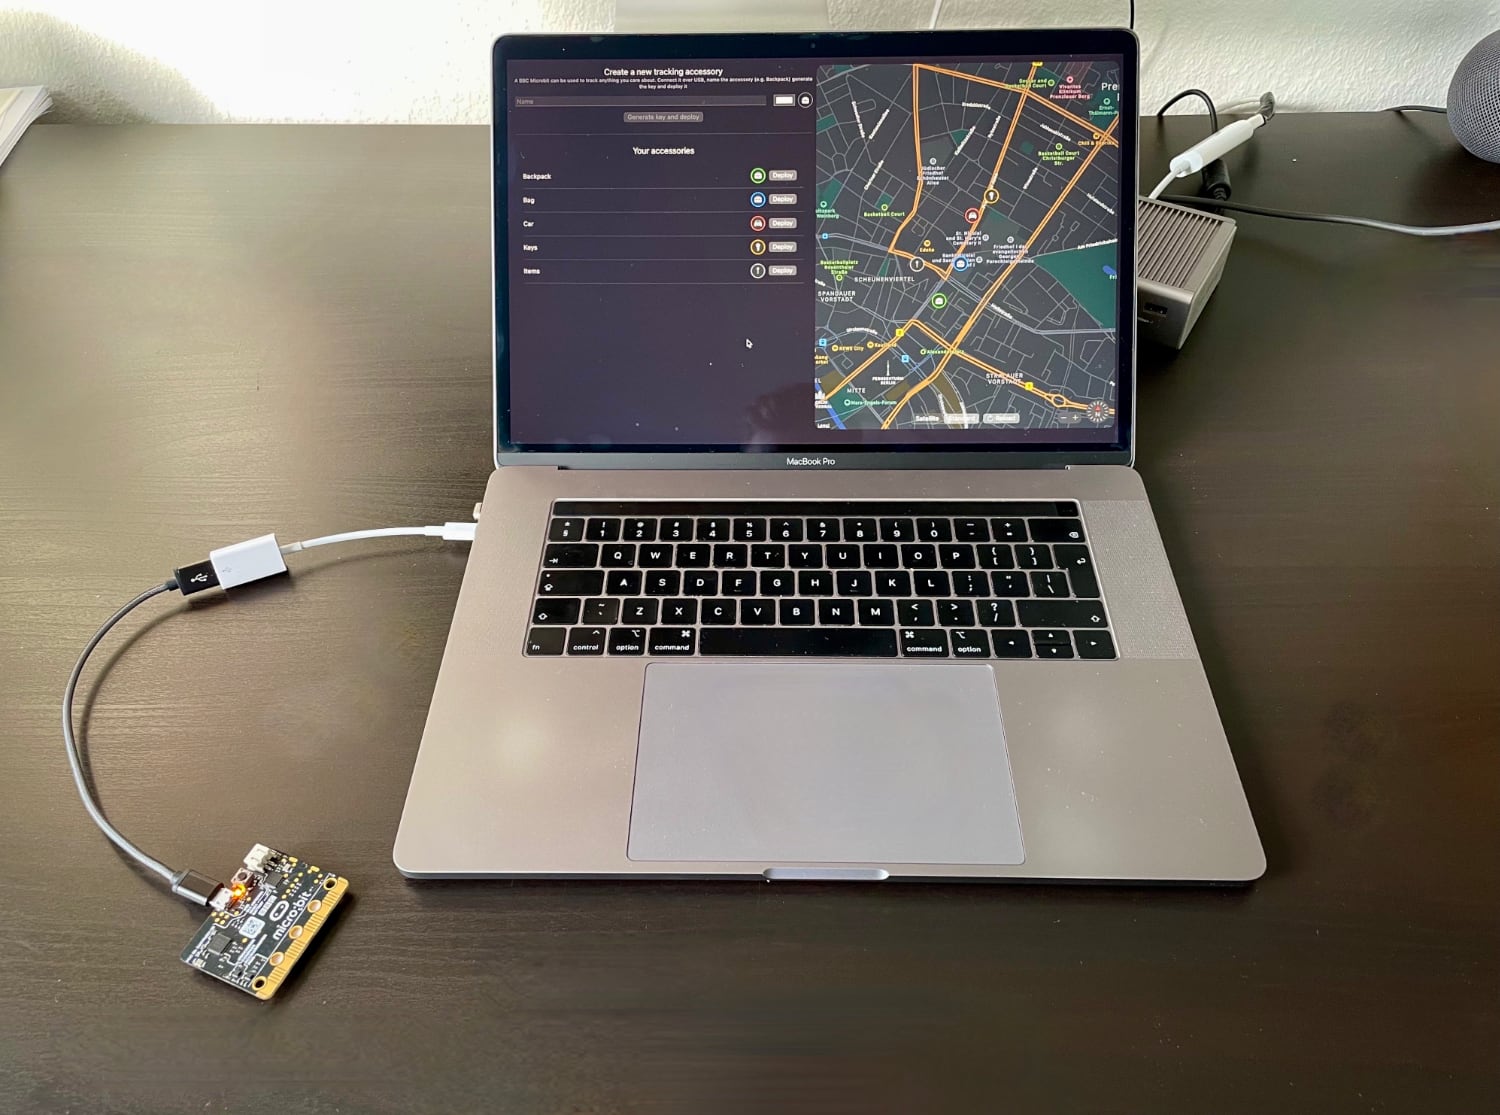 seemoo-lab/openhaystack
Build your own 'AirTags' 🏷 today! Framework for tracking personal Bluetooth devices via Apple's massive Find My network.
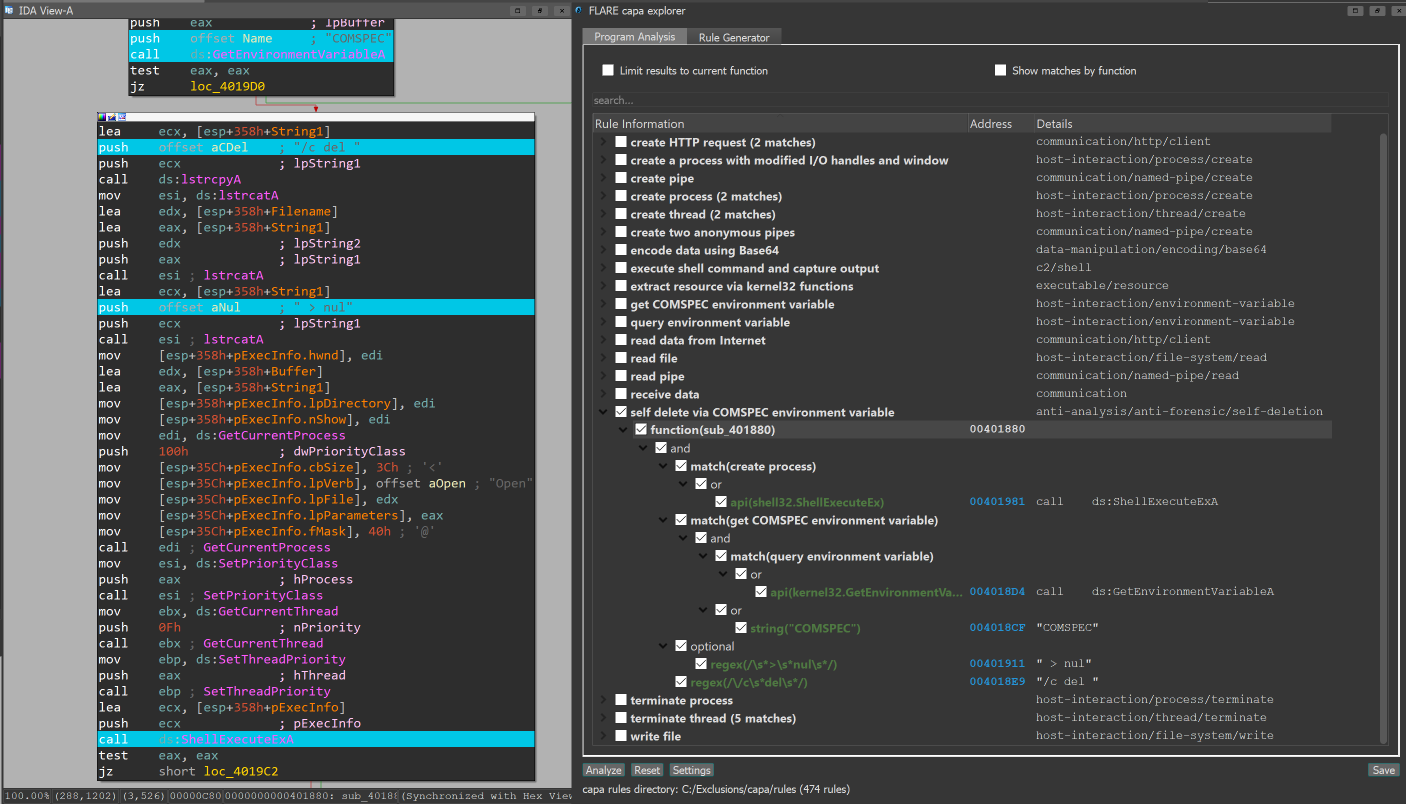 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
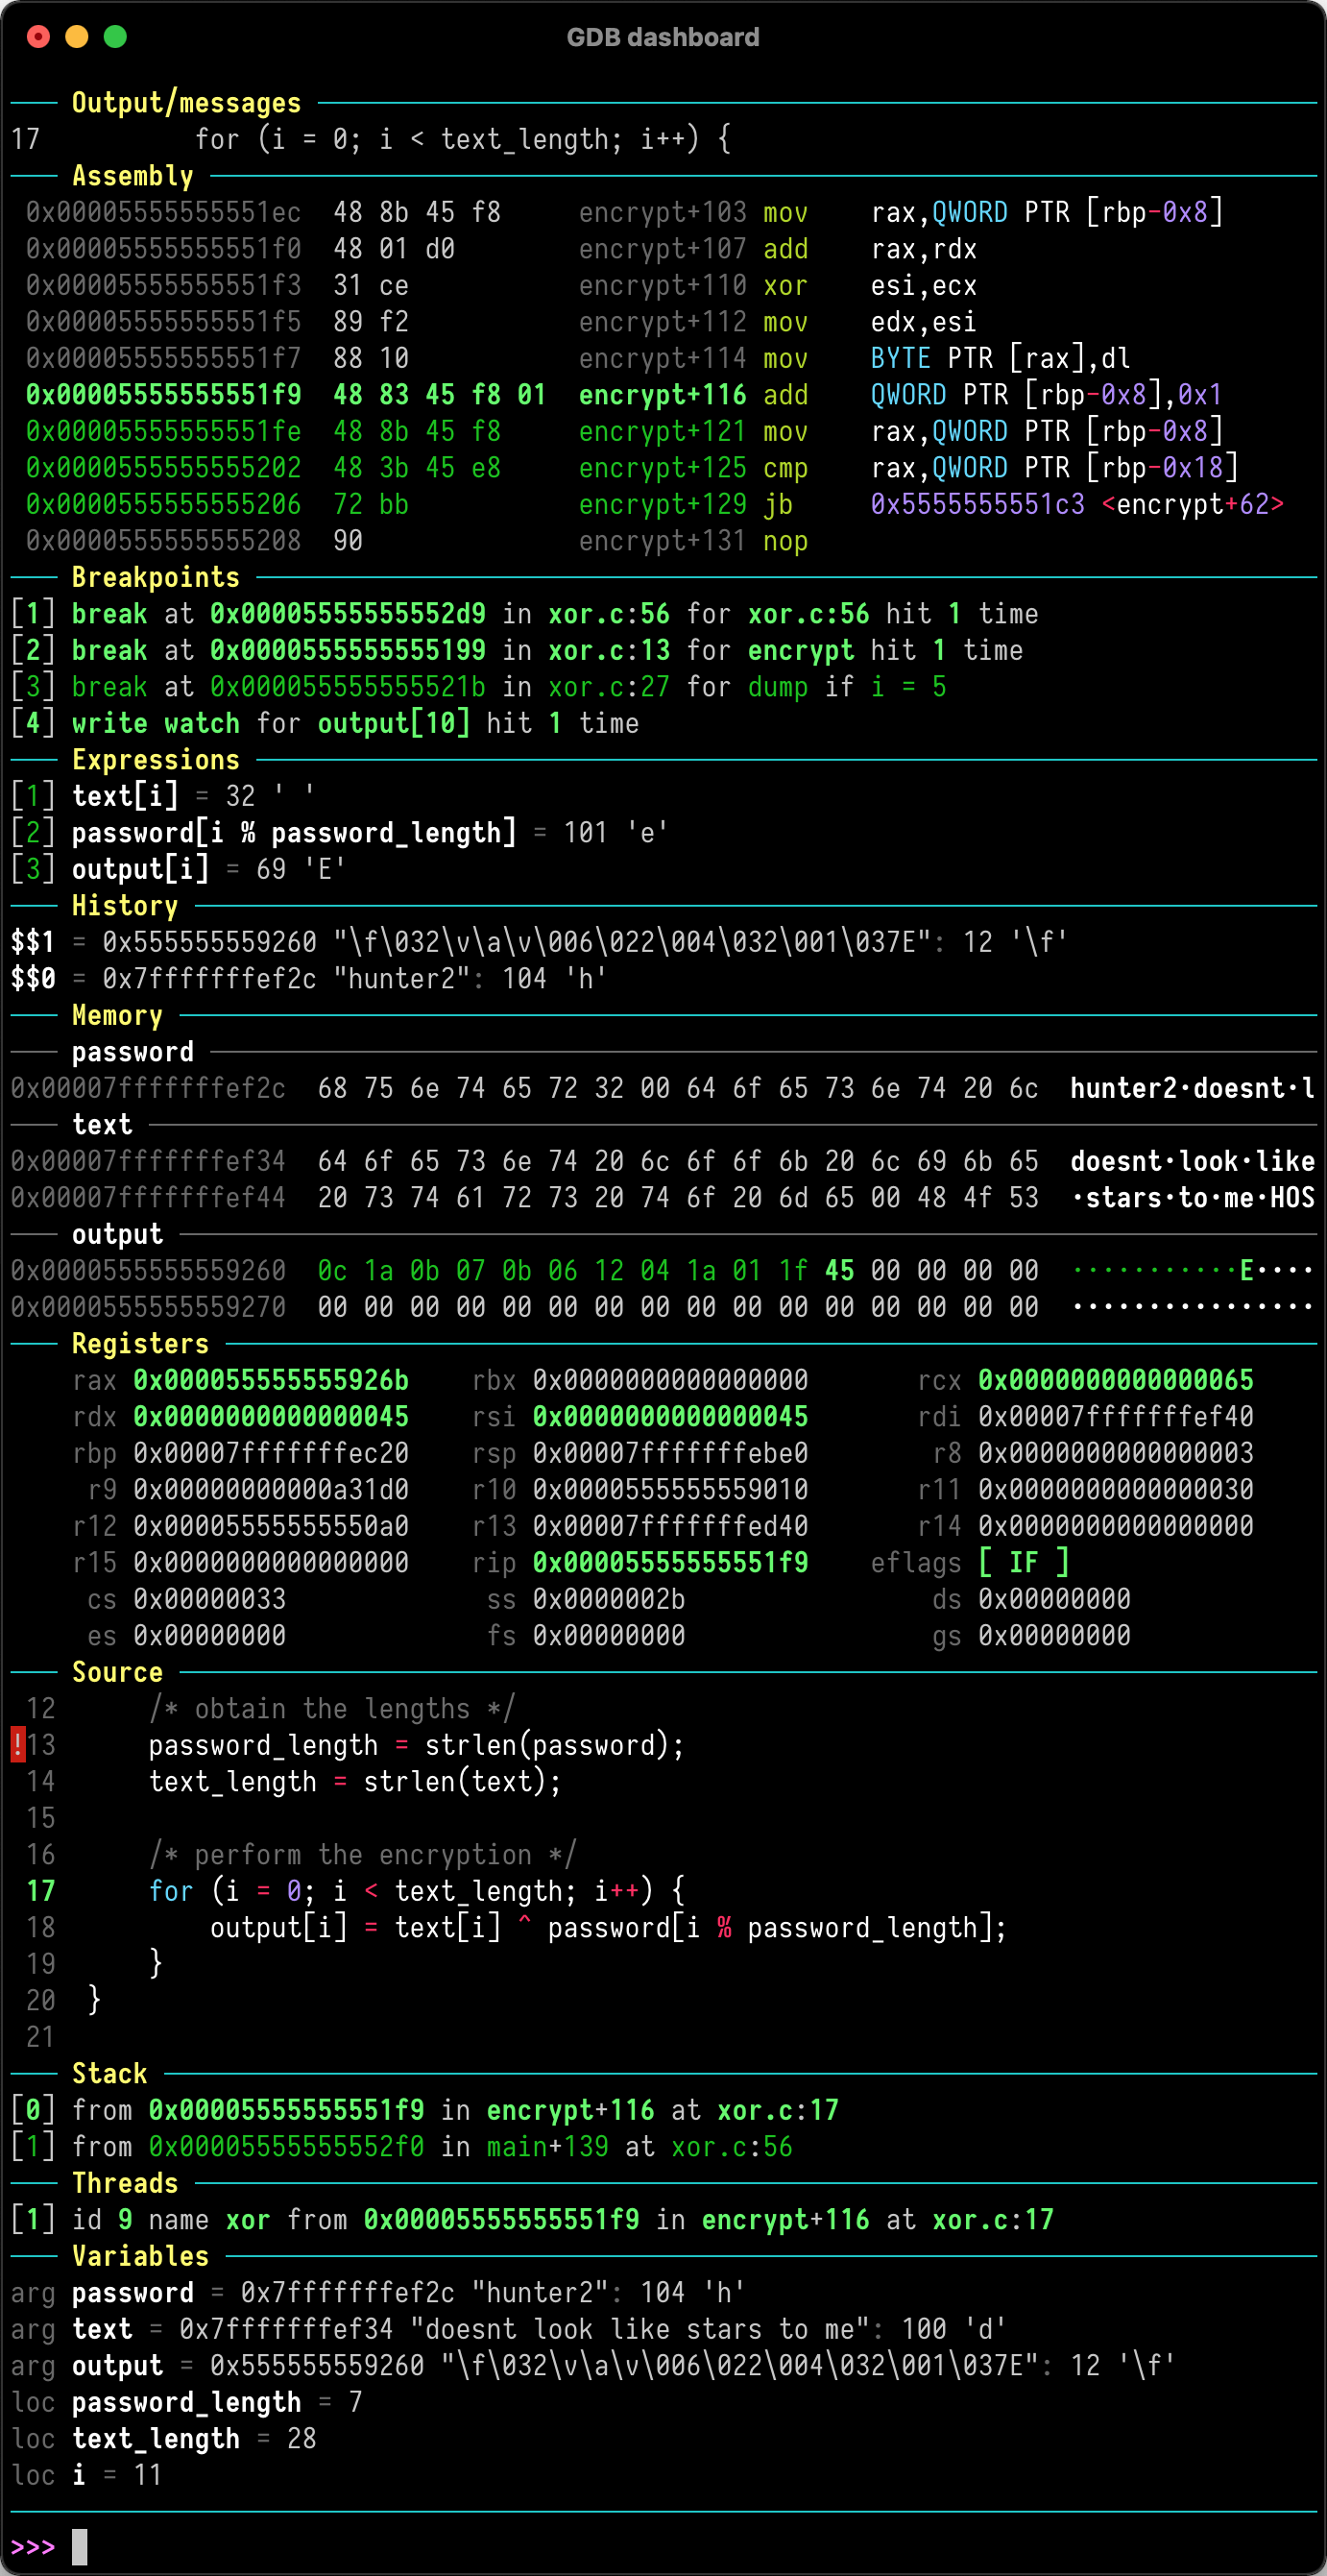 cyrus-and/gdb-dashboard
Modular GDB interface providing a visual dashboard with customizable panels for inspecting registers, source code, assembly, and program state during…
 ljagiello/ctf-skills
Agent skills for solving CTF challenges - web exploitation, binary pwn, crypto, reverse engineering, forensics, OSINT, and more
 riscv-software-src/riscv-isa-sim
Functional RISC-V ISA simulator supporting multiple extensions (RV32/64, V, cryptography) with interactive debug mode, GDB integration, and…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
 joernio/joern
Open-source code analysis platform for C/C++/Java/Binary/Javascript/Python/Kotlin based on code property graphs. Discord https://discord.gg/vv4MH284Hc
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
 0xz0f/z0fcourse_reverseengineering
Structured reverse engineering course covering x64 Windows binaries, assembly, debugging, and malware analysis. Designed for beginners to…
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
 longld/peda
PEDA - Python Exploit Development Assistance for GDB
 dosx-dev/obfus.h
Macro-header for compile-time C polymorphic obfuscation (tcc, win x86/x64)
 snare/voltron
Extensible debugger UI toolkit providing customizable register, disassembly, stack, memory, breakpoint, and backtrace views for LLDB, GDB, VDB, and…