RMS-Runtime-Mobile-Security

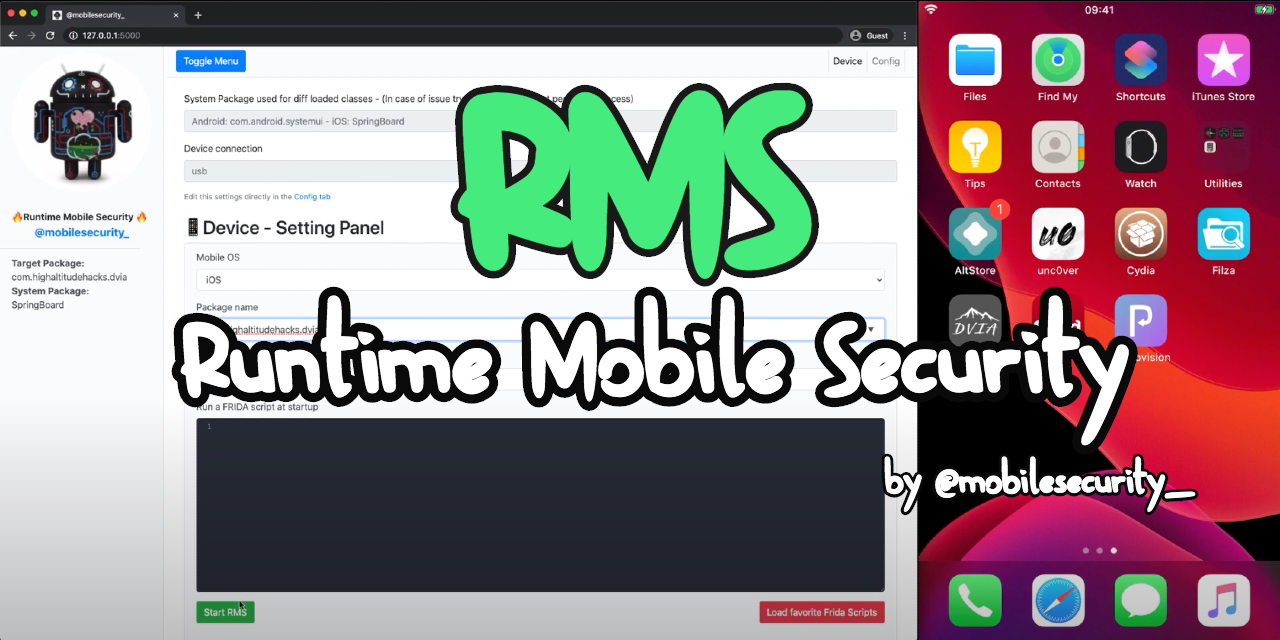
Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime

Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime

🤖 A CLI application that automatically prepares Android APK files for HTTPS inspection

APKinspector is a powerful GUI tool for analysts to analyze the Android applications.

Mediatek Flash and Repair Utility

A Virtual Machine For Assessing Android applications, Reverse Engineering and Malware Analysis

The new bridge between Burp Suite and Frida!

An intelligent reverse engineering analysis tool designed for multiple target platforms, currently supporting HarmonyOS (HAP/APP/ABC) and Android…

Binder Trace is a tool for intercepting and parsing Android Binder messages. Think of it as "Wireshark for Binder".

A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…

PoC Frida script to view Android libbinder traffic

C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…

Adaptation of CVE-2023-6241 for Google Pixel 7 from Google Pixel 8 taken from securitylab/SecurityExploits/Android/Mali/CVE_2023_6241


A tool that automates the mundane tasks of pentesting Android apps. It uses APKTool and Dex2Jar.

OPPO Find X6 Pro GhostLock (CVE-2026-43499) exploit adaptation

Android kernel CVE analysis and PoC for a MediaTek ION allocator type confusion, covering root-cause diffing, unprivileged trigger, and…

Android Reverse Engineering Framework

CVE-2026-43499 (GhostLock) adaptation for ASUS ROG Phone 5S — UAF trigger + pselect stack reclaim, KASLR leak blocked