

CVE-2018-18912
 themalwareguardian/cve-2018-18912
SEH-based buffer overflow in Easy File Sharing Web Server 7.2 demonstrating how an authenticated HTTP POST parameter can corrupt the exception…
binary-exploitationdebuggerseducation+6
1
themalwareguardian/cve-2018-18912SEH-based buffer overflow in Easy File Sharing Web Server 7.2 demonstrating how an authenticated HTTP POST parameter can corrupt the exception…
 themalwareguardian/cve-2025-34096
SEH-based buffer overflow in Easy File Sharing Web Server 7.2, reachable through the password recovery endpoint.
 nccgroup/dibf
Windows NT ioctl bruteforcer and modular fuzzer
 darioi/droidcarve
Android Reverse Engineering Framework
 tc4dy/cve-2026-87902-toolkit
WordPress CVE-2026-87902 LFI-to-RCE toolkit with a weaponized exploit chain (PEAR RCE, webshell, admin creation, loot) and a non-intrusive…
 nccgroup/mtk_bp
Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…
 reecdeep/hivev5_file_decryptor
Hive v5 file decryption algorithm
 icewall/cve-2016-2334
Exploit for CVE-2016-2334: heap overflow in 7zip's HFS+ archive parser. Includes HFS+ file generator and WinDbg heap analysis scripts for debugging…
 s3n4t0r-0x0/pixelcode-attack
Malicious PixelCode is a security research project that demonstrates a covert technique for encoding executable files into pixel data and storing…
 fortra/cve-2023-28252
Technical analysis and proof-of-concept exploit for CVE-2023-28252, a Windows Common Log File System (CLFS) driver privilege escalation vulnerability…
 pl4tyz/cve-2025-14611-centrestack-and-triofox-full-poc-exploit
CVE-2025-14611 CentreStack and Triofox full Poc/Exploit
 azefzafyoussef/cve-2026-34621
Research PoC demonstrating a prototype pollution and JavaScript injection chain in Adobe Acrobat Reader, enabling privileged JavaScript execution and…
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 themalwareguardian/cve-2025-70330
Easy Grade Pro 4.1 file parsing bug used as an educational example to show how beginners can start vulnerability research through reverse engineering.
 nccgroup/driverbuddy
DriverBuddy is an IDA Python script to assist with the reverse engineering of Windows kernel drivers.
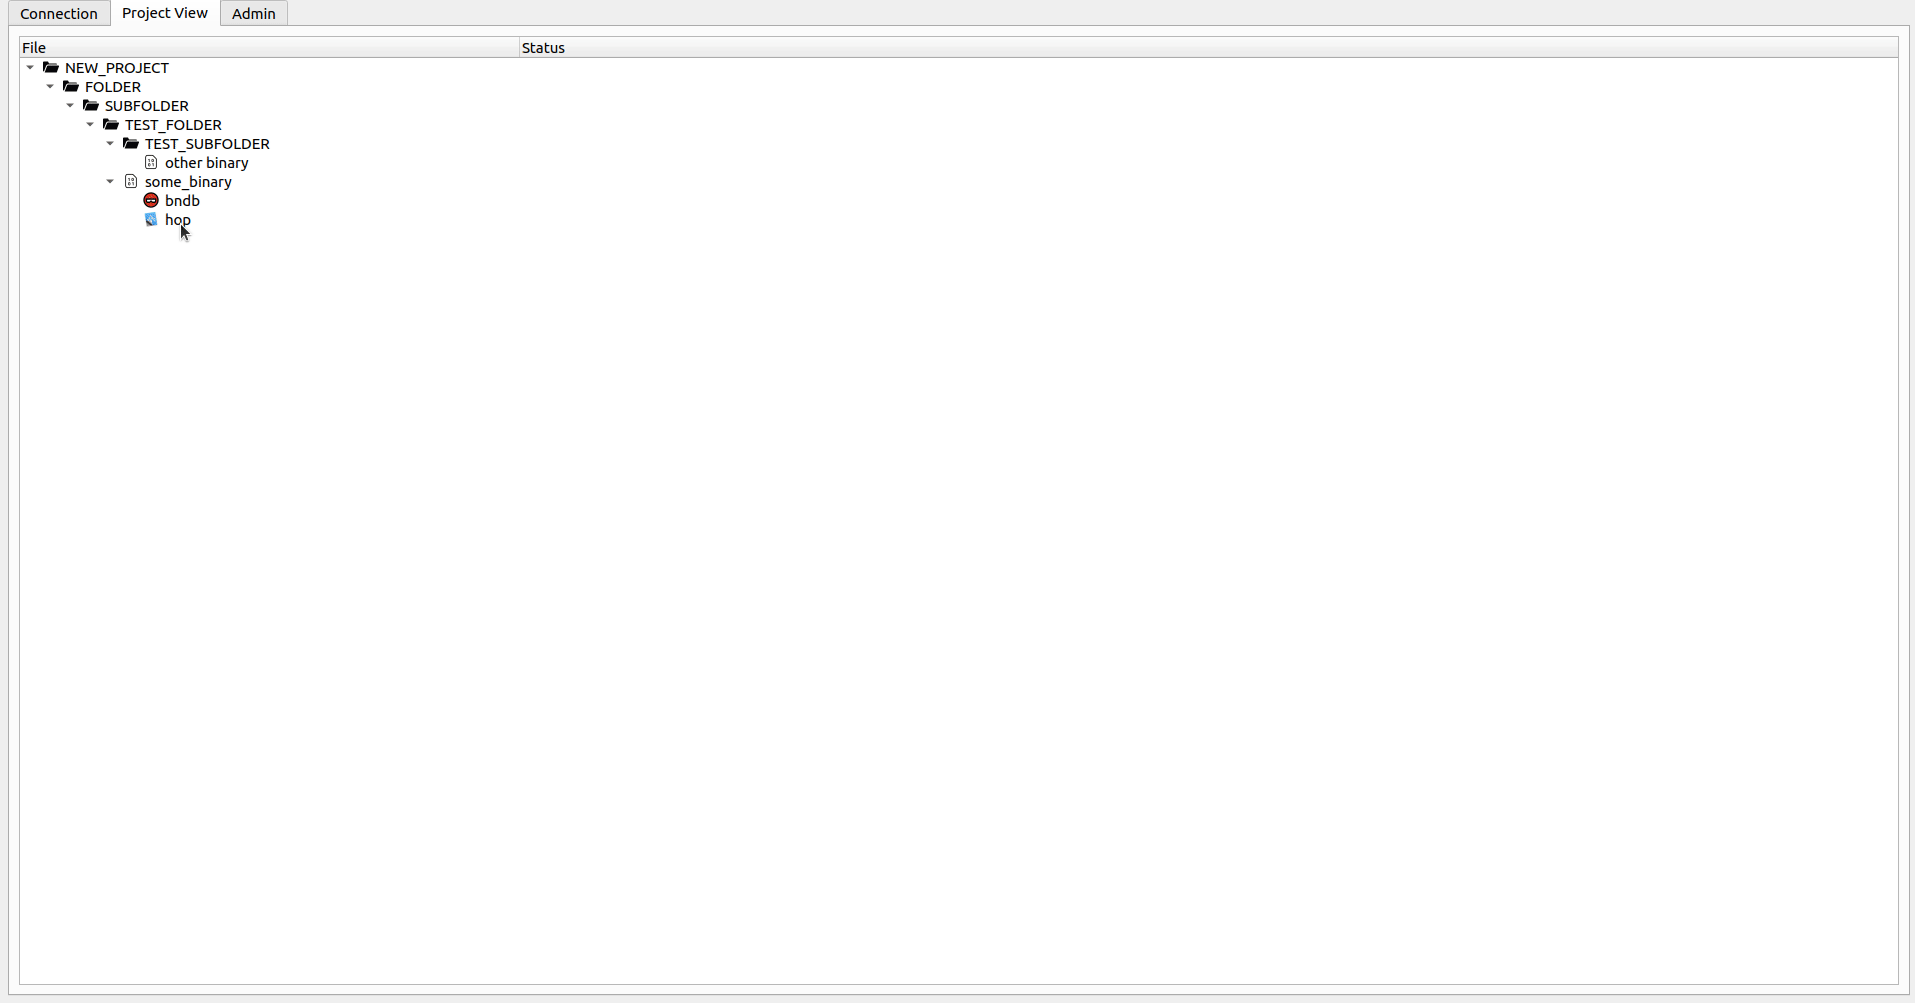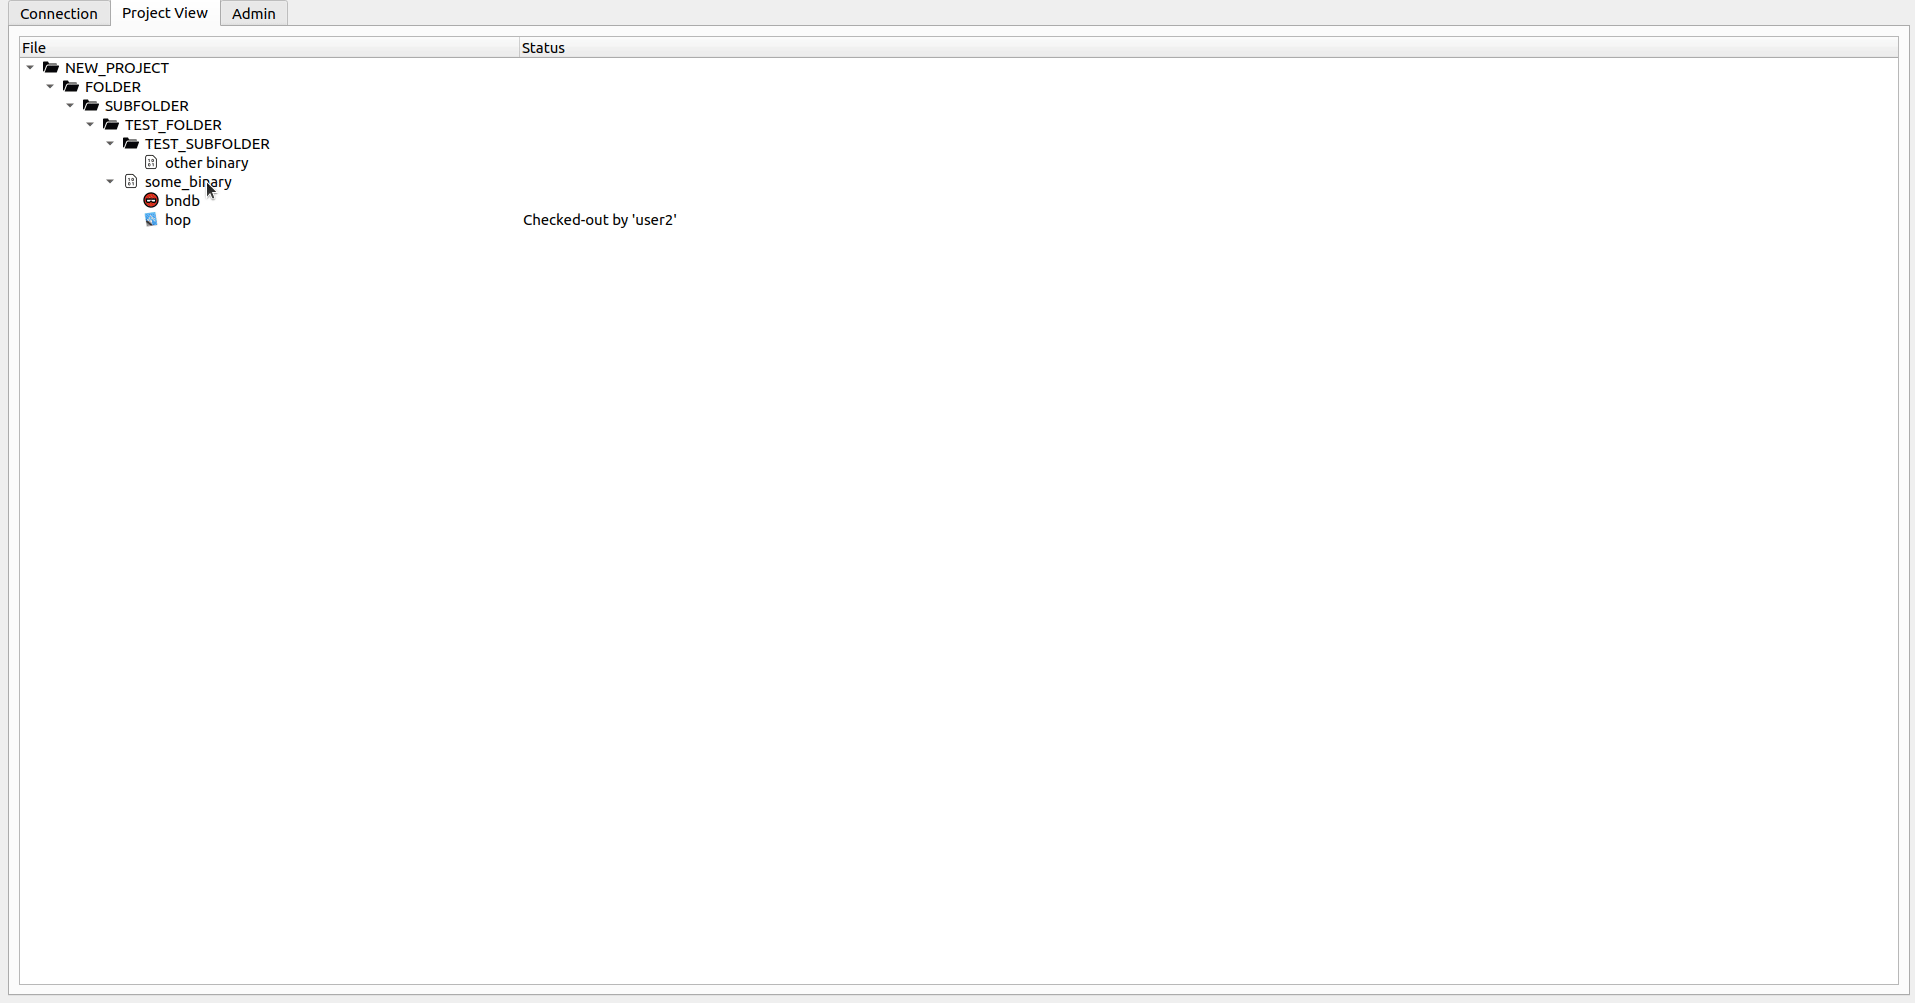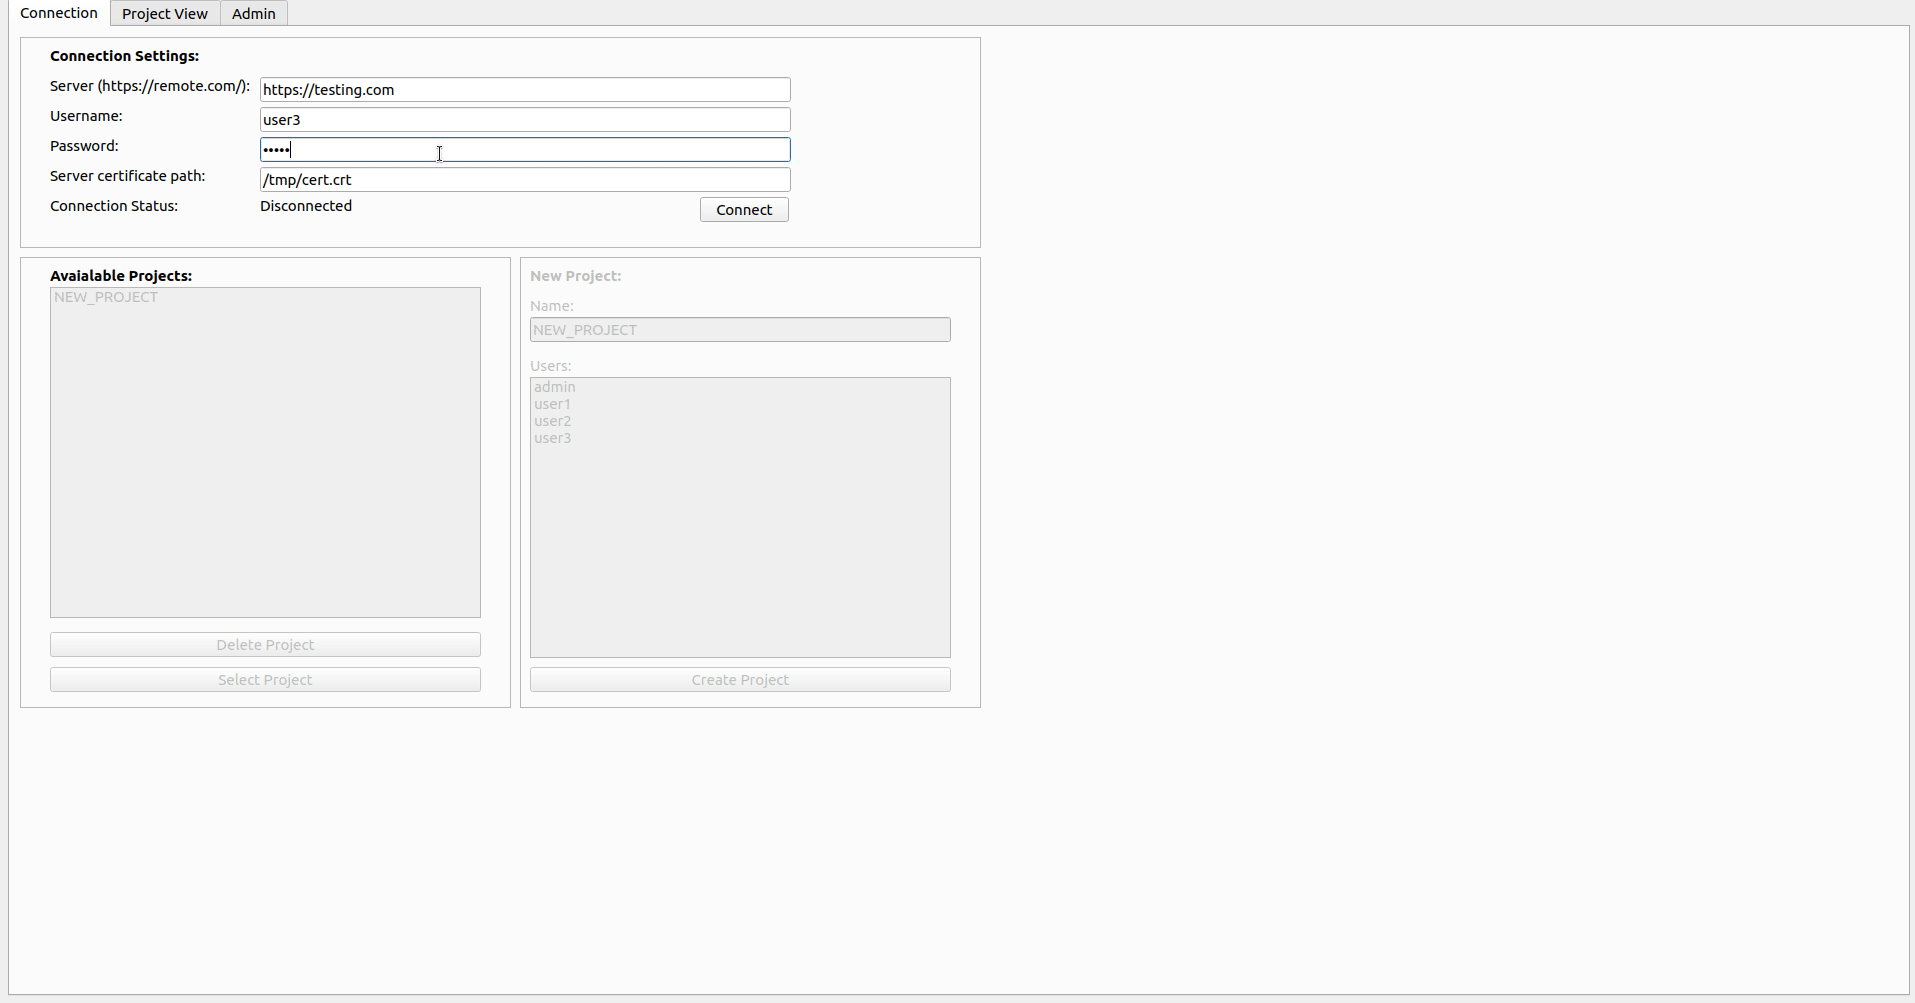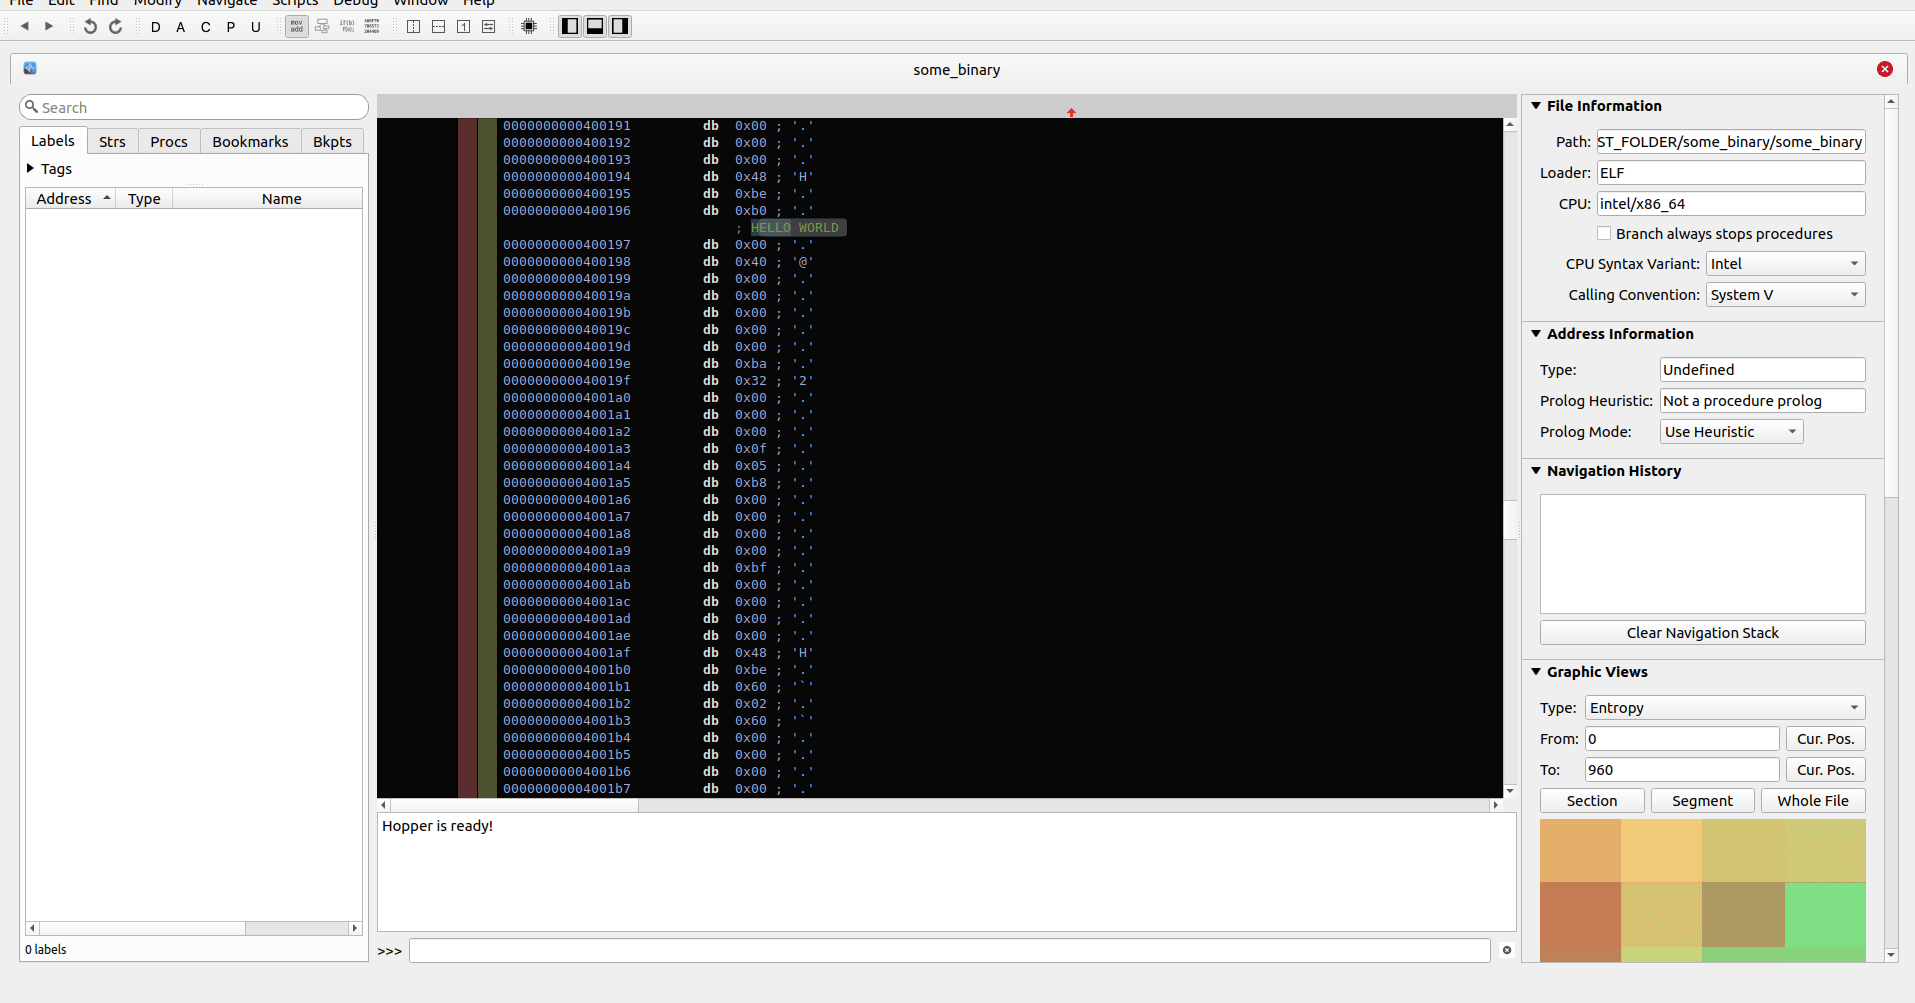 martyx00/collare
Multi-tool reverse engineering collaboration solution.
 euva-project/euva
A lightweight hex editor and decompiler to solve your binary file analysis problems.