
vmlinux-to-elf
 marin-m/vmlinux-to-elf
A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)
binary-analysisembedded-systems-securityfirmware-analysis+1
1.8k
marin-m/vmlinux-to-elfA tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)
 justasmasiulis/lazy_importer
library for importing functions from dlls in a hidden, reverse engineer unfriendly way
 mandiant/flare-learning-hub
Free educational content on reverse engineering and malware analysis from the FLARE team
 vxunderground/vxug-papers
Research code & papers from members of vx-underground.
 withsecurelabs/python-exe-unpacker
A helper script for unpacking and decompiling EXEs compiled from python code.
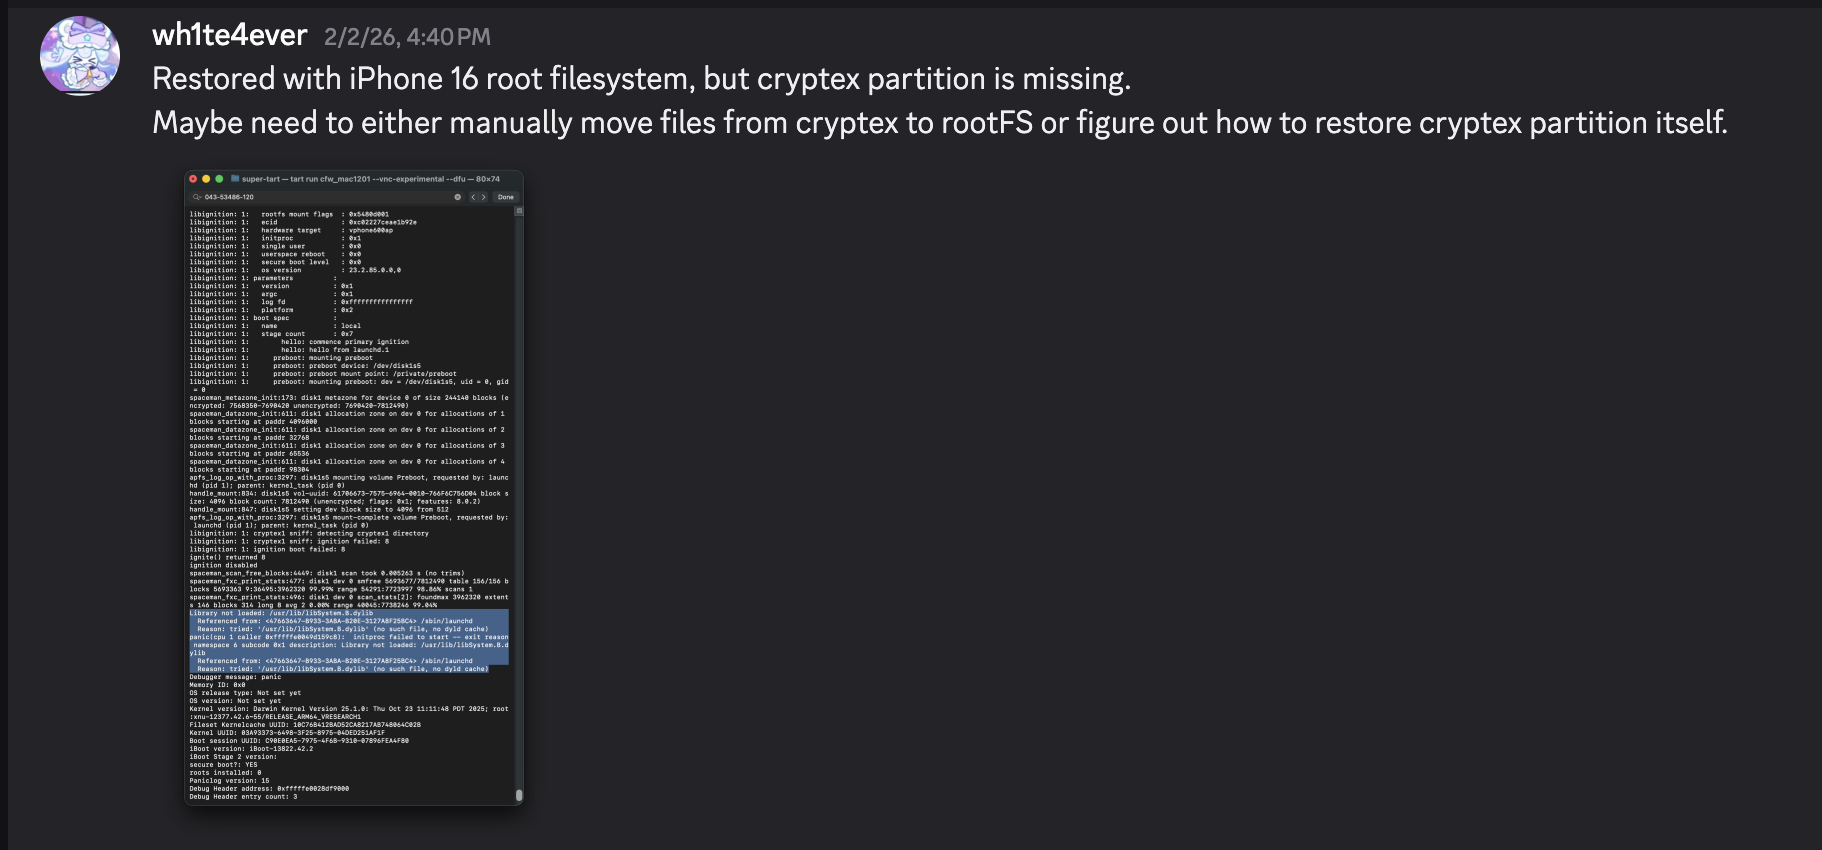 wh1te4ever/super-tart-vphone-writeup
Guide to building a virtual iPhone using VPHONE600AP components from Apple's PCC firmware, with firmware patching, bootchain modification, and kernel…
 sentinel-one/cobaltstrikeparser
Python parser for extracting CobaltStrike Beacon configurations from PE files, memory dumps, and C2 URLs using heuristic XOR decryption and…
 reversenseorg/dexcalibur
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
 grammatech/ddisasm
Datalog-based disassembler producing reassemblable assembly from ELF/PE binaries, with GTIRB intermediate representation for binary analysis and…
 rocky/python-decompile3
Python decompiler for 3.7-3.8 Stripped down from uncompyle6 so we can refactor and start to fix up some long-standing problems
 bignerd95/chimay-red
Working POC of Mikrotik exploit from Vault 7 CIA Leaks
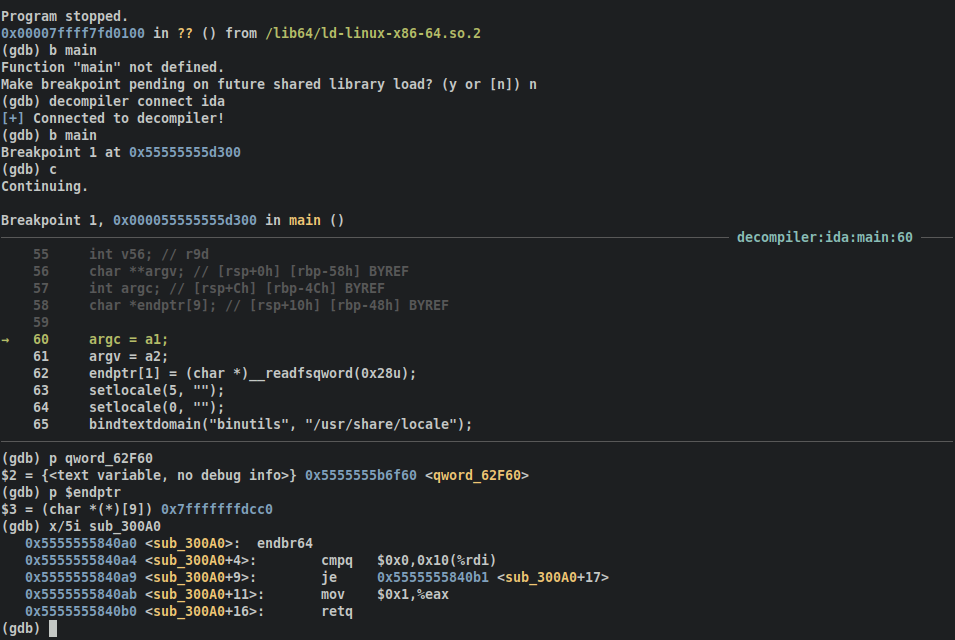 mahaloz/decomp2dbg
A plugin to introduce interactive symbols into your debugger from your decompiler
 rampagex/firmware-mod-kit
Automatically exported from code.google.com/p/firmware-mod-kit
 zealraj/cybersecurity-books
Here you will get awesome collection of mostly all well-known and usefull cybersecurity books from beginner level to expert for all cybersecurity…
 lunixbochs/patchkit
binary patching from Python
 netzob/netzob
Open-source toolkit for reverse engineering, modeling, and fuzzing communication protocols. Infers message formats and state machines from network…
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
 elttam/publications
Offensive security research hub aggregating original vulnerability advisories, CVE proof-of-concept exploits, conference talks, and internal tooling…