
frida-ipa-extract
 lautarovculic/frida-ipa-extract
Robust Frida-based tool to dump decrypted iOS apps as .ipa from a jailbroken device supports App Store, sideloaded and system.
information-gatheringios-securitymobile-app-pentesting+3
111
lautarovculic/frida-ipa-extractRobust Frida-based tool to dump decrypted iOS apps as .ipa from a jailbroken device supports App Store, sideloaded and system.
 finngineering/apxutil
A tool to manipulate Schneider Electric PLC archive files
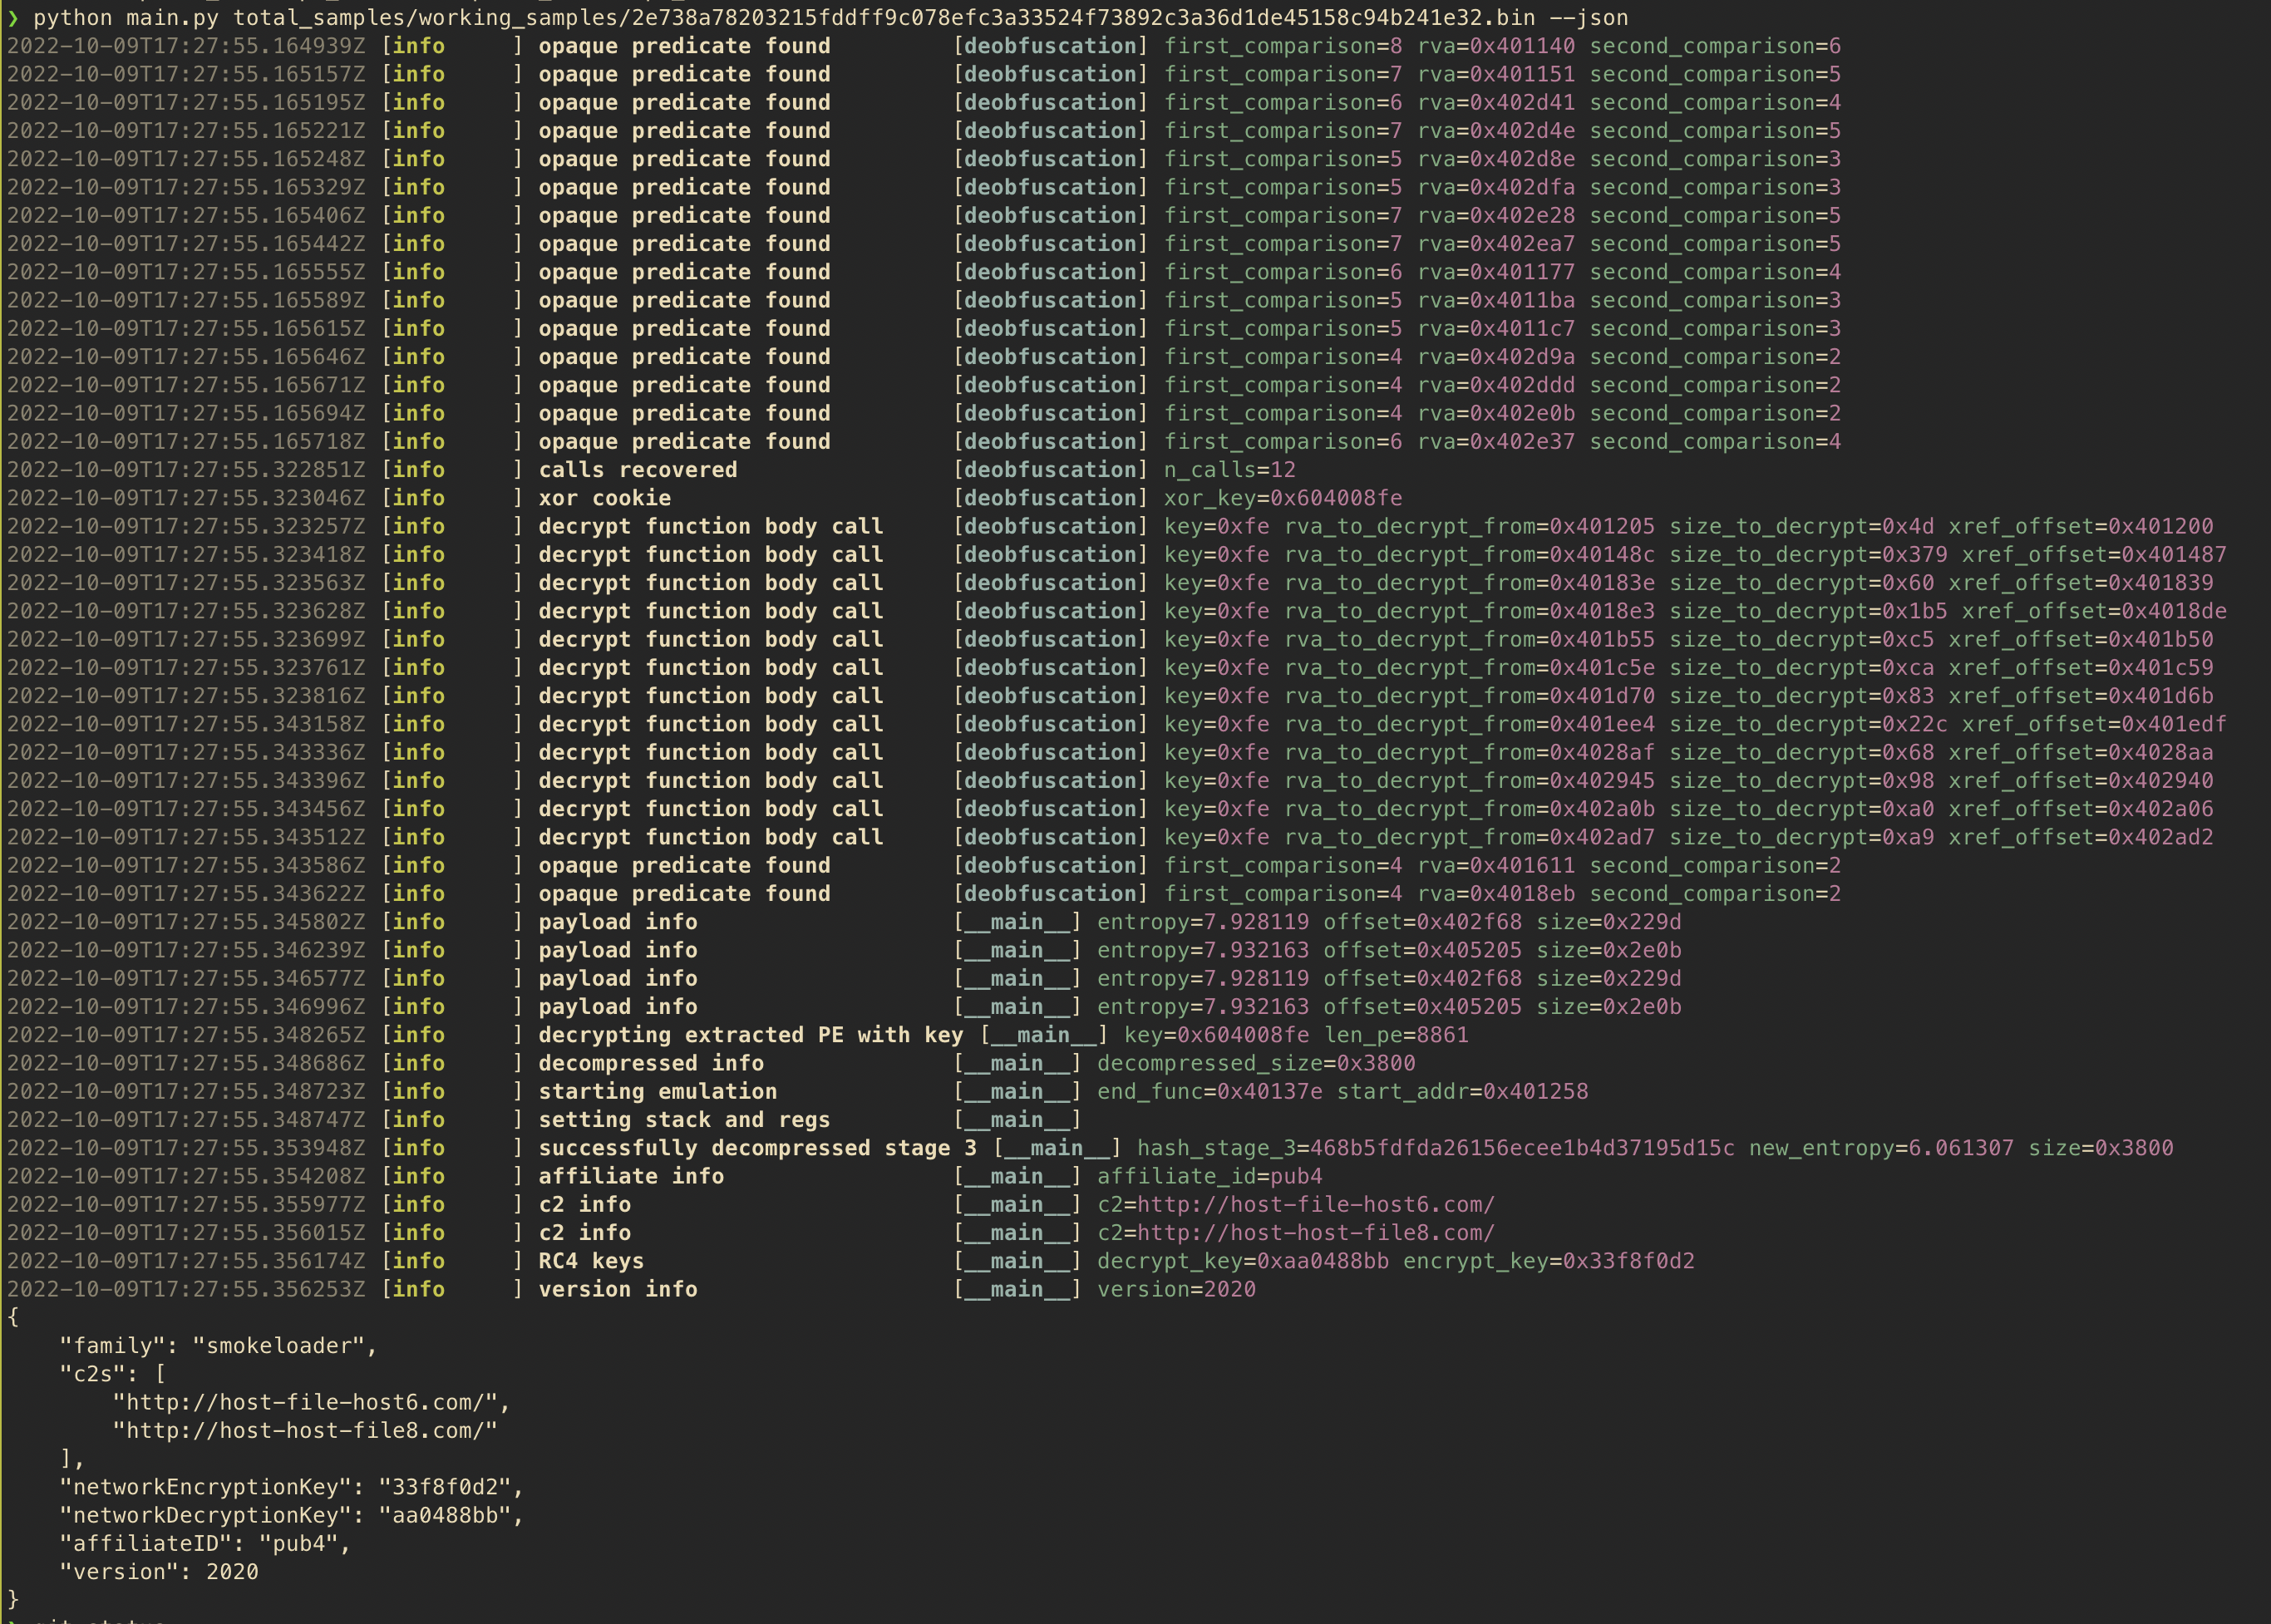 myrtus0x0/smoke_conf_extract
Static config extractor for SmokeLoader samples that deobfuscates, unpacks, and emulates protected routines to recover final-stage C2 settings.
 fuzzinglabs/octopus
Security Analysis tool for WebAssembly module (wasm) and Blockchain Smart Contracts (BTC/ETH/NEO/EOS)
 echo-devim/fhex
A Full-Featured HexEditor compatible with Linux/Windows/MacOS
 uofw/uofw
The unofficial Official FirmWare, a complete latest PSP firmware reverse engineering project
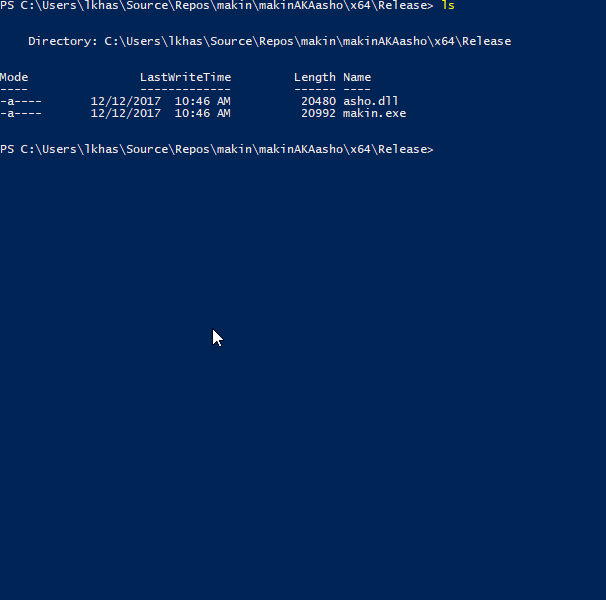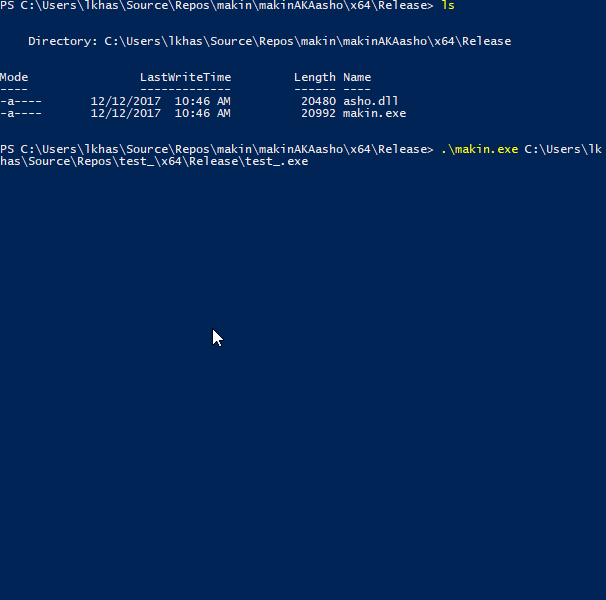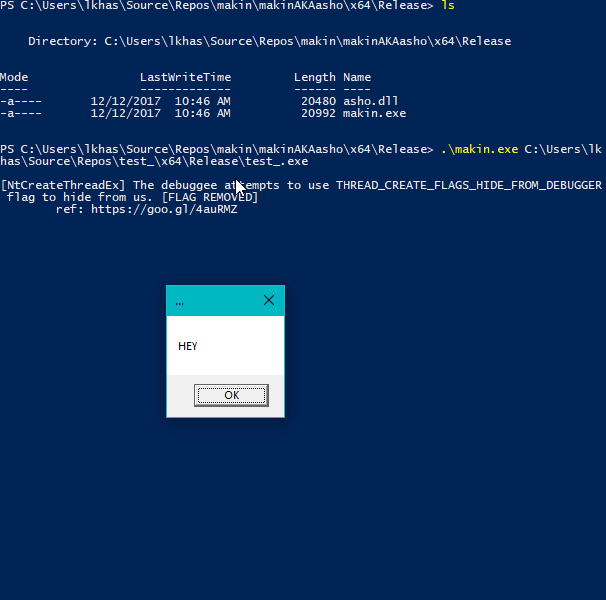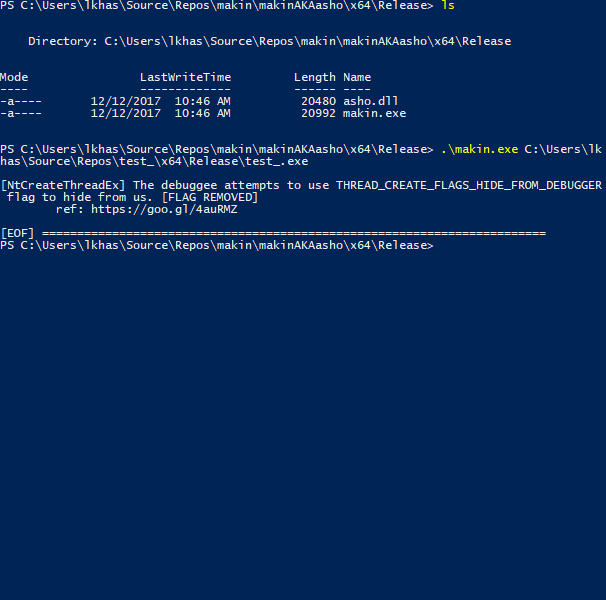 secrary/makin
makin - reveal anti-debugging and anti-VM tricks [This project is not maintained anymore]
 secrary/idenlib
idenLib - Library Function Identification [This project is not maintained anymore]
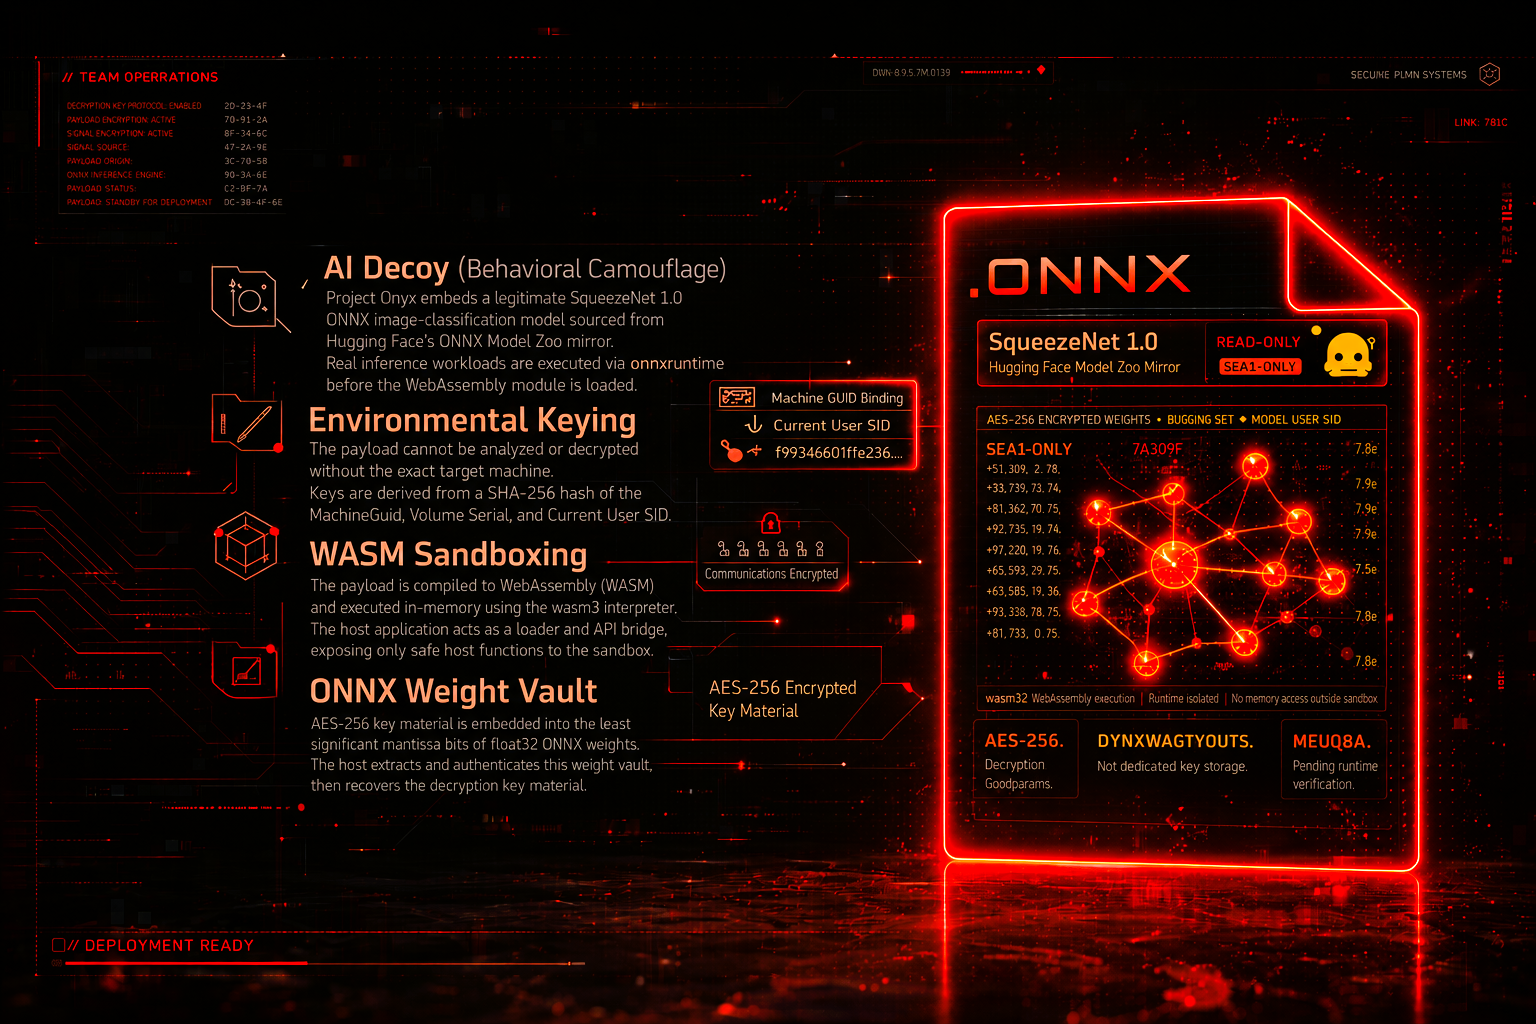 x-3306/project-onyx
Advanced EDR Evasion via AI Telemetry Spoofing & WASM Sandboxing. Project Onyx is a PoC Red Team pipeline designed to demonstrate advanced evasion…
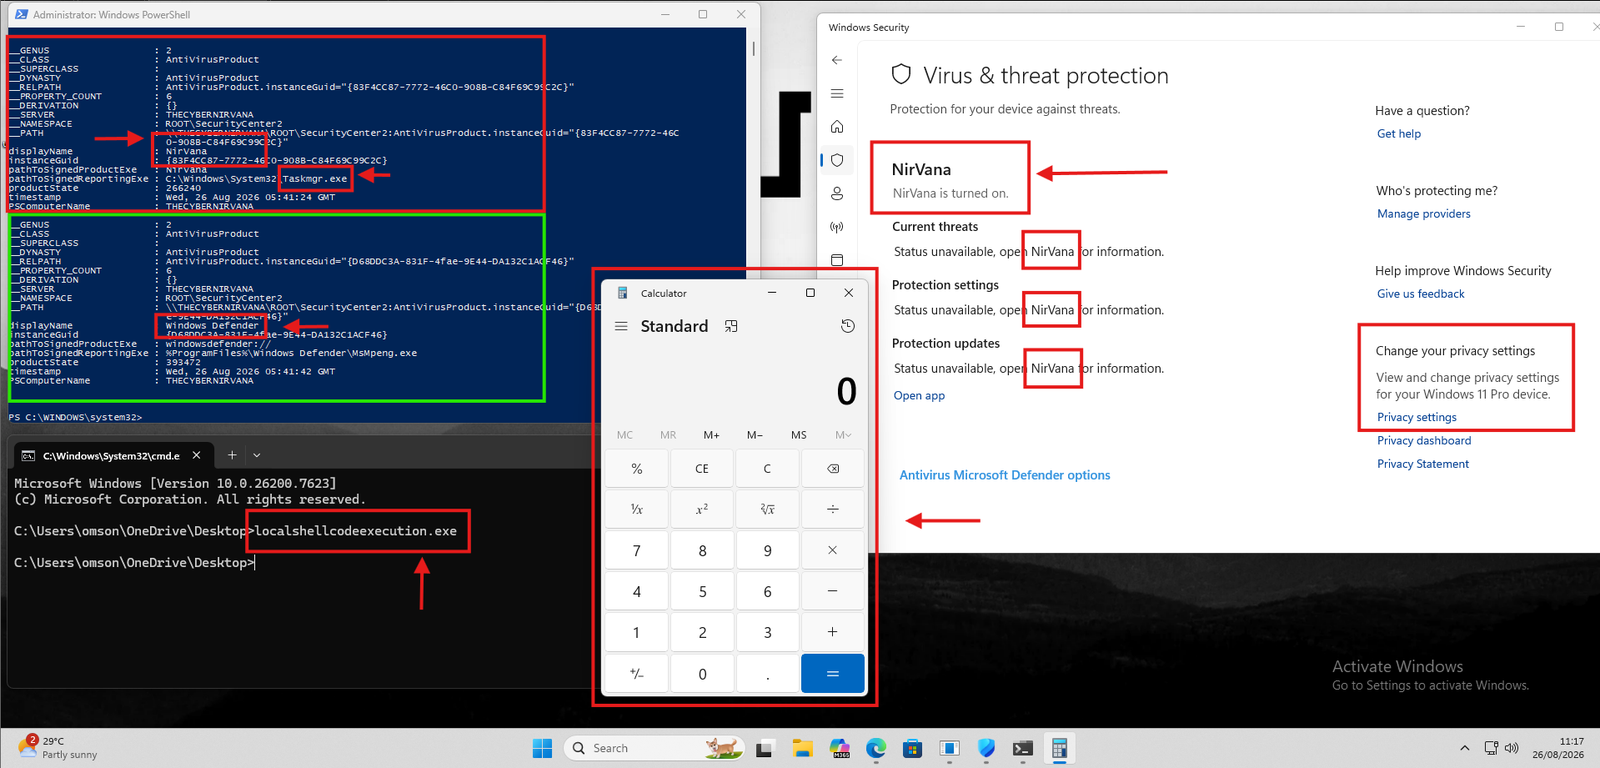 nirvanaon/own-defender
Research project reverse-engineering Windows Security Center COM interfaces to trace AV registration through ATL, vtable, WSCAPI, and RPC, with…
 owasp/mas-crackmes
The MAS Crackmes aka. UnCrackable Apps, a collection of mobile reverse engineering challenges part of the OWASP MAS project.
 canomer/cve-2025-54110-kernel-eop-poc
Project Date : Oct 2025 / PoC implementation for CVE-2025-54110 a Kernel-Level Integer Overflow Vulnerability in the Windows `NtQueryDirectoryObject`…
 vivianuba/grandstream-cve-2026-2329-analysis
Defensive vulnerability-research project comparing vulnerable and patched Grandstream GXP1600 firmware for CVE-2026-2329, using SquashFS extraction,…
 librepods-org/librepods
AirPods liberated from Apple's ecosystem.
 ashishb/android-security-awesome
A collection of android security related resources
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 pxb1988/dex2jar
Tools to work with android .dex and java .class files
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…