
Winstrument
 nccgroup/winstrument
Winstrument is a framework of modular scripts to aid in instrumenting Windows software using Frida for reverse engineering and attack surface…
binary-analysisdynamic-code-analysisreverse-engineering+1
68
nccgroup/winstrumentWinstrument is a framework of modular scripts to aid in instrumenting Windows software using Frida for reverse engineering and attack surface…
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
 tandasat/tandasat.github.io
Remote hypervisor development class for security researchers; covers virtualization internals, hypervisor security, and vulnerabilities in privileged…
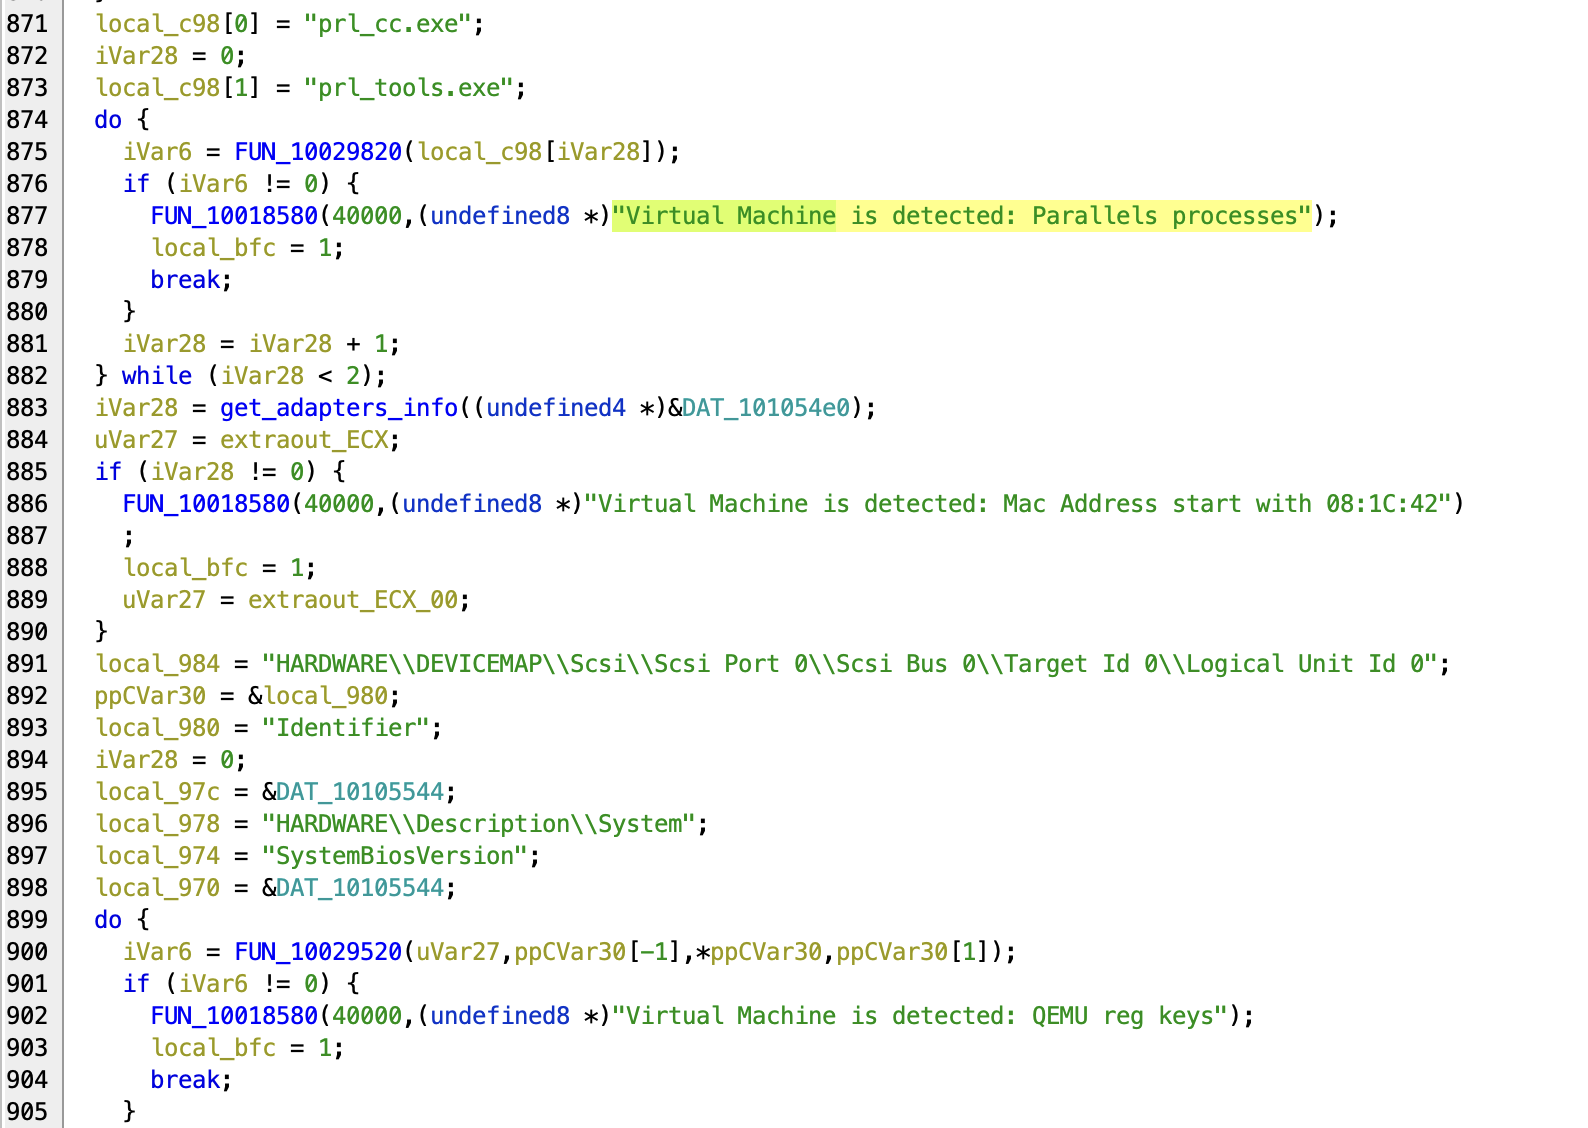 lodi-g/cve-2023-33668
Technical analysis and proof-of-concept bypass for CVE-2023-33668 in DigiExam proctoring software, demonstrating weak VM detection and native module…
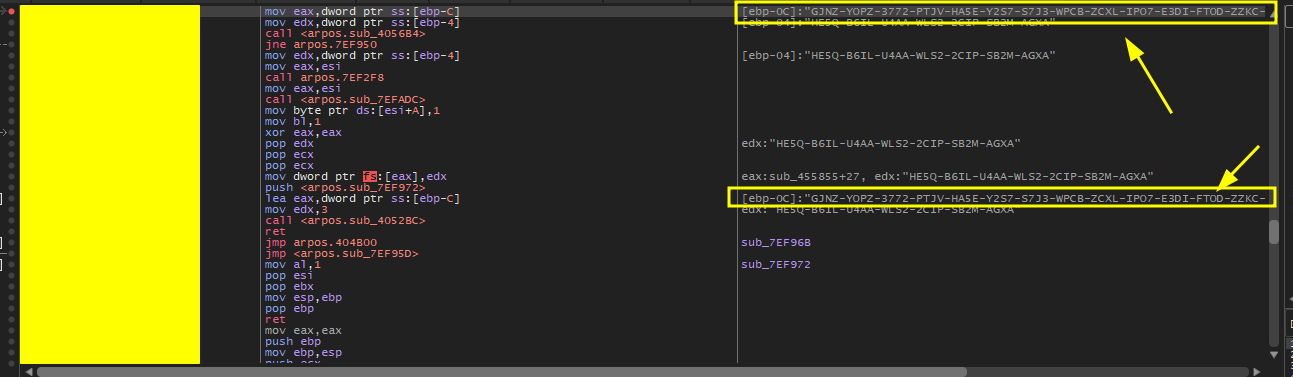 yonathanpy/cve-2025-65320
CVE-2025-65320 proof-of-concept demonstrating cleartext license key extraction from process memory via debugger attachment, enabling software…
 ugvxb/cve-2026-9789
A critical local privilege escalation vulnerability has been discovered in Acer NitroSense software (PSAdminAgent.exe). The vulnerability allows any…
 mandiant/flare-qdb
Command-line and Python debugger for instrumenting and modifying native software behavior on Windows and Linux.
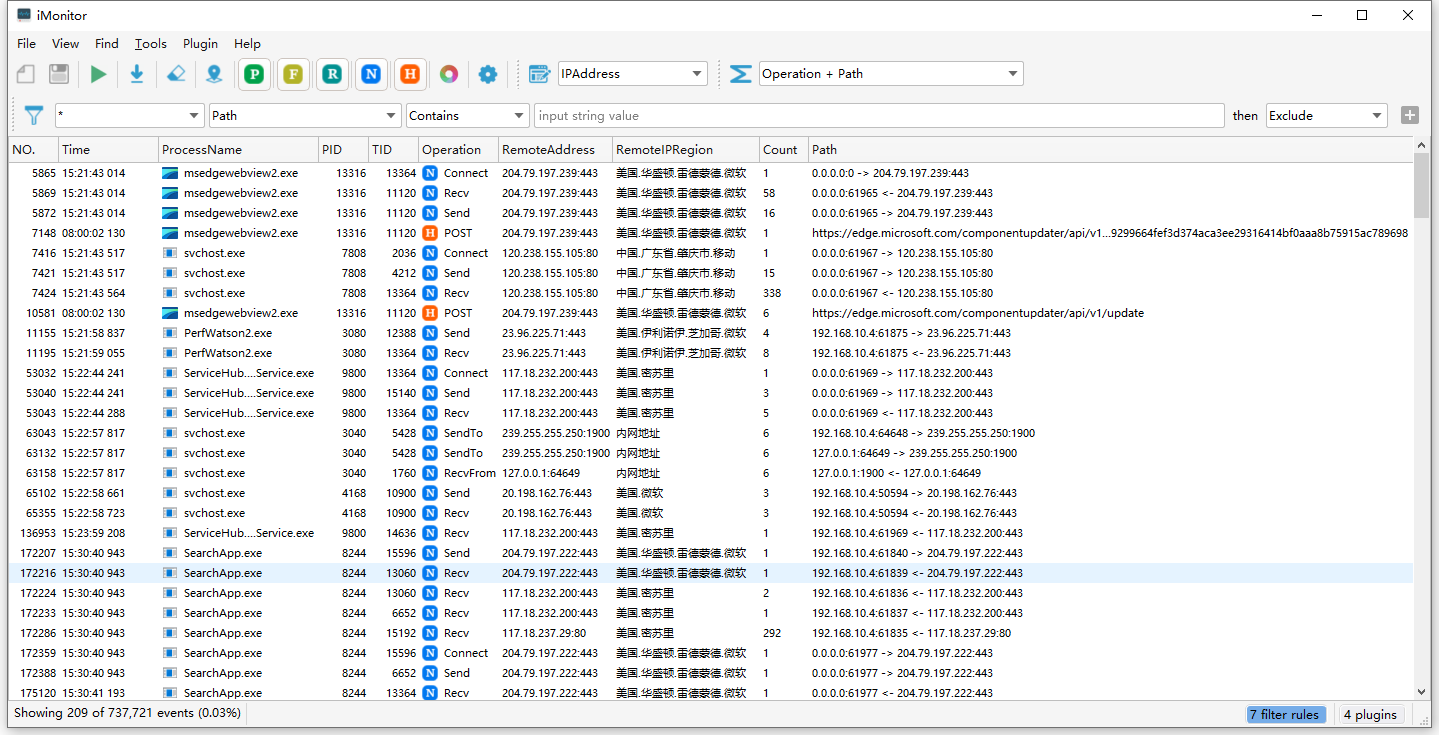 wecooperate/imonitor
Endpoint behavior monitoring and analysis system for processes, files, registry, and networks. Supports scripting, extensions, and plugins for…
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
 gaasedelen/lighthouse
A Coverage Explorer for Reverse Engineers
 greatscottgadgets/facedancer
Implement your own USB device in Python, supported by a hardware peripheral such as Cynthion or GreatFET
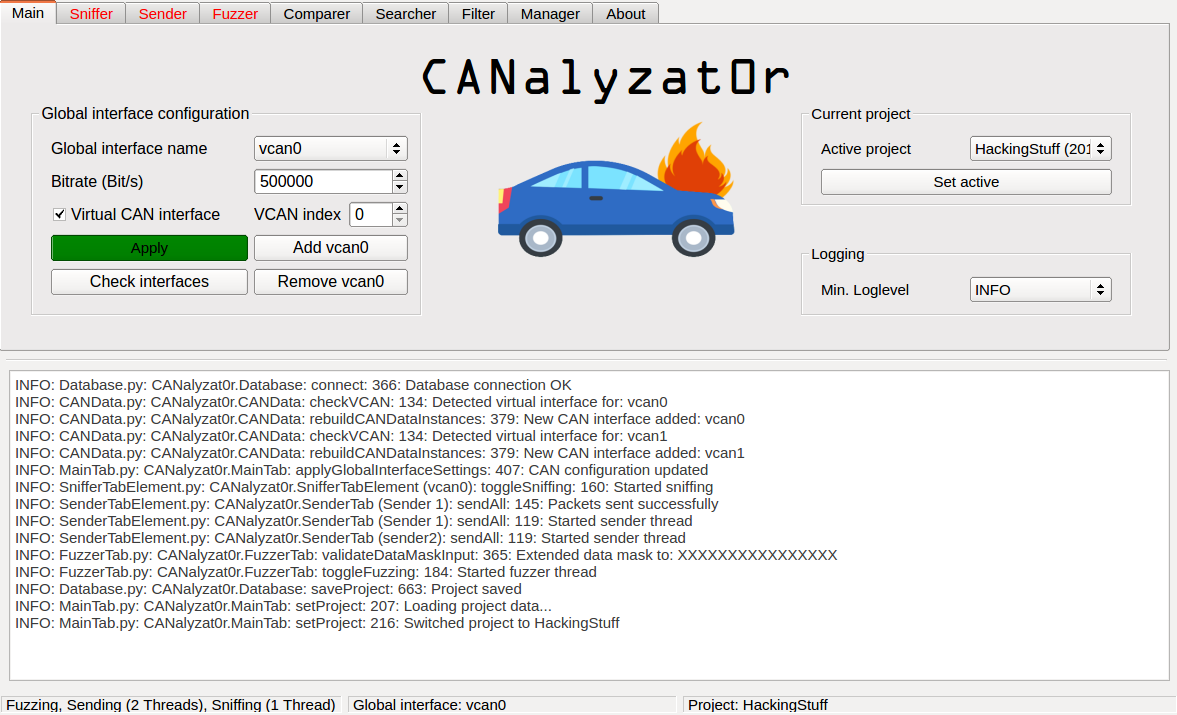 schutzwerk/canalyzat0r
Security analysis toolkit for proprietary car protocols
 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 quarkslab/conf-presentations
Quarkslab conference talks
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
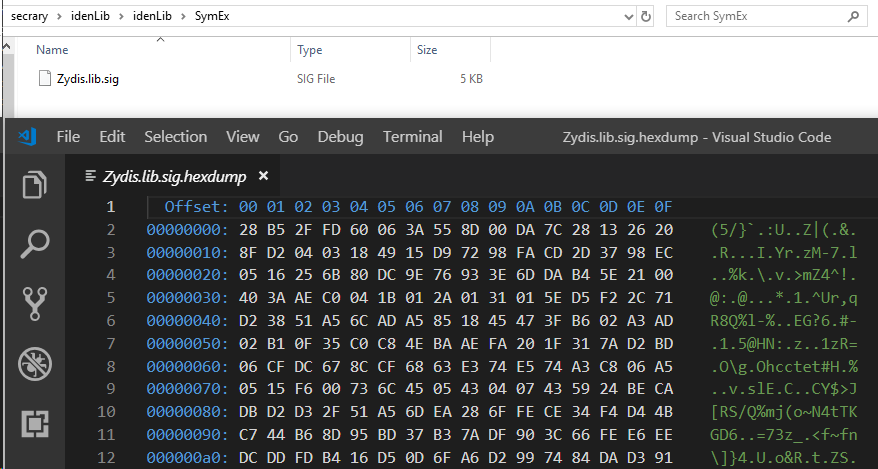 secrary/idenlib
idenLib - Library Function Identification [This project is not maintained anymore]