Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
60 results
spectrIDA-Reverse_Engineering_Stack preview

spectrIDA-Reverse_Engineering_Stack

GitHubggfuchsi-oss/spectrida-reverse_engineering_stack

Parallel IDA Pro binary analysis with AI-powered function naming, Neo4j knowledge graph, and phantomrt emulation/hooking/fuzzing engine for automated…

ai-assisted-reversingbinary-analysisctf+8
64
3 months ago
yamaha-smaf-player preview

yamaha-smaf-player

GitHubakustikrausch/yamaha-smaf-player

A dependency-free C++ PLAYER for Yamaha SMAF (.mmf) ringtones: the polyphonic-ringtone format of the 2000s MA-3 / MA-5 phone chips, rebuilt with its…

embedded-systems-securityfirmware-analysishardware-security+1
723 months ago
AutoPiff preview

AutoPiff

GitHubsplintersfury/autopiff

Semantic analysis engine for detecting vulnerability fixes in Windows kernel driver patches — 58 YAML rules, Ghidra decompilation, reachability…

binary-analysisexploitationfirmware-analysis+4
677 months ago
ft9201-libfprint preview

ft9201-libfprint

GitHubomgrant/ft9201-libfprint

Linux libfprint driver for the Focal-systems FT9201 (2808:93a9) USB fingerprint reader — runs FocalTech's own Windows matching engine natively on…

authenticationbinary-analysisembedded-systems-security+4
273 months ago
IntelTXE-PoC preview

IntelTXE-PoC

GitHubxenokovah/inteltxe-poc

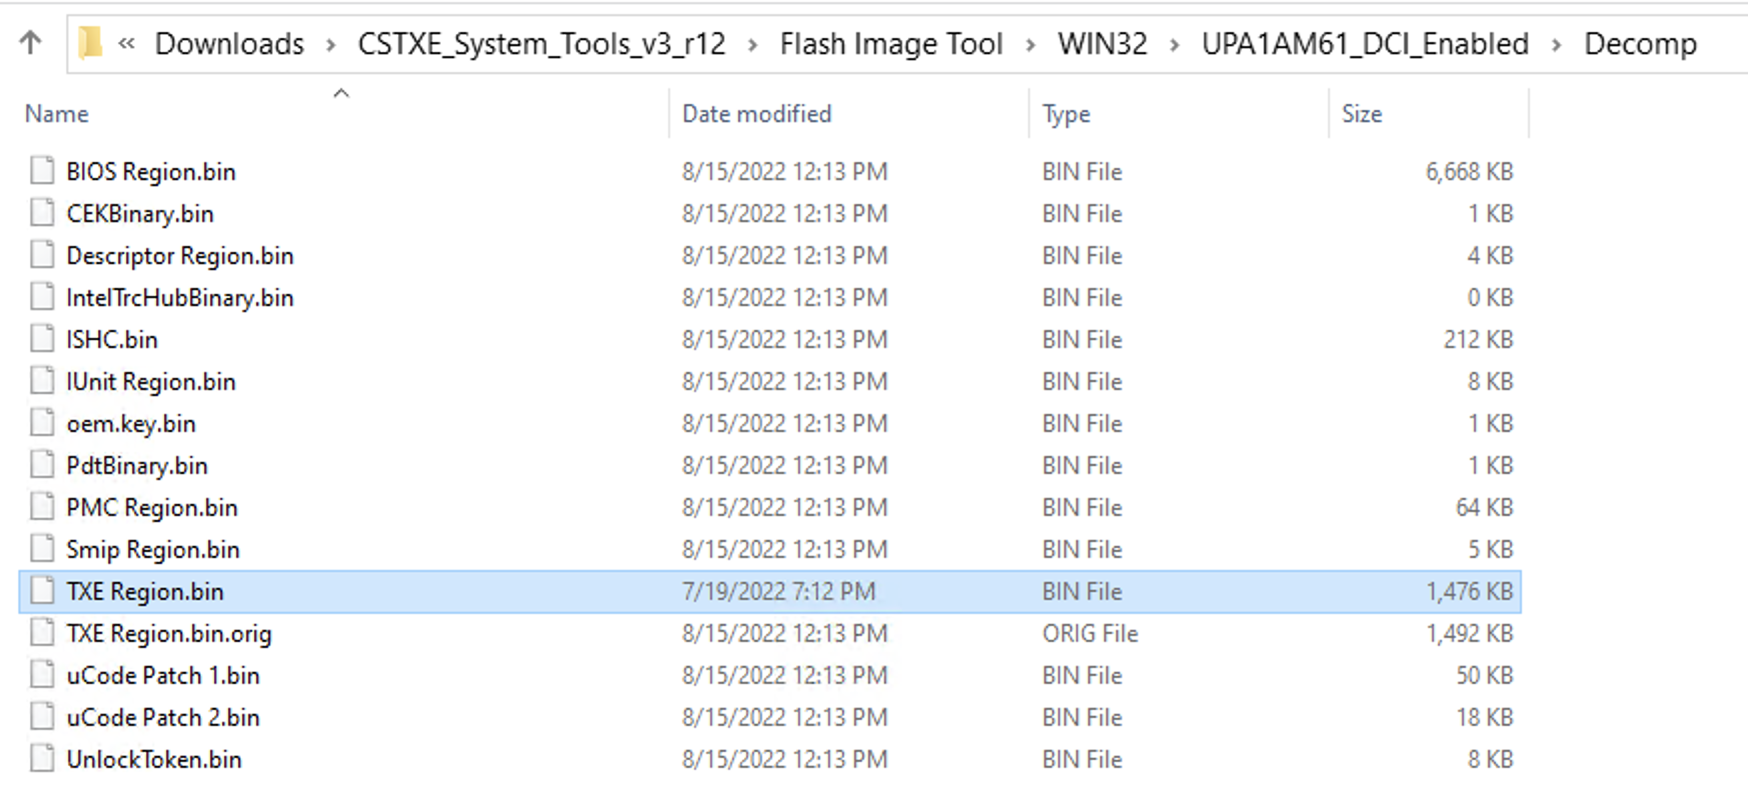
Intel Management Engine JTAG Proof of Concept - 2022 Instructions

binary-analysisbinary-exploitationembedded-systems-security+5
324 years ago
intel-me-research preview

intel-me-research

GitHubjatinkapilaq1/intel-me-research

Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…

binary-analysisembedded-systems-securityfirmware-analysis+4
172 months ago
ReflectivePluginLoader preview

ReflectivePluginLoader

GitHubracoten/reflectivepluginloader

Reflective PE mapper and evasion-hardened module stomping engine for Windows x64

binary-exploitationdefensive-toolseducation+7
84 days ago
RPC-Triage preview

RPC-Triage

GitHubtalha-nazeef-ahmed/rpc-triage

A zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.

binary-analysisreconnaissancered-teaming+3
151 month ago
entropystrip preview

entropystrip

GitHubdwexi/entropystrip

Algorithmic PE de-obfuscator, Shannon entropy radar, and incident triage engine

binary-analysisdefensive-toolsdigital-forensics+6
84 days ago
toy-wasm-symbexp preview

toy-wasm-symbexp

GitHubsynacktiv/toy-wasm-symbexp

A toy symbolic execution engine, supporting the blog article ...

binary-analysisctfeducation+1
185 years ago
Prineo_RE preview

Prineo_RE

GitHubexifdev/prineo_re

Reverse engineering of the engine powering the PriPara games on arcade.

binary-analysiscryptographyeducation+3
625 days ago
GZDoom-Arbitrary-Code-Execution-via-ZScript-PoC preview

GZDoom-Arbitrary-Code-Execution-via-ZScript-PoC

GitHubchainmanner/gzdoom-arbitrary-code-execution-via-zscript-poc

Proof of concept for CVE-2024-54756, a vulnerability I found in GZDoom's ZScript scripting engine.

binary-exploitationeducationexploitation+5
131 year ago
KeyPatchX preview

KeyPatchX

GitHubgmh5225/keypatchx

KeyPatch Enhanced — IDA Pro plugin for symbol-aware x86/x64 assembly patching, powered by Keystone Engine. Fork of Keypatch with automatic IDA symbol…

binary-analysisbinary-exploitationdebuggers+4
97 months ago
LinusWare-Source-Code-Internal preview

LinusWare-Source-Code-Internal

GitHubtekkenbugattii/linusware-source-code-internal

Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…

binary-analysiscode-analysisexploitation+3
41 month ago
CVE-2026-1801C preview

CVE-2026-1801C

GitHubmisterdengi/cve-2026-1801c

Static reverse-engineering analysis of movement input heuristics in Source 2 engine, identifying structural edge cases in input automation and jump…

binary-analysisexploitationpapers-research+2
10 days ago
gmh5225 preview

gmh5225

GitHubgmh5225/gmh5225

LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…

ai-assisted-reversingbinary-analysisbinary-exploitation+4
2 months ago
external_v8_AOSP10_r33_CVE-2021-0396 preview

external_v8_AOSP10_r33_CVE-2021-0396

GitHubsatheesh575555/external_v8_aosp10_r33_cve-2021-0396

Repository containing V8 JavaScript engine source code with a specific commit for CVE-2021-0396, likely for vulnerability research and exploitation.

binary-exploitationcode-analysisexploitation+3
3 years ago
CVE-2022-32898 preview

CVE-2022-32898

GitHubox1111/cve-2022-32898

Technical analysis and exploit demonstration of CVE-2022-32898, a kernel memory corruption vulnerability in Apple Neural Engine driver, with detailed…

binary-exploitationexploitationhardware-security+4
2 years ago
Previous1234Next